الانتقال إلى تقرير الأمان
أمن المجال وذكاء التهديدات
xautswap.finance favicon

xautswap.finance

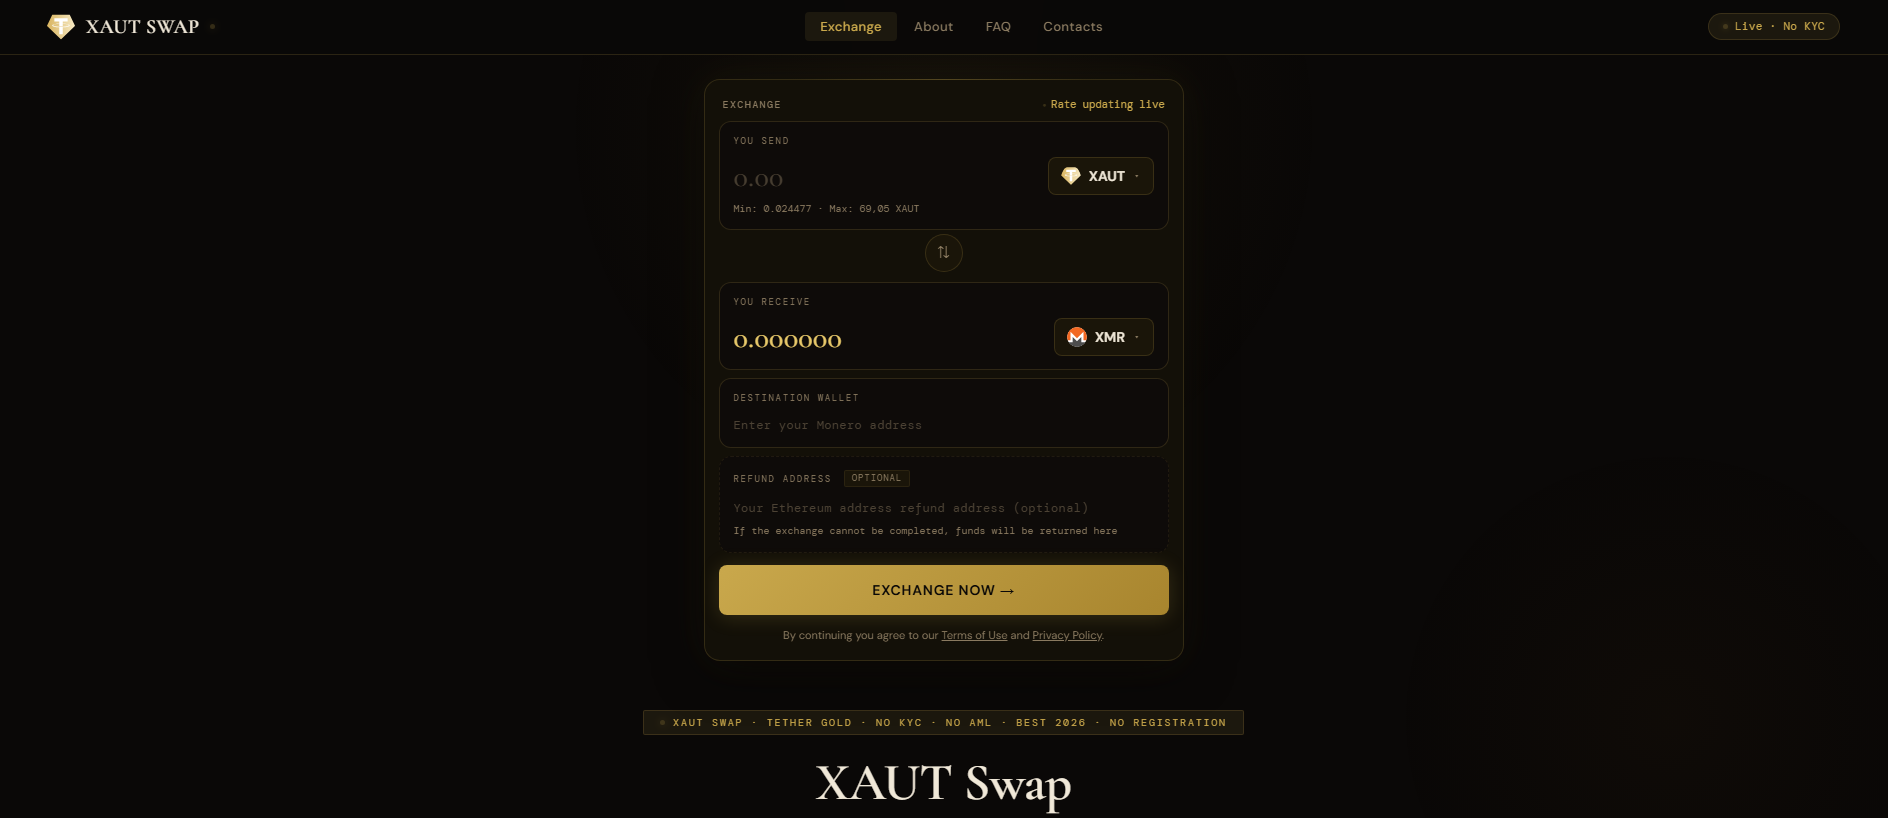
“XAUT Swap No KYC No AML Best 2026 — #1 Anonymous Crypto Exchange”

مسجّل النطاق
NiceNIC
Resolved IP
104.21.44.68
Registered
11/06/2026
حكم التهديد حرجة
التوفر آخر نشاط معروف أحدث مراقبة إمكانية الوصول المخزنة
اكتشافات VirusTotal: 14/91 Spamhaus DBL: DBL_PHISH انتحال العلامة التجارية: Aave
OTX: 16 refs 11/06/2026 Aave CDN
API
تم الإبلاغ عن هذا النطاق باعتباره ضارًّا
محركات الأمان التي تبلغ عن اكتشاف: 14. توخي الحذر الشديد — لا تدخل بيانات الاعتماد أو المعلومات الشخصية.
ملخص التقرير

Analysis of xautswap.finance, created on June 11 2026 and hosted behind Cloudflare (IP 104.21.44.68, located in CA), shows multiple indicators of malicious acti

يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
14 det.
OTX references
شهادة TLS
منتهية الصلاحية أو غير متحقق منها
العمر
4 mo
الحالة المرصودة
آخر نشاط معروف 200
PhishDestroy
قائمة الإتلاف
مدرج

Source evidence

6 sources

VirusTotal

14 / 91

إبلاغ

Spamhaus DBL

DBL_PHISH

OTX

16 community references

إبلاغ

URLScan capture

التقرير المخزن

Stored URLScan capture preview
إبلاغ

URLScan verdict

اكتمل التحليل

إبلاغ

Google Safe Browsing

Checked; no threat flag recorded

إبلاغ
استخبارات أمن الشبكات Registrar context
Registrar context NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
NiceNIC Verdict Full Investigation

ملخص الأدلة

حرجة
VirusTotal
14/91
OTX
16 community refs
URLScan
Stored capture

Analysis of xautswap.finance, created on June 11 2026 and hosted behind Cloudflare (IP 104.21.44.68, located in CA), shows multiple indicators of malicious activity. The domain is registered through NICENIC INTERNATIONAL GROUP CO., LIMITED and resolves to a Cloudflare address, obscuring the underlying server infrastructure. The site presents the page title "XAUT Swap No KYC No AML Best 2026 — #1 Anonymous Crypto Exchange," which aligns with the classified scam type of an investment scam targeting cryptocurrency users. The SSL certificate is issued by Let’s Encrypt (YE1), providing encryption but offering no assurance of legitimacy. HTTP responses return status 200, indicating the site is actively serving content.

Security telemetry records the domain on a single blocklist and notes that PhishDestroy has blocked it. VirusTotal scans report six of ninety‑one security vendors flagging the domain as malicious, reinforcing the suspicion. AlienVault OTX lists the domain in four separate threat intelligence pulses, further corroborating its malicious reputation. Independent trust scoring by Gridinsoft assigns a score of 0 out of 100, reflecting a complete lack of trust.

Nameservers kiki.ns.cloudflare.com and sri.ns.cloudflare.com are standard Cloudflare entries, offering no additional attribution. While the evidence confirms active malicious use, the precise payload or credential‑harvesting mechanisms remain undisclosed in the available data. Defenders should immediately block the domain and its resolving IP at perimeter and DNS layers, monitor for related Cloudflare‑hosted infrastructure, and apply heuristic rules to detect similar page‑title patterns. Ongoing observation of threat‑intel feeds for additional pulses or blocklist entries is recommended to capture potential expansion of the campaign.

تحليل الكشف والتهرب

فحص التمويه وتوزيع حركة المرور

لم يُلاحظ لم يُلاحظ وجود أي إخفاء في المسح المخزّن

الملاحظات المخزنة المتعلقة بالمقارنة بين برامج الزحف والمتصفح لهذا المضيف، بالإضافة إلى فحص مباشر للبصمة الرقمية لأنظمة توزيع حركة المرور على غرار «كيتارو».

علامة التخفي المخزنة
لم يُلاحظ
آخر فحص للتخفي
رأس الخادم الذي يراه الماسح الضوئي
cloudflare

ملاحظة خاصة بالماسح الضوئي: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare

التحقق المباشر من بصمات الأصابع عبر تطبيق «TDS»
سبع بصمات «كيتارو» بالإضافة إلى مقارنة بين المتصفح المتنقل والمتصفح العادي، يتم تشغيلها من الماسح الضوئي PhishDestroy عند فتح هذه اللوحة.
الانتظار

لقطة محفوظة · 2 captures

عنوان الصفحة
XAUT Swap No KYC No AML Best 2026 — #1 Anonymous Crypto Exchange
Impersonates
Aave Across Aptos Arbitrum Avalanche Base Chainlink Cosmos +9
شهادة TLS
Hostname coverage not recorded · صادرة عن Let's Encrypt / YE1 · stored validity ends in 83 days

Domain details

النطاق
URLScan Verdict اكتمل التحليل score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden لا تُنسب سمعة Edge-IP إلى هذا المجال.
OTX Tags 2026-06activeall-domainsblocklistcontentcryptoالمجالاتdrainerfraudlivemonthlyphishdestroyphishingscam
مسجّل النطاق NiceNIC RU(RU) PhishDestroy Investigation
جهة الإبلاغ عن إساءة الاستخدامabuse@nicenic.net
البحث في قاعدة بيانات WHOISICANN RDAP لـ xautswap.finance →
التسجيلتم إنشاؤه 11/06/2026 (121d) — Expires 21/03/2027
حالة HTTP200
التفاصيل التقنيةProvenance & timestamps
تاريخ أول اكتشاف11/06/2026
DOM Analysisanalyzed 09/10/2026score 98/10017 brand signals
Submitted URLhttps://xautswap.finance/
Favicon Hash
ICANN OVERSIGHT

الاعتماد وسياق RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft لا يُرسل أي شيء تلقائياً.

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
104.21.44.68
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
Toronto, CA
Server header
cloudflare

لا تُنسب سمعة Edge-IP إلى هذا المجال.

خوادم الأسماء 2

  • kiki.ns.cloudflare.com
  • sri.ns.cloudflare.com

Location describes the IP network.

شهادة TLS

Issuer
Let's Encrypt / YE1
Valid from
2026-10-05 13:47:11
Valid until
2027-01-03 13:47:10
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-10 07:02:12 UTC
Collection source
PhishDestroy collector
Certificate fingerprint90e5cff6fb3badb40d6c28466015e6024e96ad5d0aec9b7d38dd08d9ec98f591

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 104.21.44.68rapiddns.io

Latest Classified Outcome 2026-10-11 11:00:07 UTC

Primary outcome محتوى نشط reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation محتوى نشط Ordinary HTTP content served 90% 2026-10-11 11:00:07 UTC
RDAP registration غير معروف
Observed timeline last reachable: 2026-10-11 11:00:07 UTC last content: 2026-10-11 11:00:07 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
الإبلاغ عن هذا النطاق أرسل الأدلة وساعد في حماية الآخرين

تحليل VirusTotal

14 / قام موردو الأمان 91 بوضع علامة على هذا المجال
View on VT
Last analyzed Previous stored snapshot: 15 detections
alphaMountain.ai
BitDefender
Chong Lua Dao
CRDF
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
سوفوس
VIPRE
Webroot

مسار الاستجابة للتهديدات Pipeline

الاكتشاف
Analysis
Monitoring

10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

تم استيعاب التهديد
xautswap.finance تم اكتشافها وإدراجها في قائمة الانتظار لإجراء تحليل شامل
11/06/2026
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
12/09/2026
URLScan.io Capture
محفوظ URLScan report with capture artifacts
11/06/2026
VirusTotal
14/91 recorded on VirusTotal
28/09/2026
OTX Community References
16 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
03/10/2026
Registrar Context: NiceNIC
Separate registrar research is available. Registrar association is contextual and is not scored as an independent detection.
Brand Impersonation
Impersonation of Aave
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
11/06/2026
Technical Analysis Recorded
يحتوي التقرير على التكنولوجيا المخزنة أو نتائج تحليل الطب الشرعي.
11/10/2026
تم نشر قائمة «DestroyList»
11/06/2026
Monitoring Continues
يظل المجال قابلاً للوصول أو مقيد الوصول؛ قد تؤدي الفحوصات المستقبلية إلى تحديث هذه الملاحظة.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

آلة الزمن Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

نطاقات متشابهة

٩٥ نطاقًا متشابهًا محفوظًا

aavef.com addition تقرير داخلي xn--ave-ila.com homoglyph تقرير داخلي 1ave.com replacement a1ve.com replacement a2ve.com replacement aa.ve.com subdomain aaev.com transposition aage.com replacement aav4.com replacement aavi.com vowel-swap aavo.com vowel-swap aavr.com replacement
عرض الكل (83)
aavs.com replacement aavw.com replacement aove.com vowel-swap auve.com vowel-swap avae.com transposition awve.com replacement ayve.com replacement azve.com replacement oave.com vowel-swap save.com replacement uave.com vowel-swap wave.com replacement 1aave.com insertion 2ave.com replacement a-ave.com hyphenation aa6e.com bitsquatting aaave.com repetition aabe.com replacement aace.com replacement aacve.com insertion aare.com bitsquatting aate.com bitsquatting aauc.com homoglyph aaue.com homoglyph aav.com omission aav3.com replacement aava.com bitsquatting aavbe.com insertion aavc.com homoglyph aavce.com insertion aavd.com bitsquatting aavec.com addition aaved.com addition aavee.com addition aaveg.com addition aavek.com addition aavel.com addition aaven.com addition aaveo.com addition aaveq.com addition aaver.com addition aaves.com addition aavet.com addition aavex.com addition aavey.com addition aavg.com bitsquatting aavm.com bitsquatting aavu.com bitsquatting aavve.com repetition aavz.com replacement aawe.com bitsquatting acve.com bitsquatting aeve.com bitsquatting aive.com bitsquatting aqave.com insertion aqve.com bitsquatting asave.com insertion asve.com replacement ave.com omission awave.com insertion ayave.com insertion azave.com insertion cave.com bitsquatting eave.com bitsquatting iave.com bitsquatting qaave.com insertion saave.com insertion waave.com insertion xn--80aap9w.com cyrillic xn--aa-g7r68c.com homoglyph xn--aa-g7r83g.com homoglyph xn--aav-5qa.com homoglyph xn--aav-mra.com homoglyph xn--ae-dla019z.com homoglyph xn--ae-dla4955b.com homoglyph xn--ae-dla6031a.com homoglyph xn--ae-e5s275e.com homoglyph xn--ae-tfb535y.com homoglyph yaave.com insertion yave.com replacement zaave.com insertion aavea.com addition aavew.com addition

بلاغات المجتمع

أبلغ عنه عضو واحد في المجتمع؛ شوهد أول مرة في 11/06/2026

البلاغات المحفوظة
1
عناوين URL الفريدة المبلغ عنها
1
مقبول1

الأدلة والتقارير الخارجية

نظام أسماء النطاقات (DNS) والشبكات
تحسين محركات البحث (SEO) والنطاقات
تحليل متعمق

هل تأثرت بهذا الموقع؟

4 evidence signal groups linked 0 reports recorded آخر نشاط معروف
If credentials were compromised, report immediately. Do not engage with recovery scammers.

إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.

اليوروبول
ابحث عن قناة التقارير الرسمية لبلدك في الاتحاد الأوروبي
National police directory
احذروا من المحتالين الذين يزعمون أنهم يساعدون في استرداد الأموال! قد يتصل المجرمون بالضحايا مرة أخرى بينما يتظاهرون بأنهم محققون أو محامون أو وكلاء استرداد. لا تدفع رسومًا مقدمة أو تشارك بيانات الاعتماد. تعرف على المزيد حول الاحتيال في مجال التعافي →

أبلغ السلطات المحلية

حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.

دليل 97 دولة

Template-based draft · optional AI wording assistance requires separate consent

المسودة بمساعدة الذكاء الاصطناعي - تتم معالجة تفاصيل الحادث بواسطة موفر الذكاء الاصطناعي · قم بمراجعتها وتقديمها بنفسك

تحقق من أي نطاق

تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة

امسح الآن

الإبلاغ عن محاولة تصيد احتيالي

أرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع

إبلاغ

تحديثات فورية حول التهديدات

تقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة

مراقبة

ابقَ على اطلاع، وابقَ آمنًا

راقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب

تحديثات فورية حول التهديدات الاعتراض على هذا الإعلان
HTML · IFRAME

تضمين هذا التقرير

شارك هذه المعلومات الاستخباراتية المتعلقة بالتهديدات على موقعك الإلكتروني أو مدونتك

embed.html
<iframe
  src="https://phishdestroy.io/ar/embed/domain/xautswap.finance"
  title="PhishDestroy threat report for xautswap.finance"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>