مركز IC3 التابع لمكتب التحقيقات الفيدرالي (FBI)
الإبلاغ عن الجرائم المتصلة بالإنترنت في الولايات المتحدة
Federal tips line1-800-CALL-FBI
“Tornado Cash”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@porkbun.com.
The latest stored availability evidence still shows the domain reachable; 26 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
tornadocash.wiki — يمكن الوصول إليها · الوصول مقيد (HTTP 403). انتحال العلامة التجارية: Unknown; نوع الاحتيال: Impersonation. ملخص الأدلة: VirusTotal 9/91 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 80/100. مسجّل النطاق: Porkbun.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.
Assessment
Stored evidence for tornadocash.wiki: VirusTotal recorded 9 detections among 91 scanners on 2026-08-31. That ratio reproduces the stored check in its original units and is not converted into another measure. MetaMask and SEAL appear as named external blocklist observations for tornadocash.wiki. Each item in this report remains at the scope supplied by its dated source record.
Detection Evidence
VirusTotal records 9 detections among 91 scanners in the stored snapshot dated 2026-08-31. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-08-31 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.
Source Context
MetaMask and SEAL are recorded as named external blocklist observations for tornadocash.wiki in the snapshot dated 2026-09-18. The stored MetaMask and SEAL blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains tornadocash.wiki as a publisher record. That PhishDestroy record is counted separately from the MetaMask and SEAL external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.
Reachability and Timeline
The record first observed tornadocash.wiki on 2026-08-26. The MetaMask and SEAL blocklist snapshot is dated 2026-09-18 and remains a separate event in the stored timeline. A stored HTTP status 403 was observed for tornadocash.wiki on 2026-09-17. The HTTP status 403 dated 2026-09-17 records a single response for later comparison. The registration date is separately recorded as 2026-08-14. A URLScan reference was stored on 2026-08-26 as a dated artifact for review. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.
Registration and Infrastructure
For tornadocash.wiki, the registrar field records Porkbun; this is kept as an exact source value. The source stores 188.114.96.3 as the observed address in this record. The registration date for tornadocash.wiki is recorded as 2026-08-14. The SSL issuer is recorded as Google Trust Services / WE1 in the snapshot dated 2026-08-26. The stored ASN observation records 13335 and Cloudflare, Inc. in this record. The observed server header is recorded as cloudflare in this record. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.
Conclusion
The tornadocash.wiki record states that VirusTotal recorded 9 detections among 91 scanners on 2026-08-31. MetaMask and SEAL remain named blocklist observations from the snapshot dated 2026-09-18. PhishDestroy remains a separate publisher catalogue entry in the stored record. For tornadocash.wiki, the registrar field records Porkbun; this remains separate from the other source fields. The observed address field in this record contains 188.114.96.3. The supported conclusion is bounded to the exact stored observations for tornadocash.wiki. Any statement beyond those source values would require additional dated material.
Recommended Actions
Avoid submitting sensitive information to tornadocash.wiki during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain tornadocash.wiki as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and MetaMask and SEAL blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to tornadocash.wiki. The stored record does not justify extending that rule to 188.114.96.3 or to other infrastructure records.

188.114.96.3. Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
cloudflareScanner note: cloudflare_ban: raw=cf_phishing_block; http=403; via=https_proxy; server=cloudflare; provider_error=cloudflare_phishing_interstitial
Provider response during scan: cloudflare_phishing_interstitial
 (US)
 Toronto, CA
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Google PageSpeed Insights — mobile performance audit of tornadocash.wiki · checked Aug 26, 2026
٦ بلاغات مجتمعية
الفئةPHISHING
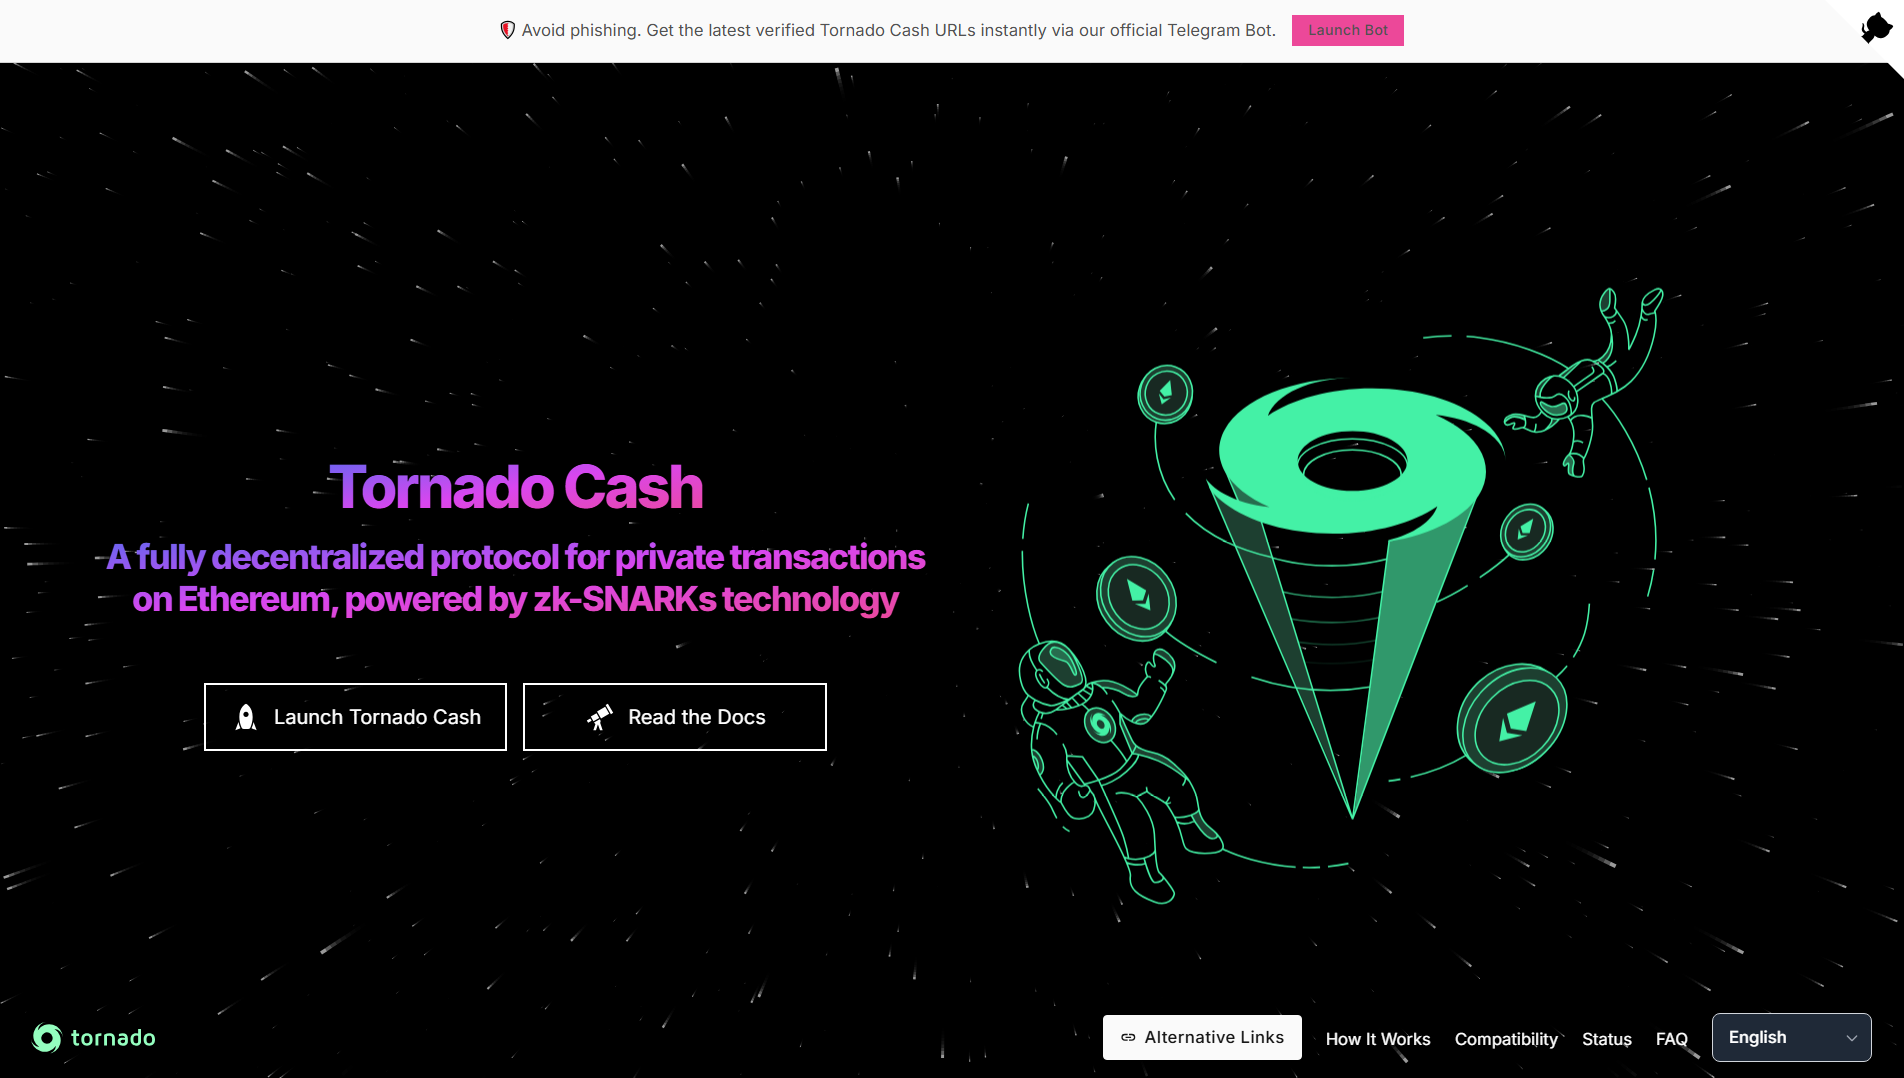
We are writing to report a phishing website that copies the Tornado Cash site to deceive visitors and put their crypto assets at risk. The domain tornadocash[.]wiki serves a full copy of the official homepage: the headline "A fully decentralized protocol for private transactions
“We are writing to report a phishing website that copies the Tornado Cash site to deceive visitors and put their crypto assets at risk. The domain tornadocash[.]wiki serves a full copy of the official homepage: the headline "A fully decentralized protocol for private transactions on Ethereum, powered by zk-SNARKs technology", the branded funnel-and-astronaut artwork, and the "Launch Tornado Cash" and "Read the Docs" buttons. The most telling part is a banner the operator placed across the top o”
PD-20260826-01F5FB Recipient: abuse@porkbun.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (US): 18 U.S.C. § 1343 - Wire Fraud 18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA) 15 U.S.C. § 45 - FTC Act (Deceptive Practices) Federal laws prohibit wire fraud, computer fraud, and deceptive business practices. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Infrastructure map · tornadocash.wiki
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
يتم حل هذه التقارير إلى نفس عنوان IP للحافة المشتركة. إنها تساعد في اكتشاف التقارير ولكنها لا تتضمن ملكية مشتركة أو خادم أصل مشترك.
These domains also target غير معروف users. View all Unknown threats →
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب


 metamask.trade
 heldge.one
 undress.xxx
 docsign.dn3.co
 primarkpolska.pl