Spamhaus DBL
DBL_PHISH
Interpretation & limits
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.

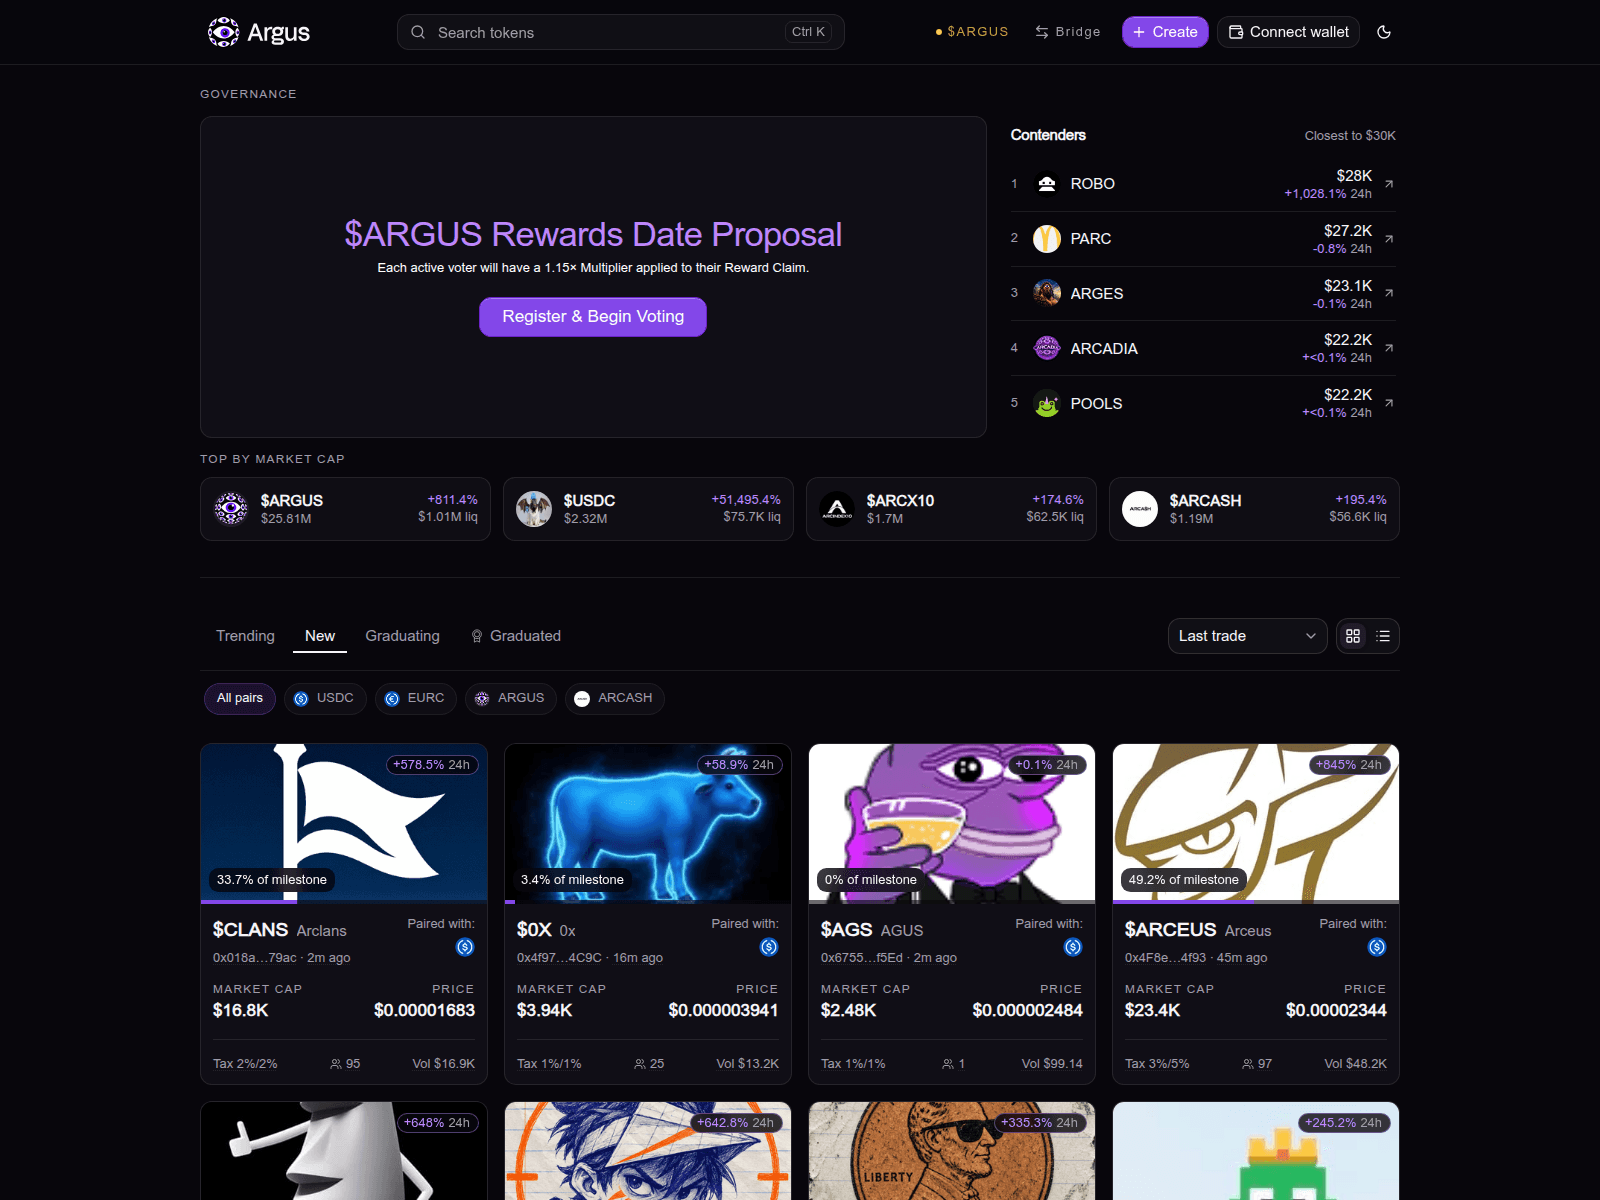
“Argus | Governance”
Assessment based on the stored source evidence below. Review sources →
gov-argus.lat — لم يتم التحقق منها. انتحال العلامة التجارية: Revolut; نوع الاحتيال: Crypto Drainer. ملخص الأدلة: VirusTotal 0/92; Spamhaus DBL_PHISH; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 85/100. مسجّل النطاق: NiceNIC.
يبقى تحليل PhishDestroy AI المفصل أدناه باللغة الإنجليزية للحفاظ على السجل الجنائي الرقمي الأصلي.

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.
DBL_PHISH
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
checked — no detections recorded
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.
no community references
إبلاغCommunity publication references, not a vendor verdict or evidence of a common operator.
provider verdict: clean
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
التقرير المخزن
 إبلاغ
A preserved page image documents what the collector received; a capture is not a safety verdict.
اكتمل التحليل
إبلاغThis is the recorded automated analysis. Completion alone is not a safety verdict.
Checked; no threat flag recorded
إبلاغA result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
Stored narrative · generated . Provider checks below retain their own observation dates.
The domain gov-argus.lat was observed in a MetaMask blocklist entry dated 2026-10-10, which provides a security context for its recorded presence. Additionally, a PageSpeed performance score was measured for the domain, offering insight into its technical profile.
MetaMask and SEAL both listed gov-argus.lat in their external blocklists as of 2026-10-10. VirusTotal checked the domain on 2026-10-10, recording 0 detections from 92 scanners. PhishDestroy internally listed the domain, and a PageSpeed performance score of 57 was measured on 2026-10-10. The domain was registered with NICENIC INTERNATIONAL GROUP CO., LIMITED on 2026-10-09.
PhishDestroy contains an internal listing for gov-argus.lat, documenting its inclusion in a security-focused database. VirusTotal records a scan measurement, which describes how many security engines detected issues at the time of observation. The blocklist entries from MetaMask and SEAL provide additional context for comparing security intelligence across sources, while the PageSpeed score offers a technical reference point.
For gov-argus.lat, retain the blocklist entries from MetaMask and SEAL for ongoing reference and comparison. Preserve the VirusTotal scan results and PhishDestroy internal listing to monitor changes in future assessments. Use the PageSpeed performance score as a baseline for tracking technical performance, and review new evidence as it becomes available.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x041D3031b8FD0f53d8CD6e085c15A75bbd5728EbFormat validated · Domain analysis0x08b4D64686591243c1C7287a4A4d72D774feC89aFormat validated · Domain analysis0x0A7428E217c846d101C5532b4570100d140EDcc9Format validated · Domain analysis0x0BFFa97f774824e9dA843699aEDd2835cb1b8022Format validated · Domain analysis0x12cE1F970722ca6e08364b60099b3d25c09b5434Format validated · Domain analysis0x1912ab620aF54c99a7cAfF0EF0CdA7a72271EC3eFormat validated · Domain analysis0x19bDcd9aa6E8584be70068517d25919A9d4D6eeFFormat validated · Domain analysis0x21255b43101F5566a540F053B117755948Bc44e2Format validated · Domain analysis0x2F4741053D78F953A74FEcC0B3e6CD047Aedd4fFFormat validated · Domain analysis0x334FF8615aB9846033510Ac12Fb441B6C41dFC98Format validated · Domain analysis0x38dfB736A696f325269BF13AD615172cD623FAF2Format validated · Domain analysis0x45671b2f51B8c7a8fCa298be9985EC03Bf0771f9Format validated · Domain analysis0x46763D1c4c974D06F561d1500b2E3B82aa4E5abbFormat validated · Domain analysis0x490300A75DB90626d3b3CB723862AA445a532E8FFormat validated · Domain analysis0x4A8E09C449A507D0307328952adc07AD1A57042fFormat validated · Domain analysis0x51D8F034c5252A137bC37BD66182F5eedDA09ABEFormat validated · Domain analysis0x5928e8cE614BE828A4B5aAF6d840910Ac6dB9525Format validated · Domain analysis0x6B830686a85b9D0B2568fEf5b3926038ef7e52B4Format validated · Domain analysis0x72a4120483059719A2Ff8d4b2627874cAc901143Format validated · Domain analysis0x7b8e7A8b164113dA9F4070a8A2144b050fefeEbfFormat validated · Domain analysishttps://t.me/argus_arcStored page referenceIoC extraction recorded 2026-10-11 04:01:31 UTC
الملاحظات المخزنة المتعلقة بالمقارنة بين برامج الزحف والمتصفح لهذا المضيف، بالإضافة إلى فحص مباشر للبصمة الرقمية لأنظمة توزيع حركة المرور على غرار «كيتارو».
ملاحظة خاصة بالماسح الضوئي: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='gov-argus.lat', port=80): Max retries exceeded with url: / (Caused by NewConnectionError("
 (RU)
PhishDestroy Investigation
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
لا تُنسب سمعة Edge-IP إلى هذا المجال.
leonard.ns.cloudflare.comveronica.ns.cloudflare.comLocation describes the IP network.
f4ef17738f599a12c5ac6ca554079d7a635bb1b931887c81b353ec5f9fc68939Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of gov-argus.lat · checked Oct 10, 2026
188.114.96.3.10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
إذا أدخلت بيانات اعتماد الحساب أو المعلومات الشخصية أو معلومات الدفع أو قمت بتنزيل ملف من هذا النطاق، فاتخذ إجراءً فوريًا. فيما يلي موارد لمساعدتك في الإبلاغ عن الحادث وحماية نفسك.


حدد بلدك للحصول على الاتصالات الرسمية المتعلقة بالجرائم الإلكترونية أو إنشاء مسودة شكوى →.
Template-based draft · optional AI wording assistance requires separate consent
كل مسار يمثل سببًا واحدًا لربط نطاق ما بهذا المضيف. يشير حجم العقدة إلى عمليات الكشف التي أجرتها VirusTotal، أما العقد المتقطعة فهي غير متصلة بالإنترنت بالفعل. وترد القوائم الكاملة أدناه.
نفس هاش أيقونة المفضلة أو نفس عنوان الصفحة الخاص بهذا المضيف.
يتم حل هذه التقارير إلى نفس عنوان IP للحافة المشتركة. إنها تساعد في اكتشاف التقارير ولكنها لا تتضمن ملكية مشتركة أو خادم أصل مشترك.
كما تستهدف هذه النطاقات مستخدمي موقع Revolut. عرض جميع التهديدات المتعلقة بـ «Revolut» →
تم تسجيلها عبر نفس الجهة المسجلة. وتقدم الجهة المسجلة خدماتها لملايين العملاء الذين لا تربطهم أي صلة ببعضهم البعض، لذا فإن هذا الأمر يُشير إلى وجود تجميع للتقارير وليس دليلاً على وجود صلة بينهما.
التقارير المضافة مؤخرًا من قاعدة بيانات PhishDestroy. لا تتضمن روابط الاكتشاف هذه بنية تحتية أو ملكية مشتركة.
تحليل التهديدات باستخدام قائمة الحظر المخزنة، وWHOIS، وDNS، وأدلة الفحص العامة
امسح الآنأرسل النطاقات المشبوهة إلى قاعدة بيانات التهديدات الخاصة بنا — ساهم في حماية المجتمع
إبلاغتقارير التصيد الاحتيالي الأخيرة وتغييرات التوفر الملحوظة
مراقبةراقب التهديدات في الوقت الفعلي أو اعترض على هذا الإدراج إذا كنت تعتقد أنه إنذار كاذب





