
ابحث في النطاقات الخاضعة للمراقبة وراجع الأدلة المخزنة وعمليات الكشف وأحدث حالة التوافر التي تمت ملاحظتها.
ابحث في التقارير المحفوظة. لا يرسل هذا الإجراء بلاغًا عن تهديد. عدم وجود سجل لا يعني أن النطاق آمن.
232,386
الإجمالي المتتبع
226,565
تم الكشف عن VT
93,667
شوهد آخر مرة نشطًا
138,719
غير متوفر عند آخر تحقق
8
في انتظار الموافقة من VT
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake النطاقات
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of التصيد الاحتيالي Pages
التصيد الاحتيالي pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of خبيث Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical التحليل
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. البنية التحتية-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea التصيد الاحتيالي Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App احتيال (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
الطلبات for private keys or seed phrases
Unexpected transaction requests
فقير website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1 Always verify domain authenticity
2 Enable two-factor authentication
3 Use hardware wallets for transactions
4 Regularly update security software
5 Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 597 domains tracked for this threat type
WalletConnect Abuse 597 domains
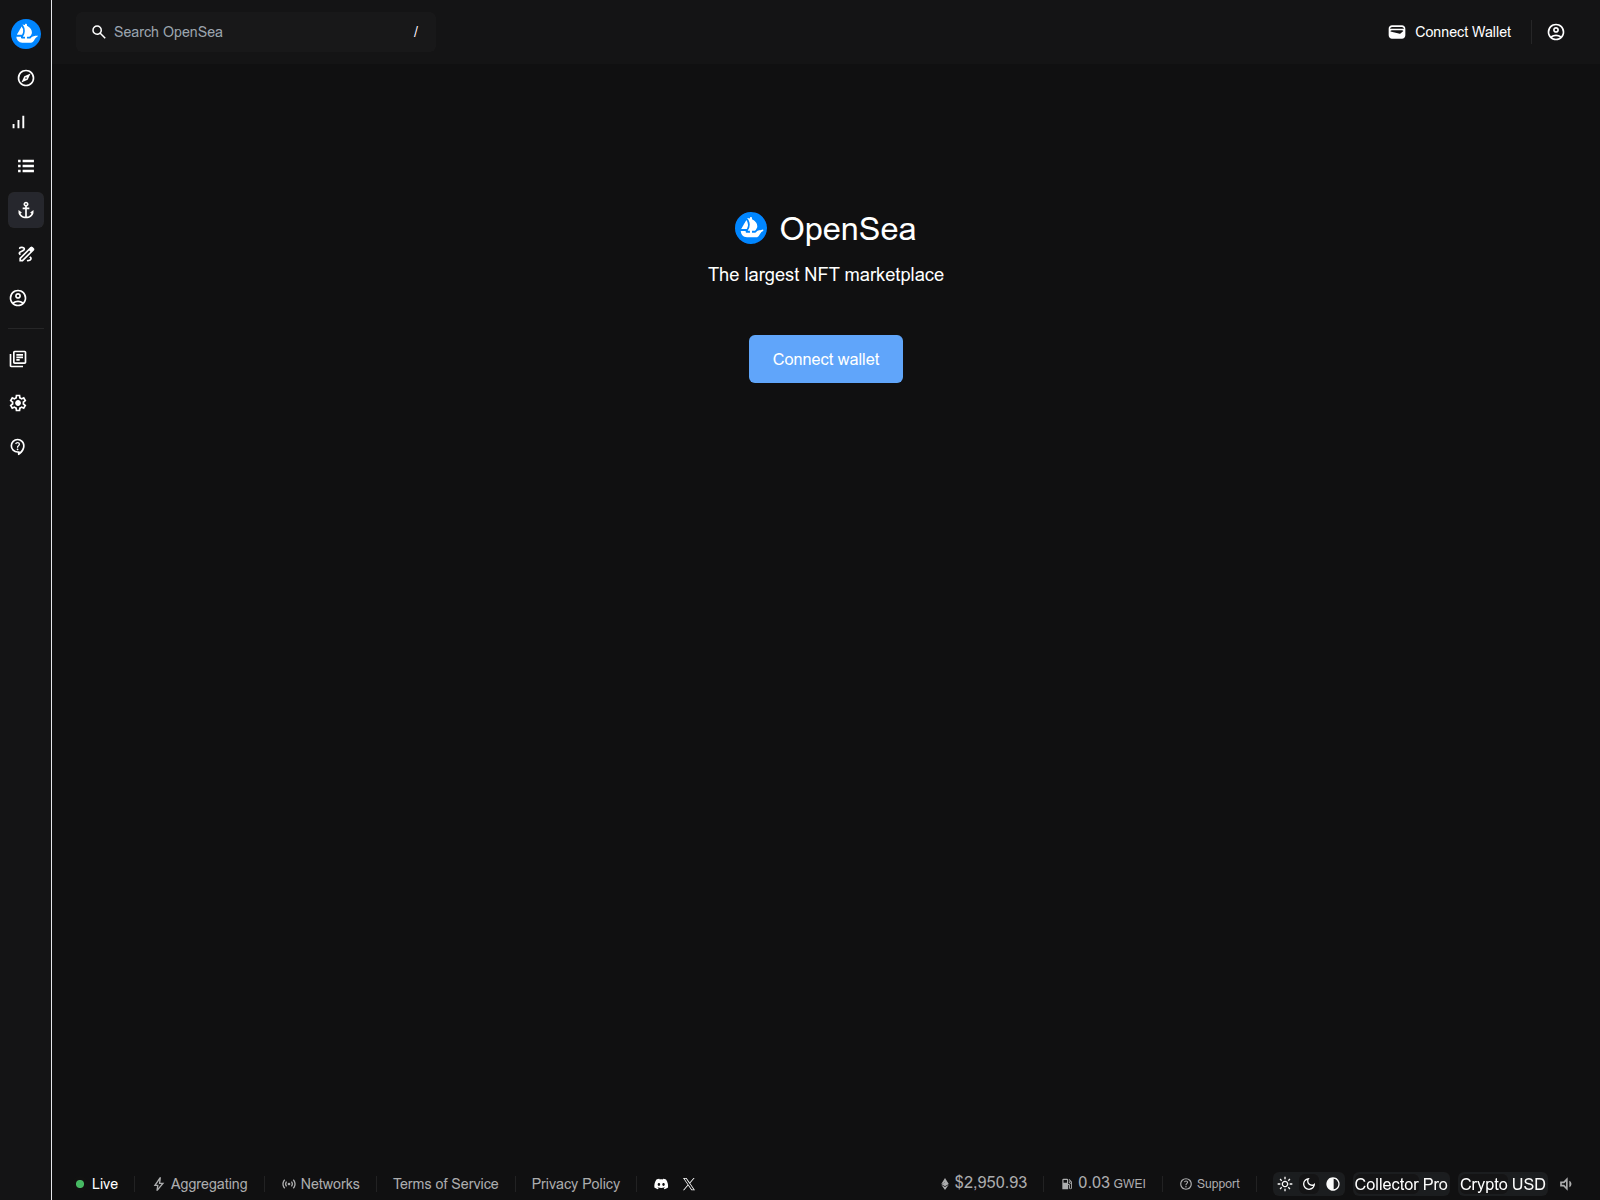

opensea.com.offer-proposal.com

getstemgames.shop

raf-pro.net

bepviews.com
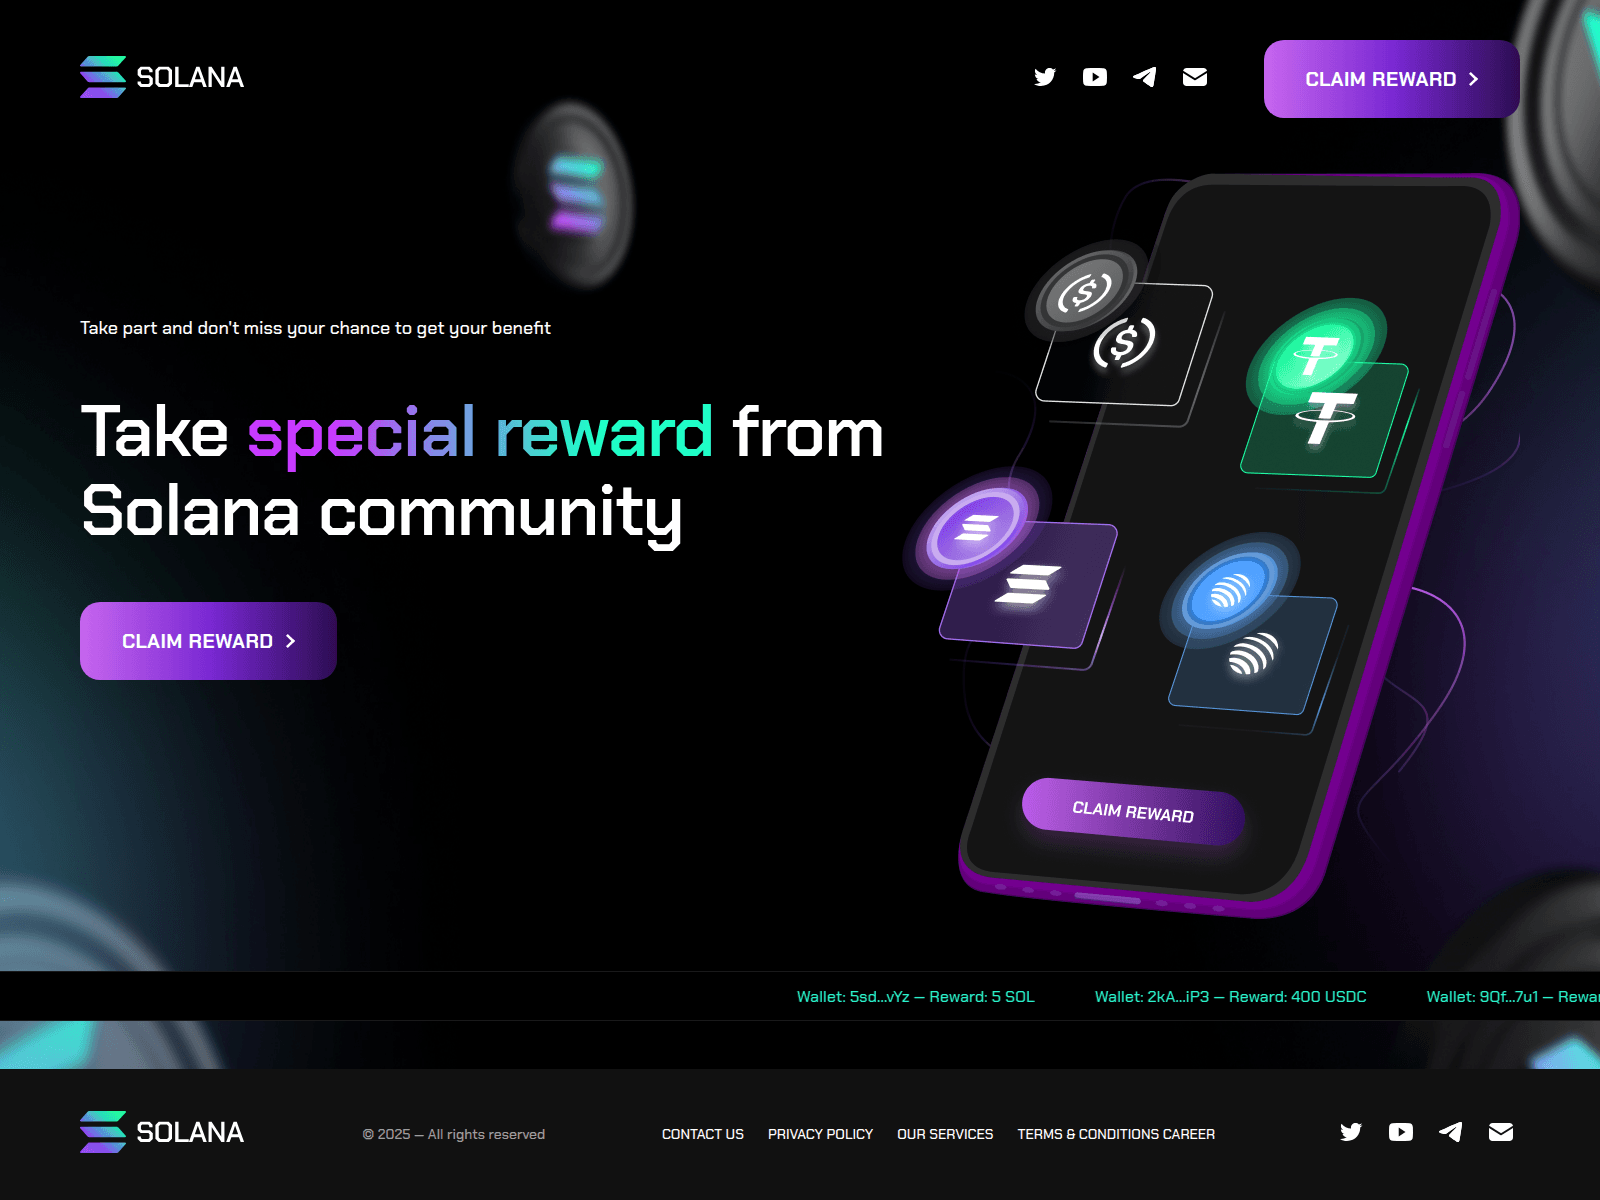
sol-blast.com
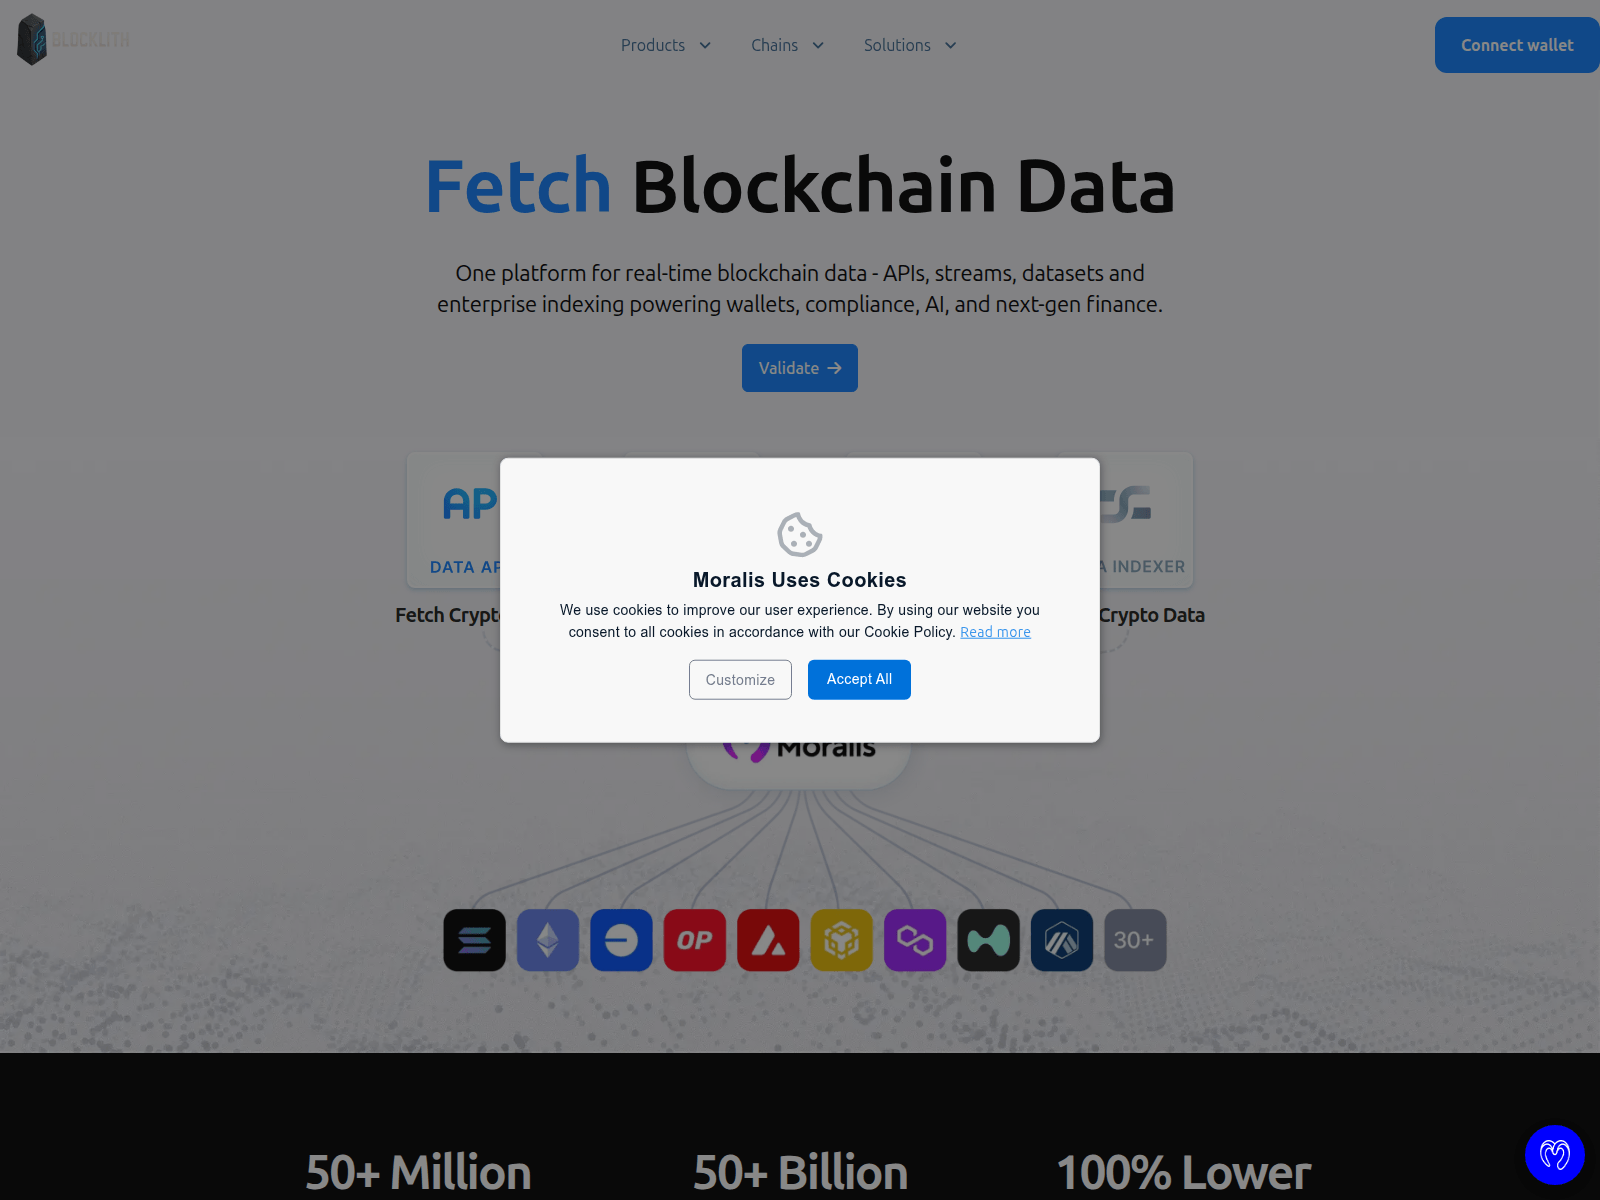
valtriva-block.xyz

fixvalidatorrefix.co
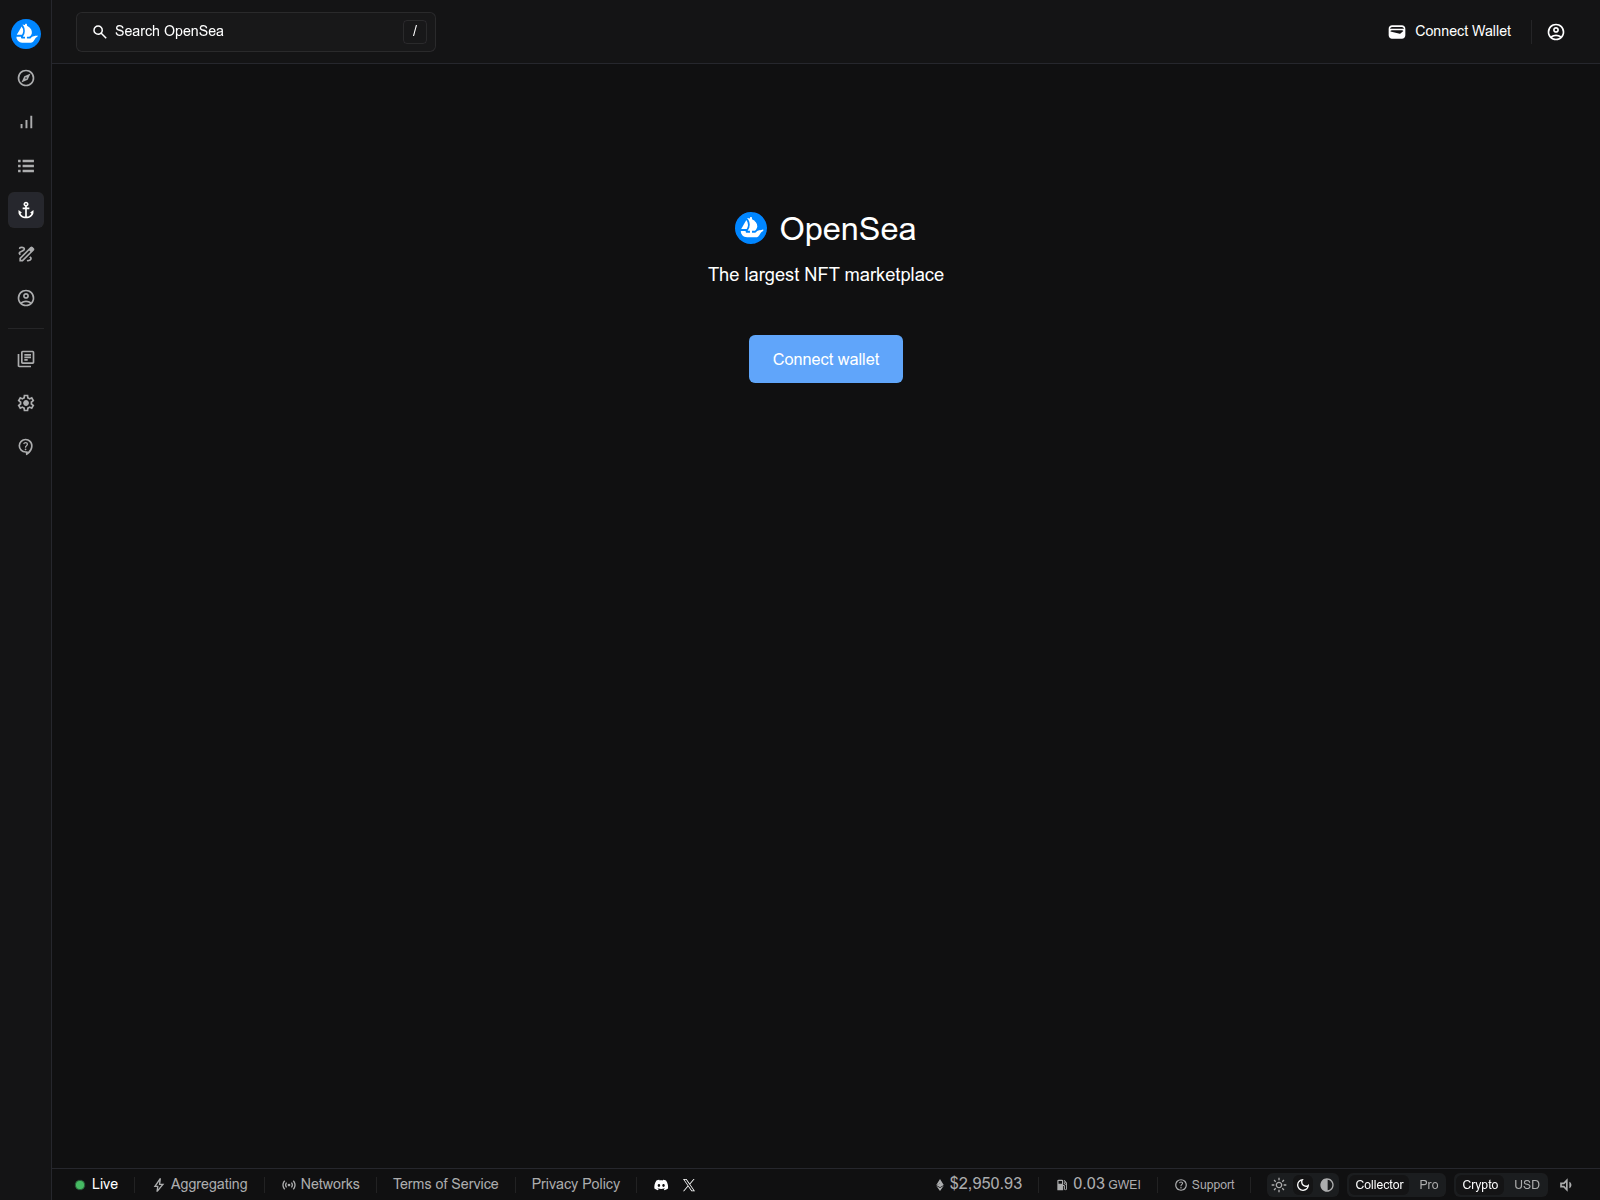
opensea.com.bids-weth.com
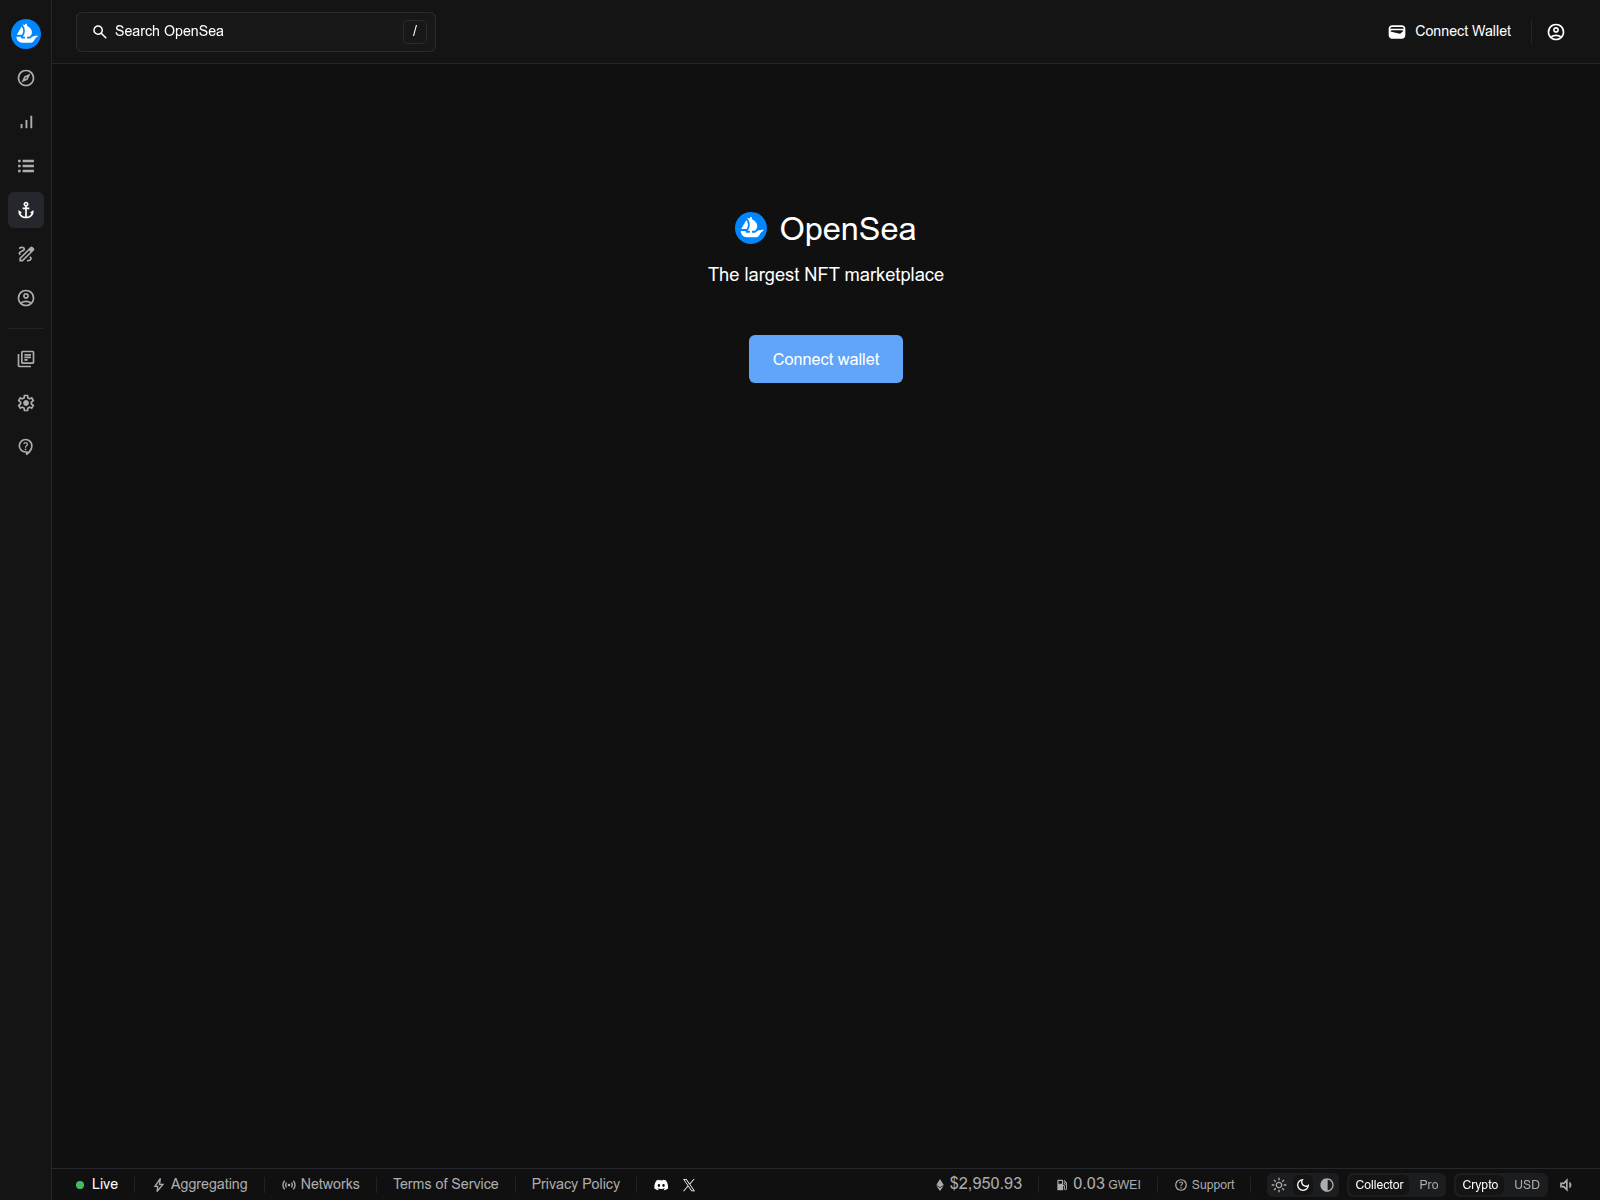
opensea.net.bid-awaiting.com

refixupdatenode.site

servicenoderectifer.site

swiftfixresolver.site

usol.top

waronusd1-claim.com
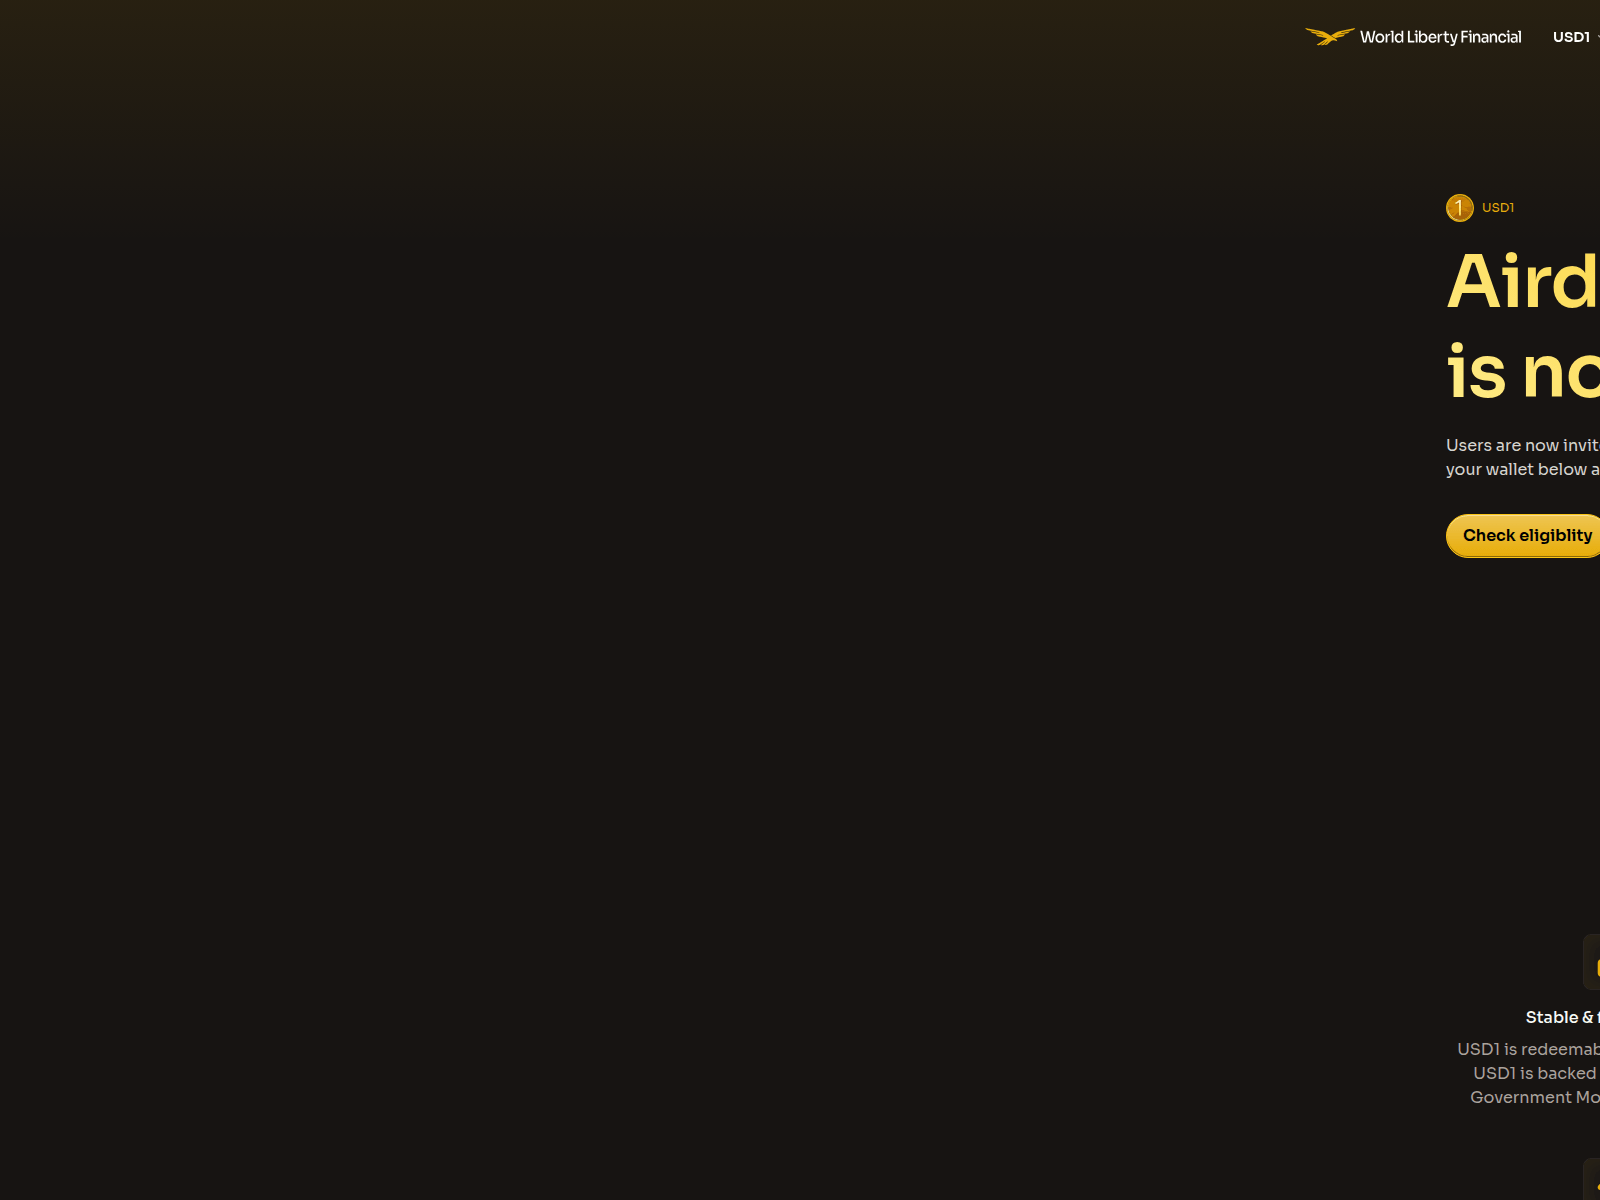
wlfilivedrop.xyz

claims-quick.live
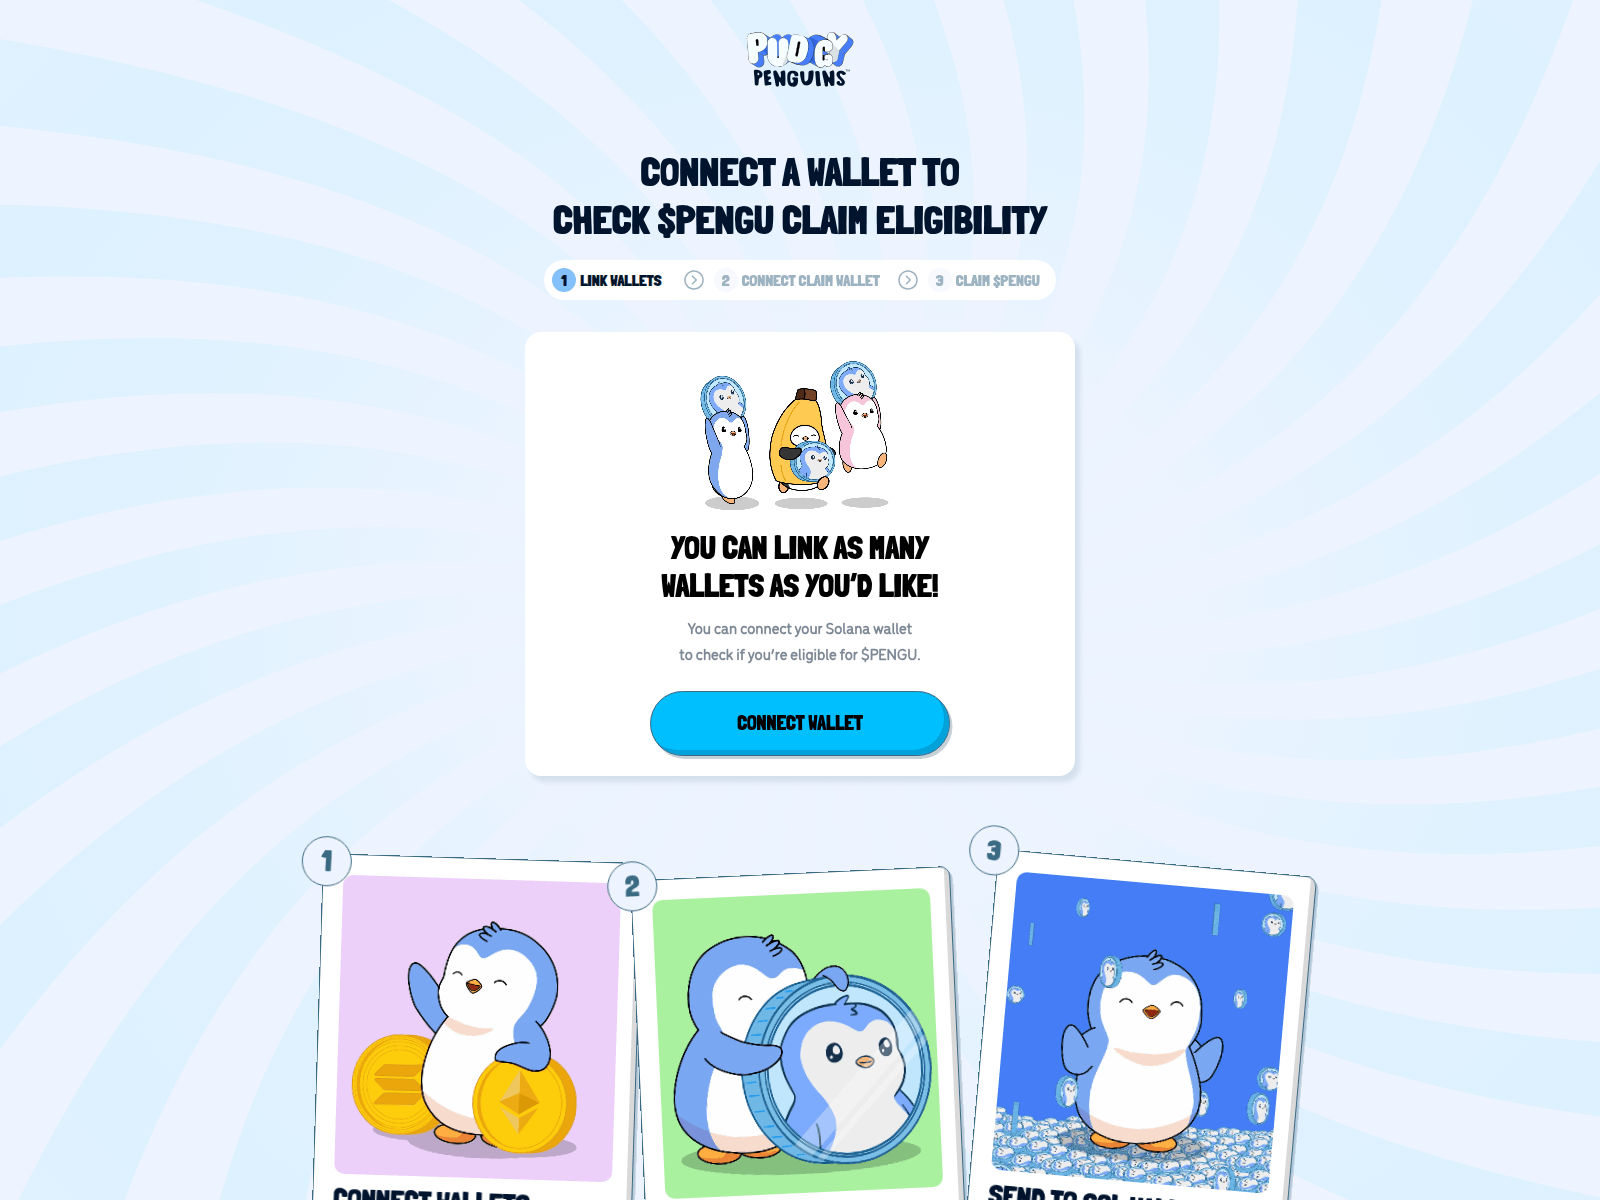
pudgyzpenguins.com

sol-generation.click
sols-drops.com

venus-protocol-interface-gupd1px1-poyaku.4everland.app
air.sol-shelter.cc
app-pancake-lunch-sw.com

deerpool.vip

dgportai.com
layer2-chain.com

nooxhub.pro
paijkcakeswap.com
paikecakeswap.com

pan-swap.org
pre-hourglass.app

sollspin.com

swiftsubdirectorynode.co

trafprt.com

trxaudit.org

usdaudit.org

webresolvvsol.xyz

wlfllibertyfinancial.com
www-cakev3pool.com
www-launchcake.com

xbt8x82irz1kbcyq.hgsa227.com

xbt8x82irz1kbcyq.hgsa242.com

app-mmt.finance

automaticnoderefix.co

bitgetmining.info
checkers-plasma.com

cryptomus.best
duplicate-disabled-12384.invalid
duplicate-disabled-12828.invalid

eligibility-xpl.xyz
iinea-hub.com
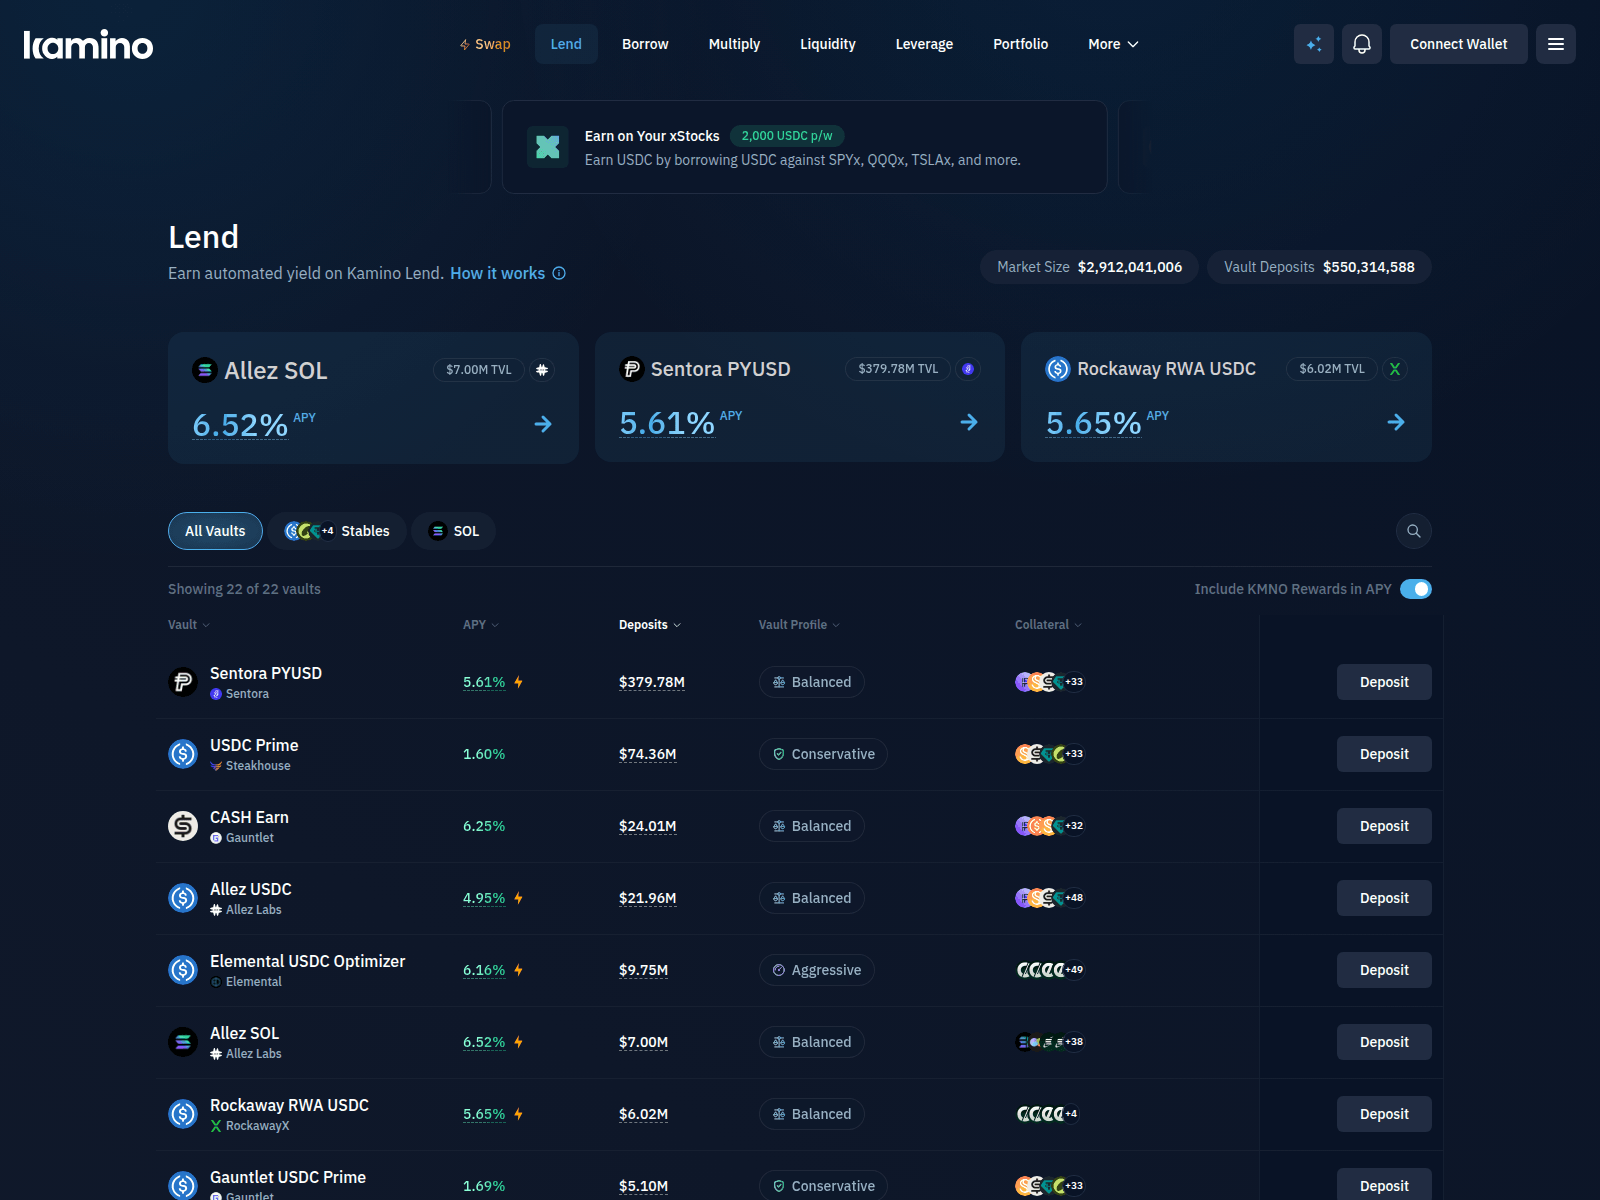
kamino.bond

kyc-hourglass.com

layer3-chain.xyz
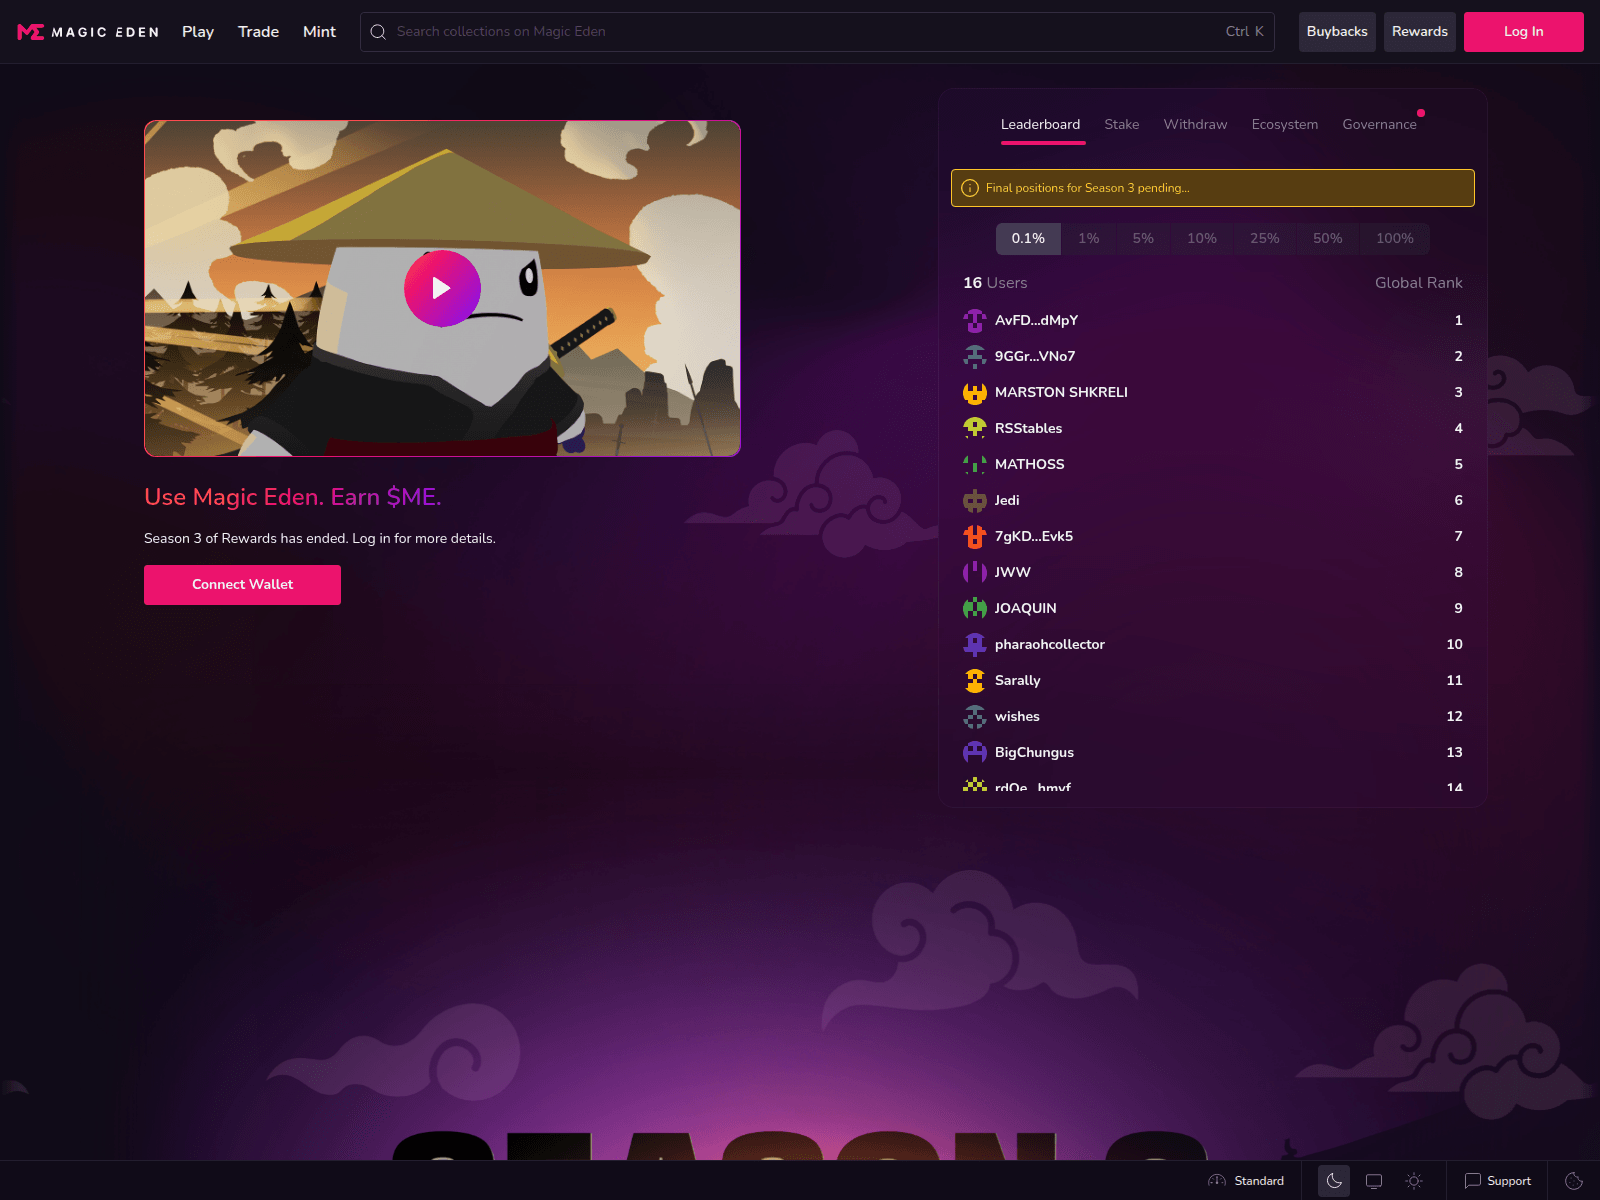
magicedena.offer-proposal.com
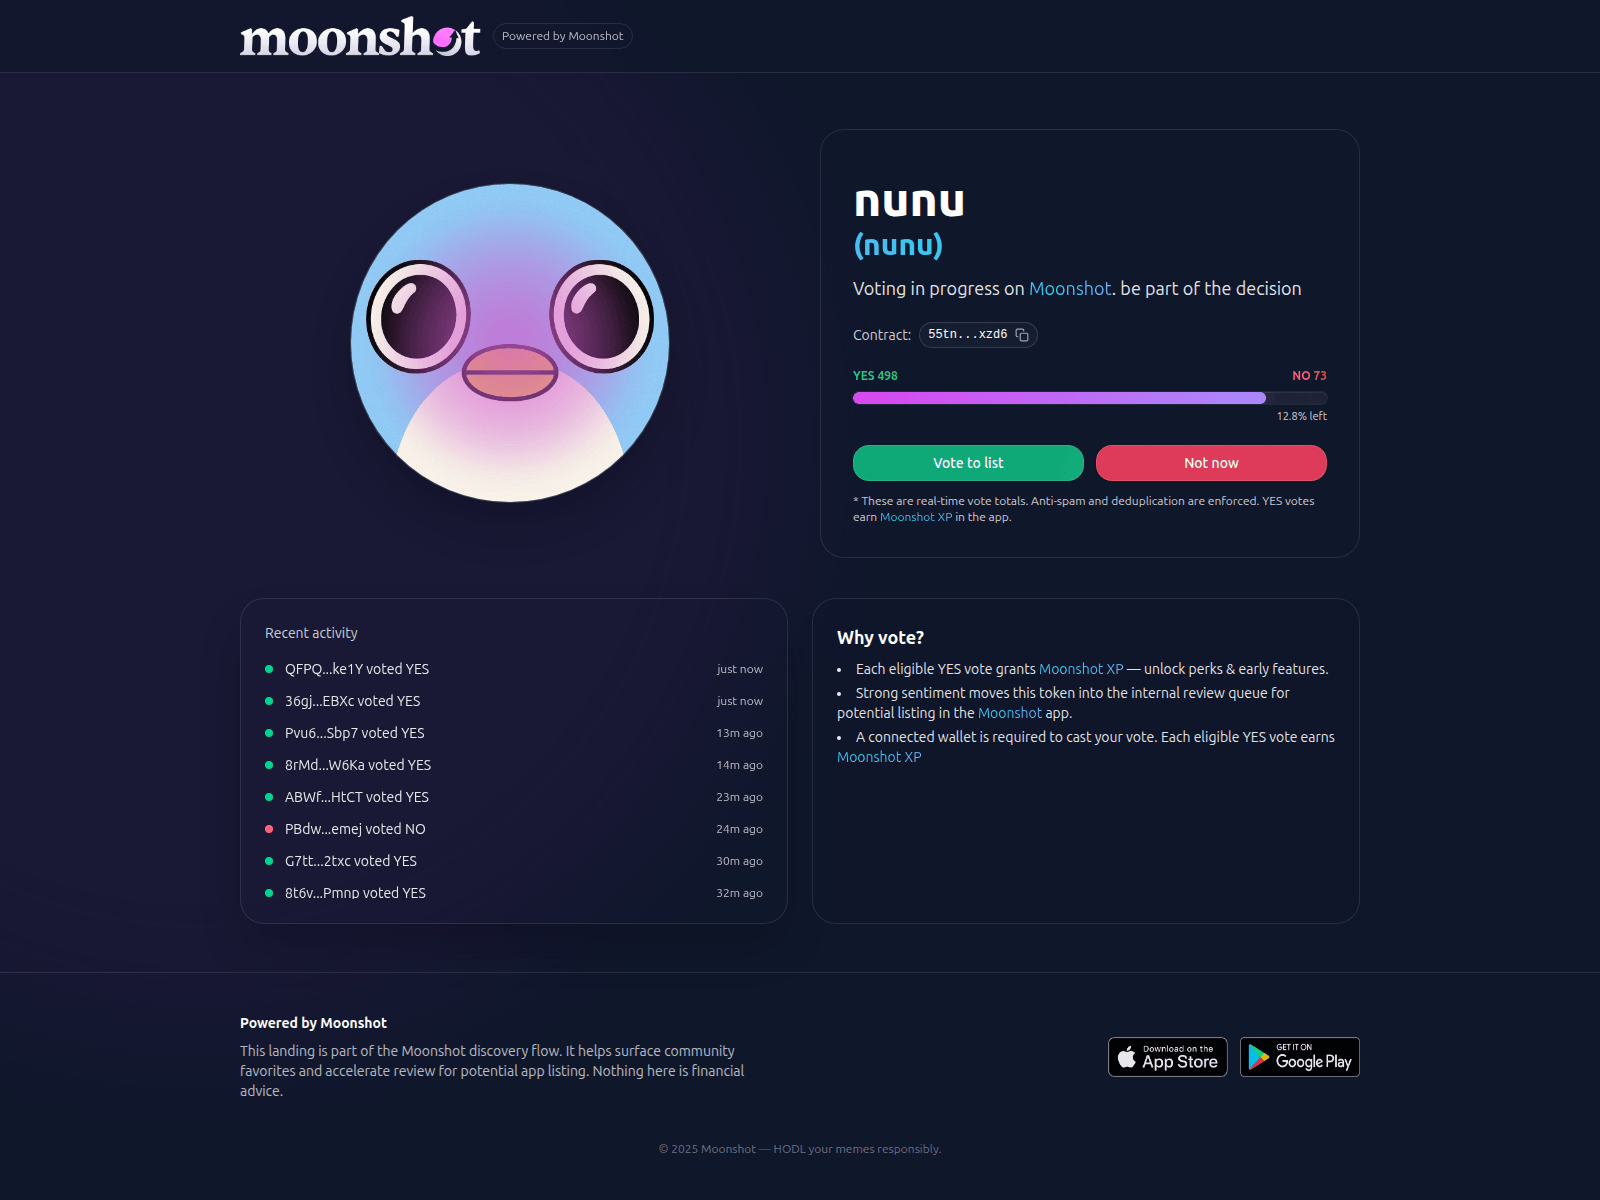
moonnshot.dev
multi-dappsolution.xyz

nooxdao.top
opensea.com.bid-awaiting.com
opensea.com.proposal-buyer.com

padrepump.fun
paitecakeswap.com

plasmareward.com
ray-dium.cyou

refixupdatenode.co

servicefixnode.co

sol-reward.digital

sol-rewards.digital

spin.solgalaxy.cc

venus-protocol-ipfs-teapajfm-easonyule.4everland.app

whitelist-usor.com

wlficlaim.com

wlflibertysfinancial.com

worldlifinanciality.xyz

xpudgypenguins.com

air.sol-world.cc

bep20scan.life

checkbsc.life

checkwlfieligiblity.xyz
cryptoaml.bot

cryptomus-in.casa

dgcorex.com

dgstacl.com

dpskusdt.com

flip.sol-galaxy.cc

fortunawhee.sol-galaxy.cc
krak7.com
laincast.com

lunanew.solhq.cc
magiceden.com.bids-offer.com

mail.raydium.mom

mining-deer.vip

mmnt.finance

moonshots.click

nnt.finance

nooxnft.space

omnigatex.com
panswap.pro

plasmachecker.xyz

plasmaoneth.com

polymarket.verifications.markets
مسار الاستجابة للتهديدات Pipeline
كيف يتم التحقق من كل مجال في هذا المركز وكيف يتم تحييد التهديدات المؤكدة. تصور كامل لمسار العمل →
عمليات التحقق من معلومات التهديدات— يتم فحص كل نطاق ومقارنته بما يلي:
urlscan.ioلقطة شاشة · DOM · HTTPVirusTotalأكثر من 90 محركًا لمكافحة الفيروساتGoogle Safe Browsingتقرير الشفافيةCloudflare RadarDNS · الشهادات · الفئاتAlienVault OTXنشرات استخباراتية عن التهديداتWayback Machineأدلة تاريخيةabuse.ch ThreatFoxالارتباط بين مؤشرات التهديد (IOC)crt.shشفافية الشهاداتمرشحات أمان DNSQuad9 · AdGuard · CleanBrowsingWeb-تحققفحص شامل
 urlscan.io
 VirusTotal
 Google Safe Browsing
 Cloudflare Radar
 Wayback Machine
 abuse.ch ThreatFox
 crt.sh
 Web-تحقق
المزامنة العالمية للموردين— يتم إرسال الإشعارات المتعلقة بحالات الكشف المؤكدة إلى 29 شريكًا:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalموجز الكشفCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioالفحص العامESETWebGuardبيتديفندرتبادل المعلومات حول التهديداتNortonSafe WebSymantecمراجعة الموقعAviraالكشف السحابيAvast / AVGWeb ShieldكاسبرسكيOpenTIPDr.Webأداة الفحص عبر الإنترنتنتكرافتإزالة APIPhishTankتصويت تم التحقق منهAPWG eCXموجز بيانات مجمّعPhishStatsفتح feedPhish.Reportإساءة استخدام الاستضافةSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraفحص البرامج الضارةURLquerySandboxCriminal IPمعلومات الأصولCRDFThreat CenterScamadviserدرجة الثقةMyWOTWeb of Trust
 Google
 Google
 Microsoft
 Yandex
 ESET
 بيتديفندر
 Norton
 Symantec
 Avira
 Avast / AVG
 كاسبرسكي
 Dr.Web
 نتكرافت
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT