VirusTotal
4 / 92 engine detections
打开报告

uat.base.bh.edu.pk:冒充 Base,PhishDestroy 于 2026-10-11 检测到。风险:关键(78/100)。状态:最后已知的活跃状态。托管:GOOGLE-CLOUD-PLATFORM - Google LLC, US。VirusTotal:4/92 个引擎标记。请勿输入登录凭据,也不要连接钱包。
“BSS Timetable”
冒充 Base: uat.base.bh.edu.pk — 最后已知的活跃状态 (HTTP 200). 证据摘要: VirusTotal 4/92 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, SOCRadar); 2 external blocklist…
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
4 / 92 engine detections
打开报告无社区引用
打开报告provider verdict: clean
打开报告无威胁标记
打开报告无恶意标记
打开报告结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。
PhishDestroy threat report
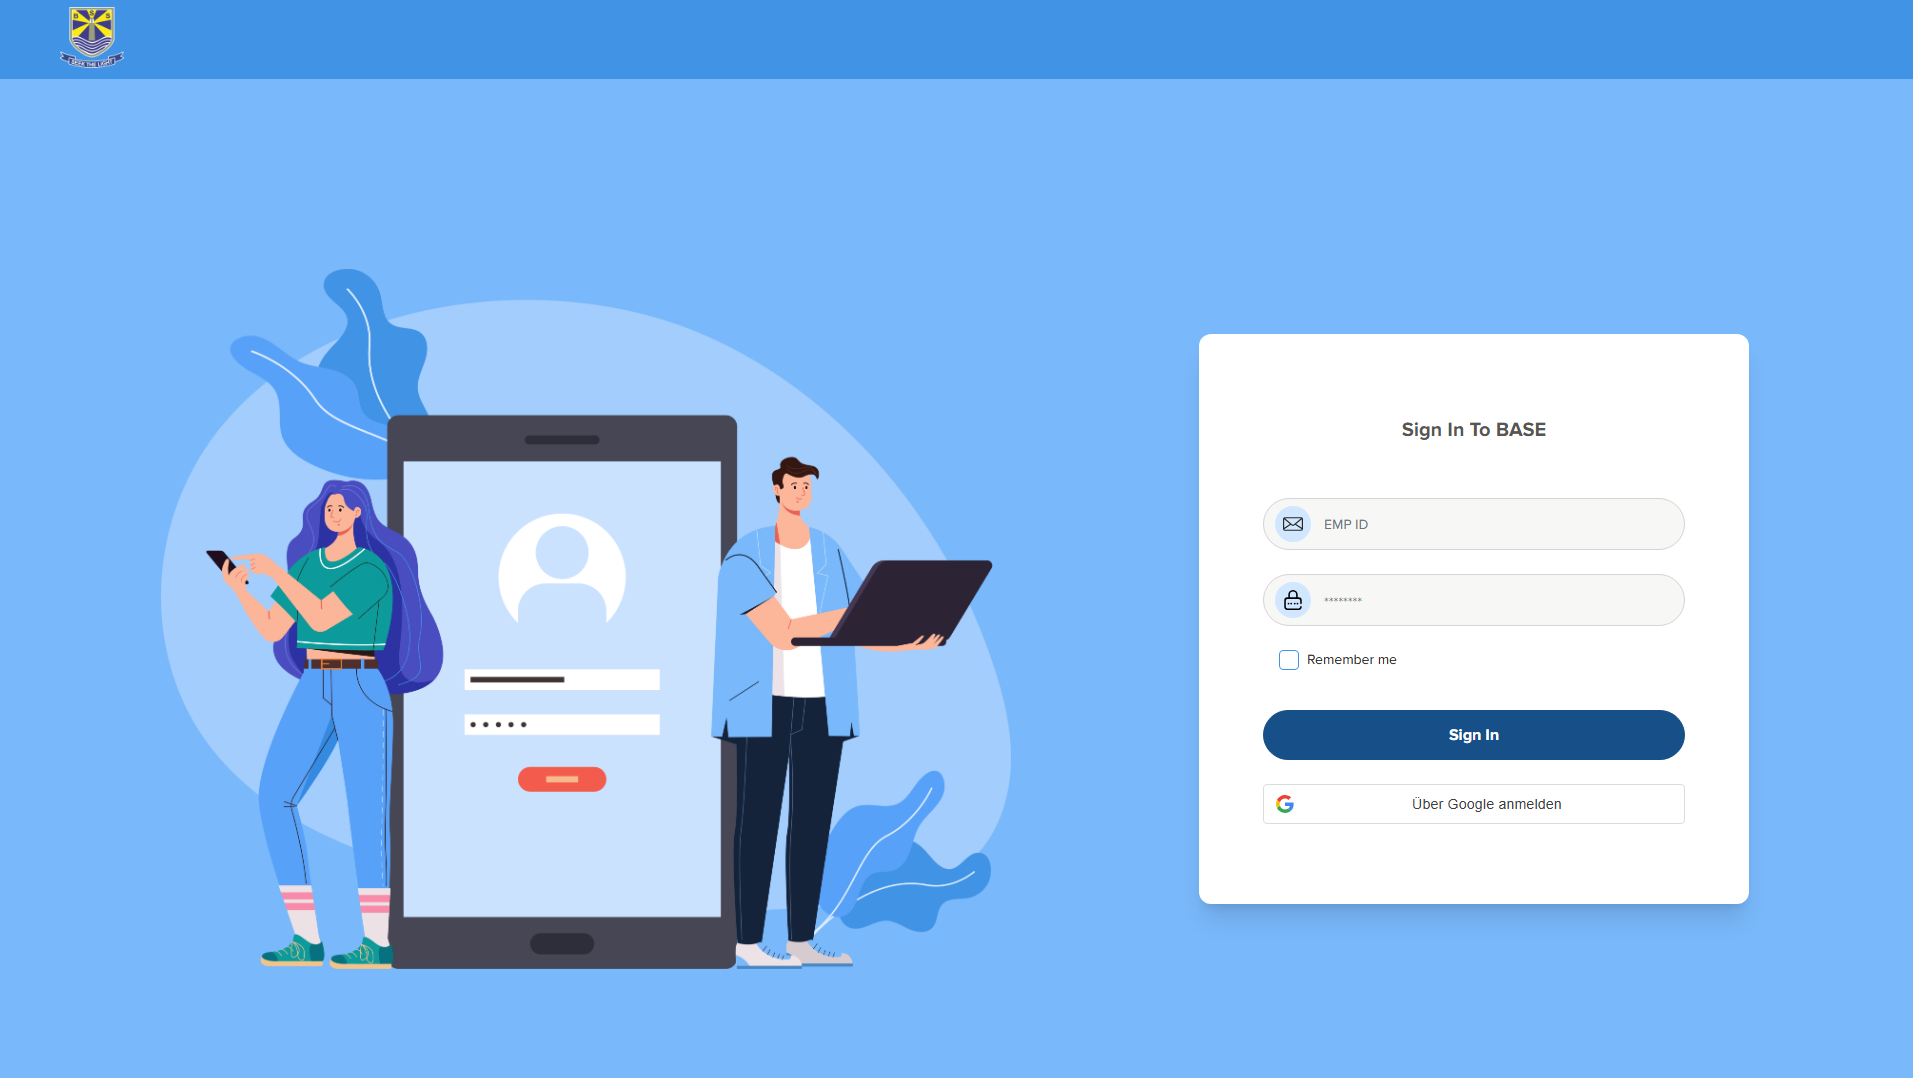
uat.base.bh.edu.pk is a subdomain under a Pakistani educational domain that PhishDestroy classifies as an impersonation phishing page. The page presents itself as "BSS Timetable," a school-scheduling title, while our classification places it among pages that imitate a trusted service to deceive visitors. PhishDestroy first saw it on 2026-10-11, and as of 2026-10-19 the site was still online and serving live content.
Impersonation pages borrow the look or name of something familiar so visitors lower their guard. They then ask for a login, personal details, or, on crypto-focused variants, a wallet connection or signature. Whatever is entered goes to the operator, who can use it to take over accounts or move assets. The title reads "BSS Timetable," a school schedule, while our classification is impersonation phishing.
On 2026-10-16, 4 of 92 VirusTotal engines flagged the site: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker and SOCRadar. That is a low count, but these vendors reached the verdict independently. The stronger signal is the blocklist coverage. Besides PhishDestroy, the site is listed by MetaMask and SEAL, two wallet-security lists, which shows the crypto community regards it as a risk to wallet users.
The parent domain was registered on 2014-03-23, more than twelve years before PhishDestroy detected this subdomain. An old institutional domain carries borrowed trust that a newly registered domain would not have. The site runs on Google Cloud Platform infrastructure, on an address located in Switzerland. It uses a free Let's Encrypt certificate, so the padlock in the browser says nothing about whether the site is legitimate.
If you entered a password here, change it now, along with any account that shares it, and turn on two-factor authentication. If you connected a crypto wallet or signed anything on this page, revoke the permissions you granted with a token-approval checker. Move any remaining funds to a fresh wallet if you exposed a seed phrase. Defenders should block the subdomain at the DNS and proxy level and check logs for visits since 2026-10-11. Report the page to the hosting provider and to the administrators of the parent educational domain so they can secure it.
已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。
观察到: · Retrieved:
| Uuid | 01a12ab7-403a-77d8-a4ec-42a3e487837c |
|---|---|
| Final url | https://uat.base.bh.edu.pk/ |
| 状态 | 200 |
| 已重定向 | https-only |
| Redirects | [
{
"to": "https://uat.base.bh.edu.pk/",
"from": "http://uat.base.bh.edu.pk/",
"status": 307
}
] |
| Ip | 34.65.68.235 |
| Ptr | 235.68.65.34.bc.googleusercontent.com |
| Contacted domains | [
"accounts.google.com",
"cdnjs.cloudflare.com"
] |
| Contacted IP addresses | [
"142.251.127.84",
"104.17.25.14",
"34.65.68.235"
] |
| Asns | [
"15169",
"13335",
"396982"
] |
| Countries | [
"US",
"CH"
] |
| Document hash | ff5bddfaf8937472d3402ffd0437ead25317f543b15d1aaa7a94c06d8a5f0747 |
| Script hashes | [
"015c3bc62fce425cc5d2fdd153205454f568c3de0511ea83af5114df35a40a7a"
] |
| Globals | [
"$",
"jQuery",
"__reactRouterVersion",
"default_gsi",
"_F_toggles_default_gsi",
"google",
"__G_ID_CLIENT__",
"closure_lm_933080"
] |
| Cookies | [
"g_state"
] |
| Storage keys | [
"__sak"
] |
| Tls | {
"san": [
"api.base.bh.edu.pk",
"prototype.base.bh.edu.pk",
"staging.base.bh.edu.pk",
"uat.base.bh.edu.pk"
],
"cipher": "AES_128_GCM",
"issuer": "YR2",
"subject": "api.base.bh.edu.pk",
"protocol": "TLS 1.3",
"valid_to": "2026-12-08T06:08:22Z",
"valid_from": "2026-09-09T06:08:23Z"
} |
| 域名年龄(天) | 937 |
| Apex age days | 2034 |
| Tls age days | 32 |
| TLS 有效天数 | 89 |
| Requests | 16 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": -15,
"malicious": false
},
"overall": {
"score": 0,
"malicious": false
}
} |
| HTTP headers | {
"server": "Apache/2.4.52 (Ubuntu)",
"content-type": "text/html"
} |
观察到: · Retrieved:
| Uuid | 5a3ef46d-ffa0-4244-a5eb-d453d6f5e269 |
|---|---|
| Final url | https://uat.base.bh.edu.pk/ |
| 状态 | 200 |
| History | [
{
"url": "https://uat.base.bh.edu.pk/",
"status": 200
}
] |
| DOM structure hash | c3f52297740dfde188023fc70548662e8eaca9f7685adc5ca3dd51da9724a9b1 |
| Document hash | ff5bddfaf8937472d3402ffd0437ead25317f543b15d1aaa7a94c06d8a5f0747 |
| Radar rank | {
"bucket": ">200000"
} |
| DNS 记录 | [
{
"name": "uat.base.bh.edu.pk",
"type": "A",
"value": "34.65.68.235"
}
] |
| DNSSEC 有效 | false |
| Ip | 34.65.68.235 |
| 注册记录 | {
"created": "2014-03-23T00:00:00Z",
"expires": "2032-03-23T00:00:00Z",
"nameservers": [
"cruz.ns.cloudflare.com",
"nile.ns.cloudflare.com"
]
} |
观察到: · Retrieved:
| Vendor result counts | {
"timeout": 0,
"harmless": 53,
"malicious": 3,
"suspicious": 1,
"undetected": 35
} |
|---|---|
| Vendor labels | {
"CRDF": "malicious",
"SOCRadar": "suspicious",
"alphaMountain.ai": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputation | 0 |
| Categories | {
"Sophos": "educational institutions",
"alphaMountain.ai": "Education, Phishing (alphaMountain.ai)",
"Forcepoint ThreatSeeker": "phishing and other frauds"
} |
| 创建 | 2014-03-23T00:00:00Z |
| 首次发现 | 2024-07-16T15:09:46Z |
| DNS 记录 | [
{
"ttl": 300,
"type": "A",
"value": "34.65.68.235"
}
] |
| Dns at | 2026-10-20T02:00:31Z |
| Jarm | 15d3fd16d29d29d00042d43d000000ad5982e0c23bdf2bdf34e47480ccc0a3 |
| Certificate | {
"san": [
"api.base.bh.edu.pk",
"prototype.base.bh.edu.pk",
"staging.base.bh.edu.pk",
"uat.base.bh.edu.pk"
],
"issuer": "Let's Encrypt / YR2",
"serial": "57f3fc3f7cb836e9a17b19447bb526dee5f",
"sha256": "05632030b3c35c8fd3fa7fc52a7b171fc3ce4ed814ab020edc3f7443c769eee0",
"subject": "api.base.bh.edu.pk",
"valid_to": "2026-12-08T06:08:22Z",
"valid_from": "2026-09-09T06:08:23Z"
} |
| 注册记录 | {
"created": "2014-03-23T00:00:00Z",
"nameservers": [
"cruz.ns.cloudflare.com",
"nile.ns.cloudflare.com"
]
} |
不是。PhishDestroy 将 uat.base.bh.edu.pk 归类为“冒充 Base”(风险:关键,78/100),首次检测于 2026-10-11。VirusTotal:4/92 个引擎标记。请将该网站视为不安全。
不安全。请勿在 uat.base.bh.edu.pk 连接钱包、签署消息或批准代币。钓鱼网站会请求授权(approve、setApprovalForAll、Permit2),让运营者转走你的资产,而已确认的交易无法撤销。
更改你在该网站输入过的所有密码,并开启双重验证。如果你连接过钱包或签署过任何内容,请撤销授权,并将剩余资金转到新钱包;切勿透露助记词。分步指南:紧急处理指南。
最近检查
cruz.ns.cloudflare.comnile.ns.cloudflare.com位置信息描述的是 IP 网络。
05632030b3c35c8fd3fa7fc52a7b171fc3ce4ed814ab020edc3f7443c769eee0api.base.bh.edu.pkprototype.base.bh.edu.pkstaging.base.bh.edu.pk已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。
Google PageSpeed Insights — 移动端性能审核: uat.base.bh.edu.pk · checked Oct 12, 2026
估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。
由监测程序和来源采集器保留的带日期变更记录。最新观测排在最前;来源状态并不能证明站点已被下架。
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
未知→live_content
content_served
可访问
带有相同采集器标签的报告。标签相同并不能证明存在仿冒或同一所有者。 查看匹配的报告 →
比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。
uat.base.bh.edu.pk
列入名单的域名至少会收到一份滥用举报;此条目没有保留的通知记录。
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。
选择您所在的国家/地区以获取 官方网络犯罪联系人 或 创建投诉草稿 →。
Template-based draft · optional AI wording assistance requires separate consent
请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。
停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。
请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 evidence guidance ↗
uat.base.bh.edu.pk)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。
AI 辅助分析的撰写时间: 。该分析描述的是当时可获得的证据;之后的来源核查结果可能有所变化。
快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。