URLQuery
2 det.
未记录
打开报告 

qfsvaultx.org:冒充 Coinbase,PhishDestroy 于 2026-10-25 检测到。风险:关键(73/100)。注册商:TuringSign。状态:最后已知的活跃状态。托管:velia.net Internetdienste GmbH。PhishDestroy 已发送1 份滥用举报。请勿输入登录凭据,也不要连接钱包。
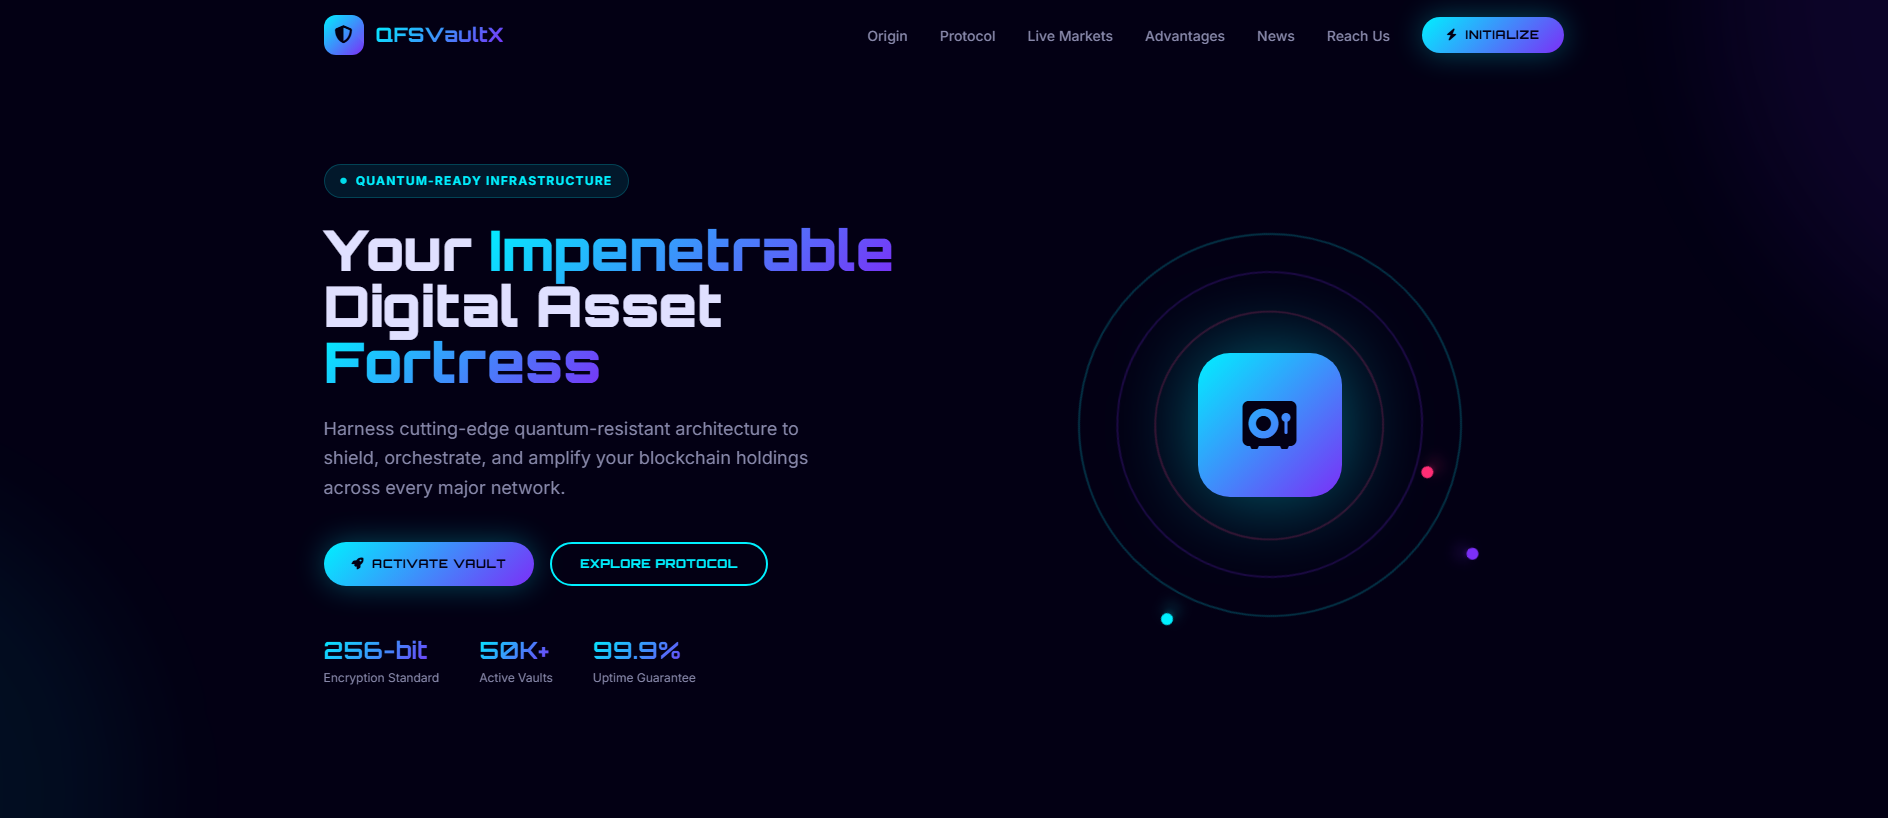
“QFSVaultX — Next-Gen Digital Fortress for Blockchain Holdings”
已发送报告日志记录了首份外发报告的时间为 . The recorded recipient is abuse@velia.net. 最新的存储可用性证据仍显示该域名可访问; 30 hours 自首份外发报告发布以来,已过去……
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
冒充 Coinbase: qfsvaultx.org — 最后已知的活跃状态 (HTTP 302). 证据摘要: VirusTotal 0/92; URLQuery 2 det.; CF Radar malicious; PhishDestroy score 73/100. 注册商: TuringSign.
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
PhishDestroy威胁报告
PhishDestroy’s intake AI classified qfsvaultx.org as malicious with a high phishing confidence based on the page’s claim to be a “Next‑Gen Digital Fortress for Blockchain Holdings” and its request to “Initialize Your Vault” by linking popular crypto wallets. The assessment was recorded on 2026-10-25, the same day the site returned an HTTP 200 response and displayed the quoted excerpt. The domain was first seen by PhishDestroy on 2026-10-25, 237 days after its registration on 2026-03-02.
A crypto‑wallet drainer typically presents a legitimate‑sounding service and prompts visitors to connect their Web3 wallet. When the user approves the connection, the site can request token transfer permissions and move funds without further user interaction. No on‑page evidence of actual transfers was captured, but the request to link MetaMask, Coinbase, Trust Wallet, Crypto.com or Exodus matches this known pattern.
VirusTotal scanned the domain on 2026-10-25 (analysis date 2026-05-02) with 92 engines and reported zero malicious or suspicious detections. Google Safe Browsing checked on 2026-10-25 and did not flag the site. OTX listed four pulses referencing the domain as of 2026-10-25. PhishDestroy’s internal blocklist marks the domain as malicious. urlscan.io captured the site on 2026-10-25, its engine flagged it as malicious with a score of 99 and tags indicating phishing, while its overall verdict was non‑malicious. Cloudflare Radar also flagged the domain for phishing and DGA‑related risk on the same date.
The domain was registered on 2026-03-02 through TuringSign Inc. d/b/a Cosmotown and was 236 days old at first sight. The recorded IP was 85.195.85.58, belonging to ASN 29066 (velia.net Internetdienste GmbH) located in Frankfurt, DE. The TLS certificate, issued by Let’s Encrypt /YR2, was valid from 2026-09-01 to 2026-11-30. Nameservers were ns1.betahostit.com and ns2.betahostit.com (also ns41.dnsiaas.com, ns42.dnsiaas.com).
Visitors should avoid connecting any crypto wallet to qfsvaultx.org; if a connection was already approved, immediately revoke all permissions in the wallet and consider moving assets to a new, secure wallet. Organizations should block the domain at the network perimeter, monitor outbound connections to the recorded IP, and add the domain to internal threat feeds. Users who entered seed phrases or private keys should treat those credentials as compromised and generate new wallets.
2 det.
网络钓鱼
打开报告观测时间: · 检索到:
| Uuid | 8bbe674a-13df-4578-a7f1-47dfccac955f |
|---|---|
| Final url | https://qfsvaultx.org/ |
| 状态 | 200 |
| 历史 | [
{
"url": "https://qfsvaultx.org/",
"status": 200
}
] |
| DOM 结构哈希 | 54a3d7949feaf6fd5f890f1e54a425b1910b98aba0c235a6739ca0970170b06c |
| 文档哈希值 | ab7e9638a854ce745fe937d6668a2aa3ed620bf946a872f9596ee16f60beed78 |
| Phishing v2 | [
"phishing"
] |
| 域名风险 | [
"DGA Domains",
"Security threats",
"CIPA Filter",
"CIPA"
] |
| Radar rank | {
"bucket": ">200000"
} |
| DNS 记录 | [
{
"name": "qfsvaultx.org",
"type": "A",
"value": "85.195.85.58"
}
] |
| DNSSEC 有效 | false |
| Ip | 85.195.85.58 |
| 判定 | {
"tags": [
"dga domains"
],
"malicious": true,
"categories": [
"dga domains"
]
} |
| 注册记录 | {
"registrar": "TuringSign Inc. d/b/a Cosmotown",
"created": "2026-03-02T06:59:06Z",
"updated": "2026-08-12T08:28:39Z",
"expires": "2027-03-02T06:59:06Z",
"nameservers": [
"ns41.dnsiaas.com",
"ns42.dnsiaas.com"
]
} |
恶意 · 引擎判定 · 评分 99
打开报告观测时间: · 检索到:
| Uuid | 01a17105-ca61-7172-bd0e-432669364e37 |
|---|---|
| Final url | https://qfsvaultx.org/ |
| 状态 | 200 |
| Ip | 85.195.85.58 |
| Ptr | de6000-r.iaasdns.com |
| 已联系的域名 | [
"www.youtube.com",
"cdnjs.cloudflare.com",
"fonts.gstatic.com",
"jnn-pa.googleapis.com",
"googleads.g.doubleclick.net",
"cdn.tailwindcss.com",
"i.ytimg.com",
"www.google.com",
"static.doubleclick.net",
"api.coingecko.com",
"fonts.googleapis.com"
] |
| 已联系的 IP 地址 | [
"172.217.115.4",
"209.85.144.119",
"142.251.152.119",
"173.194.175.149",
"173.194.68.154",
"172.66.172.219",
"172.217.222.94",
"142.251.154.4",
"104.17.25.14",
"173.194.175.95",
"104.26.2.143",
"85.195.85.58"
] |
| Asns | [
"15169",
"13335",
"29066"
] |
| Countries | [
"US",
"DE"
] |
| 文档哈希值 | ab7e9638a854ce745fe937d6668a2aa3ed620bf946a872f9596ee16f60beed78 |
| Globals | [
"tailwind",
"/template.html",
"AOS",
"toggleNav",
"closeNav",
"openModal",
"closeModal",
"loadMarketData"
] |
| Cookie | [
"XSRF-TOKEN",
"laravel_session",
"__Secure-YNID",
"YSC",
"__Secure-ROLLOUT_TOKEN",
"VISITOR_INFO1_LIVE",
"VISITOR_PRIVACY_METADATA"
] |
| Tls | {
"san": [
"*.qfsvaultx.org",
"qfsvaultx.org"
],
"cipher": "AES_128_GCM",
"issuer": "YR2",
"subject": "qfsvaultx.org",
"protocol": "TLS 1.3",
"valid_to": "2026-11-30T09:49:06Z",
"valid_from": "2026-09-01T09:49:07Z"
} |
| 域名年龄(天) | 236 |
| Apex age days | 236 |
| Tls age days | 53 |
| TLS 有效天数 | 89 |
| 请求 | 27 |
| 服务提供商评定结果 | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 99,
"malicious": true
},
"overall": {
"score": 0,
"malicious": false
}
} |
| HTTP 头 | {
"server": "LiteSpeed",
"content-type": "text/html; charset=UTF-8",
"x-powered-by": "PHP/8.3.36"
} |
单独存储的监控快照;不会替换主报告记录,也不会确定当前的可用性。
0 / 92 发动机检测 · 存储的摘要
打开报告观测时间: · 检索到:
| 供应商结果计数 | {
"timeout": 0,
"harmless": 57,
"malicious": 0,
"suspicious": 0,
"undetected": 35
} |
|---|---|
| 声誉 | 0 |
| 标签 | [
"dga"
] |
| 创建 | 2026-03-02T00:00:00Z |
| 已更新 | 2026-03-02T00:00:00Z |
| 首次发现 | 2026-03-02T09:18:51Z |
| DNS 记录 | [
{
"ttl": 21600,
"type": "NS",
"value": "ns1.betahostit.com"
},
{
"ttl": 14400,
"type": "TXT",
"value": "v=spf1 +a +mx +ip4:85.195.85.58 include:relay.mailbaby.net ~all"
},
{
"ttl": 21600,
"type": "SOA",
"rname": "biz\\.urdesigner.gmail.com",
"value": "ns1.betahostit.com"
},
{
"ttl": 14400,
"type": "MX",
"value": "qfsvaultx.org",
"priority": 0
},
{
"ttl": 14400,
"type": "A",
"value": "85.195.85.58"
},
{
"ttl": 21600,
"type": "NS",
"value": "ns2.betahostit.com"
}
] |
| Dns at | 2026-05-02T11:36:40Z |
| Jarm | 29d29d00029d29d00042d43d00041d598ac0c1012db967bb1ad0ff2491b3ae |
| 证书 | {
"san": [
"*.qfsvaultx.org",
"qfsvaultx.org"
],
"issuer": "Let's Encrypt / R12",
"serial": "55385ca526654ce8dfbc8154f2d4199c47e",
"sha256": "63b77d8b778612de8bd437a37b1e22699afdda14b33dafbded0362e03986f550",
"subject": "qfsvaultx.org",
"valid_to": "2026-07-31T09:48:23Z",
"valid_from": "2026-05-02T09:48:24Z"
} |
| 注册表数据 | {
"status": [
"client delete prohibited",
"client renew prohibited",
"client transfer prohibited",
"client update prohibited"
],
"events": {
"last changed": "2026-03-02T07:10:00Z",
"registration": "2026-03-02T06:59:06Z",
"registrar expiration": "2027-03-02T06:59:06Z",
"last update of RDAP database": "2026-05-02T11:36:40Z"
},
"registrar": "Cosmotown, Inc.",
"registrar_iana_id": "1509"
} |
上述摘要和此服务提供商记录是在不同时间收集的。两者均仍可查阅;恶意和可疑的分类结果分别显示。
4 community references
打开报告无威胁标记
打开报告已登记;未保留判决结果
打开报告73 / 100 · 启发式得分 · 8 brand references · 1 classifications
打开报告此过时的监控分析与上文的主要PhishDestroy分析是分开的。启发式评分并非经过测量的概率。
叙事生成元数据
打开报告叙述生成日期与观测日期不同。这些是保留的出版字段,并非额外的独立检测结果。
结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。
已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。
| 邮件配置 | {
"mx": [
"qfsvaultx.org"
],
"spf": "v=spf1 +a +mx +ip4:85.195.85.58 include:relay.mailbaby.net ~all",
"dkim": [
"default"
],
"dmarc": true,
"dkim_bits": 2048,
"spf_lookups": 5
} |
|---|---|
| CAA 记录 | {
"domain": "qfsvaultx.org"
} |
| DNS防护结果 | {
"resolvers": 12,
"blocked_count": 0
} |
| 网络档案观察 | {
"last": "2026-10-25T03:08:24Z",
"first": "2026-10-25T03:08:24Z",
"changes": 0,
"days_archived": 1,
"avg_page_bytes": 10629
} |
| 页面标题与元数据 | {
"title": "QFSVaultX — Next-Gen Digital Fortress for Blockchain Holdings",
"description": "Military-grade quantum protection for your decentralized portfolio."
} |
| 表单与混合内容 | {
"no_sri": [
"https://cdn.tailwindcss.com/",
"https://cdnjs.cloudflare.com/ajax/libs/aos/2.3.4/aos.js"
],
"third_party_scripts": 2
} |
| 状态 | {
"up": true,
"code": 200,
"timings": {
"dns": 5,
"tls": 10,
"wait": 548,
"connect": 6,
"download": 6
},
"response_ms": 575
} |
| TLS连接 | {
"alpn": "h2",
"cipher": "TLS_AES_256_GCM_SHA384",
"protocol": "TLSv1.3",
"versions": [
"TLSv1.2",
"TLSv1.3"
],
"authorized": true,
"forward_secrecy": true
} |
| 端口 | {
"open": [
21,
25,
53,
80,
110,
143,
443,
587,
993,
995,
3306
]
} |
| Carbon | {
"bytes": 43431,
"co2_grams": 0.0016,
"cleaner_than": 40
} |
| DNS服务器 | {
"ns": [
{
"host": "ns2.betahostit.com"
},
{
"host": "ns1.betahostit.com"
}
],
"zone": "qfsvaultx.org"
} |
| 位置 | {
"ip": "85.195.85.58",
"asn": "29066",
"org": "velia.net Internetdienste GmbH",
"city": "Frankfurt am Main",
"country": "DE"
} |
| SSL | {
"issuer": "Let's Encrypt / YR2",
"subject": "qfsvaultx.org"
} |
| DNS 记录 | {
"A": [
"85.195.85.58"
],
"MX": [
"{\"exchange\": \"qfsvaultx.org\", \"priority\": 0}"
],
"NS": [
"ns2.betahostit.com",
"ns1.betahostit.com"
],
"SOA": "{\"nsname\": \"ns1.betahostit.com\", \"hostmaster\": \"biz\\\\.urdesigner.gmail.com\", \"serial\": 2026090101, \"refresh\": 3600, \"retry\": 1800, \"expire\": 1209600, \"minttl\": 86400}",
"TXT": [
"v=spf1 +a +mx +ip4:85.195.85.58 include:relay.mailbaby.net ~all"
]
} |
| DNSsec | {
"ds": false,
"rrsig": false,
"dnskey": false
} |
| Hsts | {
"message": "Site does not serve any HSTS headers."
} |
| HTTP 安全策略 | {
"xFrameOptions": false,
"referrerPolicy": false,
"xXSSProtection": false,
"permissionsPolicy": false,
"xContentTypeOptions": false,
"contentSecurityPolicy": false,
"strictTransportPolicy": false,
"crossOriginOpenerPolicy": false,
"crossOriginEmbedderPolicy": false,
"crossOriginResourcePolicy": false
} |
| Get ip | {
"ip": "85.195.85.58",
"family": 4
} |
| 重定向 | {
"chain": [
"https://qfsvaultx.org"
]
} |
| 页面链接 | {
"internal_count": 8
} |
| 注册记录 | {
"registrar": "TuringSign Inc. d/b/a Cosmotown",
"created": "2026-03-02T06:59:06Z",
"updated": "2026-08-12T08:28:39Z",
"expires": "2027-03-02T06:59:06Z",
"status": [
"clientDeleteProhibited https://icann.org/epp",
"clientRenewProhibited https://icann.org/epp",
"clientTransferProhibited https://icann.org/epp",
"clientUpdateProhibited https://icann.org/epp"
],
"nameservers": [
"ns41.dnsiaas.com",
"ns42.dnsiaas.com"
]
} |
| HTTP 头 | {
"headers": {
"server": "LiteSpeed",
"content-type": "text/html; charset=UTF-8",
"x-powered-by": "PHP/8.3.36"
}
} |
 Cloudflare Radar Verdict 恶意
不是。PhishDestroy 将 qfsvaultx.org 归类为“冒充 Coinbase”(风险:关键,73/100),首次检测于 2026-10-25。请将该网站视为不安全。
不安全。请勿在 qfsvaultx.org 连接钱包、签署消息或批准代币。钓鱼网站会请求授权(approve、setApprovalForAll、Permit2),让运营者转走你的资产,而已确认的交易无法撤销。
更改你在该网站输入过的所有密码,并开启双重验证。如果你连接过钱包或签署过任何内容,请撤销授权,并将剩余资金转到新钱包;切勿透露助记词。分步指南:紧急处理指南。
cc4af6b506ad9df4a2278bec31dad8eda08545ad67fb4a3647accbcd600592ca · 100931 bytes 56f8aedbe1d86b81fff36c121c67974672c4d2be02f465dd5924369d1a9d37de · 153669 bytes d1436cbb28c391be2c8b9f225af10deaacc0b6792ec4aaa99b31a278a4cc4765 · 63957 bytes  (US)
ns1.betahostit.comns2.betahostit.comns41.dnsiaas.comns42.dnsiaas.comqfsvaultx.orgpriority 0位置信息描述的是 IP 网络。
63b77d8b778612de8bd437a37b1e22699afdda14b33dafbded0362e03986f550*.qfsvaultx.orgqfsvaultx.org已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。
最近一次检查时,该网站正在将访问者重定向到其他地址。
PHP is a general-purpose scripting language used for web development.
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
Google PageSpeed Insights — 移动端性能审核: qfsvaultx.org · checked Oct 25, 2026
由本地采集流程保留的带时间戳的响应元数据。以下各项数值均对应所显示的存档时间。
https://qfsvaultx.org/X-Powered-By: PHP/8.3.36Content-Type: text/html; charset=UTF-8Cache-Control: no-cache, privateContent-Encoding: gzip服务器: LiteSpeedh3=":443"; ma=2592000, h3-29=":443"; ma=2592000no-cache, privateKeep-Alivegzip9696text/html; charset=UTF-8Sun, 25 Oct 2026 03:08:39 GMTtimeout=5, max=100LiteSpeedAccept-EncodingPHP/8.3.36由采集器保留的数值;较长的值可能在采集时被截短。
估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。
比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。
redirect: raw=redirect_302; http=302; via=https_proxy; location=https://qfsvaultx.org/cgi-sys/suspendedpage.cgi; server=LiteSpeed
qfsvaultx.org 由监测程序和来源采集器保留的带日期变更记录。最新观测排在最前;来源状态并不能证明站点已被下架。
live_content→redirected
http_redirect
未知→live_content
content_served
可访问
来源:可用性监控器。每条保留的观测记录均保持独立,包括那些日期或证据哈希相同、但来源或DNS状态不同的记录。状态为“未知”并不意味着该网站已离线。
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL analysis↗
 CloudflareRadar / abuse reporting↗ YandexSafe Browsing↗
 URLScan.ioPublic scan↗
 ESETSample / URL submission↗
 BitdefenderURL submission↗
 NortonSafe Web↗
 Symantec网站评审↗
 AviraURL reporting↗
 Avast / AVGURL reporting↗
 卡巴斯基OpenTIP↗
 Dr.WebOnline scanner↗
 NetcraftAbuse reporting↗
 PhishTankCommunity reporting↗
 APWG eCXPhishing intelligence↗
 PhishStatsPublic feed↗
 Phish.ReportHosting abuse↗
 SpamhausDomain reputation↗
 PolySwarmMulti-engine analysis↗
 CheckPhishURL scan↗
 QutteraMalware scan↗
 URLqueryBrowser analysis↗
 Criminal IPAsset intelligence↗ CRDFThreat Center↗
 ScamadviserReputation check↗
 MyWOTCommunity reputation↗
已存储 255 个仿冒域名
显示 255 个中的 100 个
相同网站图标 直接链接 4
相同 IP 85.195.85.58 辅助信号 2
品牌标签:Coinbase 辅助信号 8
注册商:TuringSign 仅限探索 6
每条路径都代表一个将域名与该主机关联的原因。实心节点表示已检测到VirusTotal,虚线节点表示已离线。完整列表如下。 相关报告完整列表
与该主机的网站图标哈希值相同,或页面标题相同。
带有相同采集器标签的报告。标签相同并不能证明存在仿冒或同一所有者。 查看匹配的报告 →
通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。
最近添加了来自 PhishDestroy 数据库的报告。这些发现链接并不意味着共享基础设施或所有权。
PD-20261025-A75089 收件人: abuse@velia.net AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (US): 18 U.S.C. § 1343 - Wire Fraud 18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA) 15 U.S.C. § 45 - FTC Act (Deceptive Practices) Federal laws prohibit wire fraud, computer fraud, and deceptive business practices. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。

IC3 does not accept attachments. Keep original evidence for investigators. IC3 guidance
联邦举报热线1-800-CALL-FBI

Current service: 举报欺诈. England, Wales and Northern Ireland. Scotland: 101.
联络中心0300 123 2040请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。
停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。
请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 证据指南 ↗
qfsvaultx.org)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。
使用存储的阻止列表、WHOIS、DNS 和公共扫描证据进行威胁分析
立即扫描将可疑域名提交至我们的威胁数据库——保护社区
报告最近的网络钓鱼报告和观察到的可用性变化
监控本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。
AI 辅助分析的撰写时间: . 该内容描述了当时可获得的证据;后续的来源核查可能会导致情况发生变化。
快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。