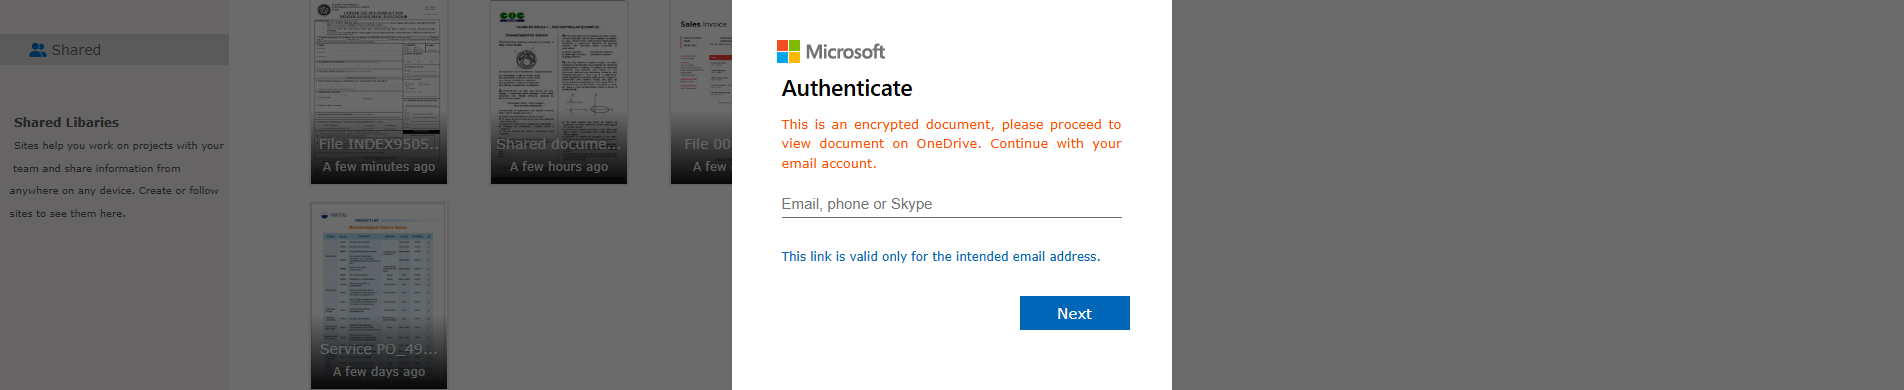
URLScan
恶意
打开报告

newww-sooty.vercel.app:冒充 Onedrive,PhishDestroy 于 2026-10-22 检测到。风险:高(68/100)。注册商:Vercel。状态:最后已知的活跃状态。托管:AMAZON-02 - Amazon.com, Inc., US。请勿输入登录凭据,也不要连接钱包。
“My Files - OneDrive”
冒充 Onedrive: newww-sooty.vercel.app — 最后已知的活跃状态 (HTTP 200). 证据摘要: URLScan malicious verdict; PhishDestroy score 68/100. 注册商: Vercel.
The evidence summary below uses retained observations. Each source keeps its own collection date.
结果反映各来源的采集时间。零检出不代表安全。OTX 引用为社区发布的内容。
已存档的页面、网络和扫描器观测结果,按来源和观测时间分组。
观察到: · Retrieved:
| Uuid | 01a16516-8018-777a-99d7-c8fc8e6a9709 |
|---|---|
| Final url | https://newww-sooty.vercel.app/ |
| 状态 | 200 |
| 已重定向 | https-only |
| Redirects | [
{
"to": "https://newww-sooty.vercel.app/",
"from": "http://newww-sooty.vercel.app/",
"status": 307
}
] |
| Ip | 64.29.17.131 |
| Contacted domains | [
"cdnjs.cloudflare.com",
"aadcdn.msauth.net",
"cdn.jsdelivr.net",
"stackpath.bootstrapcdn.com",
"ajax.googleapis.com",
"maxcdn.bootstrapcdn.com",
"code.jquery.com",
"www.w3schools.com",
"logincdn.msauth.net"
] |
| Contacted IP addresses | [
"104.17.208.5",
"172.217.25.170",
"104.18.11.207",
"151.101.129.155",
"13.107.246.31",
"104.17.24.14",
"104.99.59.17",
"64.29.17.131"
] |
| Asns | [
"13335",
"15169",
"54113",
"8075",
"20940",
"16509"
] |
| Countries | [
"US",
"AU"
] |
| Document hash | 28941f1a7101fc6bd6fa59db35e066481d2c5dcb465ac8f94ff179ab596e480b |
| Globals | [
"email_var",
"bodyDIV",
"ValidateEmail",
"redirrectPage",
"counter",
"backArrow",
"onChangeFunction",
"dd",
"tt",
"$",
"jQuery",
"Popper",
"bootstrap",
"ur",
"arrow",
"emailBlock",
"passwordBlock",
"nextButton",
"signinButton",
"emailInvalid",
"passwordError",
"passwordNull",
"passwordImput",
"emailImput",
"loaderBox",
"loaderBox2",
"bodyBlock",
"overlayBlock",
"loginBlock",
"spinerBlock",
"password_text",
"rbox",
"s_lll1",
"r_lll",
"idPresentPasswordpage",
"defaultSwitch",
"createUser",
"loaderWait",
"loaderWait2",
"next"
] |
| Cookies | [
"__session:0.7147603716924392:"
] |
| Tls | {
"san": [
"*.vercel.app"
],
"cipher": "AES_128_GCM",
"issuer": "WR1",
"subject": "*.vercel.app",
"protocol": "TLS 1.3",
"valid_to": "2026-11-27T19:48:08Z",
"valid_from": "2026-08-29T19:48:09Z"
} |
| 域名年龄(天) | 43 |
| Apex age days | 43 |
| Tls age days | 53 |
| TLS 有效天数 | 89 |
| Requests | 18 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 100,
"malicious": true
},
"overall": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"microsoft",
"genericemail"
],
"malicious": true,
"categories": [
"phishing"
]
},
"urlscan": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"Microsoft",
"Generic Email"
],
"malicious": true,
"categories": [
"phishing"
]
}
} |
| HTTP headers | {
"server": "Vercel",
"content-type": "text/html; charset=utf-8",
"strict-transport-security": "max-age=63072000; includeSubDomains; preload"
} |
观察到: · Retrieved:
| Vendor result counts | {
"timeout": 0,
"harmless": 40,
"malicious": 24,
"suspicious": 1,
"undetected": 27
} |
|---|---|
| Vendor labels | {
"DNS8": "suspicious",
"ESET": "phishing",
"Ermes": "phishing",
"VIPRE": "malware",
"G-Data": "phishing",
"Lionic": "phishing",
"Sophos": "phishing",
"CyRadar": "phishing",
"Webroot": "malicious",
"Emsisoft": "phishing",
"Fortinet": "phishing",
"Netcraft": "malicious",
"SOCRadar": "phishing",
"URLQuery": "malicious",
"Kaspersky": "phishing",
"LevelBlue": "phishing",
"Gridinsoft": "phishing",
"MalwareURL": "phishing",
"SafeToOpen": "phishing",
"BitDefender": "phishing",
"Criminal IP": "phishing",
"SCUMWARE.org": "malicious",
"alphaMountain.ai": "phishing",
"Google Safe Browsing": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputation | 0 |
| 注册商 | Tucows Domains Inc |
| 创建 | 2020-01-28T03:03:04Z |
| Expires | 2026-01-28T03:03:04Z |
| Updated | 2025-01-26T03:25:55Z |
| 首次发现 | 2026-09-09T06:28:33Z |
| DNS 记录 | [
{
"ttl": 300,
"type": "A",
"value": "64.29.17.3"
},
{
"ttl": 300,
"type": "A",
"value": "216.198.79.3"
}
] |
| Dns at | 2026-10-19T10:49:24Z |
| Jarm | 3fd3fd00000000000043d43d00043dc3b2afa8a5ec09b510a8559aff7899fb |
| Certificate | {
"san": [
"*.vercel.app"
],
"issuer": "Google Trust Services / WR1",
"serial": "f7911168ffa7d0f4135e24792e7a52a8",
"sha256": "8f46c4a0a289bfde4060d06986f2af761ee62d668dde972e6bef4687ee4f6093",
"subject": "*.vercel.app",
"valid_to": "2026-11-27T19:48:08Z",
"valid_from": "2026-08-29T19:48:09Z"
} |
| 注册记录 | {
"registrar": "Tucows Domains Inc",
"registrar_iana_id": "69",
"registrar_url": "http://www.tucows.com",
"created": "2020-01-28T03:03:04Z",
"updated": "2025-01-26T03:25:55Z",
"expires": "2026-01-28T03:03:04Z",
"status": [
"clientTransferProhibited",
"clientUpdateProhibited"
],
"nameservers": [
"ns1.vercel-dns-3.com",
"ns2.vercel-dns-3.com",
"ns3.vercel-dns-3.com",
"ns4.vercel-dns-3.com"
],
"dnssec": "unsigned"
} |
不是。PhishDestroy 将 newww-sooty.vercel.app 归类为“冒充 Onedrive”(风险:高,68/100),首次检测于 2026-10-22。请将该网站视为不安全。
不安全。请勿在 newww-sooty.vercel.app 连接钱包、签署消息或批准代币。钓鱼网站会请求授权(approve、setApprovalForAll、Permit2),让运营者转走你的资产,而已确认的交易无法撤销。
更改你在该网站输入过的所有密码,并开启双重验证。如果你连接过钱包或签署过任何内容,请撤销授权,并将剩余资金转到新钱包;切勿透露助记词。分步指南:紧急处理指南。
 (US)
Edge-IP 声誉不属于此域。
位置信息描述的是 IP 网络。
8f46c4a0a289bfde4060d06986f2af761ee62d668dde972e6bef4687ee4f6093*.vercel.app已保存的证书元数据。未带时区的证书日期按存档原样显示。传输加密并不能证明该网站值得信任。
估算时间描述的是一个观测时间窗口。它并不能证明注册商采取了措施,也不代表网站变为不可访问的确切时刻。
由监测程序和来源采集器保留的带日期变更记录。最新观测排在最前;来源状态并不能证明站点已被下架。
可访问
每条路径都代表一个将域名与该主机关联的原因。实心节点表示已检测到VirusTotal,虚线节点表示已离线。完整列表如下。
与该主机的网站图标哈希值相同,或页面标题相同。
这些报告解析为相同的共享边缘 IP。它们有助于报告发现,但并不意味着共同所有权或共享源服务器。
带有相同采集器标签的报告。标签相同并不能证明存在仿冒或同一所有者。 查看匹配的报告 →
通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。
比较浏览器与爬虫各自收到的内容,并检查是否存在 Keitaro 流量分发。
newww-sooty.vercel.app
列入名单的域名至少会收到一份滥用举报;此条目没有保留的通知记录。
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。
选择您所在的国家/地区以获取 官方网络犯罪联系人 或 创建投诉草稿 →。
Template-based draft · optional AI wording assistance requires separate consent
请根据您提供过的信息选择相应的步骤。请将本报告的副本与您自己的记录一并保存。
停止使用可疑网站。请通过官方应用或您已信任的网址访问真正的服务。
请将原始邮件、收据、消息和截图保存在安全的地方。基于事实的时间线有助于受理机构了解事件经过。 IC3 evidence guidance ↗
newww-sooty.vercel.app)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
举报并不能保证追回损失或启动调查,但及时、准确的交易数据可以帮助执法机构和服务提供商追踪事件。
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
本报告汇总了已保存的页面快照、注册与网络记录、扫描器结果以及 PhishDestroy 举报历史。每个来源均保留各自的观测日期。打开来源报告即可查看原始结果。
快照记录的是当时显示的内容。扫描器结果记录的是该服务商在检查时的评估。有效证书或零检出结果都不能保证安全。