VirusTotal
2 / 92 engine detections
打开报告

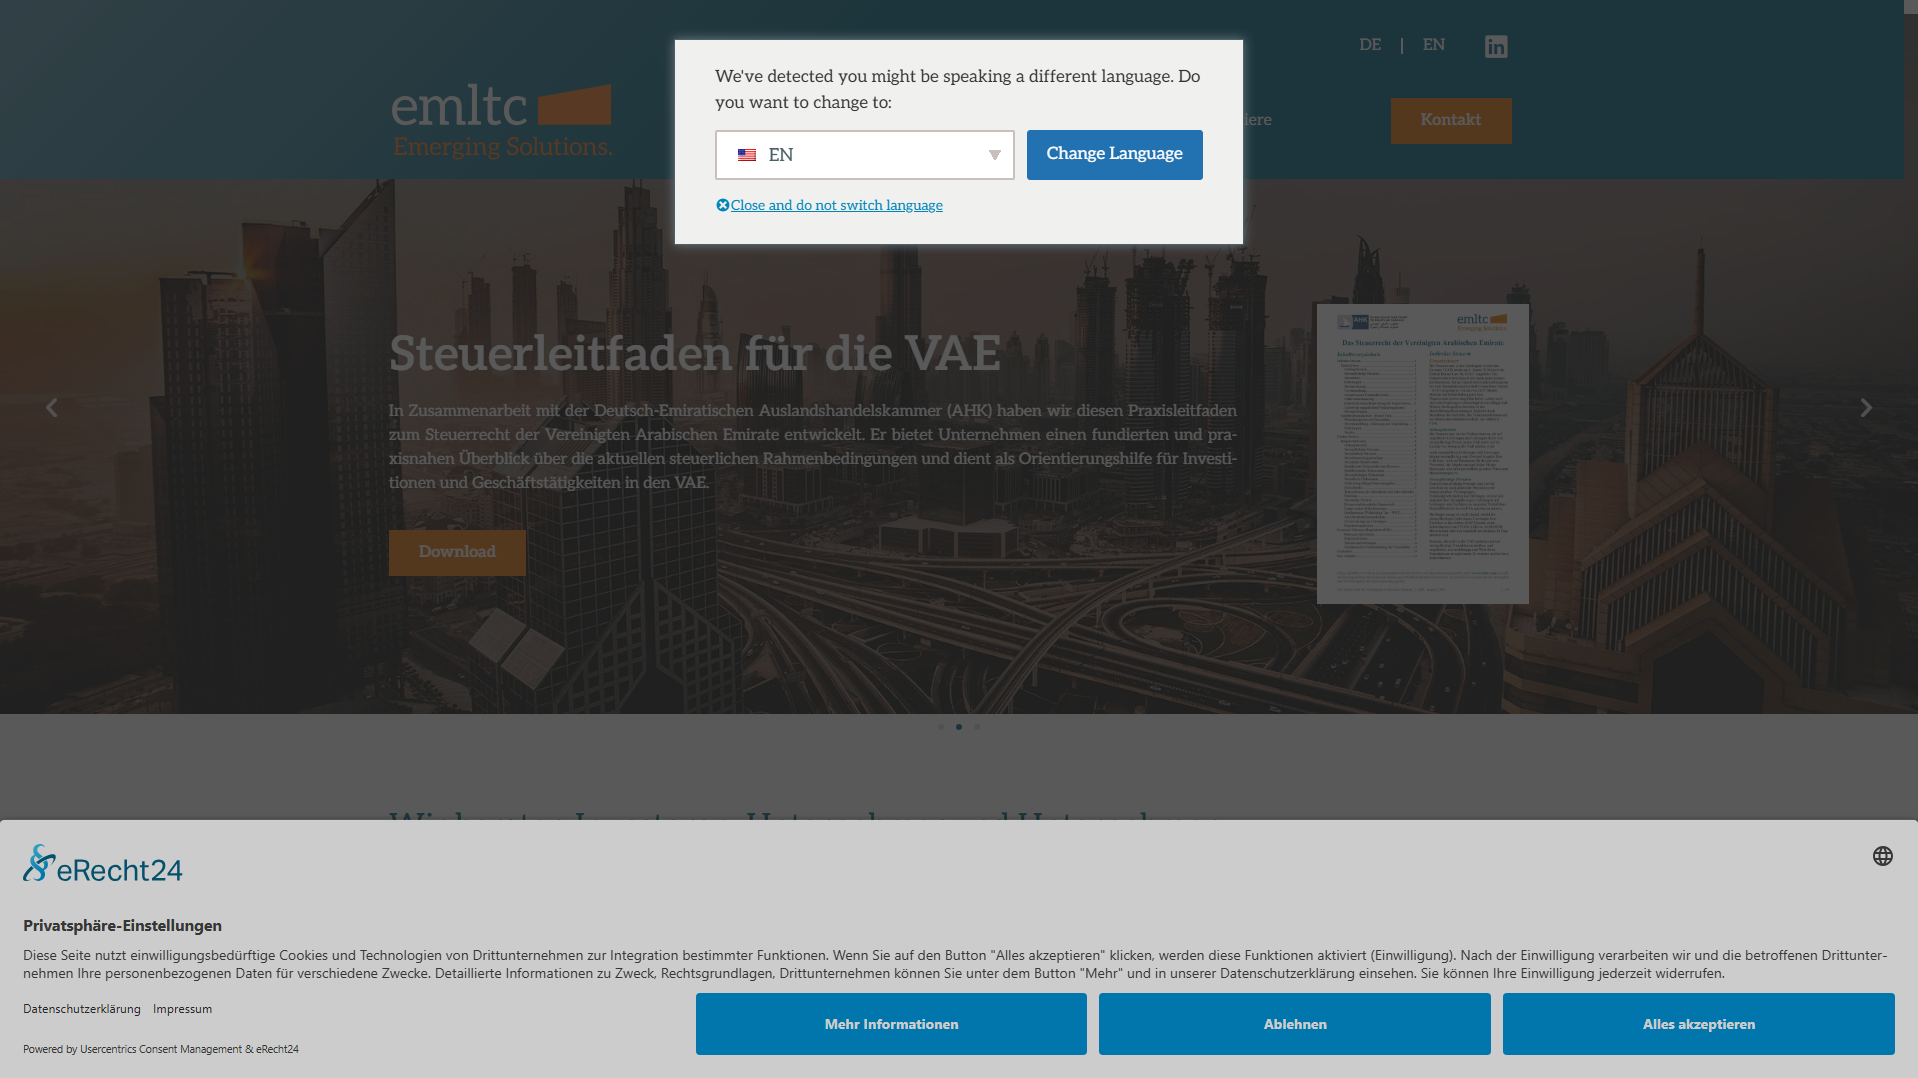
“Startseite - emltc - Legal. Tax. Compliance.”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@name.com.
The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
被列入黑名单的域名: emltc.com — 最后已知的活跃状态 (HTTP 202). 证据摘要: VirusTotal 2/92 (Forcepoint ThreatSeeker, SOCRadar); PhishDestroy score 81/100. 注册商: Name.com.
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
2 / 92 engine detections
打开报告Scan report
打开报告34 community references
打开报告provider verdict: clean
打开报告No threat flag
打开报告No malicious flag
打开报告Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
PhishDestroy lists emltc.com as an impersonation phishing page. The site presents itself as a legal, tax and compliance practice with a German-language homepage, and it targets visitors who think they have reached a legitimate advisory firm. We first flagged the domain on 2026-10-16, and on 2026-10-19 it was still online and serving content.
The page title, "Startseite - emltc - Legal. Tax. Compliance.", looks like an ordinary professional services homepage, while PhishDestroy has classified the site as impersonation. Schemes of this type copy the look and authority of a trusted firm so visitors lower their guard. Victims are typically pushed to hand over contact details, identity documents, account logins or payments for supposed fees and filings. Legal and tax branding is attractive to fraudsters because clients expect to share sensitive personal and financial information with such firms.
Independent coverage is limited. On 2026-10-16, VirusTotal showed 2 of 92 engines flagging the domain, namely Forcepoint ThreatSeeker and SOCRadar. The domain also appears in 34 AlienVault OTX pulses, and PhishDestroy carries it on its own blocklist. A low detection count does not mean the site is safe, because new impersonation pages often reach security feeds late.
The domain was registered on 2022-01-18 through Name.com, Inc. It resolves to 35.209.116.220 on a Google network attributed to Google Ireland Limited and geolocated in the US. Traffic is encrypted with a Let's Encrypt (YR1) certificate. The padlock confirms only that the connection is encrypted and says nothing about who runs the site.
Do not enter details, upload documents or send payments on emltc.com. If you typed a password there, change it on every account that shares it and turn on two-factor authentication. If you supplied ID scans or banking information, contact your bank and watch for fraud or identity misuse. Reach any firm you meant to contact only through channels you have verified yourself. Defenders should block the domain and its IP at DNS and proxy level, check logs for past visits, and file abuse reports with the registrar and hosting provider.
 (US)
ns1hwy.name.comns2cqs.name.comns3gmt.name.comns4sxy.name.comemltc-com.mail.protection.outlook.compriority 0Location describes the IP network.
9fbb609443d2ba208fec7269d36d5da2ee2261d667757eae9b612e7d60d5d5d9www.emltc.comSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.
www.emltc.comDomain recordThe original observation time is not recorded for these hostnames.
Google PageSpeed Insights — mobile performance audit of emltc.com · checked Oct 16, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
未知→protected
http_access_restricted · access_restriction
protected→live_content
content_served
未知→protected
http_access_restricted · access_restriction
live_content→protected
http_access_restricted · access_restriction
未知→live_content
content_served
live_content→protected
http_access_restricted · access_restriction
protected→live_content
content_served
未知→protected
http_access_restricted · access_restriction
0→2
可访问
No threat flag
View source2/92 engine detections
View source34 community references
View sourcePD-20261016-88EA3F
emltc.com
View sourcePage captured
View source通过同一家注册商注册。一家注册商通常为数百万互不相关的客户提供服务,因此这仅表明数据归属同一群体,而非证明存在关联。
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
emltc.com
PD-20261016-88EA3F Recipient: abuse@name.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (US): 18 U.S.C. § 1343 - Wire Fraud 18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA) 15 U.S.C. § 45 - FTC Act (Deceptive Practices) Federal laws prohibit wire fraud, computer fraud, and deceptive business practices. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。
选择您所在的国家/地区以获取 官方网络犯罪联系人 或 创建投诉草稿 →。
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
emltc.com)即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.