
搜索受监控的域名,并查看存储的证据、检测结果以及最新观察到的可用性情况。

How This Attack Works
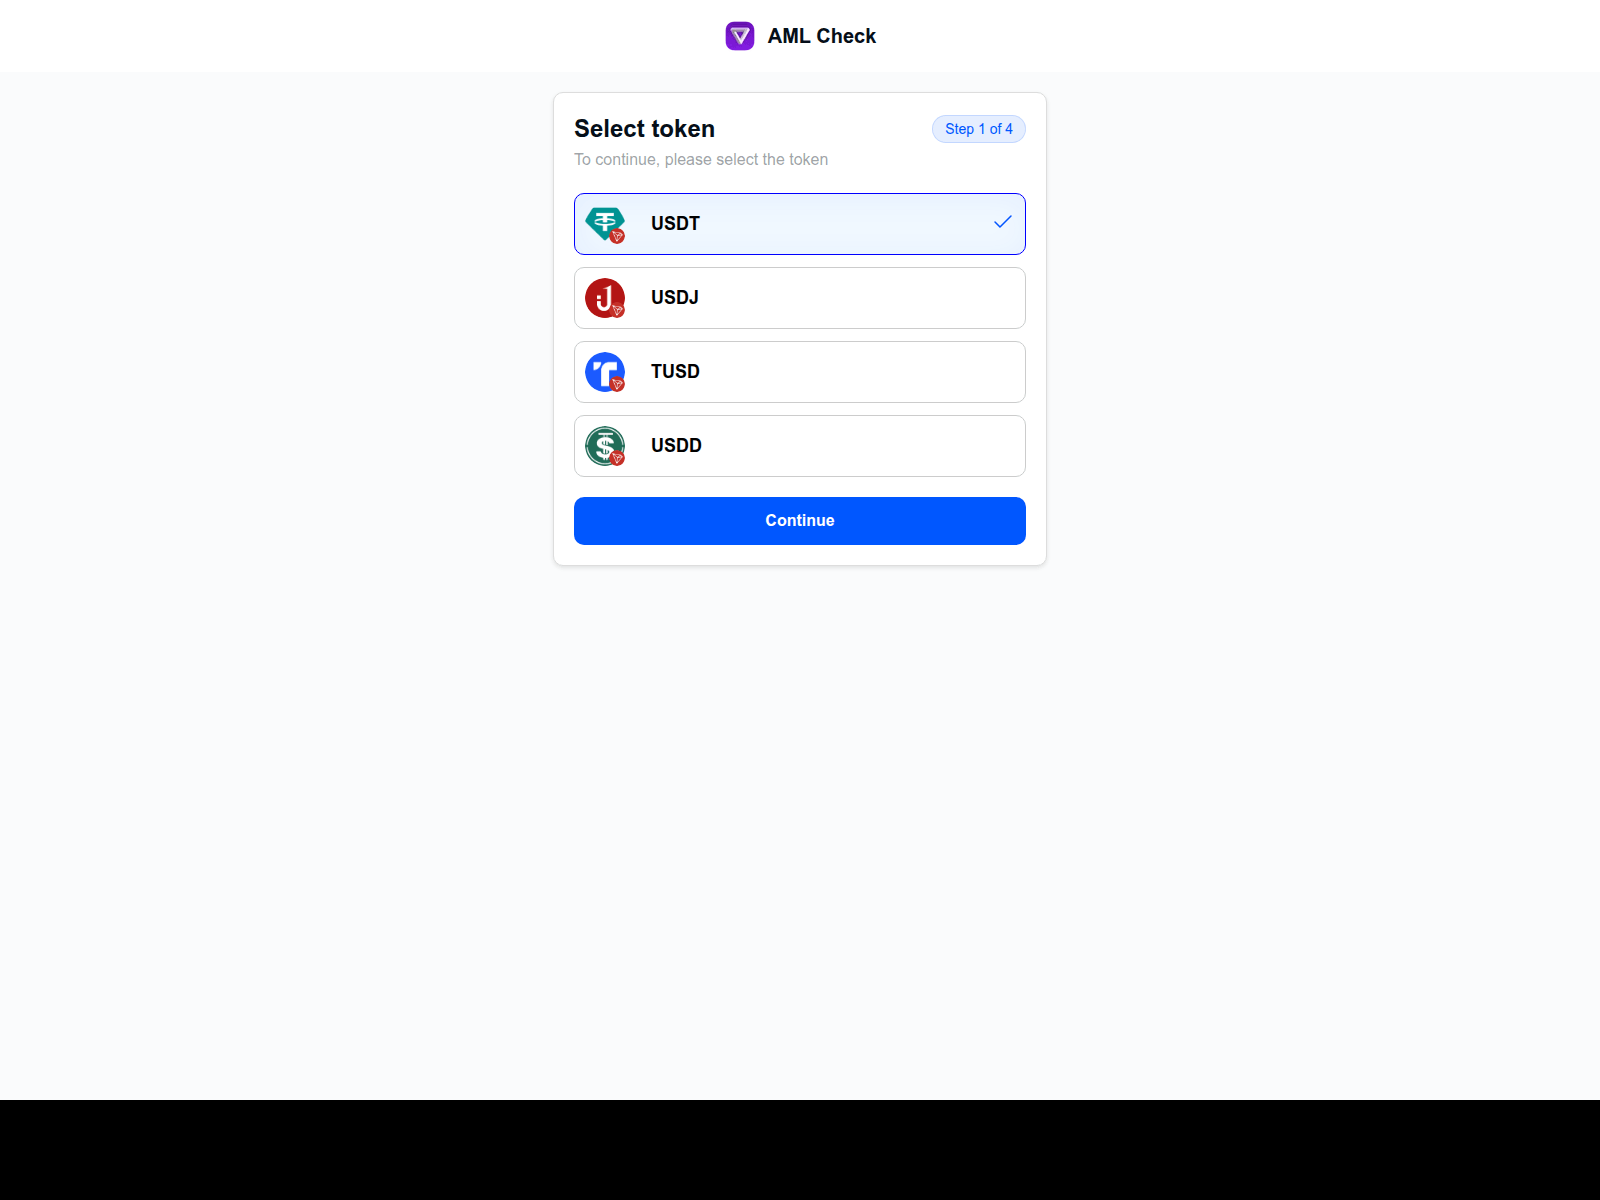
The scam exploits growing awareness of AML/KYC compliance requirements in crypto. Users who want to verify their funds are "clean" land on a convincing clone and unknowingly authorize a wallet drainer.
STEP 1
Lure via Search & Social
Victims encounter fake AML check sites through Google Ads, Telegram DMs, social media posts, or SEO-poisoned search results for queries like "check wallet AML" or "is my crypto clean."
STEP 2
Clone Legitimate UI
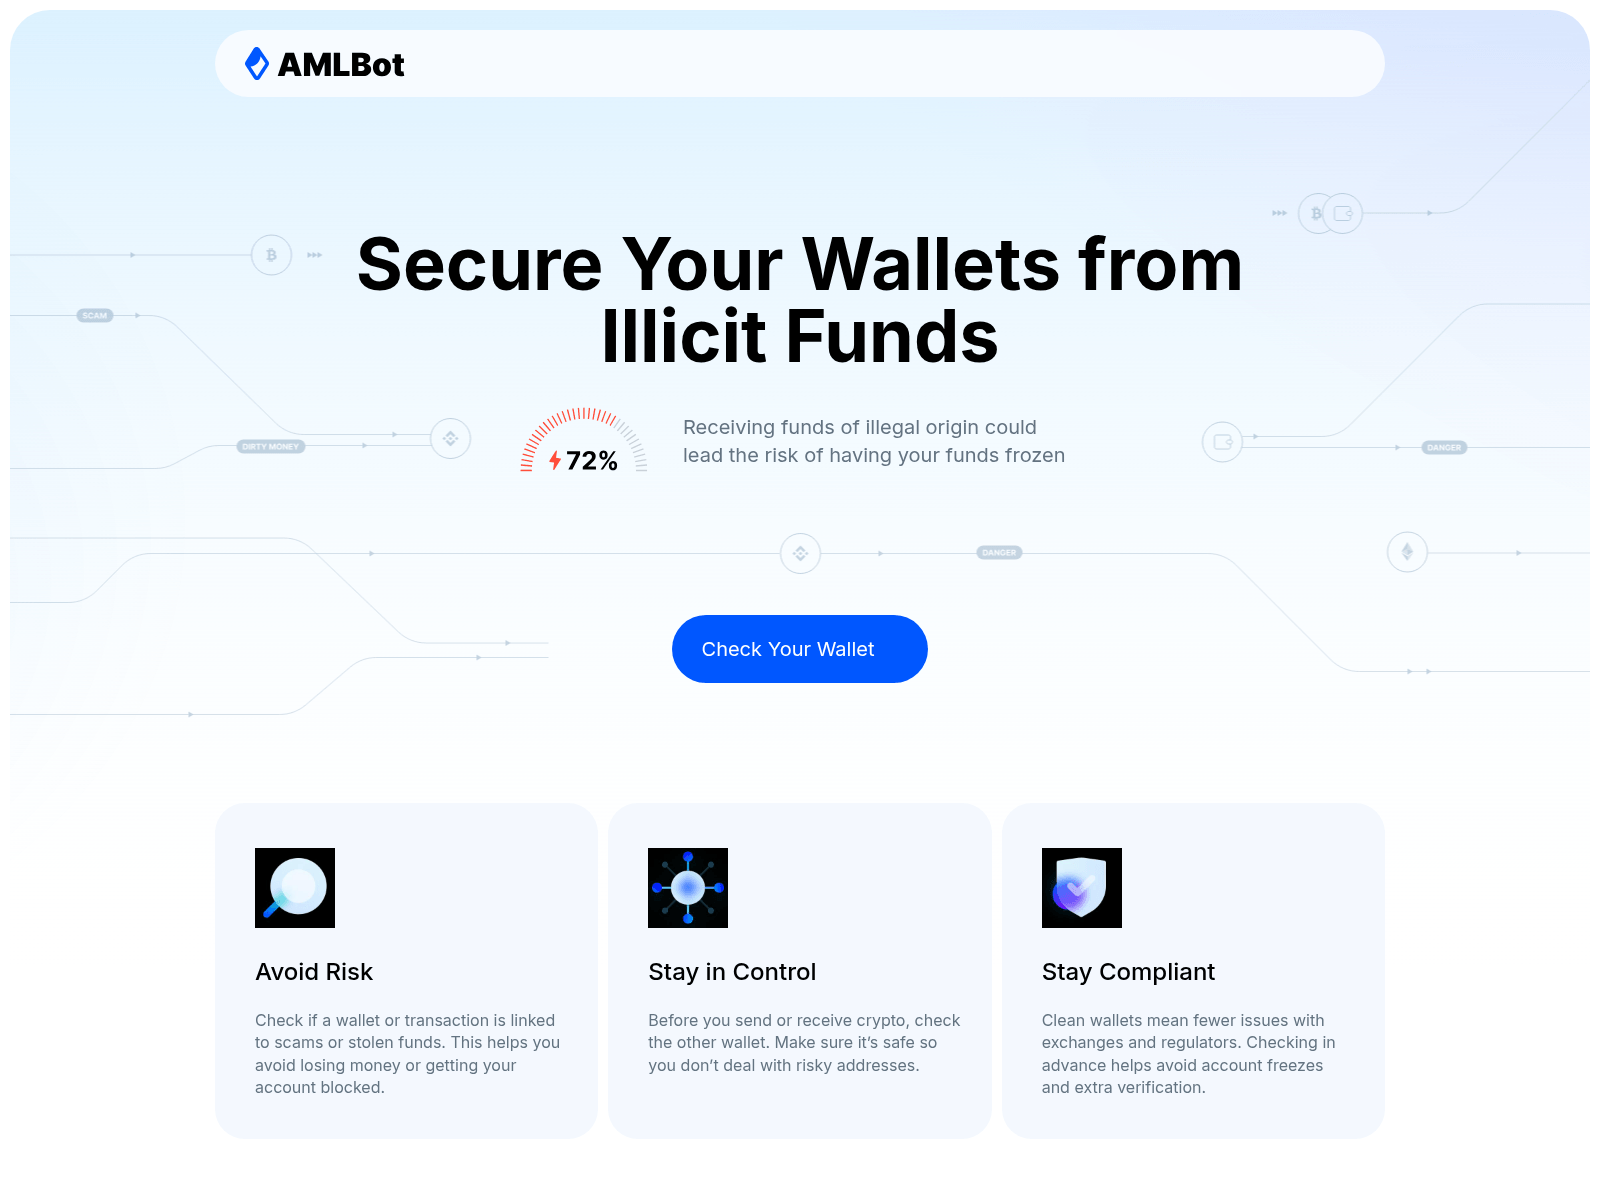
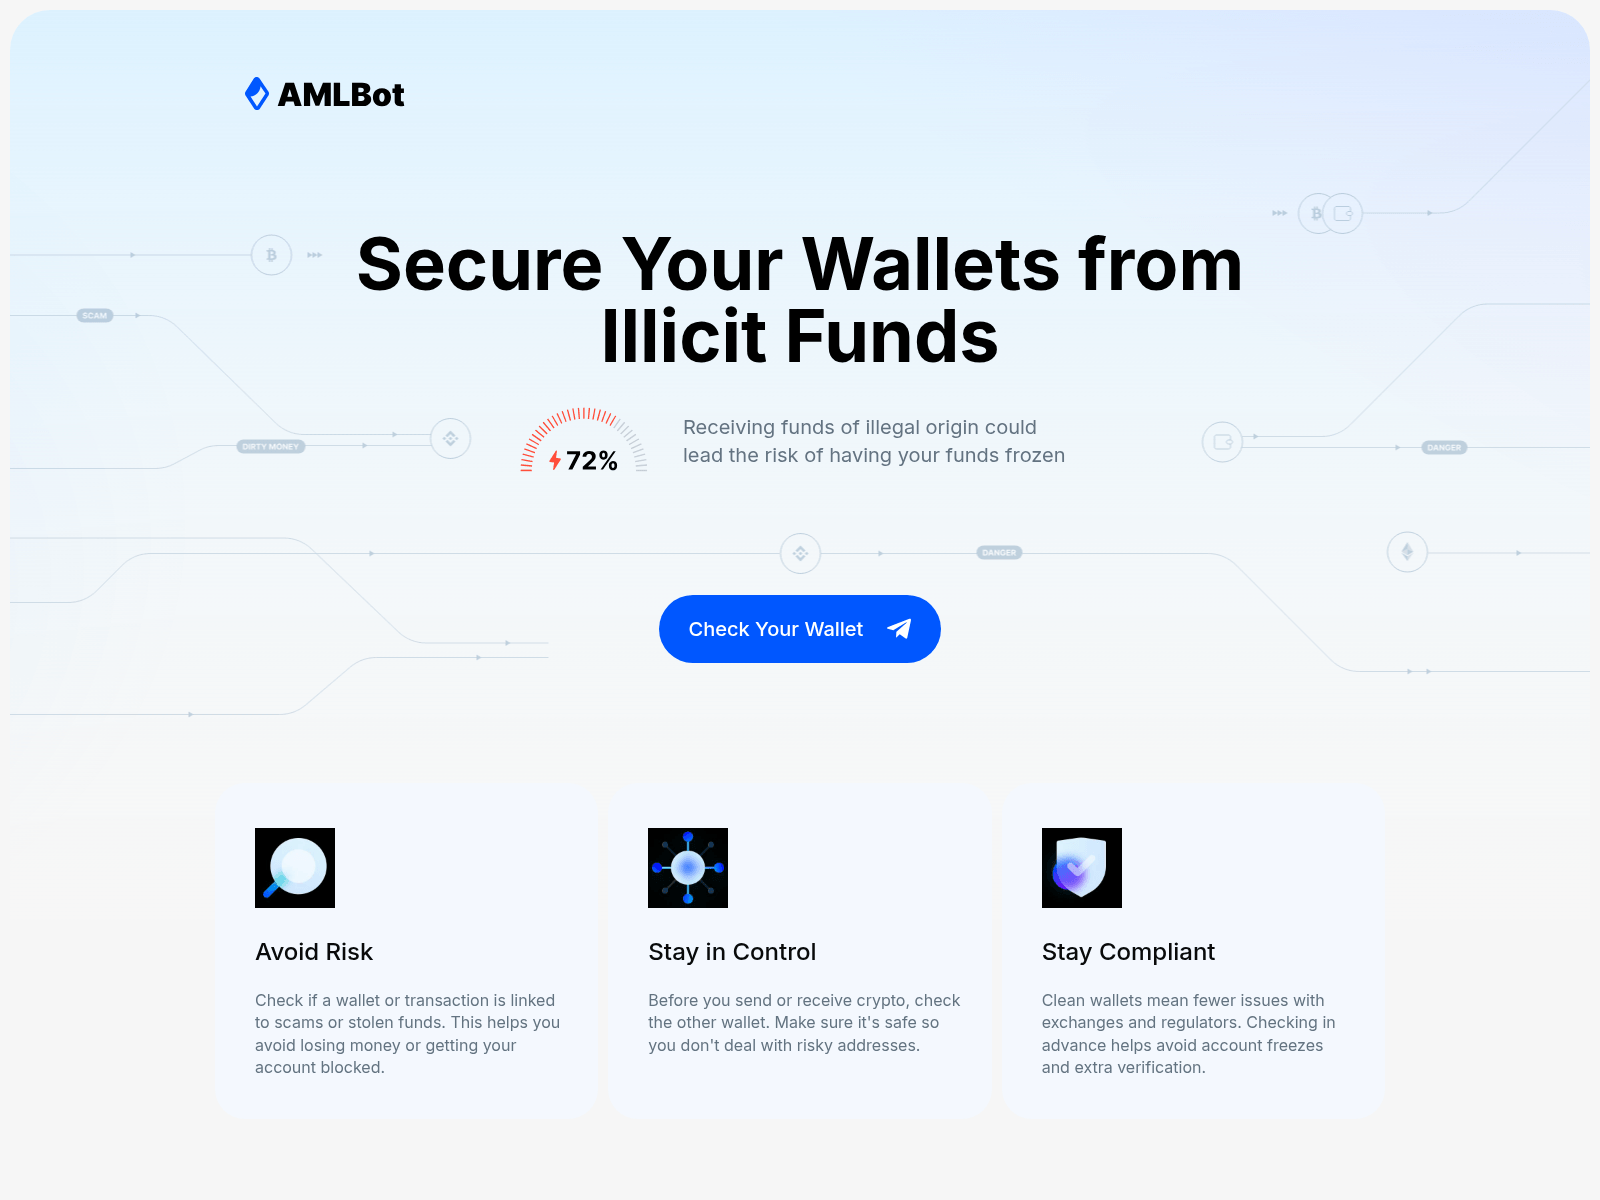
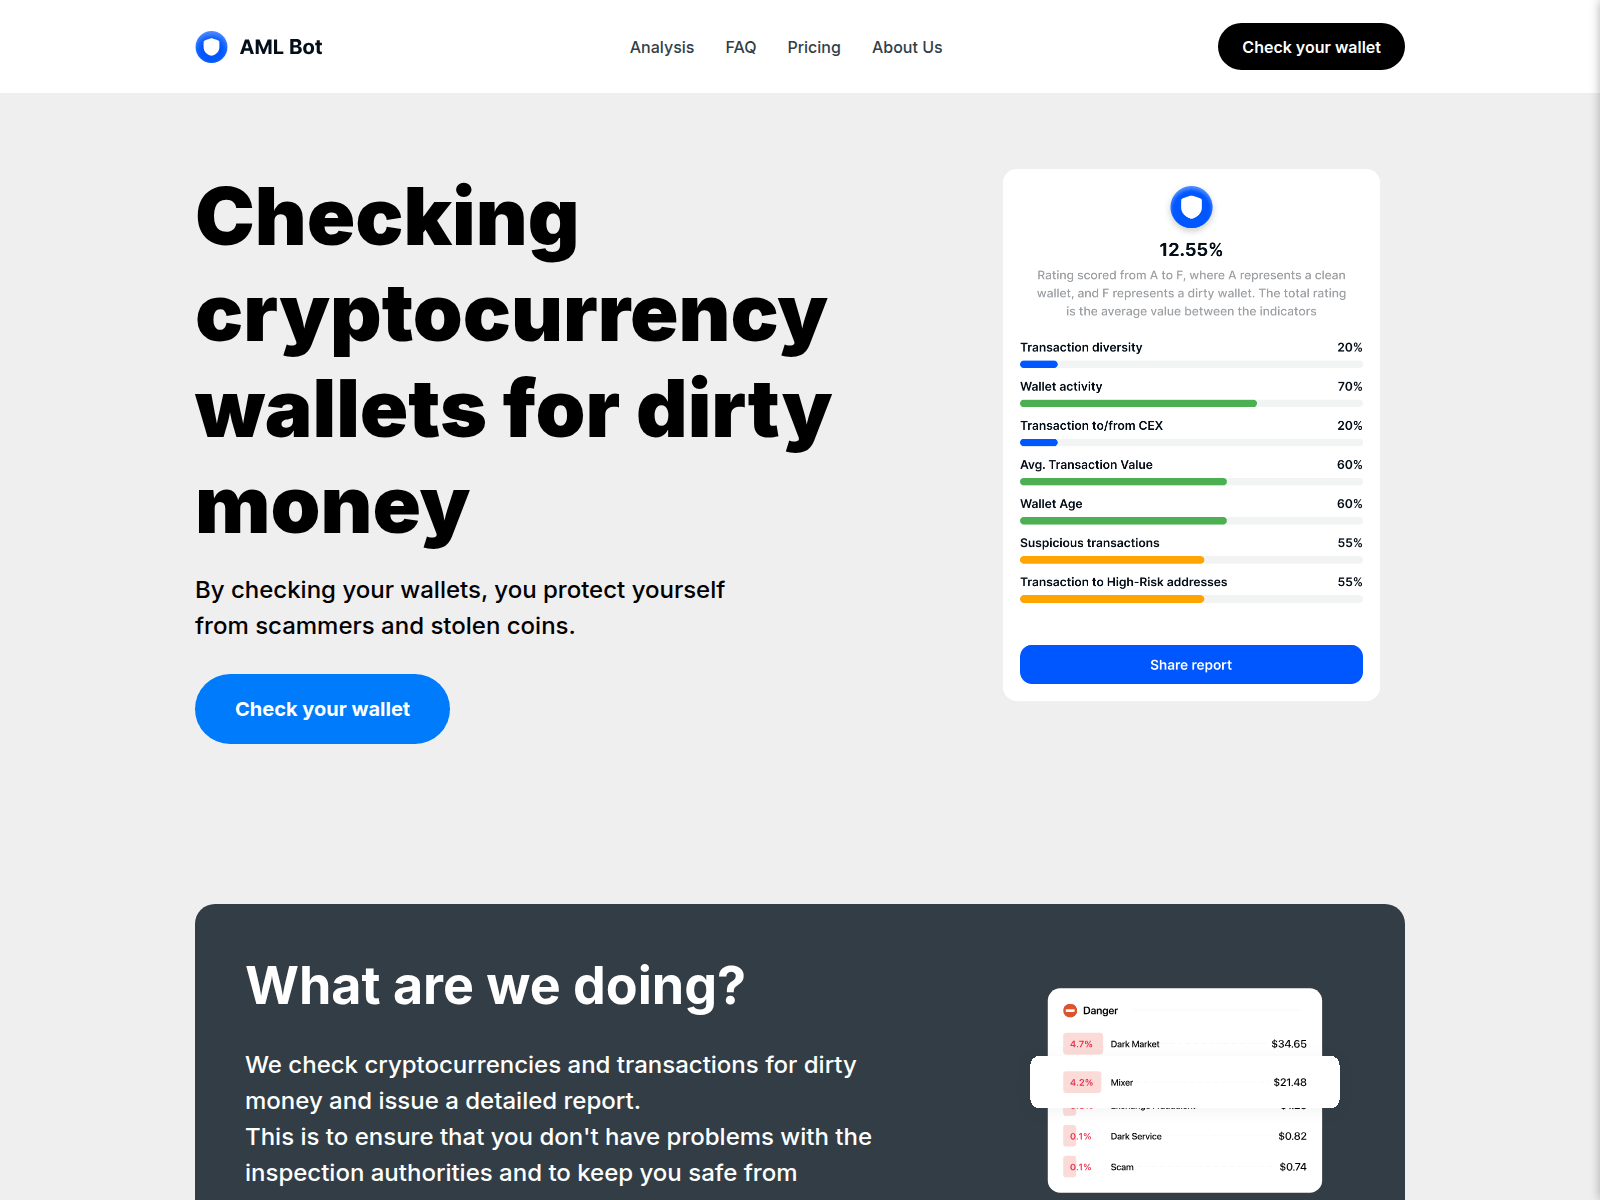
The site closely mimics the official AMLBot.com design, branding, and interface. Some clones replicate staff profiles and create fake Telegram accounts impersonating AMLBot team members.
STEP 3
Request Wallet Connection
Unlike the real AMLBot (which only needs a wallet address as text input), the fake site asks users to "connect wallet" via MetaMask or WalletConnect to "generate an AML report."
STEP 4
Drain Assets via Smart Contract
The wallet connection triggers a malicious smart contract (setApprovalForAll or token approval) that scans all tokens/NFTs, prioritizes highest-value assets, and drains everything to attacker-controlled wallets. Transactions are irreversible.
Technical Analysis
The AML scam ecosystem uses sophisticated infrastructure. 域名 typically use .com, .org, .app TLDs registered through privacy-friendly registrars (NICENIC, WEBCC account for 163+ domains). Many use Cloudflare CDN for legitimacy.
The drainer mechanism is identical to other wallet-connect phishing: upon connection, the site calls setApprovalForAll() or increaseAllowance() on the victim's token contracts. The drainer scans all assets, estimates value, and prioritizes extraction of highest-value tokens first.
According to AMLBot's 2025 Crypto Crime 报告, 65% of crypto incidents are driven by social engineering rather than technical exploits, with phishing ranking as the #2 attack type (18% of all incidents).
Key technical indicators: domains containing 'aml', 'amlbot', 'aml-check', 'aml-verify' in the URL; wallet connection prompts (the real AMLBot never requires this); recently registered domains; missing or fake SSL certificates.
Real Cases
AMLBot Clone Wave (2024-2026) (2024-2026)
1,350+ fake domains stolen
AMLBot officially warned about an alarming rise in scammers impersonating AMLBot on various platforms, including fake Telegram bots and clone websites.
amlcheckwallet.cc Drainer (2024)
Wallet drainer active stolen
Registered via Dynadot Inc, resolved to Cloudflare IP 104.21.25.10. Served a fake "AML wallet check" interface with wallet-connect drainer. PhishDestroy report.
PCRisk AML Warning (Jan 2026) (January 2026)
12+ documented domains stolen
PCRisk documented a new wave of fake AMLBot sites including amlbotchecks.com, aml-safety.app, amlrobotsaveru.com, amlpremium.top. FTC reports over 46,000 people lost $1 billion to crypto scams since 2021. PCRisk report.
amlbotchecking.com Campaign (2024)
Multiple victims stolen
Typosquat of AMLBot serving crypto drainer via fake compliance check UI. Documented by Malware Guide and PCRisk.
How to Detect
Site asks to "connect wallet" — the real AMLBot only needs a wallet ADDRESS as text input, never a wallet connection
域名 contains "aml" variations: amlbot, aml-check, aml-verify, amlcrypto (verify against official amlbot.com)
Recently registered domain (check WHOIS — legitimate AML services have years of history)
紧急 messaging: "Your wallet may be flagged" or "检查 compliance before funds are frozen"
Promoted via Telegram DMs, Google Ads, or unsolicited emails instead of organic search
How to Protect Yourself
1
Bookmark the official AMLBot at amlbot.com — never click links from ads, DMs, or emails
2
Remember: legitimate AML tools only need a wallet address (text), never a wallet connection or private keys
3
检查 any AML domain on PhishDestroy before interacting with it
4
Use a separate "burner" wallet with minimal funds when testing any new DeFi/Web3 service
5
If you connected your wallet to a suspicious site: immediately transfer remaining funds to a NEW wallet and revoke approvals at revoke.cash
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,109 domains tracked for this threat type
Fake AML 检查 Scam 2,109 domains


威胁响应 Pipeline
该中心内的每个域名是如何经过验证的,以及已确认的威胁是如何被消除的。 完整流程可视化 →
威胁情报核查— 每个域名都会经过扫描,并与以下内容进行交叉核对:
urlscan.io屏幕截图 · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency 报告Cloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulses互联网档案馆Historical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS 安全 FiltersQuad9 · AdGuard · CleanBrowsingWeb-检查Full surface scan
 crt.sh
全球供应商同步— 已确认的检测结果将推送给 29 家合作伙伴:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantec网站评审AviraCloud detectionAvast / AVGWeb Shield卡巴斯基OpenTIPDr.WebOnline scannerNetcraft关停 APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.报告Hosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust