
搜索受监控的域名,并查看存储的证据、检测结果以及最新观察到的可用性情况。
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake 域名
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains


vote-solve.com

vote-xeetsai.com

voters-facy.com

voting-pieverse.net
vpn3.fatfry.net
vq3r3-bqaaa-aaaak-qignq-cai.icp0.io
wallet-app-dfl.pages.dev

walletconnectscan.netlify.app
walletpay.pages.dev
wallstreetshiba.com
yield-yak.net
yyp11.net
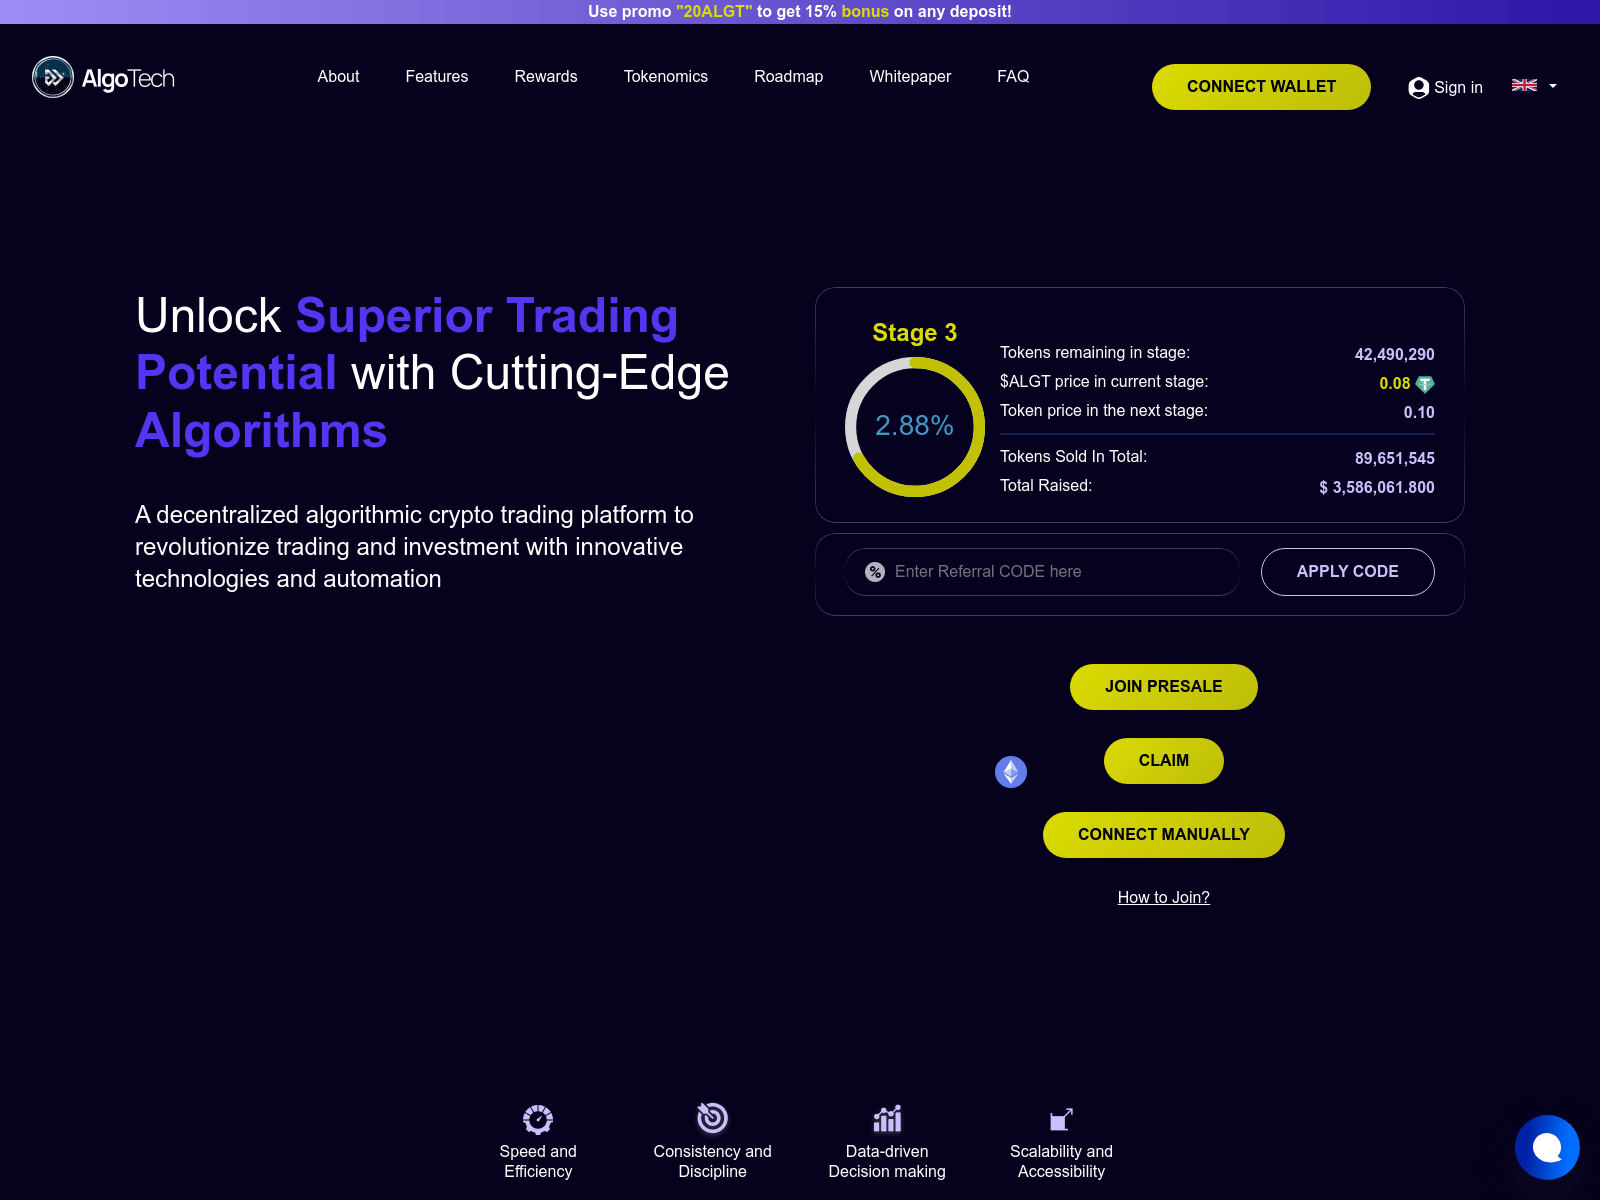
algotech.trade
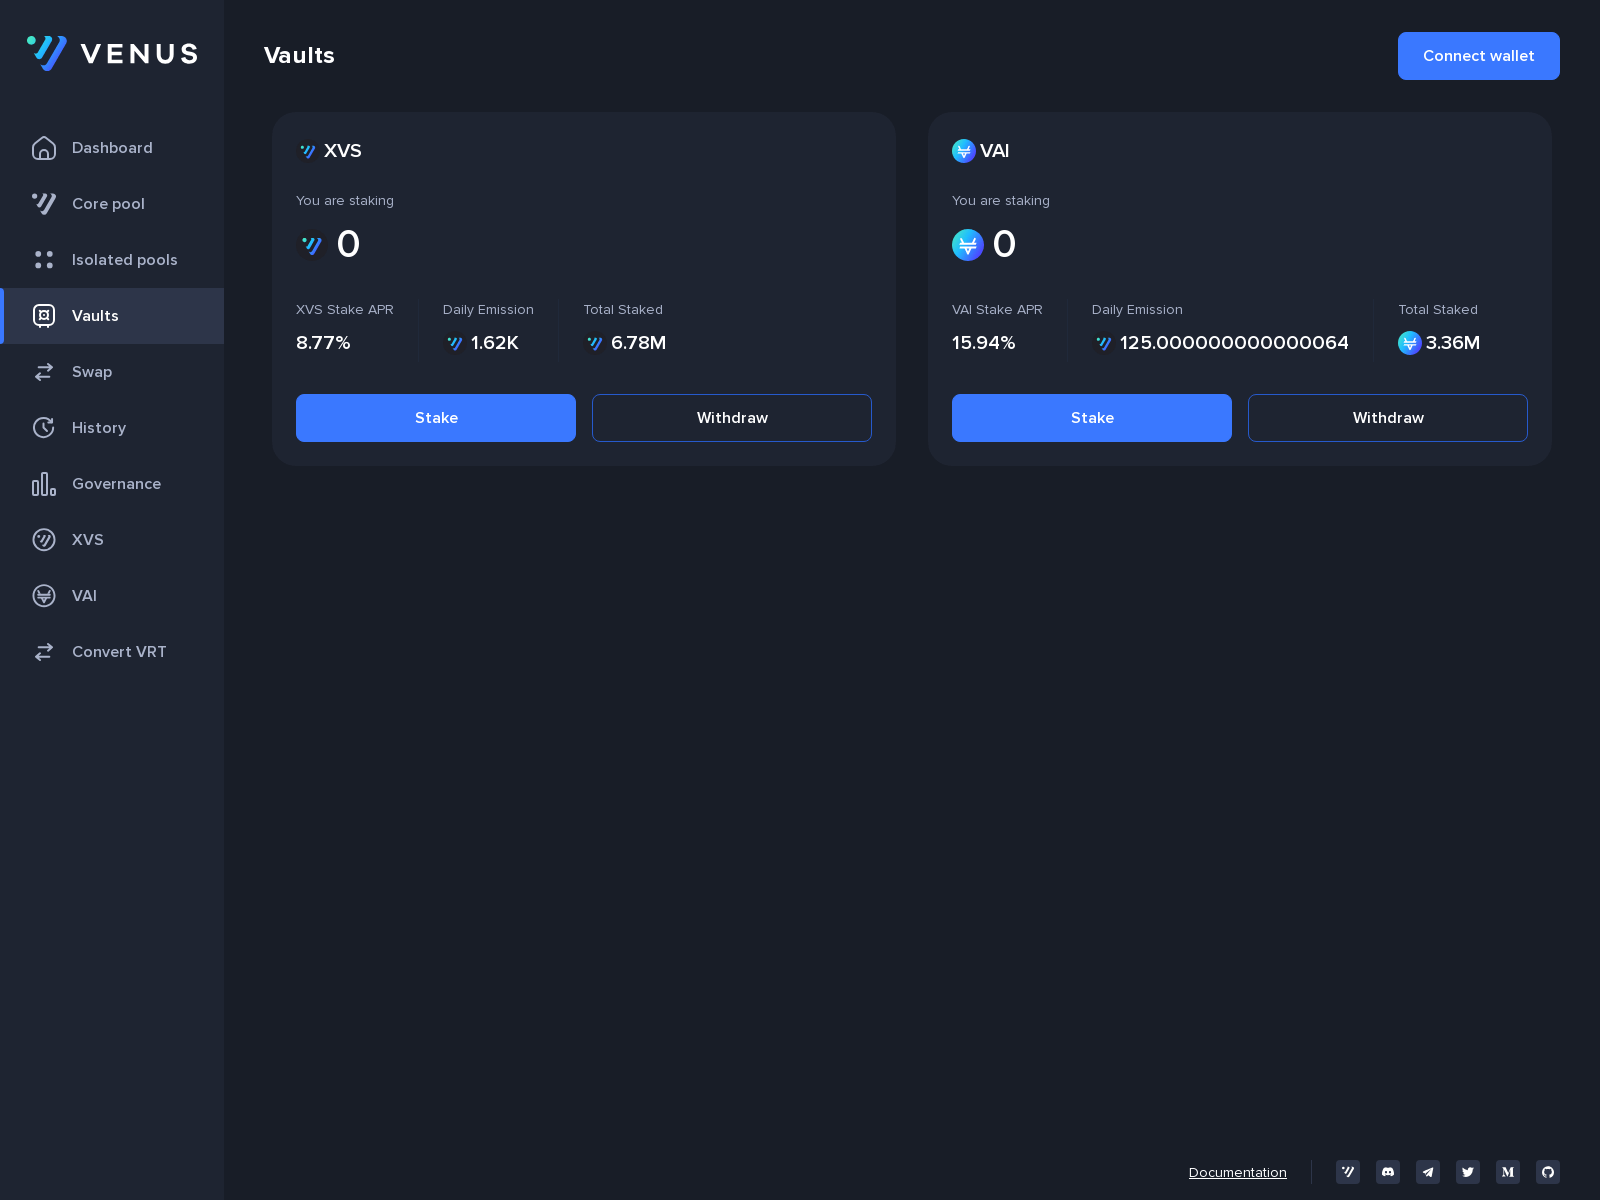
appvenus.io
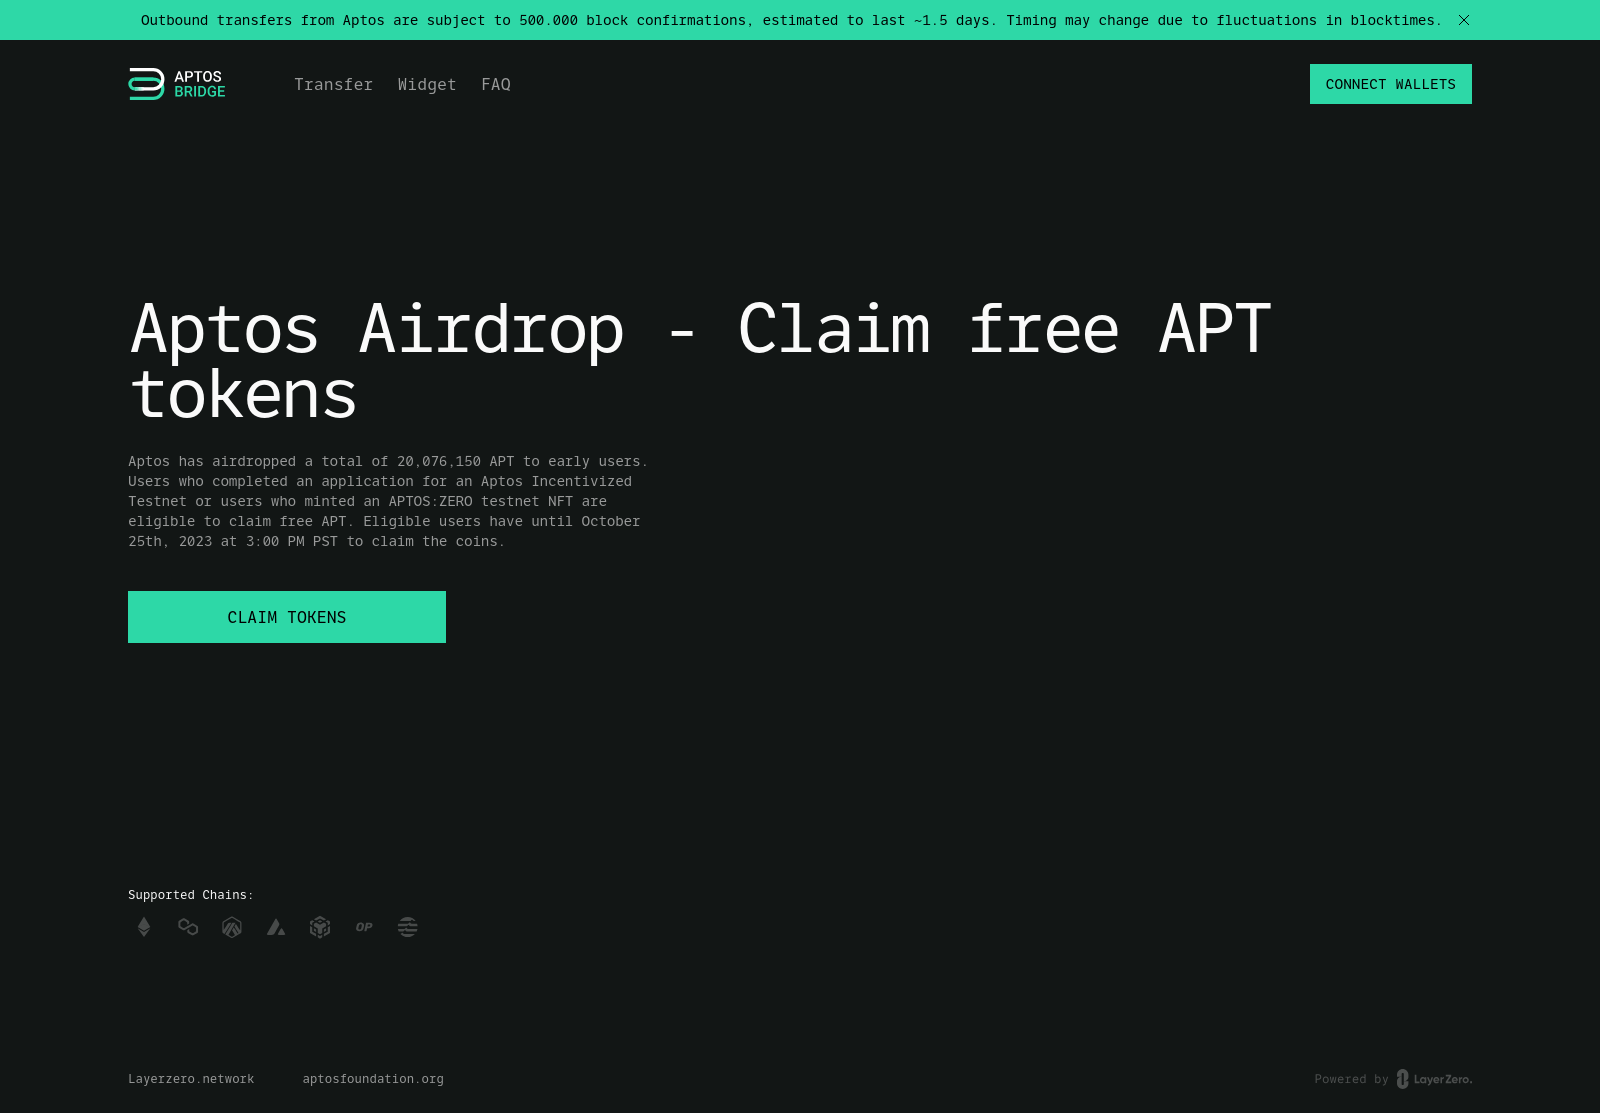
aptos-allocation.com
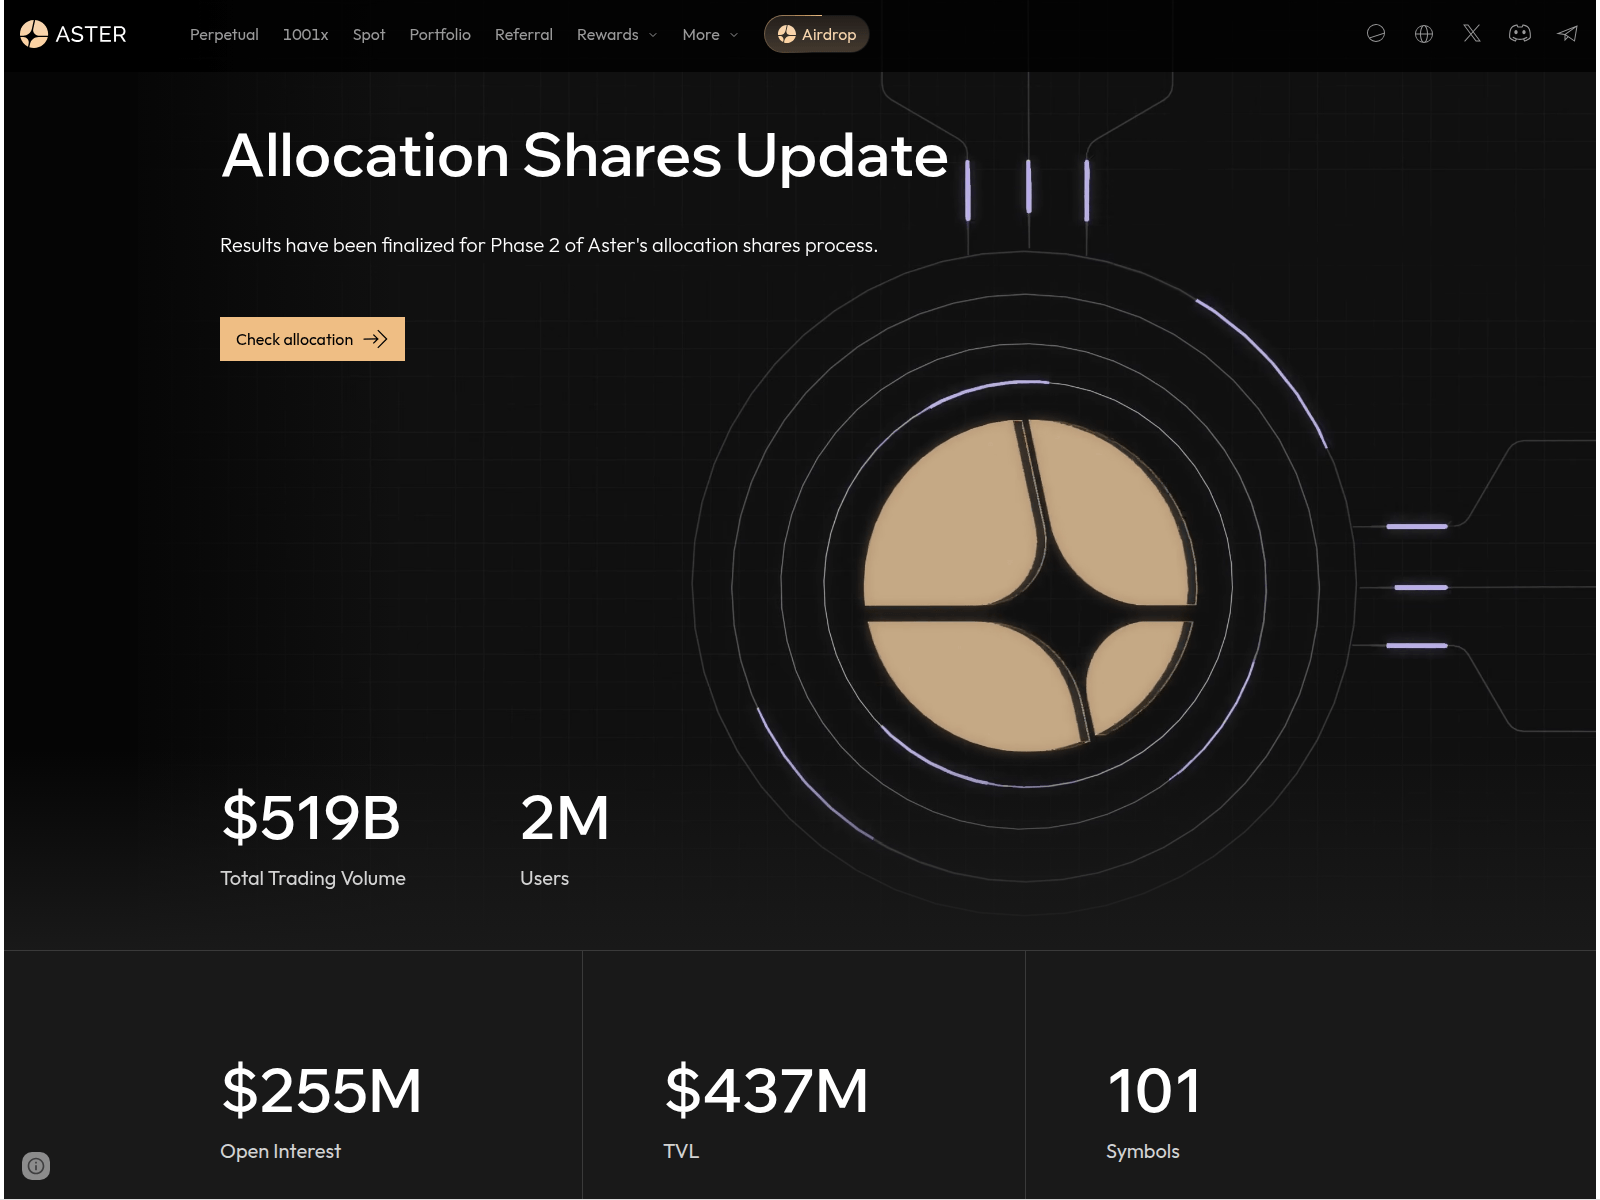
asterdex-votings.com
asterdex.pw
beeplecrap-mint.com
bob-mainnet-kle9if02h-distributed-crafts.vercel.app
bob-mainnet-staging.vercel.app
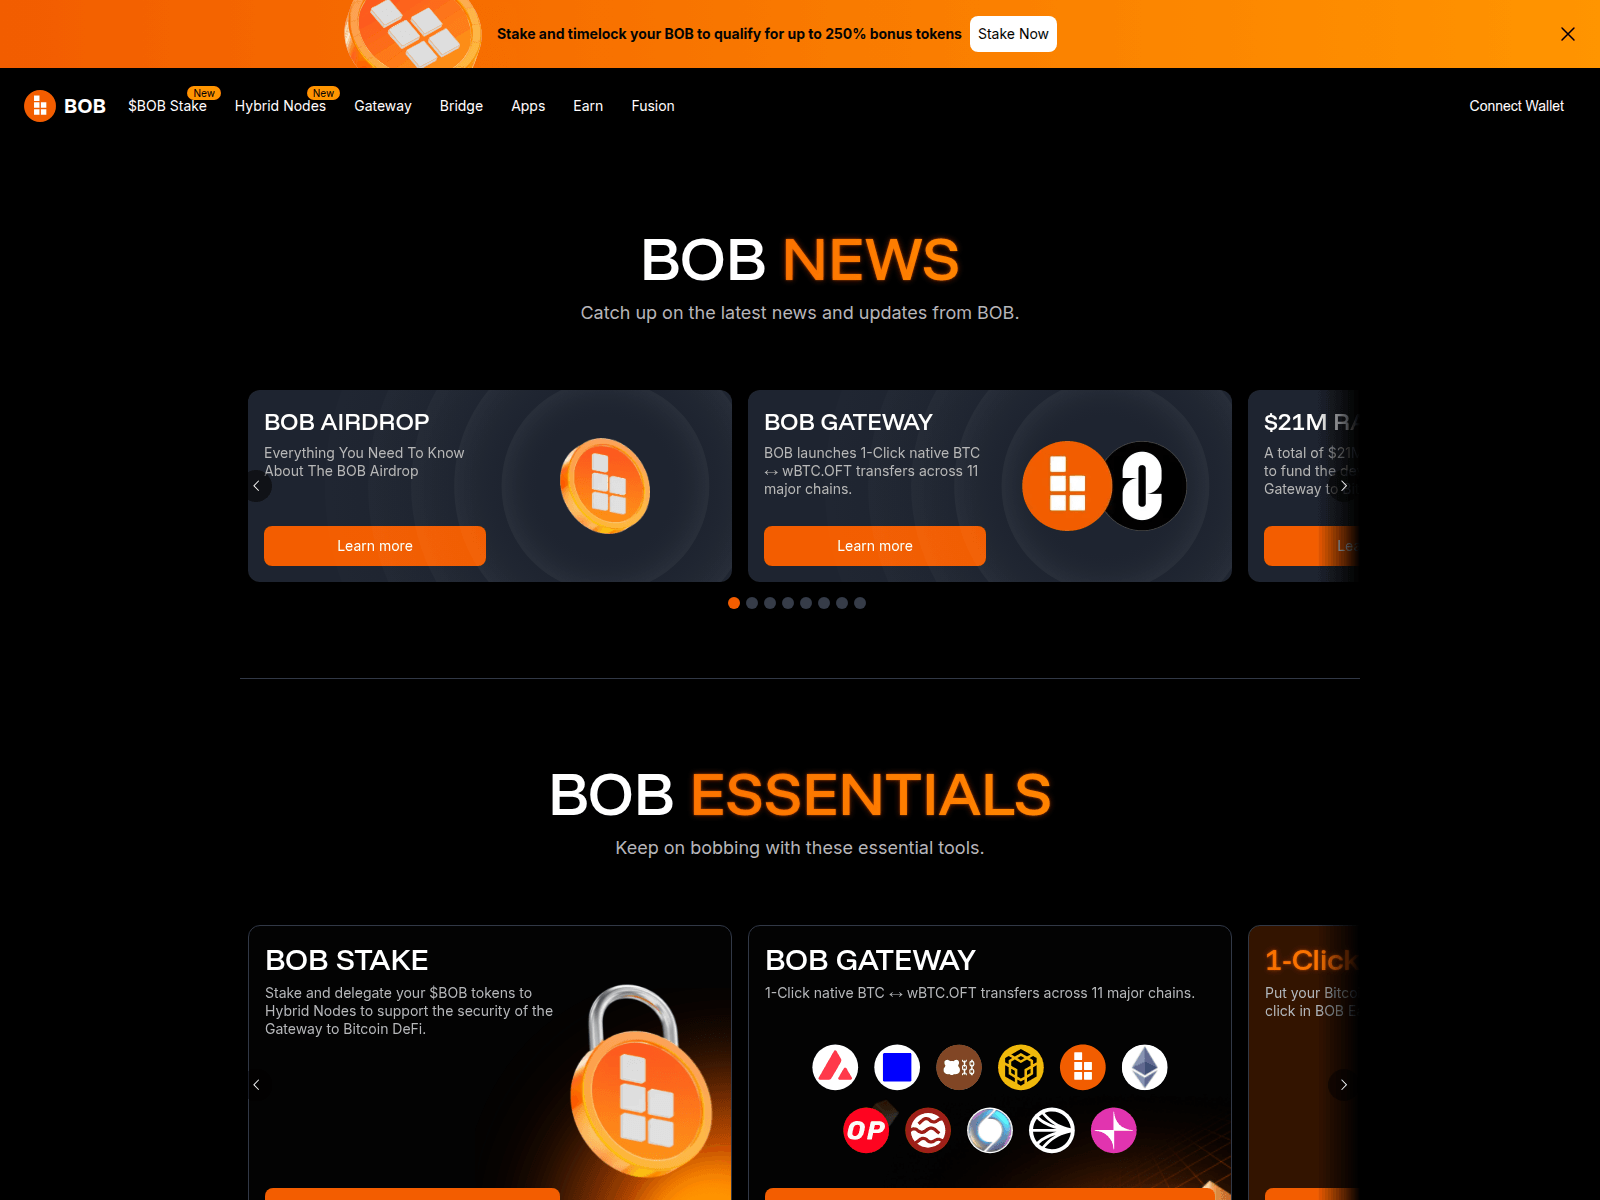
bob-sepolia-jnlut6zb3-distributed-crafts.vercel.app
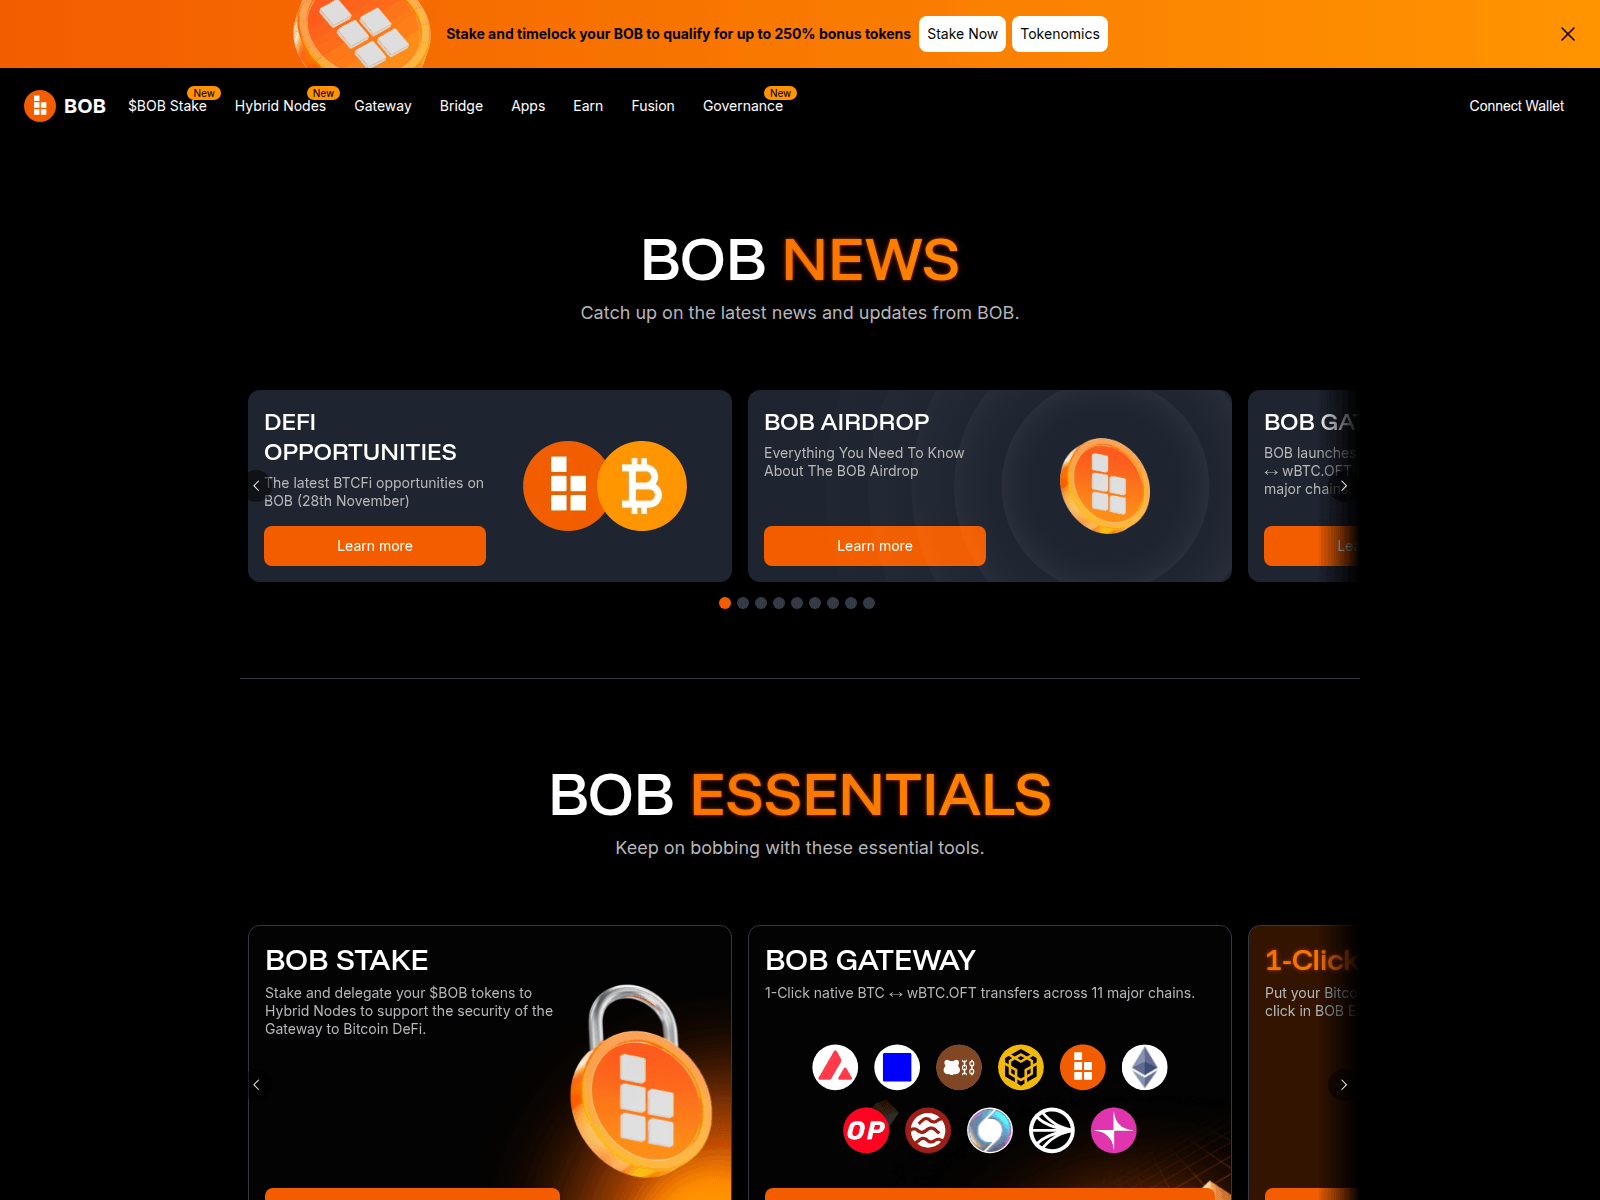
bob-sepolia-k50ei2mp5-distributed-crafts.vercel.app
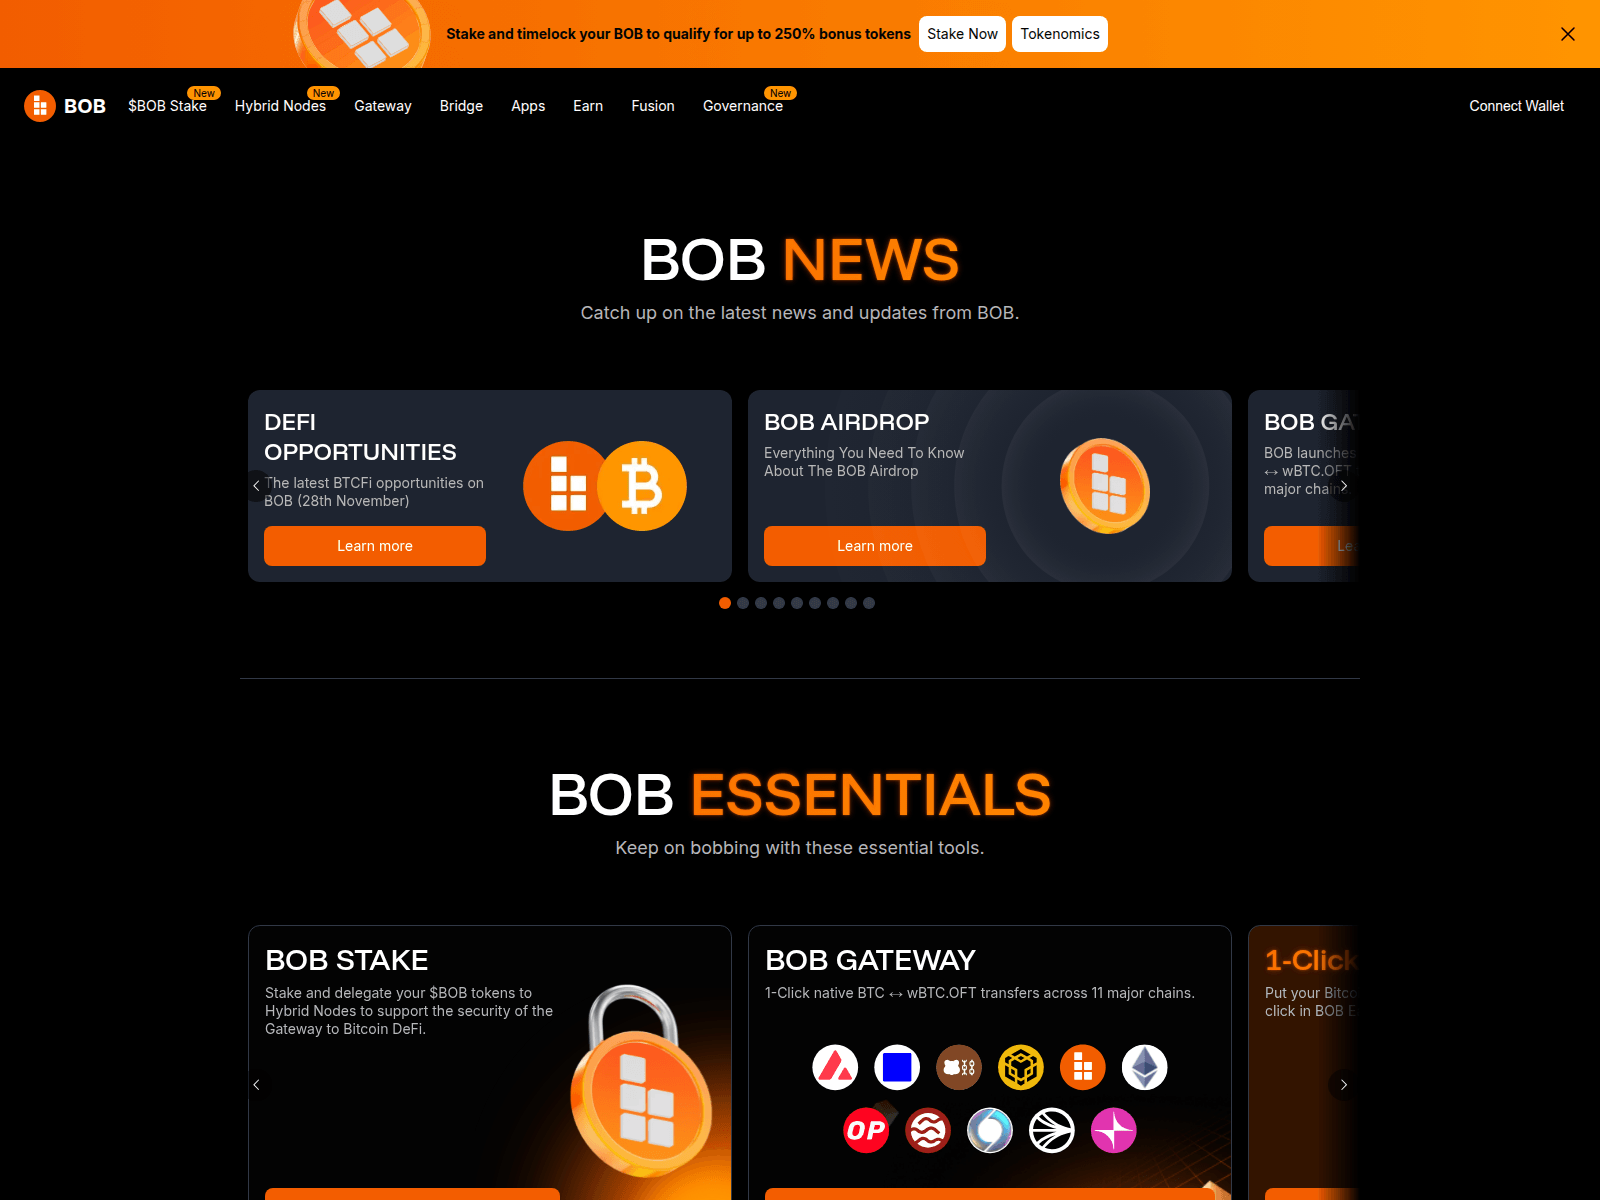
bob-sepolia-r0iniojdx-distributed-crafts.vercel.app
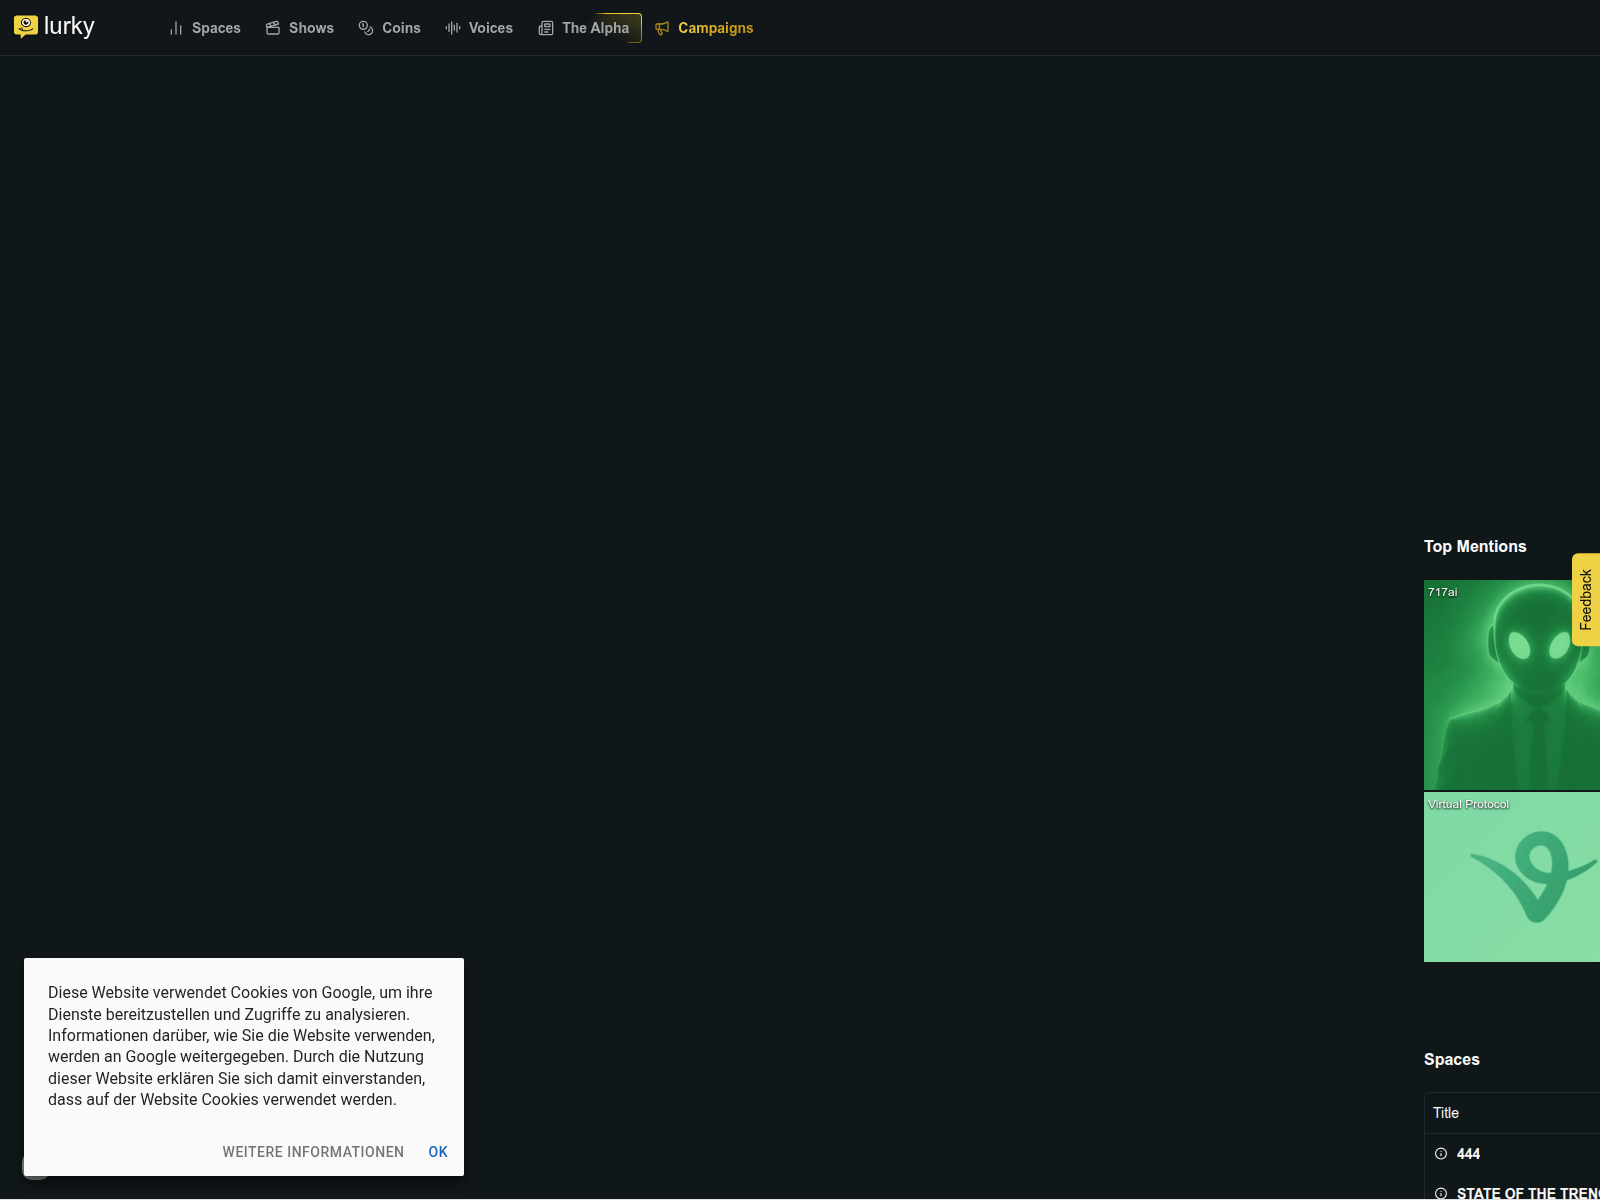
buyback-lurkys.com
chainopera-register.com
chainstats.info
chainstats.net
claim-kitefoundation.com
claim.stakecybro.live
clankers-vote.com
clashflow.finance
cypher.votings.workers.dev
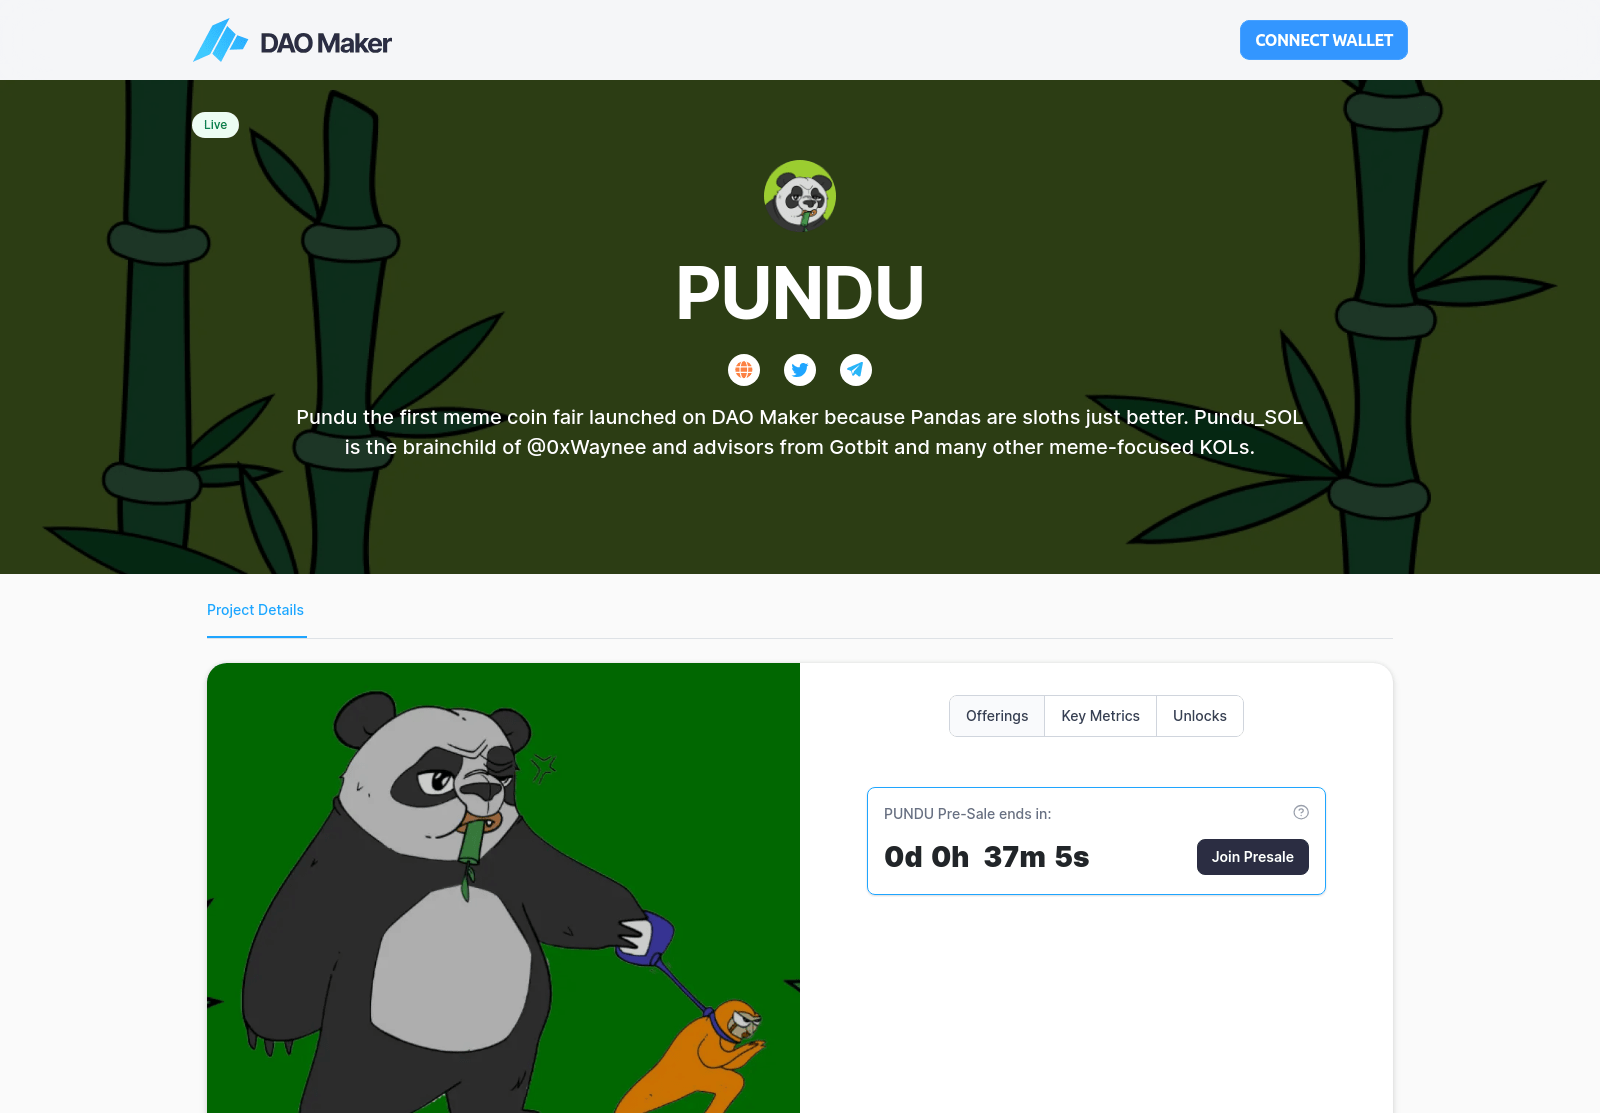
daomaker.lat
dappextension.info
eligibility-faircaster.com
erc20scan.com
ethersdrops.org
facy-voting.com
hamstr.art
hyperliquid.hedgeempire.fun
lnscribe.app
manyushib.votings.workers.dev
mavv.work
memecoinpump.fun
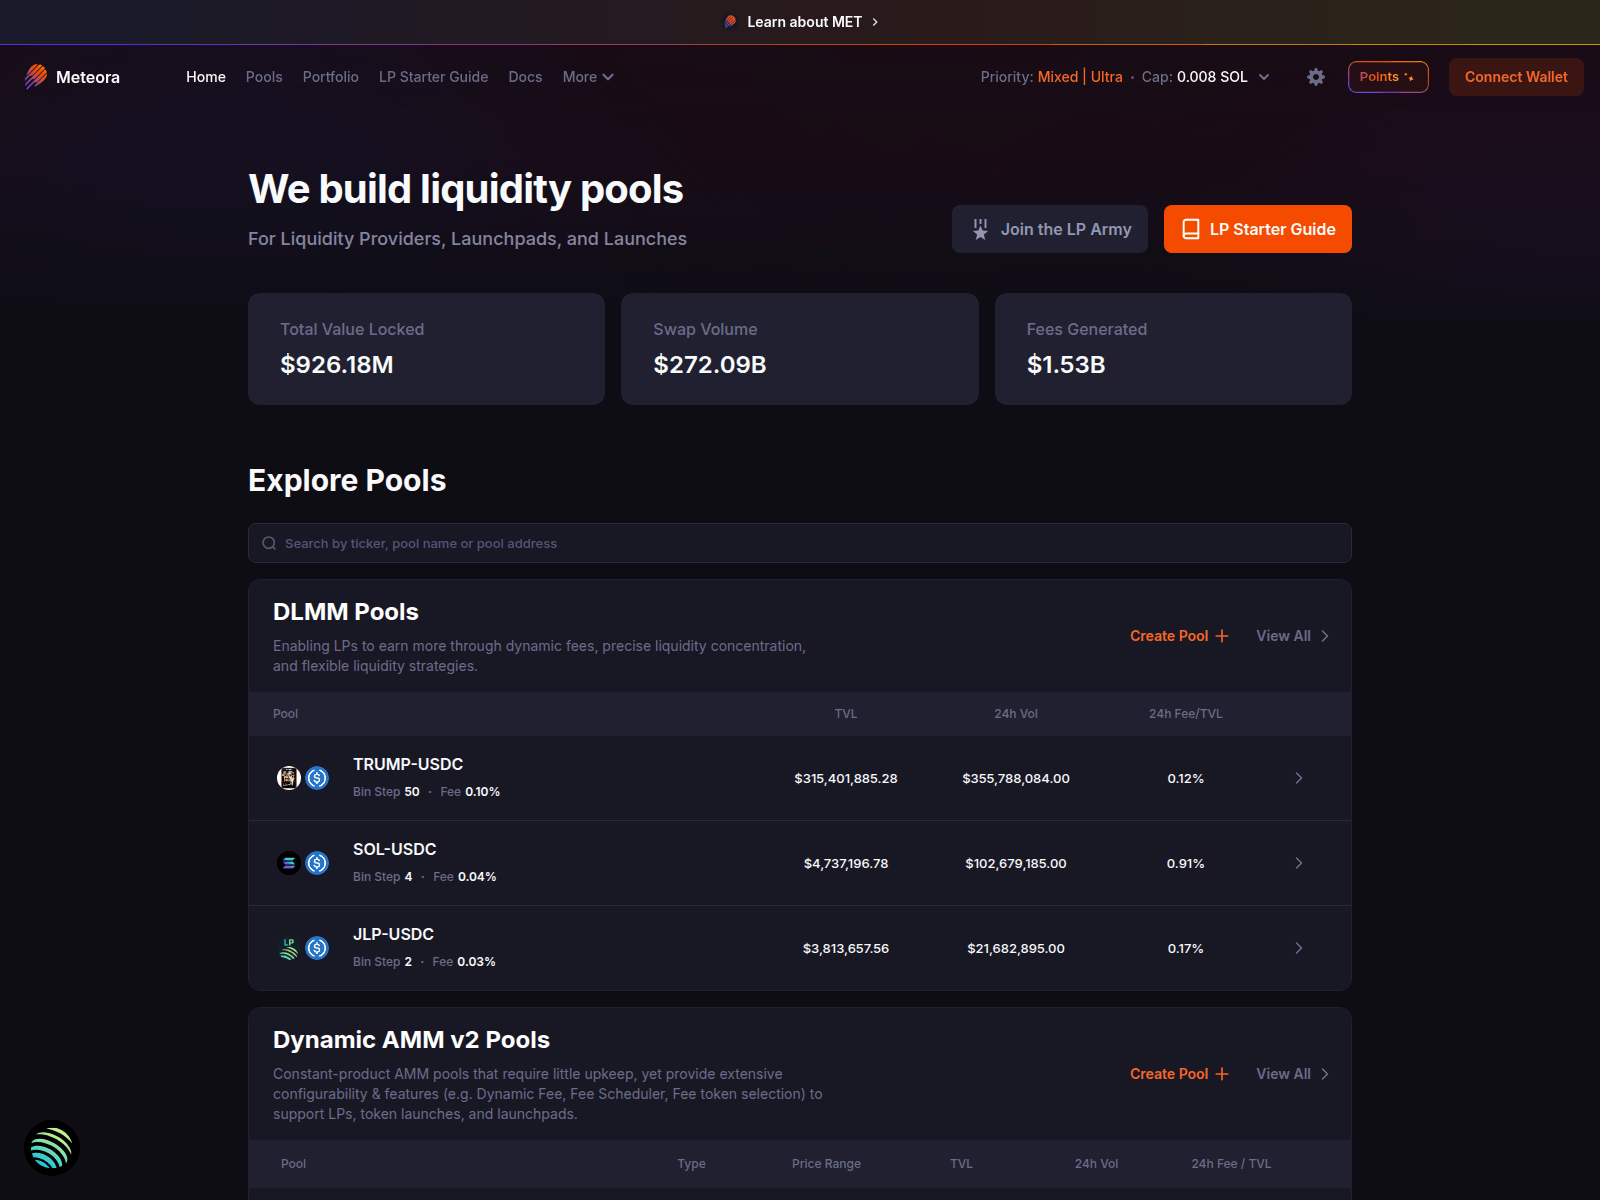
meteorateam.lat
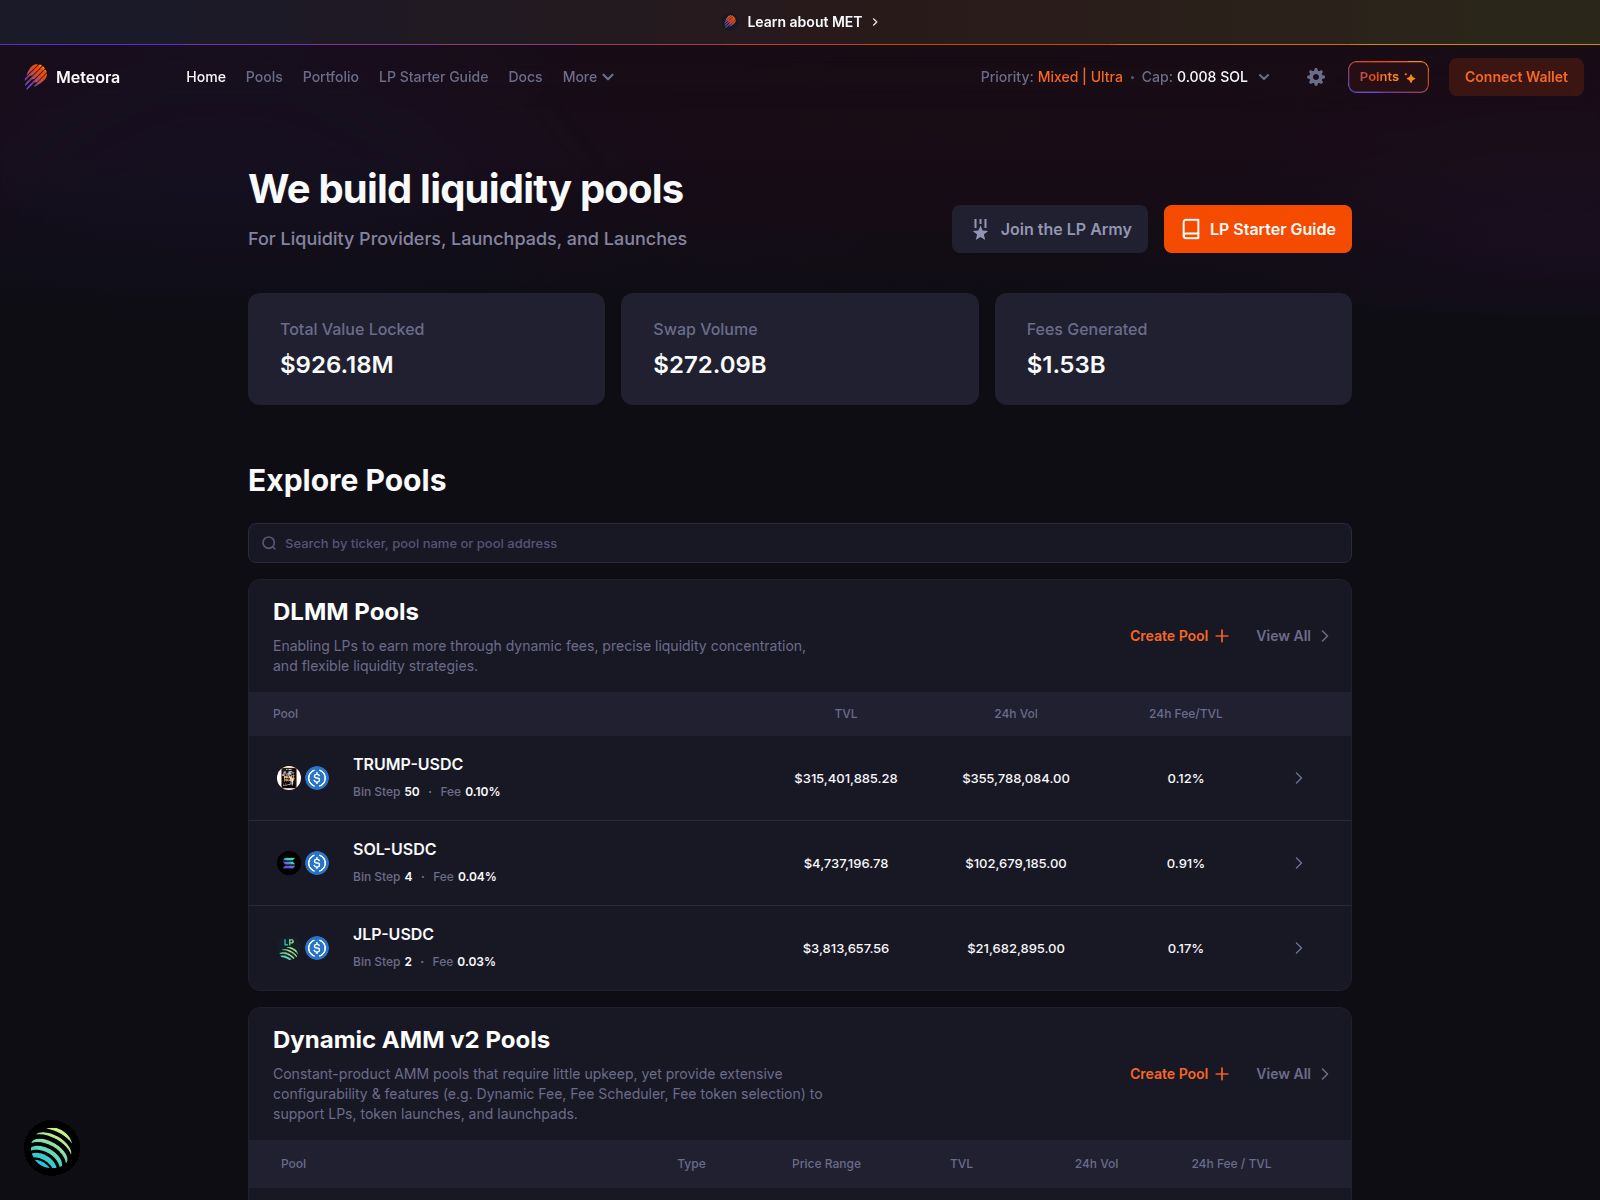
meteorateam.lol
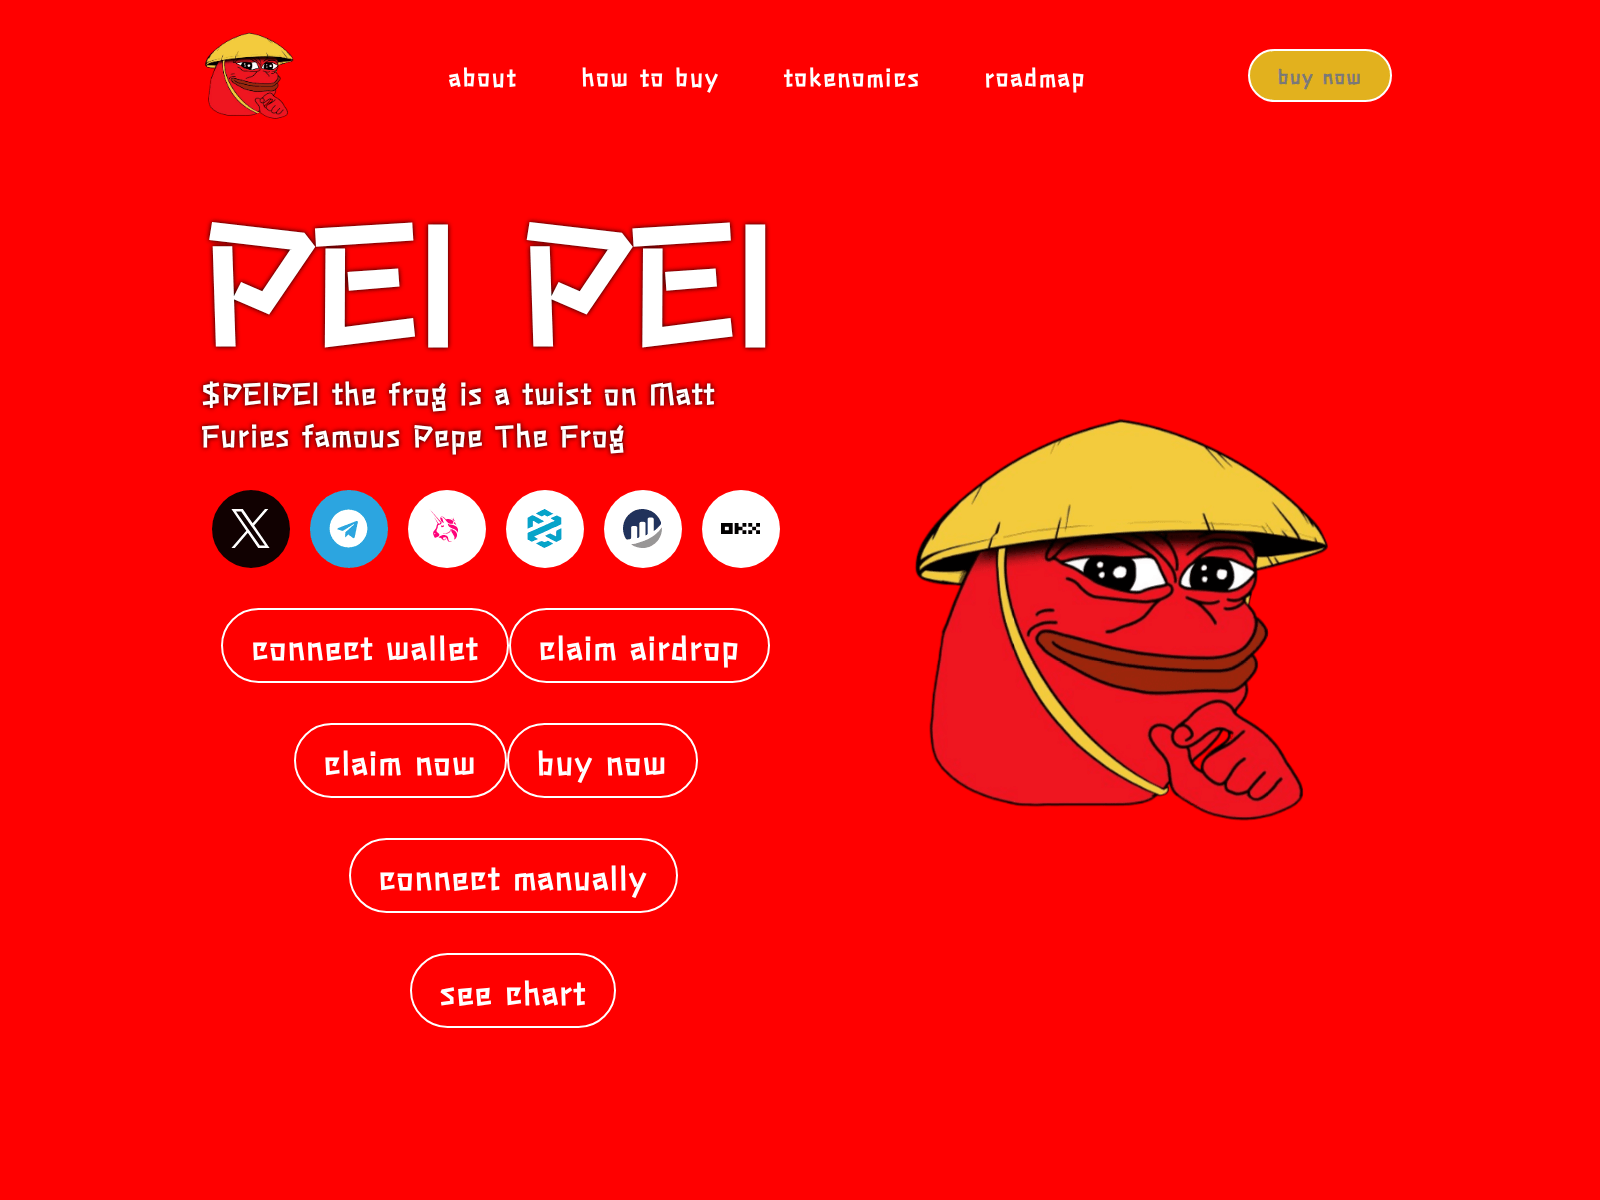
peipeicoins-ai.web.app
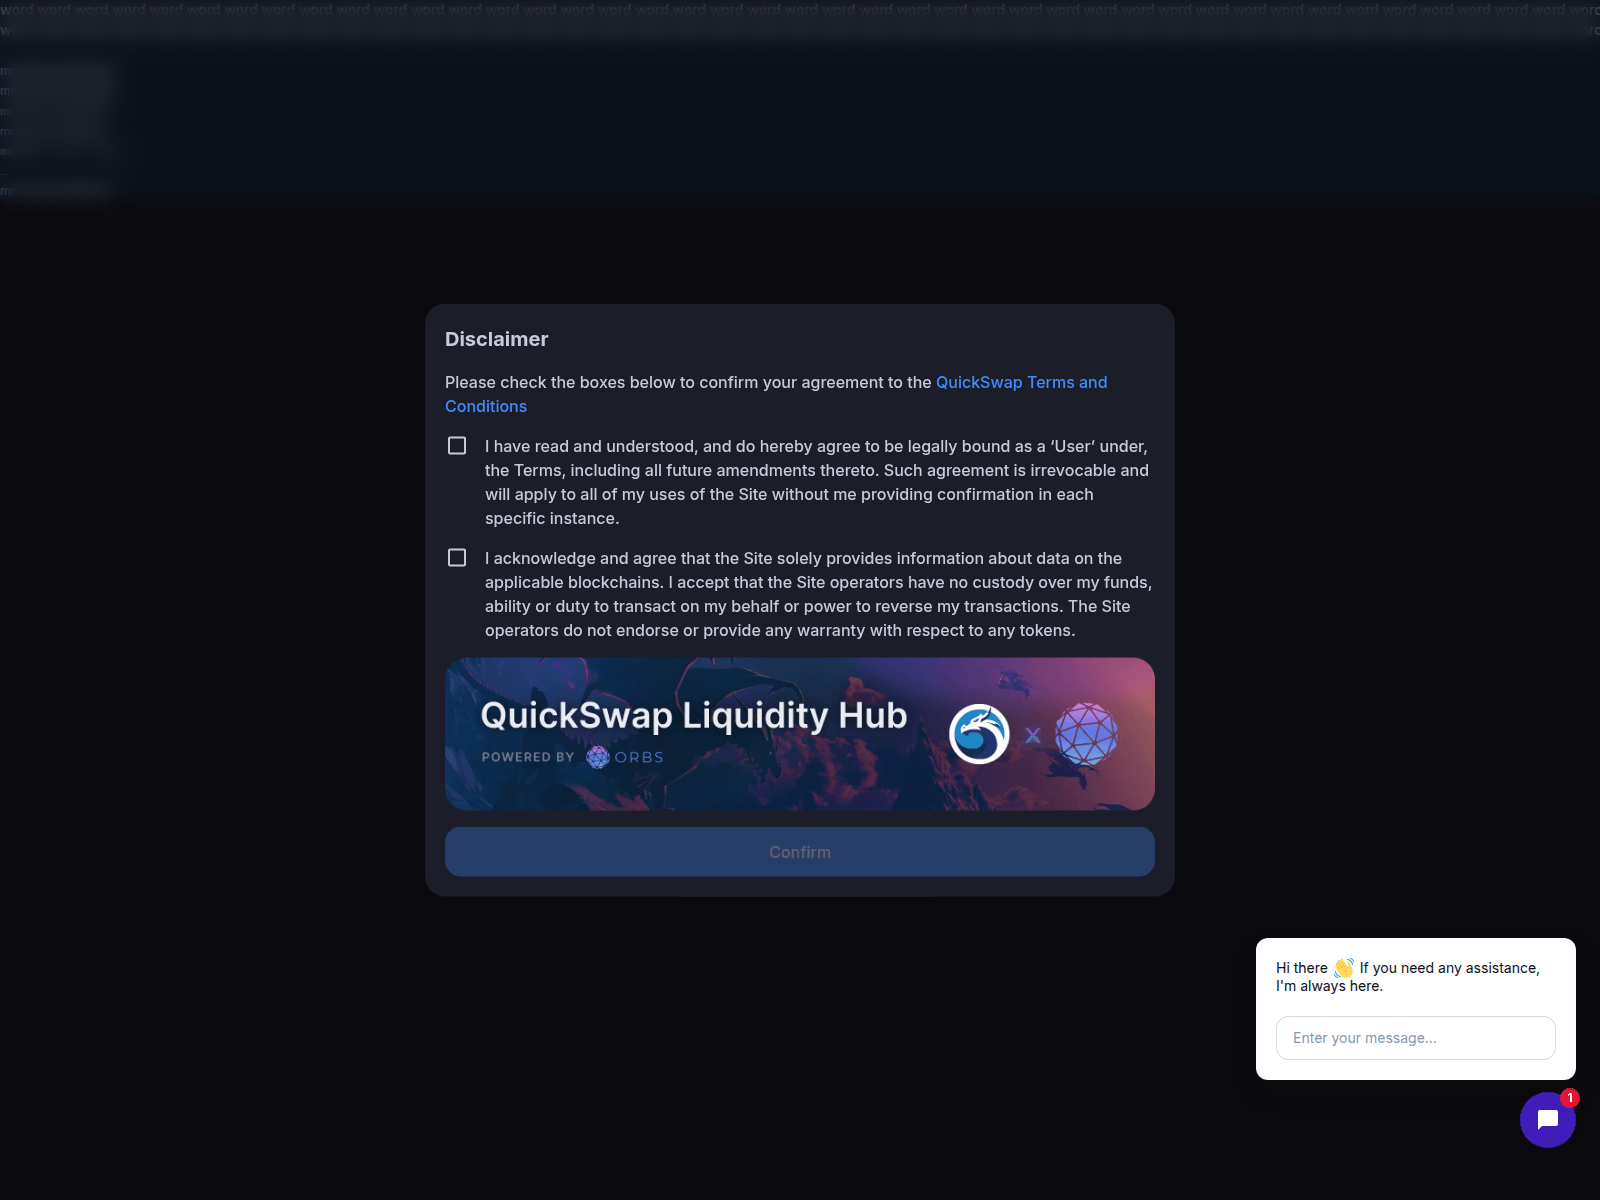
quickswap.exchange-defi-swap-referral.pics
quickswap.exchange-defi-swap-referral.world
quickswap.exchange-v3-app-referral.life
quickswap.exchange-web-referral.pics
quickswap.exchange-web-referral.world
register-apro.com
revoke-curvesfinance.com
soracles-rewards.com
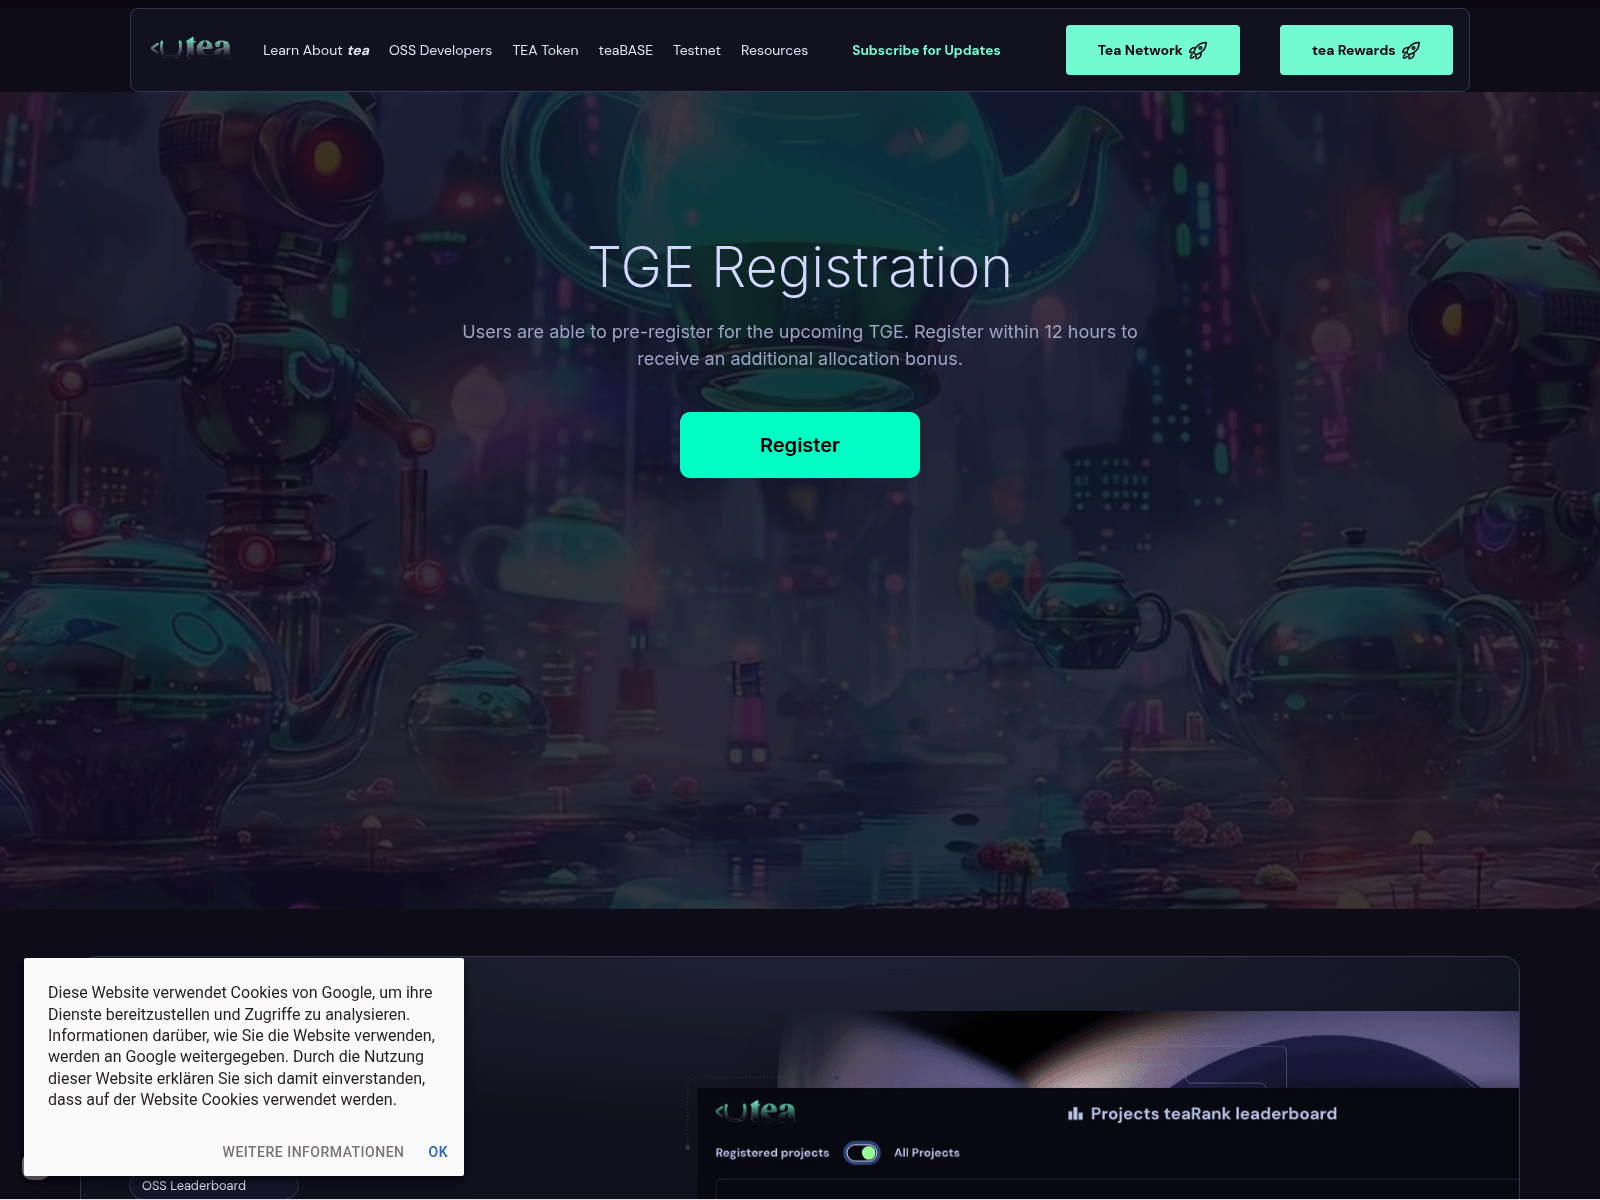
tea-tge.com
tge-capmoneys.com
tge-studioartery.com
tge-terminal.com
tibbir-voting.com
trendsfun-git-temp-devnet-takoprotocol.vercel.app
turtles-vote.net
u11716225.ct.sendgrid.net
virtual-voting.co
virtual-voting.net
vote-aethirsclouds.com
vote-capmoneys.com
vote-hybrafinance.com
vote-navis.com
vote-perleslab.net
vote-quacksai.net
votes-cypher.votings.workers.dev
votes-onbeams.votings.workers.dev
votes-pay.com
voting-intuition.com
voting-labspro.com
voting-pieverses.com
威胁响应 Pipeline
该中心内的每个域名是如何经过验证的,以及已确认的威胁是如何被消除的。 完整流程可视化 →
威胁情报核查— 每个域名都会经过扫描,并与以下内容进行交叉核对:
urlscan.io屏幕截图 · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency 报告Cloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulses互联网档案馆Historical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS 安全 FiltersQuad9 · AdGuard · CleanBrowsingWeb-检查Full surface scan
 crt.sh
全球供应商同步— 已确认的检测结果将推送给 29 家合作伙伴:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantec网站评审AviraCloud detectionAvast / AVGWeb Shield卡巴斯基OpenTIPDr.WebOnline scannerNetcraft关停 APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.报告Hosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust