
Здійснюйте пошук серед відстежуваних доменів та переглядайте збережені докази, виявлені випадки та останні дані щодо доступності.
219,727
Загальна кількість відстежених
213,470
Виявлено VT
91,730
Останнє підключення: активний
127,997
Недоступний під час останньої перевірки
495
VT — у процесі розгляду
How This Attack Works
Solana Drainer threats exploit vulnerabilities in Solana's crypto ecosystem to steal funds. Understanding their operation is crucial for prevention.
STEP 1
Target Identification
Attackers identify potential victims through phishing emails and fake websites.
STEP 2
Phishing Execution
Victims are lured to malicious sites mimicking legitimate platforms, like phantomairdrop.com.
STEP 3
Credential Harvesting
Once on the fake site, victims input sensitive information, believing it to be secure.
STEP 4
Fund Drainage
Attackers utilize harvested credentials to access wallets and drain funds via illicit transactions.
Technical Analysis
Solana Drainer attacks leverage phishing techniques to exploit the Solana blockchain. Attackers often create copycat websites using top TLDs such as .com, .xyz, and .cc, with domains hosted by registrars like Cloudflare, Inc. and PDR Ltd. These sites employ deceptive JavaScript and HTML code to mimic legitimate interfaces, tricking users into entering their private keys or seed phrases. Once credentials are obtained, attackers interact with the Solana blockchain via RPC calls to execute unauthorized transactions. The usage of smart contract functions like `transfer` and `approve` allows attackers to swiftly move funds out of victims' accounts. The infrastructure often involves a network of proxy servers to obfuscate the origin of the attack and make tracing back to the perpetrators difficult.
Real Cases
Phantom Wallet Breach (2023)
$2 million stolen
Attackers created a fraudulent Phantom wallet site to harvest user credentials, resulting in a $2 million theft.
SolUnion Scam (2024)
$1.5 million stolen
Using the domain phantom.solunion.cc, scammers executed a sophisticated phishing attack, stealing $1.5 million in SOL.
VaultBenefits Exploit (2024)
$3 million stolen
A fake airdrop campaign via vaultbenefits.net led to credential compromise and a subsequent $3 million drain.
How to Detect
Unsolicited emails or messages offering free SOL or airdrops
Websites with slight misspellings of legitimate names
Requests for private keys or seed phrases
Suspicious URL structures or unfamiliar TLDs like .xyz or .cc
Lack of HTTPS security on sites claiming to be secure
How to Protect Yourself
1
Verify URLs carefully before interacting
2
Enable multi-factor authentication on your wallet
3
Never share your private key or seed phrase
4
Regularly check transaction histories for unauthorized activity
5
Use official wallet apps and browser extensions
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 2,731 domains tracked for this threat type
Solana Drainer 2,731 domains
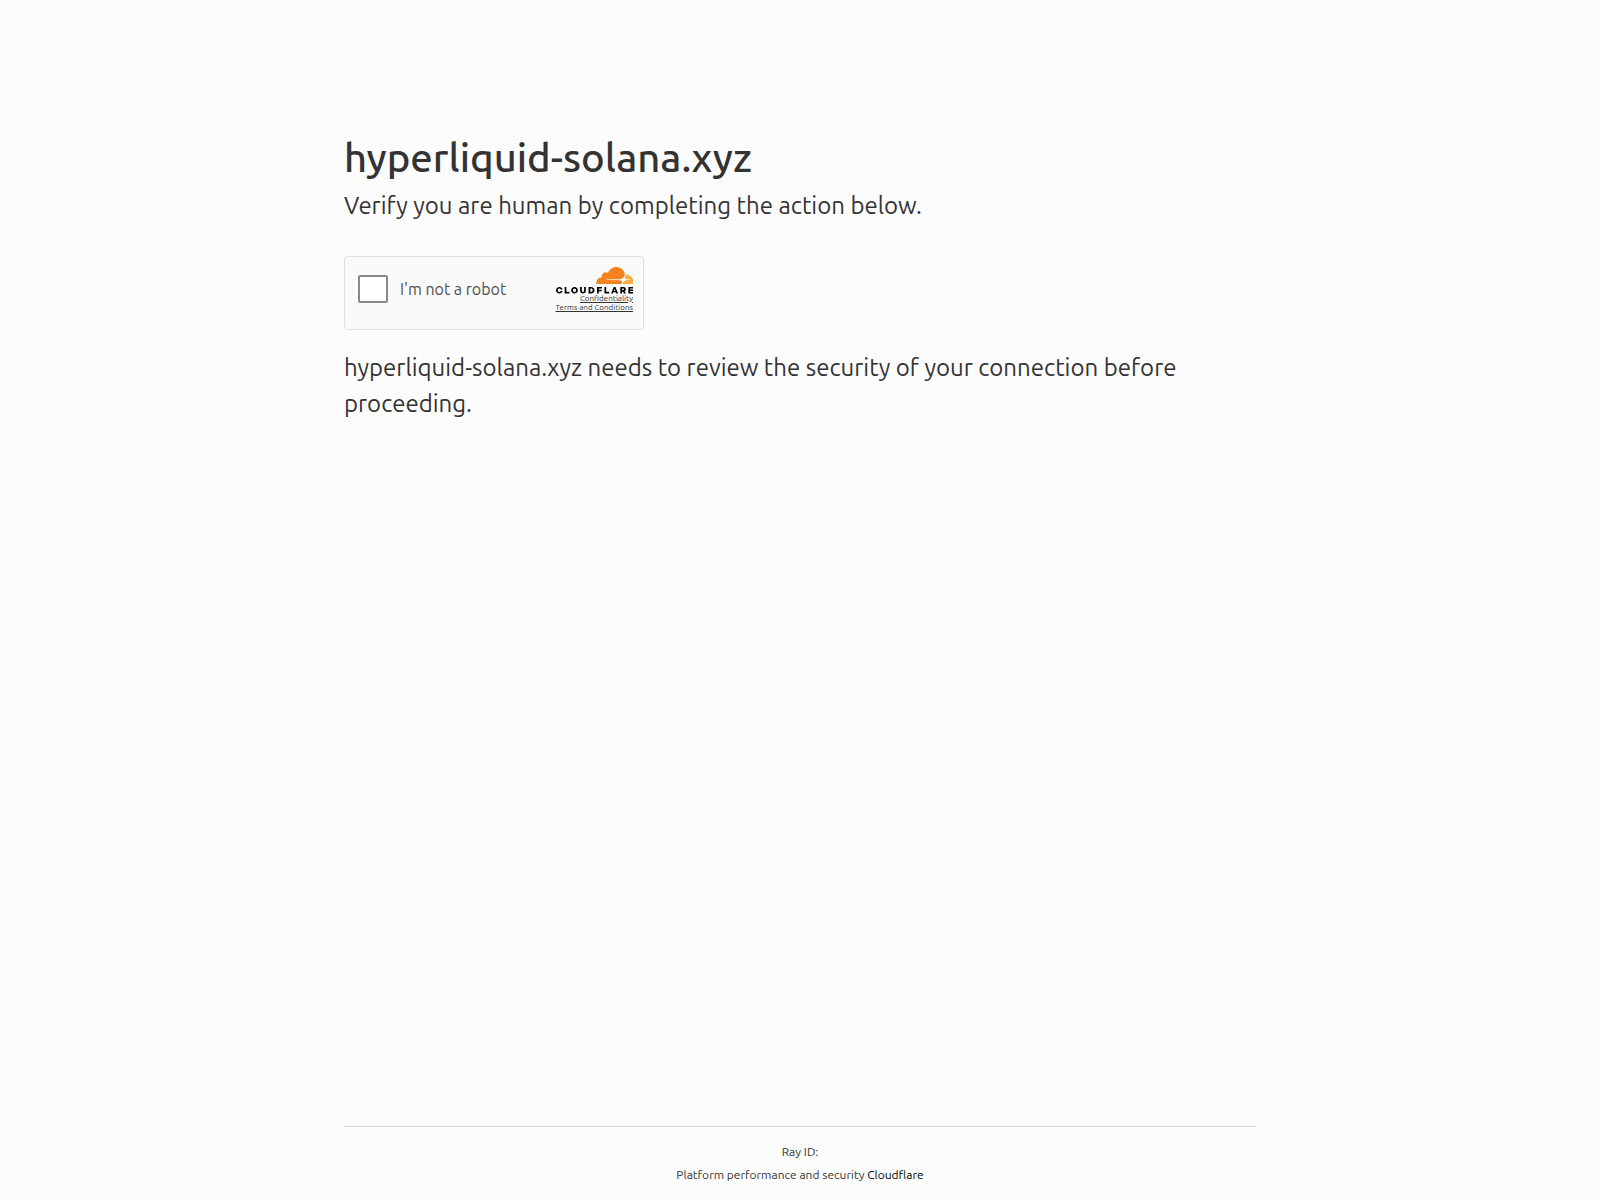
hyperliquid-solana.xyz
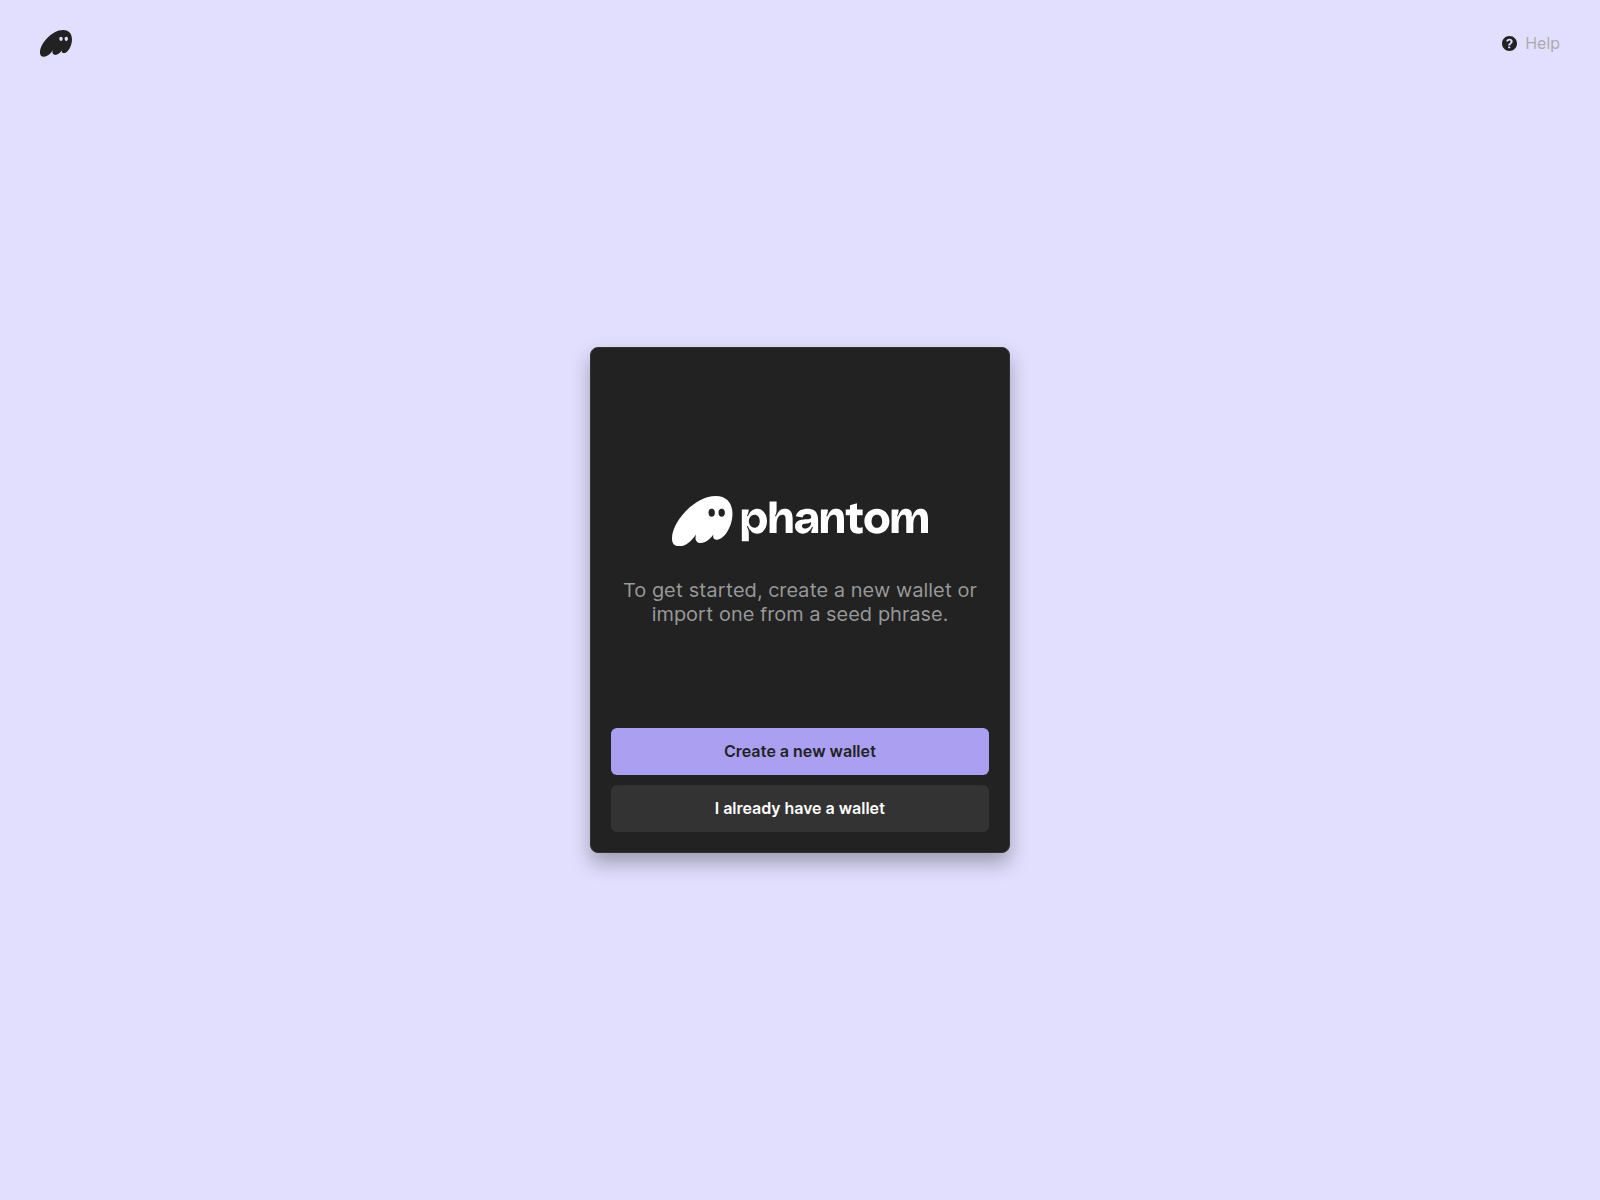
phantomsol.at
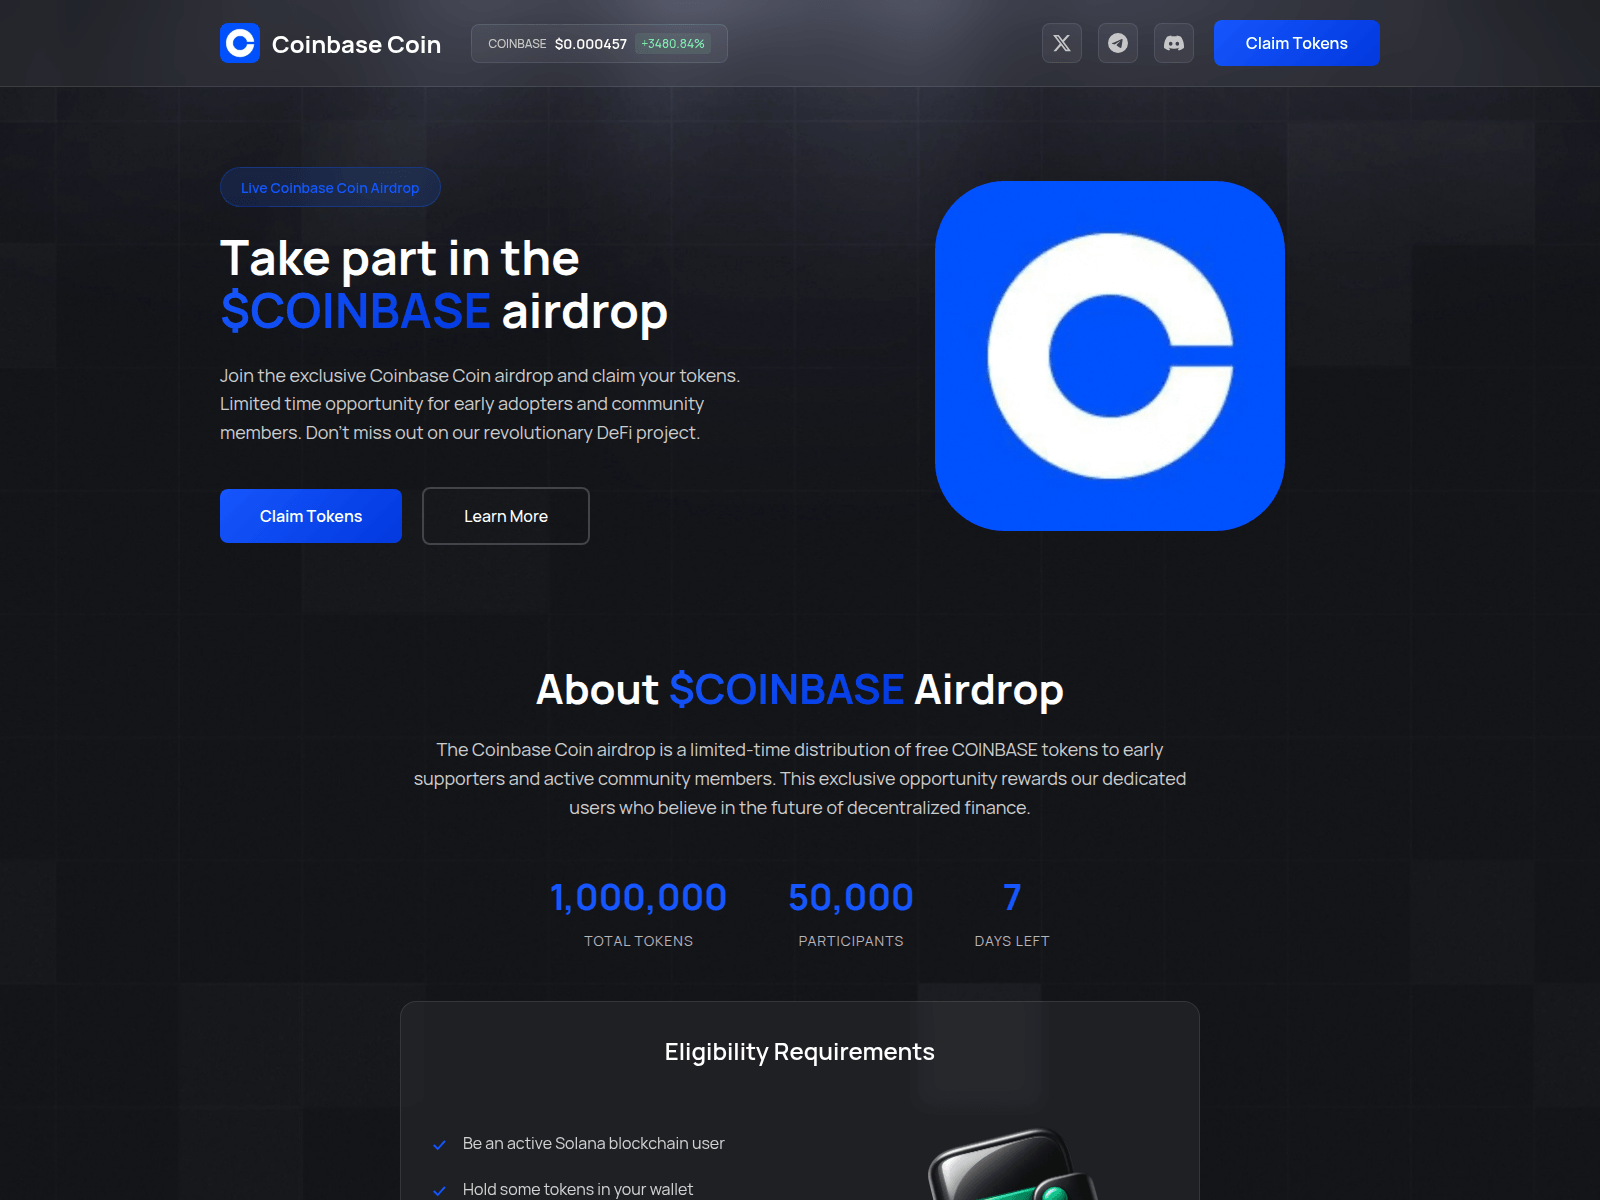
event-coinbase.fun
aa.solcenter.cc
cooldece.com

phantom-solana-guide.com
phantom.solunion.cc
phantom1-wallet.godaddysites.com
raydiumsolutions.xyz
solanasolutions.fun
usa-phantom--auth.webflow.io
coinmultiwallet.com
debank.com-en-us.network
eng-phantom.com
fitechairdrop.xyz
phantomairdrop.com
pp.solcenter.cc
ppp.solshelter.cc
sol-blast.com
sol-reward.icu
webphantom.online
abb.soluniverse.cc
app-solstice.com
eligibility-zkpass.org
jup-agf.world
jup-token.world
jupbox.net
panducoin.com
phan.solcenter.cc
phantom-activate.com
phantom-wallet.to
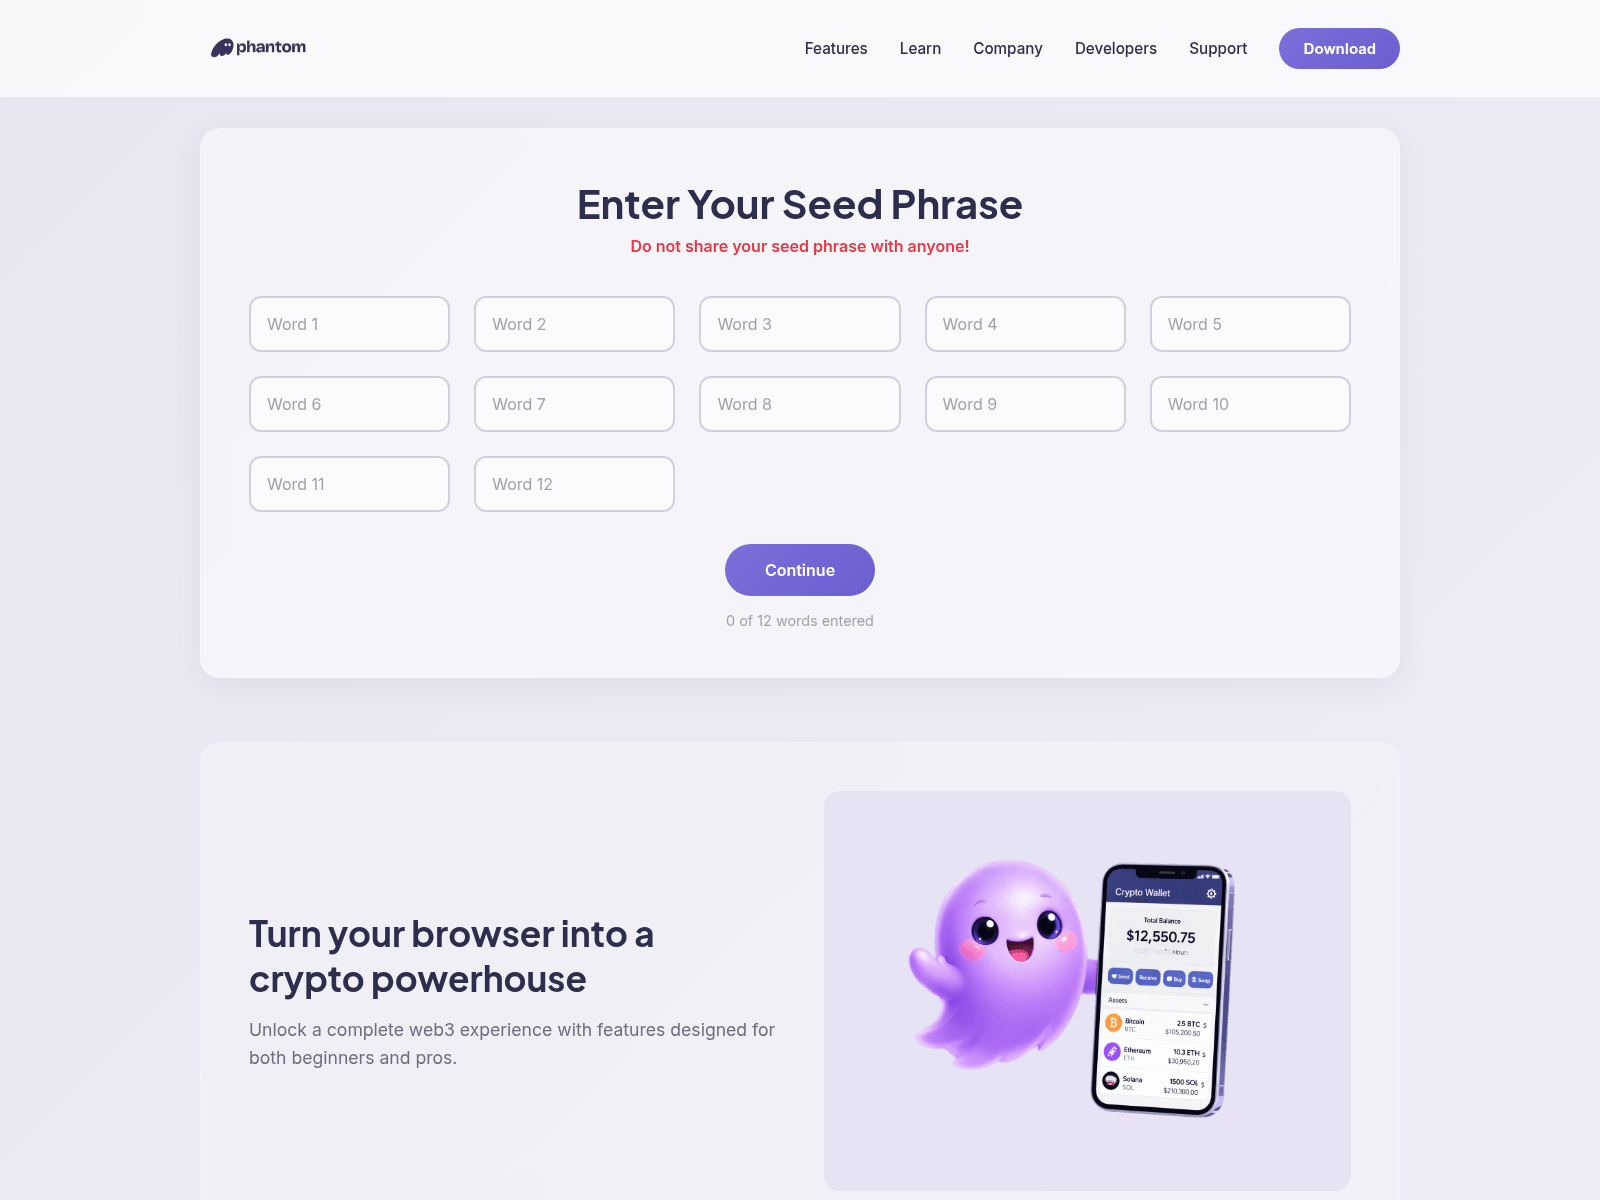
phantomsecure.net
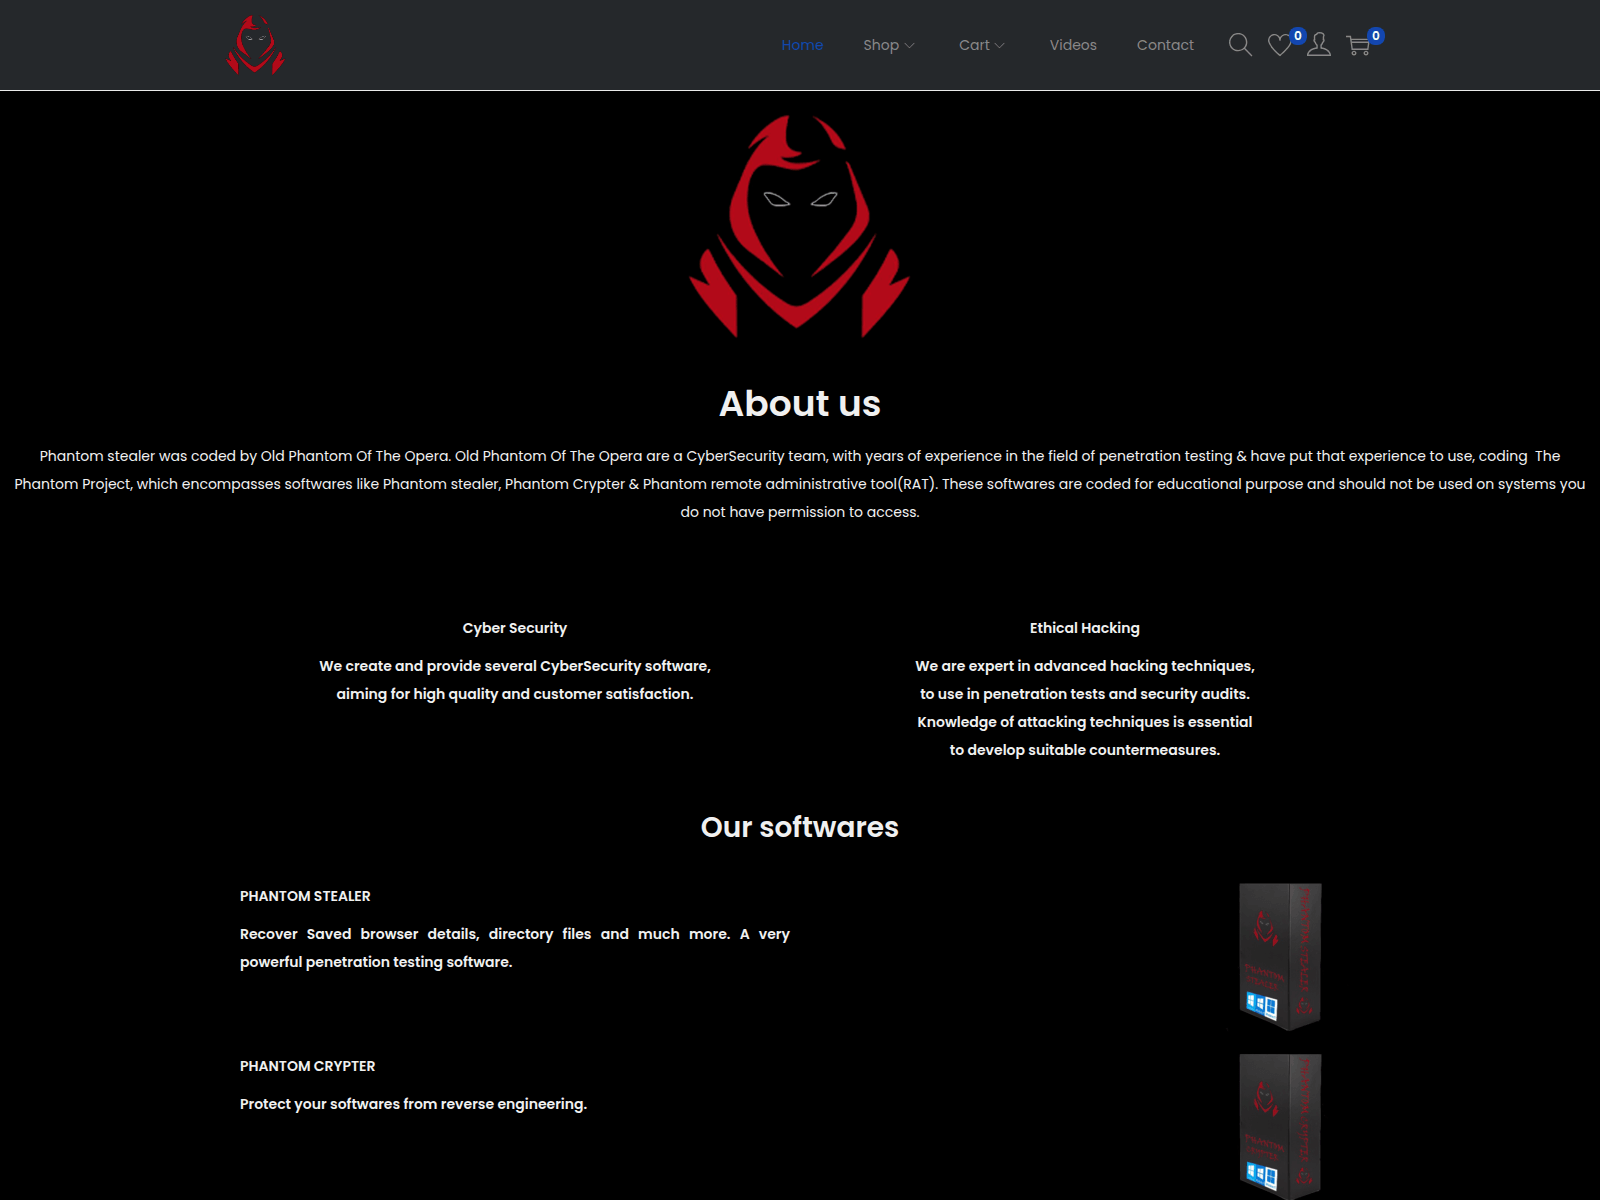
phantomsoftwares.site
phantomvoted.com
phantomwallet-solana.godaddysites.com
phanton.pro
raydium-solana.network
receipt526823.rest
solana-qr-code.com
solanamoblle.digital
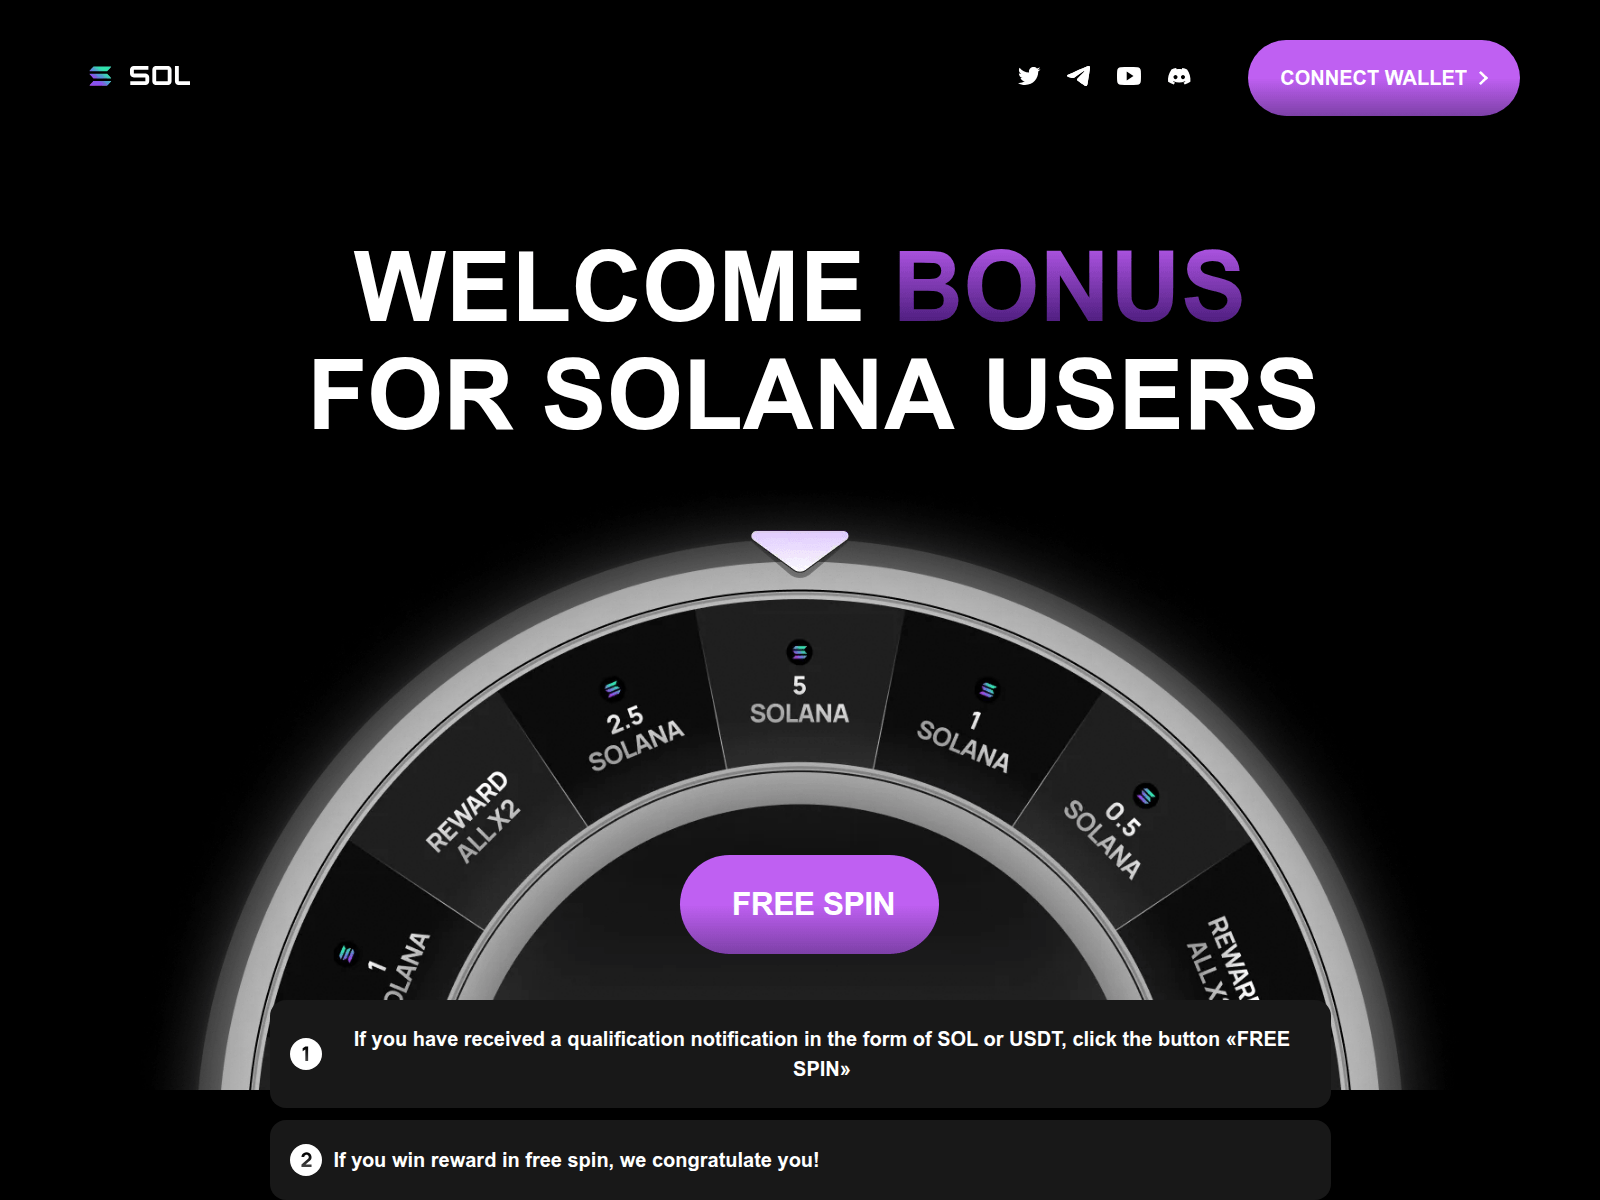
sunsolix.live
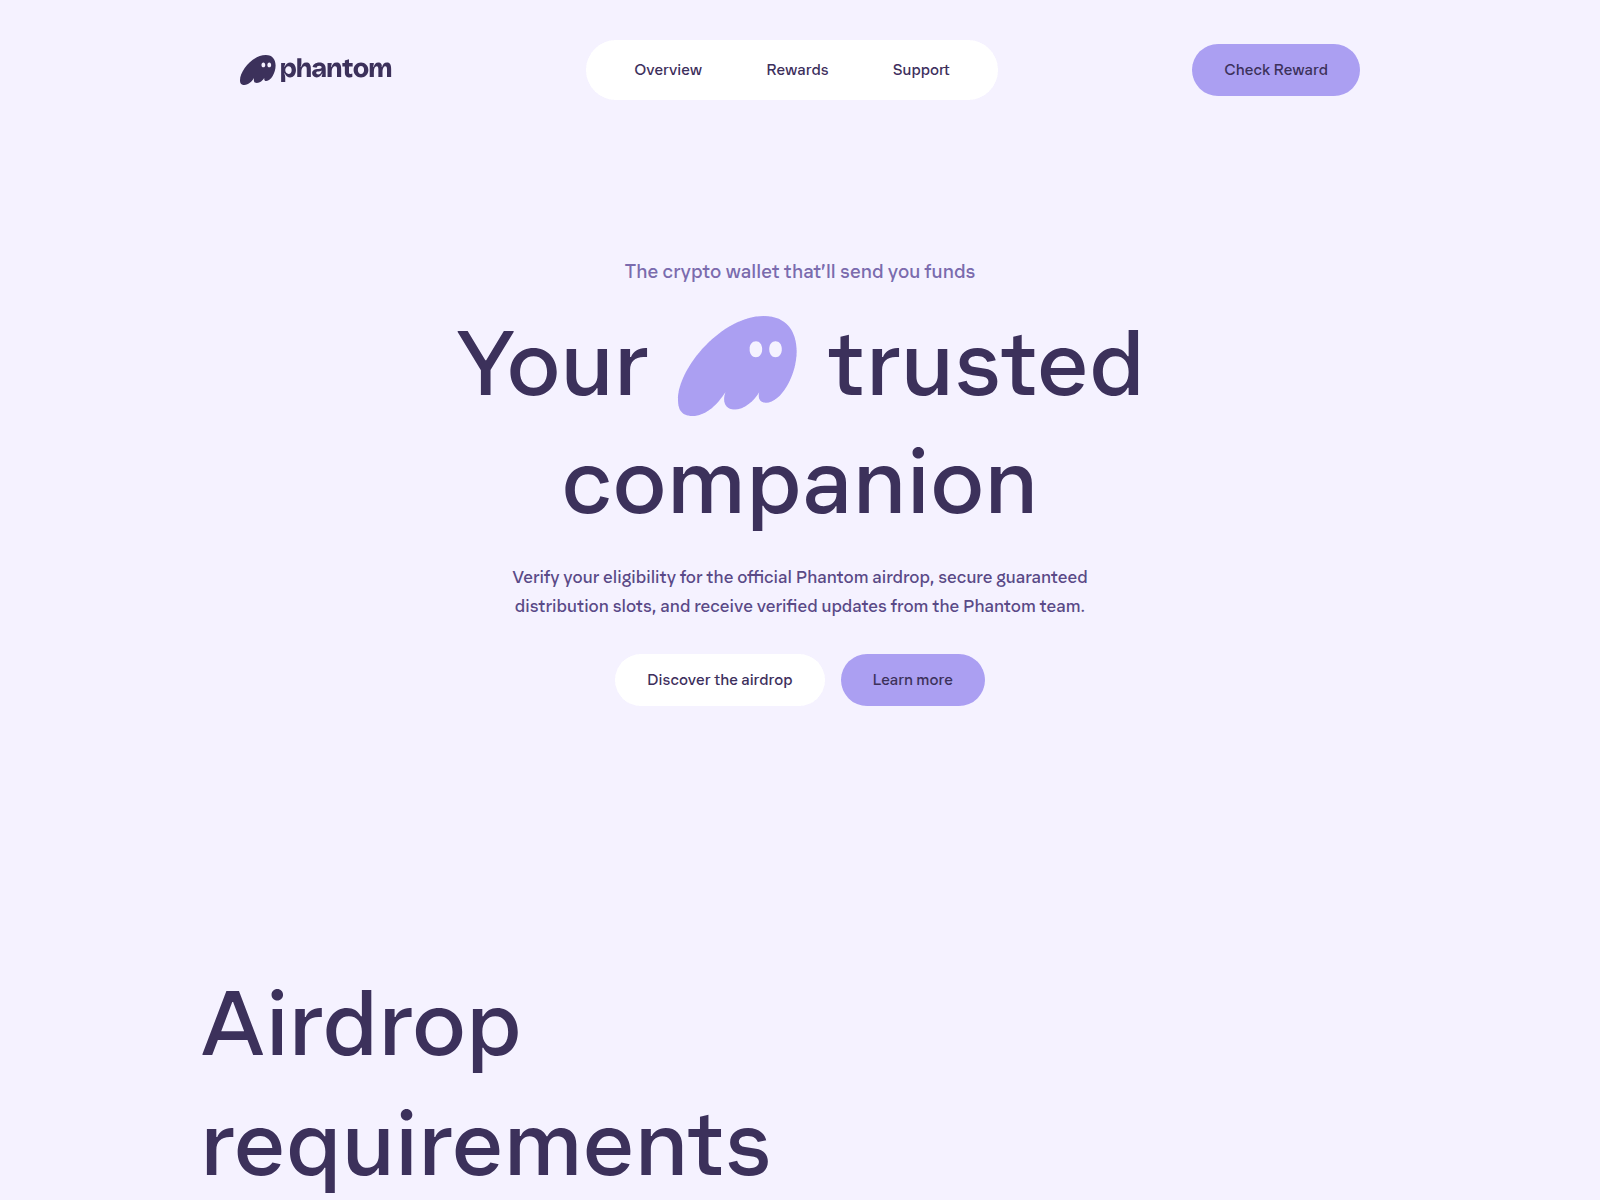
ab.sol-lib.cc
airtm.solunion.cc
based.soldex.trade
buyusaaccounts.com
derpo.icu
fartcoin-promo.com
financialnetwork.live
jup-yt.live
jupiterchecker.us
jupjhot.icu
max-ultraphantomx.click
mistclaw-phantom.com
nodefisolver.xyz
pancakeswapsfi.org
phantom-my.at
phantom.baby
phantomqe.com
phantomrt.com
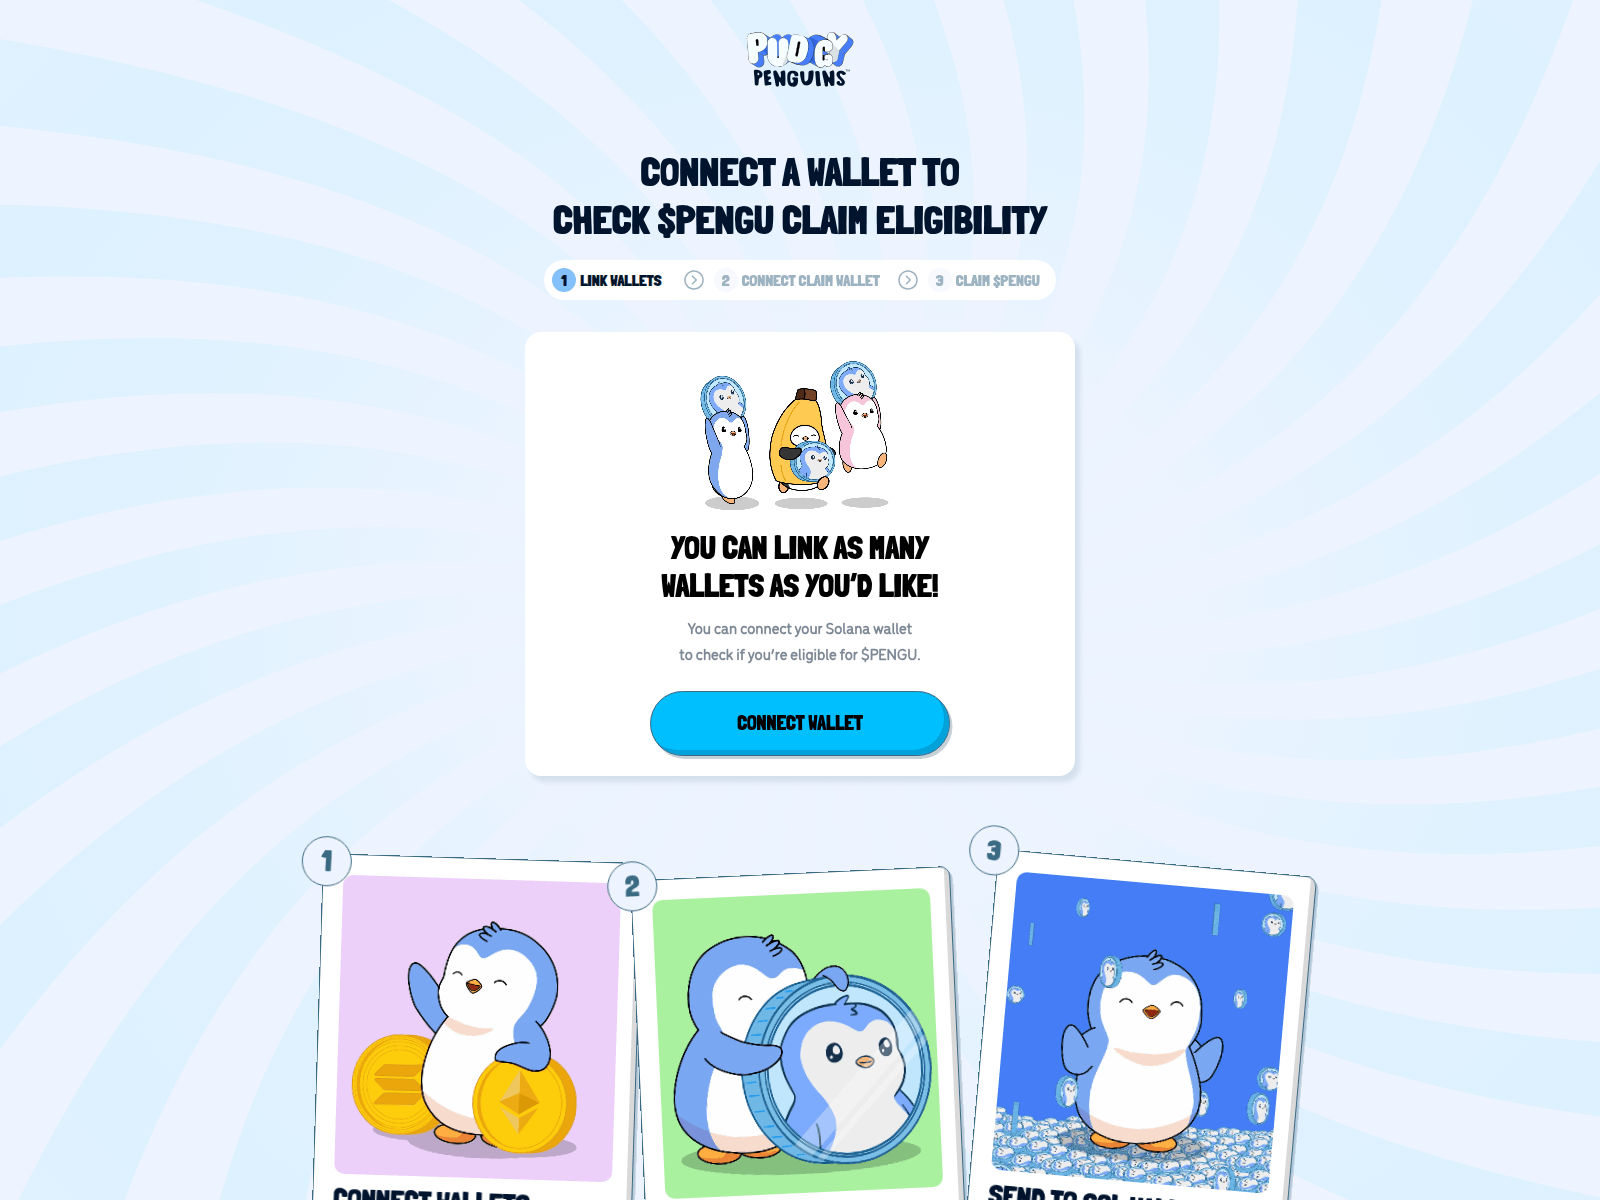
pudgyzpenguins.com
pumpsolana.fun
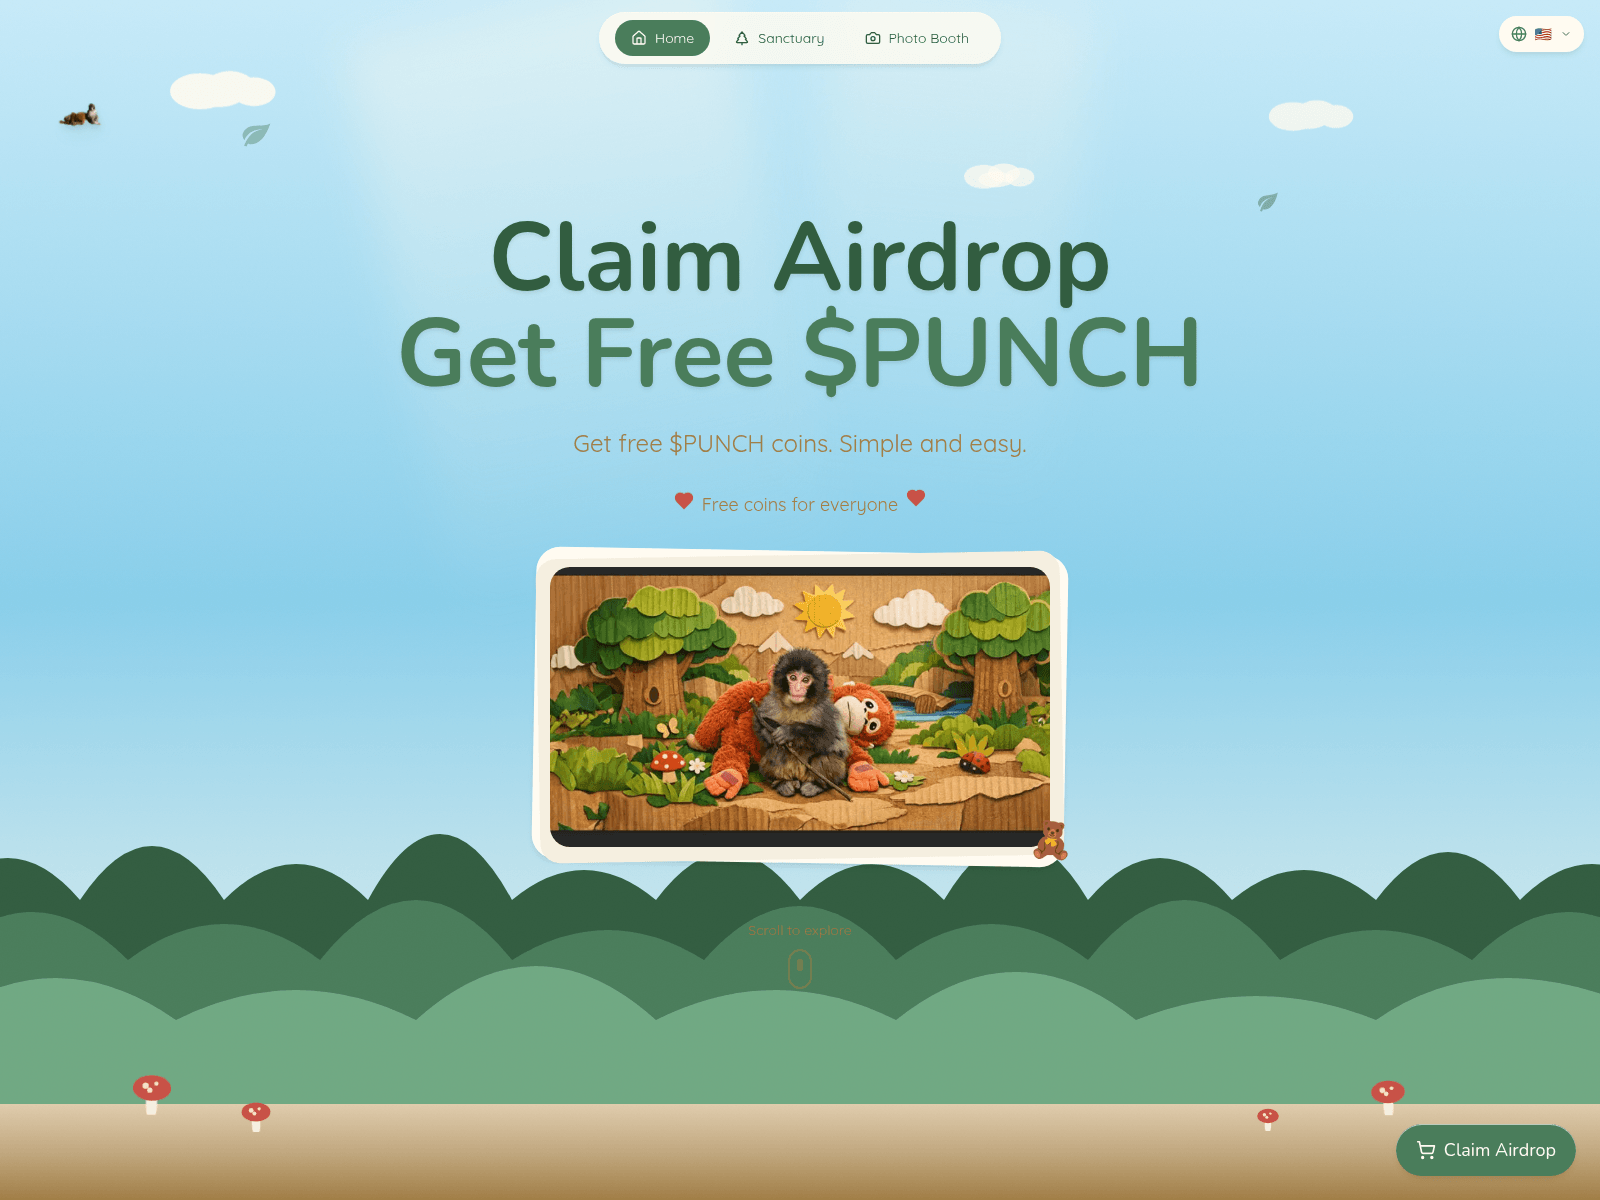
punchtoken.net
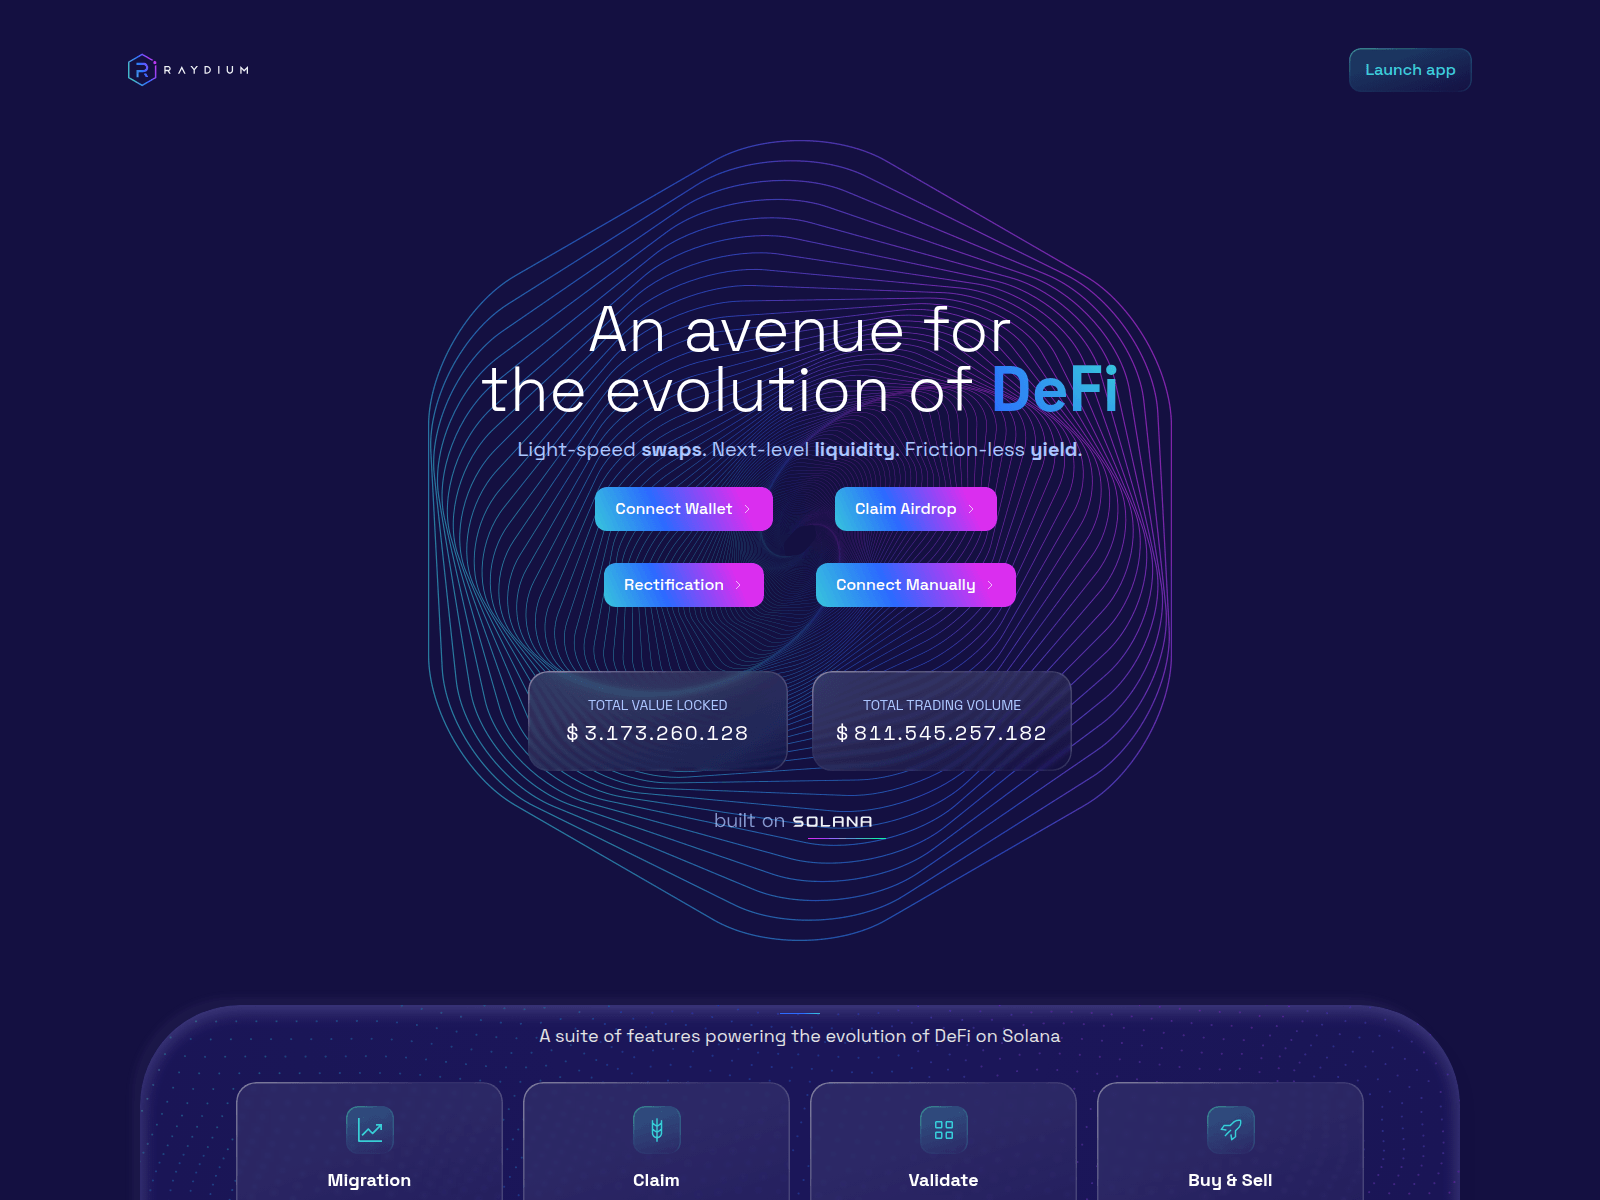
raydium-concentrated.world
return.solcenter.cc
sol-space.pro
solana-testingun.lol
solgoblin.world
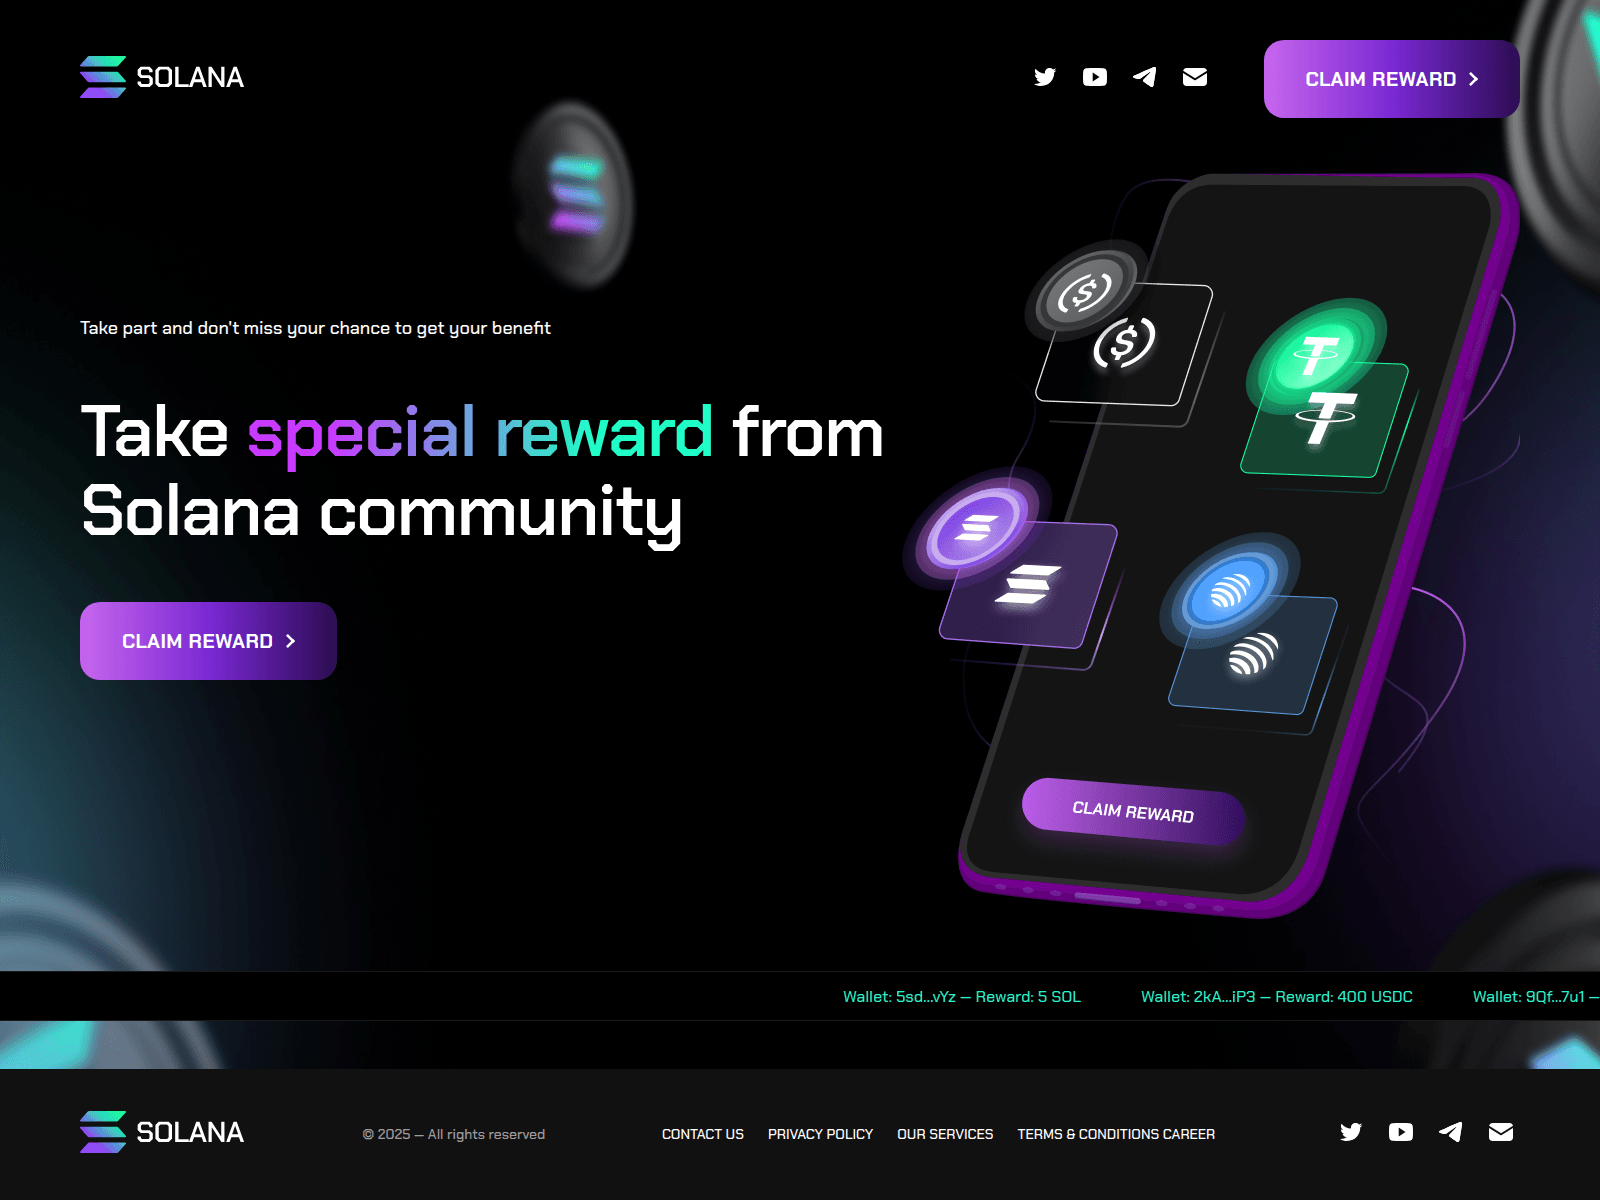
sols-drops.com
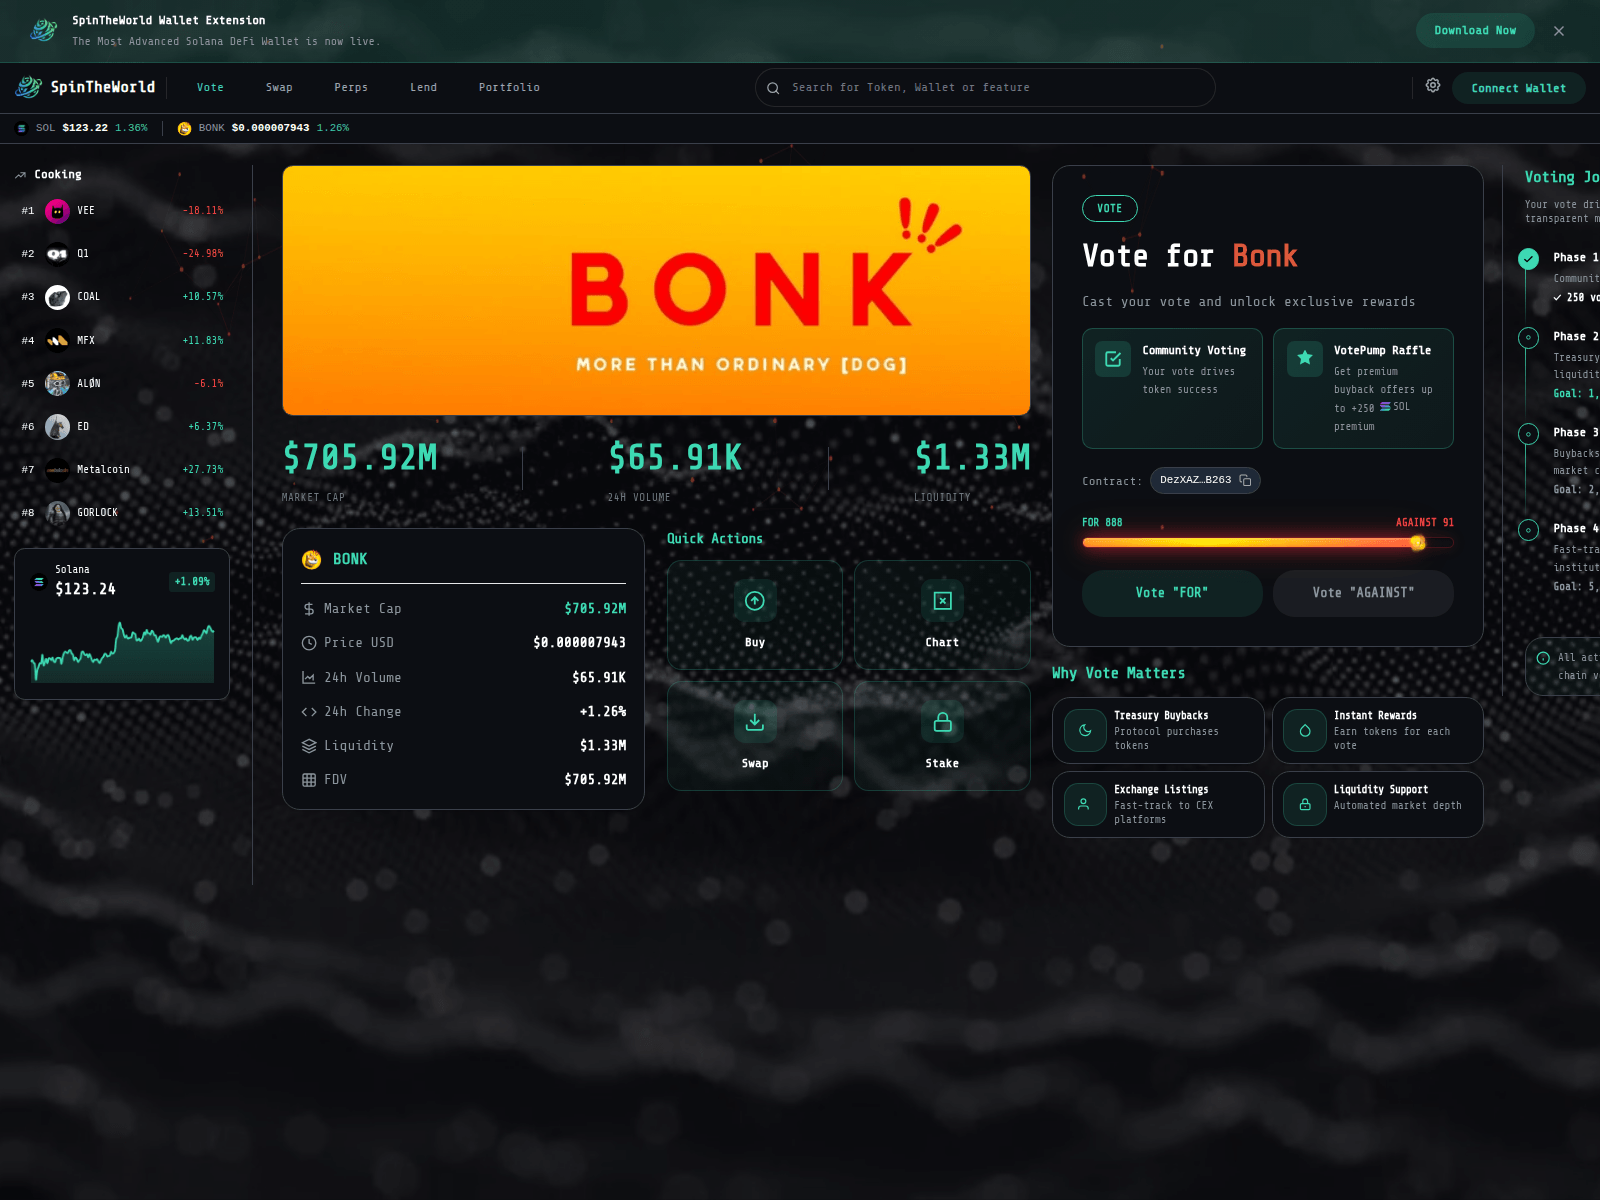
spinthe.world
start-io-phantomwallet.pages.dev
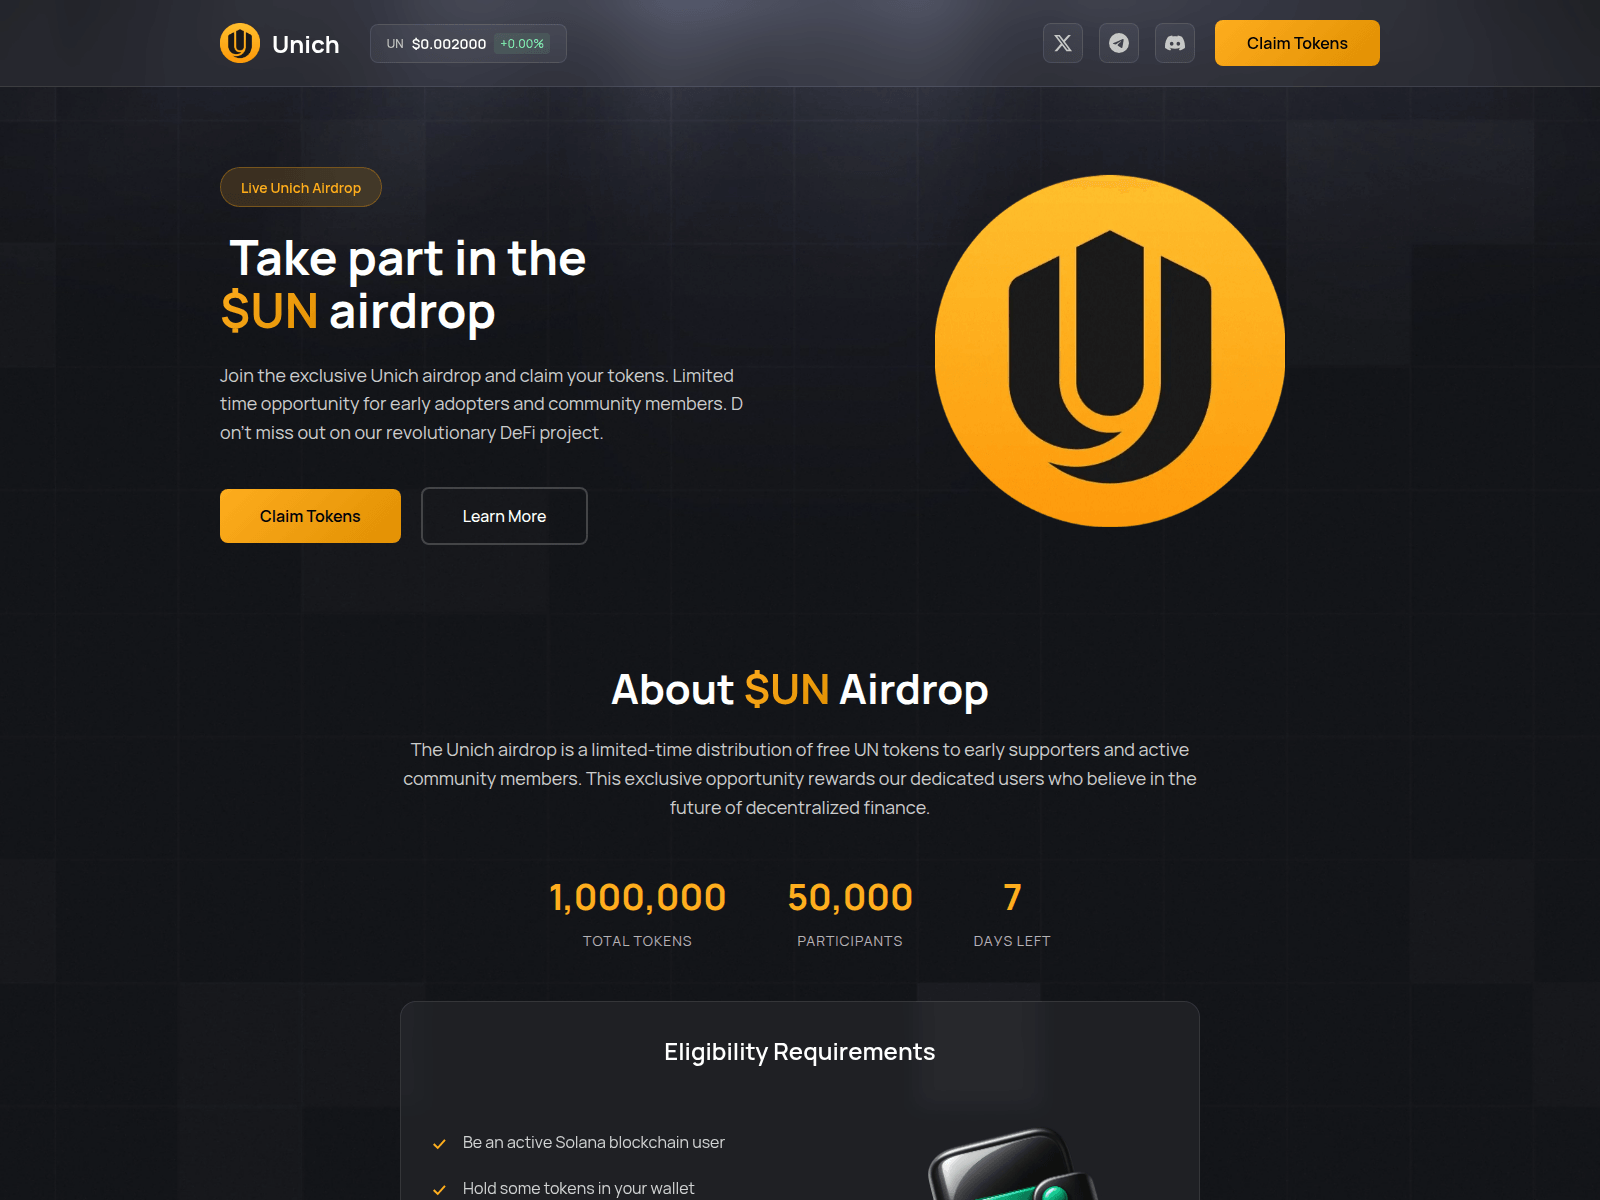
unich-gateway.click
visionfundsfindept.com
wallettconnect.com
wowcoin.bet
zypha.xyz
58035.tax
78418.tax
79597.my
79700.tax
90197.tax
92493.my
air.sol-shelter.cc
app-solflare.com
apps-phantom.com

av.phantom.lu
blocksmartwallet.live
bullishcoin.solhq.cc
calabiapp.com
card-phantom.com
dappportal.live
dappsol.live
dappsolchain.com
Процес реагування на загрози Pipeline
Як перевіряється кожен домен у цьому хабі та як нейтралізуються підтверджені загрози. Повна візуалізація технологічного процесу →
Перевірки даних про загрози— кожен домен проходить сканування та перехресну перевірку щодо:
urlscan.ioЗнімок екрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ЗвітCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безпека FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПеревіритиFull surface scan
 crt.sh
Глобальна синхронізація постачальників— підтверджені випадки передаються 29 партнерам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОгляд сайтуAviraCloud detectionAvast / AVGWeb Shield«Касперський»OpenTIPDr.WebOnline scannerNetcraftЛіквідація APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ЗвітHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust