FBI IC3
Amerika Birleşik Devletleri'nde internet bağlantılı suçları bildirin
Federal tips line1-800-CALL-FBI

“Messenger”
teletfaj.com — İçerik kullanılamıyor. Marka kimliğine bürünme: Unknown; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 10/91 (ADMINUSLabs, alphaMountain.ai, BitDefender, CyRadar, ESET); Google Safe Browsing flagged; Spamhaus DBL_SPAM; PhishDestroy score 100/100. Kayıt kuruluşu: NiceNIC.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.
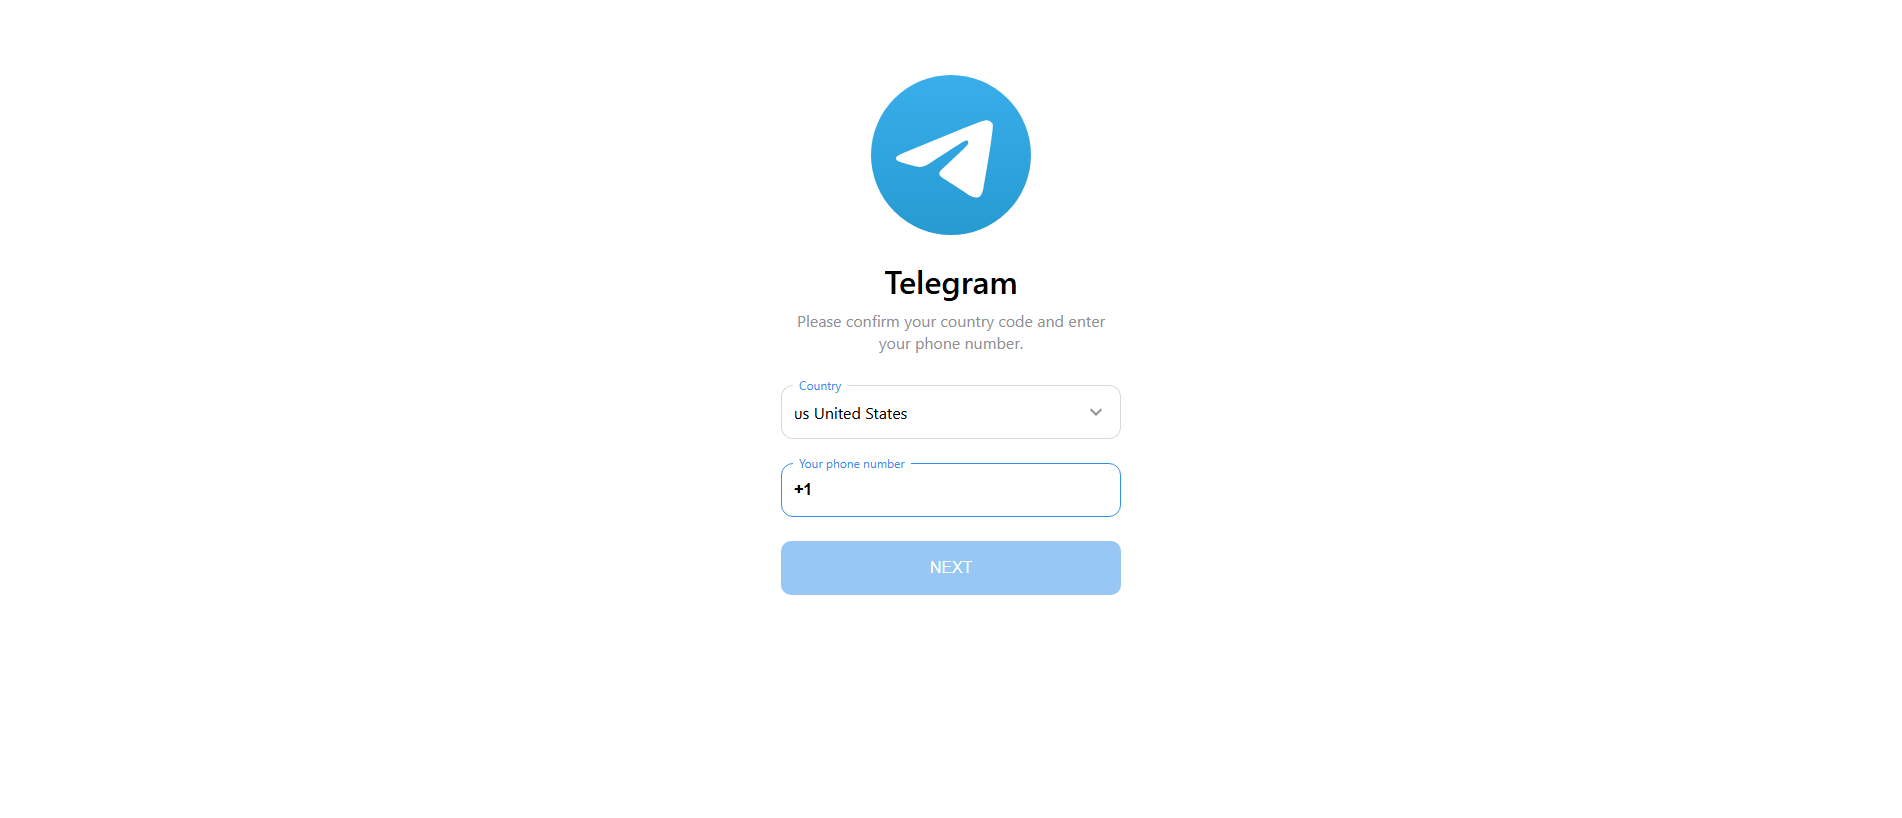
This domain is actively engaged in credential phishing targeting users of messaging platforms. Analysis indicates the site mimics legitimate Messenger login interfaces to deceive visitors into submitting account credentials, which are then captured by threat actors for unauthorized access or further exploitation. The fraudulent nature is reinforced by its use of social engineering techniques, as confirmed by its inclusion in security blocklists and Google Safe Browsing’s SOCIAL_ENGINEERING category. Infrastructure analysis reveals multiple technical indicators supporting this assessment. The domain was registered on May 24, 2026, through NICENIC INTERNATIONAL GROUP CO., LIMITED, a registrar frequently associated with high-risk domains. It resolves to the IP address 27.124.47.186 and is currently flagged by 10 out of 95 security vendors on VirusTotal. Additionally, the SSL certificate is falsely labeled as belonging to Telegram, a tactic designed to increase perceived legitimacy. The domain appears on two security blocklists, including InversionDNS and BLP-Malware, further confirming its malicious intent. Users who have visited www.teletfaj.com or entered credentials on the site should take immediate action to mitigate risk. First, change passwords for any accounts accessed or entered on the site, prioritizing email and financial services. Enable multi-factor authentication where available to prevent unauthorized access. Monitor accounts for suspicious activity, such as unrecognized logins or messages sent without consent. If credentials were reused across multiple platforms, update passwords on all affected services. Finally, report the incident to relevant security teams or fraud reporting channels to assist in broader threat mitigation efforts.

Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: dns_error: raw=dns_error; via=local_dns_prefilter
 (RU)
PhishDestroy Investigation
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Infrastructure map · teletfaj.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Bu kaynak IP, birden fazla kimlik avı alanını barındırır; altyapı, kampanyalar arasında paylaşılabilir.
These domains also target Bilinmiyor users. View all Unknown threats →
Part of the Bilinmiyor phishing campaign. View all campaign domains →
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
 wrencapstead.digital
 zywa-capovin.pro
 xtradegrok36.com
 chat-trade-ai.live
 clawnchtoken.com
 primarkpolska.pl