VirusTotal
21 / 93
Bildir


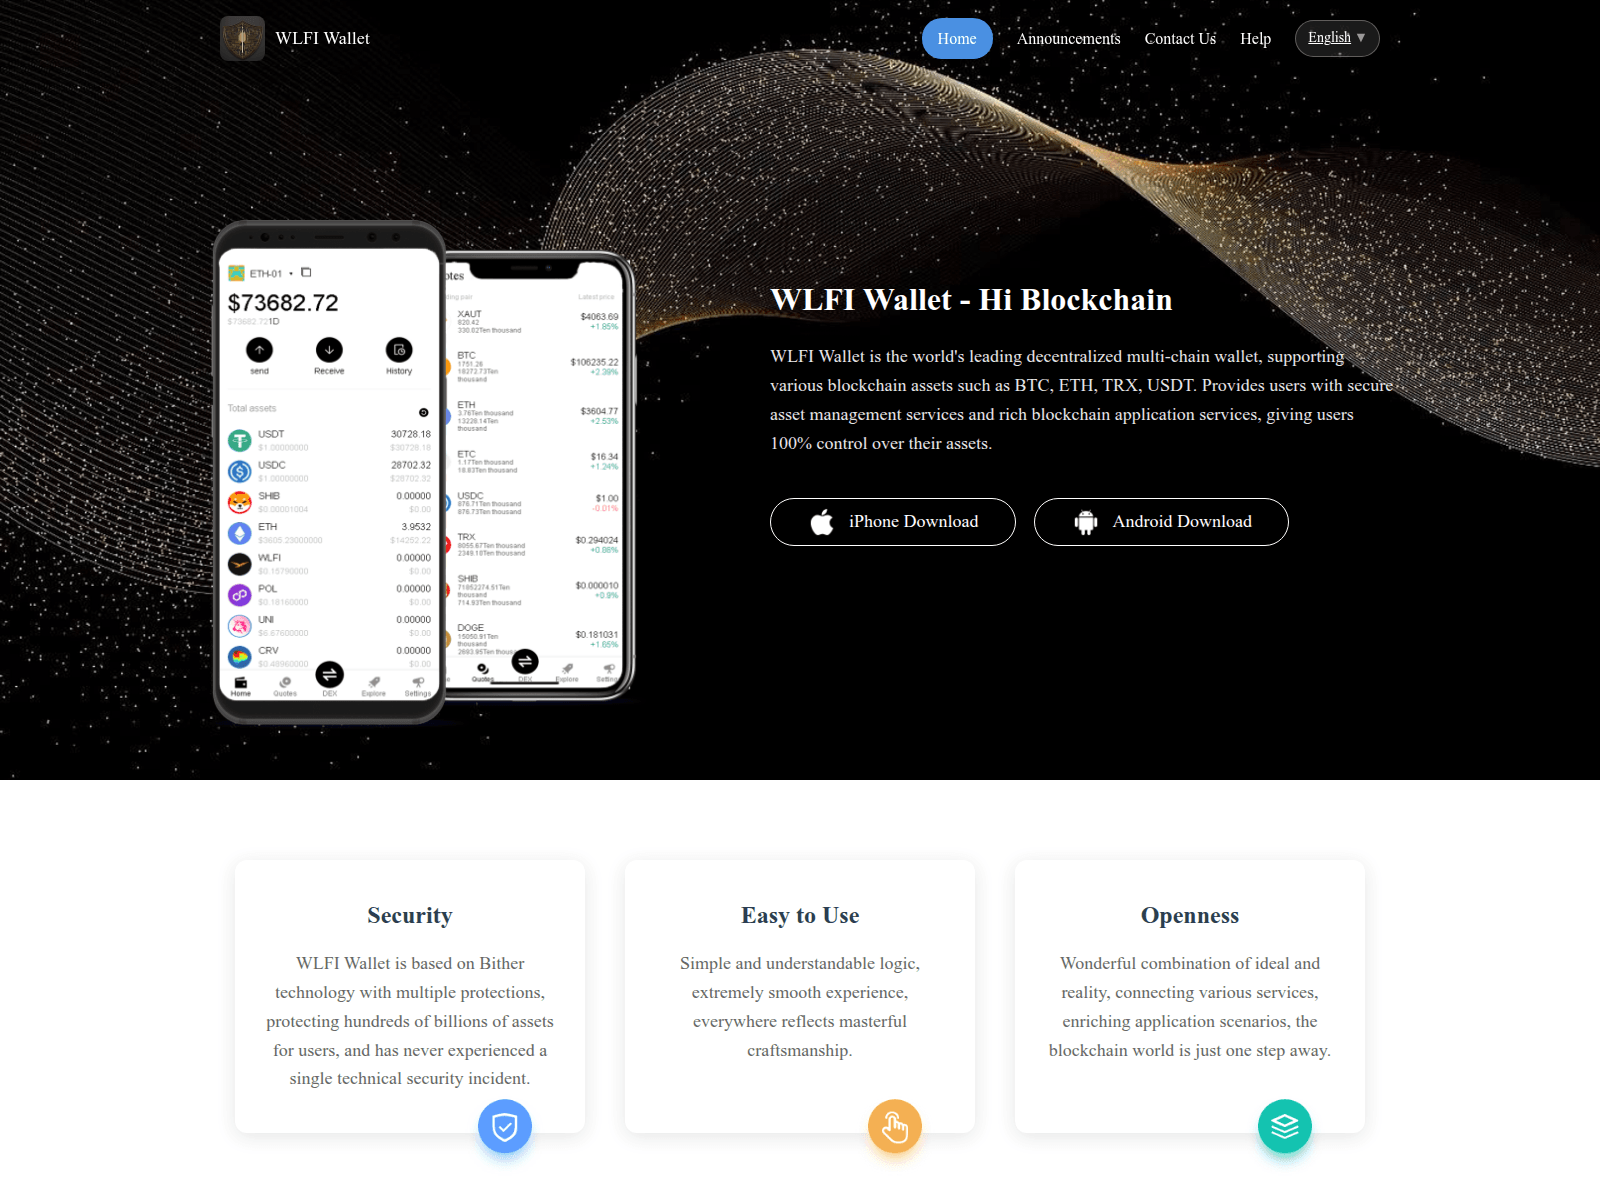
“WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co”
wlfiwallst.com — İçerik kullanılamıyor. Marka kimliğine bürünme: Arbitrum; Dolandırıcılık türü: Crypto Scam. Kanıt özeti: VirusTotal 21/93 (ADMINUSLabs, ChainPatrol, alphaMountain.ai, BitDefender, Certego); URLQuery 6 alerts; PhishDestroy score 95/100.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | wlfiwallst.com |
malicious | Sinkholed |
| OpenDNS | wlfiwallst.com |
phishing | Phishing Block |
| DigiCert UltraDNS | wlfiwallst.com |
malicious | Sinkholed |
| Hagezi Threat Feed | wlfiwallst.com |
malicious | Sinkholed |
| DNS4EU | wlfiwallst.com |
malicious | Sinkholed |
| Quad9 DNS | wlfiwallst.com |
malicious | Sinkholed |
The domain wlfiwallst.com is assessed as a high-risk brand impersonation threat, specifically targeting the Arbitrum brand. Analysis indicates that the domain is designed to deceive users into believing they are interacting with legitimate Arbitrum services, potentially leading to credential theft or other malicious activities.
Infrastructure analysis reveals that wlfiwallst.com resolves to the IP address 207.148.125.217, which is located in Singapore (SG) and is part of the AS20473 network operated by The Constant Company, LLC. The domain was created on February 21, 2026, and does not have an SSL certificate. This domain appears on three security blocklists and has been flagged by 21 out of 95 security vendors on VirusTotal, indicating a moderate to high level of suspicion among the security community. The page title, 'WLFI Wallet - Secure Your Cryptocurrencies with WLFI.co,' further supports the impersonation of Arbitrum services. The domain is currently offline, having been taken down by security measures implemented by PhishDestroy, MetaMask, and SEAL.
To mitigate the risks associated with brand impersonation, users are advised to verify the domain and URL of any website claiming to offer services related to Arbitrum or similar brands. Employing multi-factor authentication (MFA) and using reputable security software can help prevent unauthorized access to accounts. Additionally, users should report any suspicious activity to their security teams or to the official Arbitrum support channels to ensure timely action and prevent further spread of the impersonation campaign.
Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.
Tarayıcı notu: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='wlfiwallst.com', port=80): Max retries exceeded with url: / (Caused by NewConnectionError(
Location describes the IP network.
10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
28 kayıtlı benzer alan adı
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Template-based draft · optional AI wording assistance requires separate consent
Her bir satır, bir etki alanının bu ana bilgisayara bağlanmasının bir nedenini gösterir. Düğüm boyutu, VirusTotal adresindeki algılamaları gösterir; kesikli çizgili düğümler ise halihazırda çevrimdışı durumdadır. Tam listeler aşağıda yer almaktadır.
Bu sunucuyla aynı favicon hash değeri veya aynı sayfa başlığı.
Başka bir kimlik avı alanı, bu kaynak IP'yi (olası ortak konumlu altyapı) paylaşıyor.
Bu alan adları, Arbitrum kullanıcılarını da hedef almaktadır. Tüm “Arbitrum” tehditlerini görüntüle →
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin