FBI IC3
Amerika Birleşik Devletleri'nde internet bağlantılı suçları bildirin
Federal tips line1-800-CALL-FBI

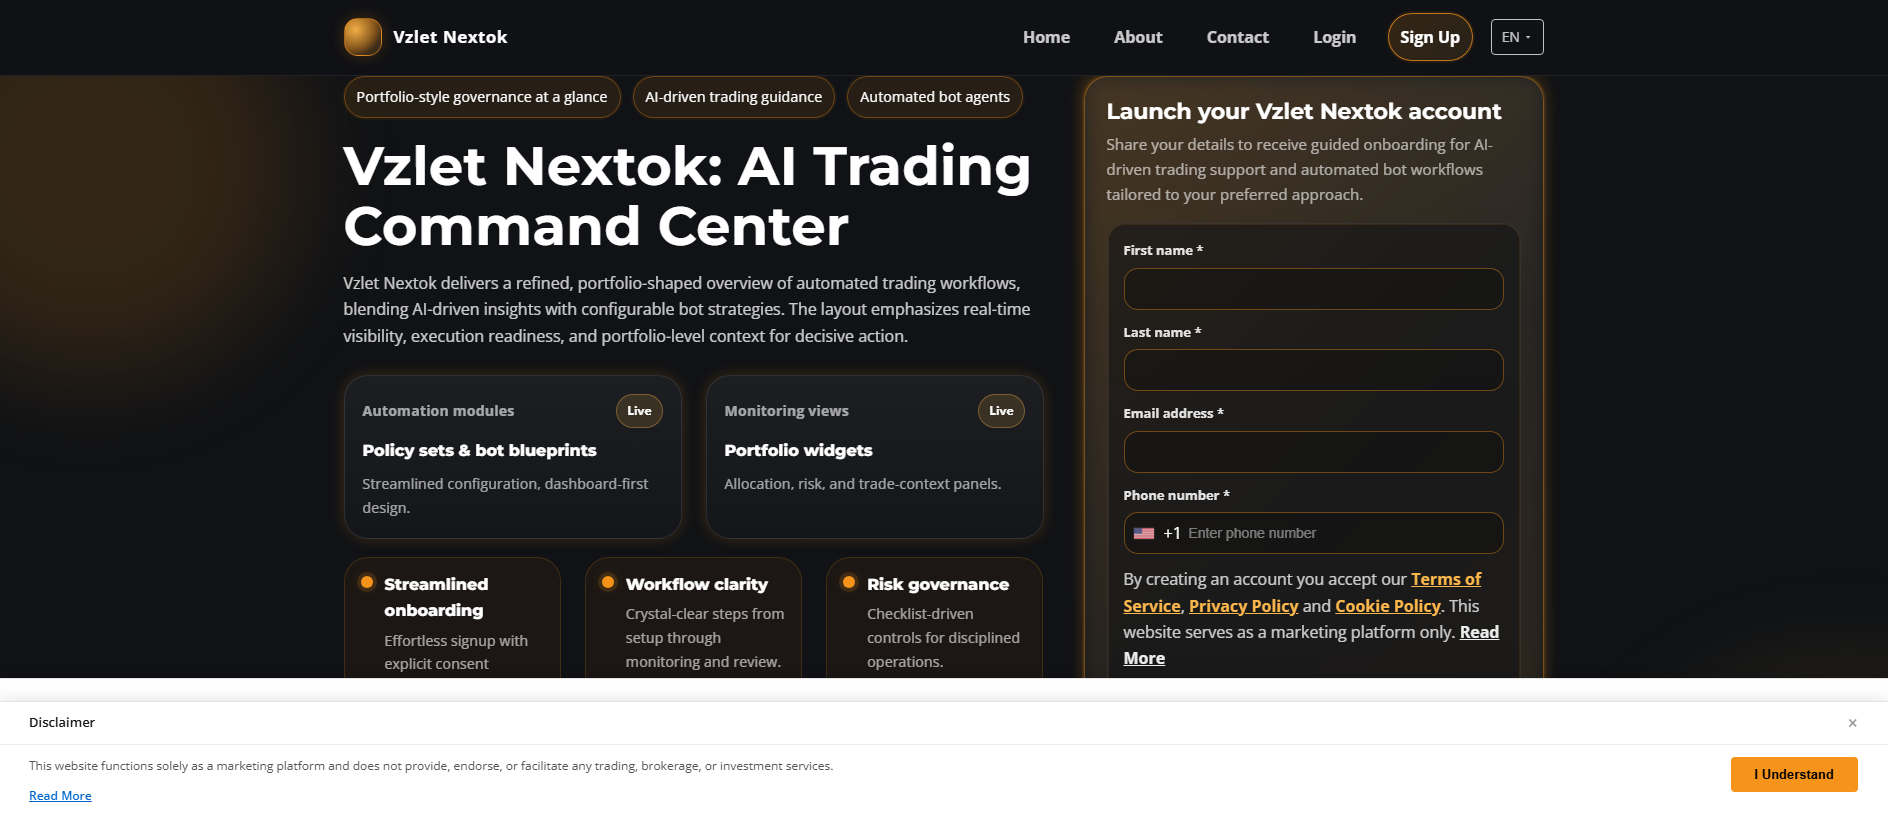
“Vzlet Nextok | AI Trading Platform | Official Website”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@netim.net.
The latest stored availability evidence still shows the domain reachable; 33 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
vzletnextok.sbs — Bilinen son aktif (HTTP 200). Marka kimliğine bürünme: Unknown; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 15/89 (alphaMountain.ai, BitDefender, CRDF, CyRadar, ESET); CF Radar malicious; PhishDestroy score 100/100. Kayıt kuruluşu: NETIM.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.
PhishDestroy first observed vzletnextok.sbs on Sep 21, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Vzlet Nextok | AI Trading Platform | Official Website”. Page analysis recorded additional brand references to Across, Argent, and Foundation. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and Cloudflare Radar. VirusTotal recorded 15 detections among 89 engines: alphaMountain.ai, BitDefender, CRDF, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Lionic, Seclookup, SOCRadar, Sophos, VIPRE, Webroot on Sep 23, 2026 at 04:26 UTC. Cloudflare Radar classified the hostname as malicious and assigned the categories malware and security threats; its verdict timestamp was not retained. Non-positive and contextual checks: AlienVault OTX listed 5 community pulse references (not vendor detections) on Sep 23, 2026 at 04:27 UTC. The separate external-blocklist snapshot contained no matches on Sep 23, 2026 at 02:20 UTC. URLQuery recorded no positive detection; no observation timestamp was retained. Google Safe Browsing returned no flag on Sep 23, 2026 at 04:26 UTC. URLScan completed without a malicious verdict (score 0) on Sep 22, 2026 at 03:30 UTC.
HTTP 200 was recorded on Sep 23, 2026 at 02:23 UTC. Registration records for the domain list NETIM as the registrar and Feb 17, 2026 as the creation date. At collection time, the hostname resolved to 185.62.58.101 on AS62370 (Snel.com B.V.). The recorded endpoint location is Rotterdam, NL. The stored server header is ESF. DOM analysis on Sep 21, 2026 at 22:20 UTC returned 98/100. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists ZeroSSL GmbH / ZeroSSL ECC DV SSL CA 2 as the certificate issuer with validity through Nov 22, 2026; checked Sep 21, 2026 at 19:02 UTC.
The content indicators and 2 positive source findings support the current Unknown-themed impersonation classification.

185.62.58.101. Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.
Tarayıcı notu: alive_content: raw=ok; http=200; via=https_proxy
 (GB)

The linked repository preserves daily zone observations across seven ShortDot-operated TLDs, including registration volume and abuse-related indicators. This registry context is supporting background and is not an independent detection for the domain in this report.
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Google PageSpeed Insights — mobile performance audit of vzletnextok.sbs · checked Sep 21, 2026
PD-20260921-A19C8D Recipient: abuse@netim.net Registrar: Netim SARL (France) Policy Violations: “Strict abuse policy classifying phishing, malware, fraud and botnet activity as illegal domain use; registrar may suspend or terminate affected domains.” Applicable Laws: French Penal Code Art.323-1+; EU Directive 2013/40/EU
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Her bir satır, bir etki alanının bu ana bilgisayara bağlanmasının bir nedenini gösterir. Düğüm boyutu, VirusTotal adresindeki algılamaları gösterir; kesikli çizgili düğümler ise halihazırda çevrimdışı durumdadır. Tam listeler aşağıda yer almaktadır.
Bu sunucuyla aynı favicon hash değeri veya aynı sayfa başlığı.
Bu kaynak IP, birden fazla kimlik avı alanını barındırır; altyapı, kampanyalar arasında paylaşılabilir.
Bu alan adları, Unknown kullanıcılarını da hedef almaktadır. Tüm “Unknown” tehditlerini görüntüle →
Aynı kayıt kuruluşu aracılığıyla kaydedilmiştir. Bir kayıt kuruluşu, birbiriyle hiçbir bağlantısı olmayan milyonlarca müşteriye hizmet verdiğinden, bu durum bir bağlantıyı kanıtlamaktan ziyade raporları bir araya getirmektedir.
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin