VirusTotal
5 / 89
Bildir
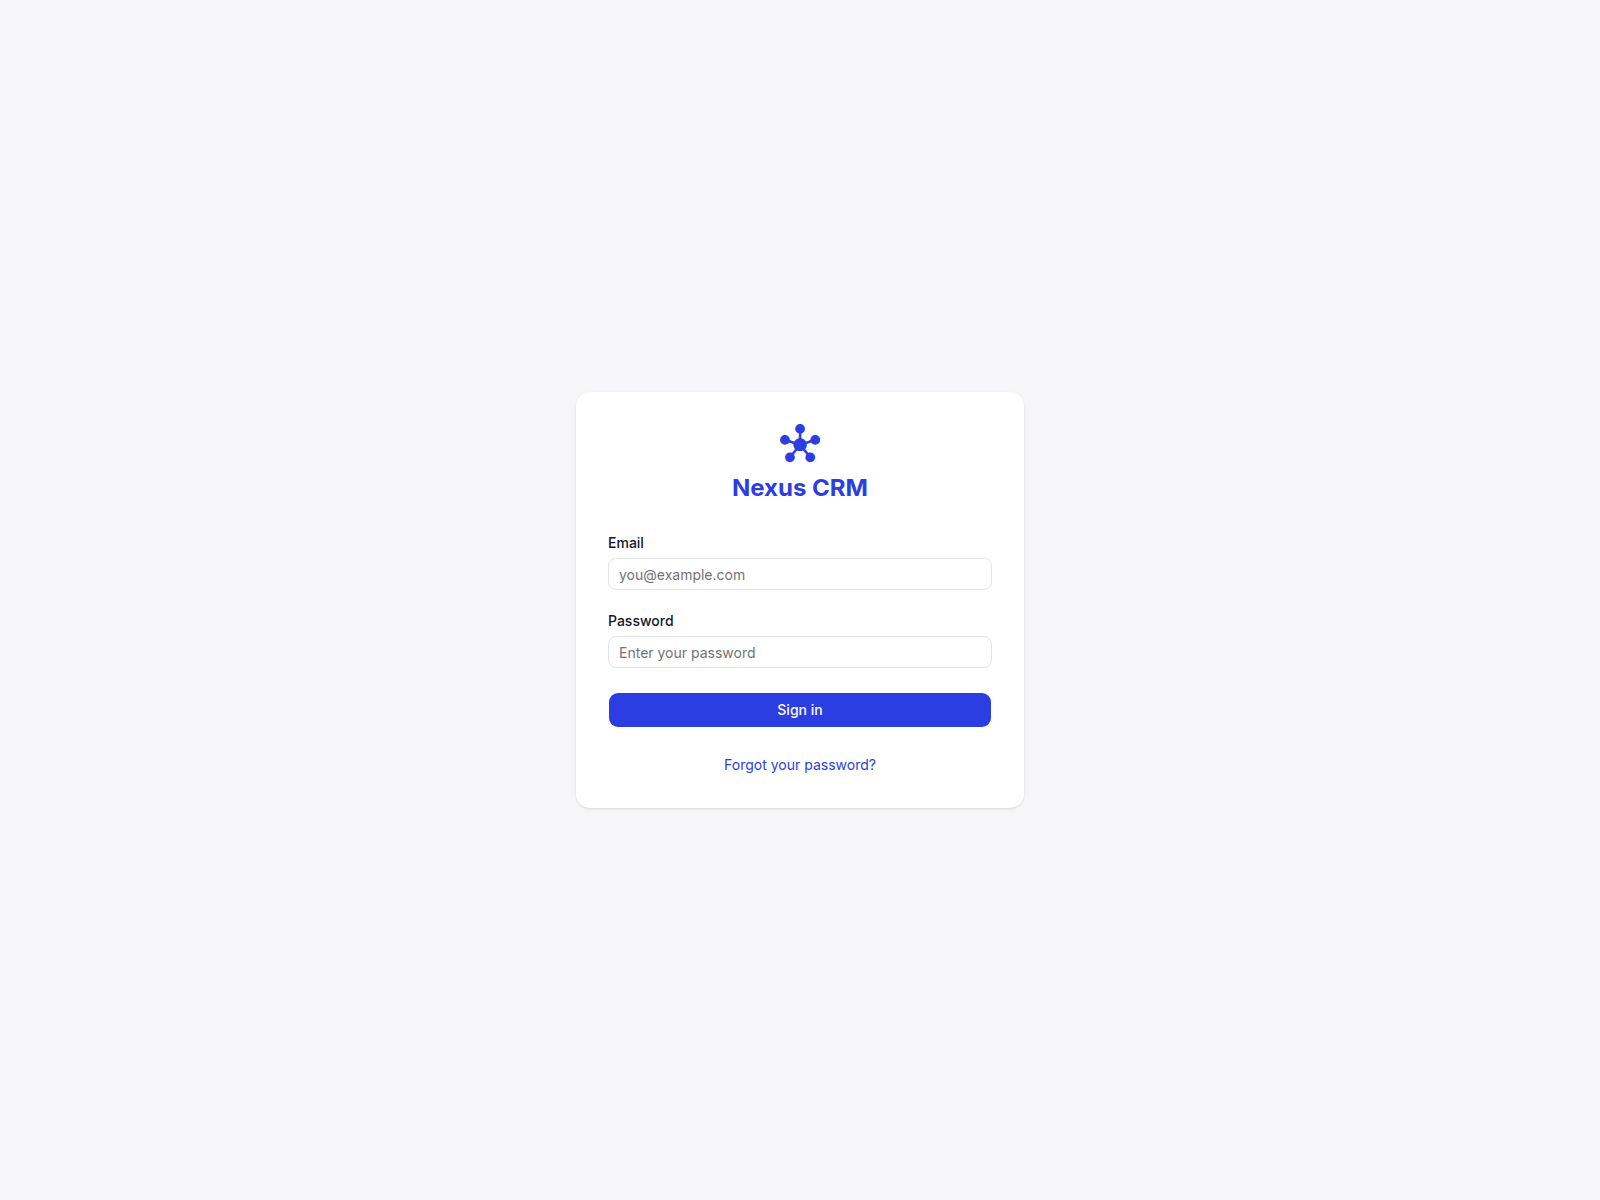
“Nexus CRM”
visioncrm.co — Bilinen son aktif (HTTP 307). Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 5/89 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar); PhishDestroy score 88/100.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Analysis of visioncrm.co as of August 04, 2026 indicates an active phishing domain targeting corporate customer-relationship management (CRM) credentials. The domain is flagged by two independent security vendors on VirusTotal and appears on one operational blocklist, resulting in an elevated risk classification. Infrastructure review shows the domain was registered through a privacy-protected registrar, obscuring beneficial ownership; no hosting ASN or geolocation data is currently available.
The site returns a valid HTTP 200 response, suggesting an operational phishing page, though the exact page title and content remain unanalysed. Defenders should treat visioncrm.co as a confirmed phishing asset and block it at the DNS and proxy layers.
Security teams are advised to monitor authentication logs for connections originating from this domain and review any recent CRM-related credential submissions for compromise. Given the limited vendor detection at this stage, additional scrutiny of related infrastructure (subdomains, SSL certificates, or co-hosted IPs) may reveal further malicious activity.
Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.
Tarayıcı notu: redirect: raw=redirect_307; http=307; via=https_proxy; location=/login
Location describes the IP network.
3a321de4c6a619f4e4ce843ba83973d8fb836a22c9a672cbe9f2e4514bcfa1c6Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of visioncrm.co · checked Aug 4, 2026
9 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Template-based draft · optional AI wording assistance requires separate consent
Her bir satır, bir etki alanının bu ana bilgisayara bağlanmasının bir nedenini gösterir. Düğüm boyutu, VirusTotal adresindeki algılamaları gösterir; kesikli çizgili düğümler ise halihazırda çevrimdışı durumdadır. Tam listeler aşağıda yer almaktadır.
Bu sunucuyla aynı favicon hash değeri veya aynı sayfa başlığı.
Bu kaynak IP, birden fazla kimlik avı alanını barındırır; altyapı, kampanyalar arasında paylaşılabilir.
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin