FBI IC3
Amerika Birleşik Devletleri'nde internet bağlantılı suçları bildirin
Federal tips line1-800-CALL-FBI

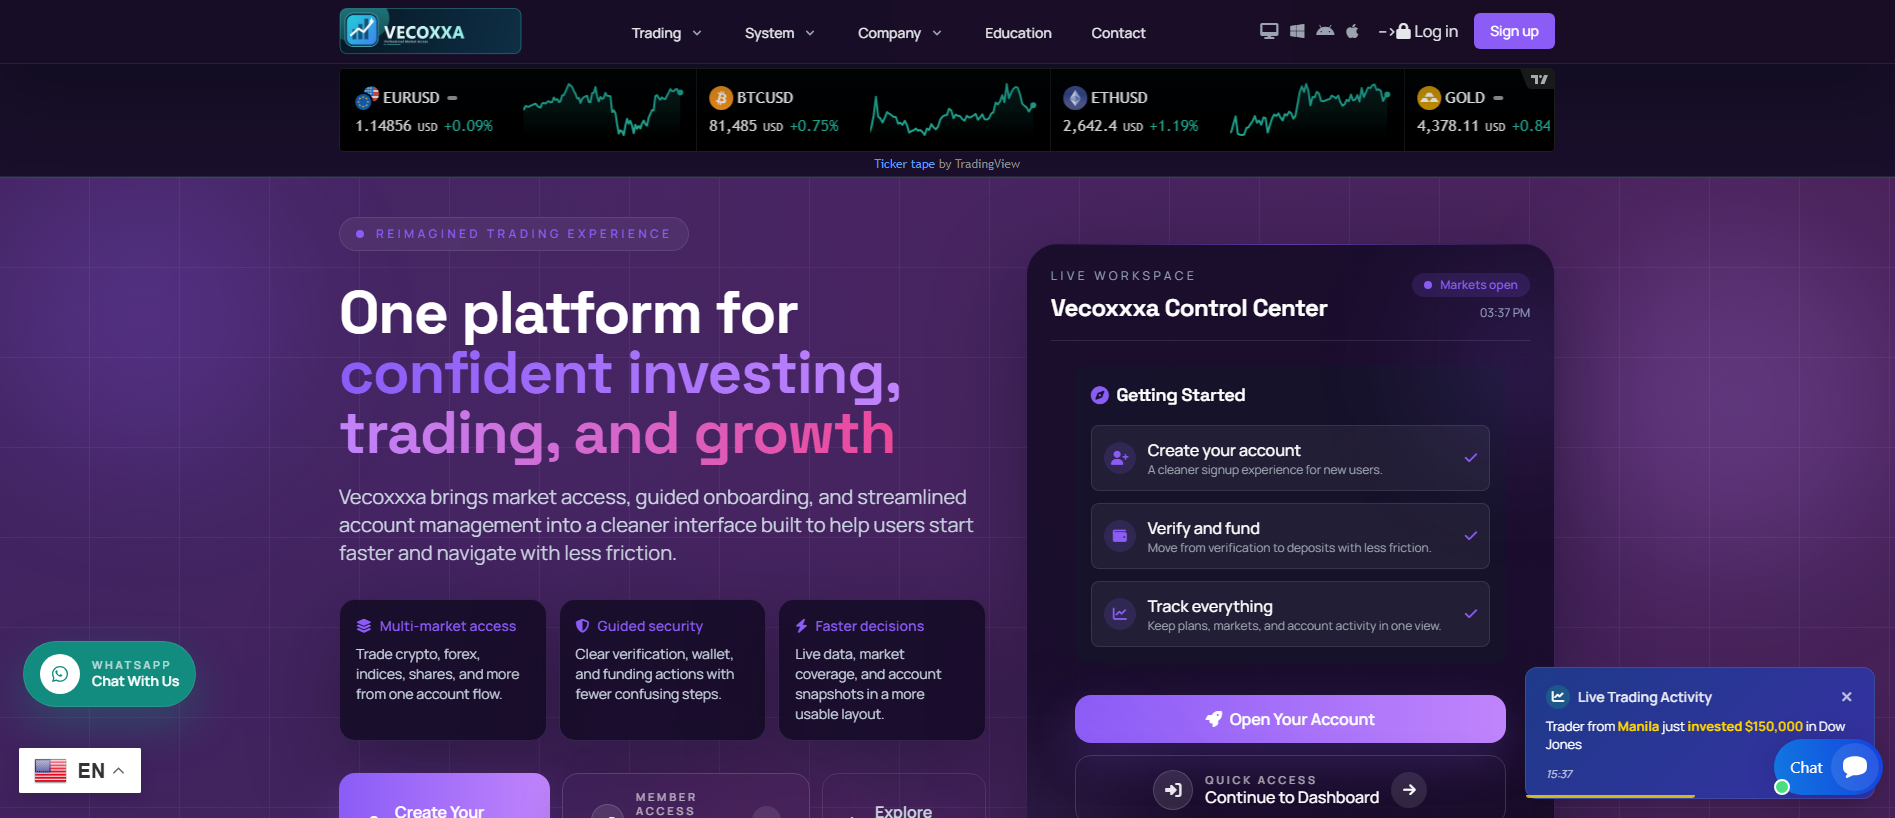
“Vecoxxxa | CFD Trading — Trading on Stocks, Gold, Oil, Indices”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse-tracker@hostinger.com.
The latest stored availability evidence still shows the domain reachable; 25 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
vecoxxxa.com — Sunucu hatası (HTTP 502). Marka kimliğine bürünme: Unknown; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 2/89 (Netcraft, SOCRadar); URLScan malicious verdict; PhishDestroy score 81/100. Kayıt kuruluşu: Hostinger.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.
PhishDestroy first observed vecoxxxa.com on Sep 19, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Vecoxxxa | CFD Trading — Trading on Stocks, Gold, Oil, Indices”. Page analysis recorded additional brand references to Across, Ethereum, Ledger, LinkedIn, and WhatsApp. Stored page analysis classifies the content as impersonation. Current evidence score: 81/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and URLScan. VirusTotal recorded 2 detections among 89 engines: Netcraft, SOCRadar on Sep 20, 2026 at 20:20 UTC. URLScan returned a malicious verdict with score 100; scan metadata assigned phishing as its category on Sep 20, 2026 at 03:30 UTC. Non-positive and contextual checks: AlienVault OTX listed 7 community pulse references (not vendor detections) on Sep 20, 2026 at 20:21 UTC. The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 18:20 UTC. URLQuery recorded no positive detection; no observation timestamp was retained. Google Safe Browsing returned no flag on Sep 20, 2026 at 20:20 UTC.
HTTP 502 server error was recorded on Sep 20, 2026 at 10:50 UTC. Registration records for the domain list HOSTINGER operations, UAB as the registrar and May 26, 2026 as the creation date. At collection time, the hostname resolved to 198.251.84.236 on AS53667 (PONYNET - FranTech Solutions, US). The recorded endpoint location is Luxembourg, US. The stored server header is LiteSpeed. DOM analysis on Sep 19, 2026 at 22:20 UTC returned 81/100. The evidence archive retains 2 visual captures from PhishDestroy and URLScan. TLS metadata lists YE2 as the certificate issuer; checked Sep 19, 2026 at 19:02 UTC.
The content indicators and 2 positive source findings support the current Unknown-themed impersonation classification.

198.251.84.236. Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
Scanner note: transient_502: raw=transient_502; http=502; via=http_proxy
 (LT)
PD-20260919-45B4AB Recipient: abuse-tracker@hostinger.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Infrastructure map · vecoxxxa.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Bu kaynak IP, birden fazla kimlik avı alanını barındırır; altyapı, kampanyalar arasında paylaşılabilir.
These domains also target Bilinmiyor users. View all Unknown threats →
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
 abgcourier.com
 unlimitedtradingsession.xyz
 bundleafricagp.live
 zeltixplatform.com
 cabal-sentralab.xyz
 vetlink.sbs
 tonwallet.my
 thegoodlifedigital.com
 cp.vexotra.com
 twojdom24.com
 gearivora.com
 sunlu-printing.com
 toolpols.com