Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
started-iotrezor.readme.io favicon

started-iotrezor.readme.io

“Hello there, human!”

Tehdit kararı Kritik 87/100 kanıt puanı
Kullanılabilirlik Bilinen son aktif En son saklanan erişilebilirlik gözlemi
VirusTotal algılamaları: 9/89 Marka kimliğine bürünme: Trezor Bilinen son aktif
10.09.2026 Trezor CDN
Actions API
⚠️
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 9. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
Rapor özeti

started-iotrezor.readme.io — Bilinen son aktif (HTTP 302). Marka kimliğine bürünme: Trezor; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 9/89 (alphaMountain.ai, CRDF, Emsisoft, Forcepoint ThreatSeeker, Fortinet); URLScan malicious verdict; PhishDestroy score 87/100. Kayıt kuruluşu: 1API.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Kanıt özeti

KRİTİK
Puan
87/100

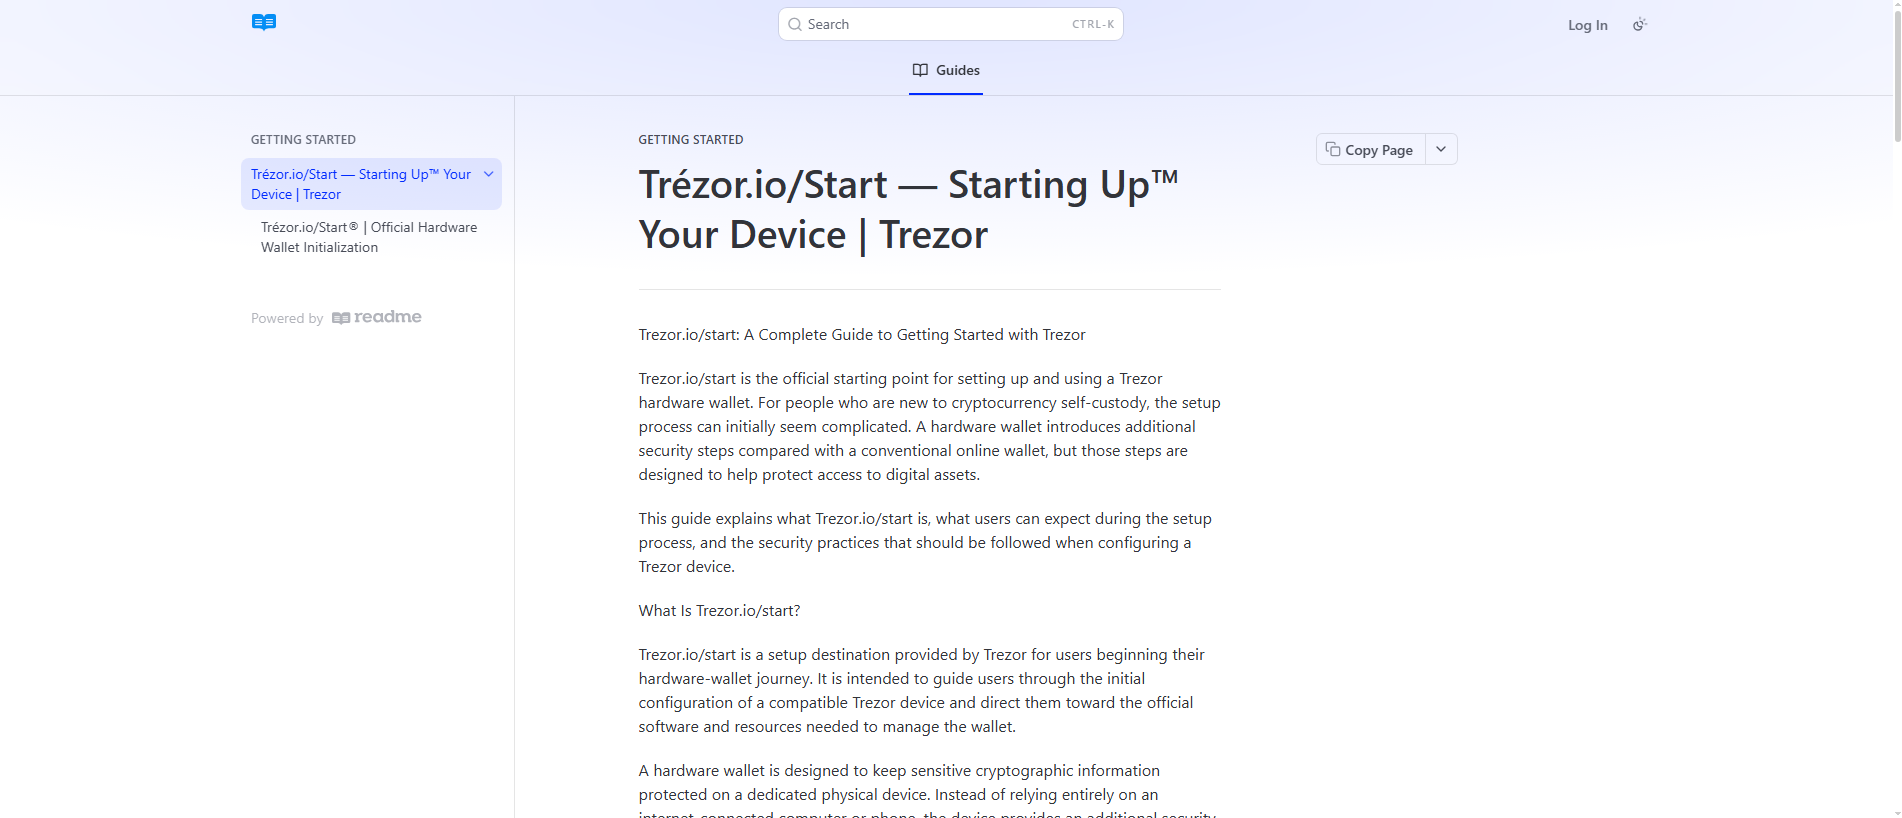
started-iotrezor.readme.io is a subdomain of readme.io. PhishDestroy first observed the hostname on Sep 10, 2026. The hostname explicitly references Trezor; stored content metadata identifies the same apparent target. The captured page title is “Hello there, human!”. Stored page analysis classifies the content as impersonation. Current evidence score: 87/100 (critical).

Positive findings are stored from 2 sources: VirusTotal and URLScan. VirusTotal recorded 9 detections among 89 engines: alphaMountain.ai, CRDF, Emsisoft, Forcepoint ThreatSeeker, Fortinet, Gridinsoft, Netcraft, PhishFort, Webroot on Sep 13, 2026 at 02:06 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Trezor and assigned phishing as its category on Sep 10, 2026 at 17:08 UTC. Non-positive and contextual checks: The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 22:20 UTC. Google Safe Browsing returned no flag on Sep 20, 2026 at 22:00 UTC.

HTTP 302 was recorded on Sep 20, 2026 at 22:16 UTC. Registration records for the registrable domain readme.io list 1API GmbH as the registrar and May 17, 2011 as the creation date. At collection time, the hostname resolved to 104.16.241.118 on AS13335 (Cloudflare, Inc.). The IP and ASN identify shared Cloudflare edge infrastructure; the origin server is not established by this address. DOM analysis on Sep 10, 2026 at 18:22 UTC returned 78/100. The evidence archive retains 2 visual captures from PhishDestroy and URLScan. TLS metadata lists Google Trust Services / WE1 as the certificate issuer with validity through Dec 7, 2026; checked Sep 10, 2026 at 16:02 UTC.

The content indicators and 2 positive source findings support the current Trezor-themed impersonation classification.

VirusTotal
VirusTotal
9 det.
URLScan
URLScan
TLS sertifikası
Google Trust Services / WE1
Yaş
15.4 yr
Gözlemlenen durum
Bilinen son aktif 302
PhishDestroy
DestroyList
Listelenmiş
Veri kapsamı VirusTotal 9 / 89 OTX no community references CF Radarı scan completed URLScan capture saklanan rapor URLScan verdict malicious TLS valid certificate, 77d WHOIS 187 mo old Ekran görüntüsü 2 captures · 2 sources

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed Sep 10, 2026 · 17:40 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 104.16.241.118.

Tehdit Müdahale Pipeline

Keşif
Checks
Reports
Erişilebilirlik
10/12

Genel Engelleme Listesi Durumu

Evasion analysis

Cloaking & traffic-distribution check

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan
Server header seen by scanner
cloudflare

Scanner note: redirect: raw=redirect_302; http=302; via=https_proxy; location=/inactive; server=cloudflare

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting

Kaydedilen görüntü · 2 sources

Etki Alanı Analizi

Alan adı
URLScan Verdict Zararlı score 100 Phishing brand: Trezor report ↗
Sunucu / ASN cloudflare · AS13335 Cloudflare, Inc.
IP Context Cloudflare shared edge origin IP hidden Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.
IP adresi 104.16.241.118 CDN
Coğrafi konumCA Toronto, CA
AS13335 · Cloudflare, Inc.
Kaynak IP, bir CDN proxy'sinin arkasına gizlenir. Uç adresine ilişkin Ters IP sonuçları ilgisiz kiracılar içerir; Kaynağı bulmak için pasif DNS veya sertifika şeffaflığı verileri gerekir.
Registration (base domain)readme.io · Oluşturuldu 17.05.2011 Expires 17.05.2027
HTTP Durumu302 Found (Temporary)
Teknik ayrıntılarDNS, SSL SAN’ları, zaman damgaları
İlk Kez Tespit Edildi10.09.2026
DOM Analysisanalyzed 10.09.2026score 78/1001 brand signal
IoC Extractionscanned 10.09.20260 wallet · 0 Telegram IoCs
Submitted URLhttps://started-iotrezor.readme.io/
Ad sunucularıjeremy.ns.cloudflare.comuma.ns.cloudflare.com
TLS Fingerprint
TLS Observationvalid from 08.09.2026scanned 10.09.2026
TLS SAN Domainsreadme.io
Favicon Hash
Sayfa başlığı
Hello there, human!
Impersonates
Trezor
TLS sertifikası
Valid transport encryption · Düzenleyen Google Trust Services / WE1 · valid for 77 days
Teknolojiler · 5 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

9 / 89 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed First positive detection Previous stored snapshot: 4 detections
alphaMountain.ai
CRDF
Emsisoft
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
Netcraft
PhishFort
Webroot
Site Performans Analizi

Google PageSpeed Insights — mobile performance audit of started-iotrezor.readme.io · checked Sep 10, 2026

37
Poor
Performance
FCP
5.86s
First Contentful Paint
LCP
6.31s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
1554ms
Total Blocking Time
SI
5.86s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Benzer alan adları

74 kayıtlı benzer alan adı

Tümünü göster (62)
rezor.io omission rrezor.io replacement rtezor.io transposition tdezor.io replacement teezor.io replacement terzor.io transposition tezor.io omission tfezor.io replacement tr.ezor.io subdomain tr3zor.io replacement treeor.io replacement treezor.io insertion treor.io omission treqor.io replacement tresor.io replacement trezeor.io insertion trezer.io vowel-swap trezior.io insertion trezir.io replacement trezkor.io insertion trezlor.io insertion trezo.io omission trezoe.io replacement trezoir.io insertion trezopr.io insertion trezor-io.com various trezorio.com various trezot.io replacement trezpor.io insertion trezpr.io replacement trezr.io omission trezro.io transposition trezxor.io insertion trezzor.io insertion trizor.io vowel-swap trozor.io vowel-swap trrzor.io replacement trtezor.io insertion trwezor.io insertion trwzor.io replacement trzeor.io transposition trzzor.io replacement ttezor.io replacement ttrezor.io insertion tyrezor.io insertion yrezor.io replacement ytrezor.io insertion prezor.io bitsquatting treazor.io insertion trerzor.io insertion trewzor.io insertion trexor.io bitsquatting trez0r.io homoglyph trezaor.io insertion trezora.io addition trezore.io addition trezoro.io addition trezorr.io addition trezors.io addition trezort.io addition xn--tezor-5bb.io homoglyph xn--trezo-9bb.io homoglyph

Topluluk istihbaratı

1 topluluk raporu

KategoriIMPERSONATION

Brand abuse: impersonation, fake affiliation, impersonating Trezor

Kanıtlar ve Dış Raporlar

Third-Party Detection — ChainAbuse
1 report filed for started-iotrezor.readme.io · category: Impersonation · source checked
Flagged by automated brand-abuse detection on Sep 11, 2026 — automated submission, not a user testimony. Source: ChainAbuse (TRM Labs).

Bu Siteden Etkilendiniz mi?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi
Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin

Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/started-iotrezor.readme.io"
  title="PhishDestroy threat report for started-iotrezor.readme.io"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>