Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
paycity.za-bzjw.cfd favicon

paycity.za-bzjw.cfd

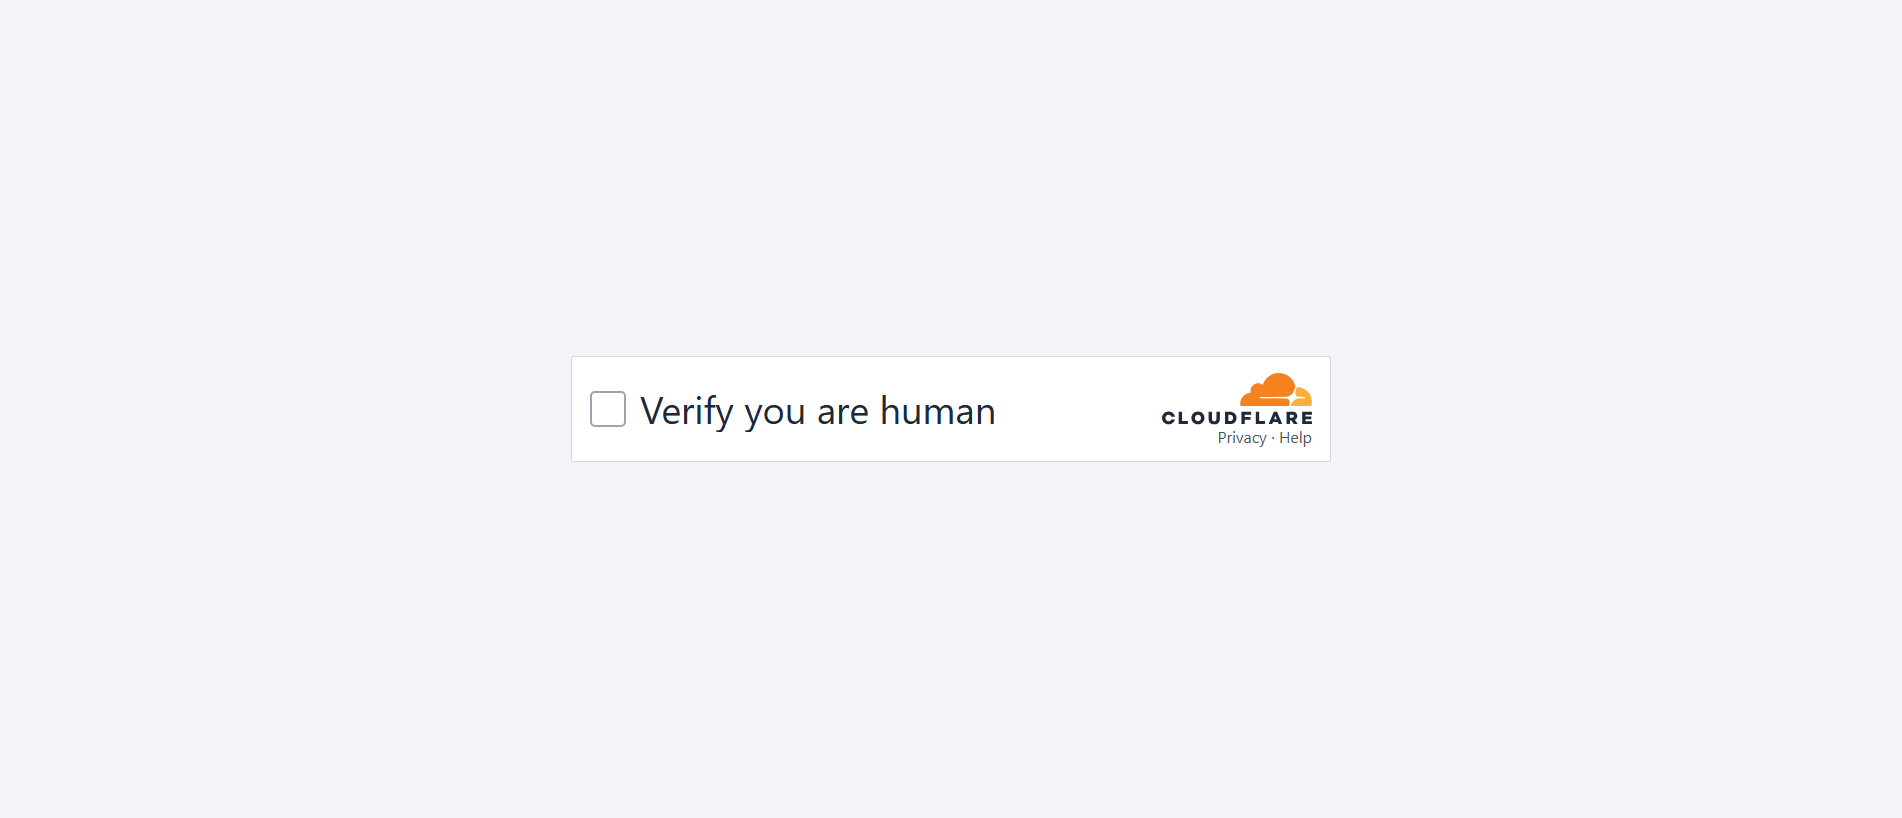
“Veuillez verifier que vous etes humain”

Kayıt kuruluşu
Dynadot
Resolved IP
172.67.178.223
Registered
04.09.2026
Tehdit kararı Kritik
Kullanılabilirlik İçerik kullanılamıyor En son gözlemde içerik mevcut değildi
VirusTotal algılamaları: 14/89 URLQuery threat systems: 2 alerts Dolandırıcılık türü: Impersonation
07.09.2026 1 Report Sent CDN
API
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 14. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
Rapor özeti

paycity.za-bzjw.cfd — İçerik kullanılamıyor (HTTP 502). Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 14/89 (alphaMountain.ai, CRDF, CyRadar, ESET, Emsisoft); URLQuery 2 alerts; CF Radar malicious; PhishDestroy score 95/100. Kayıt kuruluşu: Dynadot.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

VirusTotal
VirusTotal
14 det.
URLQuery
URLQuery
2 threat alerts
CF Radarı
Zararlı
URLScan
URLScan
TLS sertifikası
Süresi dolmuş veya doğrulanmamış
Yaş
1 mo New
Gözlemlenen durum
İçerik kullanılamıyor 502
PhishDestroy
DestroyList
Listelenmiş
Reports Sent
1

Source evidence

7 sources

VirusTotal

14 / 89

Bildir

URLQuery

2 threat-system alerts

Bildir

CF Radarı

provider verdict: malicious

Bildir

OTX

no community references

Bildir

URLScan capture

saklanan rapor

Stored URLScan capture preview
Bildir

URLScan verdict

Analiz tamamlandı

Bildir

Google Safe Browsing

Checked; no threat flag recorded

Bildir
Ağ Güvenliği İstihbaratı
Threat Detection Systems 2 alerts
Detection System Indicator Verdict Alert
DNS4EU paycity.za-bzjw.cfd malicious Sinkholed
Quad9 DNS paycity.za-bzjw.cfd malicious Sinkholed
CF Cloudflare Radar Verdict Zararlı
Phishing
SSL Certificate Invalid
SSL certificate is invalid or expired. Issuer:

Kanıt özeti

Kritik
VirusTotal
14/89
URLScan
Stored capture

Assessment

paycity.za-bzjw.cfd returned an HTTP status of 502 when checked on 2026-10-01, according to the recorded HTTP observation. The same record notes the domain was first observed on 2026-09-07, which gives a starting point for later comparisons.

Recorded Evidence

The PhishDestroy internal listing for paycity.za-bzjw.cfd was recorded as true. VirusTotal reported 14 detections across 89 scanners on 2026-09-08. The SSL certificate was issued by Google Trust Services / WE1 and scanned on 2026-09-07. The HTTP check on 2026-10-01 recorded a 502 response, while the IP address 172.67.178.223 was associated with AS13335 Cloudflare, Inc. in the US.

Interpretation

The PhishDestroy listing and the VirusTotal result were recorded on different dates, so they reflect separate snapshots rather than one combined measurement. The SSL scan on 2026-09-07 and the HTTP check on 2026-10-01 also come from different times, meaning the observations cannot be treated as simultaneous. These dated records allow a reader to compare what each source captured without deciding what the domain currently does.

Recommended Actions

Retain the dated records for paycity.za-bzjw.cfd so later checks can be compared against the same source values. When reviewing the domain, avoid submitting passwords, payment details or other sensitive information. Compare any new HTTP, SSL or listing observations with the existing dates before drawing conclusions.

Tespit ve kaçınma analizi

Gizleme ve trafik dağıtımı kontrolü

Henüz taranmadı Henüz tarayıcı ile tarayıcı arası bir fark kaydedilmemiştir

Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.

Kaydedilmiş gizleme bayrağı
Henüz taranmadı
Son gizleme taraması

Tarayıcı notu: transient_502: raw=transient_502; http=502; via=http_proxy

TDS'da canlı parmak izi kontrolü
Bu panel açıkken, PhishDestroy tarayıcısından çalıştırıldığında yedi Keitaro parmak izi ve bir tarayıcı-crawler karşılaştırması görüntülenir.
Bekleme

Kaydedilen görüntü · 3 captures

Sayfa başlığı
Veuillez verifier que vous etes humain
TLS sertifikası
Certificate hostname mismatch · Düzenleyen Google Trust Services / WE1

Domain details

Alan adı
URLScan Verdict Analiz tamamlandı score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.
Registrar (base domain) Dynadot (Unknown)
Kötüye kullanım iletişim bilgisiabuse@dynadot.com
ICANN Kayıt KuruluşuICANN Lookup (RDAP) →
Registration (base domain)za-bzjw.cfd · Oluşturuldu 04.09.2026 (34d · New) — Expires 04.09.2027
HTTP Durumu502 Error
İlk erişilemezliğe kadar geçen süre 4 days
Neyi ölçüyoruz Depolanan ilk kötüye kullanım raporundan içeriğin kullanılamadığına dair ilk gözleme kadar geçen süre. Bu, nedeni belirlemez.
Her raporun içeriği Saklanan giden rapor kayıtları, satıcı kararları, kayıt verileri, barındırma ayrıntıları, sınıflandırmalar veya ekran görüntüleri gibi o sırada mevcut olan kanıtlara referans verebilir. Bu sayfa, teslim edilen yükün, alındığının, onaylandığının veya alıcının yaptığı eylemin tam olarak ne olduğu konusunda bir sonuç çıkarmaz.
Teknik ayrıntılarProvenance & timestamps
İlk Kez Tespit Edildi07.09.2026
DOM Analysisanalyzed 07.09.2026score 78/100
Submitted URLhttp://paycity.za-bzjw.cfd/a
Favicon Hash
Vaka kimliği
SHORTDOT BÖLGESİ · KAMUYA AÇIK KANIT .cfd

ShortDot zone evidence

The linked repository preserves daily zone observations across seven ShortDot-operated TLDs, including registration volume and abuse-related indicators. This registry context is supporting background and is not an independent detection for the domain in this report.

ShortDot SA · Luxembourg 7 bölge · tüm bölgelere ait kanıtlar her gün güncellenir ShortDot kanıt deposunu aç
ICANN OVERSIGHT Registration: za-bzjw.cfd

Akreditasyon ve RAA bağlamı

Registrar accreditation and DNS abuse obligations

For the registrable domain za-bzjw.cfd behind this subdomain, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Hiçbir şey otomatik olarak gönderilmez.

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
172.67.178.223
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.

Ad sunucuları 2

  • melnicoff.ns.cloudflare.com
  • rose.ns.cloudflare.com

Location describes the IP network.

TLS sertifikası

Issuer
Google Trust Services / WE1
Valid from
2026-09-04 06:32:21
Valid until
2026-12-03 07:30:47
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-09-07 01:02:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprintfcad20112eb4817df8ff86fe71fde160e698b4161902fa8784079d43ef5e1bc2
Certificate names · 1 SANs
  • za-bzjw.cfd

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 172.67.178.223rapiddns.io

Latest Classified Outcome 2026-10-07 01:43:27 UTC

Primary outcome Bilinmiyor reason: Stale Current Evidence 0% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unknown Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Bilinmiyor Origin unreachable Http 5xx 20% 2026-10-07 01:43:27 UTC
RDAP registration Bilinmiyor
Observed timeline last reachable: 2026-09-07 22:14:33 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Teknolojiler · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

14 / 89 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed First positive detection Previous stored snapshot: 14 detections
alphaMountain.ai
CRDF
CyRadar
ESET
Emsisoft
Fortinet
G-Data
Gridinsoft
LevelBlue
Netcraft
Seclookup
SOCRadar
Sophos
Webroot

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-09-10 22:04:34 UTC
    Domain state transitioned from alive to dead.
  2. VirusTotal Detections Update 2026-09-07 03:40:08 UTC
    VirusTotal scanner detections updated from 13 to 14. Added scanner alerts: CyRadar.
  3. VirusTotal Detections Update 2026-09-07 01:37:50 UTC
    VirusTotal scanner detections updated from 12 to 13. Added scanner alerts: Gridinsoft.
  4. Threat First Observed 2026-09-07 00:36:07 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 172.67.178.223.

Tehdit Müdahale Pipeline

Keşif
Analysis
Notifications
Monitoring

14 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Tehdit Alındı
paycity.za-bzjw.cfd tespit edildi ve kapsamlı analiz için sıraya alındı
07.09.2026
URLScan.io Capture
Kaydedildi URLScan report with capture artifacts
07.09.2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
14/89 recorded on VirusTotal
08.09.2026
CF Radar: Malicious
Cloudflare Radar classified this domain as phishing
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
07.09.2026
Technical Analysis Recorded
Rapor, depolanan teknolojiyi veya adli analiz sonuçlarını içerir.
08.10.2026
Content Observed Unavailable
İzleme, kullanılamayan bir yanıt kaydetti; nedeni bağımsız olarak belirlenmemiştir.
11.09.2026
VT Detection +1
+1 new detection (13 → 14): CyRadar
07.09.2026
VT Detection +1
+1 new detection (12 → 13): Gridinsoft
07.09.2026
Sent Report Recorded
Stored outgoing record associated with registrar Dynadot Inc, 1 abuse contact
abuse@dynadot.com
07.09.2026
DestroyList Yayınlandı
07.09.2026
Content Observed Unavailable
En son saklanan kontroller, rapor edilen içeriğin mevcut olmadığını gösteriyor; bu, değişikliğe kimin veya neyin sebep olduğunu belirlemez.
11.09.2026
İlk erişilemezliğe kadar geçen süre
Tespitten ilk kullanılamayan gözleme kadar 93 saat geçti.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Kanıtlar ve Dış Raporlar

Gönderilen kanıt anlık görüntüsü
Sent: Ledger records: 1 Case ID: PD-20260907-85AECD Recipient: abuse@dynadot.com
Page title stored with report: Verify you are human
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 17.4 KB
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Derinlemesine Analiz

Bu Siteden Etkilendiniz mi?

5 evidence signal groups linked 1 reports recorded İçerik kullanılamıyor
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.

Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi

Template-based draft · optional AI wording assistance requires separate consent

Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir · Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/paycity.za-bzjw.cfd"
  title="PhishDestroy threat report for paycity.za-bzjw.cfd"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>