VirusTotal
7 / 89
Bildir


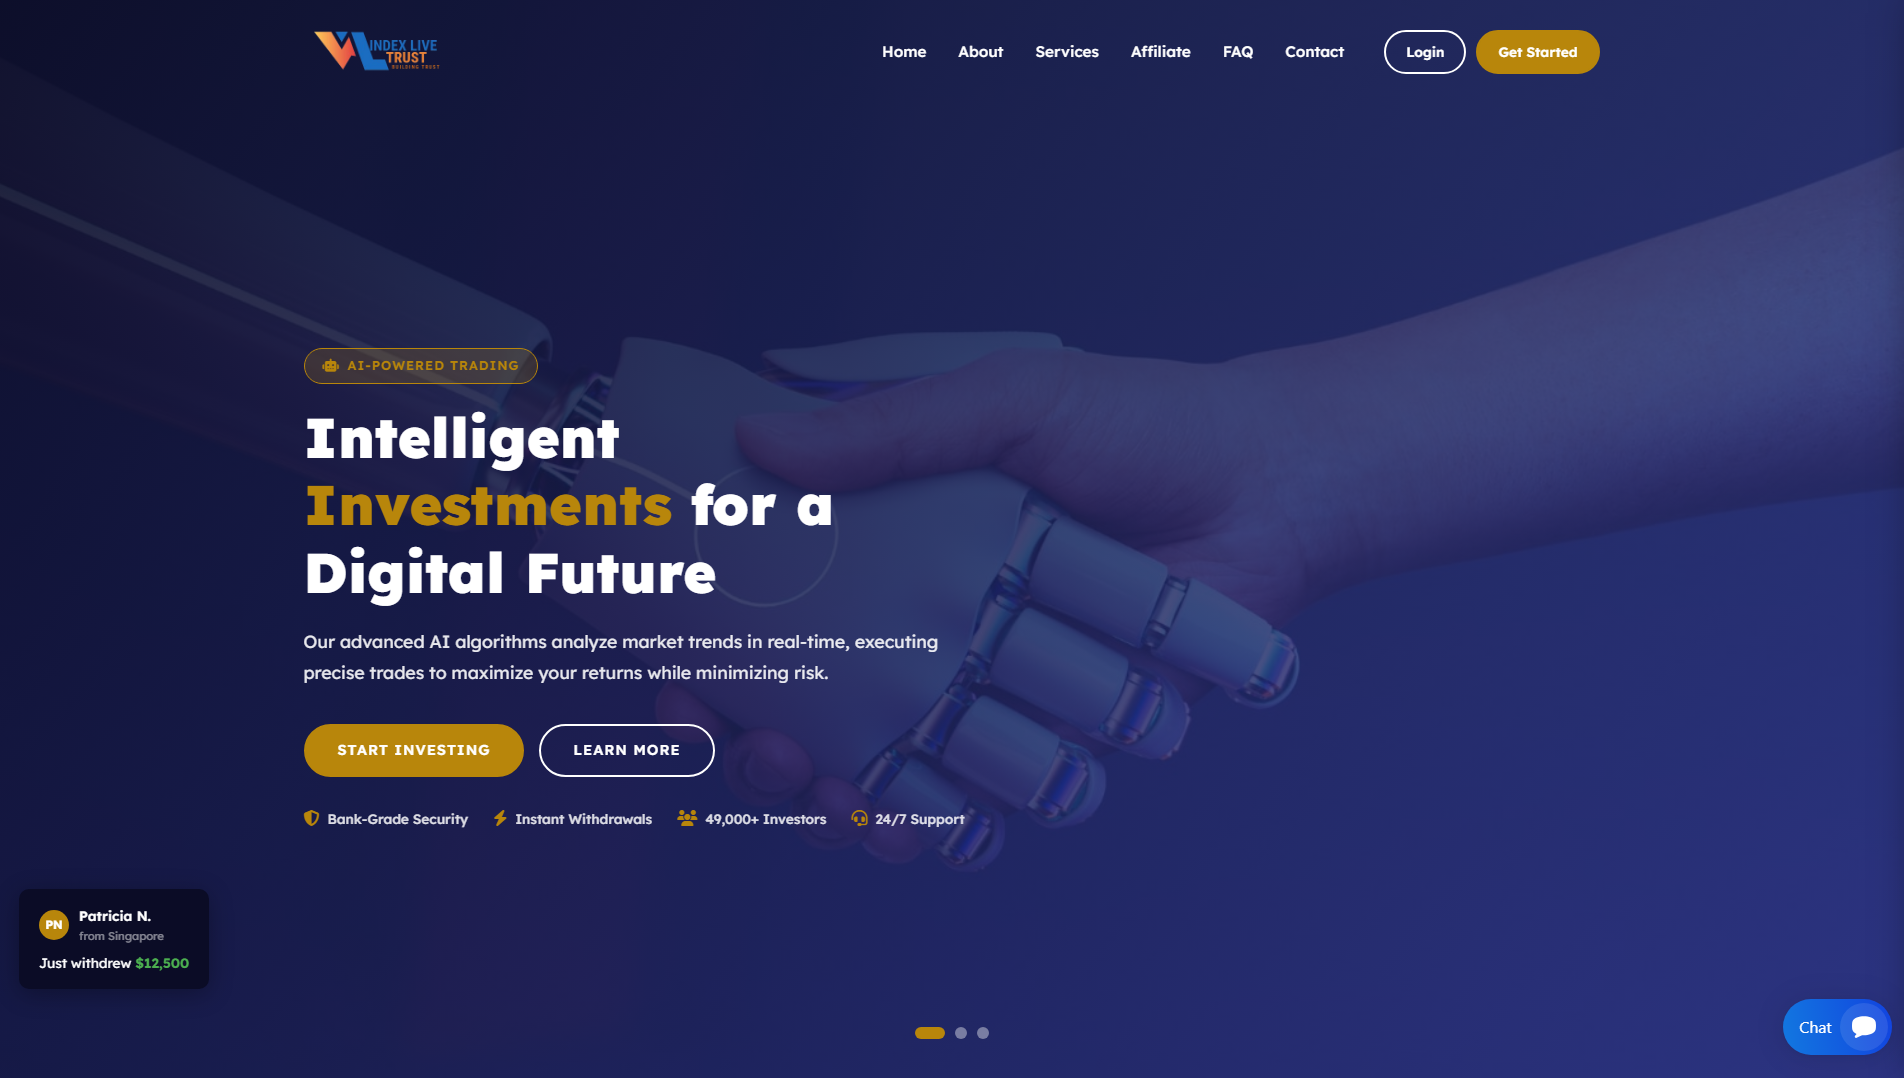
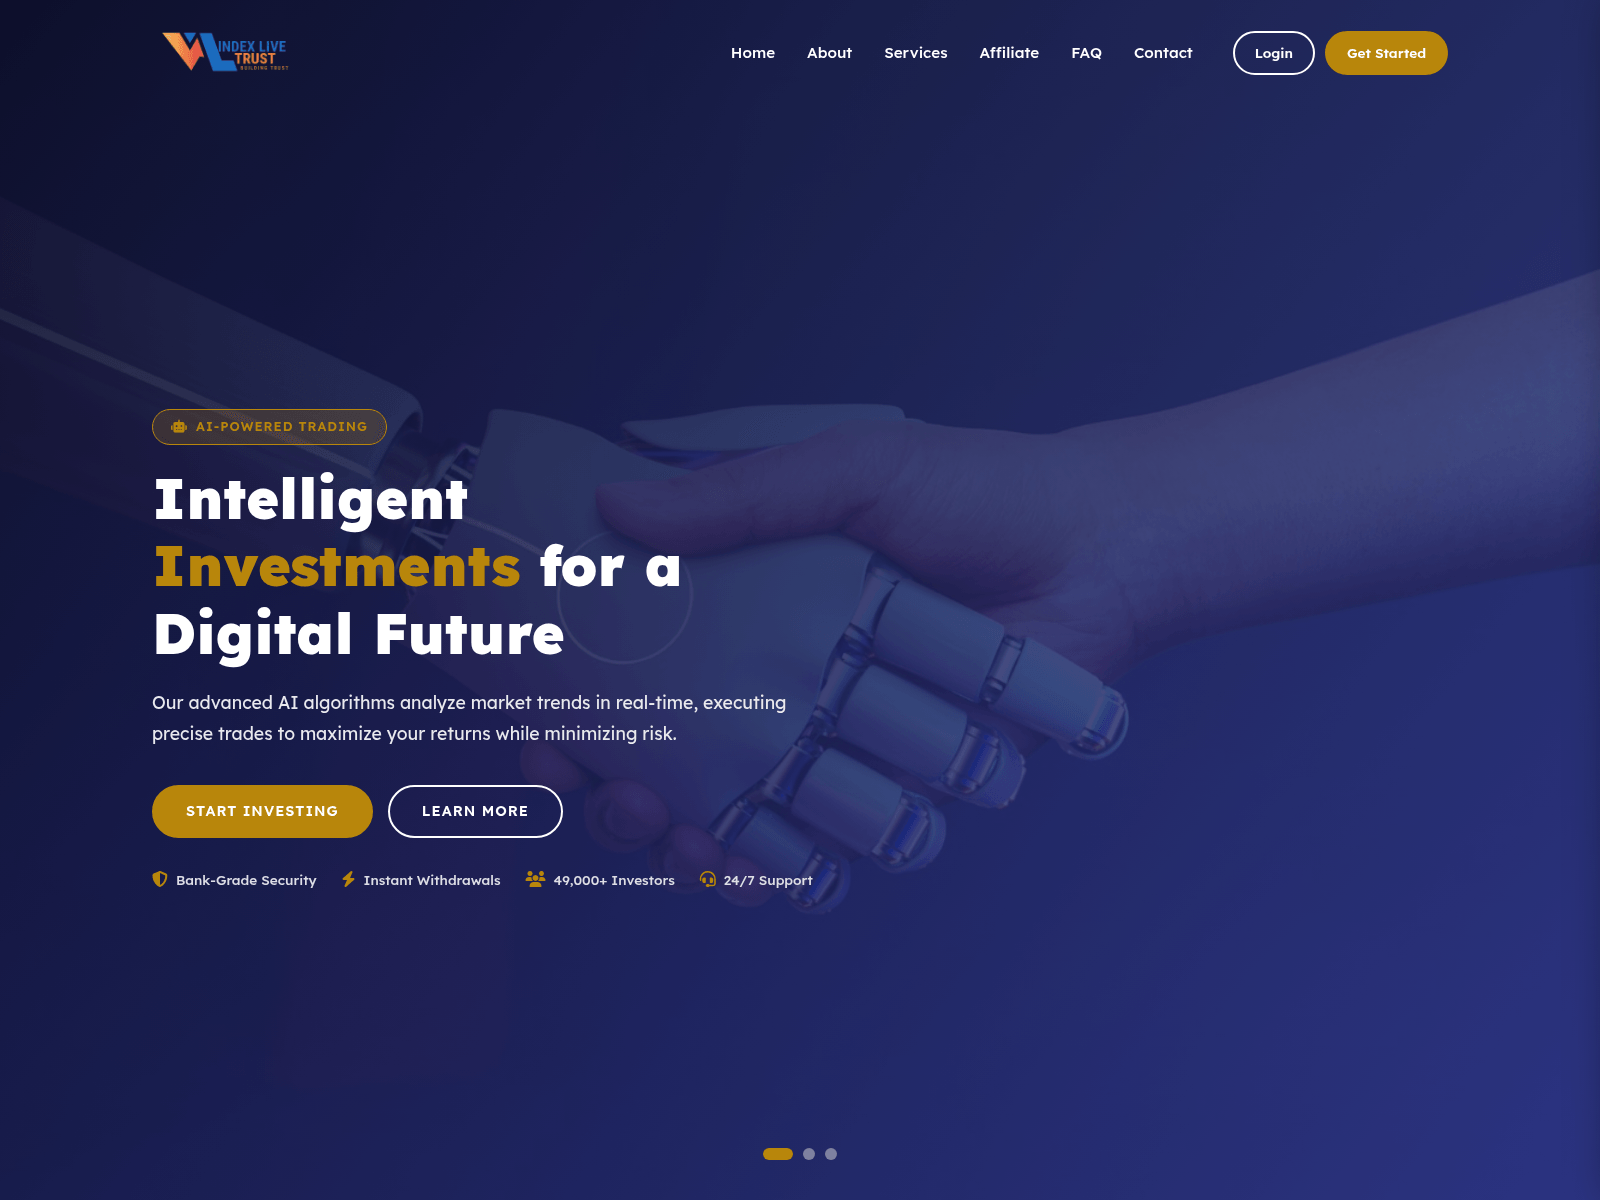
“Index Live Trust - Modern Investment Platform”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse-contact@sav.com.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
indexlivetrust.com — Bilinen son aktif (HTTP 200). Marka kimliğine bürünme: Across; Dolandırıcılık türü: Investment Scam. Kanıt özeti: VirusTotal 7/89 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, Netcraft); PhishDestroy score 88/100. Kayıt kuruluşu: Sav.com.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

7 / 89
checked — no detections recorded
Bildir4 community references
Bildirprovider verdict: clean
Bildirsaklanan rapor
 Bildir
Analiz tamamlandı
Bildir80/100
BildirChecked; no threat flag recorded
Bildirindexlivetrust.com returned HTTP status 200 in a check recorded on 2026-10-01, the most recent dated observation in this set. The domain was first observed on 2026-09-06, and its registration date is listed as 2026-09-05.
The HTTP check on 2026-10-01 recorded status 200 for indexlivetrust.com. VirusTotal, checked on 2026-09-18, reported 7 detections across 89 scanners. OTX, checked on 2026-09-11, showed 4 pulses. The domain was first observed on 2026-09-06, and its SSL certificate was scanned that same day, issued by Let's Encrypt / YE2. Registration is dated 2026-09-05 with registrar Sav.com, LLC. The IP address 198.251.84.236 is recorded in LU under FranTech Solutions.
The dated records describe separate observations made by different sources, each with its own scope and method. The HTTP response, VirusTotal detections, OTX pulses, and the PhishDestroy internal listing are distinct signals that should be read individually rather than merged into a single conclusion. The chronology shows registration and first observation close together, while later checks occurred on separate dates, so the records can be compared as a sequence without treating any single date as a complete picture.
Preserve the HTTP check record for indexlivetrust.com and the VirusTotal result as separate source documents for later comparison. Retain the OTX pulse record and the PhishDestroy internal listing alongside them, since each captures a different kind of observation. Compare these preserved records against future checks of indexlivetrust.com to see whether the recorded signals change over time.
Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.
LiteSpeedTarayıcı notu: alive_content: raw=ok; http=200; via=https_proxy; server=LiteSpeed
ns113.my-control-panel.comns114.my-control-panel.commail.indexlivetrust.compriority 10Location describes the IP network.
cf84261e43c6741a0daffcabc5a555d041b246825d97f510538ab31b211e7a4dSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
198.251.84.236. 12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20260906-05CECB Recipient: abuse-contact@sav.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Template-based draft · optional AI wording assistance requires separate consent
Her bir satır, bir etki alanının bu ana bilgisayara bağlanmasının bir nedenini gösterir. Düğüm boyutu, VirusTotal adresindeki algılamaları gösterir; kesikli çizgili düğümler ise halihazırda çevrimdışı durumdadır. Tam listeler aşağıda yer almaktadır.
Bu kaynak IP, birden fazla kimlik avı alanını barındırır; altyapı, kampanyalar arasında paylaşılabilir.
Bu alan adları, Across kullanıcılarını da hedef almaktadır. Tüm “Across” tehditlerini görüntüle →
Aynı kayıt kuruluşu aracılığıyla kaydedilmiştir. Bir kayıt kuruluşu, birbiriyle hiçbir bağlantısı olmayan milyonlarca müşteriye hizmet verdiğinden, bu durum bir bağlantıyı kanıtlamaktan ziyade raporları bir araya getirmektedir.
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin