Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
cricfyapp.pk favicon

cricfyapp.pk

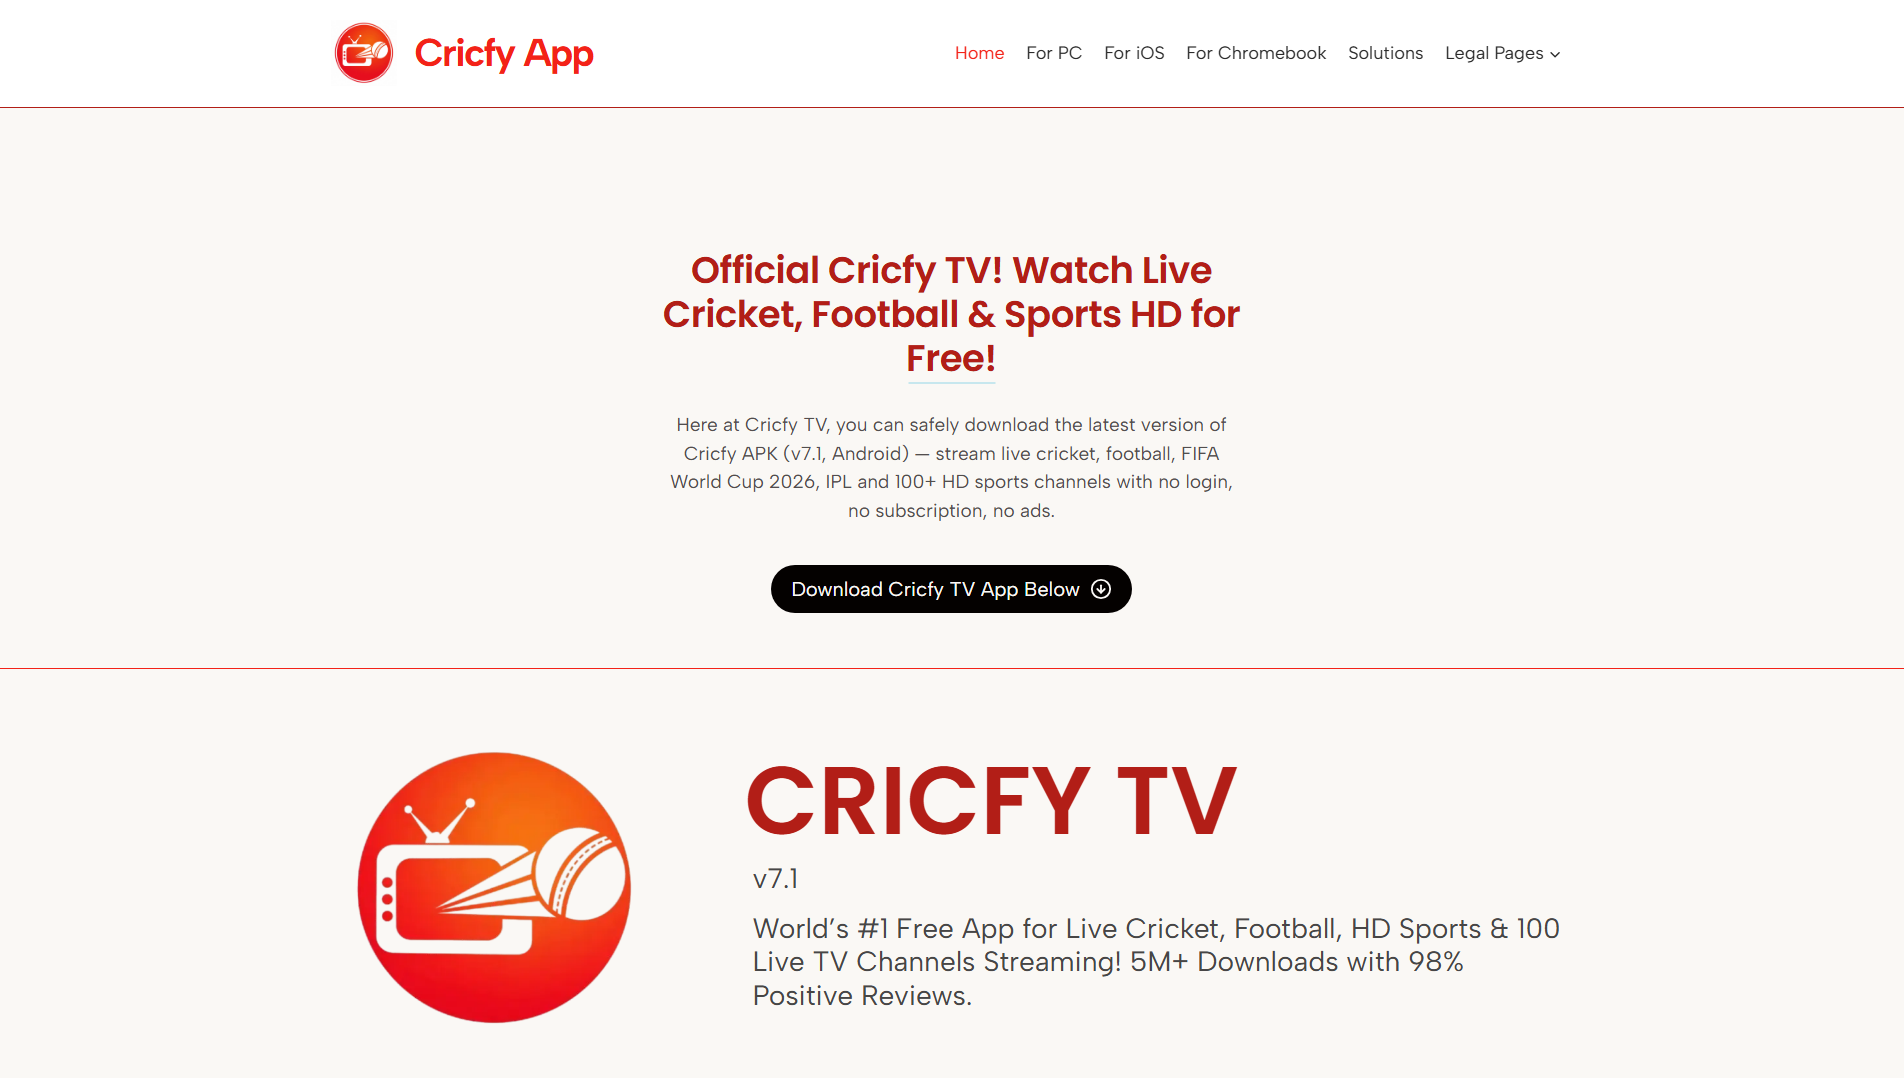
“Cricfy TV APK v7.1 Download 2026 — Live Cricket & Football HD Free”

Tehdit kararı Kritik 95/100 kanıt puanı
Kullanılabilirlik Bilinen son aktif En son saklanan erişilebilirlik gözlemi
VirusTotal algılamaları: 8/89 Saklanan engelleme listesi eşleşmeleri: 2 URLQuery threat systems: 1 alert Bilinen son aktif
OTX: 4 refs 19.09.2026 1 Report Sent
Actions API
⚠️
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 8. Bir eşleşme bildiren genel engellenenler listeleri: 2. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
ABUSE NOTICE · 24H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is report@abuseradar.com. The latest stored availability evidence still shows the domain reachable; 30 hours has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
30 hours
Reports sent
1
Latest case ID
PD-20260919-253D0B
Current status
HTTP 200 at latest stored check
Rapor özeti

cricfyapp.pk — Bilinen son aktif (HTTP 200). Kanıt özeti: VirusTotal 8/89 (BitDefender, CRDF, Forcepoint ThreatSeeker, G-Data, Gridinsoft); URLQuery 1 alert; URLScan capture; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 95/100.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Kanıt özeti

KRİTİK
Puan
95/100

PhishDestroy first observed cricfyapp.pk on Sep 19, 2026. The captured page title is “Cricfy TV APK v7.1 Download 2026 — Live Cricket & Football HD Free”. Current evidence score: 95/100 (critical).

Positive findings are stored from 4 sources: VirusTotal, MetaMask, SEAL, and URLQuery. VirusTotal recorded 8 detections among 89 engines: BitDefender, CRDF, Forcepoint ThreatSeeker, G-Data, Gridinsoft, Kaspersky, SOCRadar, VIPRE on Sep 20, 2026 at 09:44 UTC. MetaMask and SEAL listed the hostname in the separate external-blocklist snapshot on Sep 20, 2026 at 14:20 UTC. URLQuery recorded 1 threat-system alert on Sep 19, 2026 at 08:25 UTC. Non-positive and contextual checks: On Sep 20, 2026 at 09:44 UTC, AlienVault OTX listed 4 community pulse references (not vendor detections); Google Safe Browsing returned no flag. URLScan captured the page on Sep 19, 2026 at 08:07 UTC.

HTTP 200 was recorded on Sep 20, 2026 at 10:50 UTC. The recorded creation date for the domain is Aug 9, 2026. At collection time, the hostname resolved to 84.32.84.108 on AS47583 (Hostinger International Limited). The recorded endpoint location is Vilnius, LT. The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YE2 as the certificate issuer with validity through Nov 9, 2026; checked Sep 19, 2026 at 10:02 UTC.

The content indicators and 4 positive source findings support the current phishing classification. The stored fields do not identify an impersonated brand or victim interaction.

VirusTotal
VirusTotal
8 det.
URLQuery
URLQuery
1 threat alert
OTX references
URLScan
URLScan
TLS sertifikası
Let's Encrypt / YE2
Yaş
1 mo New
Gözlemlenen durum
Bilinen son aktif 200
PhishDestroy
DestroyList
Listelenmiş
Reports Sent
1
Veri kapsamı VirusTotal 8 / 89 URLQuery 1 threat-system alert OTX 4 community references CF Radarı scan completed URLScan capture saklanan rapor TLS valid certificate, 49d WHOIS 1 mo old Ekran görüntüsü 3 captures · 3 sources
Ağ Güvenliği İstihbaratı
Threat Detection Systems 1 alert
Detection System Indicator Verdict Alert
DNS4EU cricfyapp.pk malicious Sinkholed

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update Sep 19, 2026 · 16:58 UTC
    VirusTotal scanner detections updated from 6 to 8. Added scanner alerts: CRDF, Gridinsoft.
  2. VirusTotal Detections Update Sep 19, 2026 · 14:53 UTC
    VirusTotal scanner detections updated from 3 to 6. Added scanner alerts: BitDefender, G-Data, SOCRadar.
  3. VirusTotal Detections Update Sep 19, 2026 · 11:39 UTC
    VirusTotal scanner detections updated from 0 to 3. Added scanner alerts: Forcepoint ThreatSeeker, Kaspersky, VIPRE.
  4. Threat First Observed Sep 19, 2026 · 10:07 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 84.32.84.108.

Tehdit Müdahale Pipeline

Keşif
Checks
Reports
Erişilebilirlik
14/15
Sent Report Recorded
Stored sent-report record for domain registrar, hosting provider, 1 abuse contact
report@abuseradar.com
19.09.2026

Genel Engelleme Listesi Durumu

Evasion analysis

Cloaking & traffic-distribution check

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan
Server header seen by scanner
hcdn

Scanner note: alive_content: raw=ok; http=200; via=https_proxy; server=hcdn

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting

Kaydedilen görüntü · 3 sources

Etki Alanı Analizi

Alan adı
Sunucu / ASN AS47583 Hostinger International Limited
IP itibarı abuse score 0/100 0 reports checked 19.09.2026
OTX Tags 2026-09activeall-domainsblocklistcontentcryptoalan adlarıdrainerfraudlivemonthlyphishdestroyphishingscam
Kayıt kuruluşu Bilinmiyor
Kötüye kullanım iletişim bilgisireport@abuseradar.com
IP adresi 84.32.84.108 LT
Coğrafi konumLT Vilnius, LT
AS47583 · Hostinger CDN
KayıtOluşturuldu 10.08.2026 (41d · New) Expires 10.08.2028
HTTP Durumu200
Teknik ayrıntılarDNS, SSL SAN’ları, zaman damgaları
İlk Kez Tespit Edildi19.09.2026
IoC Extractionscanned 20.09.20260 wallet · 0 Telegram IoCs
Submitted URLhttp://cricfyapp.pk/
Ad sunucularıapollo.dns-parking.comathena.dns-parking.com
MX Records5 mx1.hostinger.com 10 mx2.hostinger.com
TLS Fingerprint
TLS Observationvalid from 11.08.2026scanned 19.09.2026
TLS SAN Domainswww.cricfyapp.pk
Favicon Hash
Vaka kimliği
Sayfa başlığı
Cricfy TV APK v7.1 Download 2026 — Live Cricket & Football HD Free
TLS sertifikası
Valid transport encryption · Düzenleyen Let's Encrypt / YE2 · valid for 49 days
Teknolojiler · 6 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

8 / 89 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed First positive detection Previous stored snapshot: 8 detections
BitDefender
CRDF
Forcepoint ThreatSeeker
G-Data
Gridinsoft
Kaspersky
SOCRadar
VIPRE
Site Performans Analizi

Google PageSpeed Insights — mobile performance audit of cricfyapp.pk · checked Sep 19, 2026

93
Good
Performance
FCP
2.33s
First Contentful Paint
LCP
2.43s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
4.31s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Kanıtlar ve Dış Raporlar

Gönderilen kanıt anlık görüntüsü
Sent: Ledger records: 1 Case ID: PD-20260919-253D0B Recipient: report@abuseradar.com
Page title stored with report: Cricfy TV APK v7.1 Download 2026 — Live Cricket & Football HD Free
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 170.7 KB
Blocklist hits included with submission: MetaMask, SEAL
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.

Bu Siteden Etkilendiniz mi?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi
Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin

Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/cricfyapp.pk"
  title="PhishDestroy threat report for cricfyapp.pk"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>