Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
card-metamask.com favicon

card-metamask.com

“card-metamask.com”

Tehdit kararı Kritik 100/100 kanıt puanı
Kullanılabilirlik Ulaşılabilir · erişim kısıtlı Ulaşılabilir yanıt; sayfa içeriği doğrulanmadı
VirusTotal algılamaları: 17/89 Saklanan engelleme listesi eşleşmeleri: 4 URLQuery threat systems: 3 alerts Marka kimliğine bürünme: MetaMask Bilinen son aktif
OTX: 1 ref 13.09.2026 MetaMask 1 Report Sent CDN
Actions API
⚠️
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 17. Bir eşleşme bildiren genel engellenenler listeleri: 4. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@internet.bs. The latest stored availability evidence still shows the domain reachable; 6 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
6 days
Reports sent
1
Latest case ID
PD-20260913-BC90F2
Current status
HTTP 403 at latest stored check
Rapor özeti

card-metamask.com — Ulaşılabilir · erişim kısıtlı (HTTP 403). Marka kimliğine bürünme: MetaMask; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 17/89 (ChainPatrol, alphaMountain.ai, BitDefender, Certego, CRDF); URLQuery 3 alerts; URLScan malicious verdict; 4 external blocklist matches; PhishDestroy score 100/100. Kayıt kuruluşu: Internet Domain Servic….

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Kanıt özeti

KRİTİK
Puan
100/100

Assessment
Stored evidence for card-metamask.com: VirusTotal recorded 17 detections among 89 scanners on 2026-09-13. That ratio reproduces the stored check in its original units and is not converted into another measure. ScamSniffer, Enkrypt, and PhishFeed appear as named external blocklist observations for card-metamask.com. Each item in this report remains at the scope supplied by its dated source record.

Detection Evidence
VirusTotal records 17 detections among 89 scanners in the stored snapshot dated 2026-09-13. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-09-13 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.

Source Context
ScamSniffer, Enkrypt, and PhishFeed are recorded as named external blocklist observations for card-metamask.com in the snapshot dated 2026-09-13. The stored ScamSniffer, Enkrypt, and PhishFeed blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains card-metamask.com as a publisher record. That PhishDestroy record is counted separately from the ScamSniffer, Enkrypt, and PhishFeed external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.

Reachability and Timeline
The record first observed card-metamask.com on 2026-09-13. The ScamSniffer, Enkrypt, and PhishFeed blocklist snapshot is dated 2026-09-13 and remains a separate event in the stored timeline. The registration date is separately recorded as 2026-07-07. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.

Registration and Infrastructure
For card-metamask.com, the registrar field records Internet Domain Service BS Corp; this is kept as an exact source value. The source stores 172.67.135.248 as the observed address in this record. The registration date for card-metamask.com is recorded as 2026-07-07. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.

Conclusion
The card-metamask.com record states that VirusTotal recorded 17 detections among 89 scanners on 2026-09-13. ScamSniffer, Enkrypt, and PhishFeed remain named blocklist observations from the snapshot dated 2026-09-13. PhishDestroy remains a separate publisher catalogue entry in the stored record. For card-metamask.com, the registrar field records Internet Domain Service BS Corp; this remains separate from the other source fields. The observed address field in this record contains 172.67.135.248. The supported conclusion is bounded to the exact stored observations for card-metamask.com. Any statement beyond those source values would require additional dated material.

Recommended Actions
Avoid submitting sensitive information to card-metamask.com during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain card-metamask.com as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and ScamSniffer, Enkrypt, and PhishFeed blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to card-metamask.com. The stored record does not justify extending that rule to 172.67.135.248 or to other infrastructure records.

VirusTotal
VirusTotal
17 det.
URLQuery
URLQuery
3 threat alerts
OTX references
URLScan
URLScan
TLS sertifikası
Google Trust Services / WE1
Yaş
2 mo New
Gözlemlenen durum
Ulaşılabilir · erişim kısıtlı 403
PhishDestroy
DestroyList
Listelenmiş
Reports Sent
1
Veri kapsamı VirusTotal 17 / 89 URLQuery 3 threat-system alerts OTX 1 community reference CF Radarı scan completed URLScan capture saklanan rapor URLScan verdict malicious TLS valid certificate, 74d WHOIS 2 mo old Ekran görüntüsü 4 captures · 3 sources
Ağ Güvenliği İstihbaratı
Threat Detection Systems 3 alerts
Detection System Indicator Verdict Alert
Quad9 DNS card-metamask.com malicious Sinkholed
OpenDNS card-metamask.com phishing Phishing Block
DNS4EU card-metamask.com malicious Sinkholed

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition Sep 19, 2026 · 04:17 UTC
    Domain state transitioned from alive to dead.
  2. Threat First Observed Sep 13, 2026 · 20:20 UTC
    Domain ingestion complete. Initial state is marked as unknown pointing to IP 172.67.135.248.

Tehdit Müdahale Pipeline

Keşif
Checks
Reports
Erişilebilirlik
14/15
Sent Report Recorded
Stored sent-report record for registrar Internet Domain Service BS Corp., hosting provider, 1 abuse contact
abuse@internet.bs
13.09.2026

Genel Engelleme Listesi Durumu

Evasion analysis

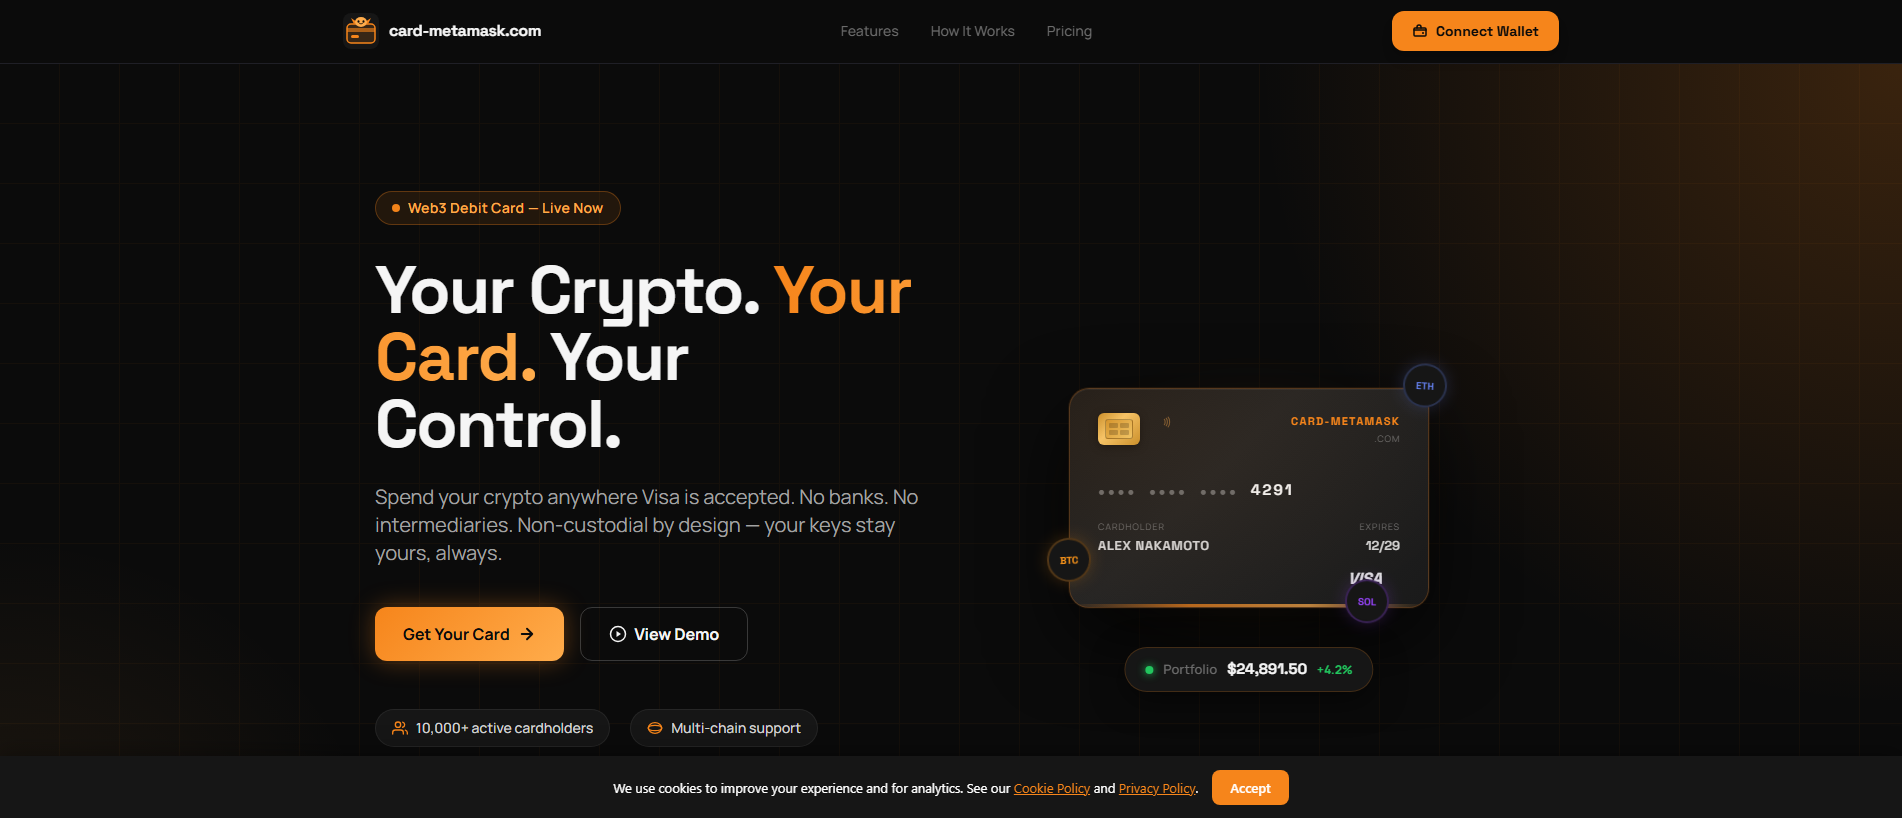
Cloaking suspected: scanner and victim titles differ

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan
Server header seen by scanner
cloudflare

Scanner note: cloudflare_ban: raw=cf_phishing_block; http=403; via=https_direct; server=cloudflare; provider_error=cloudflare_phishing_interstitial

Provider response during scan: cloudflare_phishing_interstitial

Title shown to the security scannerSuspected Phishing | Cloudflare
Title shown to a browser visitorcard-metamask.com
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting

Kaydedilen görüntü · 4 sources

Etki Alanı Analizi

Alan adı
URLScan Verdict Zararlı score 100 Phishing brand: MetaMask report ↗
Sunucu / ASN cloudflare · AS13335 Cloudflare, Inc.
IP Context Cloudflare shared edge origin IP hidden Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.
OTX Tags 2faphaasphishingtycoon
Kayıt kuruluşu Internet Domain Servic… BS(BS)
IP adresi 172.67.135.248 CDN
Coğrafi konumCA Toronto, CA
AS13335 · Cloudflare, Inc.
Kaynak IP, bir CDN proxy'sinin arkasına gizlenir. Uç adresine ilişkin Ters IP sonuçları ilgisiz kiracılar içerir; Kaynağı bulmak için pasif DNS veya sertifika şeffaflığı verileri gerekir.
KayıtOluşturuldu 07.07.2026 (74d · New) Expires 07.07.2027
HTTP Durumu403 Forbidden
Elapsed Since First Report 5 days
Neyi ölçüyoruz Raw elapsed time since the first stored abuse report. It is not a registrar response-time measurement. Latest observed status: Ulaşılabilir · erişim kısıtlı.
Her raporun içeriği Saklanan giden rapor kayıtları, satıcı kararları, kayıt verileri, barındırma ayrıntıları, sınıflandırmalar veya ekran görüntüleri gibi o sırada mevcut olan kanıtlara referans verebilir. Bu sayfa, teslim edilen yükün, alındığının, onaylandığının veya alıcının yaptığı eylemin tam olarak ne olduğu konusunda bir sonuç çıkarmaz.
Teknik ayrıntılarDNS, SSL SAN’ları, zaman damgaları
İlk Kez Tespit Edildi13.09.2026
DOM Analysisanalyzed 14.09.2026score 100/10011 brand signals
IoC Extractionscanned 14.09.20260 wallet · 0 Telegram IoCs
Submitted URLhttps://card-metamask.com/
Ad sunucularıanastasia.ns.cloudflare.comkurt.ns.cloudflare.com
TLS Fingerprint
TLS Observationvalid from 04.09.2026scanned 13.09.2026
Favicon Hash
Vaka kimliği
Sayfa başlığı
card-metamask.com
Impersonates
Across Arbitrum Avalanche Base BNB Chain Ethereum Linea MetaMask +3
TLS sertifikası
Valid transport encryption · Düzenleyen Google Trust Services / WE1 · valid for 74 days
Teknolojiler · 8 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

17 / 89 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed Previous stored snapshot: 17 detections
ChainPatrol
alphaMountain.ai
BitDefender
Certego
CRDF
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
Lionic
Seclookup
Sophos
VIPRE
Webroot
Site Performans Analizi

Google PageSpeed Insights — mobile performance audit of card-metamask.com · checked Sep 13, 2026

82
Needs Work
Performance
FCP
3.58s
First Contentful Paint
LCP
3.58s
Largest Contentful Paint
CLS
0.003
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
3.77s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Benzer alan adları

79 kayıtlı benzer alan adı

Tümünü göster (67)
metasmask.io insertion Dahili rapor metramask.io insertion Dahili rapor mewtamask.io insertion Dahili rapor mmetamask.io homoglyph Dahili rapor mtamask.io omission Dahili rapor mwetamask.io insertion Dahili rapor nmetamask.io homoglyph Dahili rapor metamark.io bitsquatting Dahili rapor metamaskj.io addition Dahili rapor metammask.io homoglyph Dahili rapor metamnask.io homoglyph Dahili rapor emtamask.io transposition m-etamask.io hyphenation meamask.io omission meatmask.io transposition meramask.io replacement mertamask.io insertion metaamask.io repetition metaamsk.io transposition metaask.io omission metalmask.io insertion metamaask.io insertion metamadsk.io insertion metamaek.io replacement metamak.io omission metamas.io omission metamasak.io insertion metamasdk.io insertion metamask-io.com various metamasl.io replacement metamasm.io replacement metamsak.io transposition metamsk.io omission metamusk.io vowel-swap metamzsk.io replacement metarnask.io homoglyph metmaask.io transposition metmask.io omission metsamask.io insertion metsmask.io replacement mettamask.io repetition metwmask.io replacement metyamask.io insertion metzmask.io replacement meyamask.io replacement meytamask.io insertion mitamask.io vowel-swap mnetamask.io homoglyph mretamask.io insertion mrtamask.io replacement mstamask.io replacement mteamask.io transposition mwtamask.io replacement rnetamask.io homoglyph matamask.io bitsquatting mdtamask.io bitsquatting metamasi.io bitsquatting metamasj.io bitsquatting metamaska.io addition metamaskk.io addition metamaskl.io addition metamaso.io bitsquatting metamesk.io bitsquatting metamqsk.io bitsquatting metemask.io bitsquatting netamask.io homoglyph xn--metamas-bhb.io homoglyph

Topluluk istihbaratı

2 topluluk raporu

KategoriPHISHING

@drainer Telegram

Kanıtlar ve Dış Raporlar

Community Scam Report — ChainAbuse
2 reports filed for card-metamask.com (1 written by a person) · category: Phishing · source checked
“@drainer Telegram”
— reported by Anonymous on Aug 14, 2024 · Source: ChainAbuse (TRM Labs) — full report and evidence there.
Gönderilen kanıt anlık görüntüsü
Sent: Ledger records: 1 Case ID: PD-20260913-BC90F2 Recipient: abuse@internet.bs
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 352.6 KB
Blocklist hits included with submission: ScamSniffer
PDF notice generated Notice text archived (640 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (BS):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and BS's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.

Bu Siteden Etkilendiniz mi?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi
Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin

Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/card-metamask.com"
  title="PhishDestroy threat report for card-metamask.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>