Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
capitalpointholdings.com favicon

capitalpointholdings.com

“Bot Verification”

Tehdit kararı Kritik 93/100 kanıt puanı
Kullanılabilirlik Bilinen son aktif En son saklanan erişilebilirlik gözlemi
VirusTotal algılamaları: 8/89 Spamhaus DBL: DBL_SPAM URLQuery threat systems: 1 alert Marka kimliğine bürünme: Unknown Genç alan adı: 19 günlük Bilinen son aktif
OTX: 5 refs 18.09.2026 Bilinmiyor 1 Report Sent
Actions API
⚠️
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 8. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
ABUSE NOTICE · 24H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@domrobot.com. The latest stored availability evidence still shows the domain reachable; 2 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
2 days
Reports sent
1
Latest case ID
PD-20260918-5933C5
Current status
HTTP 200 at latest stored check
Rapor özeti

capitalpointholdings.com — Bilinen son aktif (HTTP 200). Marka kimliğine bürünme: Unknown; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 8/89 (alphaMountain.ai, CRDF, Fortinet, Gridinsoft, Kaspersky); URLQuery 1 alert; Spamhaus DBL_SPAM; PhishDestroy score 93/100. Kayıt kuruluşu: INWX.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Kanıt özeti

KRİTİK
Puan
93/100

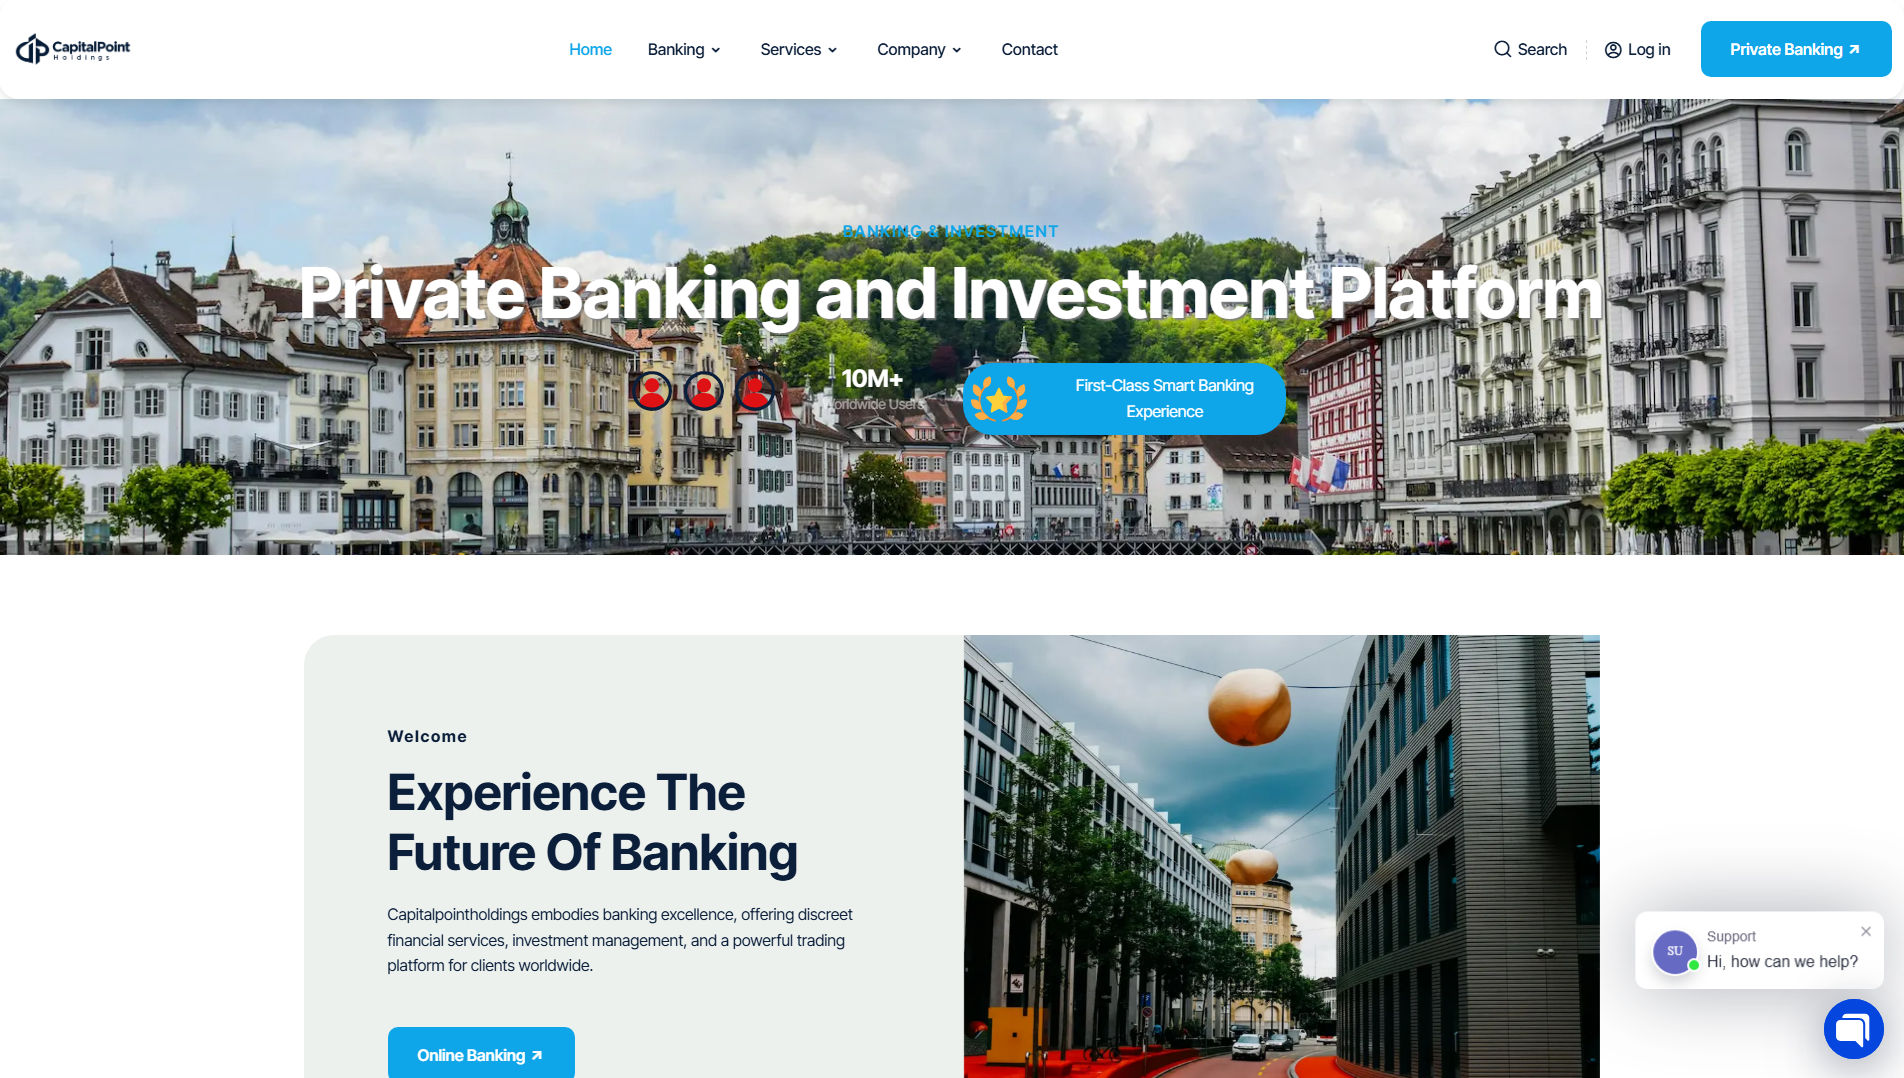
PhishDestroy first observed capitalpointholdings.com on Sep 18, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Bot Verification”. Stored page analysis classifies the content as impersonation. Current evidence score: 93/100 (critical).

Positive findings are stored from 3 sources: VirusTotal, Spamhaus DBL, and URLQuery. VirusTotal recorded 8 detections among 89 engines: alphaMountain.ai, CRDF, Fortinet, Gridinsoft, Kaspersky, SOCRadar, Sophos, desenmascara.me on Sep 19, 2026 at 21:02 UTC. Spamhaus DBL: DBL_SPAM on Sep 18, 2026 at 18:30 UTC. URLQuery recorded 1 threat-system alert on Sep 18, 2026 at 15:32 UTC. Non-positive and contextual checks: AlienVault OTX listed 5 community pulse references (not vendor detections) on Sep 18, 2026 at 16:20 UTC. The separate external-blocklist snapshot contained no matches on Sep 21, 2026 at 06:20 UTC. Google Safe Browsing returned no flag on Sep 20, 2026 at 22:00 UTC. URLScan completed without a malicious verdict (score 0) on Sep 19, 2026 at 03:30 UTC.

HTTP 200 was recorded on Sep 21, 2026 at 10:01 UTC. Registration records for the domain list INWX GmbH as the registrar and Sep 2, 2026 as the creation date. Registration preceded first observation by 16 days. At collection time, the hostname resolved to 198.251.84.200 on AS53667 (PONYNET - FranTech Solutions, US). The recorded endpoint location is Luxembourg, US. The stored server header is LiteSpeed. DOM analysis on Sep 18, 2026 at 22:20 UTC returned 93/100. The evidence archive retains 4 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YR2 as the certificate issuer with validity through Dec 1, 2026; checked Sep 18, 2026 at 16:02 UTC.

The content indicators and 3 positive source findings support the current Unknown-themed impersonation classification.

VirusTotal
VirusTotal
8 det.
URLQuery
URLQuery
1 threat alert
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
TLS sertifikası
Let's Encrypt / YR2
Yaş
19d Very New!
Gözlemlenen durum
Bilinen son aktif 200
PhishDestroy
DestroyList
Listelenmiş
Reports Sent
1
Veri kapsamı VirusTotal 8 / 89 URLQuery 1 threat-system alert OTX 5 community references CF Radarı scan completed URLScan capture saklanan rapor URLScan verdict Analiz tamamlandı TLS valid certificate, 70d WHOIS 19d old Ekran görüntüsü 4 captures · 3 sources Scamadviser 80/100
Ağ Güvenliği İstihbaratı
Threat Detection Systems 1 alert
Detection System Indicator Verdict Alert
DNS4EU capitalpointholdings.com malicious Sinkholed

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update Sep 19, 2026 · 07:34 UTC
    VirusTotal scanner detections updated from 7 to 8. Added scanner alerts: desenmascara.me.
  2. VirusTotal Detections Update Sep 19, 2026 · 04:56 UTC
    VirusTotal scanner detections updated from 6 to 7. Added scanner alerts: CRDF.
  3. Threat First Observed Sep 18, 2026 · 17:30 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 198.251.84.200.

Tehdit Müdahale Pipeline

Keşif
Checks
Reports
Erişilebilirlik
14/15
Sent Report Recorded
Stored sent-report record for registrar INWX GmbH, hosting provider, 2 abuse contacts
abuse@domrobot.comabuse@inwx.com
18.09.2026

Genel Engelleme Listesi Durumu

Evasion analysis

Cloaking & traffic-distribution check

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan
Server header seen by scanner
LiteSpeed

Scanner note: captcha: raw=captcha; http=200; via=https_proxy; server=LiteSpeed

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting

Kaydedilen görüntü · 4 sources

Etki Alanı Analizi

Alan adı
URLScan Verdict Analiz tamamlandı score 0 report ↗
Sunucu / ASN LiteSpeed · AS53667 PONYNET - FranTech Solutions, US
IP itibarı abuse score 20/100 3 reports Email SpamPort Scan checked 18.09.2026
Kayıt kuruluşu INWX NL(NL)
IP adresi 198.251.84.200 US
Coğrafi konumUS Luxembourg, US
AS53667 · FranTech Solutions
KayıtOluşturuldu 02.09.2026 (19d · Very New!) Expires 02.09.2027
HTTP Durumu200
Teknik ayrıntılarDNS, SSL SAN’ları, zaman damgaları
İlk Kez Tespit Edildi18.09.2026
DOM Analysisanalyzed 19.09.2026score 93/100
IoC Extractionscanned 19.09.20260 wallet · 0 Telegram IoCs
Submitted URLhttps://capitalpointholdings.com/
Ad sunucularıns5.asurahosting.comns5.my-control-panel.comns6.asurahosting.comns6.my-control-panel.com
MX Records0 capitalpointholdings.com
TLS Fingerprint
TLS Observationvalid from 02.09.2026scanned 18.09.2026
TLS SAN Domainscapitalpointholdings.com.allforonecode.comwww.capitalpointholdings.com.allforonecode.com
Favicon Hash
Vaka kimliği
Sayfa başlığı
Bot Verification
TLS sertifikası
Valid transport encryption · Düzenleyen Let's Encrypt / YR2 · valid for 70 days
Tehdit İstihbaratı Çapraz Referansı · source references
ScamAdviser Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
Teknolojiler · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

8 / 89 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed First positive detection Previous stored snapshot: 8 detections
alphaMountain.ai
CRDF
Fortinet
Gridinsoft
Kaspersky
SOCRadar
Sophos
desenmascara.me
Site Performans Analizi

Google PageSpeed Insights — mobile performance audit of capitalpointholdings.com · checked Sep 18, 2026

80
Needs Work
Performance
FCP
0.76s
First Contentful Paint
LCP
1.53s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
587ms
Total Blocking Time
SI
6.16s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Kanıtlar ve Dış Raporlar

Gönderilen kanıt anlık görüntüsü
Sent: Ledger records: 1 Case ID: PD-20260918-5933C5 Recipient: abuse@domrobot.com
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 1,772.0 KB
PDF notice generated Notice text archived (330 chars)
Abuse notice text as sent to the provider
Registrar: INWX GmbH & Co. KG (Germany)
Policy Violations: “Acceptable Use Policy prohibits phishing, identity fraud, malware and other illegal activities; registrar reserves the right to disable DNS or revoke domains used for abuse.”
Applicable Laws: German StGB §§202a–c; §263; EU Directive 2013/40/EU; ICANN DNS Abuse Framework

Bu Siteden Etkilendiniz mi?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi
Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin

Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/capitalpointholdings.com"
  title="PhishDestroy threat report for capitalpointholdings.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>