Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
blsp.gl favicon

blsp.gl

“blsp at”

Kayıt kuruluşu
NiceNIC
Resolved IP
101.99.93.48
Registered
28.06.2025
Tehdit kararı Kritik
Kullanılabilirlik Bilinen son aktif En son saklanan erişilebilirlik gözlemi
VirusTotal algılamaları: 5/91 Spamhaus DBL: DBL_SPAM Dolandırıcılık türü: Impersonation
OTX: 4 refs 25.09.2026 1 Report Sent
API
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 5. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@shinjiru.com.my. The latest stored availability evidence still shows the domain reachable; 16 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
16 days
Reports sent
1
Latest case ID
PD-20260924-B6271F
Current status
HTTP 200 at latest stored check
Rapor özeti

blsp.gl — Bilinen son aktif (HTTP 200). Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 5/91 (alphaMountain.ai, Forcepoint ThreatSeeker, Fortinet, Gridinsoft, SOCRadar); URLQuery 2 det.; Spamhaus DBL_SPAM; PhishDestroy score 88/100. Kayıt kuruluşu: NiceNIC.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Spamhaus DBL
DBL_SPAM
VirusTotal
VirusTotal
5 det.
URLQuery
URLQuery
2 det.
OTX references
URLScan
URLScan
TLS sertifikası
Süresi dolmuş veya doğrulanmamış
Yaş
1.3 yr
Gözlemlenen durum
Bilinen son aktif 200
PhishDestroy
DestroyList
Listelenmiş
Reports Sent
1

Source evidence

8 sources

VirusTotal

5 / 91

Bildir

Spamhaus DBL

DBL_SPAM

OTX

4 community references

Bildir

CF Radarı

provider verdict: clean

Bildir

URLScan capture

saklanan rapor

Stored URLScan capture preview
Bildir

URLScan verdict

Analiz tamamlandı

Bildir

Google Safe Browsing

Checked; no threat flag recorded

Bildir
Ağ Güvenliği İstihbaratı Registrar context
Registrar context NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
NiceNIC Verdict Full Investigation

Kanıt özeti

Kritik
VirusTotal
5/91
OTX
4 community refs
URLScan
Stored capture

Assessment

blsp.gl returned HTTP status 200 on 2026-10-01, according to the recorded HTTP check. The same domain was first observed on 2026-09-25, and a PhishDestroy internal listing is recorded as true.

Recorded Evidence

The OTX check on 2026-09-27 recorded 4 pulses for blsp.gl. VirusTotal, checked on 2026-09-30, recorded 5 detections across 91 scanners. The registration date is 2025-06-28 with NICENIC INTERNATIONAL GROUP CO., LIMITED as registrar, and the SSL certificate scanned on 2026-09-25 was issued by Let's Encrypt / YR2.

Interpretation

The OTX and VirusTotal observations were made on different dates, so their counts reflect separate snapshots rather than a single synchronized measurement. The HTTP check and PhishDestroy listing also carry distinct dates, which means a reader can compare timing but cannot treat any one record as a current state.

Recommended Actions

Retain the dated records for blsp.gl so that future checks can be compared against the 2026-09-25, 2026-09-27, 2026-09-30 and 2026-10-01 observations. When reviewing blsp.gl, avoid submitting passwords, payment details or other sensitive information, and rely on the recorded source values rather than assumptions about the domain.

Tespit ve kaçınma analizi

Gizleme ve trafik dağıtımı kontrolü

Henüz taranmadı Henüz tarayıcı ile tarayıcı arası bir fark kaydedilmemiştir

Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.

Kaydedilmiş gizleme bayrağı
Henüz taranmadı
Son gizleme taraması
Tarayıcı tarafından algılanan sunucu başlığı
nginx

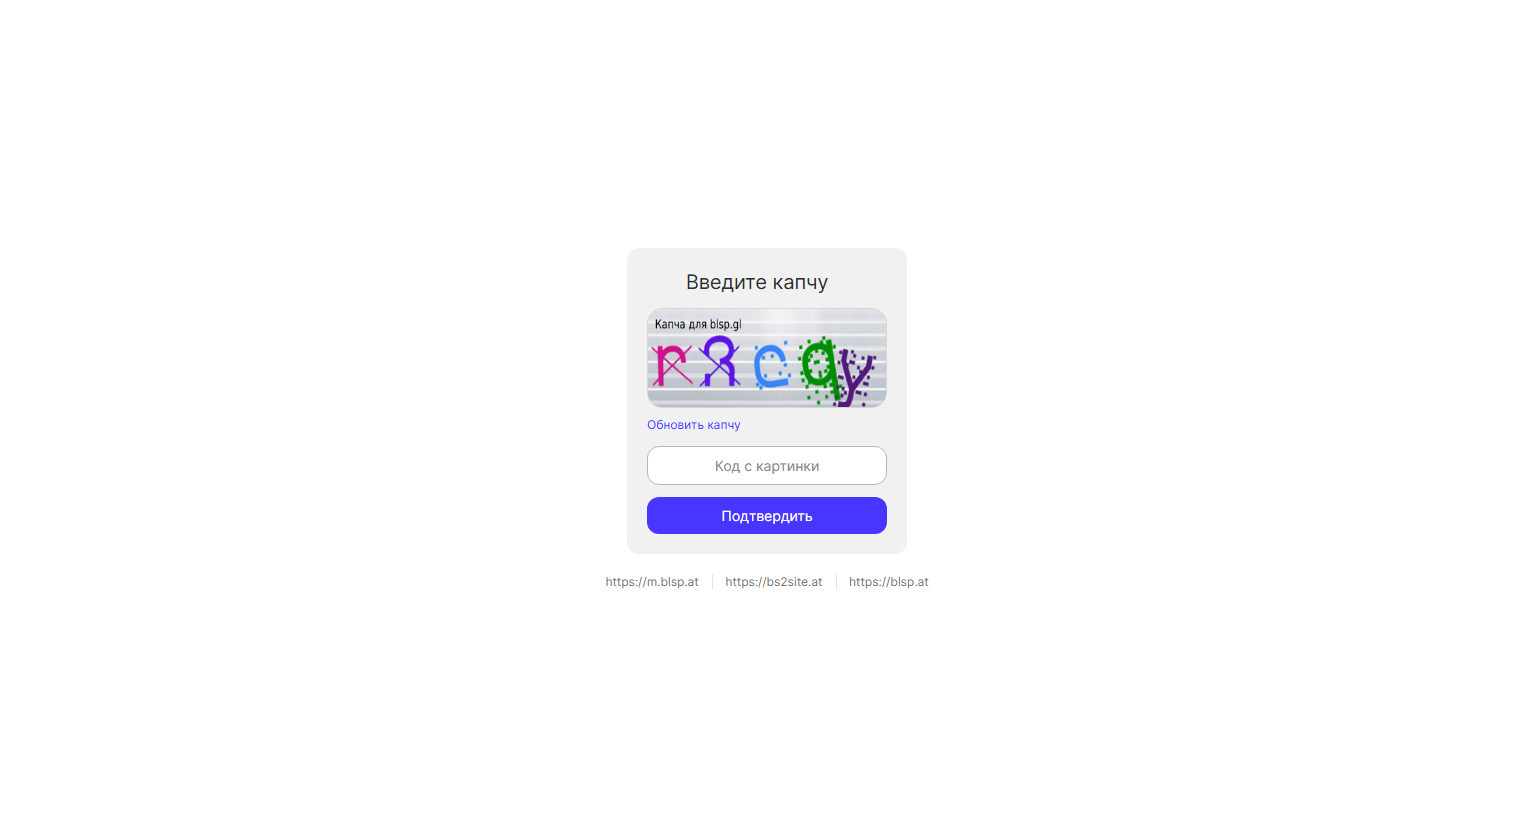
Tarayıcı notu: captcha: raw=captcha; http=200; via=https_proxy; server=nginx

TDS'da canlı parmak izi kontrolü
Bu panel açıkken, PhishDestroy tarayıcısından çalıştırıldığında yedi Keitaro parmak izi ve bir tarayıcı-crawler karşılaştırması görüntülenir.
Bekleme

Kaydedilen görüntü · 2 captures

Domain details

Alan adı
URLScan Verdict Analiz tamamlandı score 0 report ↗
IP itibarı abuse score 0/100 0 reports checked 25.09.2026
OTX Tags 2026-09activeall-domainsblocklistcontentcryptoalan adlarıdrainerfraudlivemonthlyphishdestroyphishingscam
Kayıt kuruluşu NiceNIC RU(RU) PhishDestroy Investigation
Kötüye kullanım iletişim bilgisiabuse@shinjiru.com.my, abuse@nicenic.net
ICANN Kayıt KuruluşuICANN Lookup (RDAP) →
KayıtOluşturuldu 28.06.2025 — Expires 28.06.2028
HTTP Durumu200
Teknik ayrıntılarProvenance & timestamps
İlk Kez Tespit Edildi25.09.2026
DOM Analysisanalyzed 09.10.2026score 88/100
Submitted URLhttps://blsp.gl/
Favicon Hash
Vaka kimliği
Sayfa başlığı
blsp at
TLS sertifikası
Hostname coverage not recorded · Düzenleyen Let's Encrypt / YR1 · stored validity ends in 74 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
101.99.93.48
Network ASN
AS45839
Organization
Shinjiru Technology Sdn Bhd
Observed location
Kuala Lumpur, MY
Server header
nginx

Ad sunucuları 2

  • clay.ns.cloudflare.com
  • izabella.ns.cloudflare.com

Location describes the IP network.

TLS sertifikası

Issuer
Let's Encrypt / YR1
Valid from
2026-09-25 19:22:05
Valid until
2026-12-24 19:22:04
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 04:03:35 UTC
Collection source
PhishDestroy collector
Certificate fingerprinte017a7a671d0df08a7e6cb7915da899054f5138e2a14a7443d7f0094c8c27791

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 101.99.93.48rapiddns.io

Latest Classified Outcome 2026-10-11 02:46:39 UTC

Primary outcome Reachable but protected reason: Captcha 85% confidence
Attribution mechanism: Challenge source: Current Http Probe
Evidence layers Availability: Reachable but protected Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Reachable but protected Captcha Challenge 85% 2026-10-11 02:46:39 UTC
RDAP registration Bilinmiyor
Observed timeline last reachable: 2026-10-11 02:46:39 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Teknolojiler · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

5 / 91 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed First positive detection Previous stored snapshot: 5 detections
alphaMountain.ai
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
SOCRadar

Arşivlenmiş Kanıtlar

Wayback Machine Snapshot
Kanıt incelemesi için geçmişe ait bir anlık görüntü mevcuttur
View Archive
Site Performans Analizi

Google PageSpeed Insights — mobile performance audit of blsp.gl · checked Sep 25, 2026

89
Needs Work
Performance
FCP
1.58s
First Contentful Paint
LCP
3.38s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
3.88s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-09-26 00:14:35 UTC
    VirusTotal scanner detections updated from 4 to 0. Resolved alerts: Fortinet, Gridinsoft, SOCRadar, alphaMountain.ai.
  2. VirusTotal Detections Update 2026-09-25 03:22:04 UTC
    VirusTotal scanner detections updated from 3 to 4. Added scanner alerts: SOCRadar.
  3. Threat First Observed 2026-09-24 23:30:01 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 101.99.93.48.

Tehdit Müdahale Pipeline

Keşif
Analysis
Notifications
Monitoring

14 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Tehdit Alındı
blsp.gl tespit edildi ve kapsamlı analiz için sıraya alındı
25.09.2026
Spamhaus DBL
Spamhaus DBL recorded DBL_SPAM
25.09.2026
URLScan.io Capture
Kaydedildi URLScan report with capture artifacts
25.09.2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
29.09.2026
VirusTotal
5/91 recorded on VirusTotal
06.10.2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
27.09.2026
Registrar Context: NiceNIC
Separate registrar research is available. Registrar association is contextual and is not scored as an independent detection.
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
25.09.2026
Technical Analysis Recorded
Rapor, depolanan teknolojiyi veya adli analiz sonuçlarını içerir.
11.10.2026
VT Detection -4
4 detections removed (4 → 0)
26.09.2026
VT Detection +1
+1 new detection (3 → 4): SOCRadar
25.09.2026
Sent Report Recorded
Stored outgoing record associated with registrar NICENIC INTERNATIONAL GROUP CO., LIMITED, 2 abuse contacts
abuse@shinjiru.com.myabuse@nicenic.net
24.09.2026
DestroyList Yayınlandı
25.09.2026
Monitoring Continues
Etki alanı erişilebilir durumda kalır veya erişimi kısıtlıdır; gelecekteki kontroller bu gözlemi güncelleyebilir.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Kanıtlar ve Dış Raporlar

Gönderilen kanıt anlık görüntüsü
Sent: Ledger records: 1 Case ID: PD-20260924-B6271F Recipient: abuse@shinjiru.com.my
Page title stored with report: blsp at
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 50.0 KB
PDF notice generated Notice text archived (416 chars)
Abuse notice text as sent to the provider
Registrar: NICENIC International Group Co., Limited (Hong Kong (China))
Policy Violations: “Services may be used only for lawful purposes… fraud, abuse and illegal activity prohibited. Violations may result in immediate suspension.” + dedicated abuse handling and takedown
Applicable Laws: Crimes Ordinance Cap.200 (Fraud), Theft Ordinance Cap.210 §16A (fraud by deception), Personal Data (Privacy) Ordinance Cap.486
Derinlemesine Analiz

Bu Siteden Etkilendiniz mi?

6 evidence signal groups linked 1 reports recorded Bilinen son aktif
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.

Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi

Template-based draft · optional AI wording assistance requires separate consent

Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir · Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/blsp.gl"
  title="PhishDestroy threat report for blsp.gl"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>