Güvenlik raporuna geç

bhd8fa6-4acb-be64-76e26a.xo.je

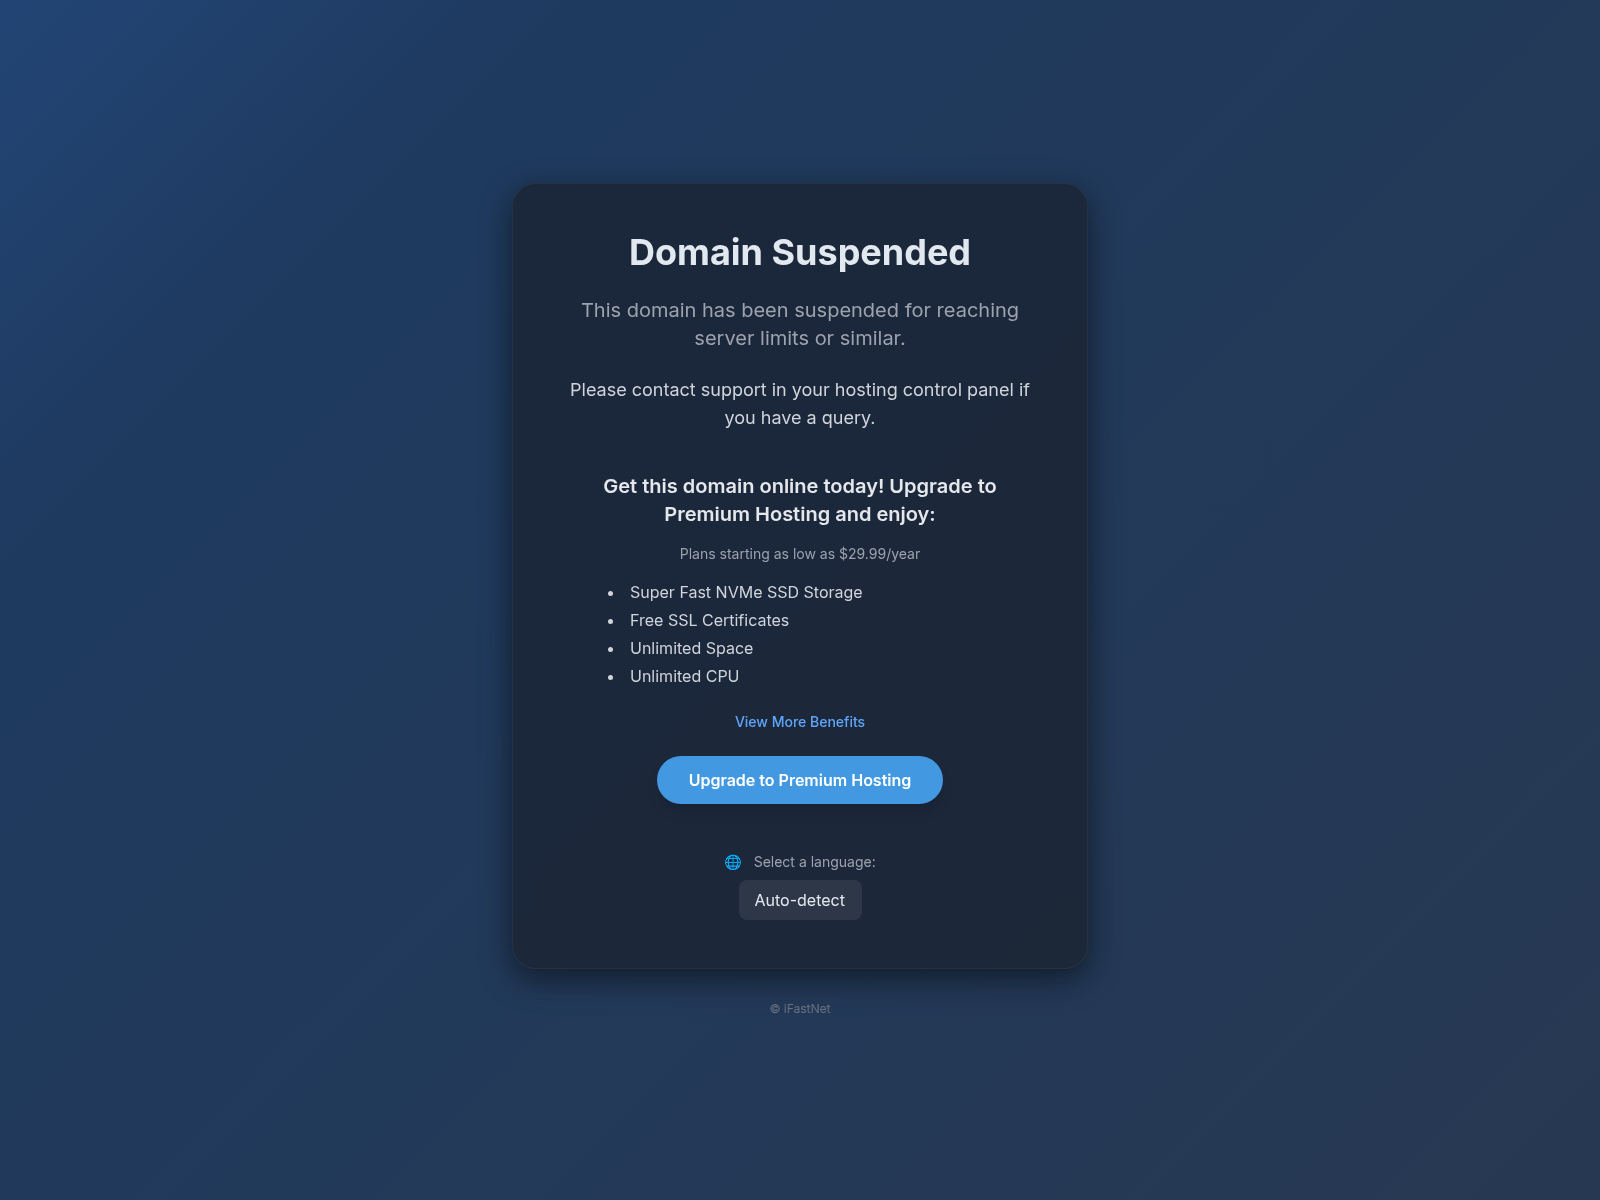
Dolandırıcılık türü: Account Takeover Page title: “Domain Suspended”

Availability last checked First listed 06.12.2025 VirusTotal analysed Sep 19, 2026 UTC

PhishDestroy verdict Kritik 91/100 evidence score

Based on 3 recorded source signals. The score is a heuristic over stored detections, not a probability or confidence level.

View evidence
Availability · last observation Doğrulanmamış

Mevcut erişilebilirlik doğrulanmadı

· Source: HTTP probe

Reachability is not a safety rating.

Key evidence

  • VirusTotal algılamaları: 12/89
  • Spamhaus DBL: DBL_PHISH
  • Dolandırıcılık türü: Account Takeover
IP
77.72.1.44
Stored capture 1 of 2 · Feb 27, 2026 UTC · Primary capture OpenAll capturesWayback

Evidence

Source checks and detection results recorded for this domain, with the time each was observed.

Rapor özeti

bhd8fa6-4acb-be64-76e26a.xo.je — Doğrulanmamış. Dolandırıcılık türü: Account Takeover. Kanıt özeti: VirusTotal 12/89 (BitDefender, Chong Lua Dao, CyRadar, ESET, Forcepoint ThreatSeeker); Spamhaus DBL_PHISH; CF Radar malicious; PhishDestroy score 91/100.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Source evidence

8 sources

VirusTotal

12 / 89

Bildir

CF Radarı

provider verdict: malicious

Bildir

Spamhaus DBL

DBL_PHISH

PhishStats

checked — no match recorded

OTX

no community references

Bildir

URLScan capture

saklanan rapor

Stored URLScan capture preview
Bildir

Google Safe Browsing

Checked; no threat flag recorded

Bildir
Detailed resultsVirusTotal vendor list · written summary · threat-intel cross-reference · cloaking analysis
Güvenlik Sinyalleri
SA Scamadviser Warnings 1/100
The Tranco rank (how much traffic) is rather low An iframe has been detected within the website The server of the site has several low reviewed other websites This website seems for sale at this time (how to get your money back) The website was reported in the last 30 days as threat by DNSFilter This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
We found a valid SSL certificate
Ağ Güvenliği İstihbaratı
CF Cloudflare Radar Verdict Zararlı
Phishing Security threats Phishing

Evidence summary

Stored written summary, generated Jul 23, 2026. It is not updated when source results change.

This summary quotes VirusTotal 20/95. The current stored result is 12/89 (analysed Sep 19, 2026).

The domain bhd8fa6-4acb-be64-76e26a.xo.je was observed returning the page title "Domain Suspended" and is currently taken offline. DNS resolution points to the IPv4 address 77.72.1.44, which is announced by AS12488 (Krystal Hosting Ltd) located in Great Britain. The domain lacks publicly resolvable nameservers, and no TLS certificate was presented when the host was queried, indicating an absence of encrypted traffic. Reputation services record a Scamadviser trust score of 1 out of 100, reflecting extreme suspicion.

Read full summary

The domain appears on a single security blocklist and has been explicitly flagged by the PhishDestroy feed. VirusTotal analysis shows that 20 out of 95 scanned security vendors flagged the domain as malicious, reinforcing the notion of malicious intent despite the offline state. The intelligence categorizes the activity as an "Account Takeover" scam, though the targeted brand or service is not disclosed in the available data.

The combination of a low trust score, lack of SSL, presence on a blocklist, and multiple vendor detections suggests the domain was deployed to harvest credentials or session tokens before being shut down.

Uncertainty remains regarding the exact victim profile and the infrastructure used to deliver the malicious payload, as the site content was not captured before suspension. Defenders should continue to deny any outbound connections to 77.72.1.44, add the domain to perimeter deny lists, and monitor DNS logs for any resurgence of the hostname or related sub‑domains. Additional investigation of Krystal Hosting Ltd’s IP range may reveal other malicious actors sharing the same hosting environment.

VirusTotal Analizi

12 / 89 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed Previous stored snapshot: 14 detections
BitDefender
Chong Lua Dao
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SOCRadar
Sophos
VIPRE
Tespit ve kaçınma analizi

Gizleme ve trafik dağıtımı kontrolü

Henüz taranmadı Henüz tarayıcı ile tarayıcı arası bir fark kaydedilmemiştir

Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.

Kaydedilmiş gizleme bayrağı
Henüz taranmadı
Son gizleme taraması

Tarayıcı notu: timeout: raw=timeout; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='bhd8fa6-4acb-be64-76e26a.xo.je', port=80): Max retries exceeded with url: / (Caused by Con

TDS'da canlı parmak izi kontrolü
Bu panel açıkken, PhishDestroy tarayıcısından çalıştırıldığında yedi Keitaro parmak izi ve bir tarayıcı-crawler karşılaştırması görüntülenir.
Bekleme

Domain & infrastructure

IP 77.72.1.44

Domain details

Alan adı
IP itibarı abuse score 0/100 0 reports checked 25.09.2026
Registrar (base domain) Bilinmiyor
Kötüye kullanım iletişim bilgisiabuse@ifastnet.com
Teknik ayrıntılarProvenance & timestamps
İlk Kez Tespit Edildi06.12.2025
DOM Analysisanalyzed 27.07.2026score 88/100
Submitted URLhttp://bhd8fa6-4acb-be64-76e26a.xo.je/

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
77.72.1.44
Network ASN
AS12488
Organization
Krystal Hosting Ltd
Observed location
London, GB
Server header
openresty

Location describes the IP network.

Kayıtlar

2 stored captures · Wayback archive

Kaydedilen görüntü · 2 captures

Sayfa başlığı
Domain Suspended

Arşivlenmiş Kanıtlar

Wayback Machine Snapshot
Kanıt incelemesi için geçmişe ait bir anlık görüntü mevcuttur
View Archive

Reports & history

No abuse reports recorded · first listed 06.12.2025 · detection timeline

Latest Classified Outcome 2026-10-14 10:41:21 UTC

Primary outcome Bilinmiyor reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Bilinmiyor Probe Inconclusive 20% 2026-10-14 10:41:21 UTC
RDAP registration Bilinmiyor
Observed timeline last reachable: 2026-09-15 22:17:50 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-07-26 22:23:32 UTC
    Domain state transitioned from dead to alive.
  2. Cloudflare Radar Scan 2026-03-07 11:44:23 UTC
    Cloudflare Radar scan registered: View Radar report.
  3. Domain Status Transition 2026-03-01 04:45:09 UTC
    Domain state transitioned from alive to dead.

Tehdit Müdahale Pipeline

Keşif
Analysis
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Topluluk raporları

1 topluluk üyesi tarafından bildirildi; ilk görülme 06.12.2025

Kayıtlı raporlar
1
Bildirilen benzersiz URL’ler
1
Kabul edildi1

Get help

Official reporting channels, a complaint draft, and listing review

Bu Siteden Etkilendiniz mi?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.

Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi
Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir · Kendiniz inceleyin ve gönderin

Tools & export

External lookups, JSON / PDF export, API and embed code
Analyze on destroy.tools Run a fresh external analysis of bhd8fa6-4acb-be64-76e26a.xo.je (opens in a new tab)

Kanıtlar ve Dış Raporlar

Derinlemesine Analiz
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/bhd8fa6-4acb-be64-76e26a.xo.je"
  title="PhishDestroy threat report for bhd8fa6-4acb-be64-76e26a.xo.je"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
Canlı Tehdit Akışı Bu İlanı İtiraz Et

