VirusTotal
10 / 91
Bildir


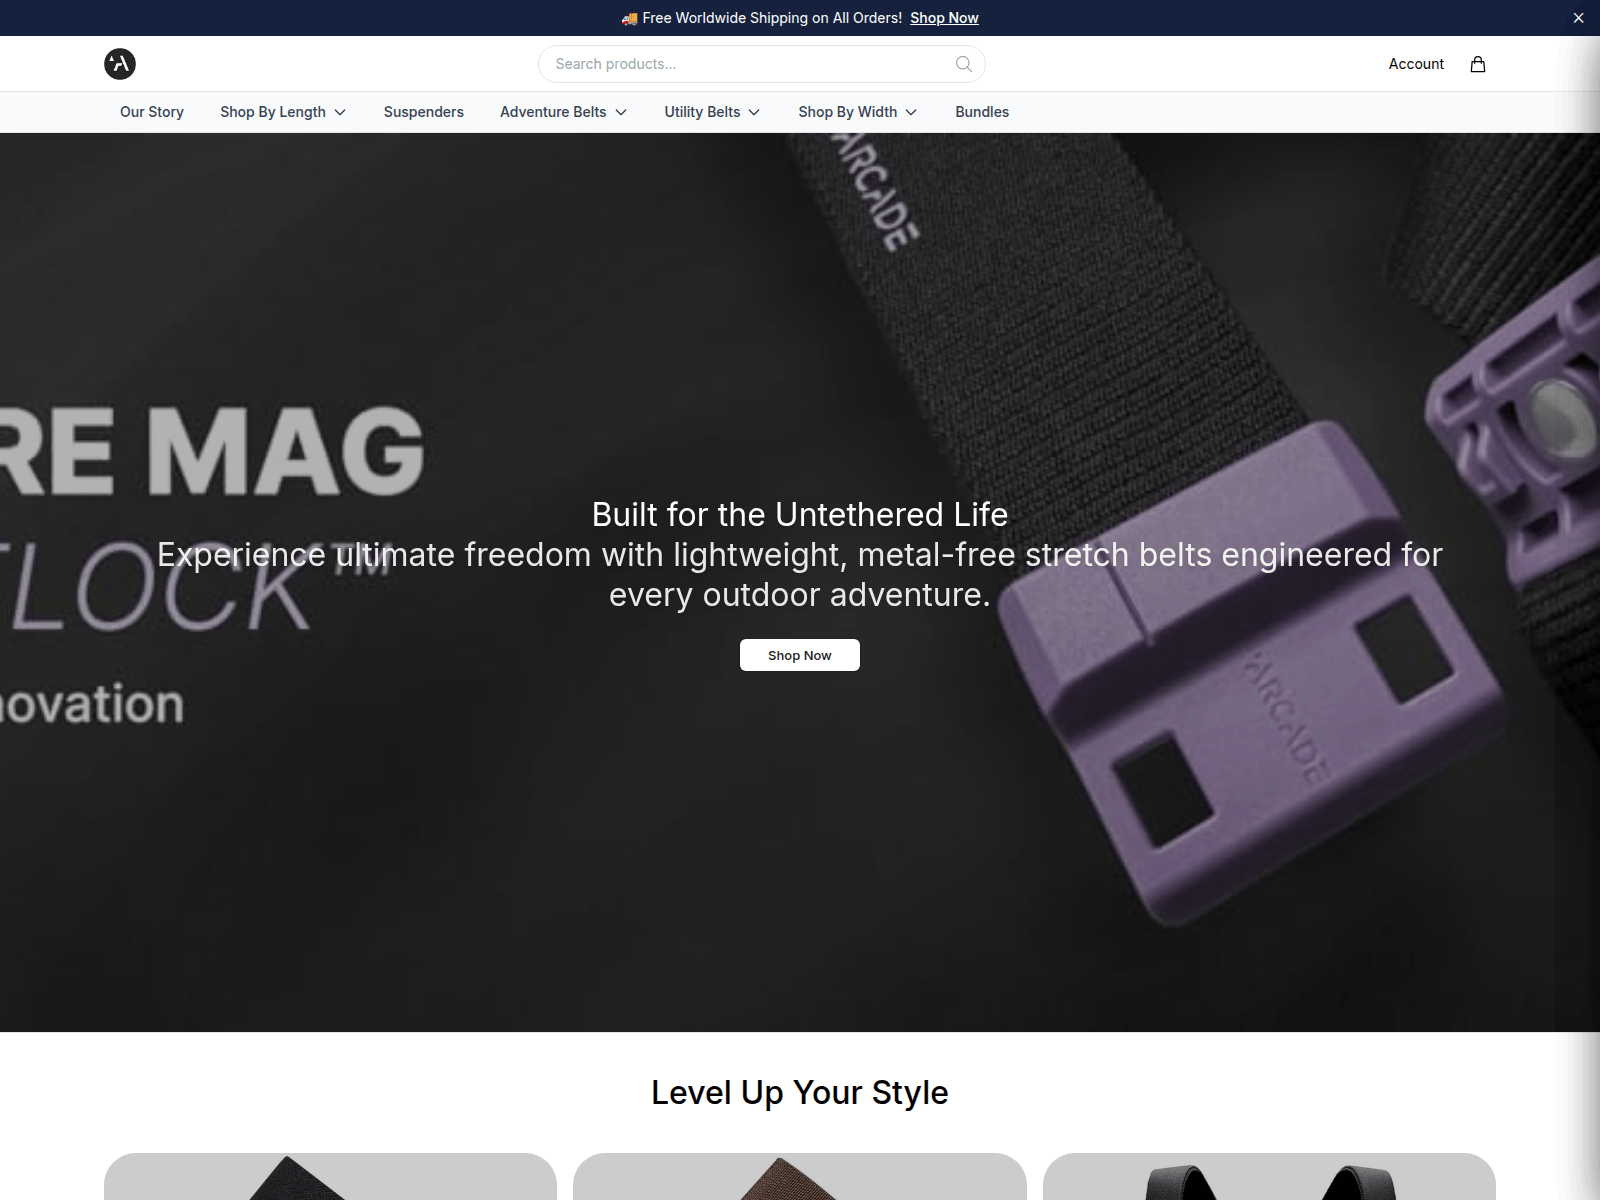
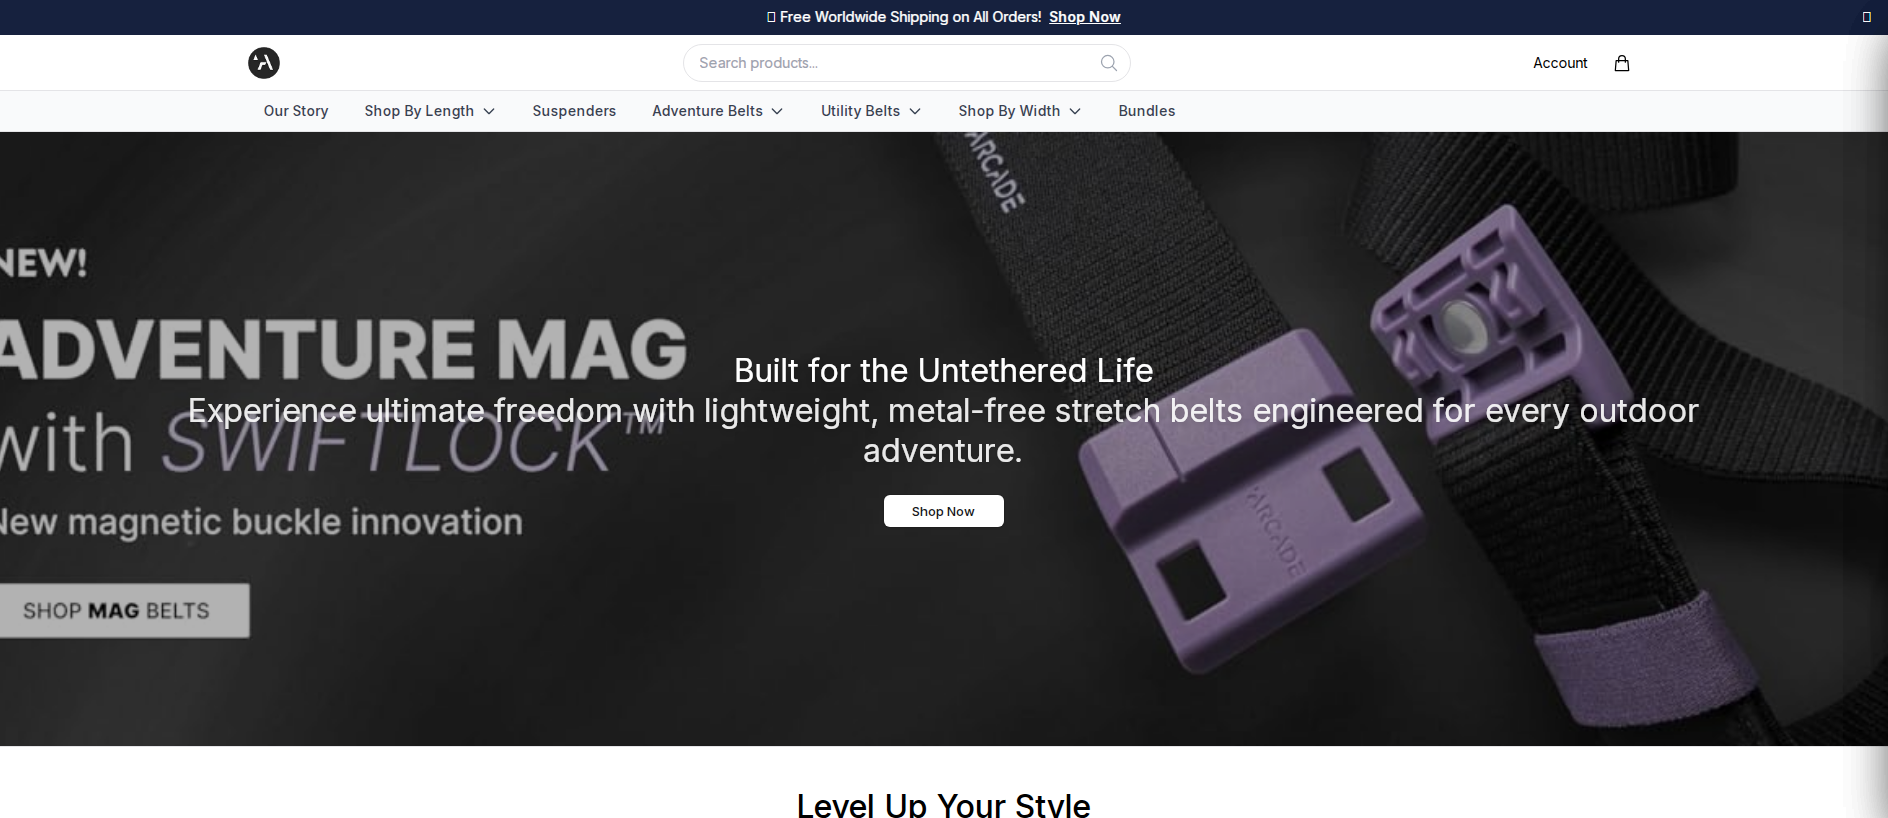
“Performance Stretch Adventure Belts | Arcade”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 8 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
arcadeofficial.shop — Bilinen son aktif (HTTP 200). Marka kimliğine bürünme: ["curve"]; Dolandırıcılık türü: Impersonation. Kanıt özeti: VirusTotal 10/91 (alphaMountain.ai, BitDefender, ESET, Forcepoint ThreatSeeker, Fortinet); URLQuery 2 det.; URLScan malicious verdict; Spamhaus DBL_SPAM; PhishDestroy score 100/100.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

arcadeofficial.shop was observed in multiple monitoring sources, with VirusTotal recording 10 detections from 91 scanners on 2026-09-24. The domain also received a PageSpeed performance score of 72 on 2026-10-03.
VirusTotal reported 10 detections out of 91 scanners for arcadeofficial.shop on 2026-09-24. OTX noted 4 pulses related to the domain as of 2026-10-03. The PhishDestroy internal listing included arcadeofficial.shop on 2026-10-03. A PageSpeed check measured a performance score of 72 on 2026-10-03.
The records from VirusTotal, OTX, and the PhishDestroy internal listing show that arcadeofficial.shop was catalogued by several monitoring services at different points in time. The PageSpeed performance score offers a technical measurement that is separate from security-related findings. Each source provides a distinct perspective on the domain's presence and characteristics as of their respective observation dates.
Preserve the VirusTotal, OTX, and PhishDestroy records for arcadeofficial.shop to support future reviews or monitoring. Compare these source observations with any new findings to track changes or updates. Use the PageSpeed performance score as a reference point for technical characteristics in subsequent assessments.
Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.
Tarayıcı notu: alive_content: raw=ok; http=200; via=https_proxy
bradley.ns.cloudflare.comlana.ns.cloudflare.comLocation describes the IP network.
627ff9938c60a1a74ef412af4dacf88b2b6ab6e6d3584ed3be5407b1a561ba39Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of arcadeofficial.shop · checked Oct 3, 2026
162.222.90.5. 12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
9 kayıtlı benzer alan adı
PD-20261003-EC2D27 Recipient: abuse@rashost.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Template-based draft · optional AI wording assistance requires separate consent
Her bir satır, bir etki alanının bu ana bilgisayara bağlanmasının bir nedenini gösterir. Düğüm boyutu, VirusTotal adresindeki algılamaları gösterir; kesikli çizgili düğümler ise halihazırda çevrimdışı durumdadır. Tam listeler aşağıda yer almaktadır.
Bu kaynak IP, birden fazla kimlik avı alanını barındırır; altyapı, kampanyalar arasında paylaşılabilir.
Bu alan adları, ["curve"] kullanıcılarını da hedef almaktadır. Tüm “["curve"]” tehditlerini görüntüle →
PhishDestroy veritabanından yeni eklenen raporlar. Bu keşif bağlantıları, paylaşılan altyapı veya mülkiyet anlamına gelmez.
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin