Güvenlik raporuna geç
Etki alanı güvenliği ve tehdit istihbaratı
appzerion.io favicon

appzerion.io

“Connect Wallet”

Kayıt kuruluşu
Immaterialism
Resolved IP
188.114.96.3
Registered
07.04.2026
Tehdit kararı Kritik
Kullanılabilirlik Ulaşılabilir · erişim kısıtlı Ulaşılabilir yanıt; sayfa içeriği doğrulanmadı Gözlemlenen
Source: HTTP probe
VirusTotal algılamaları: 8/91 Spamhaus DBL: DBL_PHISH Saklanan engelleme listesi eşleşmeleri: 3 Marka kimliğine bürünme: Ethereum Bilinen son aktif
OTX: 4 refs 12.08.2026 Ethereum CDN
API
Bu alan adı, zararlı olarak işaretlenmiştir
Güvenlik motorları bir algılama bildiriyor: 8. Bir eşleşme bildiren genel engellenenler listeleri: 3. Çok dikkatli olun — kimlik bilgilerini veya kişisel bilgileri girmeyin.
Rapor özeti

appzerion.io — Ulaşılabilir · erişim kısıtlı (HTTP 403). Marka kimliğine bürünme: Ethereum; Dolandırıcılık türü: Crypto Drainer. Kanıt özeti: VirusTotal 8/91 (ChainPatrol, alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Fortinet); Spamhaus DBL_PHISH; 3 external blocklist matches (MetaMask, ScamSniffer, SEAL); PhishDestroy score 100/100. Kayıt kuruluşu: Immaterialism.

Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
8 det.
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
TLS sertifikası
Süresi dolmuş veya doğrulanmamış
Yaş
6 mo
Gözlemlenen durum
Ulaşılabilir · erişim kısıtlı 403
PhishDestroy
DestroyList
Listelenmiş

Source evidence

8 sources

VirusTotal

8 / 91

Bildir

Spamhaus DBL

DBL_PHISH

OTX

4 community references

Bildir

CF Radarı

provider verdict: clean

Bildir

URLScan capture

saklanan rapor

Stored URLScan capture preview
Bildir

URLScan verdict

Analiz tamamlandı

Bildir

Google Safe Browsing

Checked; no threat flag recorded

Bildir

Kanıt özeti

Kritik
VirusTotal
8/91
OTX
4 community refs
URLScan
Stored capture

Assessment

Stored evidence for appzerion.io: VirusTotal recorded 1 detections among 91 scanners on 2026-08-12. That ratio reproduces the stored check in its original units and is not converted into another measure. ScamSniffer appear as named external blocklist observations for appzerion.io. Each item in this report remains at the scope supplied by its dated source record.

Detection Evidence

VirusTotal records 1 detections among 91 scanners in the stored snapshot dated 2026-08-12. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-08-12 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.

Source Context

ScamSniffer are recorded as named external blocklist observations for appzerion.io in the snapshot dated 2026-08-12. The stored ScamSniffer blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains appzerion.io as a publisher record. That PhishDestroy record is counted separately from the ScamSniffer external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.

Reachability and Timeline

The record first observed appzerion.io on 2026-08-12. The ScamSniffer blocklist snapshot is dated 2026-08-12 and remains a separate event in the stored timeline. The registration date is separately recorded as 2026-04-07. A URLScan reference was stored on 2026-08-12 as a dated artifact for review. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.

Registration and Infrastructure

For appzerion.io, the registrar field records Immaterialism Limited; this is kept as an exact source value. The source stores 188.114.96.3 as the observed address in this record. The registration date for appzerion.io is recorded as 2026-04-07. The SSL issuer is recorded as Google Trust Services / WE1 in the snapshot dated 2026-08-12. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.

Conclusion

The appzerion.io record states that VirusTotal recorded 1 detections among 91 scanners on 2026-08-12. ScamSniffer remain named blocklist observations from the snapshot dated 2026-08-12. PhishDestroy remains a separate publisher catalogue entry in the stored record. For appzerion.io, the registrar field records Immaterialism Limited; this remains separate from the other source fields. The observed address field in this record contains 188.114.96.3. The supported conclusion is bounded to the exact stored observations for appzerion.io. Any statement beyond those source values would require additional dated material.

Recommended Actions

Avoid submitting sensitive information to appzerion.io during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain appzerion.io as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and ScamSniffer blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to appzerion.io. The stored record does not justify extending that rule to 188.114.96.3 or to other infrastructure records.

Tespit ve kaçınma analizi

Gizleme şüphesi: tarayıcı ve ziyaretçi başlıkları birbirinden farklı

Henüz taranmadı Henüz tarayıcı ile tarayıcı arası bir fark kaydedilmemiştir

Bu ana bilgisayar için saklanmış tarayıcı-karşı-tarayıcı gözlemleri ile Keitaro tarzı trafik dağıtım sistemleri için gerçek zamanlı parmak izi kontrolü.

Kaydedilmiş gizleme bayrağı
Henüz taranmadı
Son gizleme taraması
Tarayıcı tarafından algılanan sunucu başlığı
cloudflare

Tarayıcı notu: cloudflare_ban: raw=cf_phishing_block; http=403; via=https_proxy; server=cloudflare; provider_error=cloudflare_phishing_interstitial

Tarama Sırasında Sağlayıcının Yanıtı: cloudflare_phishing_interstitial

Güvenlik tarayıcısında görüntülenen başlıkSuspected Phishing | Cloudflare
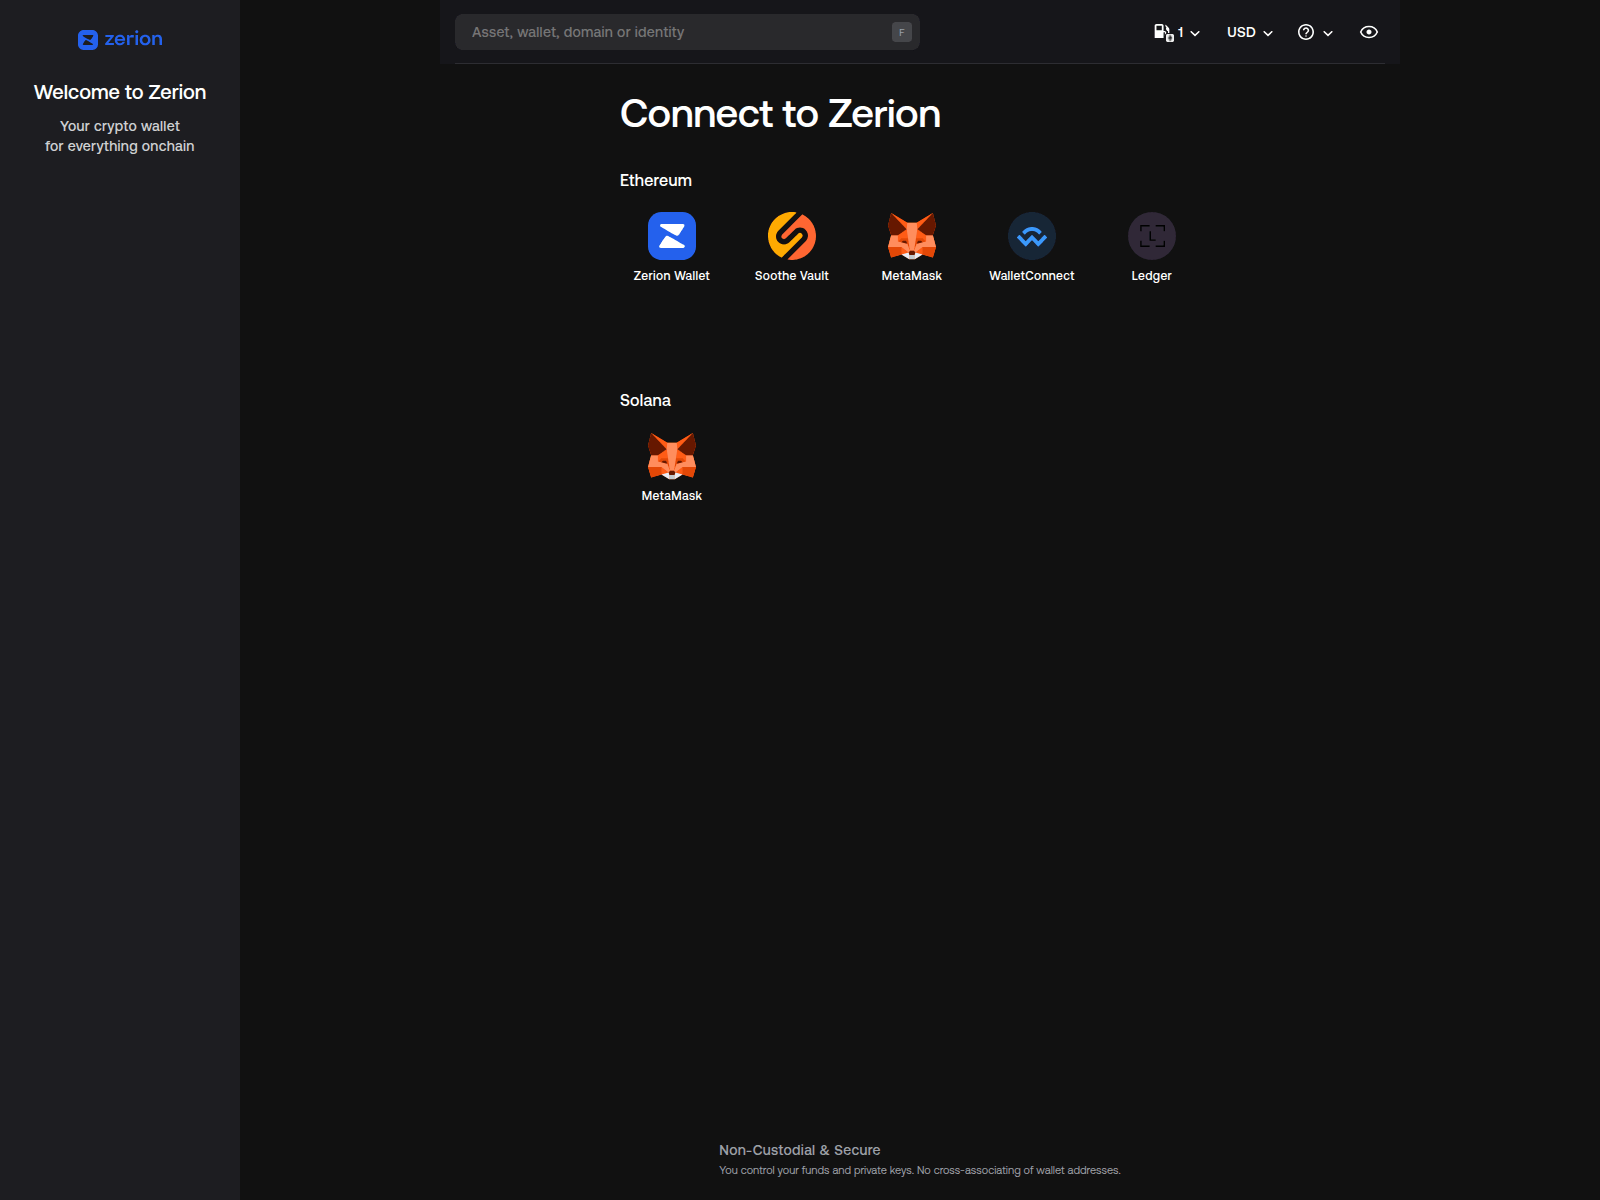
Tarayıcı ziyaretçisine gösterilen başlıkConnect Wallet
TDS'da canlı parmak izi kontrolü
Bu panel açıkken, PhishDestroy tarayıcısından çalıştırıldığında yedi Keitaro parmak izi ve bir tarayıcı-crawler karşılaştırması görüntülenir.
Bekleme

Kaydedilen görüntü · 2 captures

Domain details

Alan adı
URLScan Verdict Analiz tamamlandı score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.
OTX Tags 2026-08activeall-domainsblocklistcontentcryptoalan adlarıdrainerfraudlivemonthlyphishdestroyphishingscam
Kayıt kuruluşu Immaterialism VN(VN)
KayıtOluşturuldu 07.04.2026 (187d) — Expires 07.04.2027
HTTP Durumu403 Forbidden
Elapsed Since First Report 30 days
Neyi ölçüyoruz Raw elapsed time since the first stored abuse report. It is not a registrar response-time measurement. Latest observed status: Ulaşılabilir · erişim kısıtlı.
Her raporun içeriği Saklanan giden rapor kayıtları, satıcı kararları, kayıt verileri, barındırma ayrıntıları, sınıflandırmalar veya ekran görüntüleri gibi o sırada mevcut olan kanıtlara referans verebilir. Bu sayfa, teslim edilen yükün, alındığının, onaylandığının veya alıcının yaptığı eylemin tam olarak ne olduğu konusunda bir sonuç çıkarmaz.
Teknik ayrıntılarProvenance & timestamps
İlk Kez Tespit Edildi12.08.2026
DOM Analysisanalyzed 12.08.2026score 80/1005 brand signals
Submitted URLhttp://appzerion.io/
Favicon Hash
Sayfa başlığı
Connect Wallet
Impersonates
Ethereum Ledger MetaMask Solana Zerion
TLS sertifikası
Hostname coverage not recorded · Düzenleyen Google Trust Services · stored validity ends in 83 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.96.3
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.

Ad sunucuları 2

  • eric.ns.cloudflare.com
  • nena.ns.cloudflare.com

Location describes the IP network.

TLS sertifikası

Issuer
Google Trust Services
Valid from
2026-08-05 12:31:26
Valid until
2026-11-03 13:31:19
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-08-12 07:02:03 UTC
Collection source
PhishDestroy collector
Certificate fingerprint21bcfded559370616acf4c9a95d4bcb9afaedfdc949cfa85abc1cbab02605e91

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 188.114.96.3rapiddns.io

Latest Classified Outcome 2026-10-11 01:14:44 UTC

Primary outcome Provider block observed reason: Cloudflare anti-phishing block 95% confidence
Attribution Cloudflare mechanism: Phishing Interstitial source: Current Http Probe
Evidence layers Availability: Provider blocked Content: Provider blocked DNS: Resolved Registration: Unknown
Latest HTTP observation Provider block observed Cloudflare anti-phishing block Cloudflare Phishing Interstitial 95% provider marker verified 2026-10-11 01:14:44 UTC
RDAP registration Bilinmiyor
Observed timeline last reachable: 2026-09-15 22:17:49 UTC current episode first observed: 2026-10-01 01:39:51 UTC observed RIP window: 2026-09-15 22:17:49 UTC → 2026-10-01 01:39:51 UTC · 363.37h midpoint estimate ≈ 2026-09-23 11:58:50 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Teknolojiler · 4 identified
Detected via Cloudflare Radar · Wappalyzer engine
Bu Alan Adını Bildir Kanıt sunun ve başkalarını korumaya yardımcı olun

VirusTotal Analizi

8 / 91 güvenlik sağlayıcıları bu alanı işaretledi
View on VT
Last analyzed First positive detection Previous stored snapshot: 8 detections
ChainPatrol
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
SOCRadar
Sophos
Site Performans Analizi

Google PageSpeed Insights — mobile performance audit of appzerion.io · checked Aug 12, 2026

100
Good
Performance
FCP
0.91s
First Contentful Paint
LCP
1.65s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
0.91s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-08-14 22:15:14 UTC
    Domain state transitioned from dead to alive.
  2. Domain Status Transition 2026-08-14 12:11:44 UTC
    Domain state transitioned from alive to dead.
  3. VirusTotal Detections Update 2026-08-12 07:12:48 UTC
    VirusTotal scanner detections updated from 0 to 1. Added scanner alerts: SOCRadar.
  4. Threat First Observed 2026-08-12 06:38:35 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 188.114.96.3.

Tehdit Müdahale Pipeline

Keşif
Analysis
Monitoring

14 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Tehdit Alındı
appzerion.io tespit edildi ve kapsamlı analiz için sıraya alındı
12.08.2026
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
12.09.2026
URLScan.io Capture
Kaydedildi URLScan report with capture artifacts
12.08.2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
8/91 recorded on VirusTotal
26.08.2026
Engellenenler Listesi Algılama
Şu kaynakta bulunur: 3 blocklists: MetaMask, ScamSniffer, SEAL
11.10.2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
12.08.2026
Brand Impersonation
Impersonation of Ethereum
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
12.08.2026
Technical Analysis Recorded
Rapor, depolanan teknolojiyi veya adli analiz sonuçlarını içerir.
11.10.2026
Site Came Back Online
Domain is responding again — monitoring resumed
15.08.2026
Content Observed Unavailable
İzleme, kullanılamayan bir yanıt kaydetti (HTTP 403); nedeni bağımsız olarak belirlenmemiştir.
14.08.2026
VT Detection +1
+1 new detection (0 → 1): SOCRadar
12.08.2026
DestroyList Yayınlandı
12.08.2026
Monitoring Continues
Etki alanı erişilebilir durumda kalır veya erişimi kısıtlıdır; gelecekteki kontroller bu gözlemi güncelleyebilir.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Genel Engelleme Listesi Durumu

Benzer alan adları

52 kayıtlı benzer alan adı

ethercum.org homoglyph Dahili rapor etheruem.org transposition Dahili rapor athereum.org bitsquatting dethereum.org insertion e.thereum.org subdomain efhereum.org replacement ehereum.org omission etereum.org omission eth3reum.org replacement ether.eum.org subdomain etheream.org vowel-swap ethereim.org replacement
Tümünü göster (40)
ethereium.org insertion etherem.org omission etheremu.org transposition ethereom.org vowel-swap etheresum.org insertion ethereujm.org insertion ethereum2.org addition ethereum3.org addition ethereum4.org addition ethereumc.org addition ethereumd.org addition ethereumorg.com various ethereumr.org addition ethereums.org addition ethereumx.org addition ethereun.org homoglyph ethereunm.org homoglyph ethereurm.org homoglyph ethereurn.org homoglyph ethereuym.org insertion ethereuzm.org insertion ethereyum.org insertion etherium.org vowel-swap etherrum.org replacement etherteum.org insertion etherum.org omission ethezeum.org bitsquatting ethireum.org vowel-swap ethnereum.org insertion ethreum.org omission ethureum.org bitsquatting etihereum.org homoglyph ithereum.org vowel-swap othereum.org vowel-swap rethereum.org insertion sethereum.org insertion thereum.org omission uthereum.org bitsquatting zethereum.org insertion zthereum.org replacement

Kanıtlar ve Dış Raporlar

Derinlemesine Analiz

Bu Siteden Etkilendiniz mi?

5 evidence signal groups linked 0 reports recorded Ulaşılabilir · erişim kısıtlı
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.

Europol
AB ülkeniz için resmi raporlama kanalını bulun
National police directory
Kurtarma dolandırıcılarına dikkat edin! Suçlular, araştırmacı, avukat veya kurtarma görevlisi gibi davranarak mağdurlarla tekrar iletişime geçebilir. Peşin ücret ödemeyin veya kimlik bilgilerinizi paylaşmayın. Geri ödeme dolandırıcılığı hakkında daha fazla bilgi edinin →

Yerel Yetkililere Bildirin

resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.

97 ülke rehberi

Template-based draft · optional AI wording assistance requires separate consent

Yapay zeka destekli taslak — olay ayrıntıları yapay zeka sağlayıcısı tarafından işlenir · Kendiniz inceleyin ve gönderin

Herhangi Bir Alan Adını Kontrol Et

Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi

Şimdi Tara

Oltalama Olayını Bildir

Şüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun

Bildir

Canlı Tehdit Akışı

Son kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri

İzle

Gelişmelerden Haberdar Olun, Güvende Kalın

Canlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
Canlı Tehdit Akışı Bu İlanı İtiraz Et
HTML · IFRAME

Bu Raporu Yerleştir

Bu tehdit bilgisini web sitenizde veya blogunuzda paylaşın

embed.html
<iframe
  src="https://phishdestroy.io/tr/embed/domain/appzerion.io"
  title="PhishDestroy threat report for appzerion.io"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>


