VirusTotal
17 / 92
Сообщить
Interpretation & limits
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.


“Site is created successfully!”
Assessment based on the stored source evidence below. Review sources →
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@microsoft.com.
The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
palcay.de — Контент недоступен (HTTP 404). Олицетворение бренда: ["microsoft"]; Тип мошенничества: Impersonation. Сводка доказательств: VirusTotal 17/92 (alphaMountain.ai, Bfore.Ai PreCrime, BitDefender, CRDF, CyRadar); URLQuery 1 alert; URLScan malicious verdict; PhishDestroy score 98/100.
Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.

These are dated observations, not a live safety check. No flag, a stored capture, or a completed analysis does not establish that a site is safe.
17 / 92
Engine detections from this stored analysis. Vendors and collection times may differ from other sources.
1 threat-system alert
СообщитьAlerts refer to the preserved scan. They do not describe the current state of the site.
malicious
СообщитьThis is the recorded automated analysis. Completion alone is not a safety verdict.
5 community references
СообщитьCommunity publication references, not a vendor verdict or evidence of a common operator.
provider verdict: suspicious
A result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
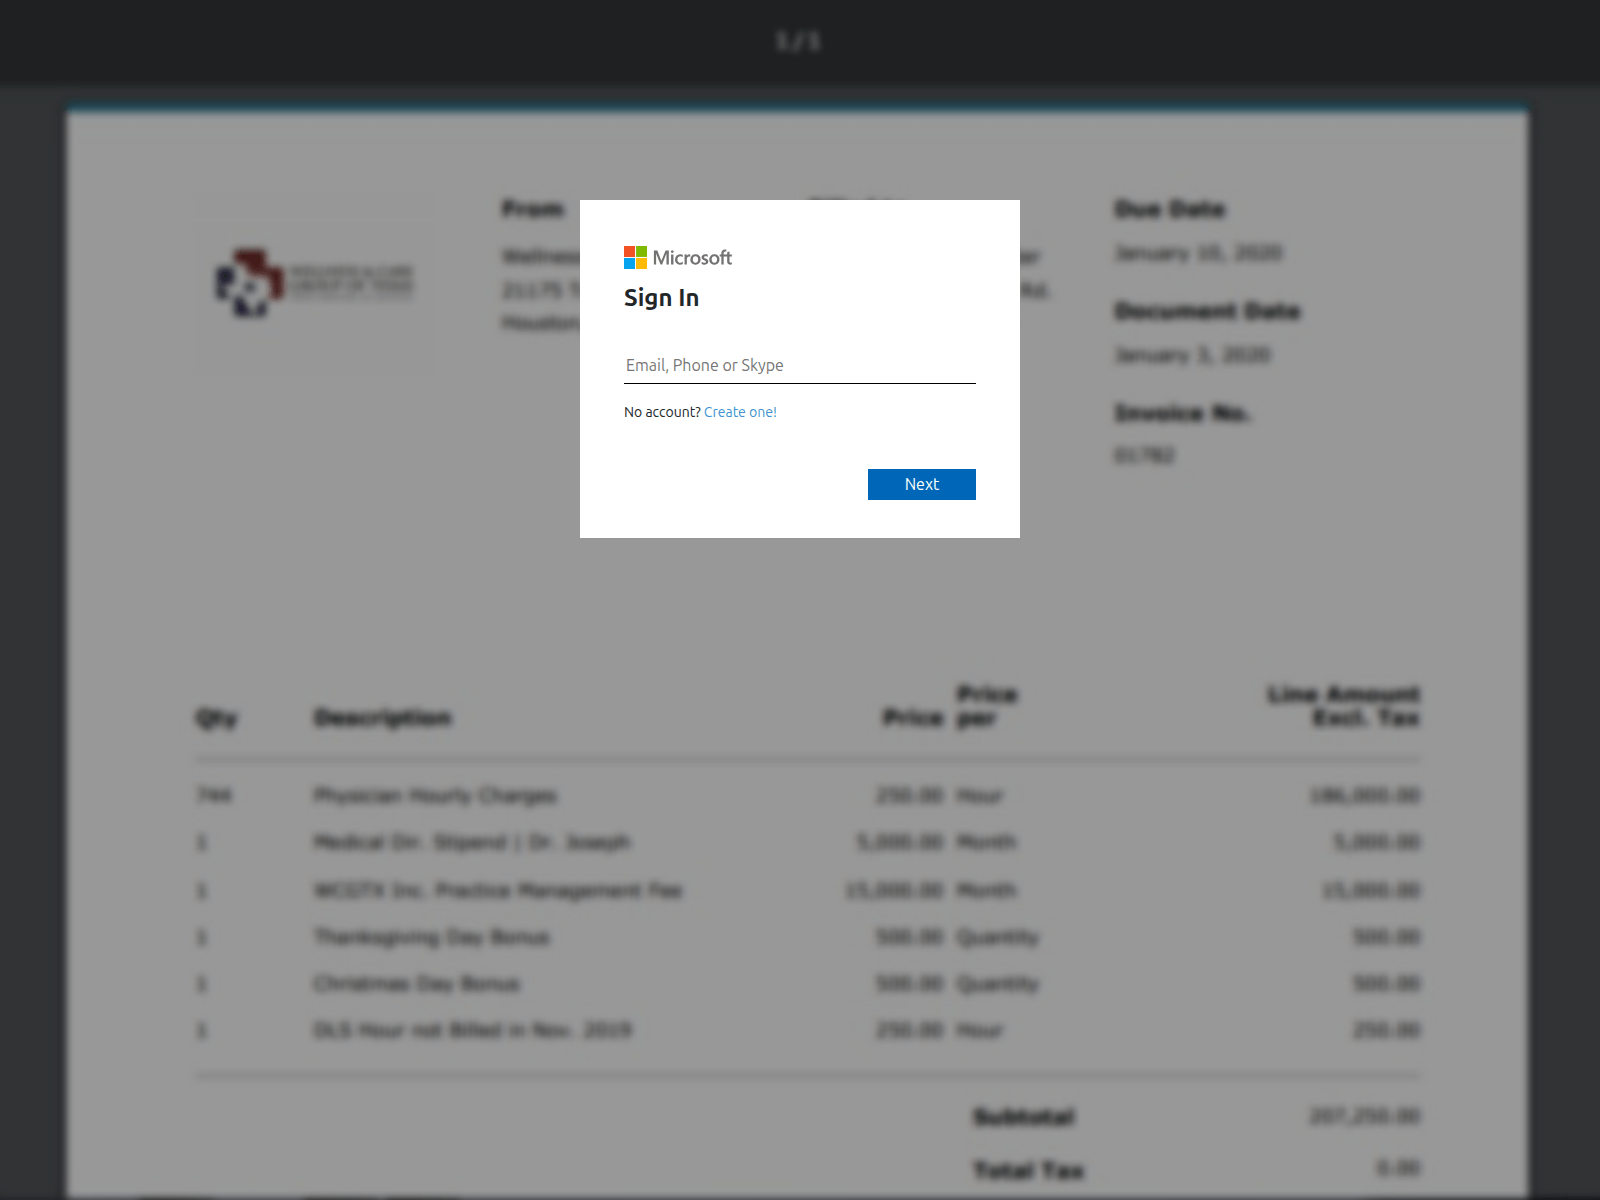
сохраненный отчет
 Сообщить
A preserved page image documents what the collector received; a capture is not a safety verdict.
Checked; no threat flag recorded
СообщитьA result applies to the recorded source and observation time. Absence of a flag is not proof of safety.
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | palcay.de |
malicious | Sinkholed |
The domain palcay.de is currently listed on a public security blocklist and remains active as of the report date, July 30, 2026. DNS resolution points to the IPv4 address 9.205.104.141, which is served by the authoritative nameservers atlas.dns-parking.com and hyperion.dns-parking.com – both commonly associated with parked or monetized domains. The presence of these parking nameservers suggests that the domain is not hosted on a dedicated web server but is instead leveraging a shared infrastructure that can be rapidly repurposed for malicious campaigns. The domain has been flagged by the PhishDestroy blocklist, confirming that at least one anti‑phishing feed has identified it as a threat.
VirusTotal analysis shows that three out of ninety‑one scanning engines have generated a detection, indicating that a minority of security products have recognized malicious activity associated with the domain, while the majority have not yet flagged it. This mixed detection profile underscores the need for defenders to treat the domain as suspicious even in the absence of a consensus across all vendors. No additional intelligence such as page titles, SSL certificate details, or specific brand impersonation has been disclosed, leaving the exact phishing lure undefined.
Consequently, security teams should block outbound connections to 9.205.104.141 and prevent DNS resolution of palcay.de at network perimeters. Continuous monitoring of threat‑intel feeds for any escalation in detection counts or additional blocklist listings is advised, as further analysis may reveal the targeted brand or payload characteristics. Until more granular evidence emerges, the domain should be considered a high‑risk phishing indicator and handled accordingly.
Сохраненные данные сравнения данных сканера и браузера для данного хоста, а также проверка отпечатков в режиме реального времени для систем распределения трафика типа «Кейтаро».
nginxLocal архивировано 2026-07-31 00:19:57 UTCПримечание к сканированию: http_other: raw=http_404; http=404; via=http_proxy; server=nginx
atlas.dns-parking.comhyperion.dns-parking.comLocation describes the IP network.
55e8c97c0767453a84df483292ac88d7fffb7f46900e138dc5c56e78e4837793Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of palcay.de · checked Jul 30, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://palcay.de/sappshttp://palcay.de/Server: nginxContent-Type: text/plainclosetext/plainThu, 30 Jul 2026 22:19:57 GMTnginxchunkedValues retained by the collector; long values may be shortened during collection.
Files, paths and sitemap entries retained by the collector.
/robots.txt
9.205.104.141.16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20260730-CE09EB Recipient: abuse@microsoft.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.


Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.
Template-based draft · optional AI wording assistance requires separate consent
Каждая полоса — это одна из причин, по которой домен связан с этим хостом. Размер узла обозначает обнаружения VirusTotal, а пунктирные узлы уже находятся в автономном режиме. Полные списки приведены ниже.
Тот же хеш фавиконы или тот же заголовок страницы, что и у этого хоста.
Еще один фишинговый домен использует этот исходный IP-адрес — возможно, совмещенную инфраструктуру.
Эти домены также нацелены на пользователей сайта ["microsoft"]. Просмотреть все угрозы, связанные с «["microsoft"]» →
Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.
Сканировать сейчасДобавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество
СообщитьНедавние сообщения о фишинге и наблюдаемые изменения доступности
ОтслеживатьОтслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание