




Безопасность домена и анализ угроз

mysticdao.click
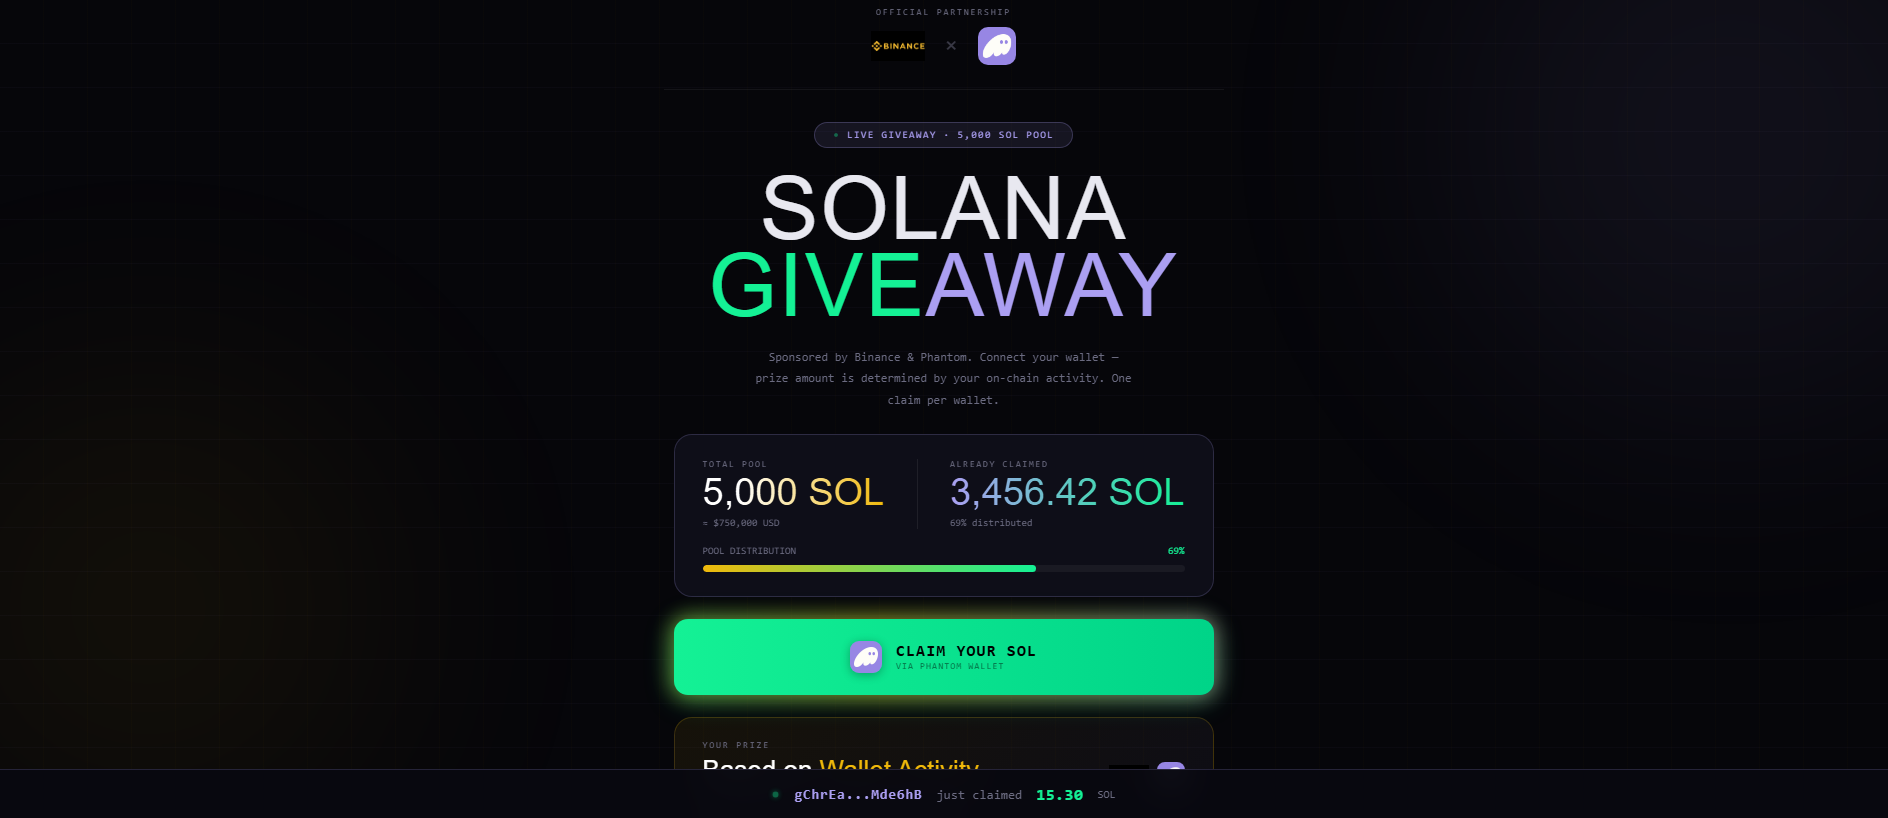
“SOL Giveaway — Binance × Phantom”
Вердикт по угрозе
Критический
95/100 оценка доказательств
Доступность
Контент недоступен
Контент был недоступен в последнем наблюдении.
Сигналы риска
Всего обнаружений вирусов: 7/89
Сохраненные совпадения в черном списке: 2.
URLQuery threat systems: 1 alert
Олицетворение бренда: Phantom
Actions
API
Краткий обзор отчёта
Stored evidence for mysticdao.click: VirusTotal recorded 4 detections among 89 scanners on 2026-09-11.
Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.
Сводка доказательств
КРИТИЧЕСКИЙ
Assessment
Stored evidence for mysticdao.click: VirusTotal recorded 4 detections among 89 scanners on 2026-09-11. That ratio reproduces the stored check in its original units and is not converted into another measure. MetaMask and SEAL appear as named external blocklist observations for mysticdao.click. Each item in this report remains at the scope supplied by its dated source record.
Detection Evidence
VirusTotal records 4 detections among 89 scanners in the stored snapshot dated 2026-09-11. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-09-11 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.
Source Context
MetaMask and SEAL are recorded as named external blocklist observations for mysticdao.click in the snapshot dated 2026-09-11. The stored MetaMask and SEAL blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains mysticdao.click as a publisher record. That PhishDestroy record is counted separately from the MetaMask and SEAL external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.
Reachability and Timeline
The record first observed mysticdao.click on 2026-09-11. The MetaMask and SEAL blocklist snapshot is dated 2026-09-11 and remains a separate event in the stored timeline. The registration date is separately recorded as 2026-01-18. A URLScan reference was stored on 2026-09-11 as a dated artifact for review. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.
Registration and Infrastructure
For mysticdao.click, the registrar field records Global Domain Group LLC; this is kept as an exact source value. The source stores 104.21.61.116 as the observed address in this record. The registration date for mysticdao.click is recorded as 2026-01-18. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.
Conclusion
The mysticdao.click record states that VirusTotal recorded 4 detections among 89 scanners on 2026-09-11. MetaMask and SEAL remain named blocklist observations from the snapshot dated 2026-09-11. PhishDestroy remains a separate publisher catalogue entry in the stored record. For mysticdao.click, the registrar field records Global Domain Group LLC; this remains separate from the other source fields. The observed address field in this record contains 104.21.61.116. The supported conclusion is bounded to the exact stored observations for mysticdao.click. Any statement beyond those source values would require additional dated material.
Recommended Actions
Avoid submitting sensitive information to mysticdao.click during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain mysticdao.click as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and MetaMask and SEAL blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to mysticdao.click. The stored record does not justify extending that rule to 104.21.61.116 or to other infrastructure records.
VirusTotal
7 det.
URLQuery
1 threat alert
URLScan
Сертификат TLS
Просрочен или не проверен
Возраст
8 mo
Зафиксированный статус
Контент недоступен

DestroyList
В списке
Reports Sent
1
Охват данных
VirusTotal
7 / 89
URLQuery
1 threat-system alert
OTX
no community references
CF Radar
scan completed
URLScan capture
сохраненный отчет
URLScan verdict
Анализ завершён
TLS
Просрочен или не проверен
WHOIS
8 mo old
Снимок экрана
4 captures · 3 sources
Данные сетевой безопасности
Threat Detection Systems
1 alert
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | mysticdao.click |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Domain Status Transition Sep 16, 2026 · 00:52 UTCDomain state transitioned from alive to dead.
-
Threat First Observed Sep 11, 2026 · 04:57 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
104.21.61.116.
Процесс реагирования на угрозы
Открытие
Checks
Reports
Доступность
15/15
Sent Report Recorded
Stored sent-report record for registrar Global Domain Group LLC, hosting provider, 1 abuse contact
abuse@globaldomaingroup.com
Статус в публичных блок-листах
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
Scanner note: timeout: raw=timeout; http=0; via=http_proxy; error=HTTPConnectionPool(host='154.6.59.178', port=6646): Read timed out. (read timeout=7)
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Сохранённый снимок · 4 sources
Аналитика доменов
Домен
URLScan Verdict
Анализ завершён
score 0 report ↗
Сервер / ASN
cloudflare · AS13335 CLOUDFLARENET - Cloudflare, Inc., US
IP Context
Cloudflare shared edge
origin IP hidden
Репутация Edge-IP не связана с этим доменом.
Регистратор
Global Domain Group
 (US)
(US)
IP-адрес
104.21.61.116
CDN
Геолокация San Francisco, US
San Francisco, USСетьAS13335 · Cloudflare, Inc.
Исходный IP-адрес скрыт за прокси-сервером CDN. Результаты обратного IP-адреса для граничного адреса содержат несвязанных клиентов; для определения источника требуется пассивный DNS или данные прозрачности сертификатов.
РегистрацияСоздано 18.01.2026 (245d) — Expires 18.01.2027
Технические деталиDNS, SAN в протоколе SSL, временные метки
Впервые обнаружено11.09.2026
DOM Analysis
IoC Extraction
Submitted URLhttp://mysticdao.click/
Серверы имёнjames.ns.cloudflare.commeiling.ns.cloudflare.com
Favicon Hash
ID дела
ICANN OVERSIGHT
Аккредитация и контекст RAA
Аккредитация и контекст RAA
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Аккредитация — это договор, а не знак безопасности.
Проверить сборы ICANN
Прочитать RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Технологии · 6 identified
Node.js
Programming languages
Vue.js
JavaScript frameworks
Nuxt.js
JavaScript frameworks
Web frameworks
Web servers
Static site generator
Cloudflare Browser Insights
Analytics
RUM
Cloudflare
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Пожаловаться на этот домен
Предоставьте доказательства и помогите защитить других
Анализ VirusTotal
7 / Поставщики средств безопасности 89 отметили этот домен
View on VT
Last analyzed Previous stored snapshot: 4 detections
alphaMountain.ai
CRDF
Ermes
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
SOCRadar
Анализ производительности сайта
Google PageSpeed Insights — mobile performance audit of mysticdao.click · checked Sep 11, 2026
92
Good
Performance
FCP
1.08s
First Contentful Paint
LCP
1.08s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
358ms
Total Blocking Time
SI
1.74s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Похожие домены
Сохранено 3 похожих домена
phantom-app.com
various
phantomapp.com
various
phantomx.app
addition
Доказательства и внешние отчеты
Анализ безопасности
Снимок отправленных доказательств
Sent: Ledger records: 1
Case ID:
PD-20260911-F9B74C Recipient: abuse@globaldomaingroup.com Page title stored with report: SOL Giveaway — Binance × Phantom
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT и разведка
DNS и сеть
SEO и домены
Повлиял ли на вас этот сайт?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.


«Action Fraud»
Сообщайте о мошенничестве и киберпреступлениях в Англии, Уэльсе и Северной Ирландии
Contact centre0300 123 2040
PhishDestroy listing review Не отчет правоохранительных органов
Обжалование решения по домену
Запросите проверку, если вы являетесь владельцем этого домена и считаете, что его данные неверны.
Остерегайтесь мошенников, предлагающих услуги по восстановлению данных! Преступники могут снова связаться с жертвами, притворяясь следователями, адвокатами или агентами по восстановлению. Не платите авансовые платежи и не делитесь учетными данными. Узнайте больше о мошенничестве при получении компенсаций →
Сообщите об этом в местные органы власти
Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.
Каталог 97 стран
Черновик по шаблону • помощь AI с формулировками включается только с отдельного согласия.
Просмотрите и отправьте его самостоятельно
Связанная инфраструктура и отчёты
Infrastructure map · mysticdao.click
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 4
Другие отчеты об общем крае Cloudflare 1
Эти отчеты относятся к одному и тому же общему граничному IP-адресу. Они помогают при обнаружении отчетов, но не подразумевают совместное владение или общий исходный сервер.
 cricfylivepros.com
Тот же регистратор: Global Domain Group 6
 provirtuetrading.com
 toronto-dominionsavings.com
Phantom impersonation 8
These domains also target Phantom users. View all Phantom threats →
Giveaway Scam kit 8
Part of the Мошенничество с розыгрышами phishing campaign. View all campaign domains →
 robinhood-main-dex-xkz.netlify.app
 trump-help.com
Недавние сообщения об угрозах 3
Недавно добавленные отчёты об угрозах. Эти ссылки не означают общую инфраструктуру или одного владельца.
 autoprimemarketrades.com
 vicocredit.com
Проверить любой домен
Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.
Сканировать сейчасСообщить о фишинге
Добавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество
СообщитьПоток оперативных данных об угрозах
Недавние сообщения о фишинге и наблюдаемые изменения доступности
ОтслеживатьБудьте в курсе событий, берегите себя
Отслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание