Перейти к отчёту о безопасности
Безопасность домена и анализ угроз
cryptomarginova.com favicon

cryptomarginova.com

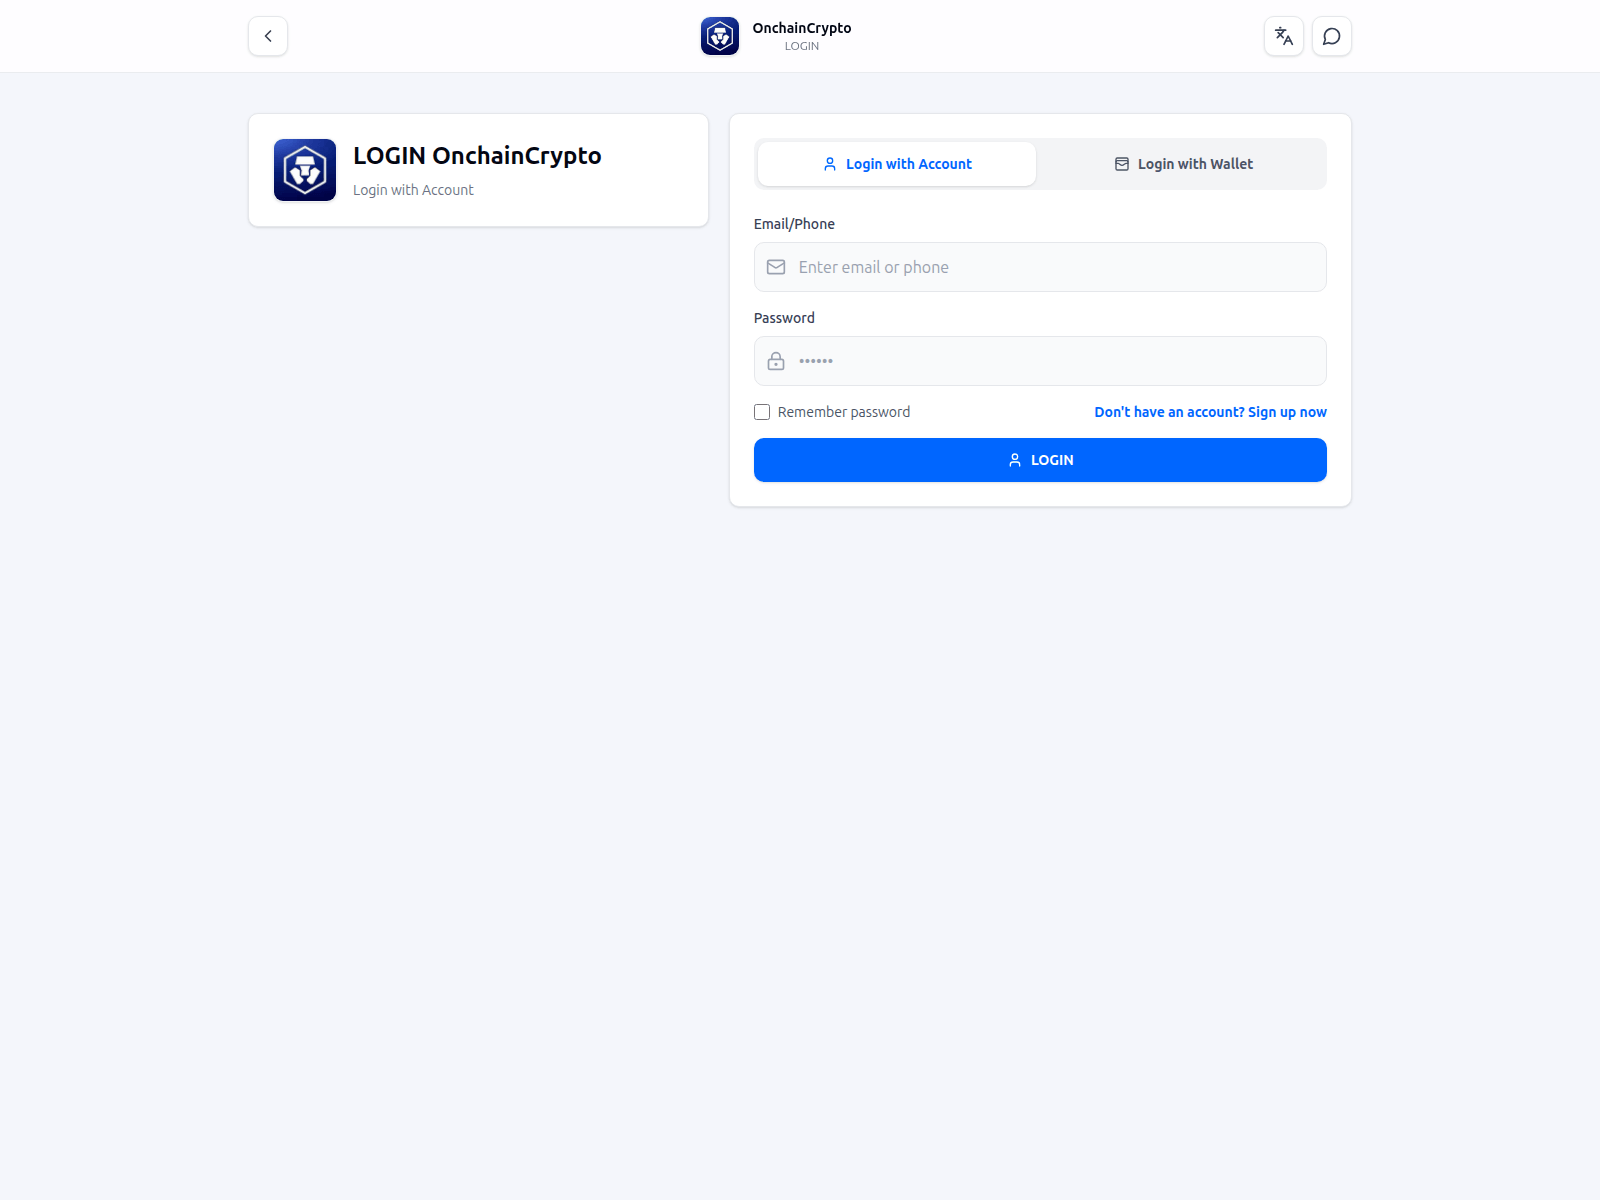
“OnchainCrypto - Trading, for everyone”

Регистратор
Realtime
Resolved IP
54.192.35.117
Registered
13.08.2026
Вердикт по угрозе Критический
Доступность Непроверенный Текущая доступность не проверена Наблюдаемое
Source: HTTP probe
VirusTotal detections: 8 (vendor total unavailable) Spamhaus DBL: DBL_PHISH Сохраненные совпадения в черном списке: 2.
OTX: 5 refs 11.10.2026 1 Report Sent
API
Этот домен был отмечен как вредоносный
Механизмы безопасности сообщают об обнаружении: 8. Публичные черные списки, сообщающие о совпадении: 2. Будьте предельно осторожны — не вводите учетные данные или личную информацию.
Краткий обзор отчёта

cryptomarginova.com — Непроверенный. Сводка доказательств: VirusTotal 8 detections (engine total unavailable) (alphaMountain.ai, BitDefender, CRDF, Forcepoint ThreatSeeker, G-Data); URLQuery 2 det.; URLScan capture; Spamhaus DBL_PHISH; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 100/100. Регистратор: Realtime.

Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.

Spamhaus DBL
DBL_PHISH
VirusTotal
VirusTotal
8 det.
URLQuery
URLQuery
2 det.
OTX references
Сертификат TLS
Просрочен или не проверен
Возраст
2 mo New
PhishDestroy
DestroyList
В списке
Reports Sent
1

Source evidence

6 sources

Spamhaus DBL

DBL_PHISH

URLScan capture

сохраненный отчет

Stored URLScan capture preview
Сообщить

Google Safe Browsing

Checked; no threat flag recorded

Сообщить

Сводка доказательств

Критический
VirusTotal
8 detections
OTX
5 community refs
URLScan
Stored capture

Assessment

cryptomarginova.com was observed with a blocklist record from MetaMask on 2026-10-11, documenting an external detection entry for that date. The domain also appears on another external blocklist, SEAL, as of the same day.

Recorded Evidence

MetaMask and SEAL both listed cryptomarginova.com on their external blocklists on 2026-10-11. PhishDestroy internally recorded the domain as listed, and the registrar is documented as Realtime Register B.V., with a registration date of 2026-08-13. The SSL certificate was issued by Amazon / Amazon RSA 2048 M04 and scanned on 2026-10-11.

Interpretation

PhishDestroy contains an internal listing for cryptomarginova.com, which records a specific type of detection relevant to its own monitoring scope. External blocklists such as MetaMask and SEAL provide additional context by documenting their own detection entries, which are separate from internal records. The evidence spans registration, certificate, and blocklist observations, allowing for comparison of technical and security-related data.

Recommended Actions

Preserve the blocklist records from MetaMask and SEAL for cryptomarginova.com to support ongoing security reviews. Retain the PhishDestroy internal listing as a reference point for internal detection history. Use the registration and SSL certificate details for technical context in future assessments.

Анализ методов обнаружения и уклонения

Проверка маскировки и распределения трафика

Еще не отсканировано Пока не было зафиксировано никаких различий между роботом-пауком и браузером

Сохраненные данные сравнения данных сканера и браузера для данного хоста, а также проверка отпечатков в режиме реального времени для систем распределения трафика типа «Кейтаро».

Сохраненный флаг маскировки
Еще не отсканировано
Проверка отпечатков пальцев в режиме реального времени с помощью «TDS»
Семь отпечатков Keitaro, а также сравнение кроулера и браузера — запускаются со сканера PhishDestroy при открытии этой панели.
Ожидание

Сохранённый снимок · 2 captures

Domain details

Домен
Репутация IP abuse score 0/100 0 reports checked 11.10.2026
OTX Tags 2026-10activeall-domainsblocklistcontentcryptoдоменовdrainerfraudlivemonthlyphishdestroyphishingscam
Регистратор Realtime
Контакт для жалобrtr-security-threats@realtimeregister.com
Реестр ICANNICANN Lookup (RDAP) →
РегистрацияСоздано 13.08.2026 (59d · New) — Expires 13.08.2027
Технические деталиProvenance & timestamps
Впервые обнаружено11.10.2026
DOM Analysisanalyzed 11.10.2026score 0/100
Submitted URLhttp://cryptomarginova.com/
Favicon Hash
ID дела
Заголовок страницы
OnchainCrypto - Trading, for everyone
Сертификат TLS
Certificate hostname mismatch · Выдан Amazon / Amazon RSA 2048 M04 · stored validity ends in 178 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
54.192.35.117
Network ASN
AS16509
Organization
Amazon.com, Inc.
Observed location
Frankfurt am Main, DE
Server header
nginx

Серверы имён 2

  • dax.ns.cloudflare.com
  • magnolia.ns.cloudflare.com

Location describes the IP network.

Сертификат TLS

Issuer
Amazon / Amazon RSA 2048 M04
Valid from
2026-09-22 00:00:00
Valid until
2027-04-07 23:59:59
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-11 13:02:04 UTC
Collection source
PhishDestroy collector
Certificate fingerprintdd98b3ce20457bfb3daadd76632c268cfb6ab50b36c9c6bbba26918be2f6f09e
Certificate names · 9 SANs
  • capitalnexiva.com
  • cryptoallocen.com
  • cryptocreditova.com
  • cryptoequitra.com
  • cryptoledgoria.com
  • cryptovaultoria.com
  • cryptoyieldon.com
  • equityvanta.com
  • marketliquora.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 54.192.35.117rapiddns.io

Latest Classified Outcome 2026-10-11 11:34:49 UTC

Primary outcome Неизвестно reason: Probe Inconclusive 20% confidence
Attribution source: Current State Backfill
Evidence layers Availability: Unreachable Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Неизвестно Probe Inconclusive 20% 2026-10-11 11:34:49 UTC
RDAP registration Неизвестно
Observed timeline last reachable: 2026-10-11 11:34:49 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Пожаловаться на этот домен Предоставьте доказательства и помогите защитить других

Анализ VirusTotal

8 detections recorded · vendor total unavailable
View on VT
alphaMountain.ai
BitDefender
CRDF
Forcepoint ThreatSeeker
G-Data
«Касперский»
Sophos
VIPRE

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-11 11:34:49 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 54.192.35.117.

Процесс реагирования на угрозы

Открытие
Analysis
Notifications
Monitoring

9 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Угроза устранена
cryptomarginova.com обнаружены и помещены в очередь для полного анализа
11.10.2026
Spamhaus DBL
Spamhaus DBL recorded DBL_PHISH
11.10.2026
URLScan.io Capture
Сохранено URLScan report with capture artifacts
11.10.2026
Обнаружение списков заблокированных адресов
Найдено в 2 blocklists: MetaMask, SEAL
11.10.2026
OTX Community References
5 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
11.10.2026
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
11.10.2026
Technical Analysis Recorded
Отчет содержит сохраненные технологии или результаты судебно-медицинской экспертизы.
11.10.2026
Sent Report Recorded
Stored outgoing record associated with registrar Realtime Register B.V., 1 abuse contact
rtr-security-threats@realtimeregister.com
11.10.2026
Опубликовано «DestroyList»
11.10.2026
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Статус в публичных блок-листах

Доказательства и внешние отчеты

Снимок отправленных доказательств
Sent: Ledger records: 1 Case ID: PD-20261011-C9AC11 Recipient: rtr-security-threats@realtimeregister.com
Page title stored with report: OnchainCrypto - Trading, for everyone
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 19.6 KB
Blocklist hits included with submission: MetaMask, SEAL
PDF notice generated Notice text archived (856 chars)
Abuse notice text as sent to the provider
AUP & Terms of Service Violations:
Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices.
Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension.
Applicable Legal Framework (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
Глубокий анализ

Повлиял ли на вас этот сайт?

6 evidence signal groups linked 1 reports recorded Непроверенный
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.

Европол
Найдите официальный канал отчетности для вашей страны ЕС
National police directory
Остерегайтесь мошенников, предлагающих услуги по восстановлению данных! Преступники могут снова связаться с жертвами, притворяясь следователями, адвокатами или агентами по восстановлению. Не платите авансовые платежи и не делитесь учетными данными. Узнайте больше о мошенничестве при получении компенсаций →

Сообщите об этом в местные органы власти

Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.

Каталог 97 стран

Template-based draft · optional AI wording assistance requires separate consent

Черновик по шаблону • помощь AI с формулировками включается только с отдельного согласия. · Просмотрите и отправьте его самостоятельно

Проверить любой домен

Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.

Сканировать сейчас

Сообщить о фишинге

Добавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество

Сообщить

Поток оперативных данных об угрозах

Недавние сообщения о фишинге и наблюдаемые изменения доступности

Отслеживать

Будьте в курсе событий, берегите себя

Отслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание
Поток оперативных данных об угрозах Подать жалобу на это объявление
HTML · IFRAME

Вставить этот отчет

Разместите эту информацию об угрозах на своём сайте или в блоге

embed.html
<iframe
  src="https://phishdestroy.io/ru/embed/domain/cryptomarginova.com"
  title="PhishDestroy threat report for cryptomarginova.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

