




Безопасность домена и анализ угроз

btcbrixalv575.com
“New Private Tab”
Вердикт по угрозе
Критический
100/100 оценка доказательств
Доступность
Последний известный активный
Последнее сохраненное наблюдение о доступности
Сигналы риска
Всего обнаружений вирусов: 17/89
URLQuery threat systems: 5 alerts
Олицетворение бренда: Unknown
Последний известный активный
Actions
API
ABUSE NOTICE · 7D+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@omegatech.sc.
The latest stored availability evidence still shows the domain reachable; 10 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
10 days
Reports sent
1
Latest case ID
PD-20260909-8C90B2
Current status
HTTP 200 at latest stored check
Краткий обзор отчёта
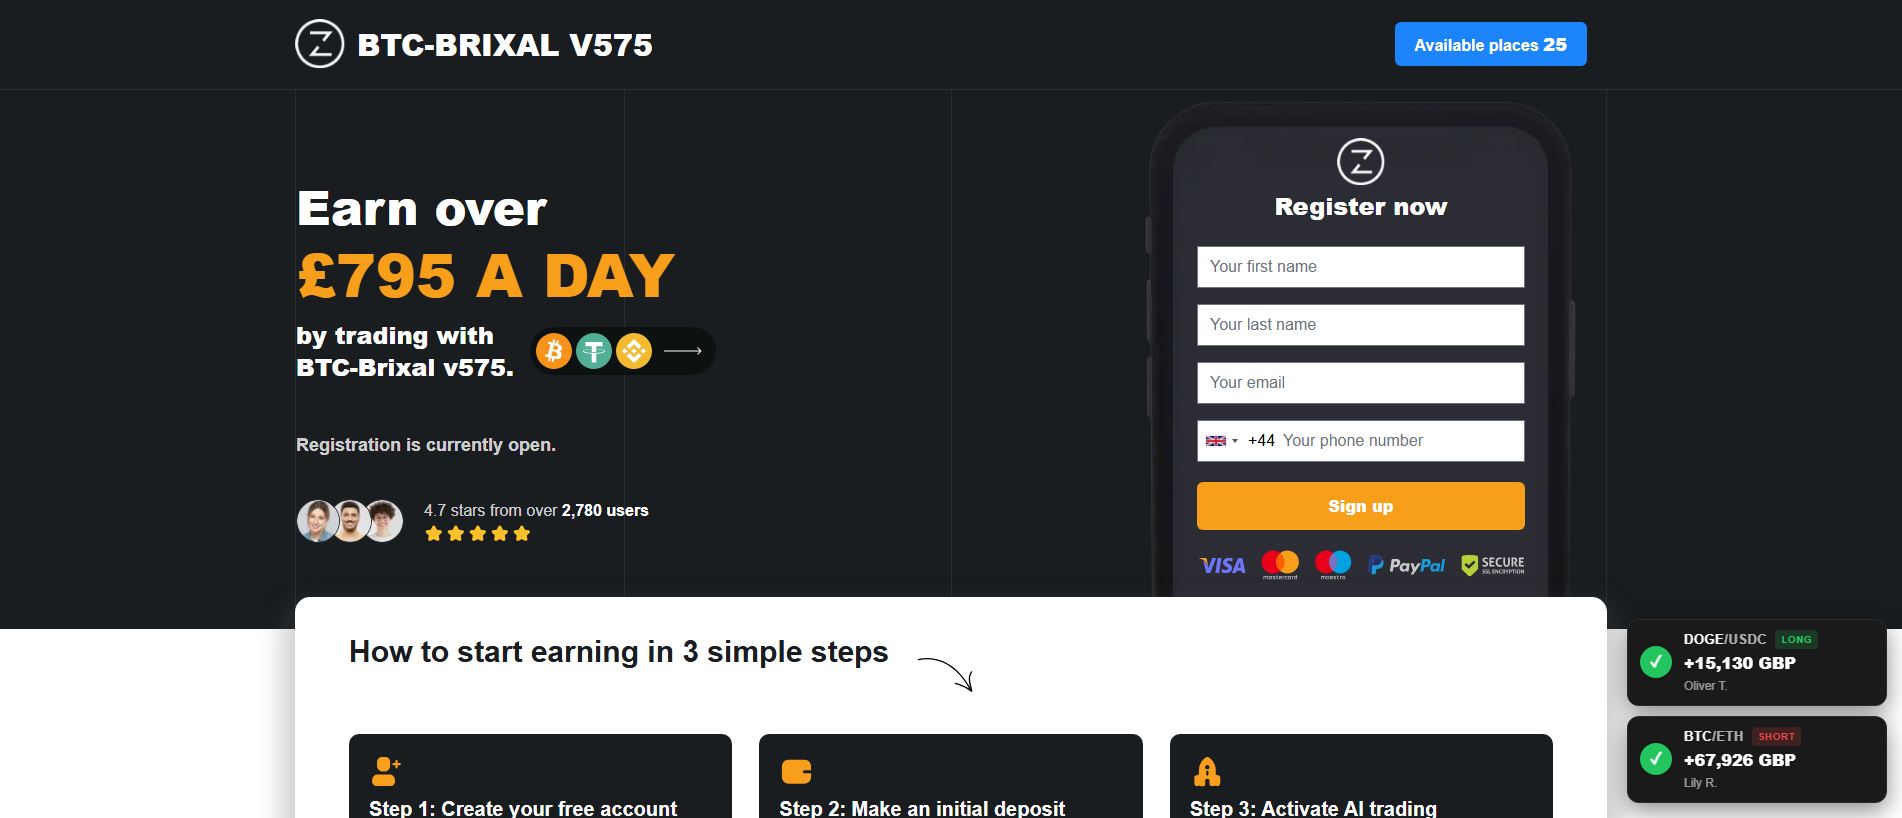
btcbrixalv575.com — Последний известный активный (HTTP 200). Олицетворение бренда: Unknown; Тип мошенничества: Impersonation. Сводка доказательств: VirusTotal 17/89 (alphaMountain.ai, Bfore.Ai PreCrime, BitDefender, CRDF, CyRadar); URLQuery 5 alerts; PhishDestroy score 100/100. Регистратор: Dynadot.
Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.
Сводка доказательств
КРИТИЧЕСКИЙ
PhishDestroy first observed btcbrixalv575.com on Sep 9, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “New Private Tab”. Stored page analysis classifies the content as impersonation. Campaign clustering links the hostname to the Unknown kit. Current evidence score: 100/100 (critical).
Positive findings are stored from 2 sources: VirusTotal and URLQuery. VirusTotal recorded 17 detections among 89 engines: alphaMountain.ai, Bfore.Ai PreCrime, BitDefender, CRDF, CyRadar, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, Lionic, Seclookup, SOCRadar, Sophos, VIPRE, Webroot on Sep 18, 2026 at 02:07 UTC. URLQuery recorded 5 threat-system alerts on Sep 9, 2026 at 19:06 UTC. Non-positive and contextual checks: AlienVault OTX listed 5 community pulse references (not vendor detections) on Sep 10, 2026 at 20:53 UTC. The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 14:20 UTC. Google Safe Browsing returned no flag on Sep 19, 2026 at 10:00 UTC. URLScan completed without a malicious verdict (score 0) on Sep 9, 2026 at 23:08 UTC.
HTTP 200 was recorded on Sep 20, 2026 at 10:10 UTC. Registration records for the domain list Dynadot Inc as the registrar and Jun 19, 2026 as the creation date. At collection time, the hostname resolved to 158.94.210.119 on AS202412 (Omegatech LTD). The recorded endpoint location is Amsterdam, NL. DOM analysis on Sep 9, 2026 at 22:22 UTC returned 98/100. The evidence archive retains 3 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YE1 as the certificate issuer with validity through Nov 26, 2026; checked Sep 9, 2026 at 19:02 UTC.
The content indicators and 2 positive source findings support the current Unknown-themed impersonation classification.
VirusTotal
17 det.
URLQuery
5 threat alerts
OTX references
URLScan
Сертификат TLS
Let's Encrypt / YE1
Возраст
3 mo
Зафиксированный статус
Последний известный активный 200

DestroyList
В списке
Reports Sent
1
Охват данных
VirusTotal
17 / 89
URLQuery
5 threat-system alerts
OTX
5 community references
CF Radar
scan completed
URLScan capture
сохраненный отчет
URLScan verdict
Анализ завершён
TLS
valid certificate, 66d
WHOIS
3 mo old
Снимок экрана
3 captures · 3 sources
Данные сетевой безопасности
Threat Detection Systems
5 alerts
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Cloudflare DNS | btcbrixalv575.com |
malicious | Sinkholed |
| OpenDNS | btcbrixalv575.com |
phishing | Phishing Block |
| DigiCert UltraDNS | btcbrixalv575.com |
malicious | Sinkholed |
| DNS4EU | btcbrixalv575.com |
malicious | Sinkholed |
| Quad9 DNS | btcbrixalv575.com |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Sep 9, 2026 · 20:55 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
158.94.210.119.
Процесс реагирования на угрозы
Открытие
Checks
Reports
Доступность
12/13
Sent Report Recorded
Stored sent-report record for registrar Dynadot Inc, hosting provider, 2 abuse contacts
abuse@omegatech.scabuse@dynadot.com
Статус в публичных блок-листах
Evasion analysis
Cloaking suspected: scanner and victim titles differ
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
Scanner note: alive_content: raw=ok; http=200; via=https_proxy
Title shown to the security scannerBTC-Brixal v575
Title shown to a browser visitorNew Private Tab
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Сохранённый снимок · 3 sources
Аналитика доменов
Домен
URLScan Verdict
Анализ завершён
score 0 report ↗
Сервер / ASN
AS202412 Omegatech LTD
Репутация IP
abuse score 0/100 0 reports checked 09.09.2026
OTX Tags
2026-09activeall-domainsblocklistcontentcryptoдоменовdrainerfraudlivemonthlyphishdestroyphishingscam
Регистратор
Dynadot
 (US)
(US)
IP-адрес
158.94.210.119

РегистрацияСоздано 19.06.2026 (93d) — Expires 19.06.2027
Статус HTTP200
Технические деталиDNS, SAN в протоколе SSL, временные метки
Впервые обнаружено09.09.2026
DOM Analysis
IoC Extraction
Submitted URLhttp://btcbrixalv575.com/
Серверы имёнns1.dyna-ns.netns2.dyna-ns.net
TLS Fingerprint
TLS Observation
Favicon Hash
ID дела
Технологии · 5 identified
jsDelivr
CDN
jQuery
JavaScript libraries
cdnjs
CDN
Cloudflare
CDN
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Пожаловаться на этот домен
Предоставьте доказательства и помогите защитить других
Анализ VirusTotal
17 / Поставщики средств безопасности 89 отметили этот домен
View on VT
Last analyzed First positive detection Previous stored snapshot: 16 detections
alphaMountain.ai
Bfore.Ai PreCrime
BitDefender
CRDF
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
«Касперский»
Lionic
Seclookup
SOCRadar
Sophos
VIPRE
Webroot
Анализ производительности сайта
Google PageSpeed Insights — mobile performance audit of btcbrixalv575.com · checked Sep 9, 2026
94
Good
Performance
FCP
0.76s
First Contentful Paint
LCP
0.76s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
6.76s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Доказательства и внешние отчеты
Анализ безопасности
Снимок отправленных доказательств
Sent: Ledger records: 1
Case ID:
PD-20260909-8C90B2 Recipient: abuse@omegatech.sc Page title stored with report: New Private Tab
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
OSINT и разведка
DNS и сеть
SEO и домены
Повлиял ли на вас этот сайт?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.


«Action Fraud»
Сообщайте о мошенничестве и киберпреступлениях в Англии, Уэльсе и Северной Ирландии
Contact centre0300 123 2040
PhishDestroy listing review Не отчет правоохранительных органов
Обжалование решения по домену
Запросите проверку, если вы являетесь владельцем этого домена и считаете, что его данные неверны.
Остерегайтесь мошенников, предлагающих услуги по восстановлению данных! Преступники могут снова связаться с жертвами, притворяясь следователями, адвокатами или агентами по восстановлению. Не платите авансовые платежи и не делитесь учетными данными. Узнайте больше о мошенничестве при получении компенсаций →
Сообщите об этом в местные органы власти
Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.
Каталог 97 стран
Черновик по шаблону • помощь AI с формулировками включается только с отдельного согласия.
Просмотрите и отправьте его самостоятельно
Связанная инфраструктура и отчёты
Infrastructure map · btcbrixalv575.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 8


Shared IP 158.94.210.119 6
На этом исходном IP-адресе размещено несколько фишинговых доменов — инфраструктура может использоваться в разных кампаниях.
 gbrawn.net
 altivexneural80.net
Тот же регистратор: Dynadot 6
 bitex-financial.cc
 alphatradexpro.net
 afiliatemktplc.live
Unknown impersonation 8
These domains also target Неизвестно users. View all Unknown threats →
Unknown kit 8
Part of the Неизвестно phishing campaign. View all campaign domains →
Проверить любой домен
Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.
Сканировать сейчасСообщить о фишинге
Добавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество
СообщитьПоток оперативных данных об угрозах
Недавние сообщения о фишинге и наблюдаемые изменения доступности
ОтслеживатьБудьте в курсе событий, берегите себя
Отслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание