Перейти к отчёту о безопасности

bhd8fa6-4acb-be64-76e26a.xo.je

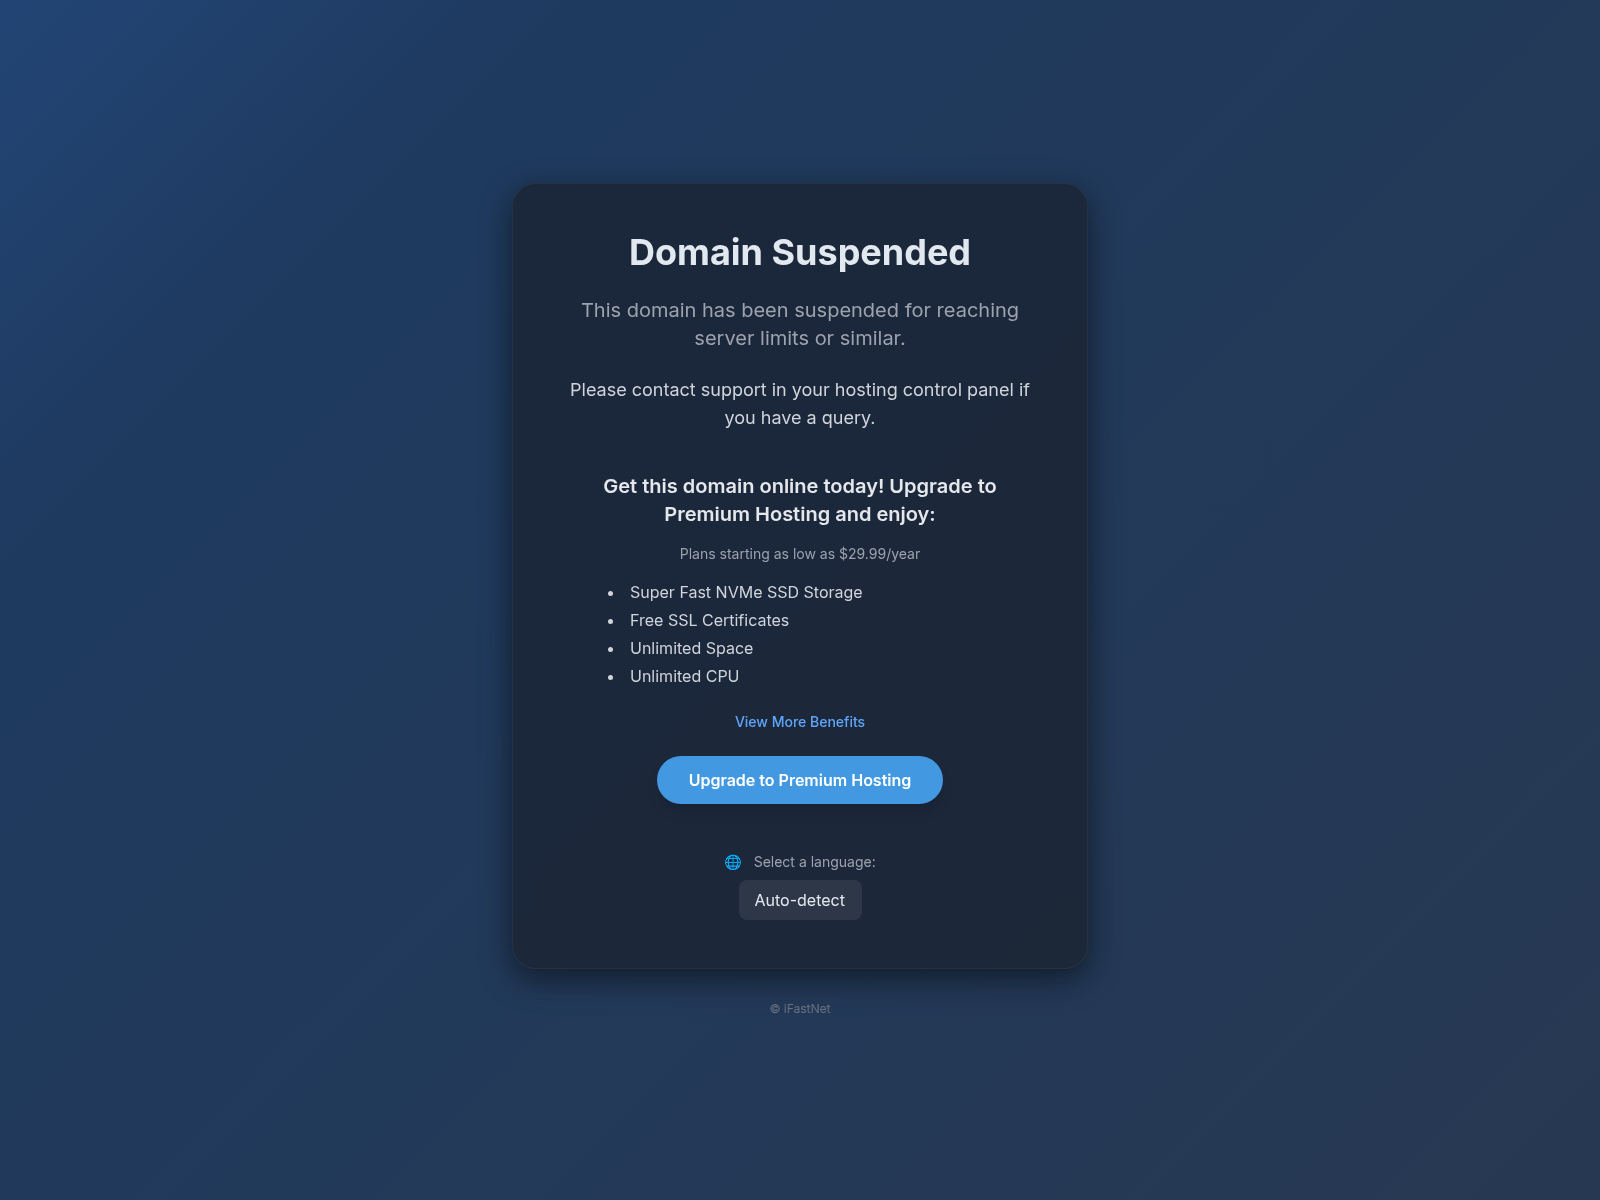
Тип мошенничества: Account Takeover Page title: “Domain Suspended”

Availability last checked First listed 06.12.2025 VirusTotal analysed Sep 19, 2026 UTC

PhishDestroy verdict Критический 91/100 evidence score

Based on 3 recorded source signals. The score is a heuristic over stored detections, not a probability or confidence level.

View evidence
Availability · last observation Непроверенный

Текущая доступность не проверена

· Source: HTTP probe

Reachability is not a safety rating.

Key evidence

  • Всего обнаружений вирусов: 12/89
  • Spamhaus DBL: DBL_PHISH
  • Тип мошенничества: Account Takeover
IP
77.72.1.44
Stored capture 1 of 2 · Feb 27, 2026 UTC · Primary capture OpenAll capturesWayback
View evidence I was affected Export & tools

Evidence

Source checks and detection results recorded for this domain, with the time each was observed.

Краткий обзор отчёта

bhd8fa6-4acb-be64-76e26a.xo.je — Непроверенный. Тип мошенничества: Account Takeover. Сводка доказательств: VirusTotal 12/89 (BitDefender, Chong Lua Dao, CyRadar, ESET, Forcepoint ThreatSeeker); Spamhaus DBL_PHISH; CF Radar malicious; PhishDestroy score 91/100.

Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.

Source evidence

8 sources

Spamhaus DBL

DBL_PHISH

PhishStats

checked — no match recorded

URLScan capture

сохраненный отчет

Stored URLScan capture preview
Сообщить

Google Safe Browsing

Checked; no threat flag recorded

Сообщить
Detailed resultsVirusTotal vendor list · written summary · threat-intel cross-reference · cloaking analysis
Сигналы безопасности
SA Scamadviser Warnings 1/100
The Tranco rank (how much traffic) is rather low An iframe has been detected within the website The server of the site has several low reviewed other websites This website seems for sale at this time (how to get your money back) The website was reported in the last 30 days as threat by DNSFilter This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
We found a valid SSL certificate
Данные сетевой безопасности
CF Cloudflare Radar Verdict Вредоносный
Phishing Security threats Phishing

Evidence summary

Stored written summary, generated Jul 23, 2026. It is not updated when source results change.

This summary quotes VirusTotal 20/95. The current stored result is 12/89 (analysed Sep 19, 2026).

The domain bhd8fa6-4acb-be64-76e26a.xo.je was observed returning the page title "Domain Suspended" and is currently taken offline. DNS resolution points to the IPv4 address 77.72.1.44, which is announced by AS12488 (Krystal Hosting Ltd) located in Great Britain. The domain lacks publicly resolvable nameservers, and no TLS certificate was presented when the host was queried, indicating an absence of encrypted traffic. Reputation services record a Scamadviser trust score of 1 out of 100, reflecting extreme suspicion.

Read full summary

The domain appears on a single security blocklist and has been explicitly flagged by the PhishDestroy feed. VirusTotal analysis shows that 20 out of 95 scanned security vendors flagged the domain as malicious, reinforcing the notion of malicious intent despite the offline state. The intelligence categorizes the activity as an "Account Takeover" scam, though the targeted brand or service is not disclosed in the available data.

The combination of a low trust score, lack of SSL, presence on a blocklist, and multiple vendor detections suggests the domain was deployed to harvest credentials or session tokens before being shut down.

Uncertainty remains regarding the exact victim profile and the infrastructure used to deliver the malicious payload, as the site content was not captured before suspension. Defenders should continue to deny any outbound connections to 77.72.1.44, add the domain to perimeter deny lists, and monitor DNS logs for any resurgence of the hostname or related sub‑domains. Additional investigation of Krystal Hosting Ltd’s IP range may reveal other malicious actors sharing the same hosting environment.

Анализ VirusTotal

12 / Поставщики средств безопасности 89 отметили этот домен
View on VT
Last analyzed Previous stored snapshot: 14 detections
BitDefender
Chong Lua Dao
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SOCRadar
Sophos
VIPRE
Анализ методов обнаружения и уклонения

Проверка маскировки и распределения трафика

Еще не отсканировано Пока не было зафиксировано никаких различий между роботом-пауком и браузером

Сохраненные данные сравнения данных сканера и браузера для данного хоста, а также проверка отпечатков в режиме реального времени для систем распределения трафика типа «Кейтаро».

Сохраненный флаг маскировки
Еще не отсканировано
Последнее сканирование на наличие маскировки

Примечание к сканированию: timeout: raw=timeout; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='bhd8fa6-4acb-be64-76e26a.xo.je', port=80): Max retries exceeded with url: / (Caused by Con

Проверка отпечатков пальцев в режиме реального времени с помощью «TDS»
Семь отпечатков Keitaro, а также сравнение кроулера и браузера — запускаются со сканера PhishDestroy при открытии этой панели.
Ожидание

Domain & infrastructure

IP 77.72.1.44

Domain details

Домен
Репутация IP abuse score 0/100 0 reports checked 25.09.2026
Registrar (base domain) Неизвестно
Контакт для жалобabuse@ifastnet.com
Технические деталиProvenance & timestamps
Впервые обнаружено06.12.2025
DOM Analysisanalyzed 27.07.2026score 88/100
Submitted URLhttp://bhd8fa6-4acb-be64-76e26a.xo.je/

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
77.72.1.44
Network ASN
AS12488
Organization
Krystal Hosting Ltd
Observed location
London, GB
Server header
openresty

Location describes the IP network.

Снимки

2 stored captures · Wayback archive

Сохранённый снимок · 2 captures

Заголовок страницы
Domain Suspended

Архивные доказательства

Wayback Machine Snapshot
Исторический снимок доступен для проверки доказательств.
View Archive

Reports & history

No abuse reports recorded · first listed 06.12.2025 · detection timeline

Latest Classified Outcome 2026-10-14 10:41:21 UTC

Primary outcome Неизвестно reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Неизвестно Probe Inconclusive 20% 2026-10-14 10:41:21 UTC
RDAP registration Неизвестно
Observed timeline last reachable: 2026-09-15 22:17:50 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-07-26 22:23:32 UTC
    Domain state transitioned from dead to alive.
  2. Cloudflare Radar Scan 2026-03-07 11:44:23 UTC
    Cloudflare Radar scan registered: View Radar report.
  3. Domain Status Transition 2026-03-01 04:45:09 UTC
    Domain state transitioned from alive to dead.

Процесс реагирования на угрозы

Открытие
Analysis
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Сообщения сообщества

Сообщил 1 участник сообщества; впервые замечено 06.12.2025

Сохранённые сообщения
1
Уникальные URL
1
Принято1

Get help

Official reporting channels, a complaint draft, and listing review

Повлиял ли на вас этот сайт?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.

Европол
Найдите официальный канал отчетности для вашей страны ЕС
National police directory
Остерегайтесь мошенников, предлагающих услуги по восстановлению данных! Преступники могут снова связаться с жертвами, притворяясь следователями, адвокатами или агентами по восстановлению. Не платите авансовые платежи и не делитесь учетными данными. Узнайте больше о мошенничестве при получении компенсаций →

Сообщите об этом в местные органы власти

Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.

Каталог 97 стран
Черновик по шаблону • помощь AI с формулировками включается только с отдельного согласия. · Просмотрите и отправьте его самостоятельно

Tools & export

External lookups, JSON / PDF export, API and embed code
Analyze on destroy.tools Run a fresh external analysis of bhd8fa6-4acb-be64-76e26a.xo.je (opens in a new tab)

Доказательства и внешние отчеты

Глубокий анализ
HTML · IFRAME

Вставить этот отчет

Разместите эту информацию об угрозах на своём сайте или в блоге

embed.html
<iframe
  src="https://phishdestroy.io/ru/embed/domain/bhd8fa6-4acb-be64-76e26a.xo.je"
  title="PhishDestroy threat report for bhd8fa6-4acb-be64-76e26a.xo.je"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

Проверить любой домен

Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.

Сканировать сейчас

Сообщить о фишинге

Добавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество

Сообщить

Поток оперативных данных об угрозах

Недавние сообщения о фишинге и наблюдаемые изменения доступности

Отслеживать

Будьте в курсе событий, берегите себя

Отслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание

Поток оперативных данных об угрозах Подать жалобу на это объявление