Выполняйте поиск по отслеживаемым доменам и просматривайте сохраненные доказательства, данные об обнаружениях и последние данные о доступности.
209,576
Всего отслеженных
204,200
Обнаружено VT
74,302
Последнее появление: активен
135,274
По последним данным — недоступно
1
VT — в процессе рассмотрения
How This Attack Works
Fake Token Presale scams trick victims into believing they are investing in legitimate cryptocurrency projects. Here's how the scam typically unfolds:
STEP 1
Create Fake Websites
Scammers set up realistic-looking websites mimicking legitimate token presale portals.
STEP 2
Promote Presale on Social Media
Using social media and fake endorsements, scammers attract potential investors.
STEP 3
Collect Cryptocurrency
Victims are prompted to send cryptocurrency to a specified address under the guise of buying tokens.
STEP 4
Disappear with Funds
Once funds are collected, scammers shut down the site and disappear, leaving victims without recourse.
Technical Analysis
Fake Token Presale scams often leverage phishing tactics combined with cryptocurrency-specific techniques. Attackers use homograph attacks to create URLs that closely resemble legitimate sites, often registered through top registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED and PDR Ltd. d/b/a PublicDomainRegistry.com. They exploit the decentralized nature of blockchain networks, utilizing smart contracts that mimic legitimate presale contracts but are programmed to divert funds to the attacker’s wallet. The infrastructure often involves cloud-based hosting services to quickly deploy and dismantle sites, minimizing the chance of detection. HTML and JavaScript are commonly used to create dynamic, convincing interfaces that reassure potential victims of the site’s legitimacy. Additionally, attackers might deploy SEO techniques to improve the visibility of their fraudulent sites in search engine results, further increasing their reach.
Real Cases
CryptoX Presale Scam (2024)
$2 million stolen
A fake presale for a non-existent token, CryptoX, duped investors into contributing significant sums.
TokenLaunch Fraud (2023)
$1.5 million stolen
Victims were lured into a fake token launch with promises of high returns, only for the site to vanish post-collection.
QuickCoin Deception (2024)
$3 million stolen
Scammers created a sophisticated site mimicking a known exchange, leading to substantial financial losses.
How to Detect
Проверить for slight misspellings in domain names.
Look for inconsistent branding or layout compared to legitimate sites.
Be wary of unsolicited investment opportunities via social media.
Verify presale details on official project channels.
Beware of high-pressure tactics urging immediate investment.
How to Protect Yourself
1
Always verify URLs before entering personal information.
2
Use browser extensions to detect phishing attempts.
3
Consult official project websites or channels for presale information.
4
Enable two-factor authentication on cryptocurrency exchanges.
5
Отчет suspicious sites to authorities and platforms like PhishDestroy.
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 358 domains tracked for this threat type
Fake Token Presale 358 domains
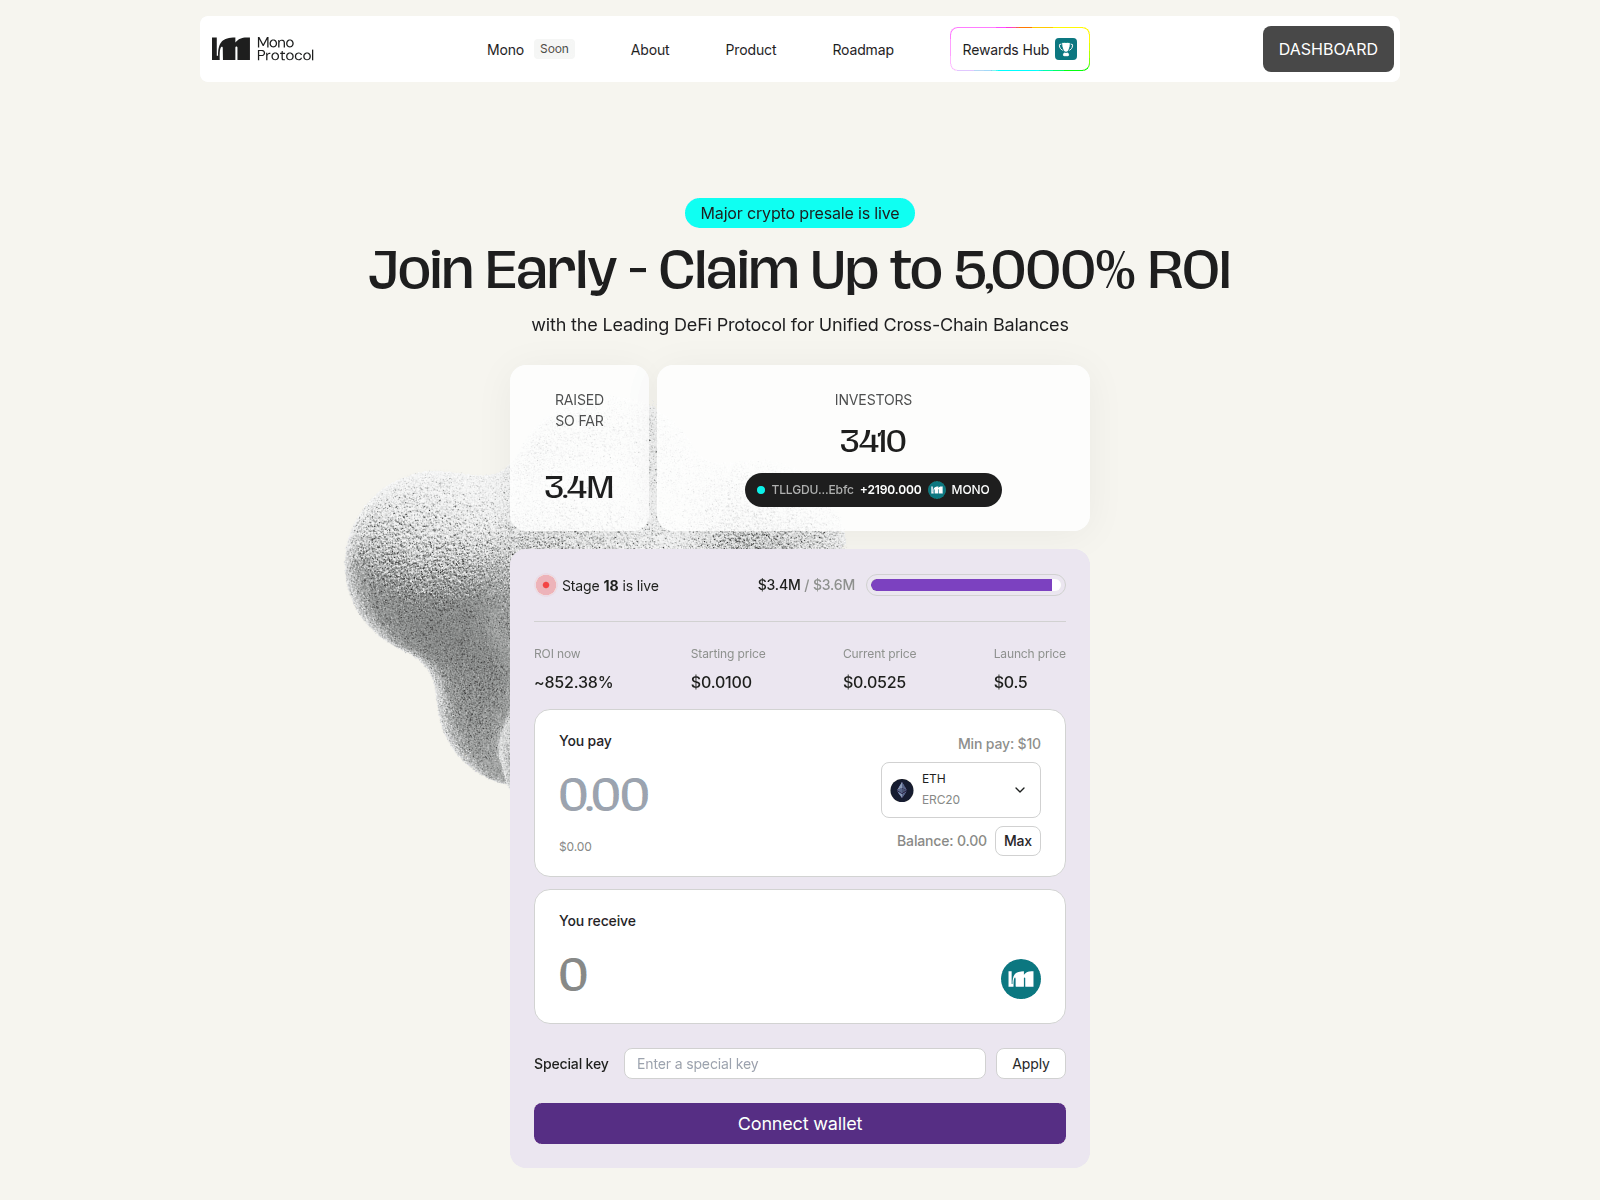
monoprotocol.live

opz-io.xyz

peperider.com

pomerdoge-ai.pages.dev

spax41k.com

spax51k.com

spx30b.com
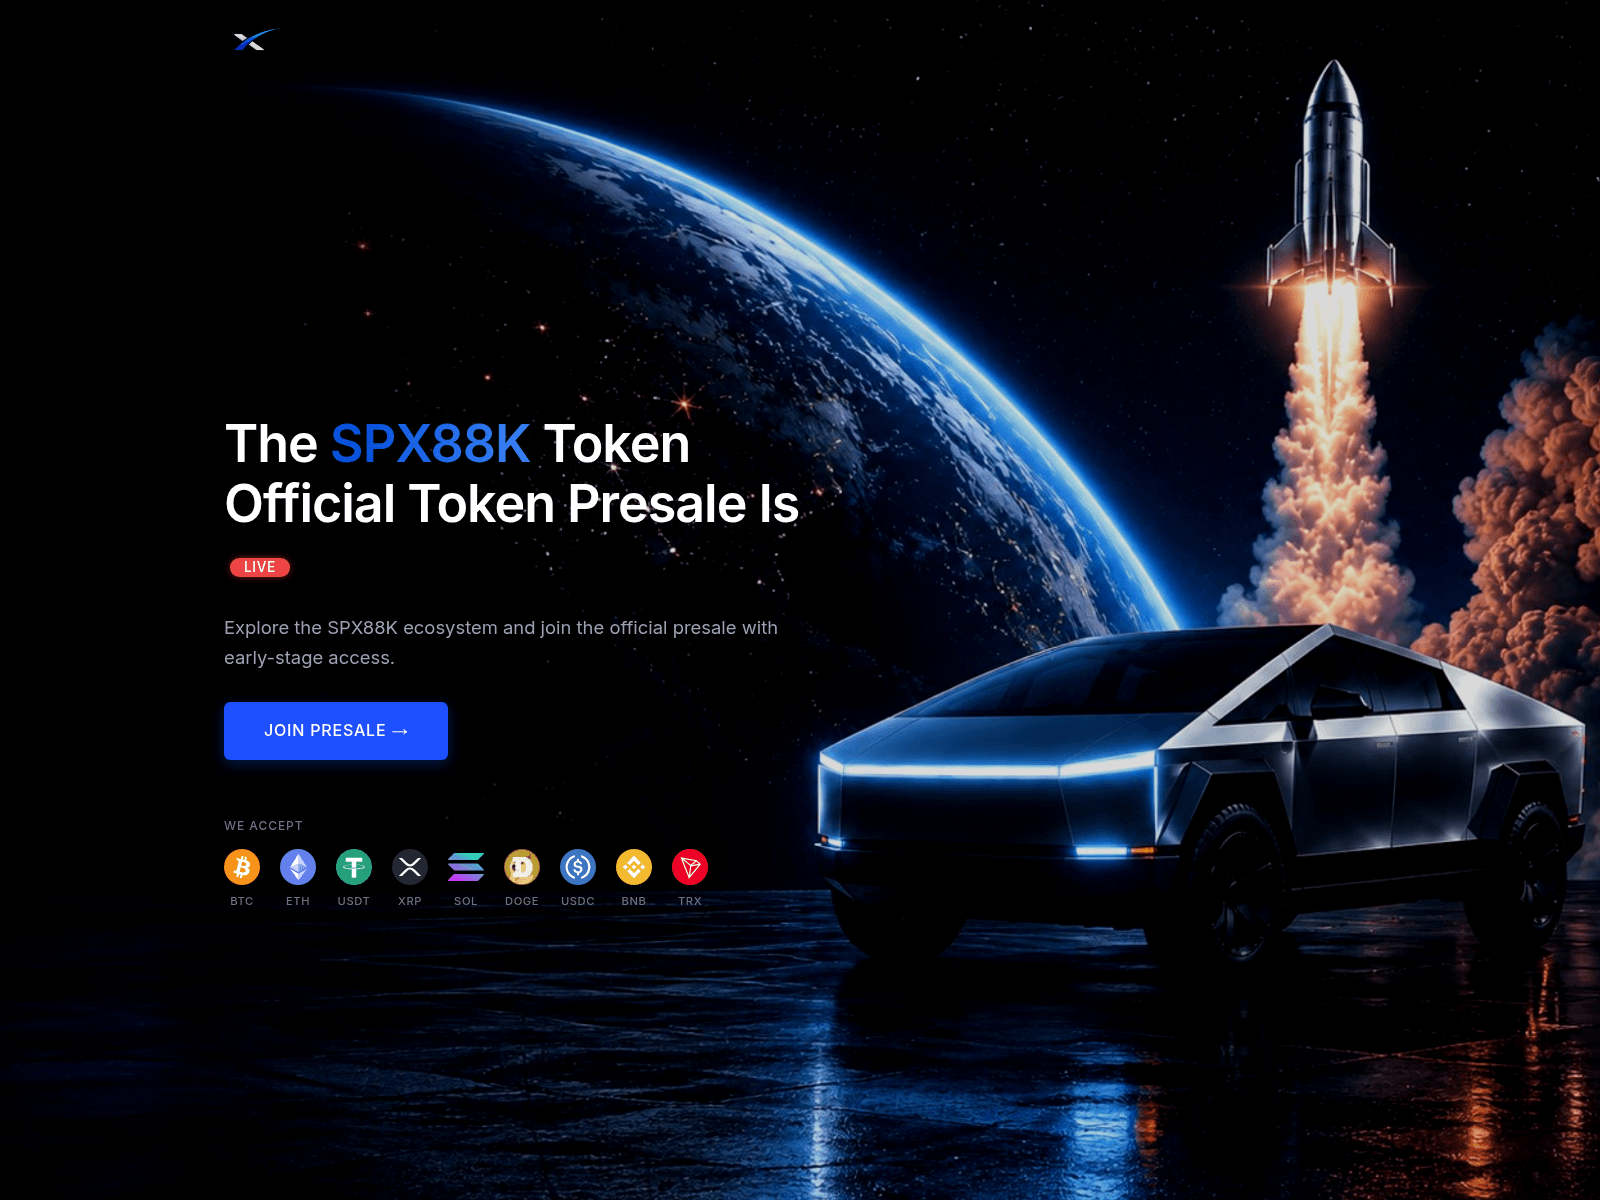
spx88k.org

spx99x.org

thetokencentral.com
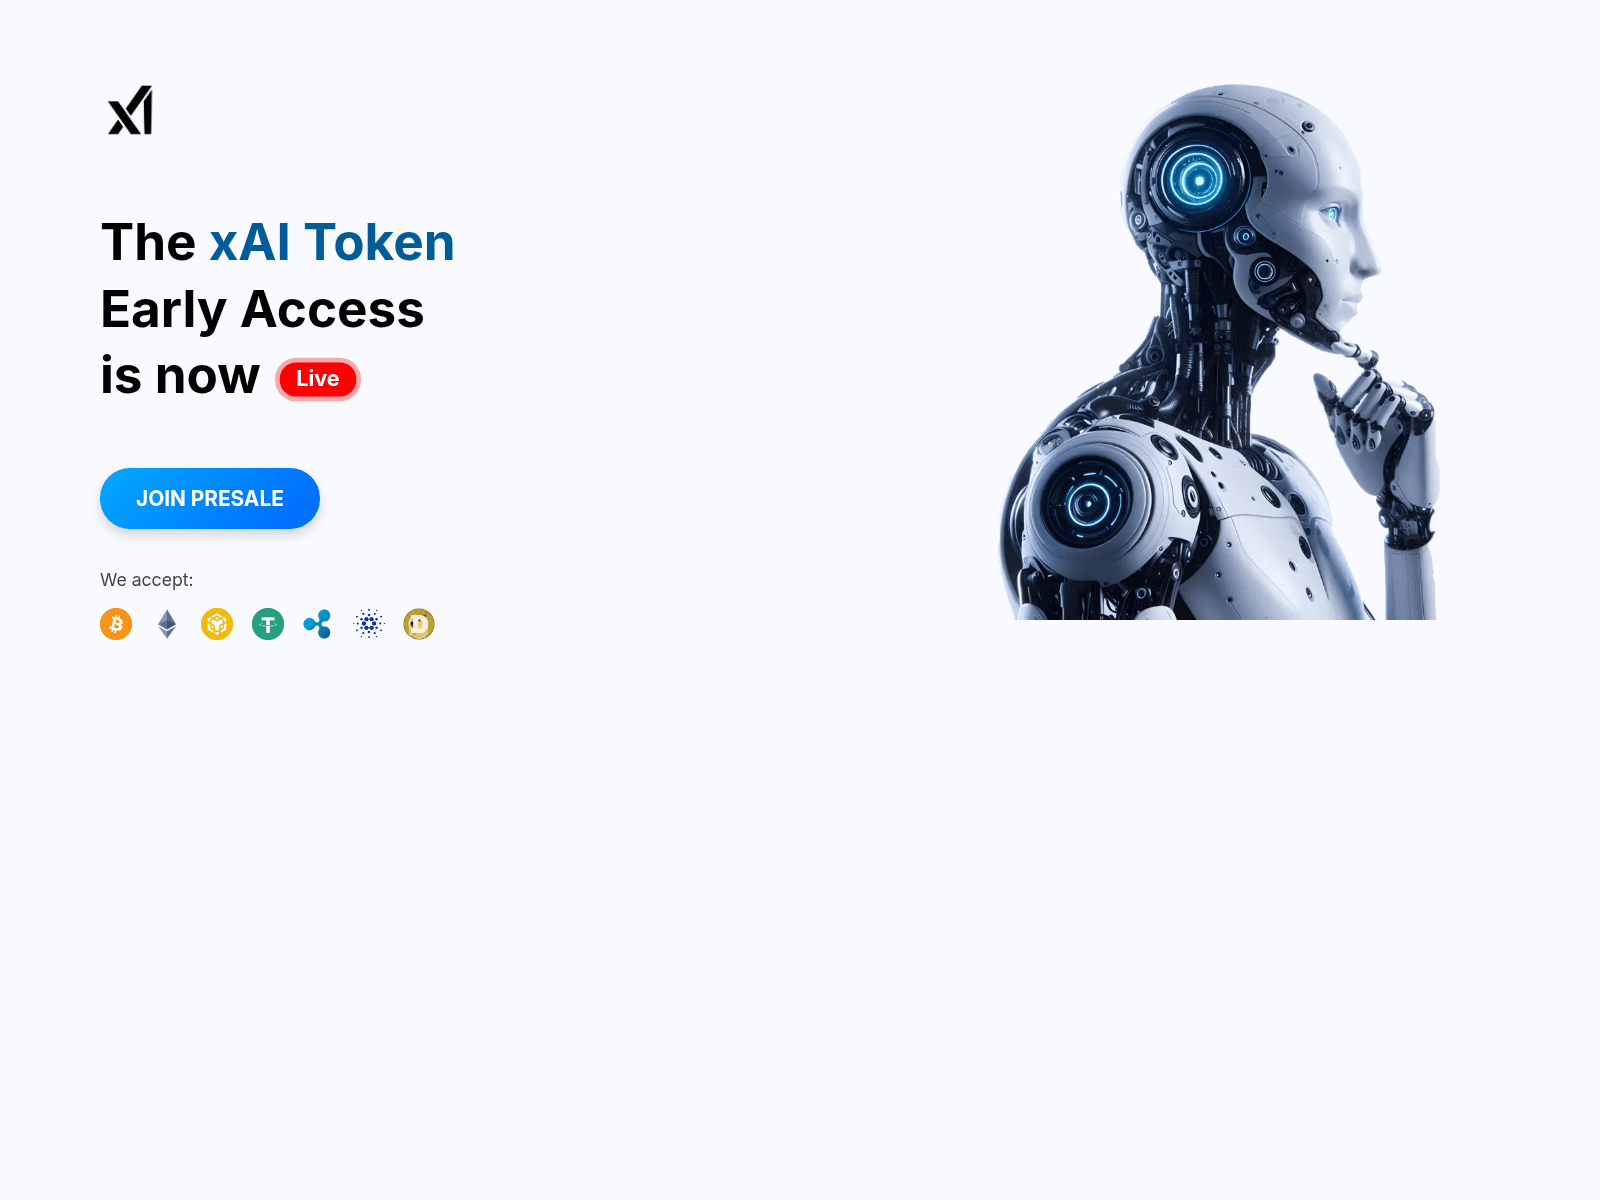
xa28r.org
xaicore.net

bestwallettoken.crescentnetworks.co.ke

bitcoins-hyper.pages.dev

bl0ckdag.network

bl0ckdaq.network

block-dagnet.live

btfd.io

buy-pepeheimer.io

cysicpresale.xyz

digitoad-dapp.pages.dev

gro25b.net

grok15ktoken.com

grok20g.net

grok25h-fxempire.com

grok35k-cointelegraph.com

grok35k.com

grok49k.net

grok87k-fxempire.com

groknetwork.net

helioschain.net

ionixchain.co

litlpeppe.com

llttlepepe.com

lttllepepe.com
ne-xchain.live

nexc-hain.live

nexchain.exchange
pepeoftherings.io

perenapresale.xyz

phoenicvesting.com

pikachusub.pages.dev

ruviai.info
solxscan.xyz

spx99x.net
xa28r.net

xa32p.net

xa40p.org
xa909k.net

xai99r.net
xai99r.org

xaidov-fxempire.com

xaifox-fxempire.com

xeronum.org

xpage-meta.com
aaasz.pages.dev

allocation.ondrix.com

ashmemecoin.com
bestwallet.top

bitcoinhyper.pages.dev

bitcoinhyperpresale.com
bitcoinpepe-live.web.app
bitcoinshyper.live

blastuptoken.github.io

claimsflockerz.pages.dev
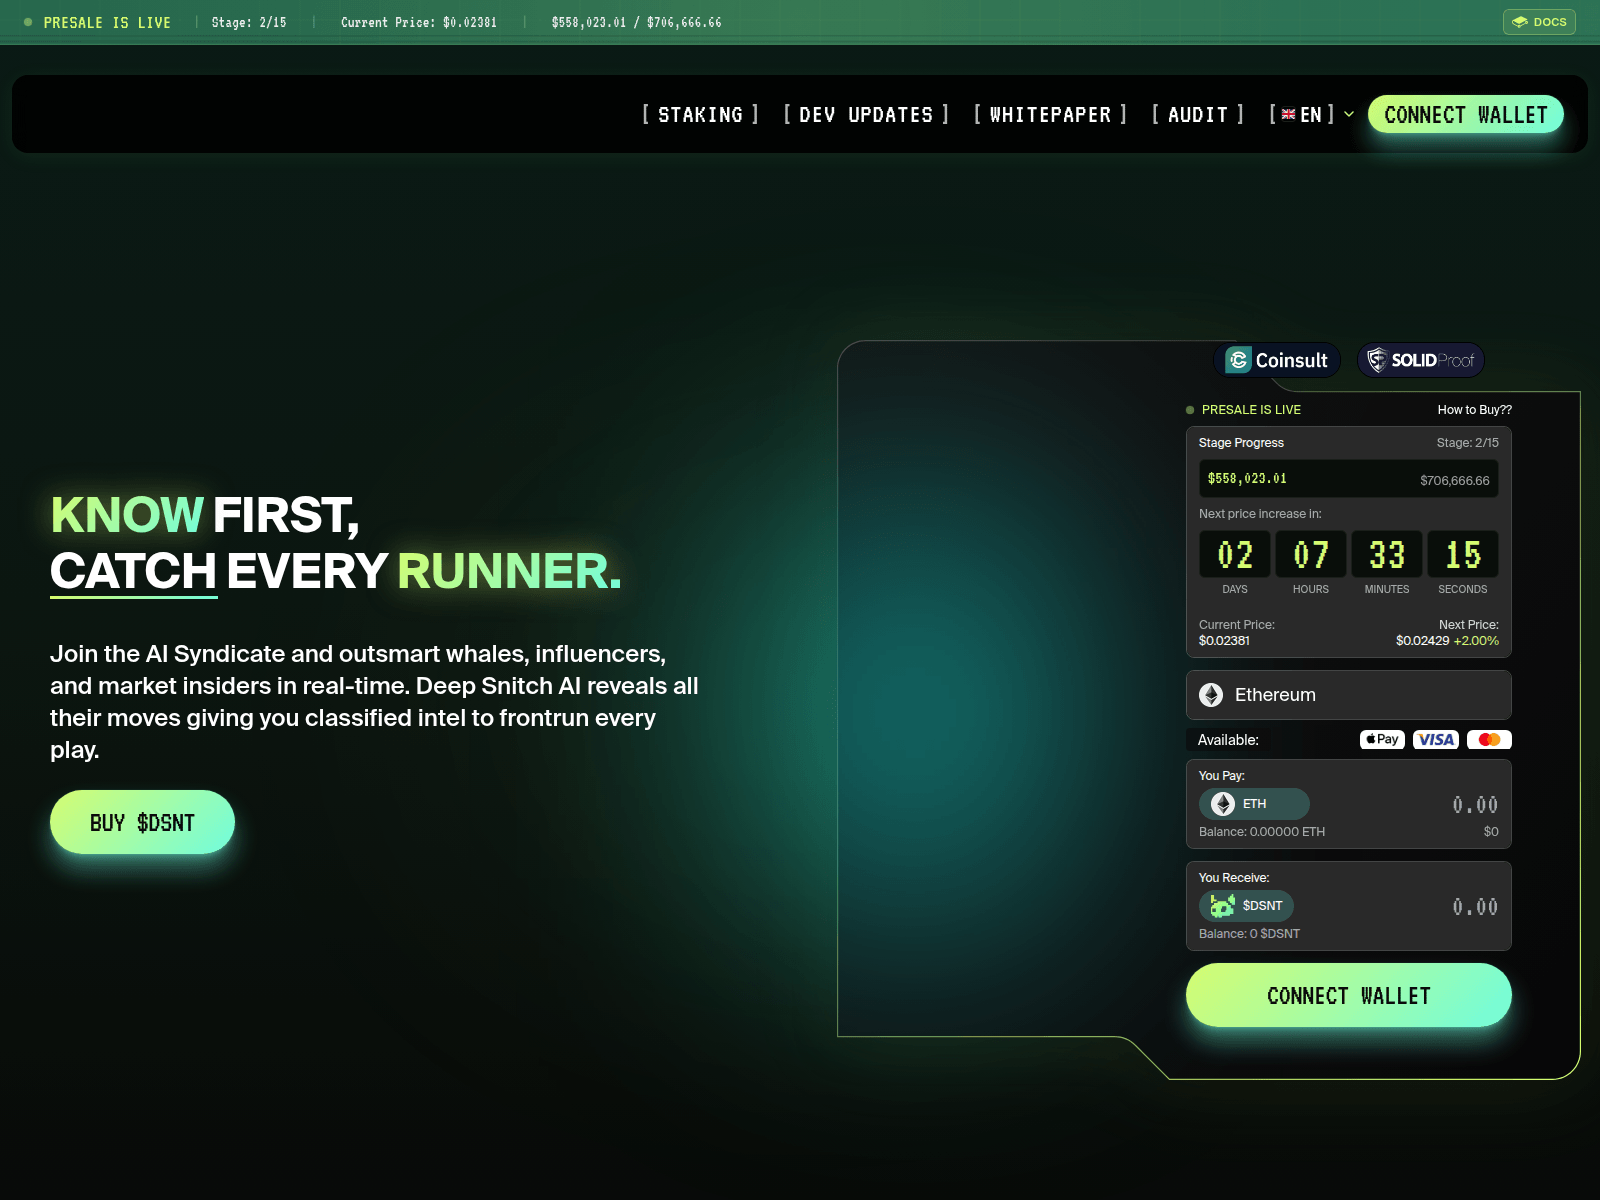
deepsnitch.io
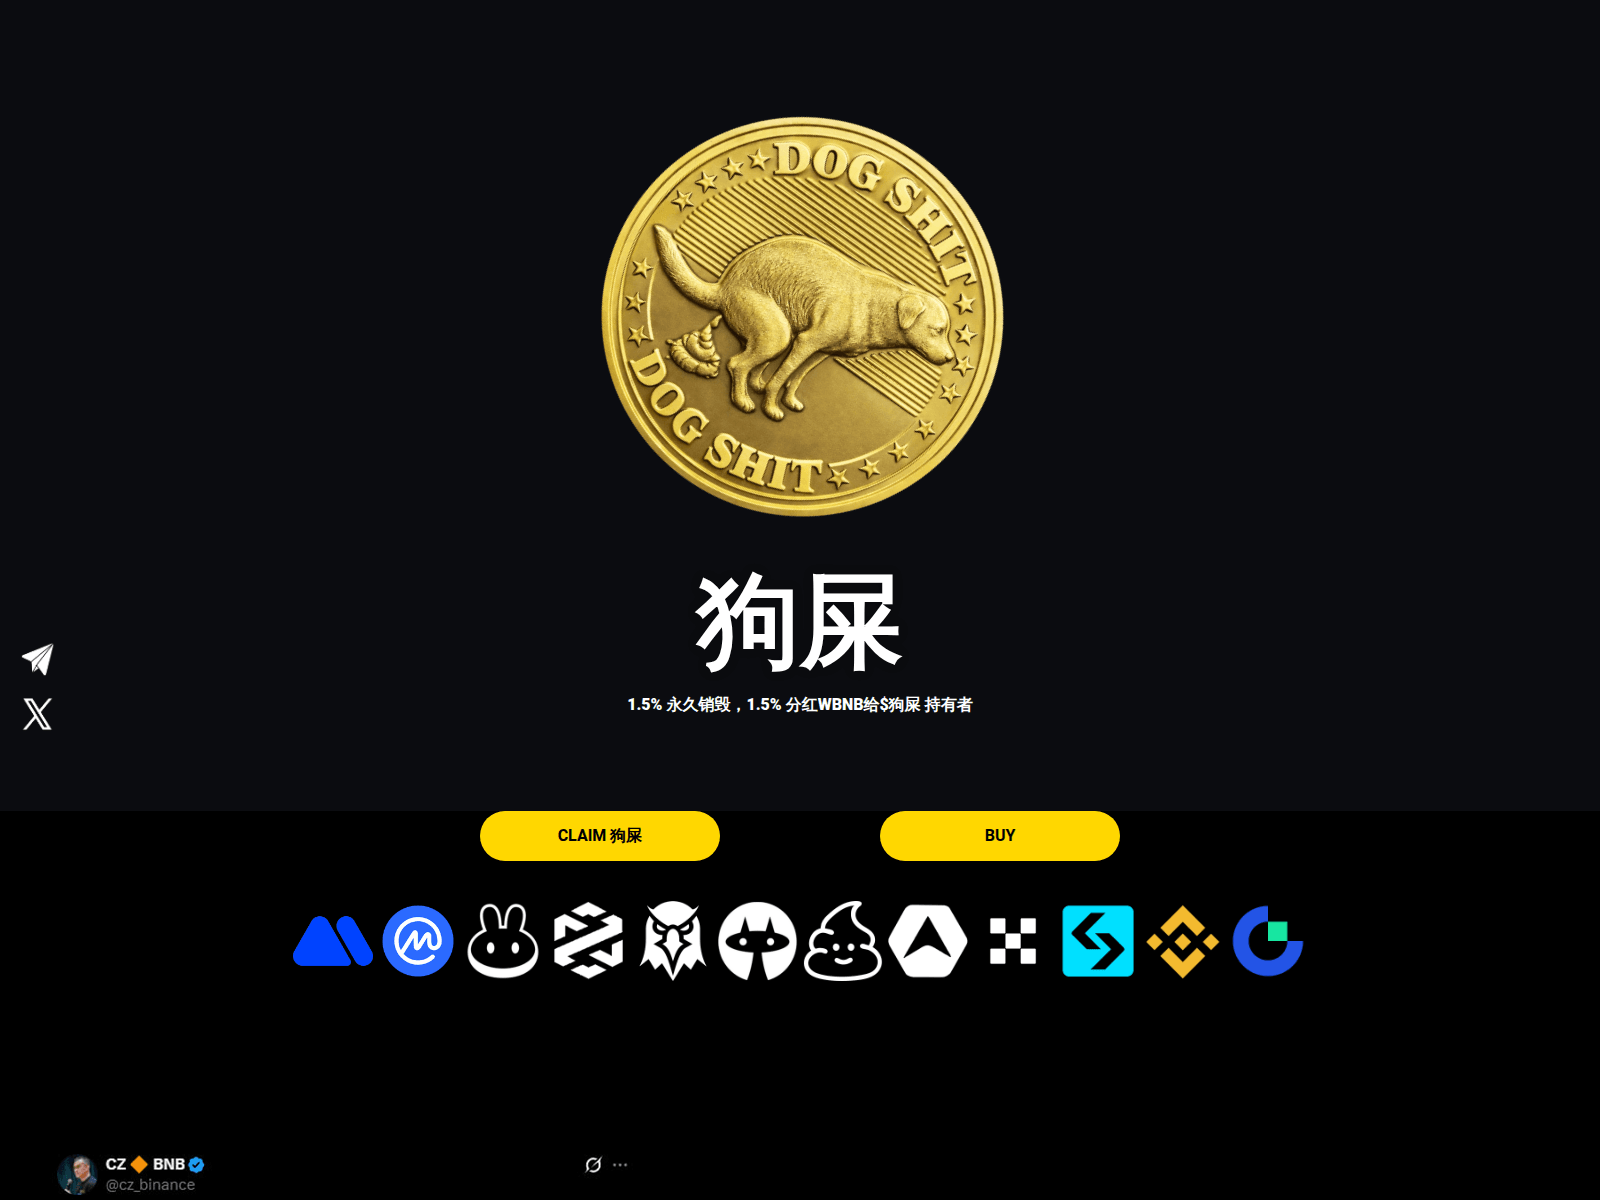
dogshltmeme.xyz

flockerz-dh1.pages.dev

grok87k.org

ionixchain.org

kadven.io

magacoinsfinance.pages.dev
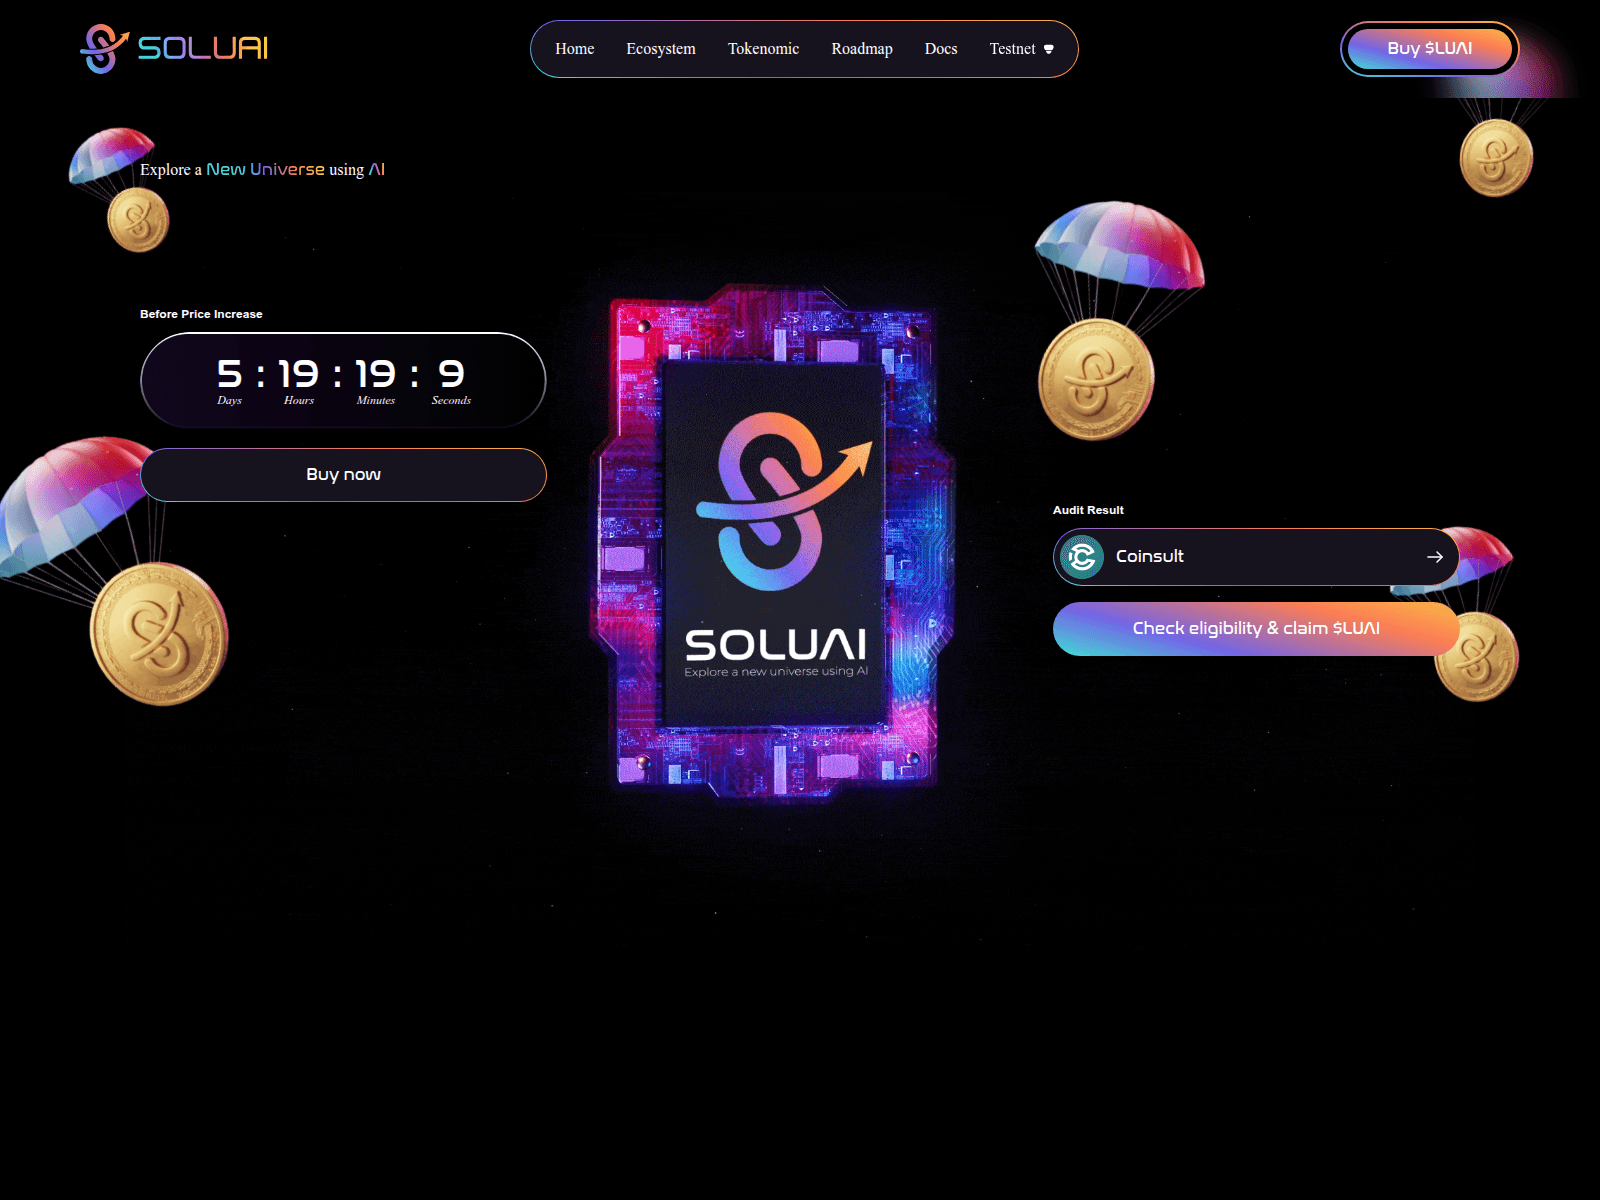
officialsoluai.live

pepeascension.com

pepeheimer-claimlive.pages.dev

pexebel.com
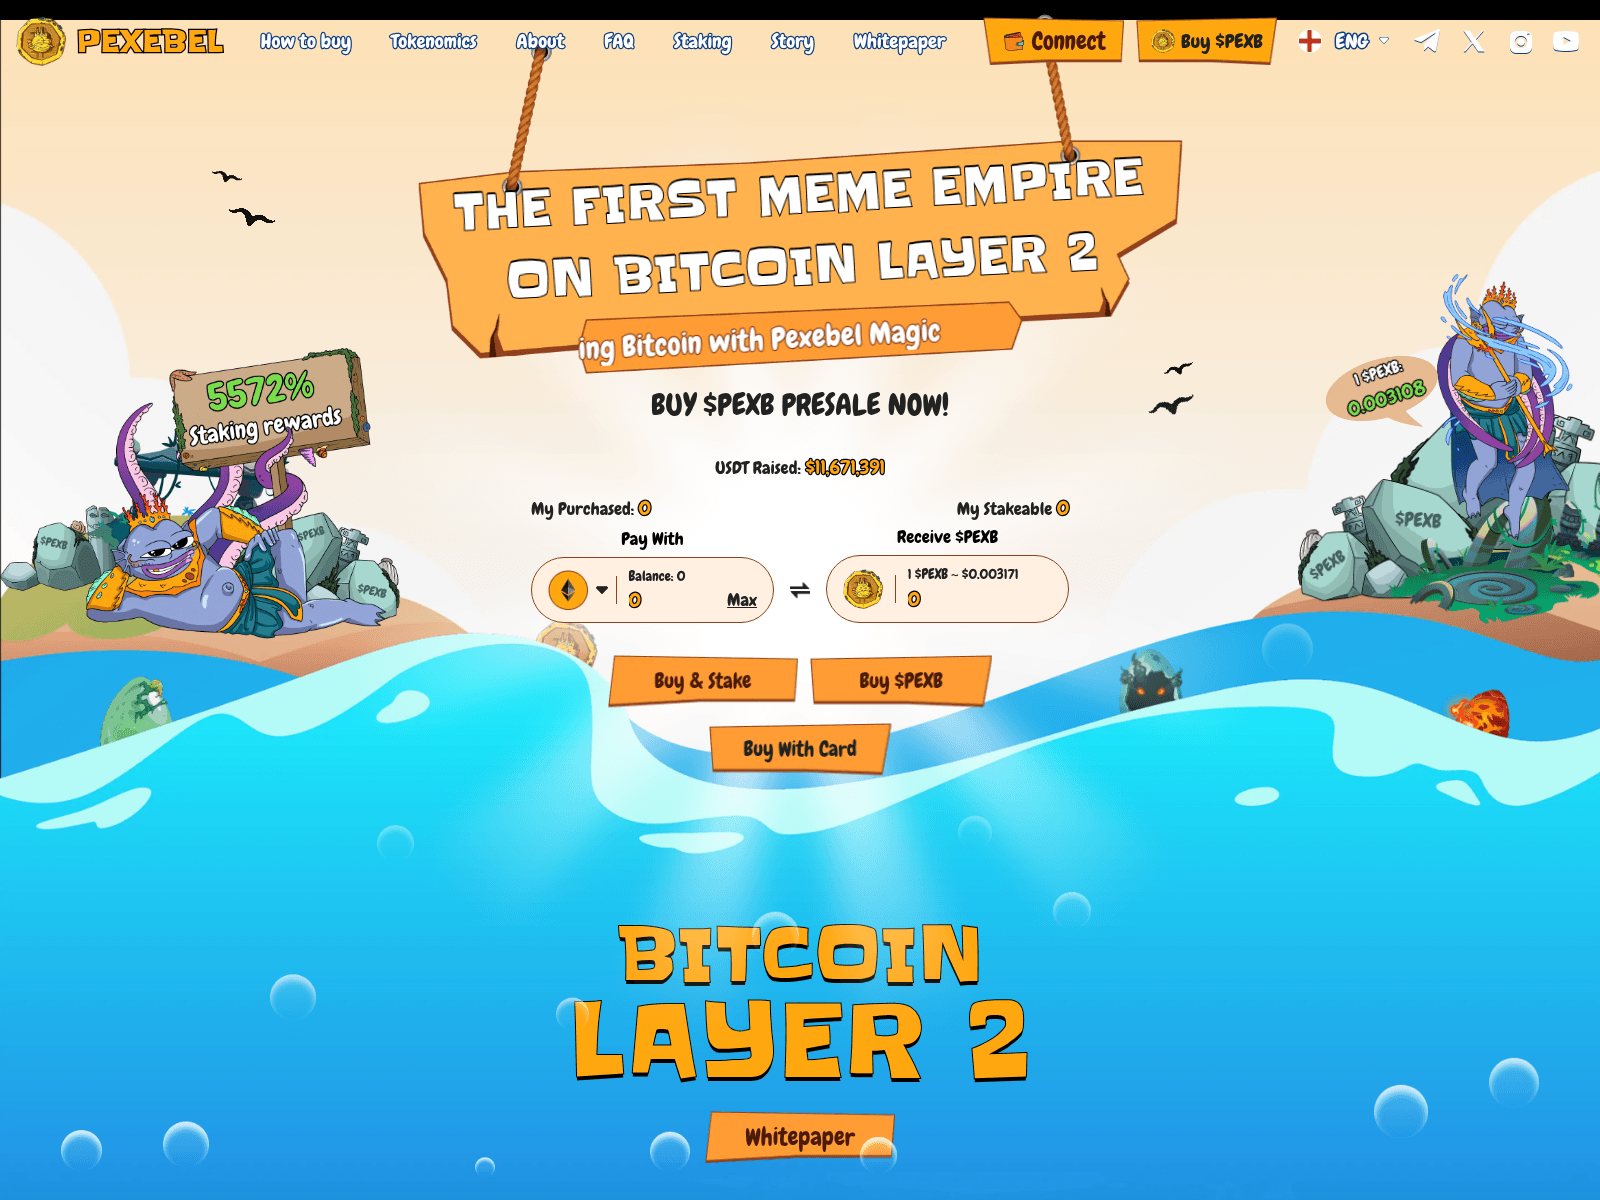
pexebel.us

qadden.com
rainbows.bet
rnbw.rainsbow.xyz

seismicpresale.xyz
snorterstoken.live

solaxy-sol.pages.dev
spx10k-cointelegraph.com
spx15k-cryptoslate.com
spx15k-fxempire.com

subbdtoken-app.pages.dev

subbdtoken.wiki

syneris.tech

www.spydoge.com
xainog-fxempire.com

xaiwalletgo.com
Процесс реагирования на угрозы
Как мы проверяем каждый домен в этом разделе и нейтрализуем подтверждённые угрозы. Полная визуализация конвейера →
Проверка по источникам данных об угрозах— каждый домен сканируется и сверяется со следующими источниками:
urlscan.ioСнимок экрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ОтчетCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безопасность FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПроверитьFull surface scan
 crt.sh
Передача данных партнёрам— подтверждённые детекты передаются 29 партнёрам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОбзор сайтаAviraCloud detectionAvast / AVGWeb Shield«Касперский»OpenTIPDr.WebOnline scannerNetcraftЛиквидация APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ОтчетHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust