VirusTotal
6 / 92
Denunciar


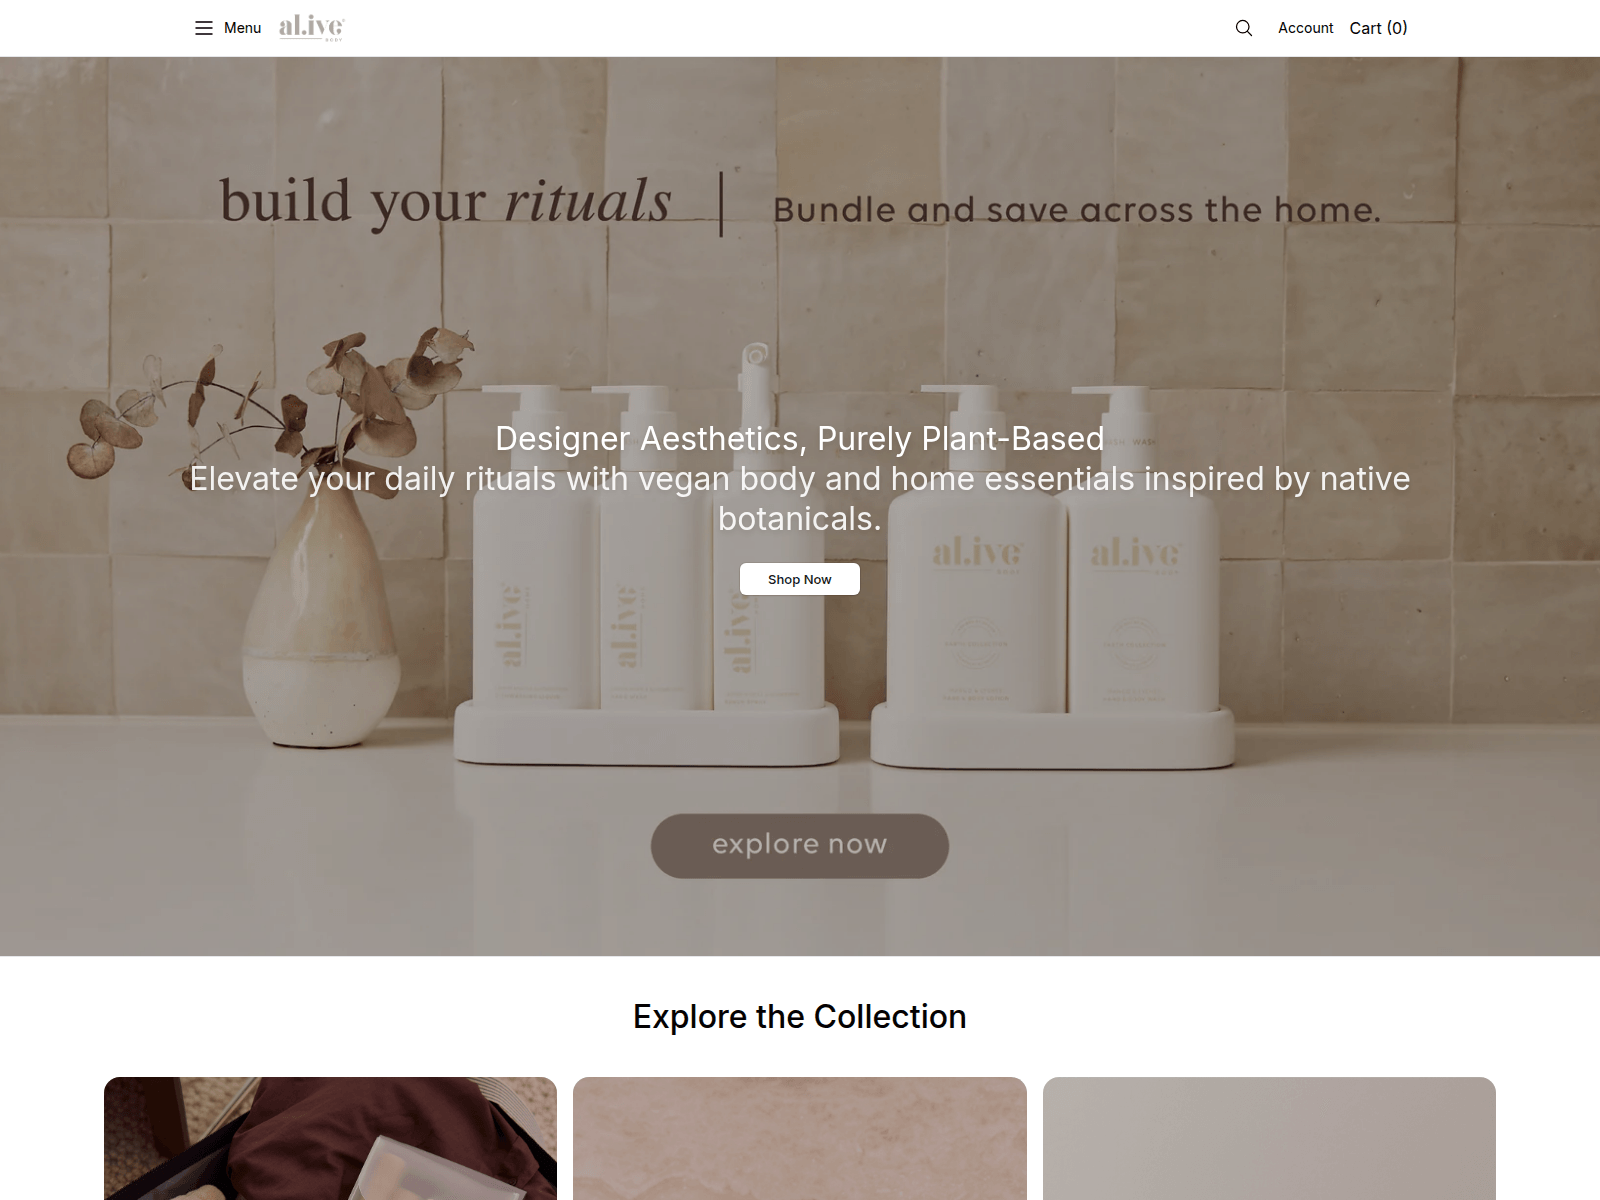
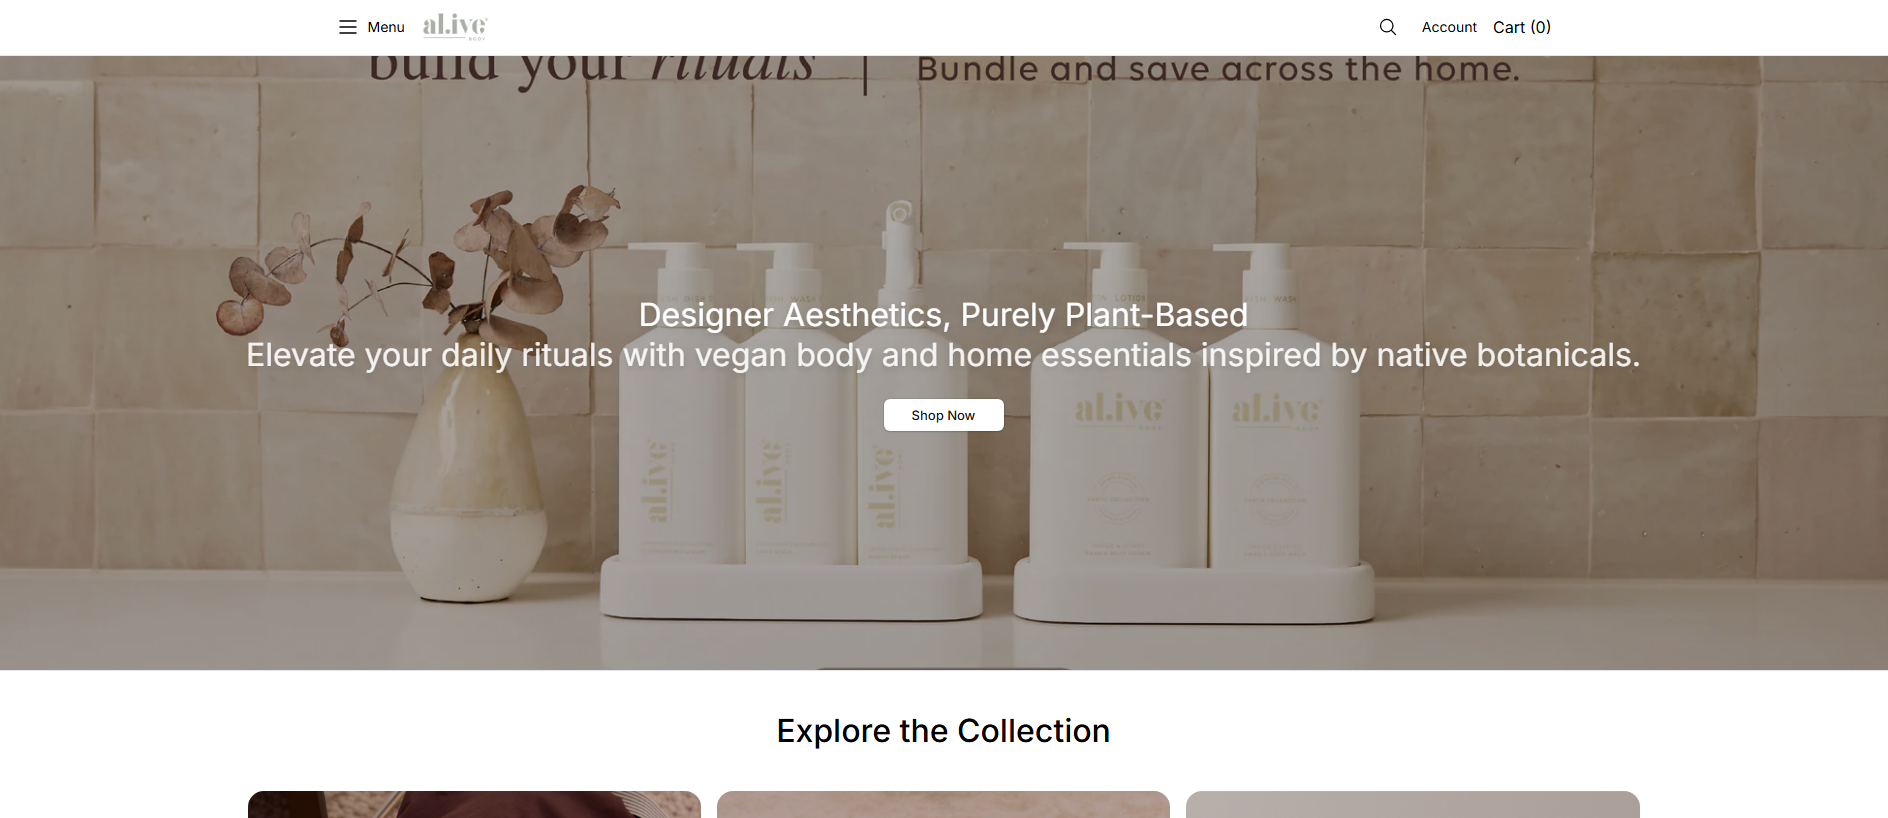
“Products for Home, Hair, Body & Skin Care | al.ive body”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 10 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
alvpure.shop — Último ativo conhecido (HTTP 200). Representação da marca: Fakeshop; Tipo de golpe: Impersonation. Resumo das evidências: VirusTotal 6/92 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar); URLQuery 2 det.; URLScan malicious verdict; PhishDestroy score 90/100.
A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.

On 2026-10-08, alvpure.shop returned an HTTP 200 status, confirming a successful server response at that date. The domain was also observed with a pagespeed performance score of 81, indicating moderate optimization as of 2026-10-01.
OTX included alvpure.shop in four pulses on 2026-10-08. VirusTotal reported 6 detections out of 92 scanners on 2026-10-07. The domain was listed in the PhishDestroy internal catalogue, and a urlscan report was available as of 2026-10-01.
These observations provide a snapshot of alvpure.shop’s web response, performance, and presence in multiple security sources. The dated records from OTX, VirusTotal, and PhishDestroy offer points of comparison without suggesting changes or trends over time.
For alvpure.shop, retain the VirusTotal, OTX, and urlscan records for ongoing reference. Use the PhishDestroy internal listing as a baseline when reviewing future evidence or evaluating the domain's status.
Observações armazenadas comparando o rastreador com o navegador para este host, além de uma verificação em tempo real da assinatura digital para sistemas de distribuição de tráfego do tipo Keitaro.
Nota do digitalizador: alive_content: raw=ok; http=200; via=https_proxy
lilith.ns.cloudflare.commarvin.ns.cloudflare.comLocation describes the IP network.
8c9c090824fdb3c8db9523849884dafa8b527128b7cf943c3329265a59ee1dedSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of alvpure.shop · checked Oct 1, 2026
46.245.239.81. 15 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261001-48F171 Recipient: abuse@rashost.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.


Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.
Template-based draft · optional AI wording assistance requires separate consent
Cada faixa representa um motivo pelo qual um domínio está vinculado a este host. O tamanho dos nós indica as detecções do VirusTotal, e os nós tracejados já estão offline. As listas completas seguem abaixo.
Este IP de origem hospeda vários domínios de phishing — a infraestrutura pode ser compartilhada entre campanhas.
Esses domínios também têm como alvo os usuários do Fakeshop. Ver todas as ameaças do tipo “Fakeshop” →
Relatórios adicionados recentemente do banco de dados PhishDestroy. Esses links de descoberta não implicam infraestrutura ou propriedade compartilhada.
Análise de ameaças usando lista de bloqueio armazenada, WHOIS, DNS e evidências de verificação pública
Digitalize agoraEnvie domínios suspeitos para nosso banco de dados de ameaças — proteja a comunidade
DenunciarRelatórios recentes de phishing e alterações de disponibilidade observadas
MonitorarMonitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo