보안 보고서로 이동
도메인 보안 및 위협 인텔리전스
morlseopt.com favicon

morlseopt.com

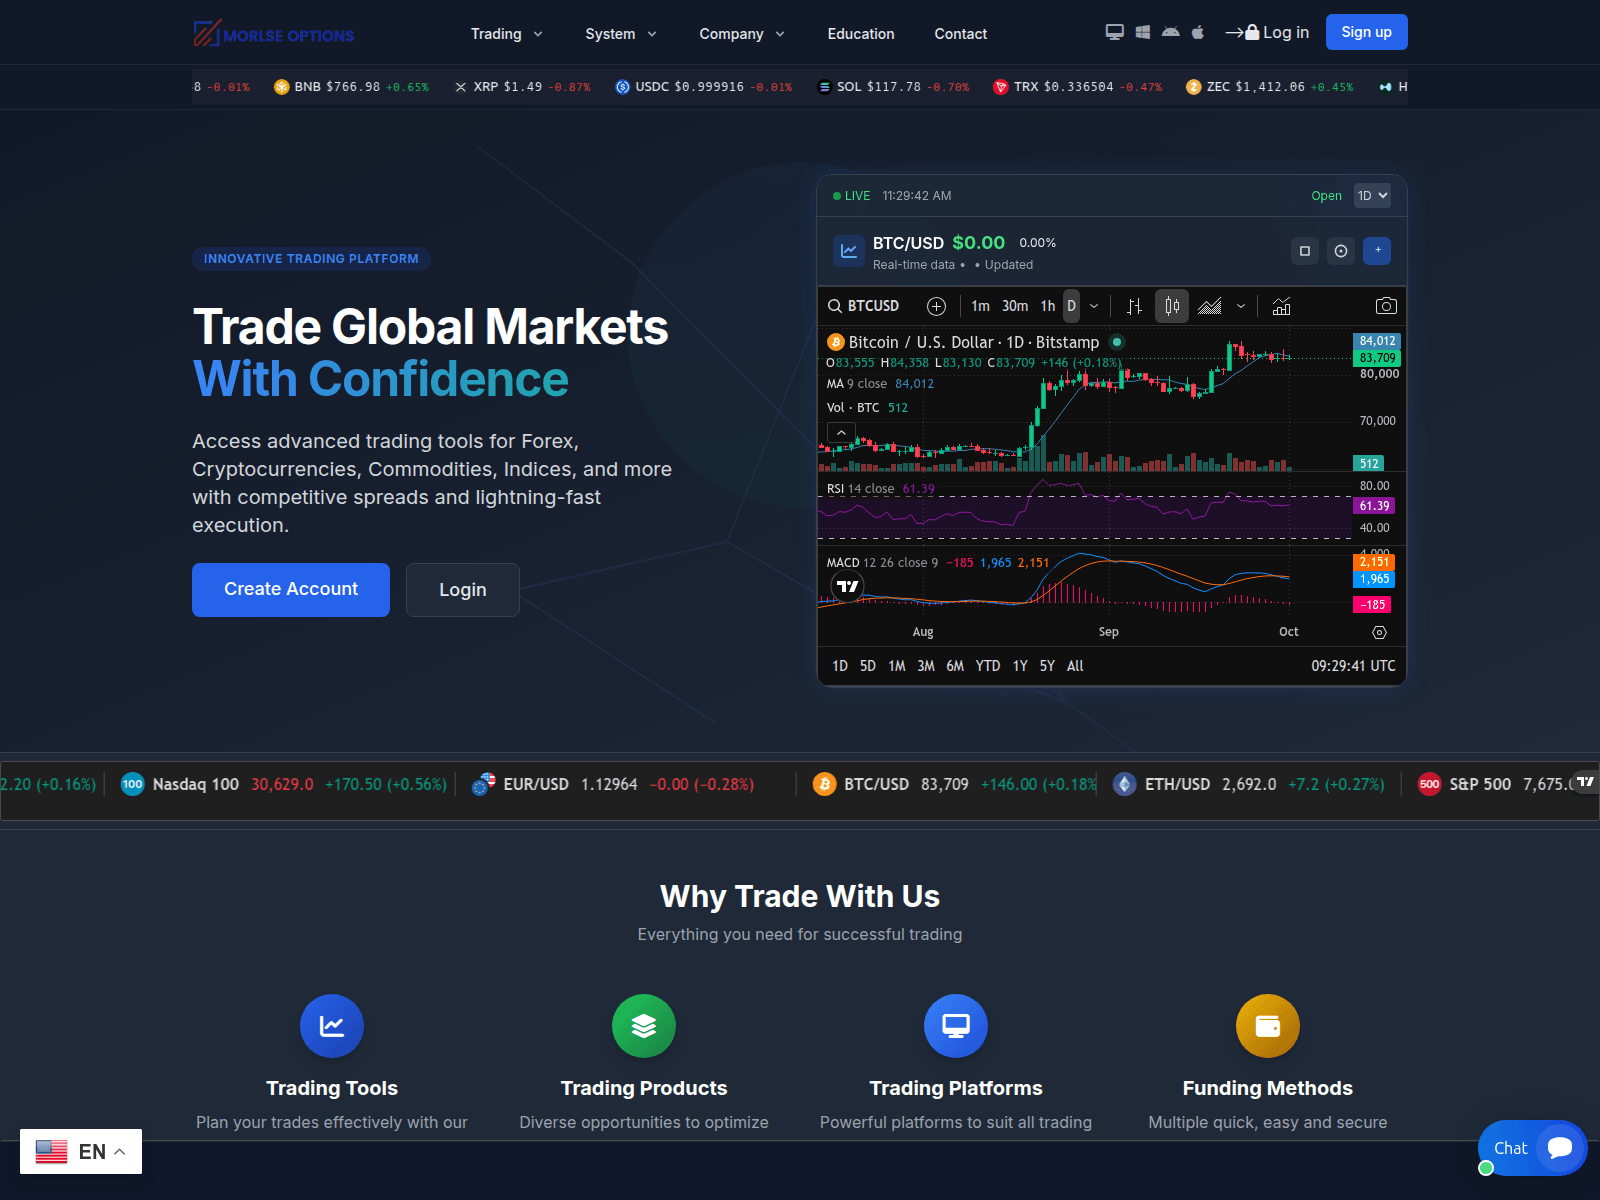
“Morlse Options | CFD Trading — Trading on Stocks, Gold, Oil, Indices”

등록기관
INWX
Resolved IP
23.153.104.17
Registered
2026년 8월 30일
위협 평결 심각
가용성 마지막으로 알려진 활성 최근에 저장된 도달 가능성 관찰 관측됨
Source: HTTP probe
VirusTotal 탐지: 5/92 브랜드 사칭: Across
OTX: 1 ref 2026년 10월 3일 Across
API
이 도메인은 악성 도메인으로 표시되었습니다.
탐지를 보고하는 보안 엔진: 5. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
보고서 요약

morlseopt.com — 마지막으로 알려진 활성 (HTTP 200). 브랜드 사칭: Across; 사기 유형: Impersonation. 증거 요약: VirusTotal 5/92 (alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, Netcraft, SOCRadar); URLScan malicious verdict; PhishDestroy score 83/100. 등록기관: INWX.

원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.

VirusTotal
VirusTotal
5 det.
OTX references
URLScan
URLScan
TLS 인증서
만료되었거나 검증되지 않음
연령
1 mo New
관측 상태
마지막으로 알려진 활성 200
PhishDestroy
DestroyList
등재됨

Source evidence

6 sources

VirusTotal

5 / 92

보고서

URLScan verdict

malicious

보고서

OTX

1 community reference

보고서

URLScan capture

저장된 보고서

Stored URLScan capture preview
보고서

CF 레이더

Report stored; verdict not recorded

보고서

Google Safe Browsing

Checked; no threat flag recorded

보고서

증거 요약

심각
VirusTotal
5/92
OTX
1 community ref
URLScan
Stored capture

Assessment

The domain morlseopt.com was noted in the PhishDestroy internal catalogue on 2026-10-05, following its first observation on 2026-10-03. It was registered on 2026-08-30, providing a documented timeline for its appearance in monitoring sources.

Recorded Evidence

PhishDestroy internally listed morlseopt.com as of 2026-10-05. OTX recorded one pulse for the domain on 2026-10-05. The domain was registered with INWX GmbH on 2026-08-30 and first observed on 2026-10-03.

Interpretation

The presence of morlseopt.com in both the PhishDestroy internal catalogue and OTX pulse records shows that it has been documented by multiple monitoring sources within a short period after its registration. These observations allow for comparison of its status across different dates and monitoring platforms.

Recommended Actions

For morlseopt.com, preserve the PhishDestroy internal listing and OTX pulse records for ongoing review. Use these source records to compare future monitoring results and track any new observations related to the domain.

탐지 회피 분석

클로킹 의심: 스캐너와 방문자 제목이 다름

아직 스캔되지 않았습니다 크롤러와 브라우저 간의 차이는 아직 보고된 바가 없습니다.

이 호스트에 대해 저장된 크롤러 대 브라우저 관측 데이터와, 케이타로 스타일의 트래픽 분배 시스템을 위한 실시간 지문 확인 정보.

저장된 은신 플래그
아직 스캔되지 않았습니다
마지막 은폐 스캔
스캐너가 감지한 서버 헤더
LiteSpeed

스캐너 메모: captcha: raw=captcha; http=200; via=https_proxy; server=LiteSpeed

보안 스캐너에 표시된 제목Bot Verification
브라우저 방문자에게 표시되는 제목Morlse Options | CFD Trading — Trading on Stocks, Gold, Oil, Indices
TDS 지문 인식 실시간 확인
이 패널이 열려 있을 때 PhishDestroy 스캐너에서 실행되는 7개의 케이타로 지문과 크롤러 대 브라우저 비교 결과.
기다림

저장된 캡처 · 2 captures

Domain details

도메인
URLScan Verdict 악성 score 100 Phishing report ↗
IP 평판 abuse score 2/100 1 report PhishingBad Web Bot checked 2026년 10월 5일
OTX Tags 2026-10all-domainscrypto도메인monthlyphishdestroyphishingscam
등록기관 INWX
악용 신고 연락처["abuse@inwx.com"]
ICANN 레지스트리ICANN Lookup (RDAP) →
등록 정보생성됨 2026년 8월 30일 (41d · New) — Expires 2027년 8월 30일
HTTP 상태200
기술 세부 정보Provenance & timestamps
최초 발견2026년 10월 3일
DOM Analysisanalyzed 2026년 10월 9일score 83/1004 brand signals
Submitted URLhttps://morlseopt.com/
Favicon Hash
페이지 제목
Morlse Options | CFD Trading — Trading on Stocks, Gold, Oil, Indices
Impersonates
Across Ethereum Ledger LinkedIn
TLS 인증서
Certificate hostname mismatch · 발급자 Let's Encrypt / YR1 · stored validity ends in 67 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
23.153.104.17
Network ASN
AS32561
Organization
Aquiryn LLC
Observed location
Sheridan, US
Server header
LiteSpeed

네임서버 1

  • ns8.my-control-panel.com

Mail routing 1 MX record

  • morlseopt.compriority 0

Location describes the IP network.

TLS 인증서

Issuer
Let's Encrypt / YR1
Valid from
2026-09-19 07:28:14
Valid until
2026-12-18 07:28:13
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-06 10:02:03 UTC
Collection source
PhishDestroy collector
Certificate fingerprint630804c5e57f10dcc3ca1727af6e035e1e355bea052662e87e345e55a1211734
Certificate names · 11 SANs
  • autoconfig.morlseopt.com
  • autodiscover.morlseopt.com
  • cpanel.morlseopt.com
  • cpcalendars.morlseopt.com
  • cpcontacts.morlseopt.com
  • mail.morlseopt.com
  • morlseopt.com.primestocksmarket.com
  • webdisk.morlseopt.com
  • webmail.morlseopt.com
  • www.morlseopt.com
  • www.morlseopt.com.primestocksmarket.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 23.153.104.17rapiddns.io

Latest Classified Outcome 2026-10-11 10:08:43 UTC

Primary outcome Reachable but protected reason: Captcha 85% confidence
Attribution mechanism: Challenge source: Current Http Probe
Evidence layers Availability: Reachable but protected Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Reachable but protected Captcha Challenge 85% 2026-10-11 10:08:43 UTC
RDAP registration 알 수 없음
Observed timeline last reachable: 2026-10-11 10:08:43 UTC last content: 2026-10-09 10:08:03 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
위협 인텔리전스 교차 확인 · source references
ScamAdviser Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
이 도메인 신고하기 증거를 제출하고 다른 사람들을 보호하는 데 힘을 보태주세요

VirusTotal 분석

5 / 92 보안 공급업체가 이 도메인에 플래그를 지정했습니다.
View on VT
Last analyzed First positive detection Previous stored snapshot: 4 detections
alphaMountain.ai
Forcepoint ThreatSeeker
Gridinsoft
넷크래프트
SOCRadar

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-03 19:28:03 UTC
    Domain ingestion complete. Initial state is marked as unknown pointing to IP 23.153.104.17.

위협 대응 Pipeline

발견
Analysis
Monitoring

10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

위협 탐지됨
morlseopt.com 탐지되어 전체 분석을 위해 대기열에 추가됨
2026년 10월 3일
URLScan.io Capture
저장됨 URLScan report with capture artifacts
URLScan Verdict
URLScan returned a malicious verdict · score 100
2026년 10월 7일
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
5/92 recorded on VirusTotal
2026년 10월 11일
OTX Community References
1 community publication reference on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
2026년 10월 5일
Brand Impersonation
Impersonation of Across
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
Technical Analysis Recorded
보고서에는 저장된 기술 또는 포렌식 분석 결과가 포함됩니다.
2026년 10월 11일
DestroyList 게시됨
2026년 10월 3일
Monitoring Continues
도메인은 계속 연결 가능하거나 액세스가 제한되어 있습니다. 향후 점검을 통해 이 관찰 내용이 업데이트될 수 있습니다.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

웨이백 머신 Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

증거 및 외부 보고서

심층 분석

이 사이트로 인해 영향을 받으셨나요?

4 evidence signal groups linked 0 reports recorded 마지막으로 알려진 활성
If credentials were compromised, report immediately. Do not engage with recovery scammers.

계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.

유로폴
EU 국가의 공식 신고 채널 찾기
National police directory
회복 사기꾼들을 조심하세요! 범죄자는 수사관, 변호사, 회복요원인 척 하면서 피해자에게 다시 연락할 수도 있습니다. 선불 비용을 지불하거나 자격 증명을 공유하지 마십시오. 회복 관련 사기에 대해 자세히 알아보기 →

지역 당국에 신고하십시오

공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.

97개국 디렉토리

Template-based draft · optional AI wording assistance requires separate consent

AI 지원 초안 - 사고 세부정보는 AI 제공업체에서 처리됩니다. · 직접 검토하고 제출하세요.

모든 도메인 확인

저장된 차단 목록, WHOIS, DNS 및 공개 스캔 증거를 사용한 위협 분석

지금 스캔하기

피싱 신고

의심스러운 도메인을 당사의 위협 데이터베이스에 신고해 주세요 — 커뮤니티를 보호해 주세요

보고서

실시간 위협 정보

최근 피싱 보고서 및 관찰된 가용성 변경 사항

모니터링

최신 정보를 확인하고, 안전을 지키세요

실시간 위협을 모니터링하거나, 오탐이라고 판단될 경우 이 목록에 이의를 제기하십시오.

실시간 위협 정보 이 목록에 이의 제기하기
HTML · IFRAME

이 보고서 삽입하기

이 위협 정보를 귀하의 웹사이트나 블로그에 공유하세요

embed.html
<iframe
  src="https://phishdestroy.io/ko/embed/domain/morlseopt.com"
  title="PhishDestroy threat report for morlseopt.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>