보안 보고서로 이동
도메인 보안 및 위협 인텔리전스
ambetterhealthplans.org favicon

ambetterhealthplans.org

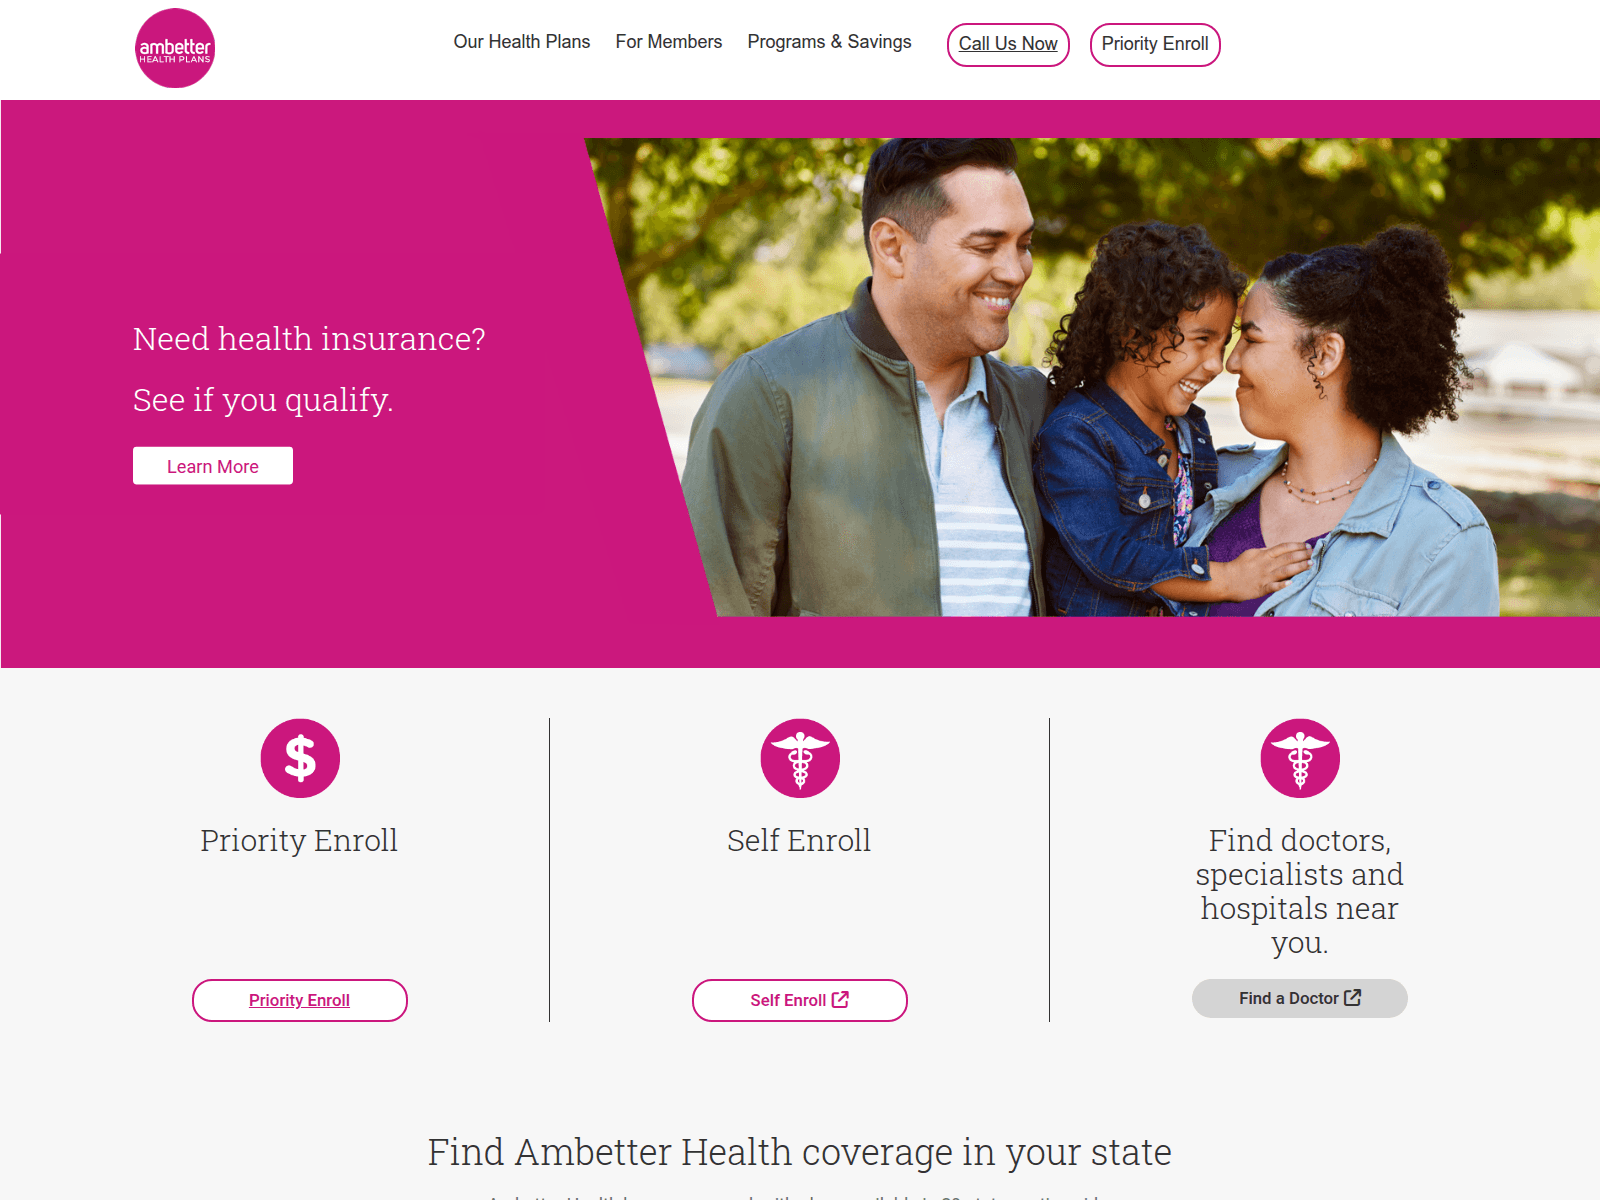
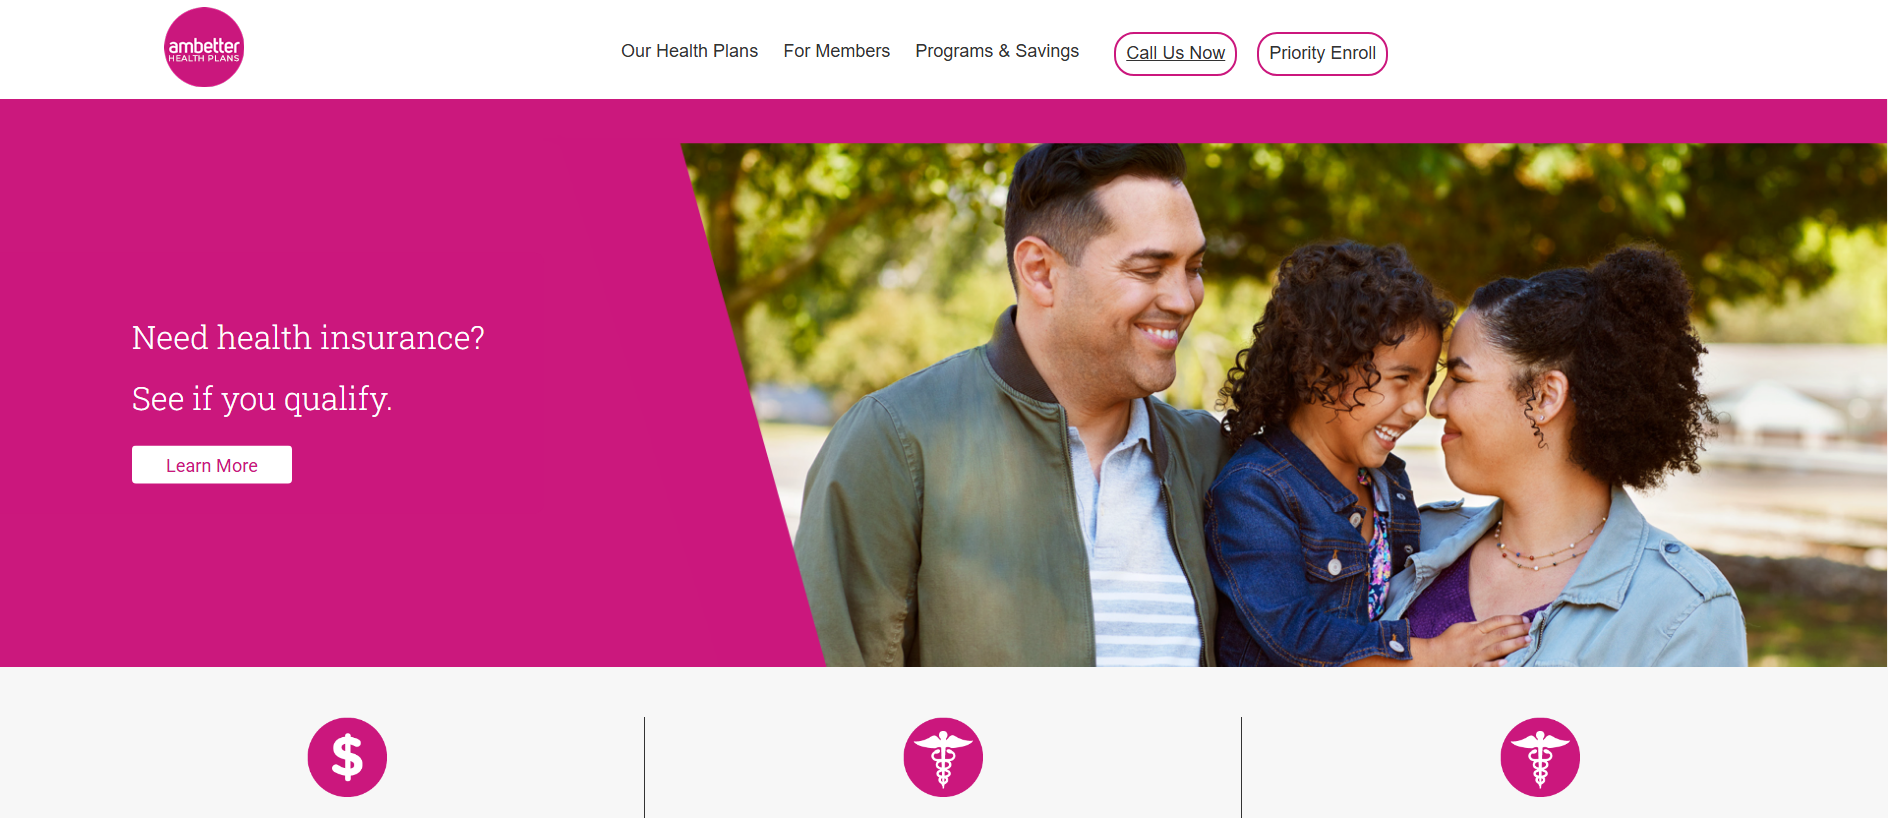
“Affordable Health Insurance: Shop & Compare Plans | Ambetter”

등록기관
TUCOWS.COM, CO
Resolved IP
34.174.117.206
Registered
2024년 8월 7일
위협 평결 심각
가용성 마지막으로 알려진 활성 최근에 저장된 도달 가능성 관찰 관측됨
Source: HTTP probe
VirusTotal 탐지: 15/89 URLQuery threat systems: 5 alerts 브랜드 사칭: Near
OTX: 1 ref 2026년 9월 12일 Near 1 Report Sent
API
이 도메인은 악성 도메인으로 표시되었습니다.
탐지를 보고하는 보안 엔진: 15. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is domainabuse@tucows.com. The latest stored availability evidence still shows the domain reachable; 29 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
29 days
Reports sent
1
Latest case ID
PD-20260912-93C7C6
Current status
HTTP 202 at latest stored check
보고서 요약

ambetterhealthplans.org — 마지막으로 알려진 활성 (HTTP 202). 브랜드 사칭: Near; 사기 유형: Impersonation. 증거 요약: VirusTotal 15/89 (alphaMountain.ai, BitDefender, CyRadar, ESET, Forcepoint ThreatSeeker); URLQuery 5 alerts; CF Radar malicious; PhishDestroy score 100/100. 등록기관: TUCOWS.COM, CO.

원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.

VirusTotal
VirusTotal
15 det.
URLQuery
URLQuery
5 threat alerts
OTX references
CF 레이더
악성
URLScan
URLScan
TLS 인증서
만료되었거나 검증되지 않음
연령
2.2 yr
관측 상태
마지막으로 알려진 활성 202
PhishDestroy
DestroyList
등재됨
Reports Sent
1

Source evidence

7 sources

VirusTotal

15 / 89

보고서

URLQuery

5 threat-system alerts

보고서

CF 레이더

provider verdict: malicious

보고서

OTX

1 community reference

보고서

URLScan capture

저장된 보고서

Stored URLScan capture preview
보고서

URLScan verdict

분석 완료

보고서

Google Safe Browsing

Checked; no threat flag recorded

보고서
네트워크 보안 인텔리전스
Threat Detection Systems 5 alerts
Detection System Indicator Verdict Alert
DigiCert UltraDNS ambetterhealthplans.org malicious Sinkholed
Cloudflare DNS ambetterhealthplans.org malicious Sinkholed
Quad9 DNS ambetterhealthplans.org malicious Sinkholed
DNS4EU ambetterhealthplans.org malicious Sinkholed
OpenDNS ambetterhealthplans.org phishing Phishing Block
CF Cloudflare Radar Verdict 악성
Phishing

증거 요약

심각
VirusTotal
15/89
OTX
1 community ref
URLScan
Stored capture

Assessment

ambetterhealthplans.org returned HTTP status 403 on 2026-10-01, a dated response recorded during an HTTP check. The same domain was first observed on 2026-09-12, and a PageSpeed performance score of 36 was recorded that day.

Recorded Evidence

The PhishDestroy internal listing for ambetterhealthplans.org was recorded on 2026-09-12. OTX showed 1 pulse on 2026-09-12, while VirusTotal reported 15 detections across 89 scanners on 2026-09-20. The SSL certificate from Let's Encrypt / YR1 was scanned on 2026-09-12, and registration through TUCOWS.COM, CO. dates to 2024-08-07.

Interpretation

The PhishDestroy listing and the OTX pulse share the 2026-09-12 date, so those two records can be compared directly. The VirusTotal result and the HTTP response carry later dates, meaning each reflects a separate point in time rather than a single snapshot. Because the observation dates differ, a reader should treat the records as dated entries to line up, not as one combined measurement.

Recommended Actions

Retain the dated records for ambetterhealthplans.org, including the PhishDestroy listing, OTX pulse, VirusTotal result and HTTP response, so later checks can be matched against them. When new observations arrive, compare each against the record bearing the closest date instead of merging entries from different days. Avoid submitting sensitive information to ambetterhealthplans.org while its status remains under review.

탐지 회피 분석

클로킹 및 트래픽 분산 점검

아직 스캔되지 않았습니다 크롤러와 브라우저 간의 차이는 아직 보고된 바가 없습니다.

이 호스트에 대해 저장된 크롤러 대 브라우저 관측 데이터와, 케이타로 스타일의 트래픽 분배 시스템을 위한 실시간 지문 확인 정보.

저장된 은신 플래그
아직 스캔되지 않았습니다
마지막 은폐 스캔
스캐너가 감지한 서버 헤더
nginx

스캐너 메모: alive_http: raw=http_202; http=202; via=https_proxy; server=nginx

TDS 지문 인식 실시간 확인
이 패널이 열려 있을 때 PhishDestroy 스캐너에서 실행되는 7개의 케이타로 지문과 크롤러 대 브라우저 비교 결과.
기다림

저장된 캡처 · 4 captures

Domain details

도메인
URLScan Verdict 분석 완료 score 0 report ↗
IP 평판 abuse score 0/100 0 reports checked 2026년 9월 12일
등록기관 TUCOWS.COM, CO US(US)
등록 정보생성됨 2024년 8월 7일 — Expires 2027년 8월 7일
HTTP 상태202
기술 세부 정보Provenance & timestamps
최초 발견2026년 9월 12일
DOM Analysisanalyzed 2026년 9월 12일score 93/1001 brand signal
Submitted URLhttp://ambetterhealthplans.org/
Favicon Hash
사건 ID
페이지 제목
Affordable Health Insurance: Shop & Compare Plans | Ambetter
Impersonates
Near
TLS 인증서
Hostname coverage not recorded · 발급자 Let's Encrypt / YR2 · stored validity ends in 74 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
34.174.117.206
Network ASN
AS396982
Organization
Google Cloud (us-south1)
Observed location
Dallas, US
Server header
nginx

네임서버 2

  • ns1.siteground.net
  • ns2.siteground.net

Mail routing 3 MX records

  • mx10.antispam.mailspamprotection.compriority 10
  • mx20.antispam.mailspamprotection.compriority 20
  • mx30.antispam.mailspamprotection.compriority 30

Location describes the IP network.

TLS 인증서

Issuer
Let's Encrypt / YR2
Valid from
2026-09-26 08:25:41
Valid until
2026-12-25 08:25:40
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 01:03:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprint51116639a6b815e44129707503a0f8732713b5b6b4fd8ab27daf813070a542f7

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 34.174.117.206rapiddns.io

Latest Classified Outcome 2026-10-11 22:21:25 UTC

Primary outcome 활성 콘텐츠 reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation 활성 콘텐츠 Ordinary HTTP content served 90% 2026-10-11 22:21:25 UTC
RDAP registration 알 수 없음
Observed timeline last reachable: 2026-10-11 22:21:25 UTC last content: 2026-10-11 22:21:25 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Casino / Gambling License Verification
Unverified gambling license
This domain markets casino/gambling services. Scam casinos routinely display fake Curaçao, MGA, or Kahnawake license badges that don’t exist in the real registries. Always verify the license number against the official regulator database before depositing. If the site shows a seal but no clickable registry link — or the linked registry page doesn’t exist — treat it as fraudulent.
Curaçao eGaming (official) Malta Gaming Authority UK Gambling Commission PA Gaming Control Kahnawake Gaming Gibraltar Gambling
기술 · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
이 도메인 신고하기 증거를 제출하고 다른 사람들을 보호하는 데 힘을 보태주세요

VirusTotal 분석

15 / 89 보안 공급업체가 이 도메인에 플래그를 지정했습니다.
View on VT
Last analyzed Previous stored snapshot: 16 detections
alphaMountain.ai
BitDefender
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
카스퍼스키
Lionic
Seclookup
SOCRadar
소포스
VIPRE
Webroot

보관된 증거

Wayback Machine Snapshot
증거 검토를 위해 과거 스냅샷을 사용할 수 있습니다.
View Archive
사이트 성능 분석

Google PageSpeed Insights — mobile performance audit of ambetterhealthplans.org · checked Sep 12, 2026

36
Poor
Performance
FCP
4.55s
First Contentful Paint
LCP
19.26s
Largest Contentful Paint
CLS
0.112
Cumulative Layout Shift
TBT
749ms
Total Blocking Time
SI
9.58s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-09-12 17:58:18 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 34.174.117.206.

위협 대응 Pipeline

발견
Analysis
Notifications
Monitoring

12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

위협 탐지됨
ambetterhealthplans.org 탐지되어 전체 분석을 위해 대기열에 추가됨
2026년 9월 12일
URLScan.io Capture
저장됨 URLScan report with capture artifacts
2026년 9월 12일
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in 웨이백 머신 — historical evidence archived
2026년 9월 23일
VirusTotal
15/89 recorded on VirusTotal
2026년 9월 20일
OTX Community References
1 community publication reference on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
2026년 9월 12일
CF Radar: Malicious
Cloudflare Radar classified this domain as phishing
Brand Impersonation
Impersonation of Near
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
2026년 9월 12일
Technical Analysis Recorded
보고서에는 저장된 기술 또는 포렌식 분석 결과가 포함됩니다.
2026년 10월 12일
Sent Report Recorded
Stored outgoing record associated with registrar TUCOWS.COM, CO., 2 abuse contacts
tucows@domains.siteground.comdomainabuse@tucows.com
2026년 9월 12일
DestroyList 게시됨
2026년 9월 12일
Monitoring Continues
도메인은 계속 연결 가능하거나 액세스가 제한되어 있습니다. 향후 점검을 통해 이 관찰 내용이 업데이트될 수 있습니다.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

웨이백 머신 Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

커뮤니티 인텔리전스

커뮤니티 신고 1건

범주PHISHING

The PhishFort Detection System has flagged this as a domain threat, classified as phishing. Threat detected at 2025-06-25T05:56:24.514Z.

증거 및 외부 보고서

Third-Party Detection — ChainAbuse
1 report filed for ambetterhealthplans.org · category: Phishing · source checked
Flagged by PhishFort Detection System on Jun 25, 2025 — automated submission, not a user testimony. Source: ChainAbuse (TRM Labs).
제출된 증거 스냅샷
Sent: Ledger records: 1 Case ID: PD-20260912-93C7C6 Recipient: domainabuse@tucows.com
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 922.7 KB
PDF notice generated Notice text archived (653 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (US):
18 U.S.C. § 1343 - Wire Fraud
18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA)
15 U.S.C. § 45 - FTC Act (Deceptive Practices)
Federal laws prohibit wire fraud, computer fraud, and deceptive business practices.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
심층 분석

이 사이트로 인해 영향을 받으셨나요?

6 evidence signal groups linked 1 reports recorded 마지막으로 알려진 활성
If credentials were compromised, report immediately. Do not engage with recovery scammers.

계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.

유로폴
EU 국가의 공식 신고 채널 찾기
National police directory
회복 사기꾼들을 조심하세요! 범죄자는 수사관, 변호사, 회복요원인 척 하면서 피해자에게 다시 연락할 수도 있습니다. 선불 비용을 지불하거나 자격 증명을 공유하지 마십시오. 회복 관련 사기에 대해 자세히 알아보기 →

지역 당국에 신고하십시오

공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.

97개국 디렉토리

Template-based draft · optional AI wording assistance requires separate consent

AI 지원 초안 - 사고 세부정보는 AI 제공업체에서 처리됩니다. · 직접 검토하고 제출하세요.

모든 도메인 확인

저장된 차단 목록, WHOIS, DNS 및 공개 스캔 증거를 사용한 위협 분석

지금 스캔하기

피싱 신고

의심스러운 도메인을 당사의 위협 데이터베이스에 신고해 주세요 — 커뮤니티를 보호해 주세요

보고서

실시간 위협 정보

최근 피싱 보고서 및 관찰된 가용성 변경 사항

모니터링

최신 정보를 확인하고, 안전을 지키세요

실시간 위협을 모니터링하거나, 오탐이라고 판단될 경우 이 목록에 이의를 제기하십시오.

실시간 위협 정보 이 목록에 이의 제기하기
HTML · IFRAME

이 보고서 삽입하기

이 위협 정보를 귀하의 웹사이트나 블로그에 공유하세요

embed.html
<iframe
  src="https://phishdestroy.io/ko/embed/domain/ambetterhealthplans.org"
  title="PhishDestroy threat report for ambetterhealthplans.org"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>