VirusTotal
22 / 94
보고서

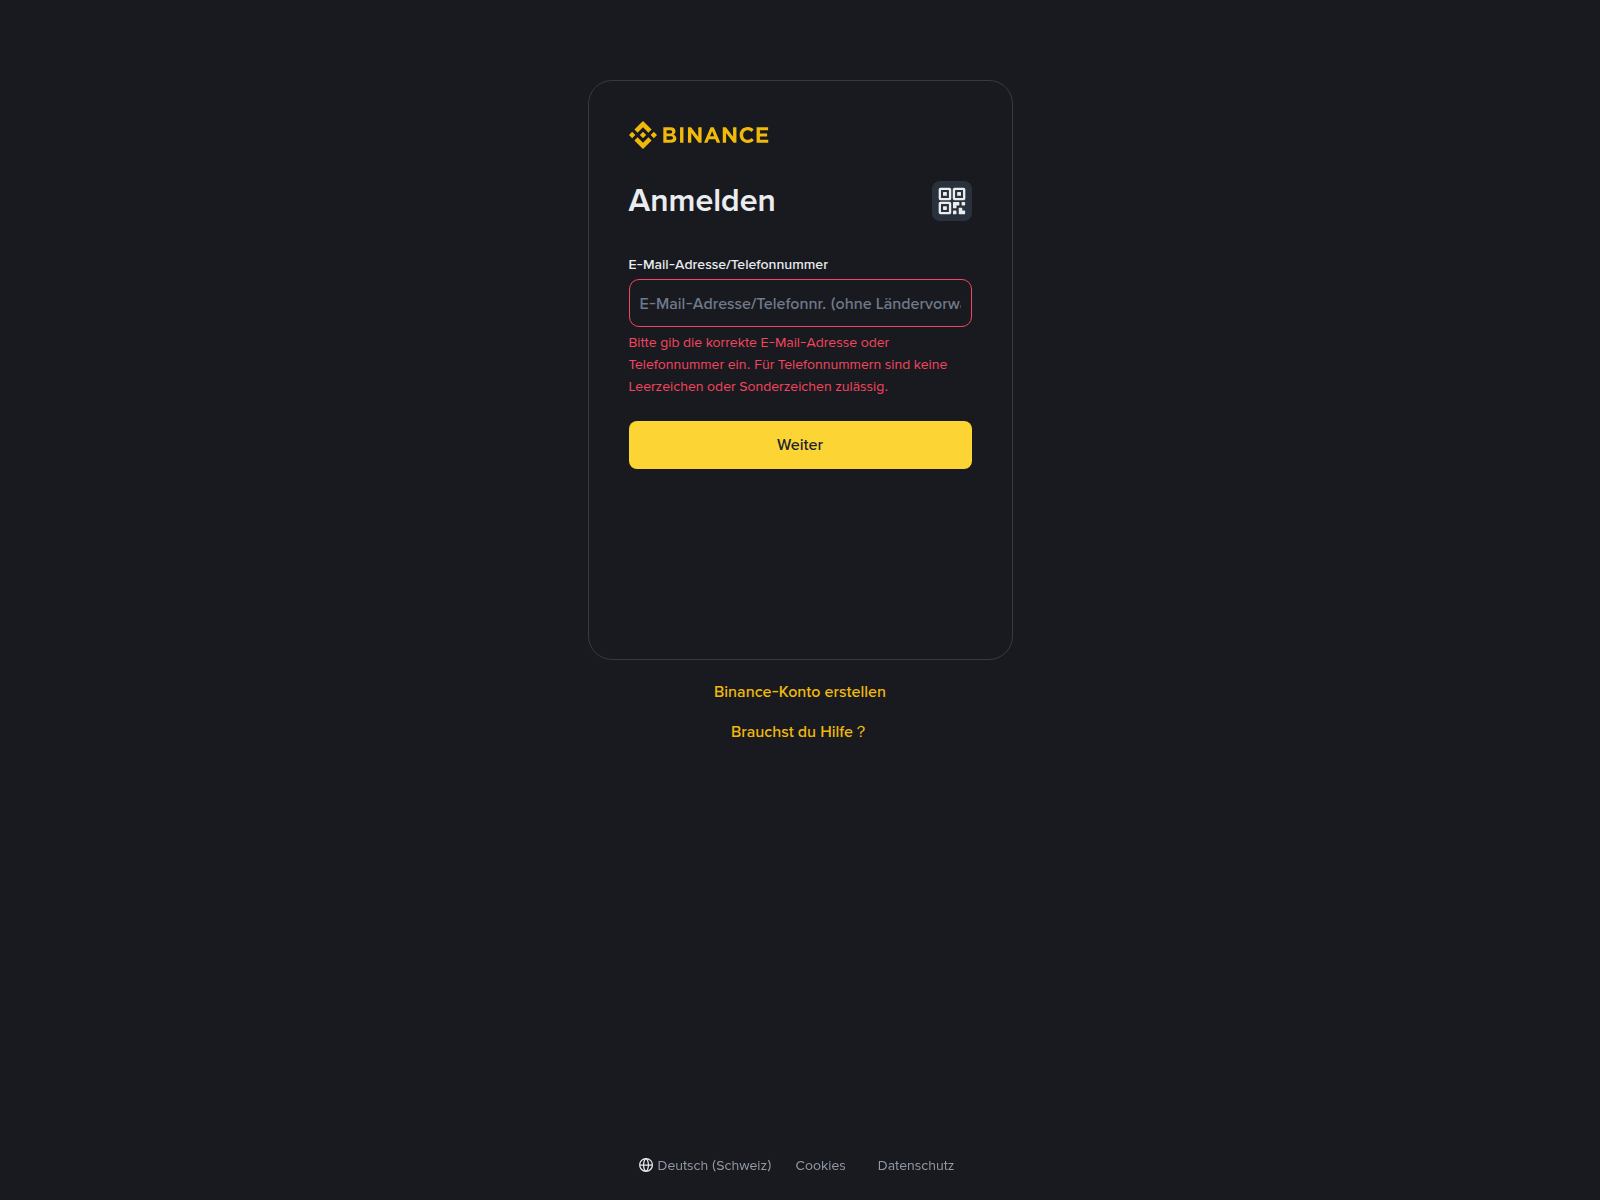
“Log In | Binance”
accounts.bmwweb.cc — 콘텐츠를 사용할 수 없음 (HTTP 502). 브랜드 사칭: Binance; 사기 유형: Crypto Scam. 증거 요약: VirusTotal 22/94 (ADMINUSLabs, Criminal IP, alphaMountain.ai, BitDefender, Chong Lua Dao); URLQuery 4 alerts; URLScan malicious verdict; PhishDestroy score 100/100. 등록기관: Amazon.
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.

| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Hagezi Threat Feed | accounts.bmwweb.cc |
malicious | Sinkholed |
| DNS4EU | accounts.bmwweb.cc |
malicious | Sinkholed |
| Cloudflare DNS | accounts.bmwweb.cc |
malicious | Sinkholed |
| OpenDNS | accounts.bmwweb.cc |
phishing | Phishing Block |
The domain accounts.bmwweb.cc is flagged as a brand impersonation threat targeting Binance, a major cryptocurrency exchange platform. Analysis indicates the site was designed to mimic Binance’s login interface, as evidenced by the page title 'Log In | Binance,' suggesting an intent to harvest user credentials. The domain is currently offline, though prior activity aligns with credential theft campaigns. Infrastructure analysis reveals the domain was registered on March 11, 2026, through Amazon Registrar, Inc., and resolves to the IP address 43.159.94.13, hosted in Singapore under AS139341 (ACE). The SSL certificate is issued by TrustAsia Technologies, Inc., under the TrustAsia DV TLS RSA CA 2025 chain. Detection metrics show the domain was flagged by 22 of 95 security vendors on VirusTotal and appears on one security blocklist. The combination of recent registration, brand impersonation, and low detection prevalence underscores its elevated risk profile. Current status confirms the domain has been taken offline, though residual risk remains for users who may have interacted with it prior to deactivation. Organizations and individuals are advised to block the domain and associated IP (43.159.94.13) at the network level. Users should verify the authenticity of login portals by cross-checking URLs with official sources and enable multi-factor authentication to mitigate credential theft risks. Monitoring for similar domains registered under the same registrar or IP range is recommended for proactive threat detection.
이 호스트에 대해 저장된 크롤러 대 브라우저 관측 데이터와, 케이타로 스타일의 트래픽 분배 시스템을 위한 실시간 지문 확인 정보.
스캐너 메모: transient_502: raw=transient_502; http=502; via=http_proxy
 (US)
ns-670.awsdns-19.netLocation describes the IP network.
2549a05932998d0e0939a4499a6774279b33871b29181845a4cf34fa4e4112a7Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of accounts.bmwweb.cc · checked Mar 24, 2026
11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
저장된 유사 도메인 187개
전체 187개 중 100개 표시
커뮤니티 구성원 1명이 신고 · 최초 확인 2026년 3월 11일
PD-20260312-786020 Recipient: as139341_abuse@aceville.net Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (GB): Computer Misuse Act 1990 Fraud Act 2006 Communications Act 2003 - Section 127 UK law criminalizes unauthorized computer access, fraud, and malicious communications. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
Template-based draft · optional AI wording assistance requires separate consent
각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
이 호스트와 동일한 파비콘 해시이거나 동일한 페이지 제목을 가진 경우.
이 원본 IP는 여러 피싱 도메인을 호스팅합니다. 인프라는 여러 캠페인에서 공유될 수 있습니다.
이 도메인들은 Binance 사용자들도 표적으로 삼고 있습니다. Binance의 모든 위협 보기 →
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.
최근 PhishDestroy 데이터베이스에서 보고서가 추가되었습니다. 이러한 검색 링크는 공유 인프라나 소유권을 의미하지 않습니다.