セキュリティレポートへ移動
ドメインのセキュリティと脅威インテリジェンス
webs3coinme.lol favicon

webs3coinme.lol

“undefined”

レジストラ
NameMart
Resolved IP
104.21.9.4
Registered
2026年10月1日
脅威の評決 クリティカル
可用性 未検証 現在の到達可能性は未検証です 観測された
Source: HTTP probe
VirusTotal 検出数: 7/92 保存されたブロックリストの一致: 2 ブランドの偽装: Telegram 若いドメイン: 12 日経過
OTX: 3 refs 2026年10月9日 Telegram 1 Report Sent CDN
API
このドメインは悪意のあるものとして報告されています
検出を報告するセキュリティ エンジン: 7。 一致を報告する公開ブロックリスト: 2。 細心の注意を払ってください — 資格情報や個人情報を入力しないでください。
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@namemart.com. The latest stored availability evidence still shows the domain reachable; 3 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
3 days
Reports sent
1
Latest case ID
PD-20261009-0DB9E9
Current status
Observed active at latest stored check
レポート概要

webs3coinme.lol — 未検証. ブランドの偽装: Telegram; 詐欺タイプ: Impersonation. 証拠の概要: VirusTotal 7/92 (CRDF, Emsisoft, Fortinet, Kaspersky, Netcraft); URLScan malicious verdict; 2 external blocklist matches (MetaMask, SEAL); CF Radar malicious; PhishDestroy score 100/100. レジストラ: NameMart.

元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。

VirusTotal
VirusTotal
7 det.
OTX references
CFレーダー
悪意あり
TLS証明書
期限切れまたは未検証
年齢
12d Very New!
PhishDestroy
DestroyList
掲載あり
Reports Sent
1

Source evidence

7 sources

URLScan verdict

malicious

レポート

URLQuery

Report stored; detailed verdict not recorded

レポート

OTX

3 community references

レポート

URLScan capture

保存されたレポート

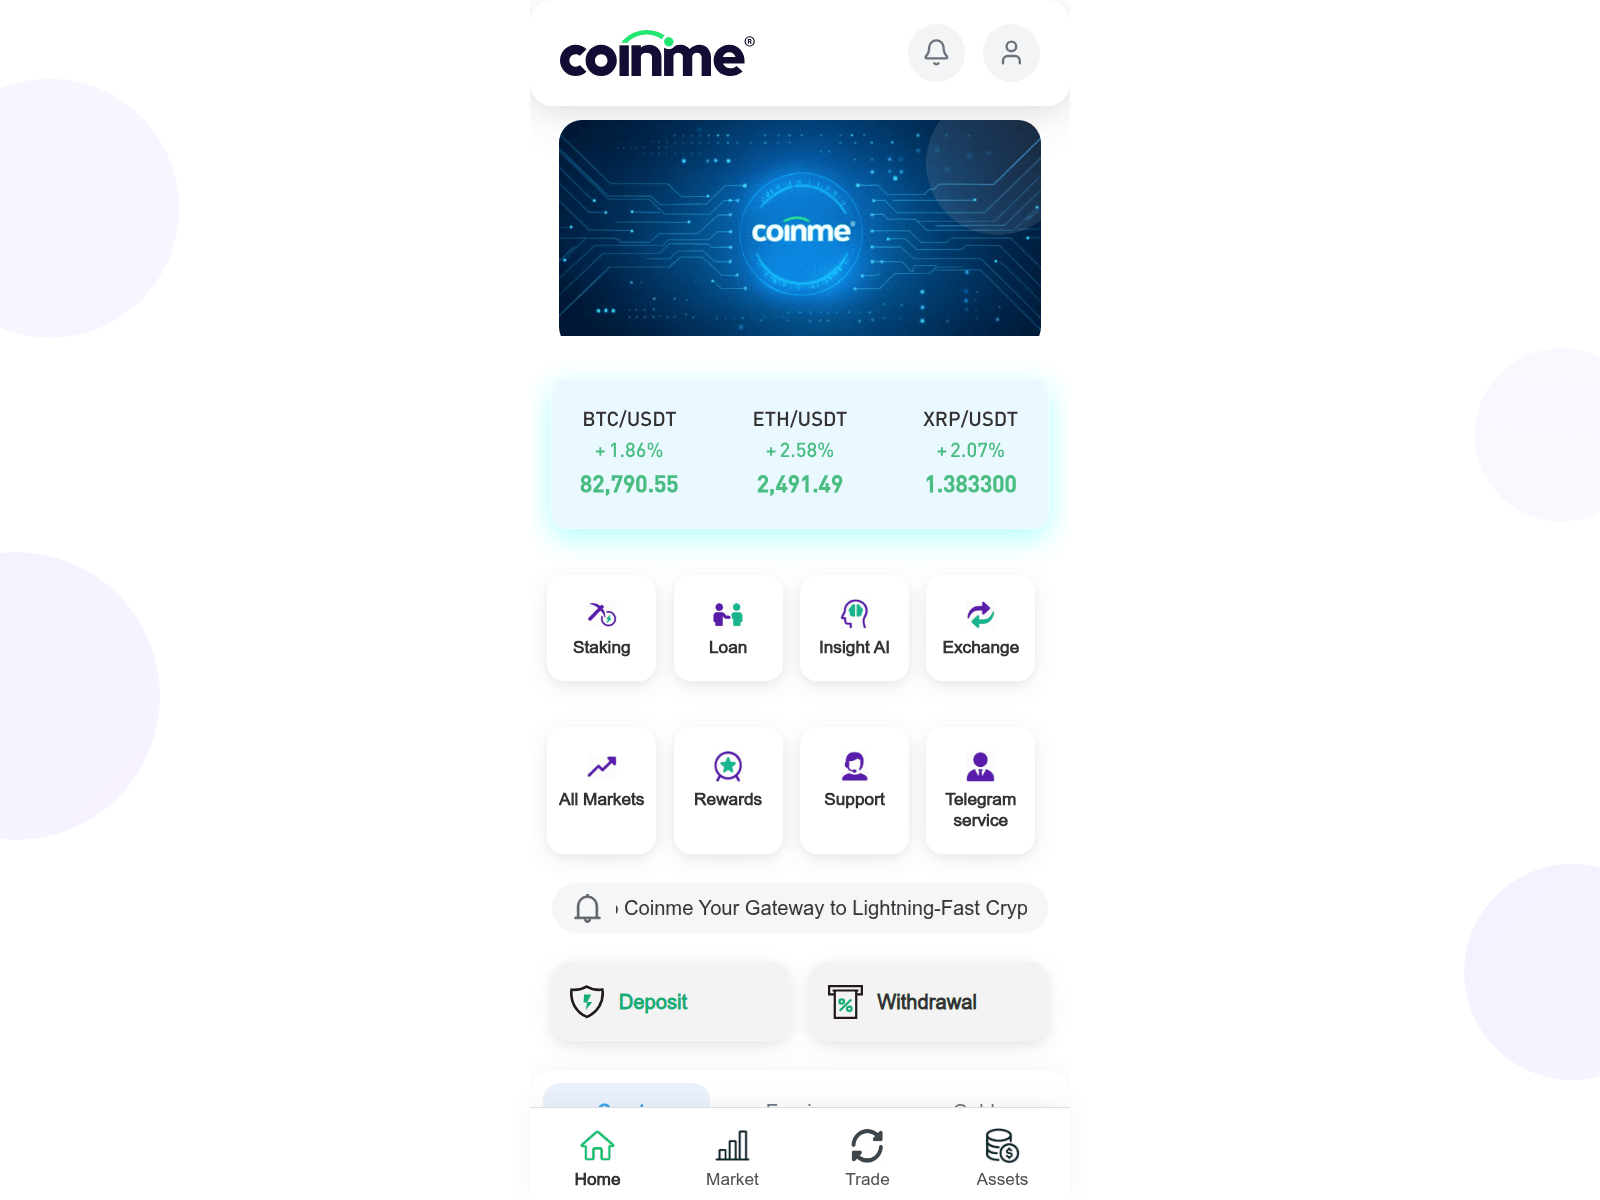
Stored URLScan capture preview
レポート

Google Safe Browsing

Checked; no threat flag recorded

レポート
ネットワークセキュリティインテリジェンス
CF Cloudflare Radar Verdict 悪意あり
Phishing New Domains Security threats Phishing Security Risks

証拠の概要

クリティカル
VirusTotal
7/92
OTX
3 community refs
URLScan
Stored capture

Assessment

webs3coinme.lol was listed on the MetaMask blocklist as of 2026-10-09, providing a dated external reference for its status. The domain was also referenced on the SEAL blocklist, and VirusTotal recorded multiple detections for it.

Recorded Evidence

On 2026-10-09, webs3coinme.lol appeared on both the MetaMask and SEAL external blocklists. VirusTotal checked the domain on 2026-10-08, recording 7 detections out of 92 total scanners. OTX referenced webs3coinme.lol in 3 pulses on 2026-10-09. PhishDestroy internally listed the domain on 2026-10-09.

Interpretation

The VirusTotal record contains a measurement of how webs3coinme.lol was detected by several independent scanners, documenting its classification across different security tools. The MetaMask and SEAL blocklist entries provide context by capturing the domain’s presence in external blocklist records. OTX adds further scope by recording the domain’s appearance in multiple collaborative intelligence pulses.

Recommended Actions

For webs3coinme.lol, preserve the VirusTotal, PhishDestroy, and OTX records for future reference and comparison. Use the MetaMask and SEAL blocklist entries to inform ongoing technical reviews. Avoid submitting sensitive information to this domain based on its recorded evidence.

探知・回避の分析

クローキングおよびトラフィック分散の確認

まだスキャンされていません クローラーとブラウザの間に違いは見られていない

このホストに関するクローラーとブラウザの観測データの蓄積に加え、ケイタロ式トラフィック分散システム向けのリアルタイムフィンガープリントチェック。

保存されたクローキングフラグ
まだスキャンされていません
前回のクローキングスキャン

スキャナーに関する注記: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='webs3coinme.lol', port=80): Max retries exceeded with url: / (Caused by NewConnectionError

TDSの指紋認証のライブデモ
このパネルが開いている間、PhishDestroyスキャナーから、7つのケイタロの指紋と、クローラー対ブラウザの比較が実行されます。
待つ

保存済みキャプチャ · 3 captures

ページタイトル
undefined
Impersonates
Telegram
TLS証明書
Hostname coverage not recorded · 発行者 Let's Encrypt / YE1 · stored validity ends in 77 days

Domain details

ドメイン
URLScan Verdict 悪意あり score 100 Phishing report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP の評判はこのドメインに起因しません。
OTX Tags 2026-10activeall-domainsblocklistcontentcryptoドメインdrainerfraudmonthlyphishdestroyphishingscam
レジストラ NameMart SE(SE)
不正利用連絡先abuse@namemart.com
ICANNレジストリICANN Lookup (RDAP) →
登録情報作成日 2026年10月1日 (12d · Very New!) — Expires 2027年10月1日
技術詳細Provenance & timestamps
初確認2026年10月9日
DOM Analysisanalyzed 2026年10月9日score 100/1001 brand signal
Submitted URLhttp://webs3coinme.lol/
Favicon Hash
ケース ID
ICANN OVERSIGHT

認定と RAA の背景

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft 自動送信は一切行われません。

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
104.21.9.4
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

Edge-IP の評判はこのドメインに起因しません。

ネームサーバー 2

  • gloria.ns.cloudflare.com
  • maxim.ns.cloudflare.com

Location describes the IP network.

TLS証明書

Issuer
Let's Encrypt / YE1
Valid from
2026-10-01 07:51:11
Valid until
2026-12-30 07:51:10
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-09 19:02:04 UTC
Collection source
PhishDestroy collector
Certificate fingerprint2ab4c6866115461eac8b8e565afc0ca172ed6680ddd1a6617b568e6df3cbf43d

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 104.21.9.4rapiddns.io

Latest Classified Outcome 2026-10-12 20:20:57 UTC

Primary outcome DNS 非アクティブ reason: DNS NXDOMAIN 80% confidence
Attribution source: Dns Cache
Evidence layers Availability: DNS inactive Content: Unreachable DNS: NXDOMAIN Registration: Unknown
Latest HTTP observation 不明 Probe Inconclusive 20% 2026-10-13 10:42:40 UTC
RDAP registration 不明
Observed timeline last reachable: 2026-10-11 02:17:27 UTC last content: 2026-10-11 02:17:27 UTC current episode first observed: 2026-10-11 20:20:50 UTC observed RIP window: 2026-10-11 02:17:27 UTC → 2026-10-11 20:20:50 UTC · 18.06h midpoint estimate ≈ 2026-10-11 11:19:08 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 5 identified
Detected via Cloudflare Radar · Wappalyzer engine
このドメインを報告する 証拠を提出し、他の人を守る手助けをしましょう

VirusTotalによる分析

7 / 92 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed Previous stored snapshot: 7 detections
CRDF
Emsisoft
Fortinet
カスペルスキー
ネットクラフト
ソフォス
Webroot

アーカイブ済み証拠

Wayback Machine Snapshot
過去のスナップショットは証拠のレビューに利用可能です
View Archive
サイトパフォーマンス分析

Google PageSpeed Insights — mobile performance audit of webs3coinme.lol · checked Oct 9, 2026

78
Needs Work
Performance
FCP
3.08s
First Contentful Paint
LCP
3.36s
Largest Contentful Paint
CLS
0.004
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
10.24s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Threat First Observed 2026-10-09 15:53:51 UTC
    Domain ingestion complete. Initial state is marked as unknown pointing to IP 104.21.9.4.

脅威対応 Pipeline

ディスカバリー
Analysis
Notifications
Monitoring

14 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

脅威の検知
webs3coinme.lol 検出され、詳細な分析のためにキューに入れられた
2026年10月9日
URLScan.io Capture
保存済み URLScan report with capture artifacts
2026年10月9日
URLScan Verdict
URLScan returned a malicious verdict · score 100
2026年10月10日
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in ウェイバック・マシン — historical evidence archived
2026年10月13日
VirusTotal
7/92 recorded on VirusTotal
2026年10月9日
ブロックリストの検出
掲載先 2 blocklists: MetaMask, SEAL
2026年10月13日
OTX Community References
3 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
2026年10月9日
CF Radar: Malicious
Cloudflare Radar classified this domain as phishing, New Domains, Security threats, Phishing, Security Risks
Brand Impersonation
Impersonation of Telegram
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
2026年10月9日
Technical Analysis Recorded
レポートには、保存されたテクノロジーまたはフォレンジック分析の結果が含まれます。
2026年10月13日
Sent Report Recorded
Stored outgoing record associated with registrar NameMart Pte. Ltd., 1 abuse contact
abuse@namemart.com
2026年10月9日
DestroyList 公開
2026年10月9日
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

公開ブロックリスト登録状況

証拠および外部報告書

送信済み証拠のスナップショット
Sent: Ledger records: 1 Case ID: PD-20261009-0DB9E9 Recipient: abuse@namemart.com
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 88.7 KB
PDF notice generated Notice text archived (856 chars)
Abuse notice text as sent to the provider
AUP & Terms of Service Violations:
Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices.
Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension.
Applicable Legal Framework (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
詳細な分析

このサイトによって何か影響を受けましたか?

6 evidence signal groups linked 1 reports recorded 未検証
If credentials were compromised, report immediately. Do not engage with recovery scammers.

アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。

ユーロポール
EU 加盟国の公式報告チャネルを見つける
National police directory
復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →

お住まいの地域の当局へ報告してください

サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。

97か国のディレクトリ

Template-based draft · optional AI wording assistance requires separate consent

AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます · 自分で確認して送信する

任意のドメインを確認する

保存されたブロックリスト、WHOIS、DNS、および公開スキャン証拠を使用した脅威分析

今すぐスキャン

フィッシングを報告する

不審なドメインを当社の脅威データベースに報告してください — コミュニティを守りましょう

レポート

リアルタイム脅威情報フィード

最近のフィッシングレポートと観察された可用性の変化

監視

最新情報を入手し、安全を確保しましょう

リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください
リアルタイム脅威情報フィード この掲載情報について異議を申し立てる
HTML · IFRAME

このレポートを埋め込む

この脅威情報を、ご自身のウェブサイトやブログで共有してください

embed.html
<iframe
  src="https://phishdestroy.io/ja/embed/domain/webs3coinme.lol"
  title="PhishDestroy threat report for webs3coinme.lol"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

