




ドメインのセキュリティと脅威インテリジェンス
piast-kapitura.com
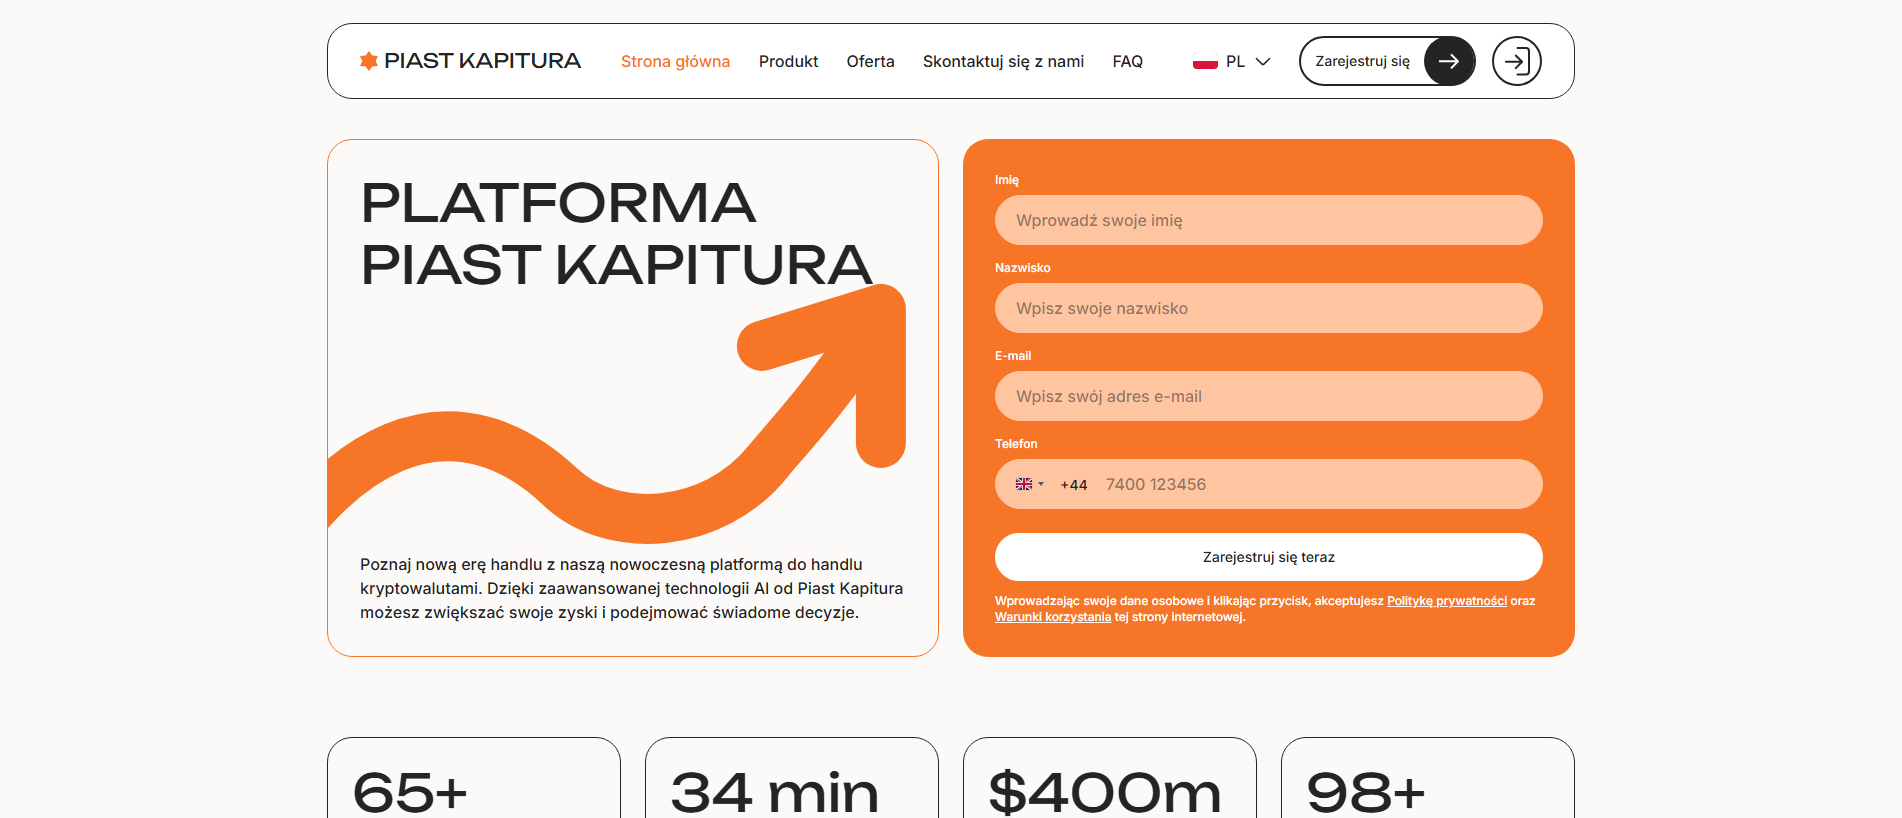
“Platforma Piast Kapitura | Oficjalna strona internetowa”
脅威の評決
クリティカル
100/100 証拠スコア
可用性
最後に確認されたアクティブな状態
最新の保存された到達可能性の観測
リスクシグナル
VirusTotal 検出数: 18/89
Spamhaus DBL: DBL_SPAM
URLQuery threat systems: 5 alerts
ブランドの偽装: Unknown
最後に確認されたアクティブな状態
Actions
API
ABUSE NOTICE · 24H+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@w1n.nl.
The latest stored availability evidence still shows the domain reachable; 2 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
2 days
Reports sent
1
Latest case ID
PD-20260917-8838F6
Current status
HTTP 200 at latest stored check
レポート概要
piast-kapitura.com — 最後に確認されたアクティブな状態 (HTTP 200). ブランドの偽装: Unknown; 詐欺タイプ: Impersonation. 証拠の概要: VirusTotal 18/89 (alphaMountain.ai, BitDefender, CRDF, CyRadar, ESET); URLQuery 5 alerts; URLScan malicious verdict; Spamhaus DBL_SPAM; CF Radar malicious; PhishDestroy score 100/100. レジストラ: NETIM.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
証拠の概要
重要
PhishDestroy first observed piast-kapitura.com on Sep 17, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Platforma Piast Kapitura | Oficjalna strona internetowa”. Page analysis recorded additional brand references to Argent, Ethereum, and PayPal. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).
Positive findings are stored from 5 sources: VirusTotal, Spamhaus DBL, Cloudflare Radar, URLQuery, and URLScan. VirusTotal recorded 18 detections among 89 engines: alphaMountain.ai, BitDefender, CRDF, CyRadar, ESET, Emsisoft, Forcepoint ThreatSeeker, Fortinet, G-Data, Gridinsoft, Kaspersky, Lionic, PREBYTES, Seclookup, SOCRadar, Sophos, VIPRE, Webroot on Sep 19, 2026 at 10:46 UTC. Spamhaus DBL: DBL_SPAM on Sep 17, 2026 at 22:30 UTC. Cloudflare Radar classified the hostname as malicious and placed it in the malware category; its verdict timestamp was not retained. URLQuery recorded 5 threat-system alerts on Sep 17, 2026 at 18:55 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Investmentscam and assigned phishing as its category on Sep 18, 2026 at 03:30 UTC. Non-positive and contextual checks: AlienVault OTX listed 5 community pulse references (not vendor detections) on Sep 19, 2026 at 10:47 UTC. The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 14:20 UTC. Google Safe Browsing returned no flag on Sep 19, 2026 at 10:46 UTC.
HTTP 200 was recorded on Sep 20, 2026 at 10:47 UTC. Registration records for the domain list NETIM as the registrar and Apr 23, 2026 as the creation date. At collection time, the hostname resolved to 91.236.116.217 on AS42237 (w1n ltd). The recorded endpoint location is Stockholm, SE. The stored server header is nginx. DOM analysis on Sep 17, 2026 at 22:20 UTC returned 98/100. The evidence archive retains 4 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YR1 as the certificate issuer with validity through Nov 19, 2026; checked Sep 17, 2026 at 19:02 UTC.
The content indicators and 5 positive source findings support the current Unknown-themed impersonation classification.
VirusTotal
18 det.
URLQuery
5 threat alerts
OTX references
CFレーダー
悪意あり
URLScan
TLS証明書
Let's Encrypt / YR1
年齢
5 mo
観測ステータス
最後に確認されたアクティブな状態 200

DestroyList
掲載あり
Reports Sent
1
データの網羅性
VirusTotal
18 / 89
URLQuery
5 threat-system alerts
OTX
5 community references
CFレーダー
provider verdict: malicious
URLScan capture
保存されたレポート
URLScan verdict
malicious
TLS
valid certificate, 59d
WHOIS
5 mo old
スクリーンショット
4 captures · 3 sources
ネットワークセキュリティインテリジェンス
Threat Detection Systems
5 alerts
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DigiCert UltraDNS | piast-kapitura.com |
malicious | Sinkholed |
| Cloudflare DNS | piast-kapitura.com |
malicious | Sinkholed |
| Quad9 DNS | piast-kapitura.com |
malicious | Sinkholed |
| OpenDNS | piast-kapitura.com |
phishing | Phishing Block |
| DNS4EU | piast-kapitura.com |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Sep 17, 2026 · 20:45 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
91.236.116.217.
脅威対応 Pipeline
ディスカバリー
Checks
Reports
可用性
13/14
Sent Report Recorded
Stored sent-report record for registrar NETIM, hosting provider, 2 abuse contacts
abuse@w1n.nlabuse@netim.net
公開ブロックリスト登録状況
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
- Server header seen by scanner
nginx
Scanner note: alive_content: raw=ok; http=200; via=https_proxy; server=nginx
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
保存済みキャプチャ · 4 sources
ドメイン・インテリジェンス
ドメイン
URLScan Verdict
悪意あり
score 100 Phishing brand: Investmentscam report ↗
サーバー / ASN
nginx · AS42237 w1n ltd
IPレピュテーション
abuse score 0/100 0 reports checked 2026年9月17日
OTX Tags
2026-09activeall-domainsblocklistcontentcryptoドメインdrainerfraudlivemonthlyphishdestroyphishingscam
レジストラ
NETIM
 (PL)
(PL)
登録情報作成日 2026年4月23日 (150d) — Expires 2027年4月23日
HTTPステータス200
技術詳細DNS、SSL SAN、タイムスタンプ
初確認2026年9月17日
DOM Analysis
IoC Extraction
Submitted URLhttp://piast-kapitura.com/
ネームサーバーns1.rt78u9.comns1.wn0vib.comns2.rt78u9.comns2.wn0vib.comns3.pl9vr3.comns3.wn0vib.com
TLS Fingerprint
TLS Observation
TLS SAN Domainswww.piast-kapitura.com
Favicon Hash
ケース ID
使用技術 · 3 identified
Nginx
Web servers
Reverse proxies
Unpkg
CDN
HSTS
セキュリティ
Detected via Cloudflare Radar · Wappalyzer engine
このドメインを報告する
証拠を提出し、他の人を守る手助けをしましょう
VirusTotalによる分析
18 / 89 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed Previous stored snapshot: 18 detections
alphaMountain.ai
BitDefender
CRDF
CyRadar
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
カスペルスキー
Lionic
PREBYTES
Seclookup
SOCRadar
ソフォス
VIPRE
Webroot
サイトパフォーマンス分析
Google PageSpeed Insights — mobile performance audit of piast-kapitura.com · checked Sep 17, 2026
82
Needs Work
Performance
FCP
1.66s
First Contentful Paint
LCP
3.46s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
9.6s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
証拠および外部報告書
証券分析
送信済み証拠のスナップショット
Sent: Ledger records: 1
Case ID:
PD-20260917-8838F6 Recipient: abuse@w1n.nl
PDF notice generated Notice text archived (275 chars)
Abuse notice text as sent to the provider
Registrar: Netim SARL (France)
Policy Violations: “Strict abuse policy classifying phishing, malware, fraud and botnet activity as illegal domain use; registrar may suspend or terminate affected domains.”
Applicable Laws: French Penal Code Art.323-1+; EU Directive 2013/40/EU
OSINTおよび情報分析
DNSとネットワーク
SEOとドメイン
このサイトによって何か影響を受けましたか?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。


PhishDestroy listing review 法執行機関の報告書ではありません
ドメイン異議申立て
このドメインを所有していて、リストが間違っていると思われる場合は、審査をリクエストしてください
復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →
お住まいの地域の当局へ報告してください
サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。
97か国のディレクトリ
AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます
自分で確認して送信する
関連インフラとレポート
Infrastructure map · piast-kapitura.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Shared IP 91.236.116.217 6
この発信元 IP は複数のフィッシング ドメインをホストします。インフラストラクチャはキャンペーン全体で共有される可能性があります。
同じレジストラ: NETIM 6
 xenkrupomia.click
Unknown impersonation 8
These domains also target 不明 users. View all Unknown threats →
最近の脅威レポート 6
PhishDestroy データベースから最近追加されたレポート。これらの検出リンクは、共有インフラストラクチャや所有権を意味するものではありません。
任意のドメインを確認する
保存されたブロックリスト、WHOIS、DNS、および公開スキャン証拠を使用した脅威分析
今すぐスキャンフィッシングを報告する
不審なドメインを当社の脅威データベースに報告してください — コミュニティを守りましょう
レポートリアルタイム脅威情報フィード
最近のフィッシングレポートと観察された可用性の変化
監視最新情報を入手し、安全を確保しましょう
リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください