




ドメインのセキュリティと脅威インテリジェンス

feierverki.com
“Дядя Гриша - Интернет магазин пиротехники в Смоленске, фейерверки - цены, доставка”
脅威の評決
クリティカル
81/100 証拠スコア
可用性
最後に確認されたアクティブな状態
最新の保存された到達可能性の観測
リスクシグナル
VirusTotal 検出数: 2/89
ブランドの偽装: Unknown
最後に確認されたアクティブな状態
Actions
API
レポート概要
feierverki.com — 最後に確認されたアクティブな状態 (HTTP 200). ブランドの偽装: Unknown; 詐欺タイプ: Impersonation. 証拠の概要: VirusTotal 2/89 (alphaMountain.ai, SOCRadar); URLQuery 3 det.; URLScan malicious verdict; PhishDestroy score 81/100. レジストラ: Registrar of Domain Na….
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
証拠の概要
重要
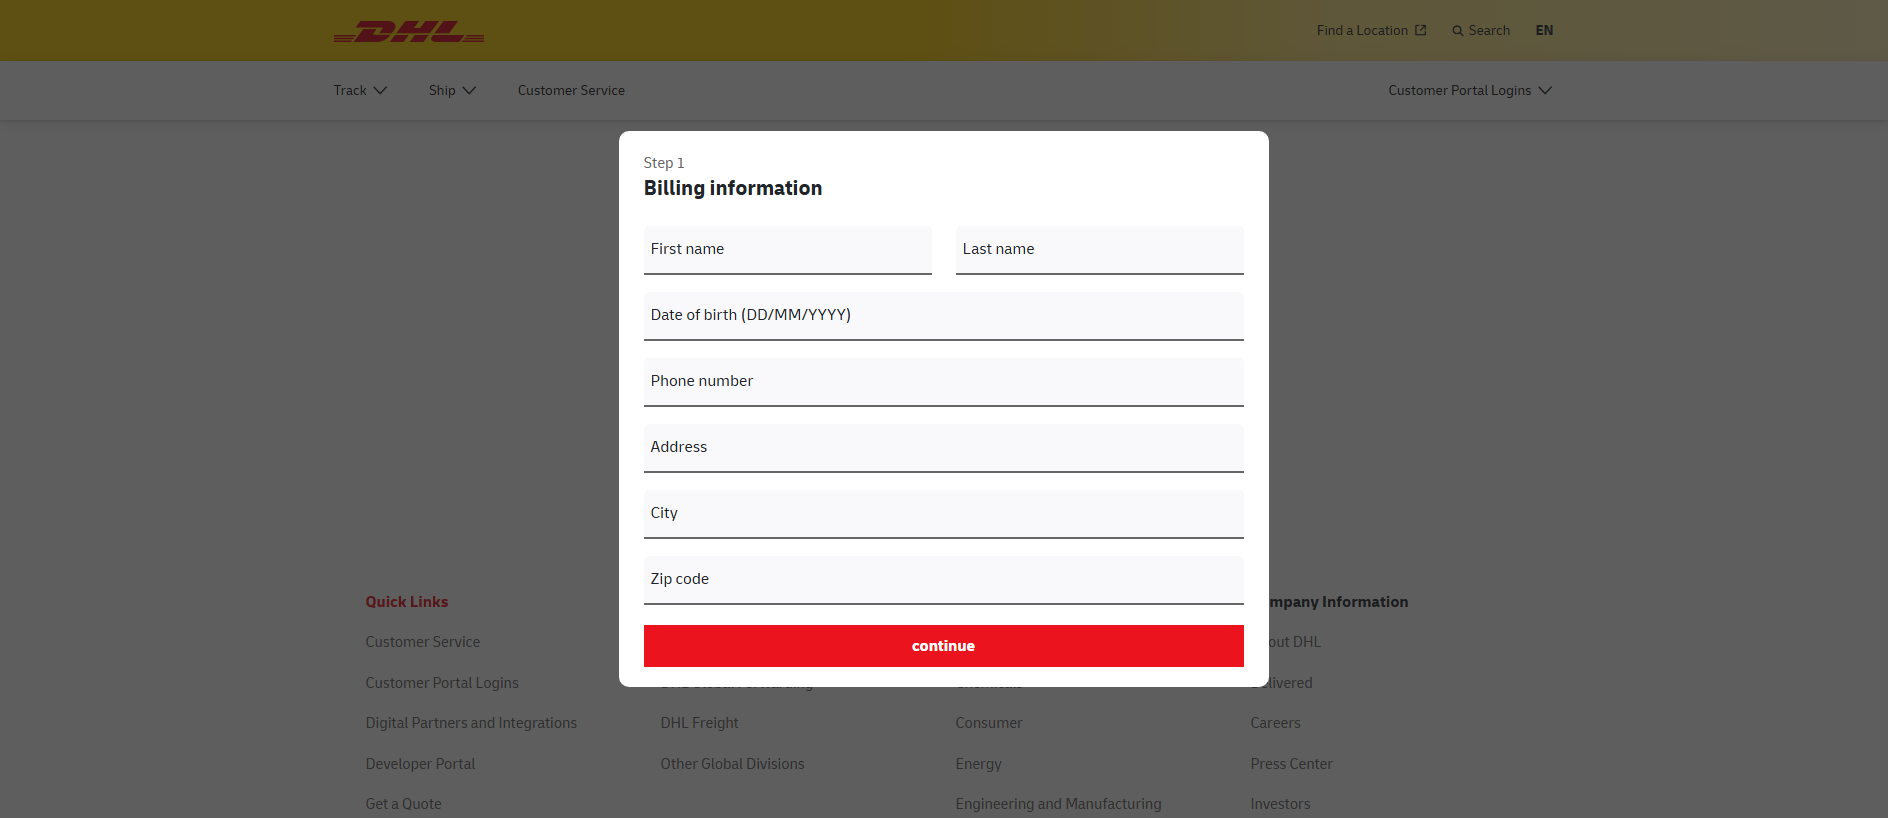
PhishDestroy first observed feierverki.com on Sep 22, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Дядя Гриша - Интернет магазин пиротехники в Смоленске, фейерверки - цены, доставка”. Page analysis recorded additional brand references to Dhl. Stored page analysis classifies the content as impersonation. Current evidence score: 81/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, URLQuery, and URLScan. VirusTotal recorded 2 detections among 89 engines: alphaMountain.ai, SOCRadar on Sep 23, 2026 at 05:22 UTC. URLQuery recorded 3 detections; no observation timestamp was retained. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Dhl and assigned phishing as its category on Sep 23, 2026 at 03:30 UTC. Non-positive and contextual checks: ScamAdviser assigned a trust score of 15/100 (Very Likely Unsafe); no observation timestamp was retained. On Sep 23, 2026 at 05:22 UTC, AlienVault OTX listed 5 community pulse references (not vendor detections); Google Safe Browsing returned no flag. The separate external-blocklist snapshot contained no matches on Sep 23, 2026 at 02:20 UTC.
HTTP 200 was recorded on Sep 22, 2026 at 23:04 UTC. Registration records for the domain list Registrar of Domain Names REG.RU LLC as the registrar and Jan 19, 2010 as the creation date. At collection time, the hostname resolved to 87.236.16.58 on AS198610 (Beget LLC). The recorded endpoint location is St Petersburg, RU. The stored server header is nginx-reuseport/1.21.1. DOM analysis on Sep 22, 2026 at 22:20 UTC returned 81/100. The evidence archive retains 3 visual captures from PhishDestroy and URLScan. TLS metadata lists Let's Encrypt / YR2 as the certificate issuer with validity through Dec 7, 2026; checked Sep 22, 2026 at 22:02 UTC.
The content indicators and 3 positive source findings support the current Unknown-themed impersonation classification.
VirusTotal
2 det.
URLQuery
3 det.
OTX references
URLScan
Scamadviser
15/100Very Likely Unsafe
TLS証明書
Let's Encrypt / YR2
年齢
16.7 yr
観測ステータス
最後に確認されたアクティブな状態 200

DestroyList
掲載あり
Reports Sent
1
データの網羅性
VirusTotal
2 / 89
URLQuery
3 det.
OTX
5 community references
CFレーダー
scan completed
URLScan capture
保存されたレポート
URLScan verdict
malicious
TLS
valid certificate, 75d
WHOIS
203 mo old
スクリーンショット
3 captures · 2 sources
Scamadviser
15/100
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
Threat First Observed Sep 22, 2026 · 22:37 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
87.236.16.58.
脅威対応 Pipeline
ディスカバリー
Checks
Reports
可用性
12/13
Sent Report Recorded
Stored sent-report record for registrar Registrar of Domain Names REG.RU LLC, hosting provider, 3 abuse contacts
feierverki.com@regprivate.ruabuse@beget.ruabuse@reg.ru
公開ブロックリスト登録状況
探知・回避の分析
クローキングおよびトラフィック分散の確認
まだスキャンされていません
クローラーとブラウザの間に違いは見られていない
このホストに関するクローラーとブラウザの観測データの蓄積に加え、ケイタロ式トラフィック分散システム向けのリアルタイムフィンガープリントチェック。
- 保存されたクローキングフラグ
- まだスキャンされていません
- 前回のクローキングスキャン
- スキャナーが検知したサーバーヘッダー
nginx-reuseport/1.21.1
スキャナーに関する注記: alive_content: raw=ok; http=200; via=https_proxy; server=nginx-reuseport/1.21.1
TDSの指紋認証のライブデモ
このパネルが開いている間、PhishDestroyスキャナーから、7つのケイタロの指紋と、クローラー対ブラウザの比較が実行されます。
待つ
保存済みキャプチャ · 3 sources
ドメイン・インテリジェンス
ドメイン
URLScan Verdict
悪意あり
score 100 Phishing brand: Dhl report ↗
サーバー / ASN
nginx-reuseport/1.21.1 · AS198610 Beget LLC
IPレピュテーション
abuse score 0/100 0 reports checked 2026年9月23日
OTX Tags
2026-09activeall-domainsblocklistcontentcryptodhldomainドメインdrainerfraudlivemonthlyphishdestroy+4 more
レジストラ
Registrar of Domain Na…
(PERSONAL DATA, CAN NOT BE PUBLICLY DISCLOSED ACCORDING TO APPLICABLE LAWS.)
IPアドレス
87.236.16.58

登録情報作成日 2010年1月19日 — Expires 2030年1月19日
HTTPステータス200
技術詳細DNS、SSL SAN、タイムスタンプ
初確認2026年9月22日
DOM Analysis
IoC Extraction
Submitted URLhttp://feierverki.com/wp-includes/fonts/css/v2/images/css/2026/js/details.php?… query redacted
ネームサーバーns1.beget.comns1.beget.prons1.beget.runs2.beget.comns2.beget.prons2.beget.ru
MX Records10 mx1.beget.ru 20 mx2.beget.ru
TLS Fingerprint
TLS Observation
TLS SAN Domainswww.feierverki.com
Favicon Hash
ケース ID
使用技術 · 12 identified
WordPress
CMS
Blogs
MySQL
Databases
PHP
Programming languages
particles.js
JavaScript graphics
Yoast SEO
SEO
WordPress plugins
Nginx
Web servers
Reverse proxies
Yandex.Metrika
Analytics
OWL Carousel
JavaScript libraries
jQuery Migrate
JavaScript libraries
jQuery
JavaScript libraries
Font Awesome
Font scripts
Facebook Pixel
Analytics
Detected via Cloudflare Radar · Wappalyzer engine
このドメインを報告する
証拠を提出し、他の人を守る手助けをしましょう
VirusTotalによる分析
2 / 89 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed Previous stored snapshot: 2 detections
alphaMountain.ai
SOCRadar
サイトパフォーマンス分析
Google PageSpeed Insights — mobile performance audit of feierverki.com · checked Sep 22, 2026
53
Needs Work
Performance
FCP
4.96s
First Contentful Paint
LCP
12.53s
Largest Contentful Paint
CLS
0.042
Cumulative Layout Shift
TBT
227ms
Total Blocking Time
SI
9.19s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
証拠および外部報告書
証券分析
送信済み証拠のスナップショット
Sent: Ledger records: 1
Case ID:
PD-20260922-2D8C6B Recipient: abuse@beget.ru Page title stored with report: DHL
PDF notice generated Notice text archived (324 chars)
Abuse notice text as sent to the provider
Registrar: REG.RU (Russia)
Policy Violations: Abuse policy + ICANN contractual obligations; phishing classified as bad-faith use in UDRP; domains may be suspended/removed
Applicable Laws: Criminal Code RF Art.159 (fraud), Art.272 (illegal access), Art.273 (malware creation), Art.274.1 (critical infrastructure interference)
OSINTおよび情報分析
DNSとネットワーク
SEOとドメイン
このサイトによって何か影響を受けましたか?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。

PhishDestroy listing review 法執行機関の報告書ではありません
ドメイン異議申立て
このドメインを所有していて、リストが間違っていると思われる場合は、審査をリクエストしてください
復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →
お住まいの地域の当局へ報告してください
サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。
97か国のディレクトリ
AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます
自分で確認して送信する
関連インフラとレポート
- 直接リンク 登録情報や、同一のフィッシングキットを共有する。
- 補助信号 インフラや対象ブランドを共有しているだけであり、単一の運営者である証拠にはならない。
- 「ディスカバリー」のみ ナビゲーション用にリストされています。このホストとは共通の属性はありません。
各レーンは、ドメインがこのホストにリンクされている理由の1つを示しています。ノードのサイズは「VirusTotal」の検出件数を表しており、破線のノードはすでにオフラインになっています。完全なリストは以下の通りです。
Unknown なりすまし 8
これらのドメインは、Unknownのユーザーも標的にしています。 「Unknown」に関連するすべての脅威を表示する →
同じレジストラ: Registrar of Domain Na… 6
同じレジストラを通じて登録されています。レジストラは、互いに関係のない何百万もの顧客に対応しているため、この事実は関連性を証明するものではなく、単に報告をまとめているに過ぎません。
最近の脅威レポート 6
PhishDestroy データベースから最近追加されたレポート。これらの検出リンクは、共有インフラストラクチャや所有権を意味するものではありません。


任意のドメインを確認する
保存されたブロックリスト、WHOIS、DNS、および公開スキャン証拠を使用した脅威分析
今すぐスキャンフィッシングを報告する
不審なドメインを当社の脅威データベースに報告してください — コミュニティを守りましょう
レポートリアルタイム脅威情報フィード
最近のフィッシングレポートと観察された可用性の変化
監視最新情報を入手し、安全を確保しましょう
リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください