
追跡対象のドメインを検索し、保存されている証拠、検知結果、および最新の稼働状況を確認します。
How This Attack Works
Fake Token Presale scams trick victims into believing they are investing in legitimate cryptocurrency projects. Here's how the scam typically unfolds:
STEP 1
Create Fake Websites
Scammers set up realistic-looking websites mimicking legitimate token presale portals.
STEP 2
Promote Presale on Social Media
Using social media and fake endorsements, scammers attract potential investors.
STEP 3
Collect Cryptocurrency
Victims are prompted to send cryptocurrency to a specified address under the guise of buying tokens.
STEP 4
Disappear with Funds
Once funds are collected, scammers shut down the site and disappear, leaving victims without recourse.
Technical Analysis
Fake Token Presale scams often leverage phishing tactics combined with cryptocurrency-specific techniques. Attackers use homograph attacks to create URLs that closely resemble legitimate sites, often registered through top registrars like NICENIC INTERNATIONAL GROUP CO., LIMITED and PDR Ltd. d/b/a PublicDomainRegistry.com. They exploit the decentralized nature of blockchain networks, utilizing smart contracts that mimic legitimate presale contracts but are programmed to divert funds to the attacker’s wallet. The infrastructure often involves cloud-based hosting services to quickly deploy and dismantle sites, minimizing the chance of detection. HTML and JavaScript are commonly used to create dynamic, convincing interfaces that reassure potential victims of the site’s legitimacy. Additionally, attackers might deploy SEO techniques to improve the visibility of their fraudulent sites in search engine results, further increasing their reach.
Real Cases
CryptoX Presale Scam (2024)
$2 million stolen
A fake presale for a non-existent token, CryptoX, duped investors into contributing significant sums.
TokenLaunch Fraud (2023)
$1.5 million stolen
Victims were lured into a fake token launch with promises of high returns, only for the site to vanish post-collection.
QuickCoin Deception (2024)
$3 million stolen
Scammers created a sophisticated site mimicking a known exchange, leading to substantial financial losses.
How to Detect
確認 for slight misspellings in domain names.
Look for inconsistent branding or layout compared to legitimate sites.
Be wary of unsolicited investment opportunities via social media.
Verify presale details on official project channels.
Beware of high-pressure tactics urging immediate investment.
How to Protect Yourself
1
Always verify URLs before entering personal information.
2
Use browser extensions to detect phishing attempts.
3
Consult official project websites or channels for presale information.
4
Enable two-factor authentication on cryptocurrency exchanges.
5
レポート suspicious sites to authorities and platforms like PhishDestroy.
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 689 domains tracked for this threat type
Fake Token Presale 689 domains

inqubeta-ai-xy.pages.dev
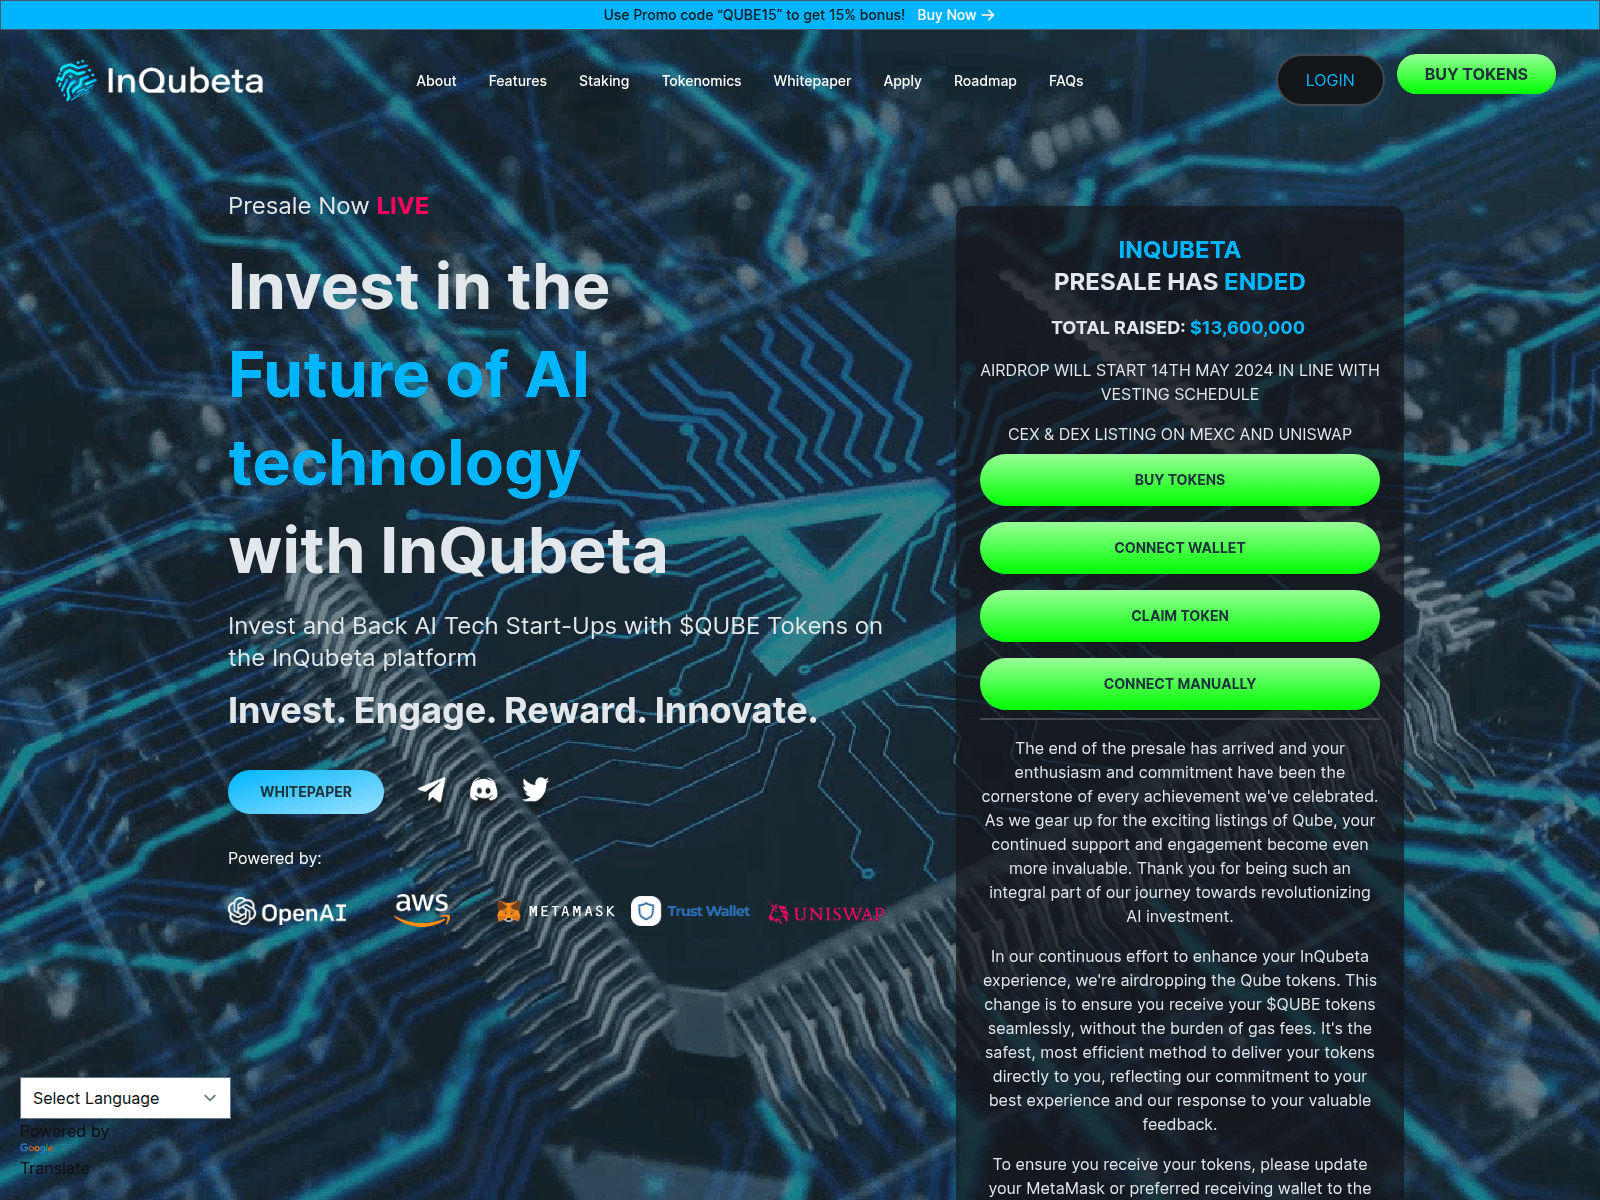
inqubeta-im.pages.dev

inqubeta-in.pages.dev

ionixchain.co
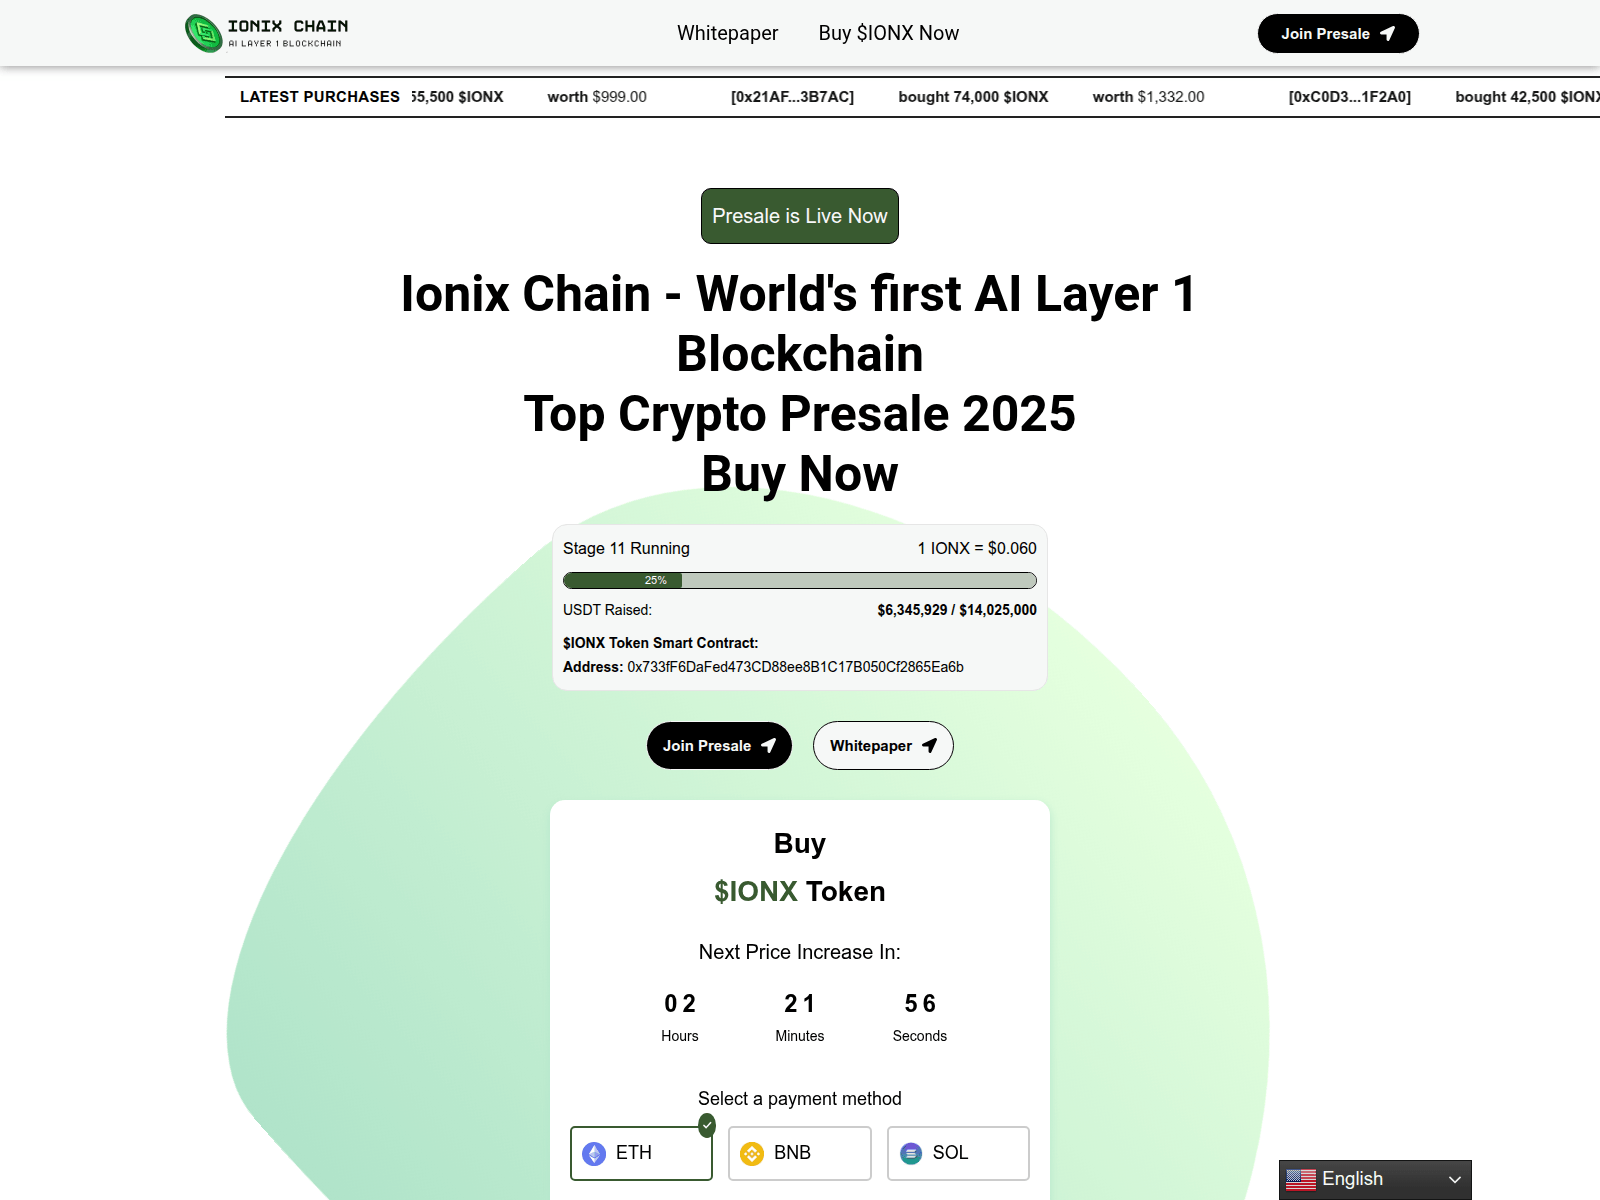
ionixchqin.com
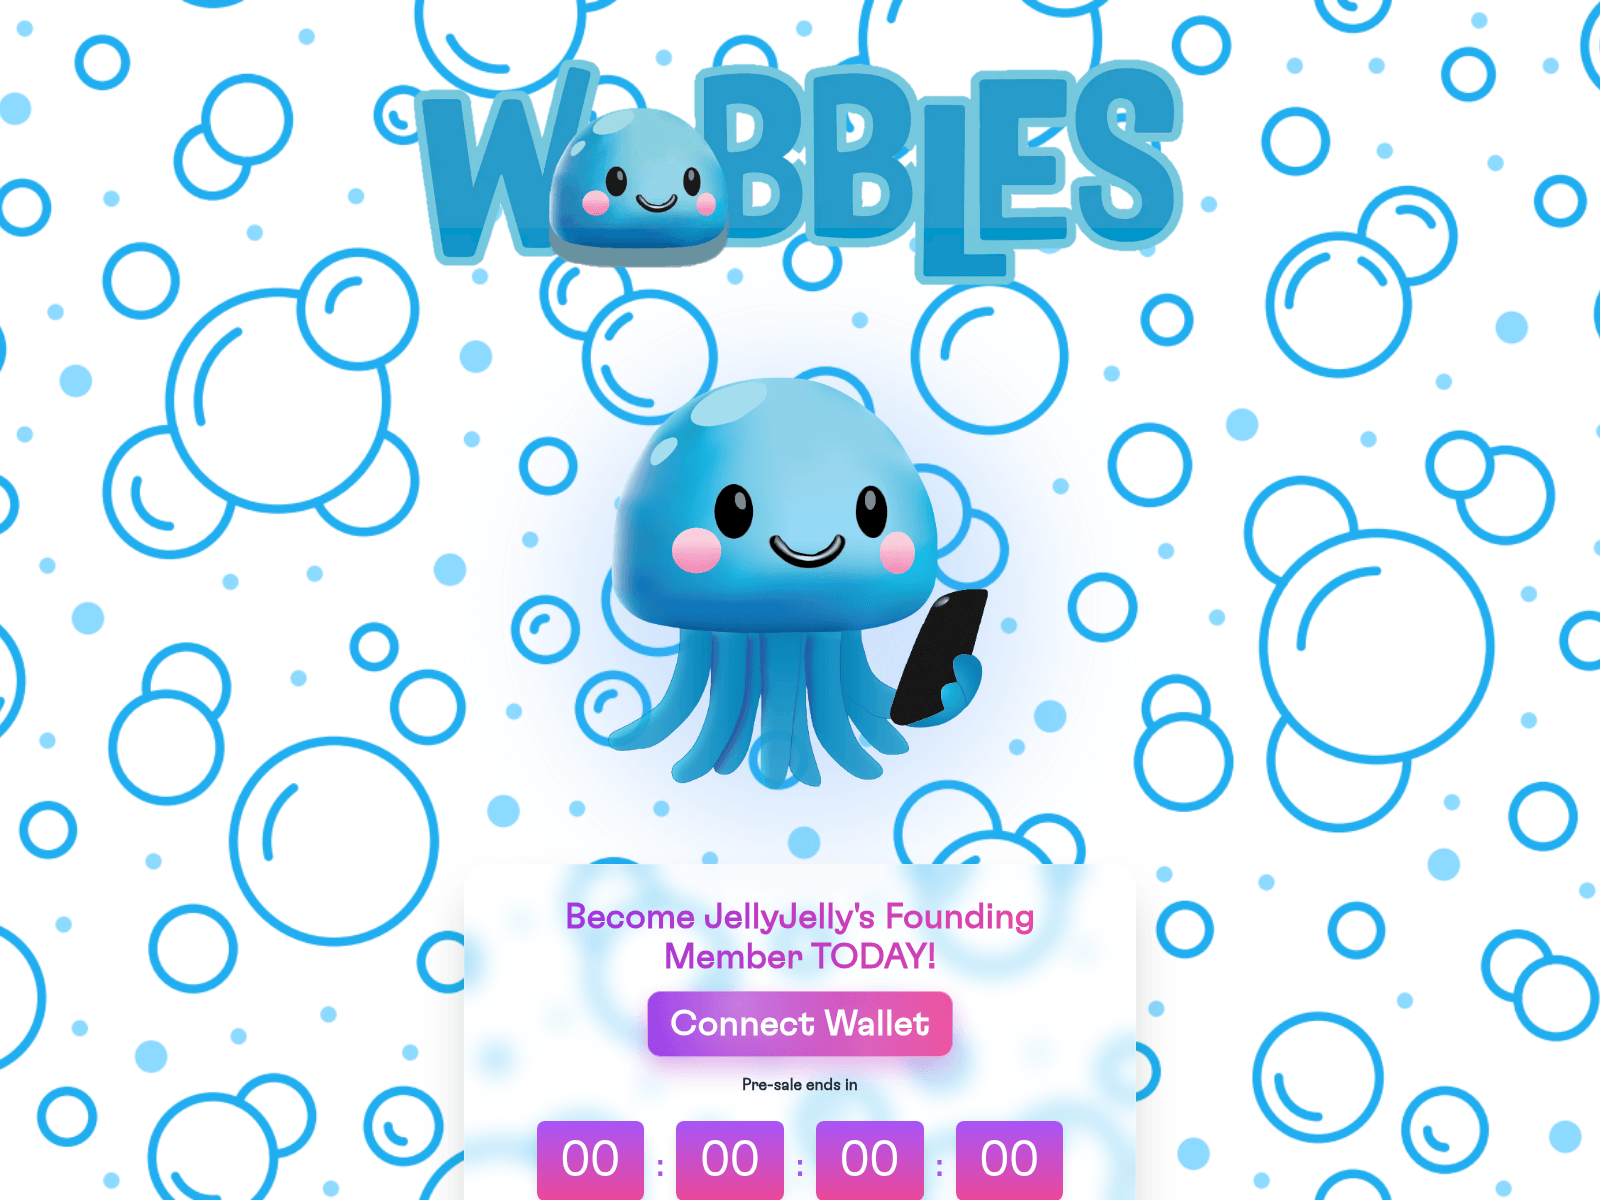
jellyjelly-wobbles.com

jesse-presale-8r8.pages.dev
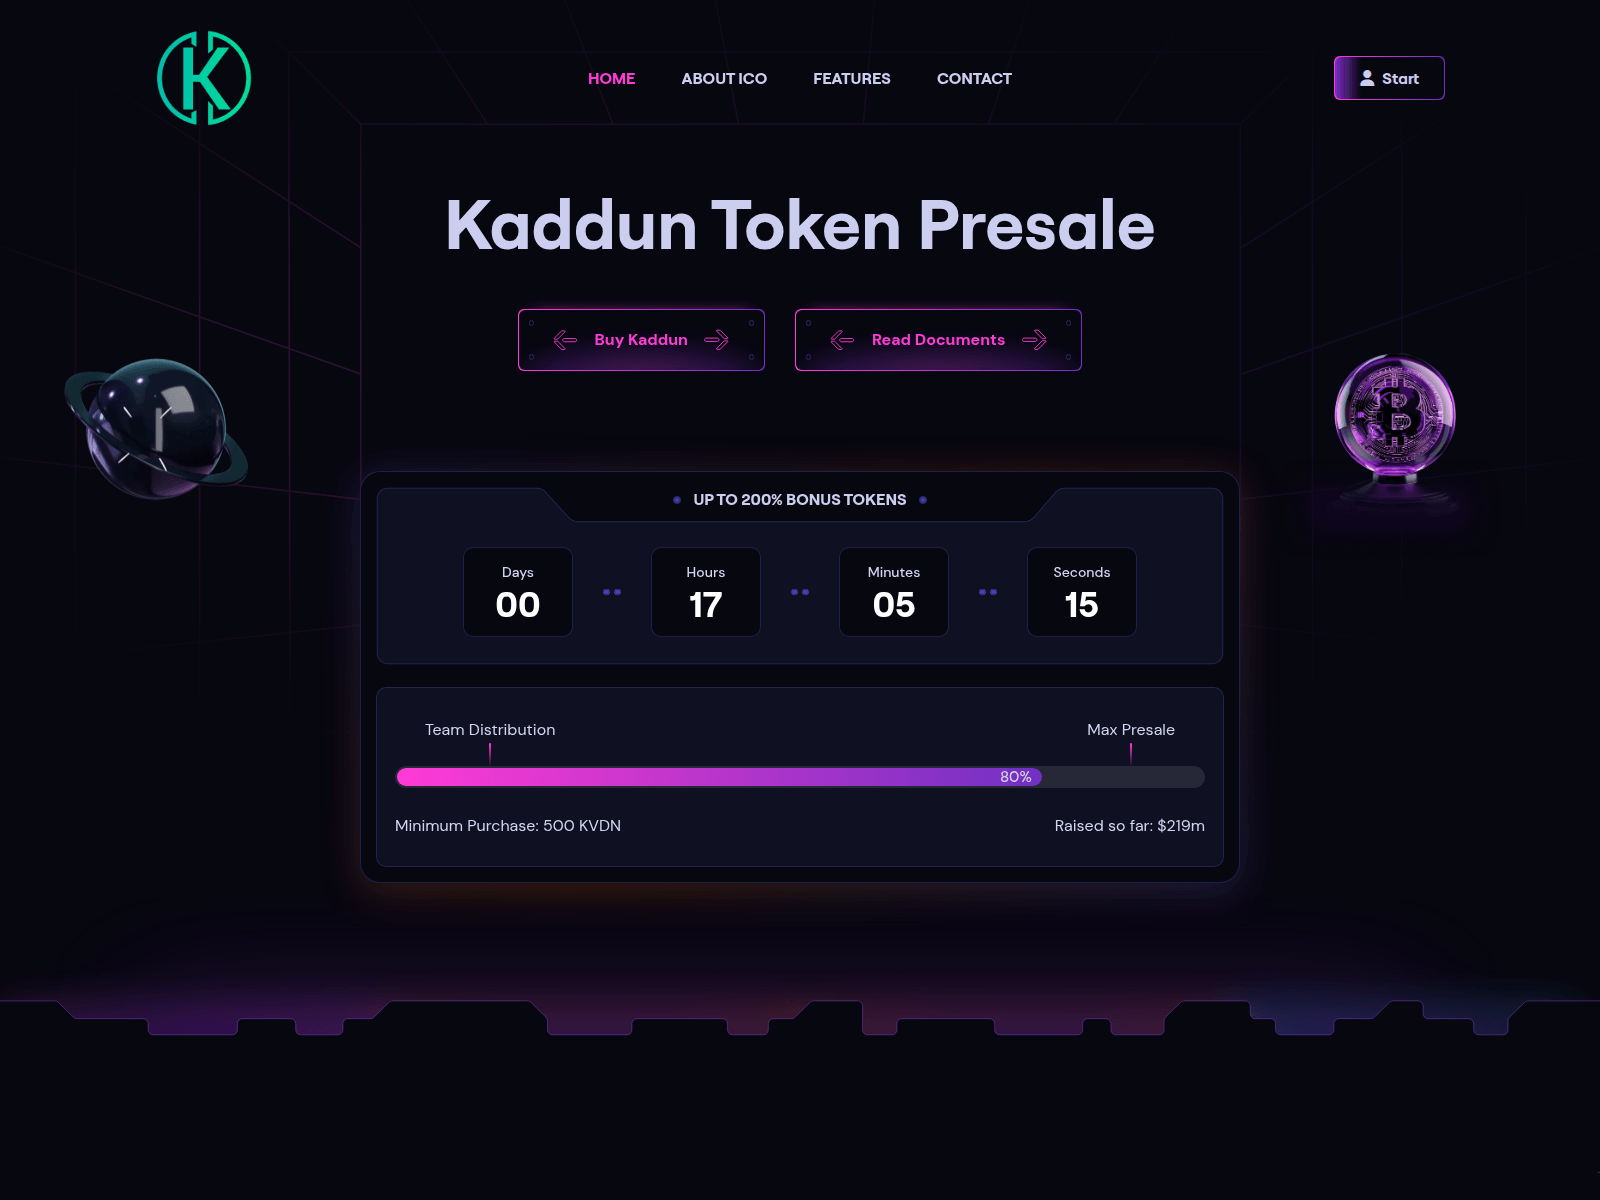
kaddunproject.com

litlpeppe.com
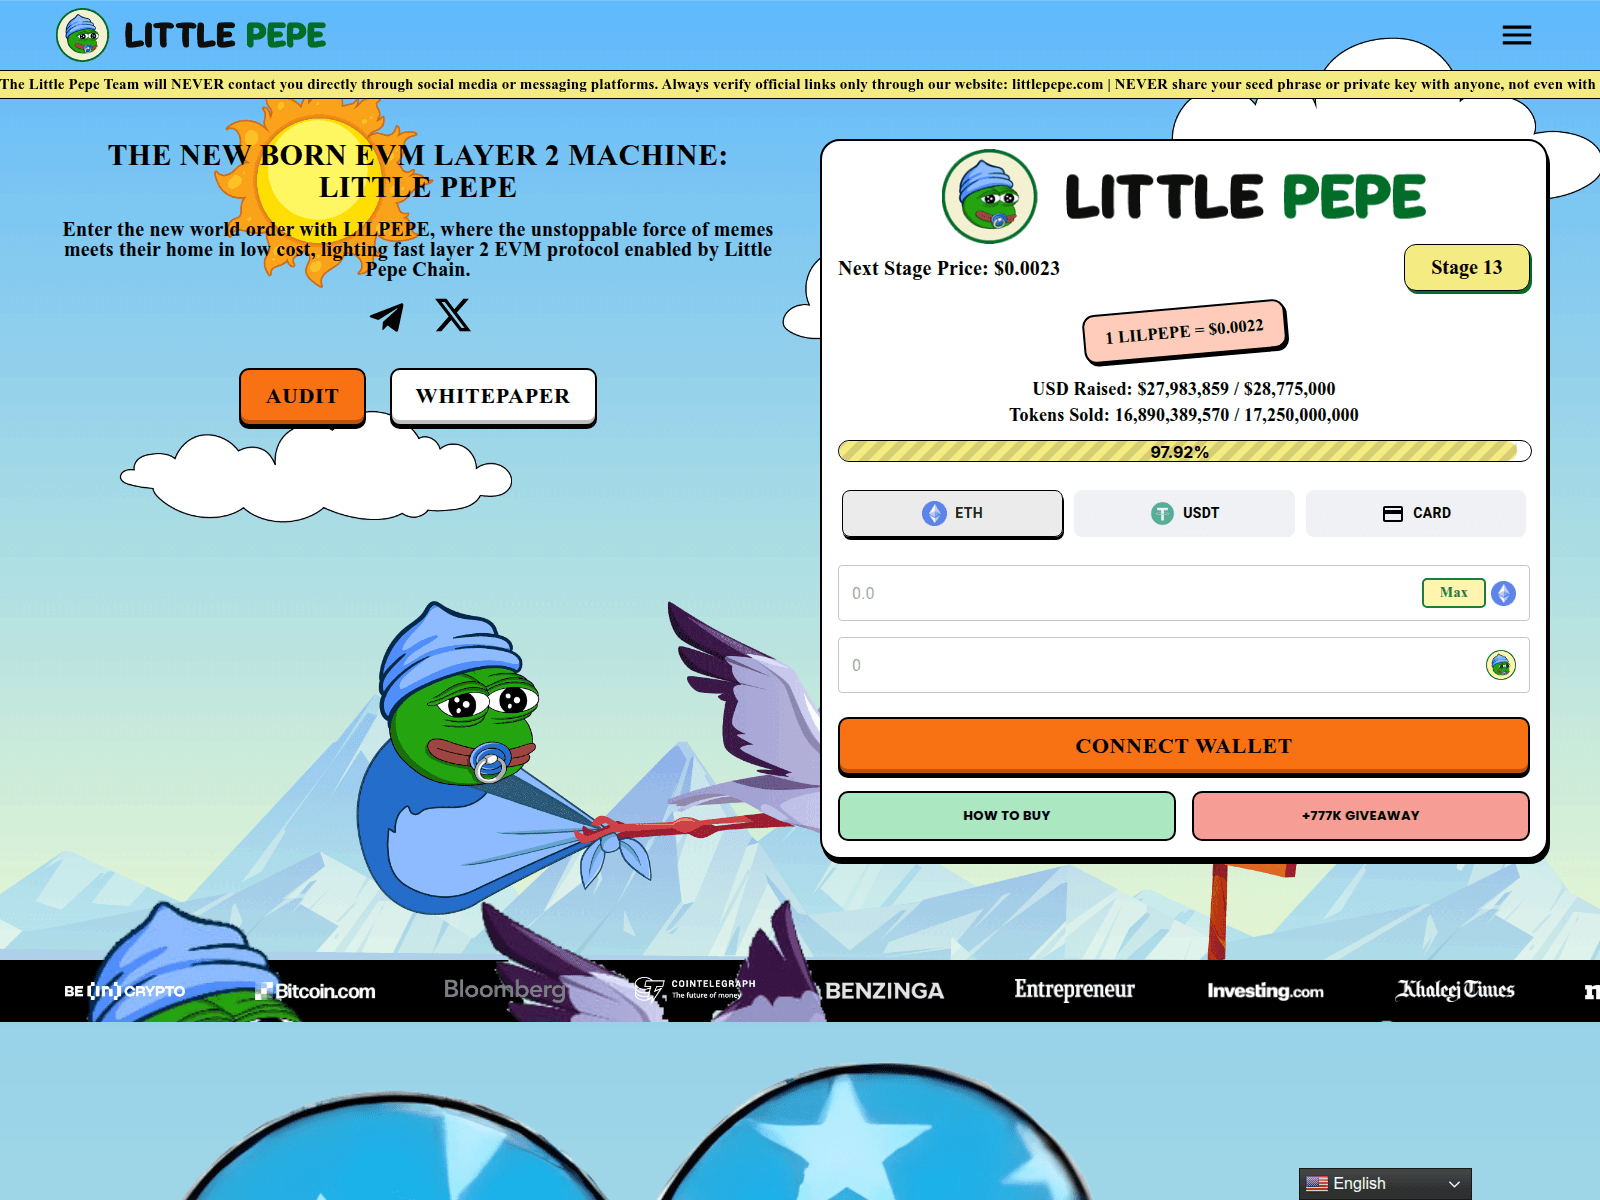
littlepeepe.pages.dev
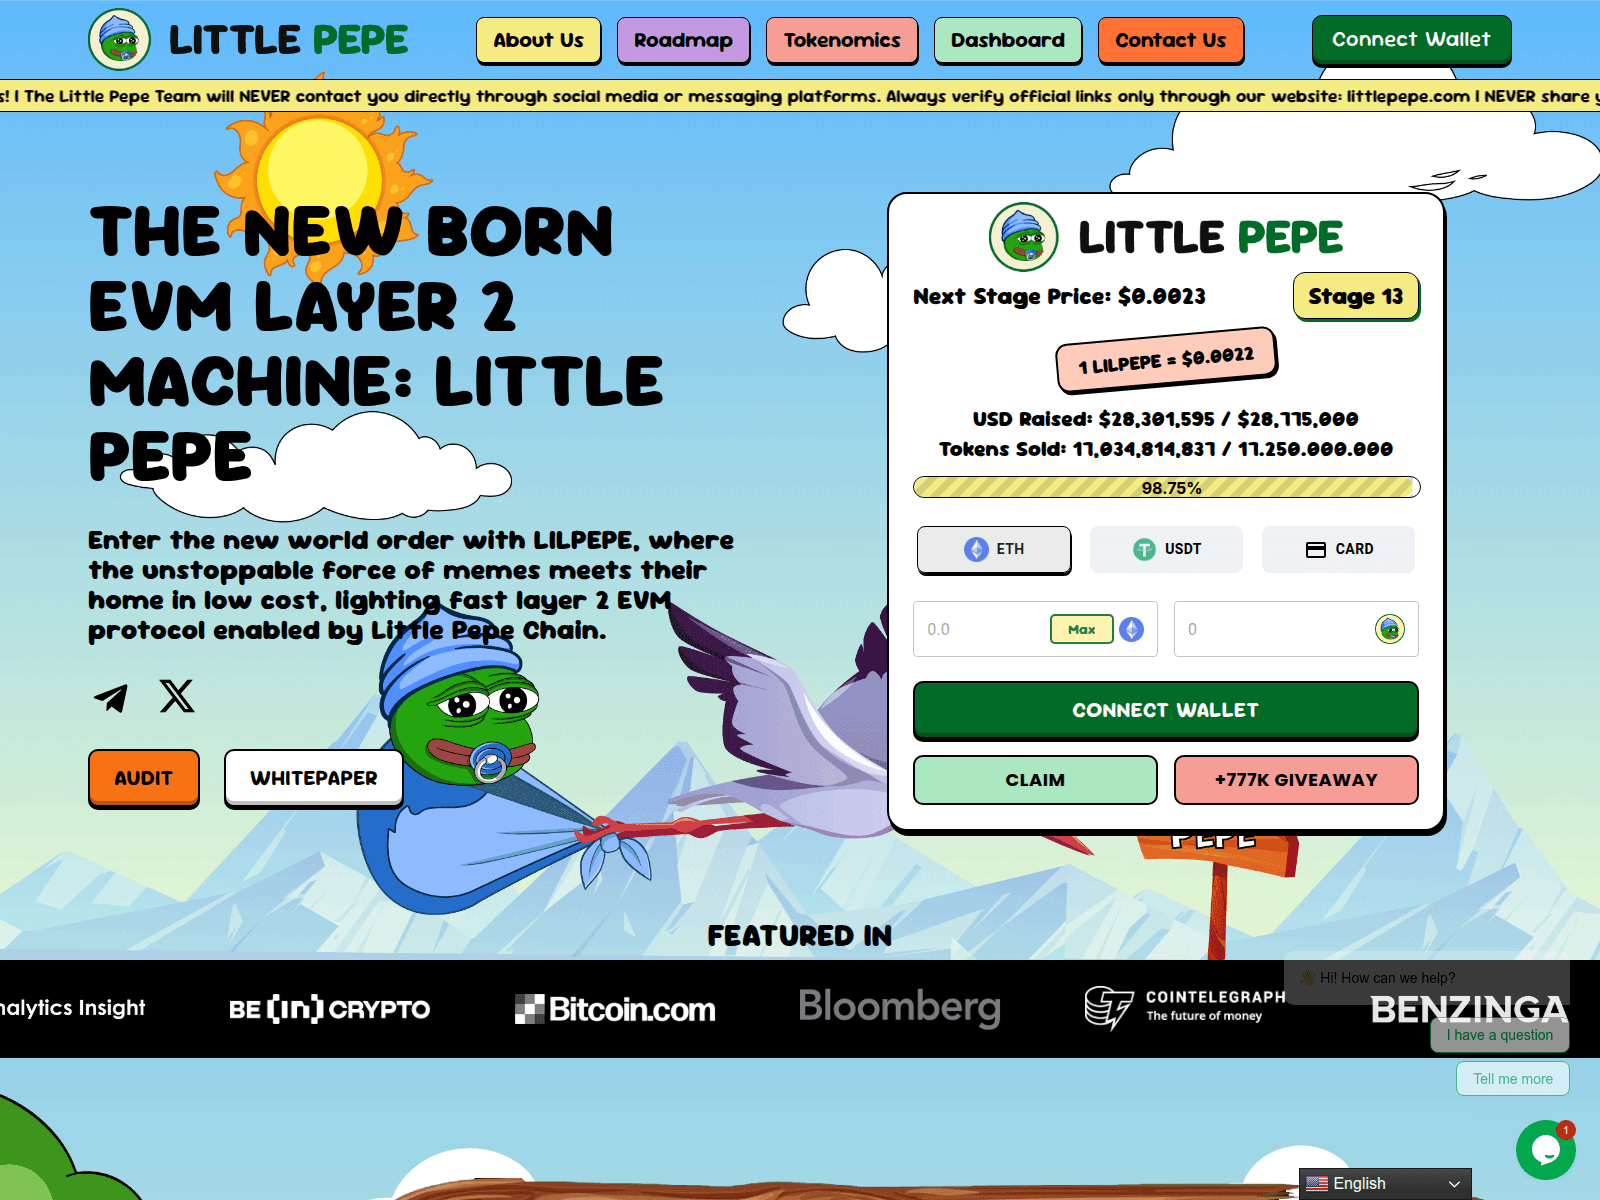
littlepepelive.pages.dev

llttlepepe.com

lttllepepe.com
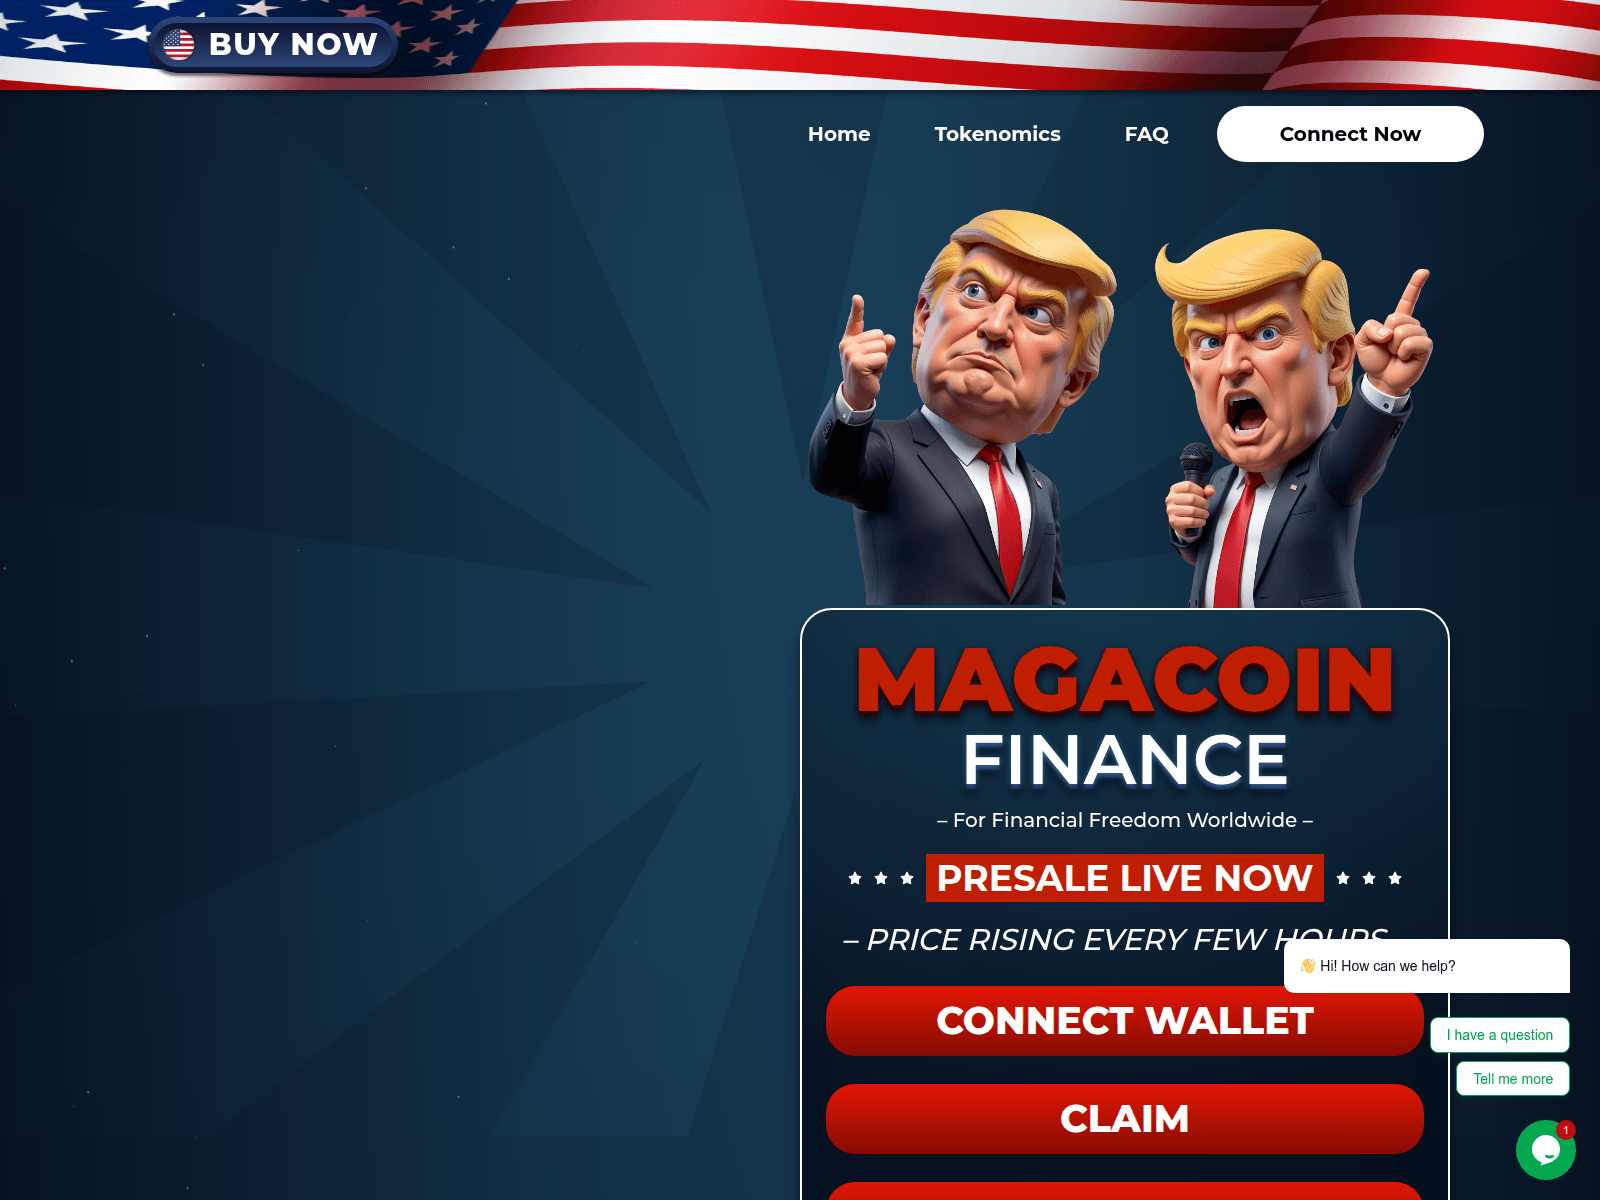
magacoinfinance.com

magacoinofficial.pages.dev
mrbob.io
ne-xchain.live

nexchain.exchange

nlp1rbp.pages.dev

nxuqmp.pages.dev
openeden.sale

pepeascension.info
pepeoftherings.io

perenapresale.xyz

phoenicvesting.com

pomerdoge-ai.pages.dev

presale-cambria.live
presalefarm.pages.dev
presales-jessepollak.pages.dev

qubetics-hubs.pages.dev
qubetics-sale.pages.dev
qubeticsrpc.pages.dev
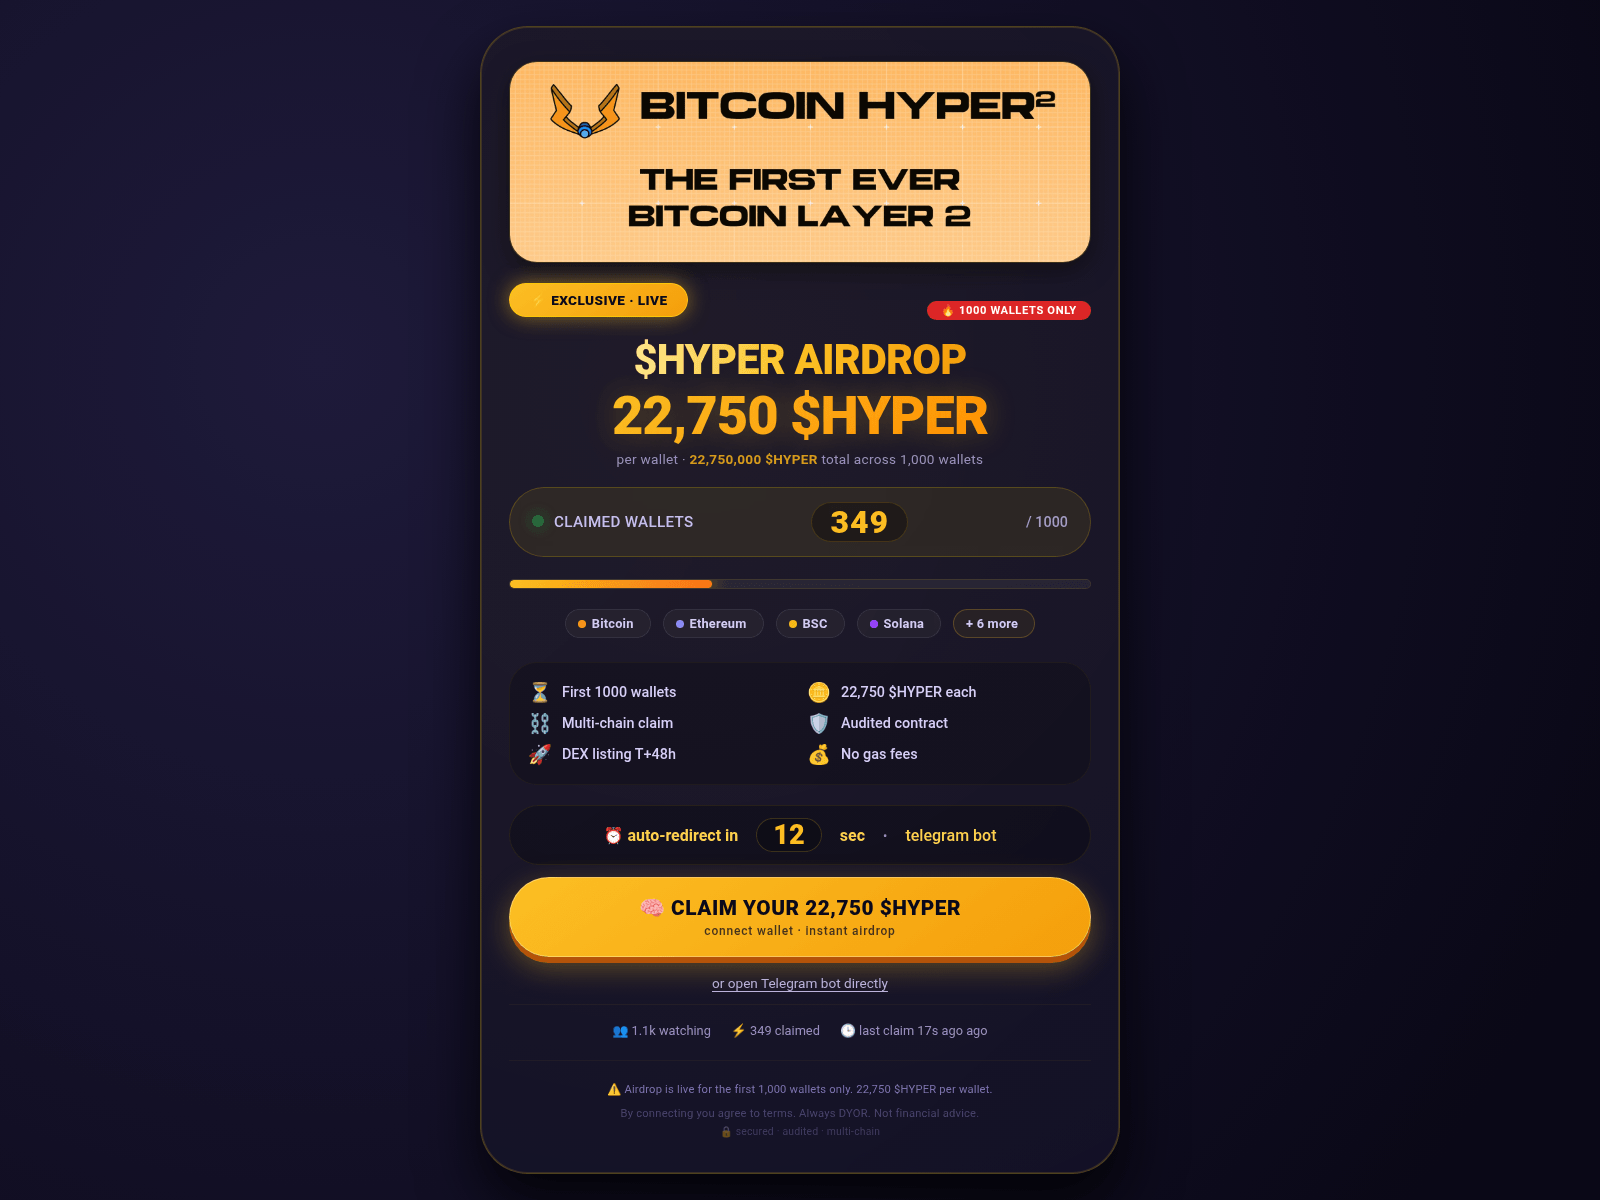
riveranetworks.com

ruviai.info
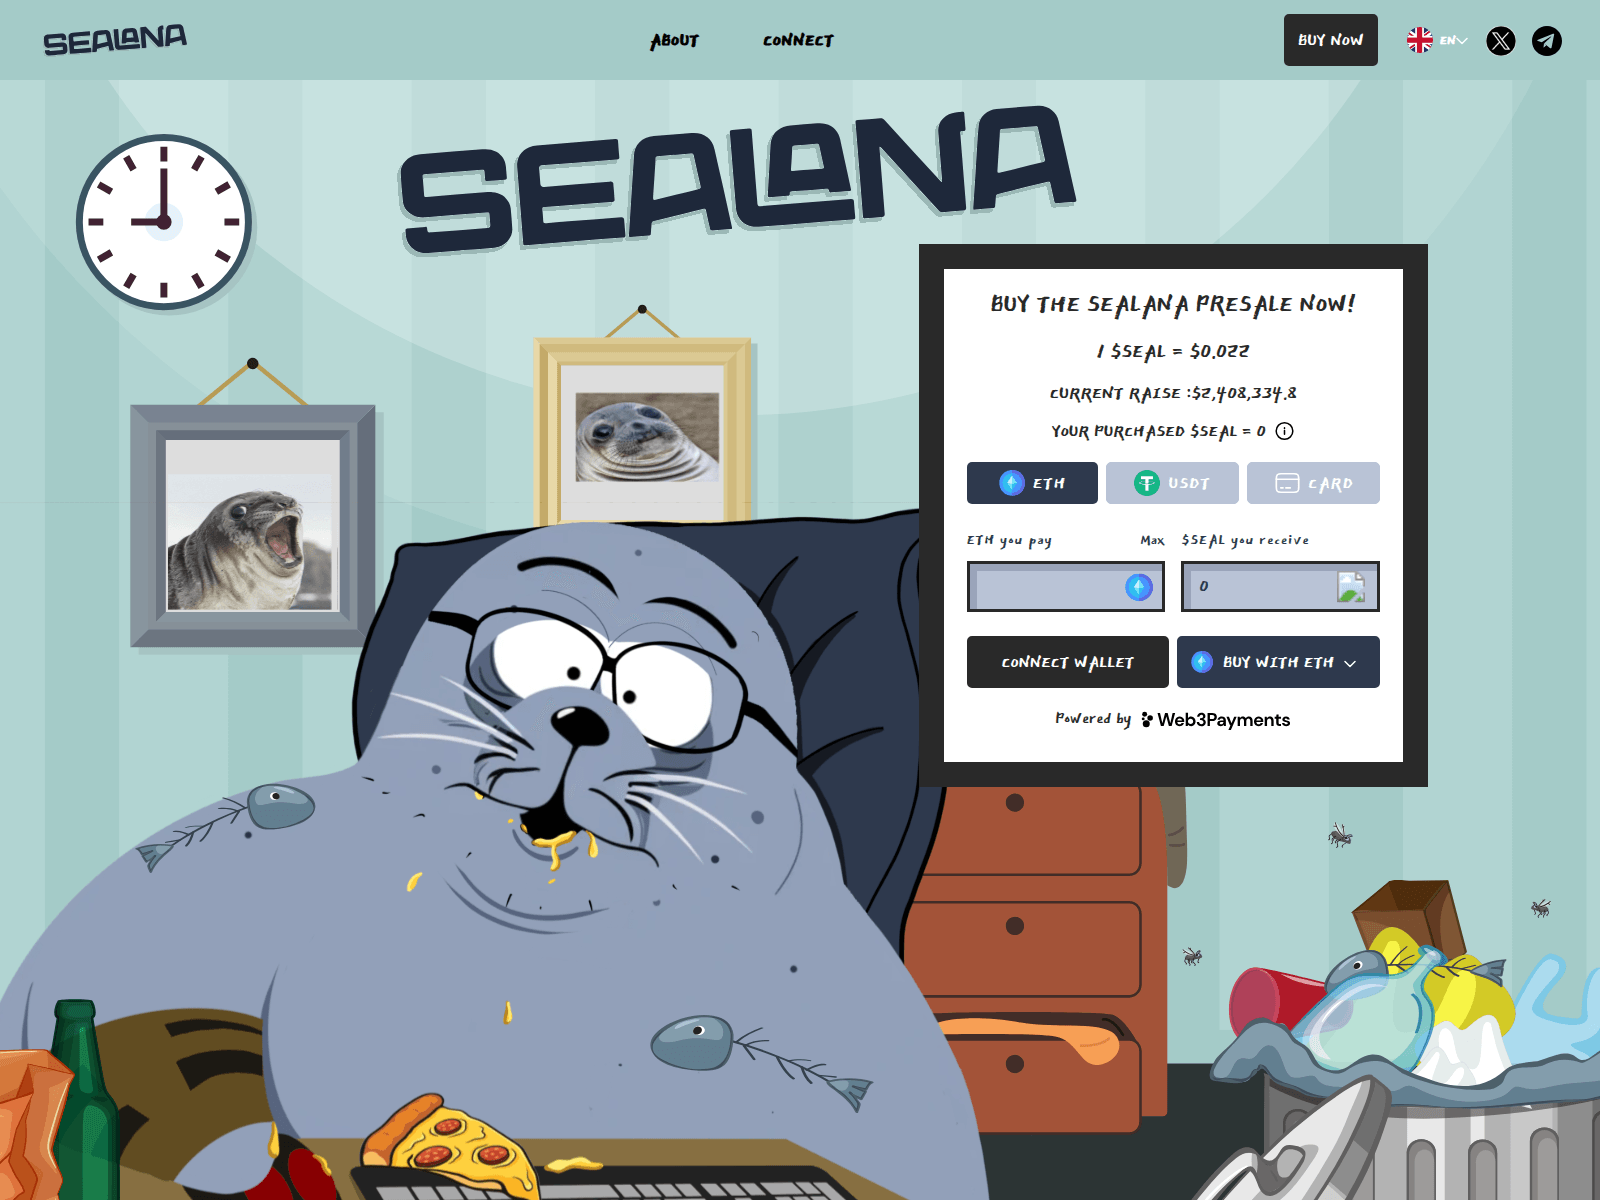
sealana-presale.pages.dev

sealanaio.pages.dev
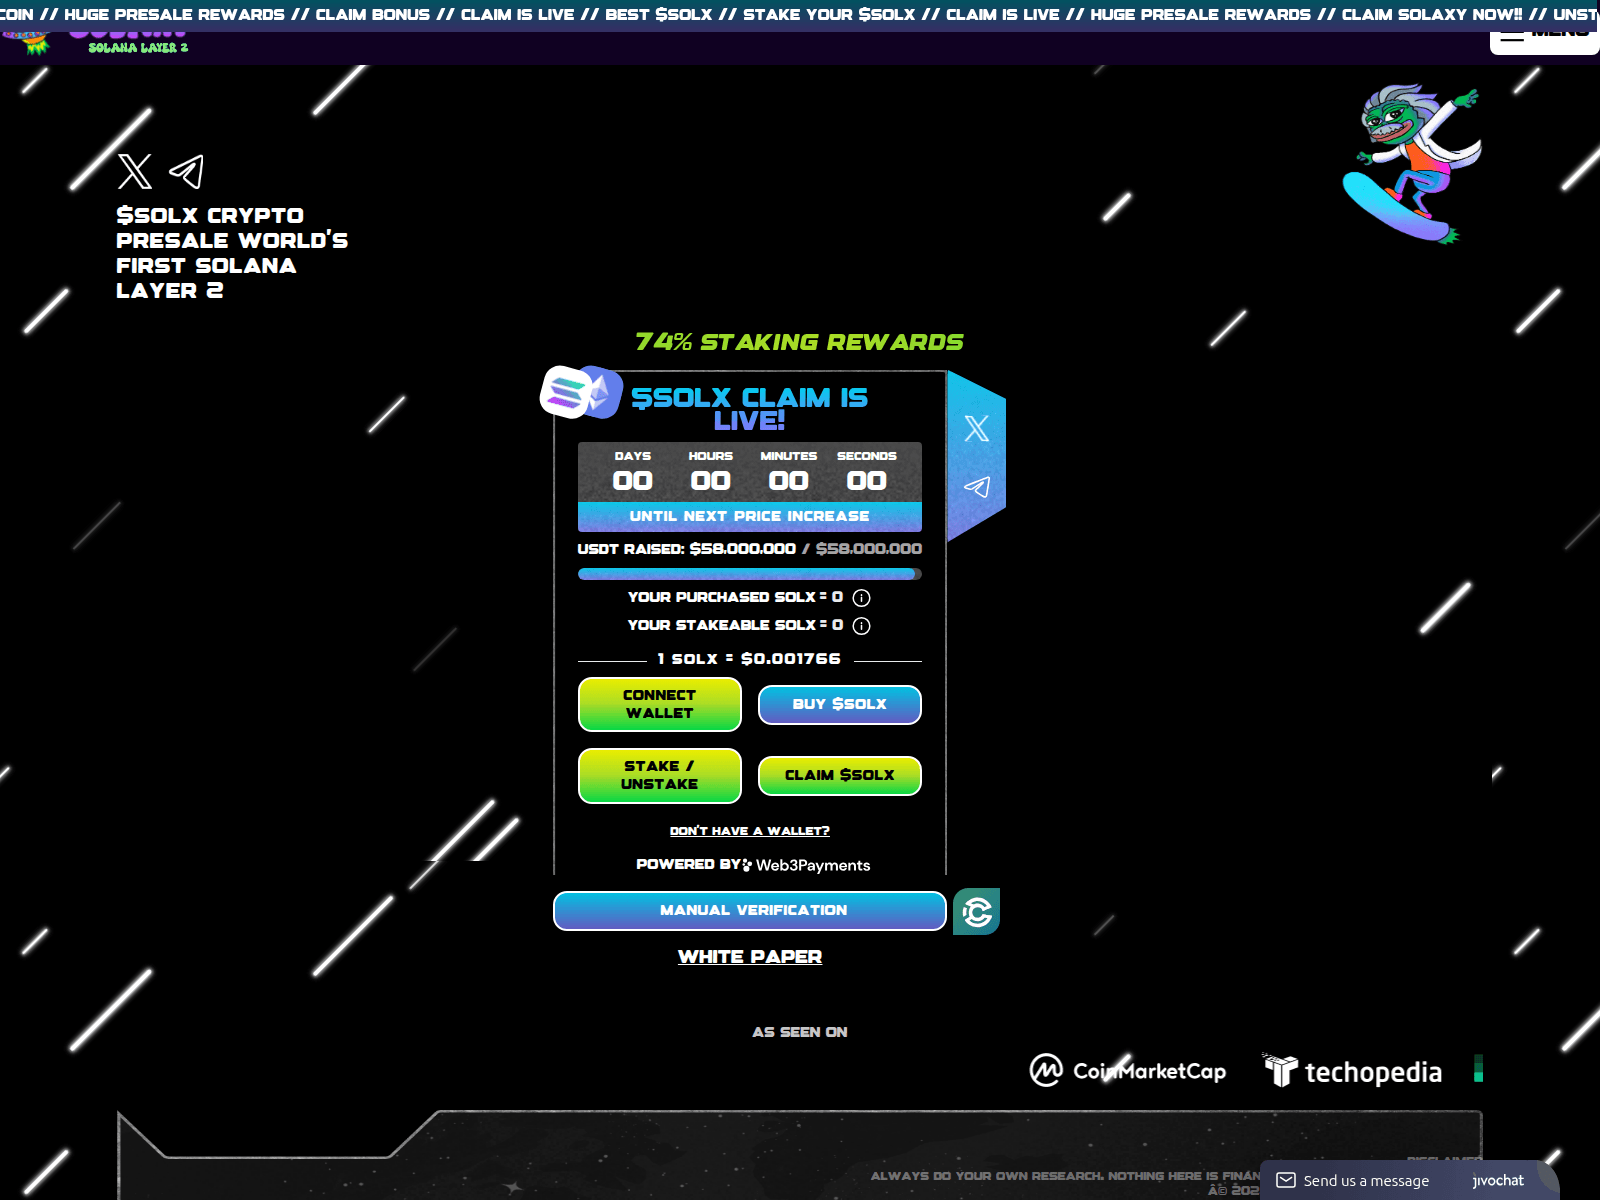
solxscan.xyz

spax24k.com
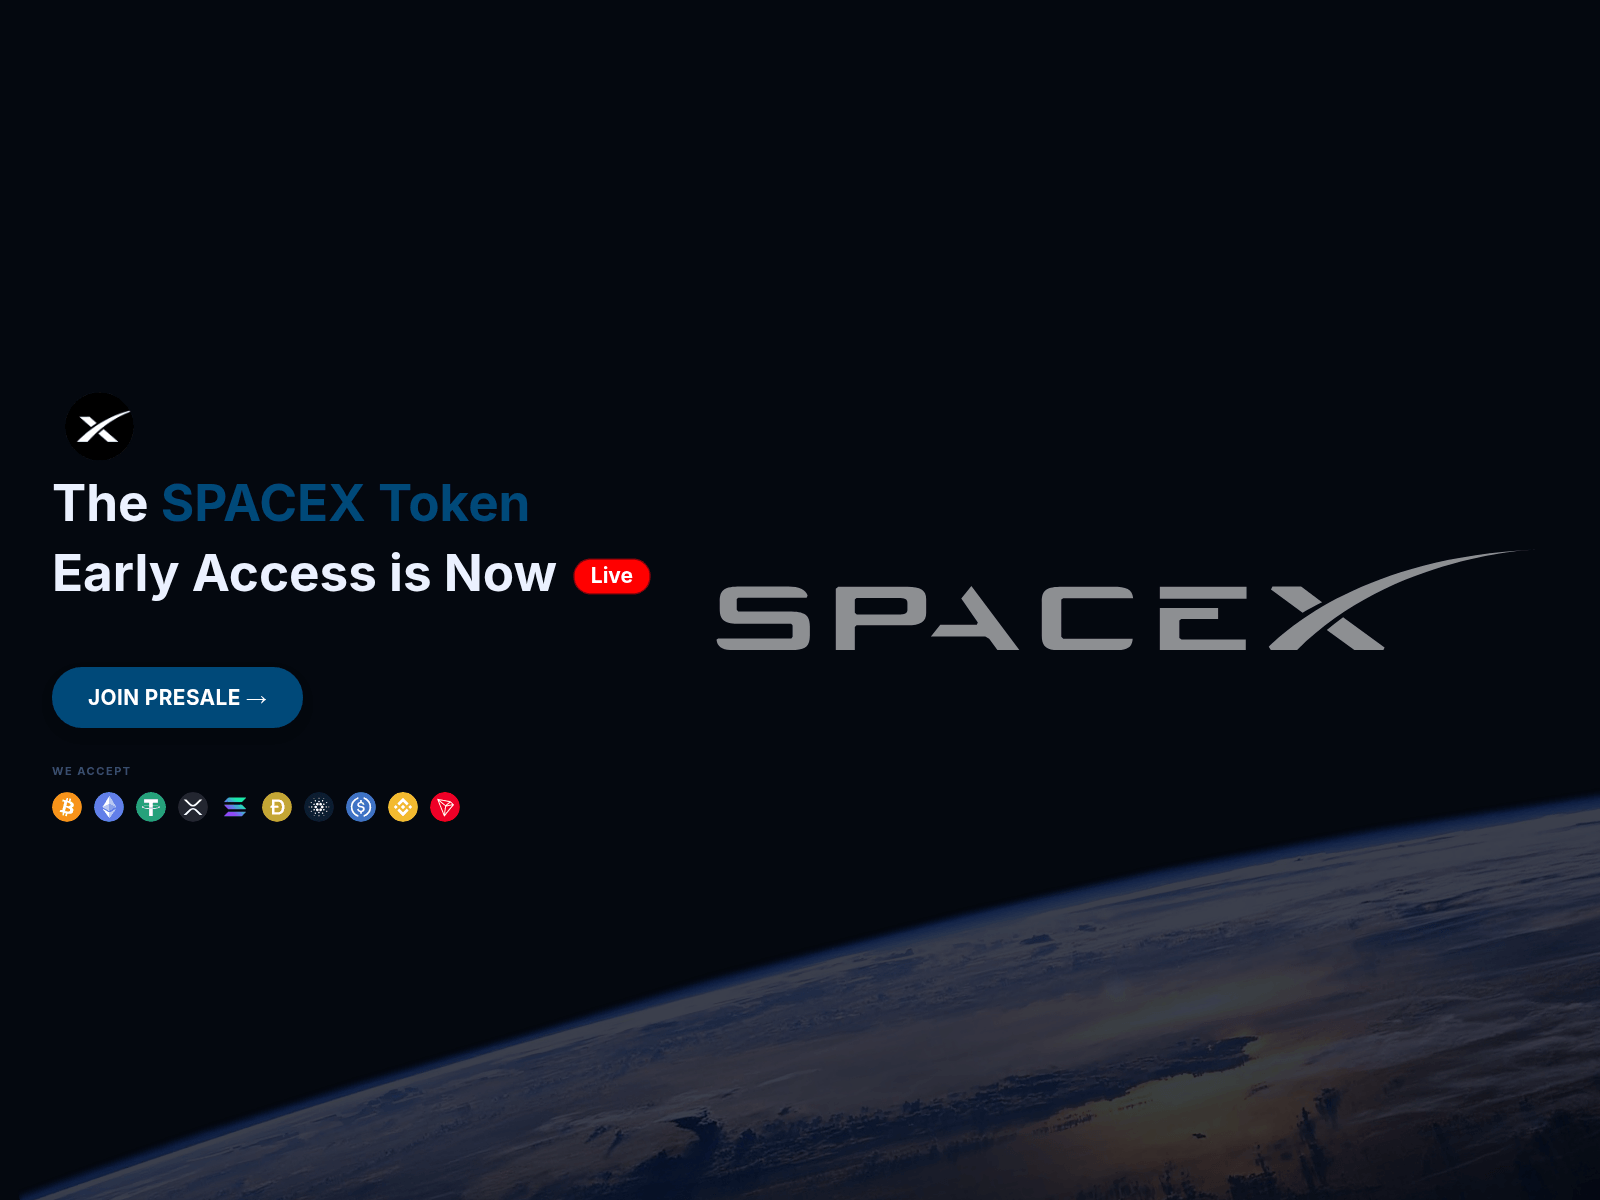
spax30t.net
spax88k.com
spax88k.net

spx99x.net

trustgoldtoken.com

uniontoken.sale

vro1lxi.pages.dev

xa20b.net

xa32p.net

xa40p.org
xa909k.net
xai320k.com
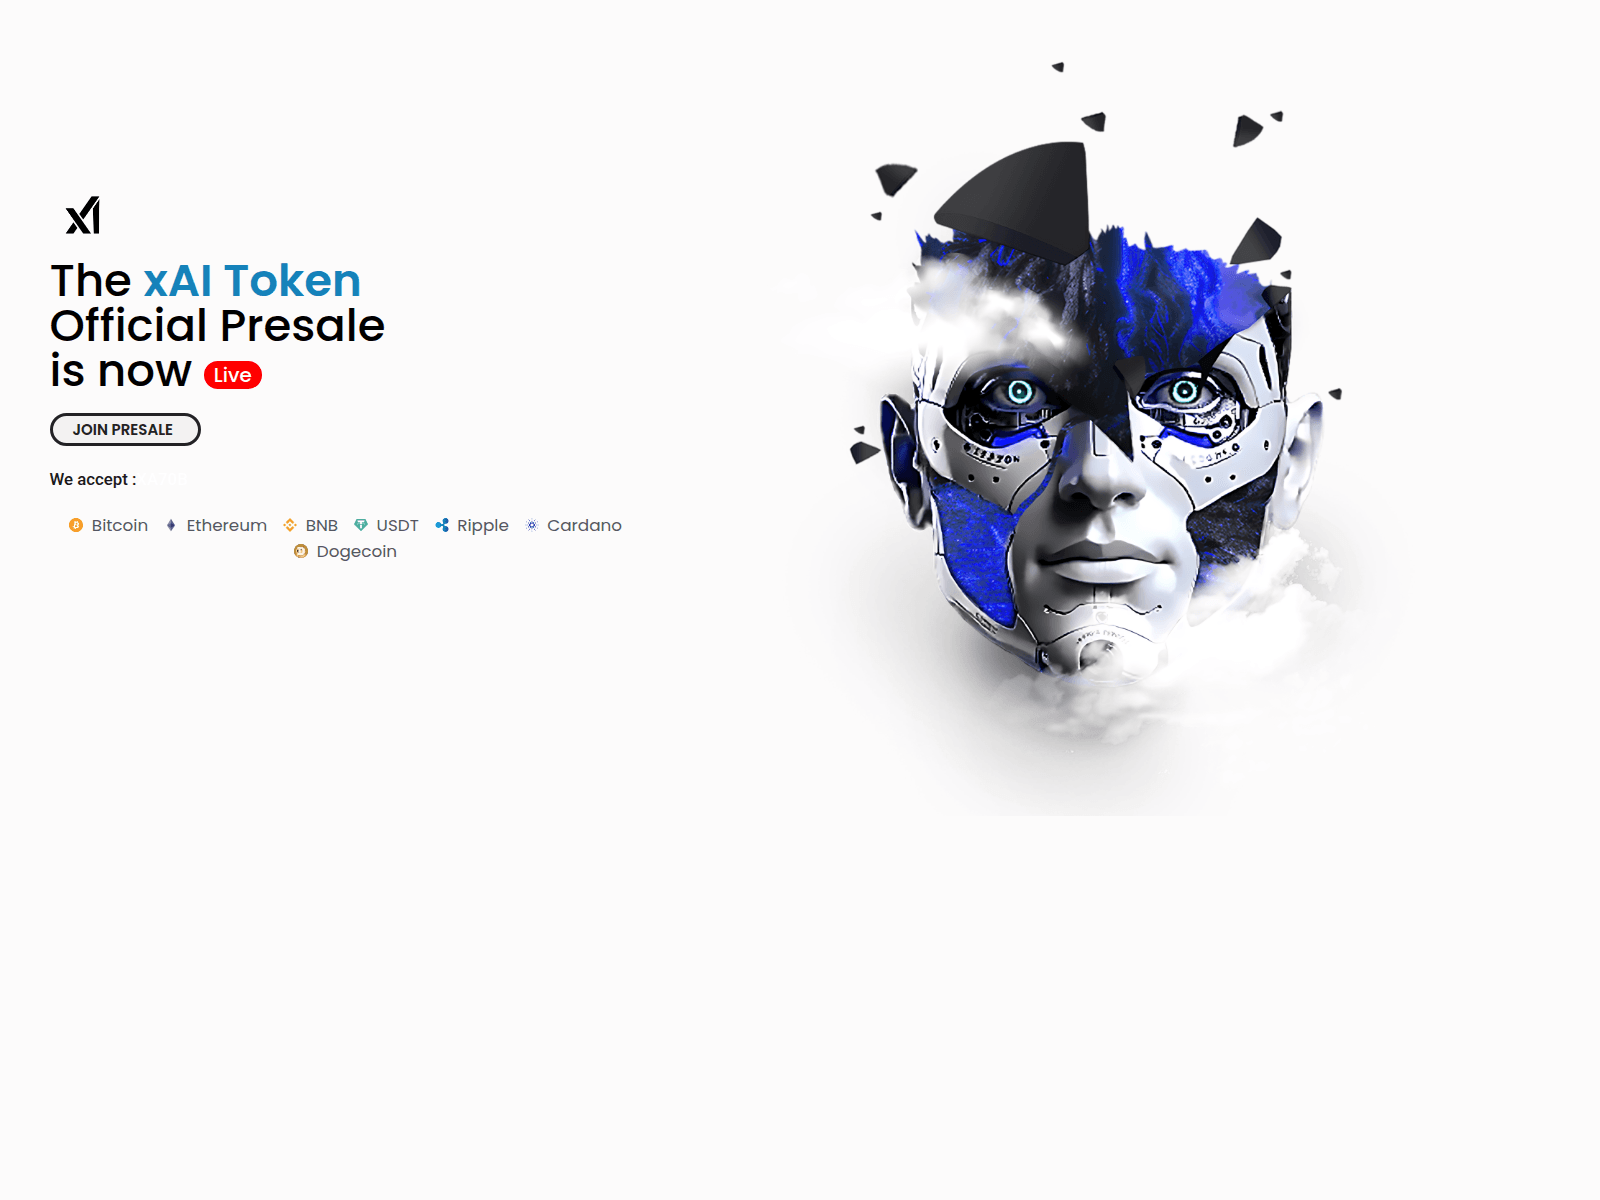
xai99r.org

xaidov-fxempire.com

xaifox-fxempire.com

xbo-com-platform.pages.dev
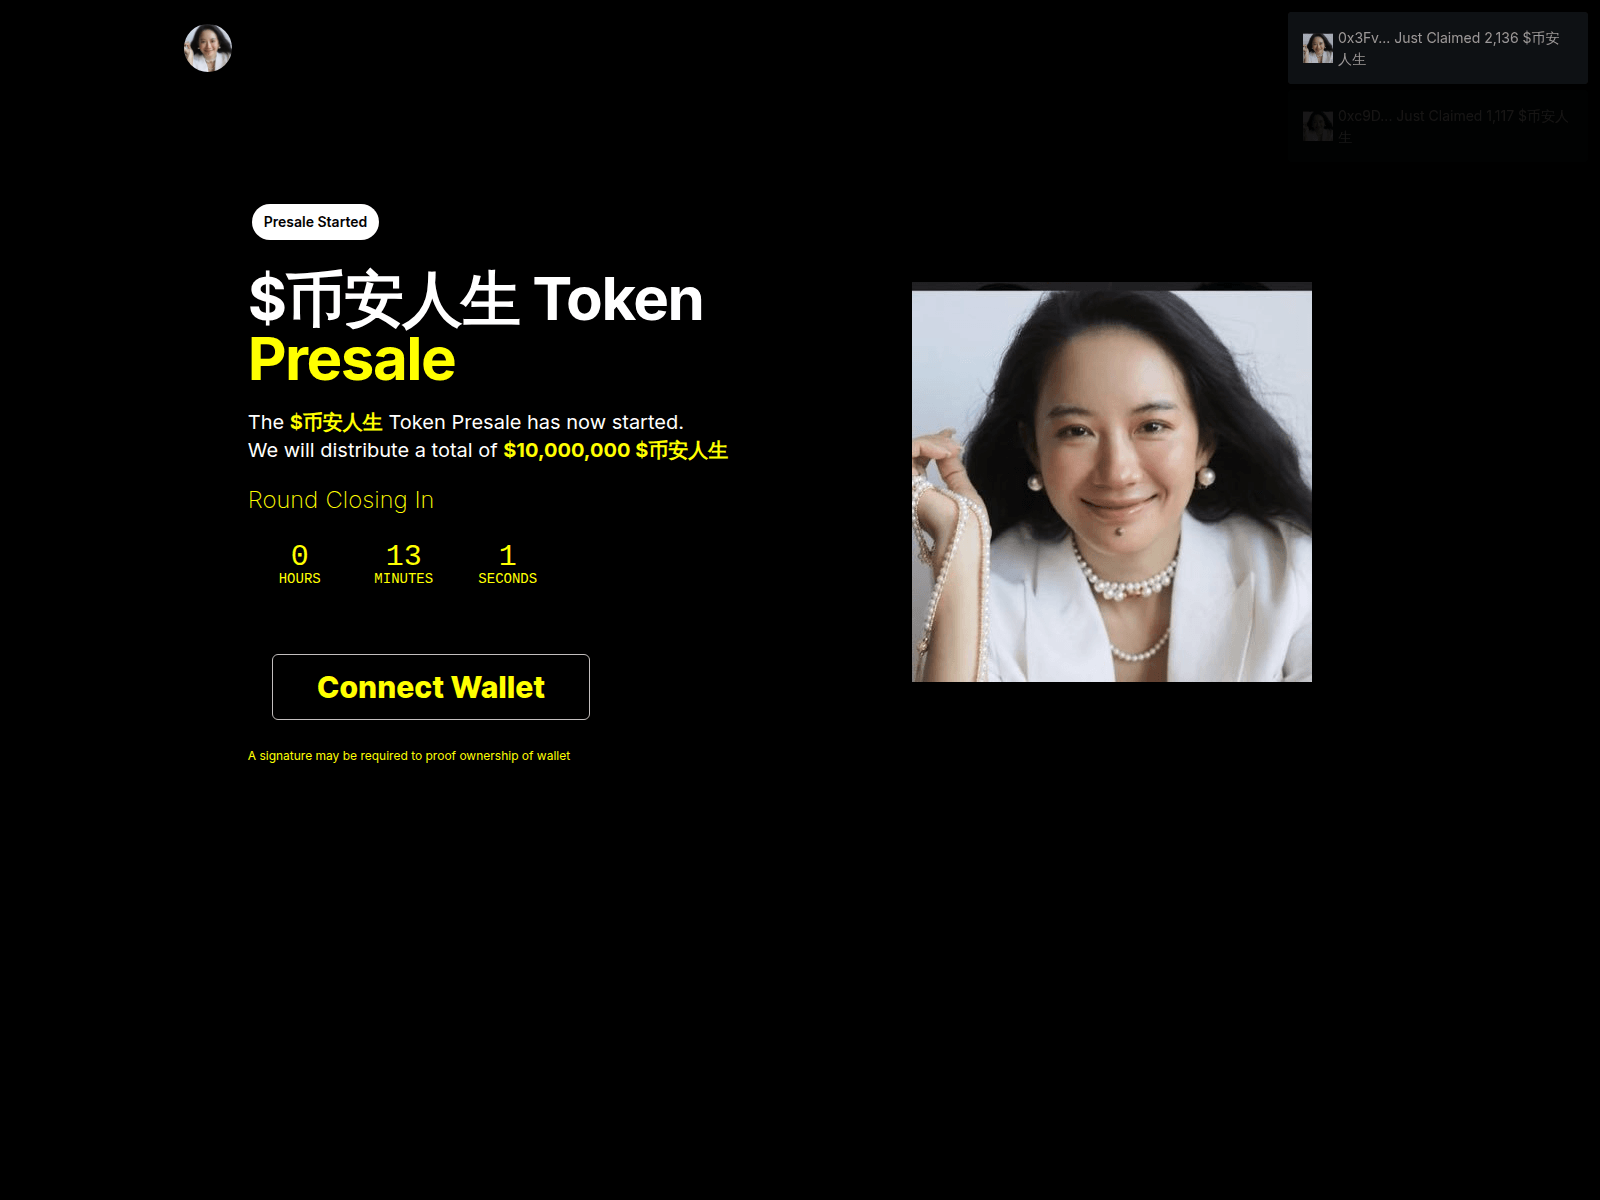
zcorkr.pages.dev

5th-scape-token.pages.dev
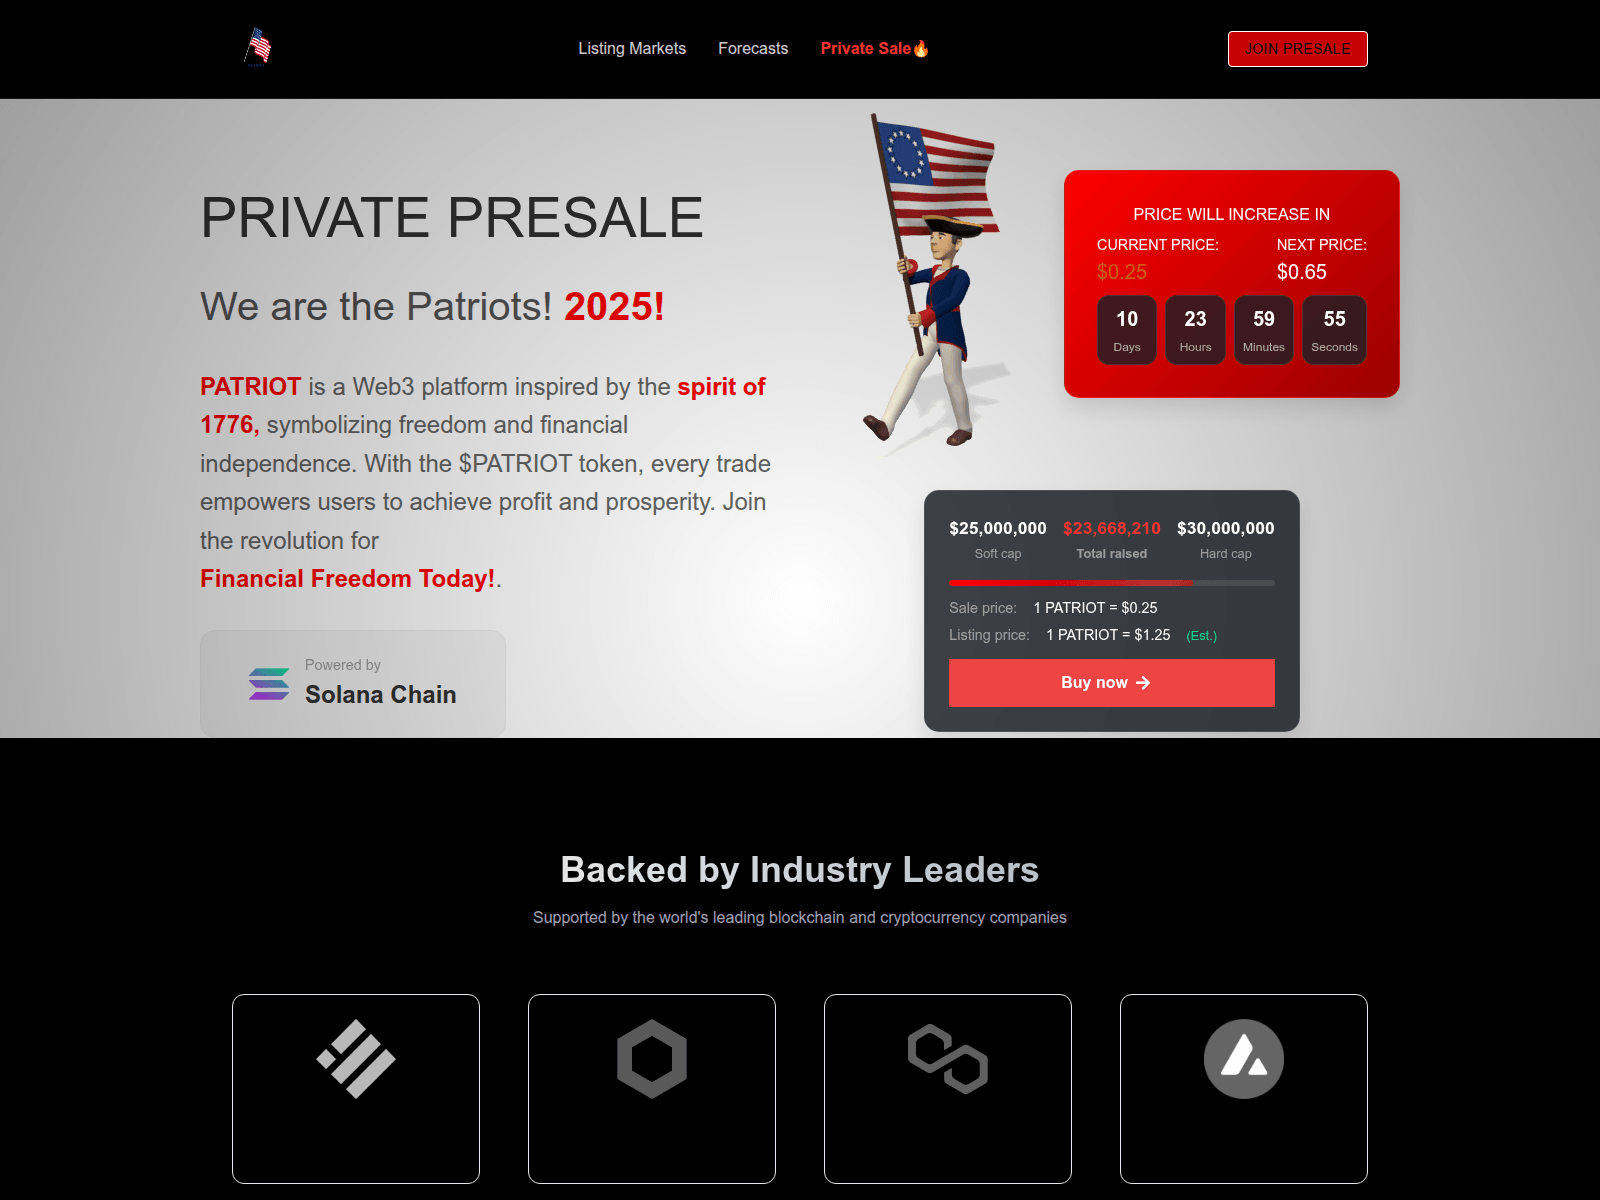
aaasz.pages.dev

aisnengh.com

apemars-presale.pages.dev
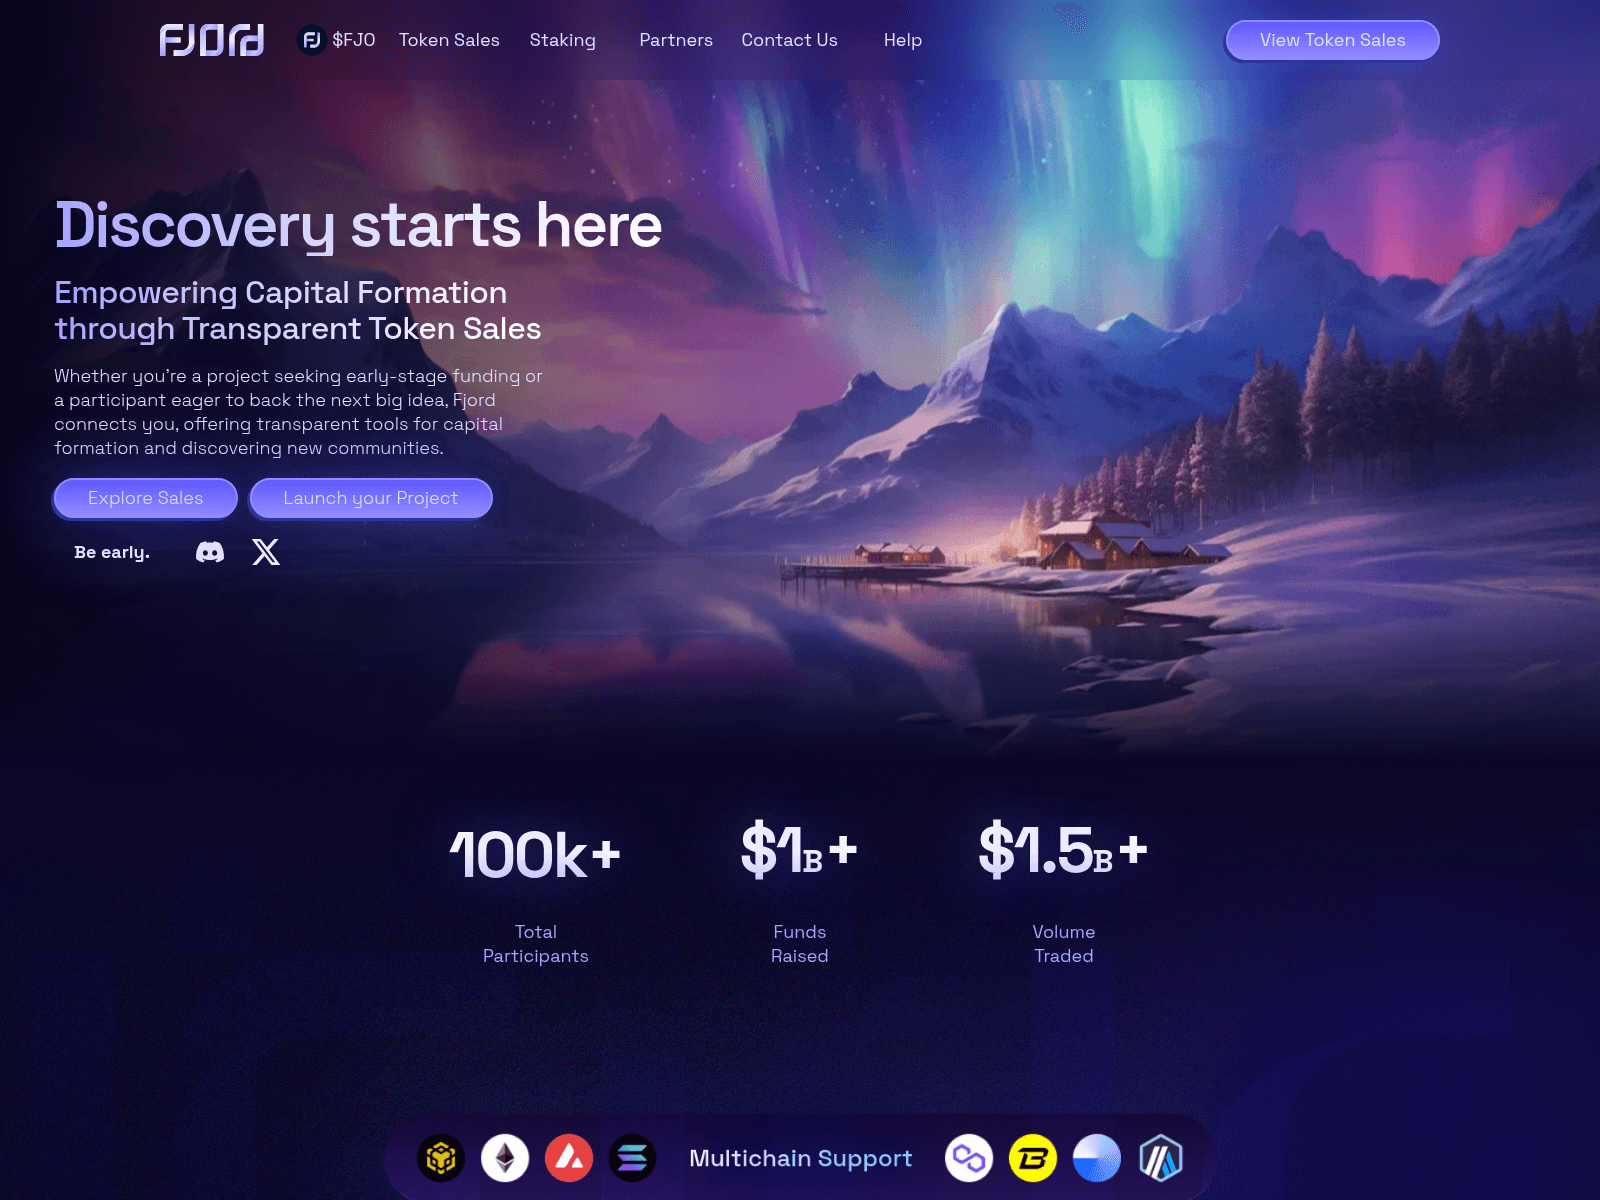
app.fjordfoundry.com

arcticpablotoken.com

ashmemecoin.com
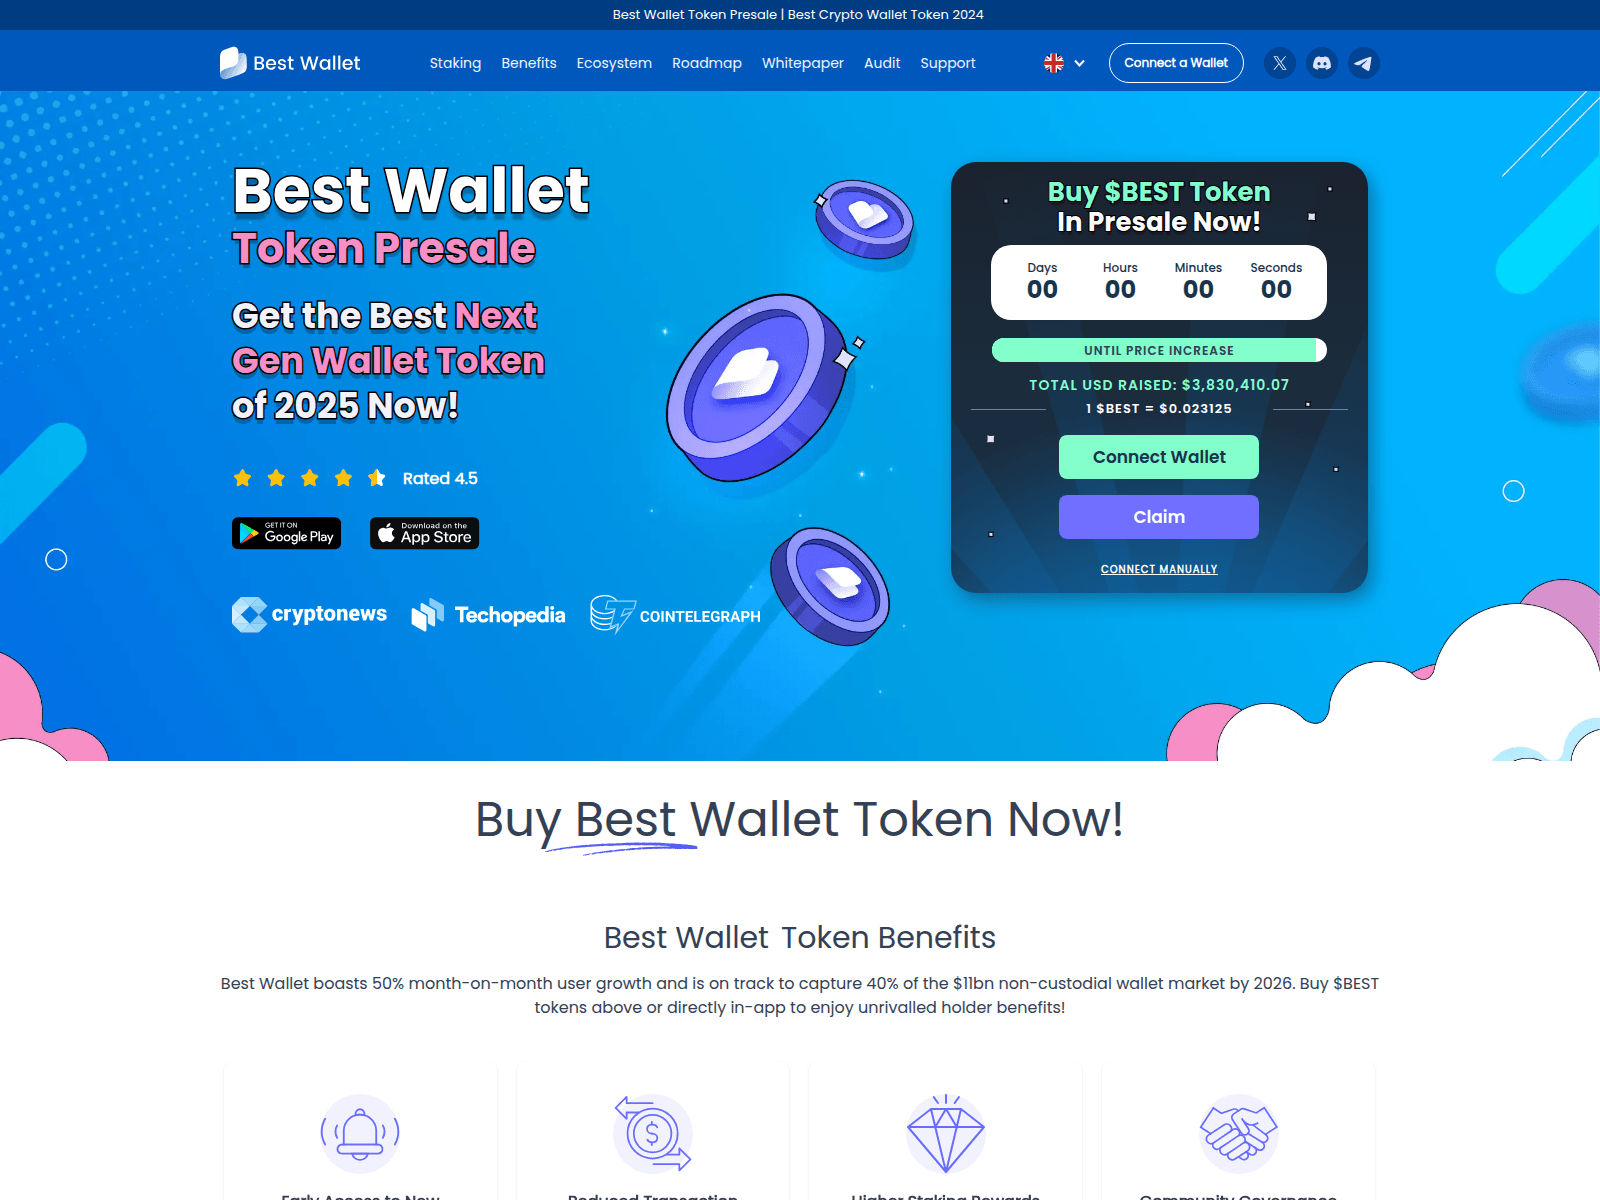
bestwallet.top


bitcoinhyper.de

bitcoinhyper.dev

bitcoinhyper.pages.dev

bitcoinhyperpresale.com
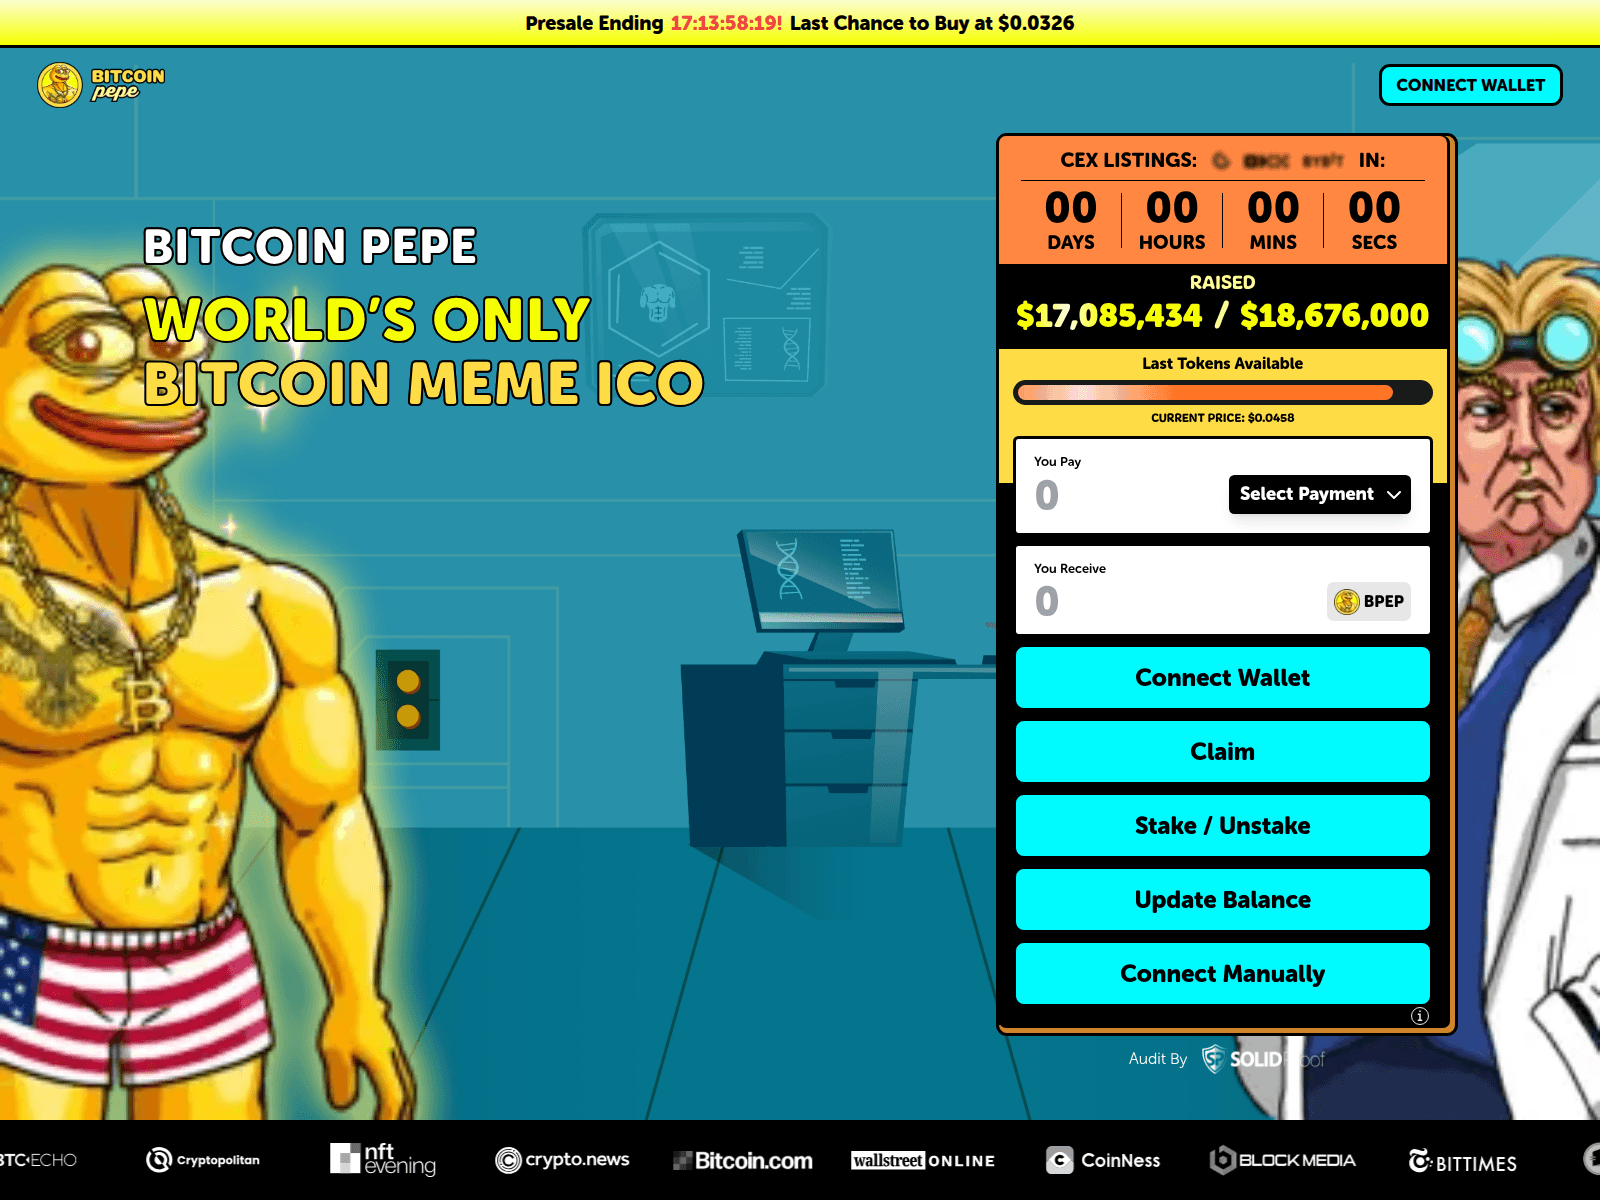
bitcoinpepe-live.web.app
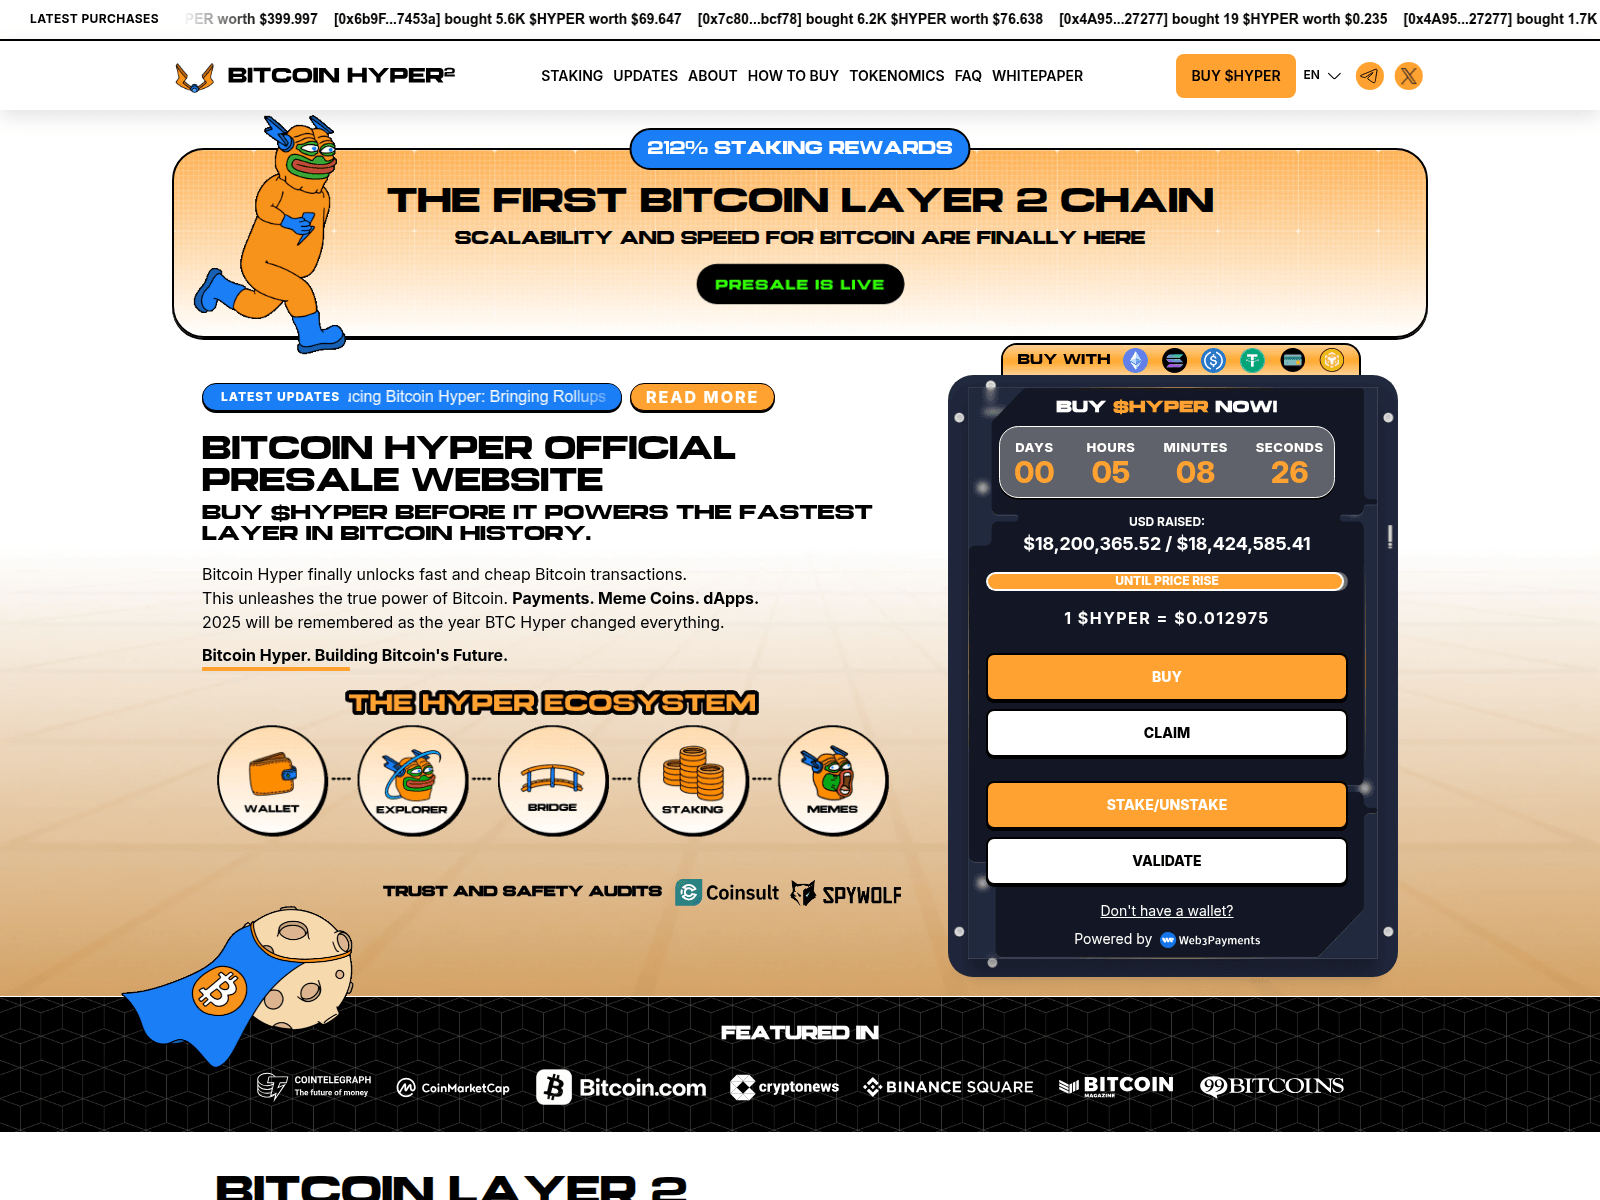
bitcoinshyper.live

bl0ckdag.network

block-dagnet.live

blockdags-netw0rk.pages.dev
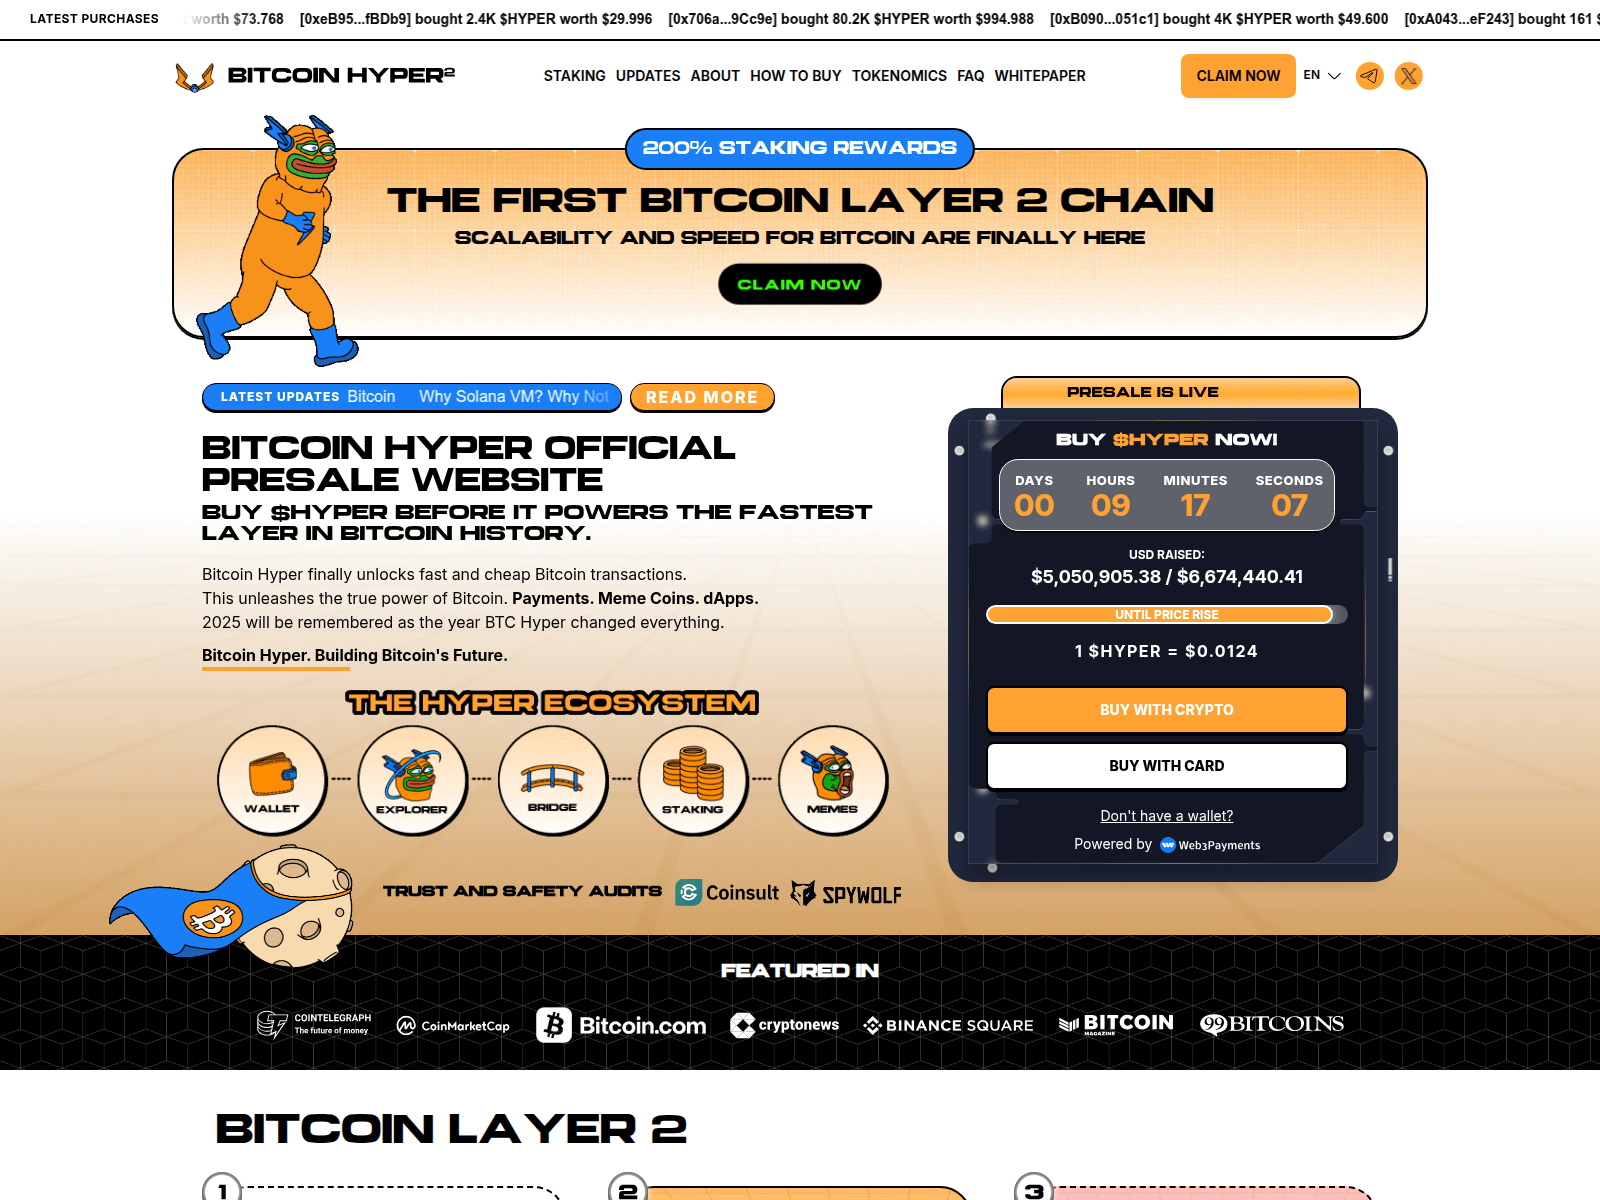
btconhyper.live
cg4wer4.pages.dev

chainbank-network.pages.dev
claimfury.pages.dev
claiming-wallstreetpepe.pages.dev

claimsflockerz.pages.dev

dawgz-claim.pages.dev
deepsnitch.io

dep100v.com

dep72t.com

digitoad-dapp.pages.dev
dogshltmeme.xyz

duplicate-disabled-43562.invalid

famous-sable-8d2114.pages.dev
fattypresale.pages.dev
flockerzclaiming.pages.dev

gempad-app-sol.pages.dev

gro36v.com

gro75k.net
gro83k.net

grok37k.com
grok82c-fxempire.com

grok87k.org

grokr-allocations.xyz
脅威対応 Pipeline
このハブ内の各ドメインがどのように検証され、確認された脅威がどのように無力化されるのか。 パイプラインの完全な可視化 →
脅威インテリジェンスの確認— すべてのドメインについて、以下の項目との照合・確認が行われます:
urlscan.ioスクリーンショット · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency レポートCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesウェイバック・マシンHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS セキュリティ FiltersQuad9 · AdGuard · CleanBrowsingWeb-確認Full surface scan
 crt.sh
グローバルベンダー同期— 検出が確認されたデータは、29のパートナーにプッシュされます:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardビットディフェンダーThreat exchangeNortonSafe WebSymantecサイトレビューAviraCloud detectionAvast / AVGWeb ShieldカスペルスキーOpenTIPDr.WebOnline scannerネットクラフトテイクダウン APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.レポートHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust