PhishDestroy threat report
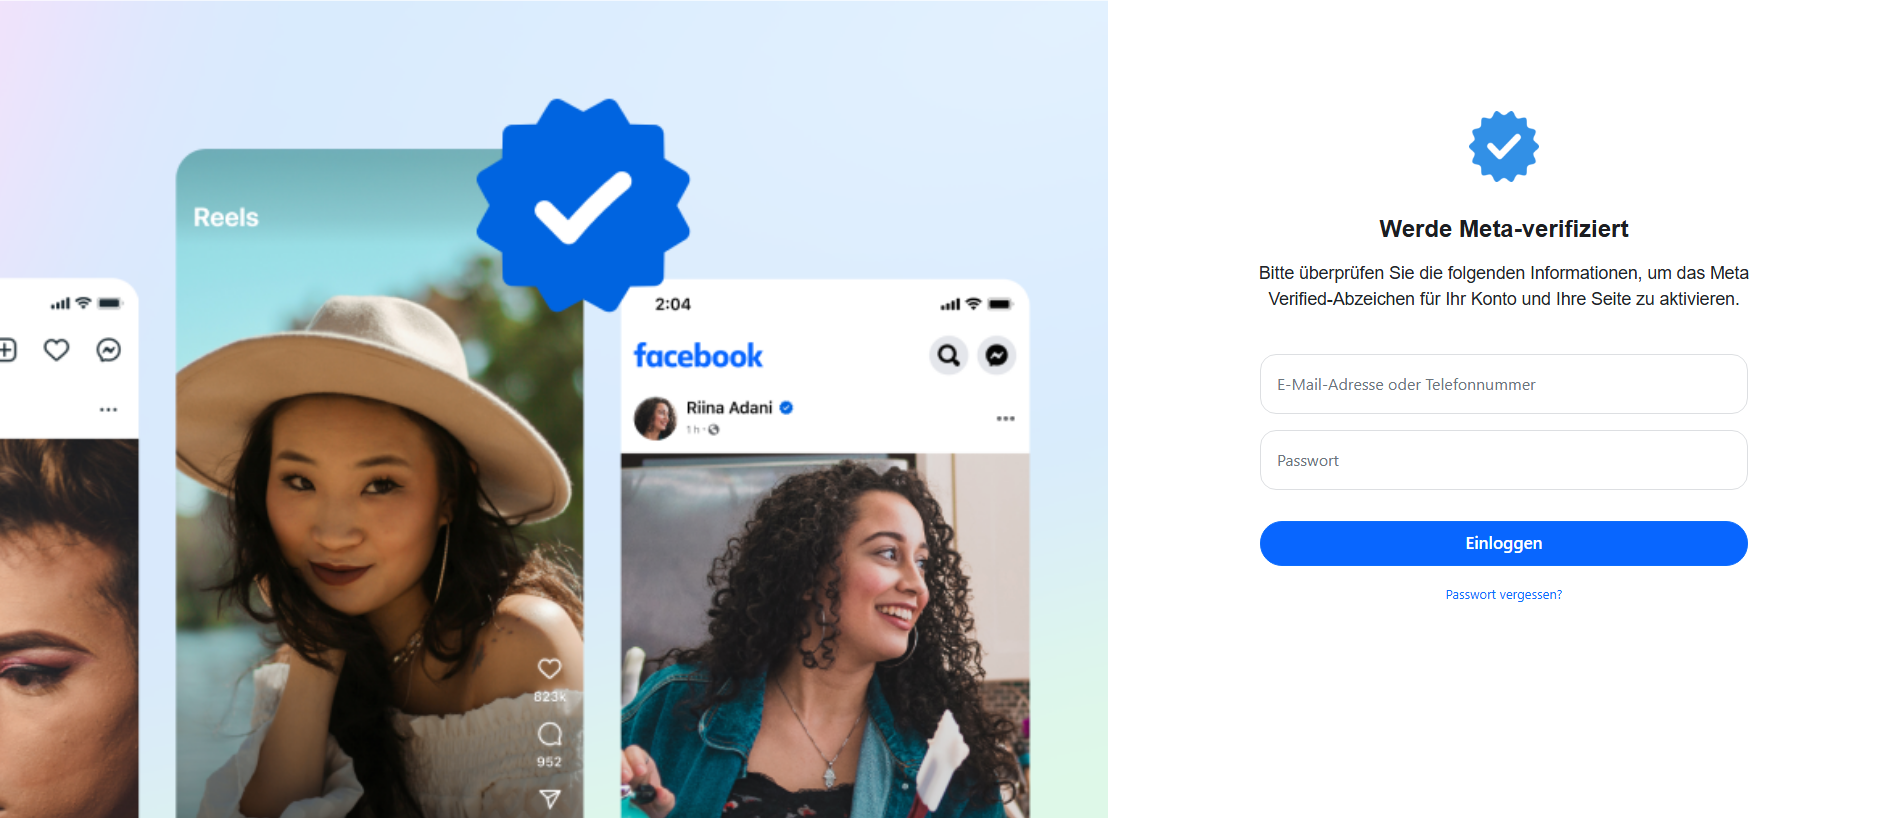
txorliva-mest617283945.vercel.app is a tenant hostname on Vercel, not a separately registered domain. PhishDestroy first observed the hostname on Oct 24, 2026. Stored content metadata identifies Facebook as the apparent target. The captured page title is “Blaues Häkchen verifiziert”. Page analysis recorded additional brand references to Google. Stored page analysis classifies the content as impersonation. Current evidence score: 68/100 (high).
Positive findings are stored from 2 sources: OpenPhish and URLScan. OpenPhish listed the hostname in the separate external-blocklist snapshot on Oct 24, 2026 at 22:20 UTC. URLScan returned a malicious verdict with score 100; scan metadata linked the capture to Facebook and assigned phishing as its category on Oct 24, 2026 at 03:30 UTC.
HTTP 200 was recorded on Oct 24, 2026 at 22:52 UTC. Latest classified outcome: live content observed; cause content served on Oct 24, 2026 at 08:56 UTC. Vercel is the hosting platform for this tenant, not its registrar. At collection time, the hostname resolved to 216.198.79.195 on AS16509 (Amazon.com, Inc.). The IP and ASN identify shared Vercel infrastructure, not the tenant operator. DOM analysis on Oct 24, 2026 at 02:20 UTC returned 68/100. The evidence archive retains 4 visual captures from PhishDestroy and URLScan. The platform TLS certificate was issued by Google Trust Services / WR1 with validity through Nov 27, 2026.
The content indicators and 2 positive source findings support the current Facebook-themed impersonation classification.