




Sicurezza del dominio e intelligence sulle minacce

interactransactions.xyz
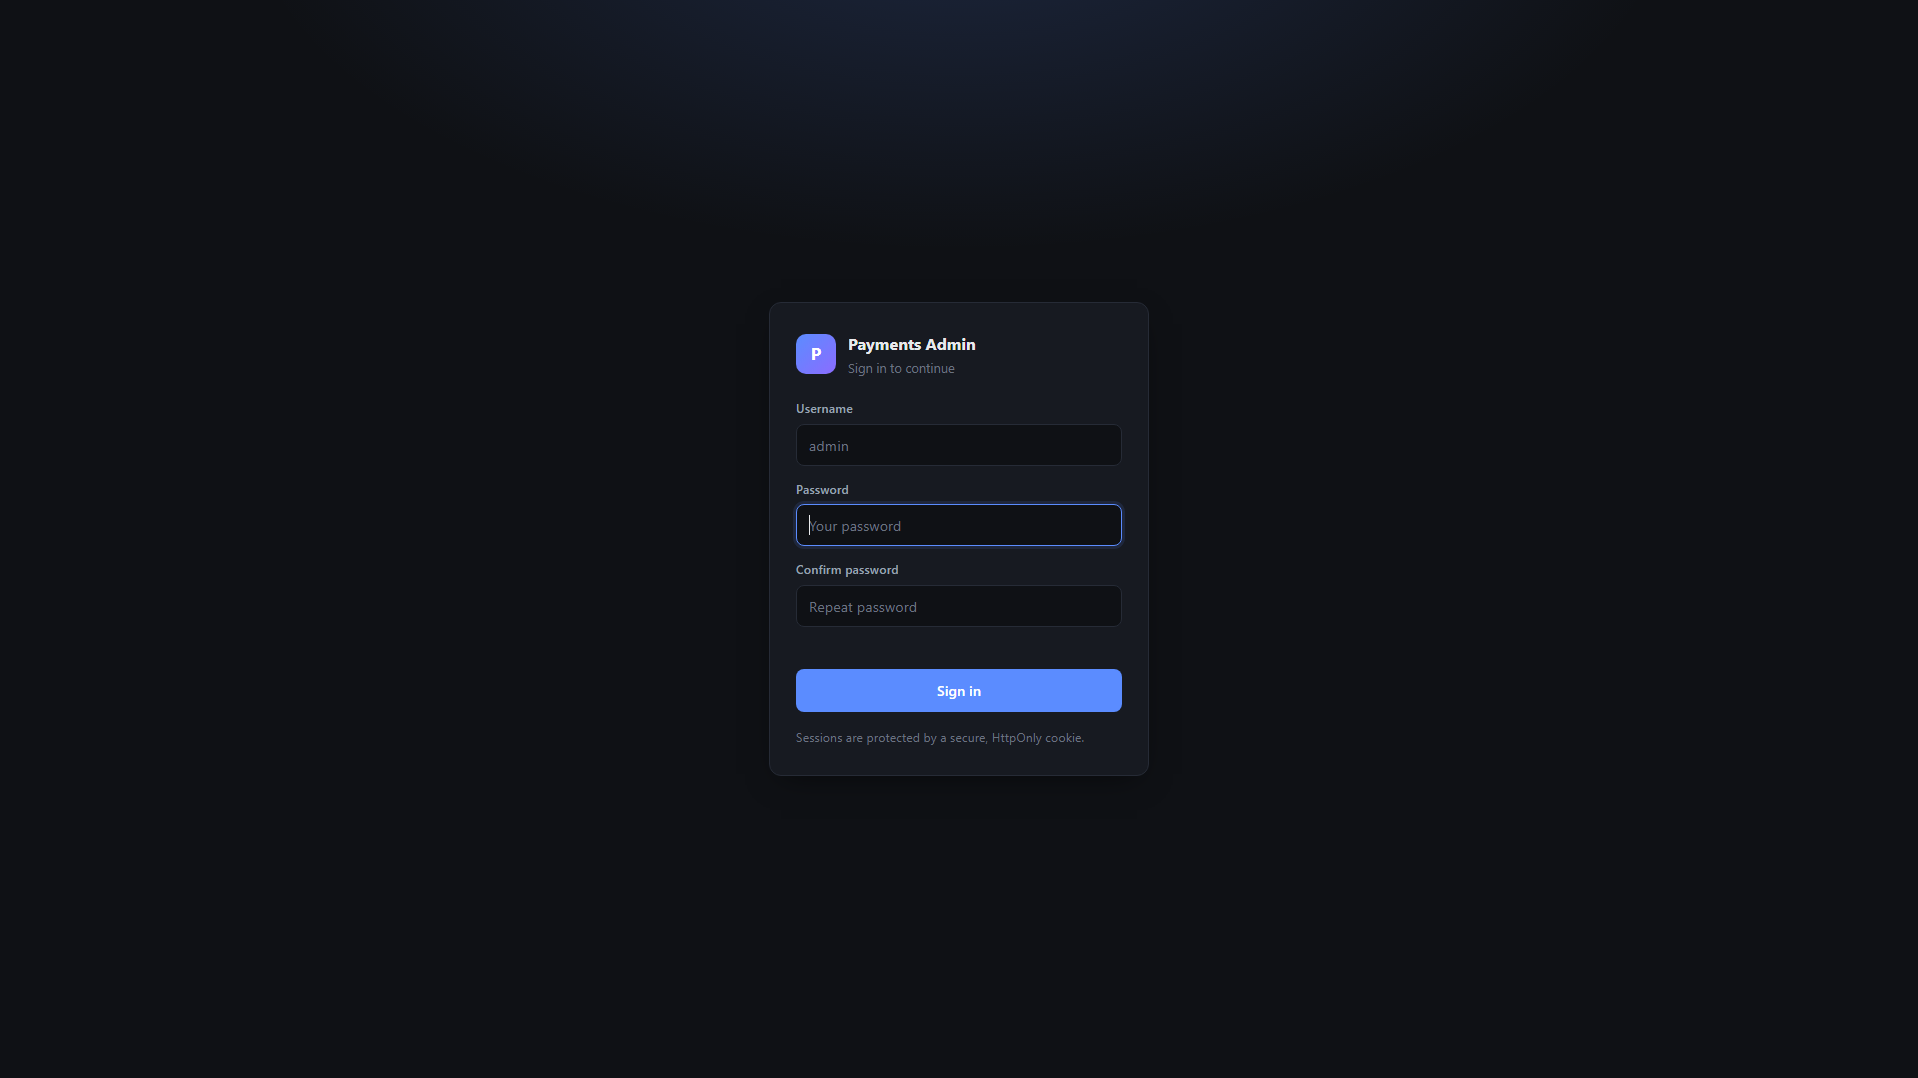
“Payments · Admin”
Verdetto di minaccia
Critico
Punteggio delle prove 98/100
Disponibilità
Ultimo attivo conosciuto
Ultima osservazione di raggiungibilità memorizzata
Segnali di rischio
Rilevamenti VirusTotal: 7/89
Spamhaus DBL: DBL_SPAM
URLQuery threat systems: 1 alert
Simulazione del marchio: Unknown
Dominio giovane: 3 giorni
Ultimo attivo conosciuto
Actions
API
ABUSE NOTICE · 24H+ OPEN
Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@whiteprivacy.com.
The latest stored availability evidence still shows the domain reachable; 33 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Elapsed since first report
33 hours
Reports sent
1
Latest case ID
PD-20260919-B2BD7B
Current status
HTTP 200 at latest stored check
Riepilogo del rapporto
interactransactions.xyz — Ultimo attivo conosciuto (HTTP 200). Simulazione del marchio: Unknown; Tipo di truffa: Impersonation. Riepilogo delle prove: VirusTotal 7/89 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Fortinet, Gridinsoft); URLQuery 1 alert; URLScan capture; Spamhaus DBL_SPAM; PhishDestroy score 98/100. Registrar: COSMOTOWN.
L’analisi dettagliata di PhishDestroy AI resta in inglese per preservare il rapporto forense originale.
Riepilogo delle prove
CRITICO
PhishDestroy first observed interactransactions.xyz on Sep 19, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Payments · Admin”. Page analysis recorded additional brand references to Telegram. Stored page analysis classifies the content as impersonation. Current evidence score: 98/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, Spamhaus DBL, and URLQuery. VirusTotal recorded 7 detections among 89 engines: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Fortinet, Gridinsoft, SOCRadar, desenmascara.me on Sep 20, 2026 at 09:54 UTC. Spamhaus DBL: DBL_SPAM on Sep 19, 2026 at 06:30 UTC. URLQuery recorded 1 threat-system alert on Sep 19, 2026 at 04:51 UTC. Non-positive and contextual checks: AlienVault OTX listed 4 community pulse references (not vendor detections) on Sep 20, 2026 at 09:55 UTC. The separate external-blocklist snapshot contained no matches on Sep 20, 2026 at 14:20 UTC. Google Safe Browsing returned no flag on Sep 20, 2026 at 09:54 UTC. URLScan captured the page on Sep 19, 2026 at 04:50 UTC.
HTTP 200 was recorded on Sep 20, 2026 at 10:50 UTC. Registration records for the domain list COSMOTOWN, INC. as the registrar and Sep 17, 2026 as the creation date. Registration preceded first observation by 1 day. At collection time, the hostname resolved to 163.61.188.9 on AS153568 (NEW DHAKA HARDWARE). The recorded endpoint location is Staten Island, US. The stored server header is LiteSpeed. DOM analysis on Sep 19, 2026 at 06:20 UTC returned 98/100. The evidence archive retains 4 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists Let's Encrypt / YR2 as the certificate issuer with validity through Dec 16, 2026; checked Sep 19, 2026 at 07:02 UTC.
The content indicators and 3 positive source findings support the current Unknown-themed impersonation classification.
VirusTotal
7 det.
URLQuery
1 threat alert
OTX references
URLScan
Scamadviser
80/100Likely Safe
Certificato TLS
Let's Encrypt / YR2
Età
3d Brand New!
Stato osservato
Ultimo attivo conosciuto 200

Elenco da eliminare
Presente
Reports Sent
1
Copertura dei dati
VirusTotal
7 / 89
URLQuery
1 threat-system alert
OTX
4 community references
CF Radar
scan completed
URLScan capture
rapporto memorizzato
TLS
valid certificate, 87d
WHOIS
3d old
Screenshot
4 captures · 3 sources
Scamadviser
80/100
Informazioni sulla sicurezza di rete
Threat Detection Systems
1 alert
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| DNS4EU | interactransactions.xyz |
malicious | Sinkholed |
Forensic History & Detection Timeline
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
-
VirusTotal Detections Update Sep 20, 2026 · 05:26 UTCVirusTotal scanner detections updated from 6 to 7. Added scanner alerts: CRDF.
-
VirusTotal Detections Update Sep 19, 2026 · 20:11 UTCVirusTotal scanner detections updated from 5 to 6. Added scanner alerts: desenmascara.me.
-
VirusTotal Detections Update Sep 19, 2026 · 14:37 UTCVirusTotal scanner detections updated from 4 to 5. Added scanner alerts: SOCRadar.
-
VirusTotal Detections Update Sep 19, 2026 · 08:53 UTCVirusTotal scanner detections updated from 3 to 4. Added scanner alerts: Gridinsoft.
-
Threat First Observed Sep 19, 2026 · 06:45 UTCDomain ingestion complete. Initial state is marked as alive pointing to IP
163.61.188.9.
Pipeline di risposta alle minacce
Scoperta
Checks
Reports
Disponibilità
15/16
Sent Report Recorded
Stored sent-report record for registrar COSMOTOWN, INC., hosting provider, 3 abuse contacts
abuse@whiteprivacy.comabuse@cosmotown.comprivacy@cosmotown.com
Stato della lista di blocco pubblica
Evasion analysis
Cloaking & traffic-distribution check
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
- Stored cloaking flag
- Not yet scanned
- Last cloaking scan
- Server header seen by scanner
LiteSpeed
Scanner note: alive_content: raw=ok; http=200; via=https_proxy; server=LiteSpeed
Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting
Acquisizione salvata · 4 sources
Analisi dei domini
Dominio
Server / ASN
LiteSpeed · AS153568 NEW DHAKA HARDWARE
Reputazione IP
abuse score 11/100 3 reports Brute-Force checked 19/09/2026
OTX Tags
2026-09activeall-domainsblocklistcontentcryptodominidrainerfraudlivemonthlyphishdestroyphishingscam
Registrar
COSMOTOWN
 (US)
(US)
Indirizzo IP
163.61.188.9
RegistrazioneCreato 17/09/2026 (3d · Brand New!) — Expires 17/09/2027
Stato HTTP200
Dettagli tecniciDNS, SAN SSL, timestamp
Rilevato per la prima volta19/09/2026
DOM Analysis
IoC Extraction
Submitted URLhttps://interactransactions.xyz/
Nameserverdns1.lytehosting.comdns2.lytehosting.comdns3.lytehosting.comdns4.lytehosting.com
MX Records0 interactransactions.xyz
TLS Fingerprint
TLS Observation
Favicon Hash
ID del caso
ICANN OVERSIGHT
Accreditamento e contesto RAA
Accreditamento e contesto RAA
Registrar accreditation and DNS abuse obligations
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
Accreditation is a contract, not a safety certification.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
L’accreditamento è un contratto, non un sigillo di sicurezza.
Verifica le tariffe ICANN
Leggi il RAA §3.18
PHISHDESTROY INVESTIGATIONICANN funding, contracts, and DNS abuse oversight
Tecnologie · 4 identified
Node.js
Programming languages
LiteSpeed
Web servers
Express
Web frameworks
Web servers
HTTP/3
Miscellaneous
Detected via Cloudflare Radar · Wappalyzer engine
Segnala questo dominio
Invia le prove e contribuisci a proteggere gli altri
Analisi di VirusTotal
7 / I fornitori di sicurezza 89 hanno contrassegnato questo dominio
View on VT
Last analyzed Previous stored snapshot: 7 detections
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
SOCRadar
desenmascara.me
Analisi delle prestazioni del sito
Google PageSpeed Insights — mobile performance audit of interactransactions.xyz · checked Sep 19, 2026
100
Good
Performance
FCP
0.93s
First Contentful Paint
LCP
0.93s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
1.27s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Dati e relazioni esterne
Analisi della sicurezza
Istantanea delle prove inviate
Sent: Ledger records: 1
Case ID:
PD-20260919-B2BD7B Recipient: abuse@whiteprivacy.com Page title stored with report: Payments · Admin
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
OSINT e intelligence
DNS e rete
SEO e dominio
Questo sito ti ha influenzato in qualche modo?
If credentials were compromised, report immediately. Do not engage with recovery scammers.
Se hai inserito credenziali dell'account, informazioni personali o di pagamento oppure hai scaricato un file da questo dominio, agisci immediatamente. Di seguito sono riportate le risorse per aiutarti a segnalare l'incidente e proteggerti.

Europol
Trova il canale di segnalazione ufficiale per il tuo paese dell'UE
National police directory

Action Fraud
Segnala frodi e crimini informatici in Inghilterra, Galles e Irlanda del Nord
Contact centre0300 123 2040
PhishDestroy listing review Non un rapporto delle forze dell'ordine
Ricorso in materia di domini
Richiedi una revisione se possiedi questo dominio e ritieni che l'elenco non sia corretto
Attenzione ai truffatori che promettono il recupero dei fondi! I criminali possono contattare nuovamente le vittime fingendo di essere investigatori, avvocati o agenti di recupero. Non pagare commissioni anticipate né condividere credenziali. Scopri di più sulle frodi relative ai sussidi di recupero →
Segnalalo alle autorità locali
Seleziona il tuo Paese per ottenere contatti ufficiali del crimine informatico o creare una bozza di reclamo →.
Elenco di 97 paesi
Bozza assistita dall'intelligenza artificiale: i dettagli dell'incidente vengono elaborati dal fornitore di intelligenza artificiale
Controllalo e invialo tu stesso
Infrastruttura e rapporti correlati
Infrastructure map · interactransactions.xyz
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
Content matches 4
Shared IP 163.61.188.9 6
Questo IP di origine ospita più domini di phishing: l'infrastruttura può essere condivisa tra campagne.
 inxparknord.cc
 firstprimeassets.com
 bgaccessult.cc
 estatedao.today
Stesso registrar: COSMOTOWN 6
 vertexbets.com
 amazoncapitalsinvests.com
 bank.goldenmarshprime.sbs
 fnfort.com
 imperialroute.com
Unknown impersonation 8
These domains also target Sconosciuto users. View all Unknown threats →
Rapporti recenti sulle minacce 4
Rapporti aggiunti di recente dal database PhishDestroy. Questi collegamenti di scoperta non implicano infrastrutture o proprietà condivise.
 libertycbk.com.sendriadelivery.com
 bitex-financial.cc
 autoprimemarketrades.com
 vicocredit.com
Verifica qualsiasi dominio
Analisi delle minacce utilizzando blocklist archiviate, WHOIS, DNS e prove di scansione pubblica
Scansiona oraSegnala un tentativo di phishing
Segnala i domini sospetti al nostro database delle minacce — proteggi la comunità
SegnalaFeed in tempo reale sulle minacce
Segnalazioni recenti di phishing e modifiche osservate della disponibilità
MonitoraRimani informato, rimani al sicuro
Controlla le minacce in tempo reale oppure contesta questa segnalazione se ritieni che si tratti di un falso positivo