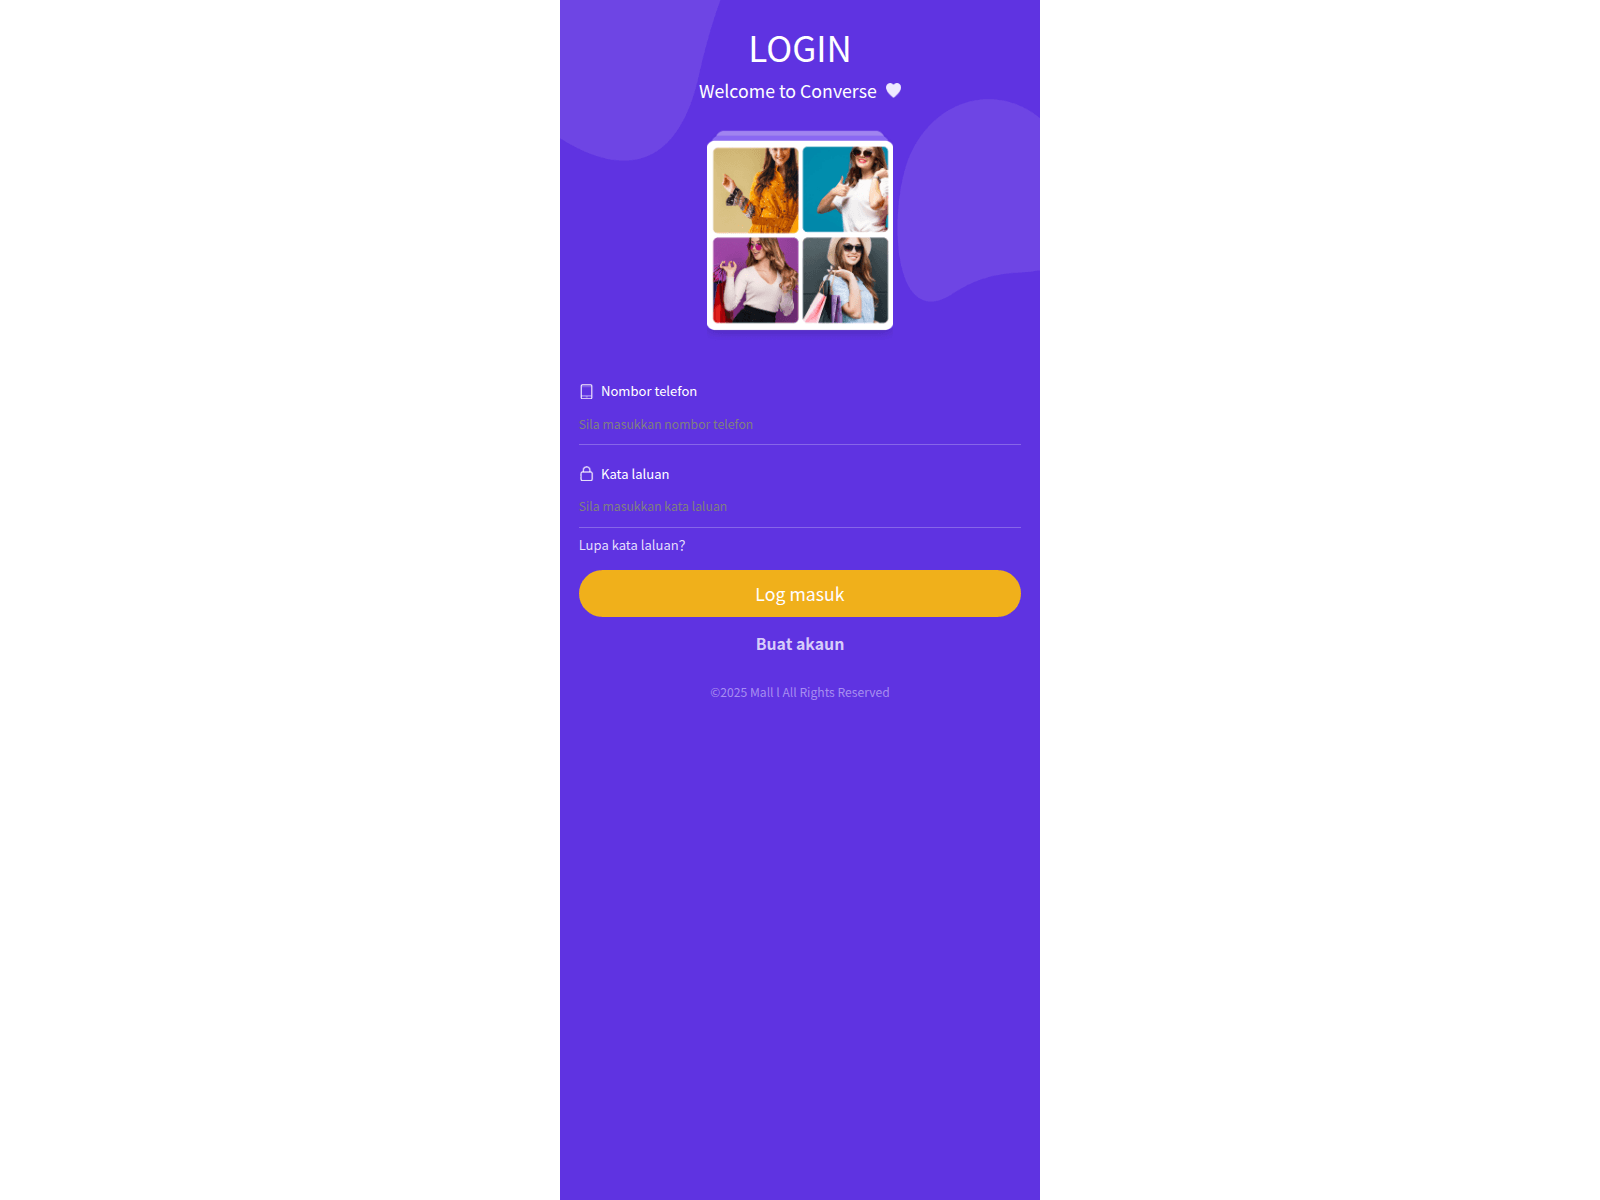
188.114.96.3
VirusTotal

17 / 92 rilevamenti del motore
Analisi:
Apri il rapporto VirusTotalRecord originale della fonteOsservato: 11 campi
Osservato: · Estratto da:
Conteggio dei risultati dei fornitori
- Timeout
- 0
- Innocuo
- 42
- Malevolo
- 16
- Sospetto
- 1
- Non rilevato
- 33
Etichette dei fornitori
- CRDF
- malicious
- ESET
- phishing
- Ermes
- not recommended
- VIPRE
- phishing
- G-Data
- phishing
- Lionic
- phishing
- Sophos
- phishing
- CyRadar
- phishing
- Webroot
- malicious
- Fortinet
- phishing
- SOCRadar
- malicious
- Kaspersky
- phishing
- Seclookup
- malicious
- BitDefender
- phishing
- alphaMountain.ai
- phishing
- Yandex Safebrowsing
- phishing
- Forcepoint ThreatSeeker
- phishing
Punteggio di reputazione
0Creato
Aggiornato
Prima rilevazione
Record DNS
- TTL, secondi
- 300
- Tipo
- A
- Valore
- 172.67.186.159
- TTL, secondi
- 300
- Tipo
- AAAA
- Valore
- 2606:4700:3035::ac43:ba9f
- TTL, secondi
- 1800
- Tipo
- SOA
- Casella del responsabile
- dns.cloudflare.com
- Valore
- tessa.ns.cloudflare.com
- TTL, secondi
- 300
- Tipo
- AAAA
- Valore
- 2606:4700:3033::6815:3bfe
- TTL, secondi
- 21600
- Tipo
- NS
- Valore
- tessa.ns.cloudflare.com
- TTL, secondi
- 21600
- Tipo
- NS
- Valore
- wells.ns.cloudflare.com
- TTL, secondi
- 300
- Tipo
- A
- Valore
- 104.21.59.254
Record DNS rilevati
Impronta JARM
27d40d40d00040d1dc42d43d00041d6183ff1bfae51ebd88d70384363d525cCertificato
- Nomi alternativi del soggetto (SAN)
- conversemy.today
- *.conversemy.today
- Emittente
- Google Trust Services / WE1
- Numero di serie
- ee1e9167ef47449513ac68cdd3e4d6dd
- SHA-256
- 60347c18c193c0945edb6dfa421f5ac21ba1bbedff58b30461fba1741143eb02
- Soggetto
- conversemy.today
- Valido fino al
- Valido dal
Dati del registro (RDAP)
- Stato
- client hold
- client transfer prohibited
- Eventi del registro
- Scadenza della registrazione
- Registrazione
- Ultimo aggiornamento del database RDAP
- Registrar
- Gname.com Pte. Ltd.
- ID IANA del registrar
- 1923
Campi originali della fonte · JSON
| Conteggio dei risultati dei fornitori | {
"timeout": 0,
"harmless": 42,
"malicious": 16,
"suspicious": 1,
"undetected": 33
} |
|---|---|
| Etichette dei fornitori | {
"CRDF": "malicious",
"ESET": "phishing",
"Ermes": "not recommended",
"VIPRE": "phishing",
"G-Data": "phishing",
"Lionic": "phishing",
"Sophos": "phishing",
"CyRadar": "phishing",
"Webroot": "malicious",
"Fortinet": "phishing",
"SOCRadar": "malicious",
"Kaspersky": "phishing",
"Seclookup": "malicious",
"BitDefender": "phishing",
"alphaMountain.ai": "phishing",
"Yandex Safebrowsing": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputazione | 0 |
| Creato | 2025-09-27T00:00:00Z |
| Aggiornato | 2025-09-27T00:00:00Z |
| Prima rilevazione | 2025-09-29T16:05:23Z |
| Record DNS | [
{
"ttl": 300,
"type": "A",
"value": "172.67.186.159"
},
{
"ttl": 300,
"type": "AAAA",
"value": "2606:4700:3035::ac43:ba9f"
},
{
"ttl": 1800,
"type": "SOA",
"rname": "dns.cloudflare.com",
"value": "tessa.ns.cloudflare.com"
},
{
"ttl": 300,
"type": "AAAA",
"value": "2606:4700:3033::6815:3bfe"
},
{
"ttl": 21600,
"type": "NS",
"value": "tessa.ns.cloudflare.com"
},
{
"ttl": 21600,
"type": "NS",
"value": "wells.ns.cloudflare.com"
},
{
"ttl": 300,
"type": "A",
"value": "104.21.59.254"
}
] |
| Dns at | 2026-07-27T17:55:59Z |
| Jarm | 27d40d40d00040d1dc42d43d00041d6183ff1bfae51ebd88d70384363d525c |
| Certificato | {
"san": [
"conversemy.today",
"*.conversemy.today"
],
"issuer": "Google Trust Services / WE1",
"serial": "ee1e9167ef47449513ac68cdd3e4d6dd",
"sha256": "60347c18c193c0945edb6dfa421f5ac21ba1bbedff58b30461fba1741143eb02",
"subject": "conversemy.today",
"valid_to": "2026-09-01T14:04:34Z",
"valid_from": "2026-06-03T13:05:53Z"
} |
| Dati del Registro di sistema | {
"status": [
"client hold",
"client transfer prohibited"
],
"events": {
"expiration": "2027-09-27T13:07:37Z",
"registration": "2025-09-27T13:07:37Z",
"last update of RDAP database": "2026-10-25T13:13:06Z"
},
"registrar": "Gname.com Pte. Ltd.",
"registrar_iana_id": "1923"
} |
Separate collector summary
This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.
- source
- VirusTotal
- scope
- unknown
- result_state
- null
- numerator
- 21
- denominator
- 91
- malicious
- null
- suspicious
- null
- vendors
- ["alphaMountain.ai","BitDefender","Cluster25","CRDF","CyRadar","Ermes","ESET","Emsisoft","Forcepoint ThreatSeeker","Fortinet","G-Data","Kaspersky","LevelBlue","Lionic","Netcraft","OpenPhish","SOCRadar","Sophos","VIPRE","Webroot","Yandex Safebrowsing"]
- observed_at
- null
- checked_at
- 2026-08-04 04:14:13
- fetched_at
- null
- time_basis
- as stored; legacy timezone not established


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT