Vai al rapporto di sicurezza
Sicurezza del dominio e intelligence sulle minacce
ahaselectedboutique.shop favicon

ahaselectedboutique.shop

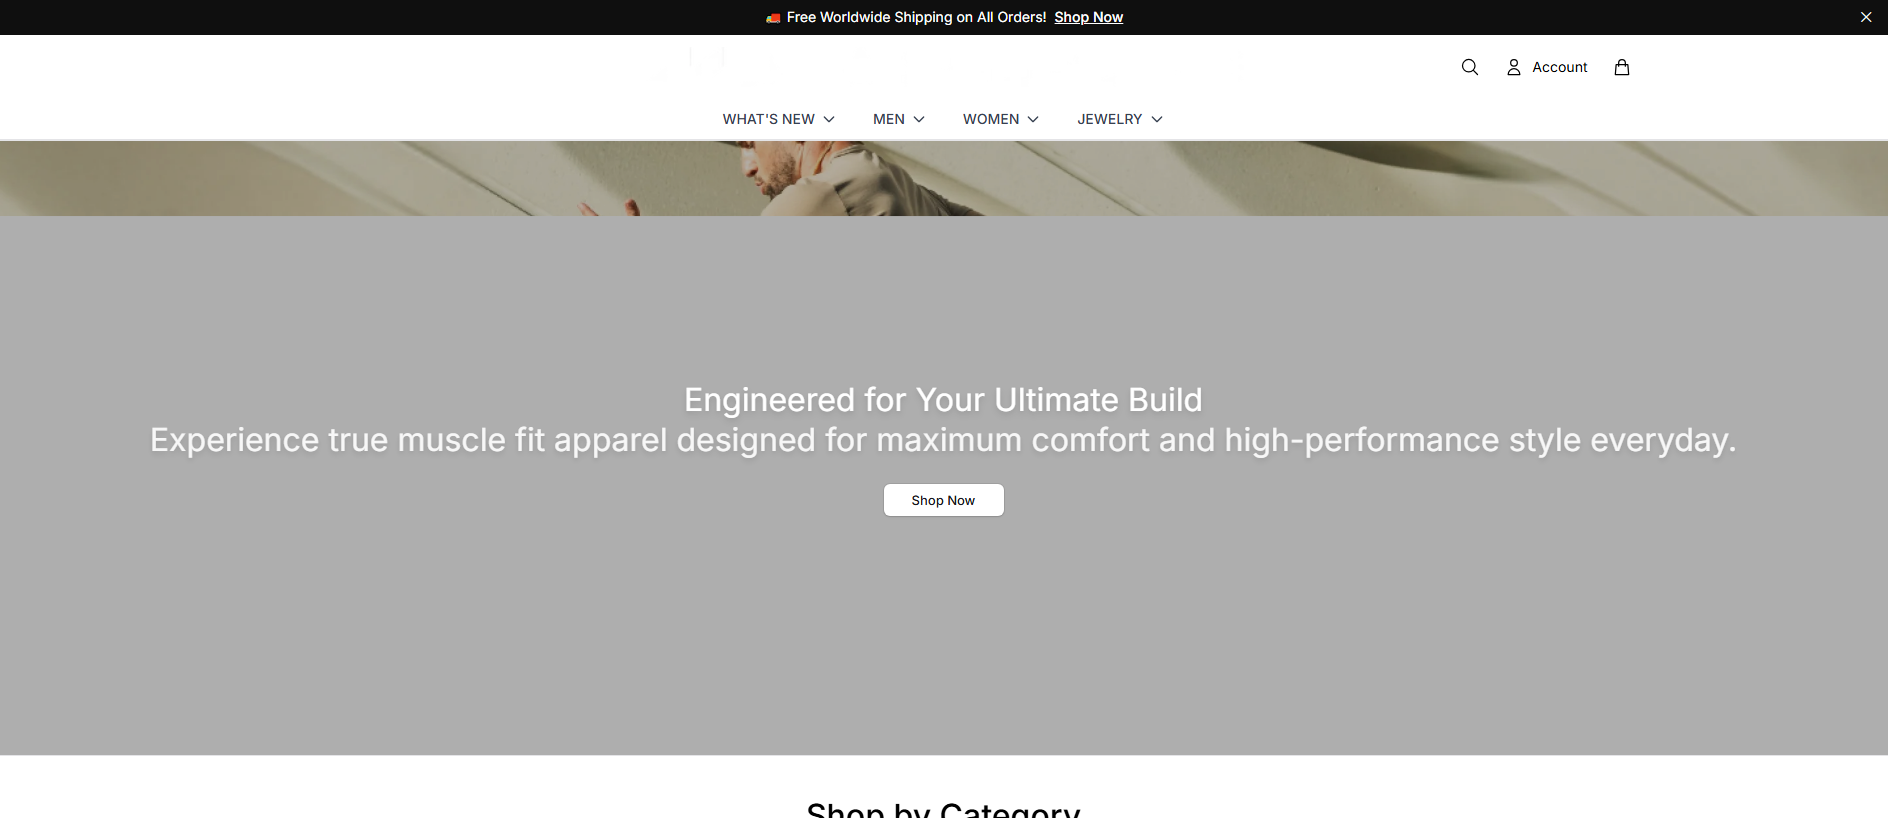
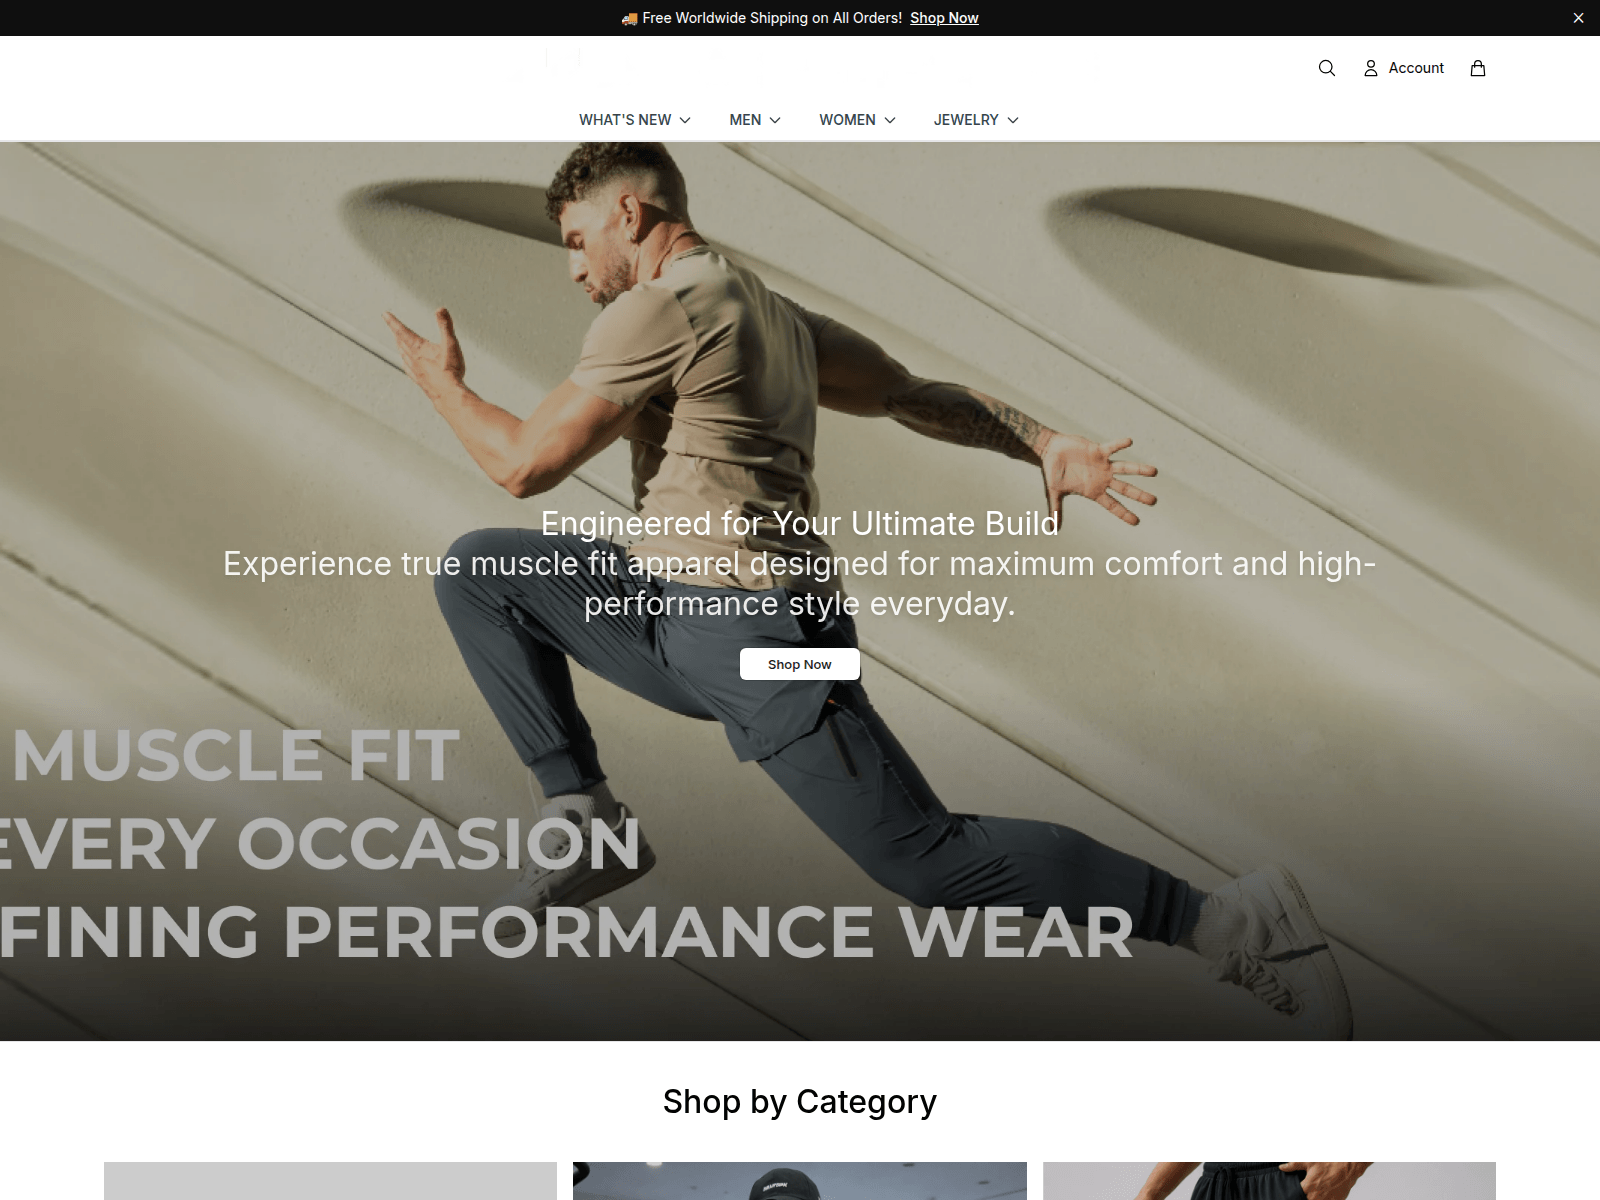
“AHA SELECTED | Best Muscle Fit Technical Apparel for Men | AHA SELECTED”

Registrar
Dynadot
Resolved IP
31.222.234.210
Registered
27/04/2026
Verdetto di minaccia Critico
Rilevamenti VirusTotal: 12/92 Simulazione del marchio: Fakeshop
OTX: 4 refs 25/09/2026 Fakeshop 1 Report Sent
API
Questo dominio è stato segnalato come dannoso
Motori di sicurezza che segnalano un rilevamento: 12. Prestare estrema cautela: non inserire credenziali o informazioni personali.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@dynadot.com. The latest stored availability evidence still shows the domain reachable; 16 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
16 days
Reports sent
1
Latest case ID
PD-20260925-D5A9FC
Current status
Observed active at latest stored check
Riepilogo del rapporto

ahaselectedboutique.shop — Non verificato. Simulazione del marchio: Fakeshop; Tipo di truffa: Impersonation. Riepilogo delle prove: VirusTotal 12/92 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); URLQuery 2 det.; URLScan malicious verdict; PhishDestroy score 98/100. Registrar: Dynadot.

L’analisi dettagliata di PhishDestroy AI resta in inglese per preservare il rapporto forense originale.

VirusTotal
VirusTotal
12 det.
URLQuery
URLQuery
2 det.
OTX references
URLScan
URLScan
Certificato TLS
Scaduto o non verificato
Età
6 mo
PhishDestroy
Elenco da eliminare
Presente
Reports Sent
1

Source evidence

7 sources

VirusTotal

12 / 92

Segnala

URLScan verdict

malicious

Segnala

OTX

4 community references

Segnala

CF Radar

provider verdict: clean

Segnala

URLScan capture

rapporto memorizzato

Stored URLScan capture preview
Segnala

Google Safe Browsing

Checked; no threat flag recorded

Segnala

Riepilogo delle prove

Critico
VirusTotal
12/92
OTX
4 community refs
URLScan
Stored capture

Assessment

As recorded on 2026-10-01, ahaselectedboutique.shop returned an HTTP 301 status during that check. The domain was first observed on 2026-09-25, and its registration date is listed as 2026-04-27.

Recorded Evidence

A VirusTotal check on 2026-09-27 recorded 12 detections across 91 scanners. An OTX check on 2026-09-27 recorded 4 pulses, while the PhishDestroy internal listing was also recorded as true. The registrar is listed as Dynadot Inc., and the SSL certificate issuer is Let's Encrypt / YE2, scanned on 2026-09-25. A PageSpeed check on 2026-09-25 recorded a performance score of 67.

Interpretation

The VirusTotal and OTX observations share the 2026-09-27 date, so those two sources can be compared directly, while the HTTP, PageSpeed and SSL records from 2026-10-01 and 2026-09-25 reflect different points in time. Because the observation dates differ, the PhishDestroy listing and the HTTP response describe separate snapshots rather than one continuous state. The named sources therefore allow comparison of recorded values across dates, not a single combined conclusion.

Recommended Actions

Anyone reviewing ahaselectedboutique.shop should retain the dated records from VirusTotal, OTX, PhishDestroy, PageSpeed and the HTTP check so later observations can be compared against them. Subsequent checks should be logged with their own dates before any change is assumed. During review, avoid submitting sensitive information to the domain until the recorded observations have been independently verified.

Analisi di rilevamento ed evasione

Verifica del cloaking e della distribuzione del traffico

Non ancora scansionato Non è stata ancora rilevata alcuna differenza tra crawler e browser

Osservazioni archiviate relative al confronto tra crawler e browser per questo host, oltre a una verifica in tempo reale delle impronte digitali per i sistemi di distribuzione del traffico in stile Keitaro.

Flag di occultamento memorizzato
Non ancora scansionato
Ultima scansione di occultamento

Nota dello scanner: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='ahaselectedboutique.shop', port=80): Max retries exceeded with url: / (Caused by NewConnec

Verifica delle impronte digitali in tempo reale TDS
Sette impronte digitali di Keitaro più un confronto tra crawler e browser, eseguiti dallo scanner PhishDestroy quando questa finestra è aperta.
In attesa

Acquisizione salvata · 2 captures

Titolo della pagina
AHA SELECTED | Best Muscle Fit Technical Apparel for Men | AHA SELECTED
Impersonates
Stripe
Certificato TLS
Hostname coverage not recorded · Emesso da Let's Encrypt / YE2 · stored validity ends in 42 days

Domain details

Dominio
URLScan Verdict Malevolo score 100 Phishing brand: Fakeshop report ↗
Reputazione IP abuse score 0/100 1 report Fraud Orders checked 25/09/2026
OTX Tags 2026-09activeall-domainsblocklistcontentcryptodominidrainerfraudlivemonthlyphishdestroyphishingscam
Registrar Dynadot (Unknown)
RegistrazioneCreato 27/04/2026 (167d) — Expires 27/04/2027
Dettagli tecniciProvenance & timestamps
Rilevato per la prima volta25/09/2026
DOM Analysisanalyzed 09/10/2026score 98/1001 brand signal
Submitted URLhttps://ahaselectedboutique.shop/
Favicon Hash
ID del caso
ICANN OVERSIGHT

Accreditamento e contesto RAA

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Nulla viene inviato automaticamente.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
31.222.234.210
Network ASN
AS199242
Organization
Beijing Ruihao Kai Yuan Technology Co., Ltd
Observed location
Los Angeles, US
Server header
Caddy

Nameserver 2

  • amos.ns.cloudflare.com
  • millie.ns.cloudflare.com

Location describes the IP network.

Certificato TLS

Issuer
Let's Encrypt / YE2
Valid from
2026-08-24 17:54:34
Valid until
2026-11-22 17:54:33
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 04:03:35 UTC
Collection source
PhishDestroy collector
Certificate fingerprintf002c273e92ba73e918463c2b33af508f1e1cee15d6a4780c07c24d46a66ac23

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 31.222.234.210rapiddns.io

Latest Classified Outcome 2026-10-11 01:44:15 UTC

Primary outcome Contenuto attivo reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Contenuto attivo Ordinary HTTP content served 90% 2026-10-11 01:44:15 UTC
RDAP registration Sconosciuto
Observed timeline last reachable: 2026-10-11 01:44:15 UTC last content: 2026-10-11 01:44:15 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Tecnologie · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
Segnala questo dominio Invia le prove e contribuisci a proteggere gli altri

Analisi di VirusTotal

12 / I fornitori di sicurezza 92 hanno contrassegnato questo dominio
View on VT
Last analyzed First positive detection Previous stored snapshot: 12 detections
alphaMountain.ai
BitDefender
CRDF
ESET
Forcepoint ThreatSeeker
G-Data
Gridinsoft
LevelBlue
Lionic
Netcraft
SOCRadar
Webroot

Prove archiviate

Wayback Machine Snapshot
È disponibile un'istantanea storica per la revisione delle prove
View Archive
Analisi delle prestazioni del sito

Google PageSpeed Insights — mobile performance audit of ahaselectedboutique.shop · checked Sep 25, 2026

67
Needs Work
Performance
FCP
2.86s
First Contentful Paint
LCP
5.41s
Largest Contentful Paint
CLS
0.029
Cumulative Layout Shift
TBT
363ms
Total Blocking Time
SI
2.86s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-09-25 05:55:02 UTC
    VirusTotal scanner detections updated from 11 to 12. Added scanner alerts: SOCRadar.
  2. Threat First Observed 2026-09-25 00:12:49 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 31.222.234.210.

Pipeline di risposta alle minacce

Scoperta
Analysis
Notifications
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Minaccia rilevata
ahaselectedboutique.shop rilevati e inseriti in coda per un’analisi completa
25/09/2026
URLScan.io Capture
Memorizzato URLScan report with capture artifacts
25/09/2026
URLScan Verdict
URLScan returned a malicious verdict · score 100
25/09/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
29/09/2026
VirusTotal
12/92 recorded on VirusTotal
07/10/2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
27/09/2026
Brand Impersonation
Impersonation of Fakeshop
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
25/09/2026
Technical Analysis Recorded
Il report contiene tecnologia archiviata o risultati di analisi forensi.
11/10/2026
VT Detection +1
+1 new detection (11 → 12): SOCRadar
25/09/2026
Sent Report Recorded
Stored outgoing record associated with registrar Dynadot Inc., 2 abuse contacts
abuse@dynadot.comabuse@rashost.com
25/09/2026
DestroyList pubblicato
25/09/2026
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Dati e relazioni esterne

Istantanea delle prove inviate
Sent: Ledger records: 1 Case ID: PD-20260925-D5A9FC Recipient: abuse@dynadot.com
Page title stored with report: AHA SELECTED | Best Muscle Fit Technical Apparel for Men | AHA SELECTED
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 159.3 KB
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Analisi approfondita

Questo sito ti ha influenzato in qualche modo?

6 evidence signal groups linked 1 reports recorded Non verificato
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Se hai inserito credenziali dell'account, informazioni personali o di pagamento oppure hai scaricato un file da questo dominio, agisci immediatamente. Di seguito sono riportate le risorse per aiutarti a segnalare l'incidente e proteggerti.

Europol
Trova il canale di segnalazione ufficiale per il tuo paese dell'UE
National police directory
Attenzione ai truffatori che promettono il recupero dei fondi! I criminali possono contattare nuovamente le vittime fingendo di essere investigatori, avvocati o agenti di recupero. Non pagare commissioni anticipate né condividere credenziali. Scopri di più sulle frodi relative ai sussidi di recupero →

Segnalalo alle autorità locali

Seleziona il tuo Paese per ottenere contatti ufficiali del crimine informatico o creare una bozza di reclamo →.

Elenco di 97 paesi

Template-based draft · optional AI wording assistance requires separate consent

Bozza assistita dall'intelligenza artificiale: i dettagli dell'incidente vengono elaborati dal fornitore di intelligenza artificiale · Controllalo e invialo tu stesso

Verifica qualsiasi dominio

Analisi delle minacce utilizzando blocklist archiviate, WHOIS, DNS e prove di scansione pubblica

Scansiona ora

Segnala un tentativo di phishing

Segnala i domini sospetti al nostro database delle minacce — proteggi la comunità

Segnala

Feed in tempo reale sulle minacce

Segnalazioni recenti di phishing e modifiche osservate della disponibilità

Monitora

Rimani informato, rimani al sicuro

Controlla le minacce in tempo reale oppure contesta questa segnalazione se ritieni che si tratti di un falso positivo
Feed in tempo reale sulle minacce Contesta questo annuncio
HTML · IFRAME

Incorpora questo rapporto

Condividi queste informazioni sulle minacce sul tuo sito web o sul tuo blog

embed.html
<iframe
  src="https://phishdestroy.io/it/embed/domain/ahaselectedboutique.shop"
  title="PhishDestroy threat report for ahaselectedboutique.shop"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>