
Cerca i domini monitorati ed esamina le prove archiviate, i rilevamenti e gli ultimi dati relativi alla disponibilità osservata.
Cerca nei rapporti salvati. Questa azione non invia una segnalazione. L’assenza di un record non significa che il dominio sia sicuro.
232,387
Totale monitorato
226,566
VT rilevato
93,668
Ultima visualizzazione: attivo
138,719
Non disponibile all'ultimo controllo
8
VT In attesa di conferma
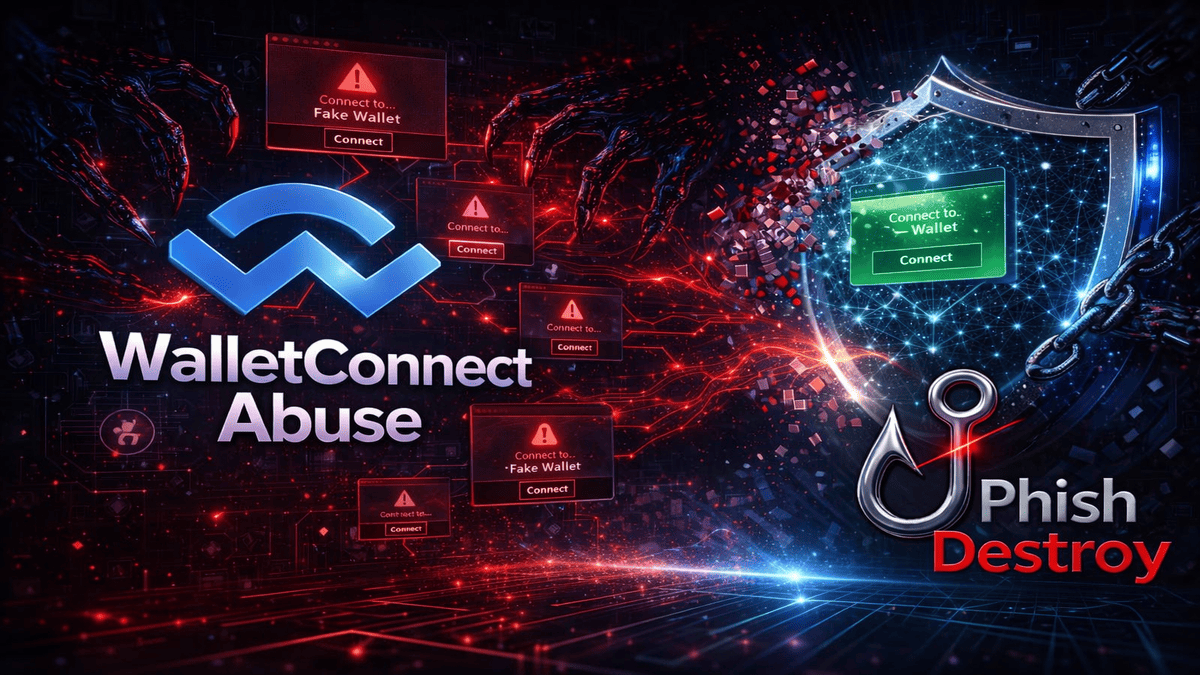
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domini
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malizioso Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analisi
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastrutture-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Truffa (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Richieste for private keys or seed phrases
Unexpected transaction requests
Povero website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1 Always verify domain authenticity
2 Enable two-factor authentication
3 Use hardware wallets for transactions
4 Regularly update security software
5 Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 597 domains tracked for this threat type
WalletConnect Abuse 597 domains


duplicate-disabled-6924.invalid

earn-plasma.to
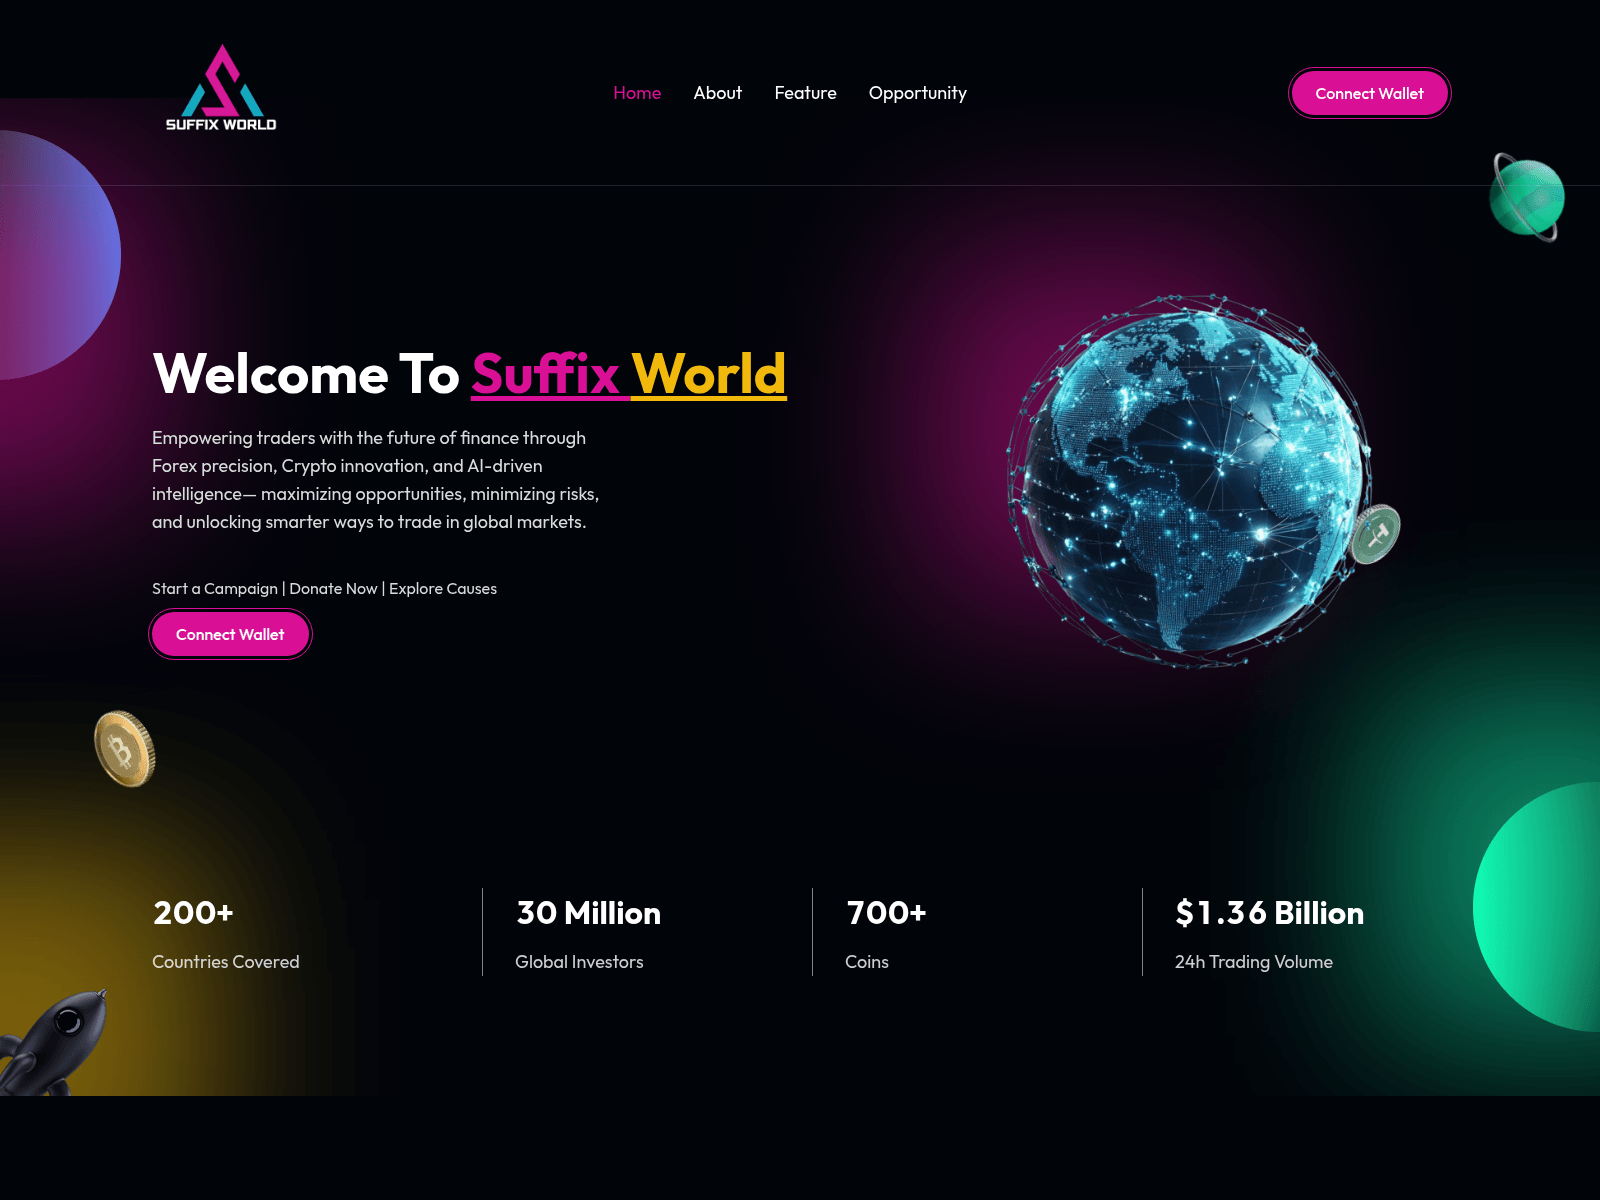
freshcenterr986.store

getpol.org

houdinizwap.com

hyperliquid.com-api-gateway-v1-gateway-dex.cloud

iucim.com

launchpol.com

mail.asssiterr.network

mailer.token2049.cyou

myneighborealice.xyz
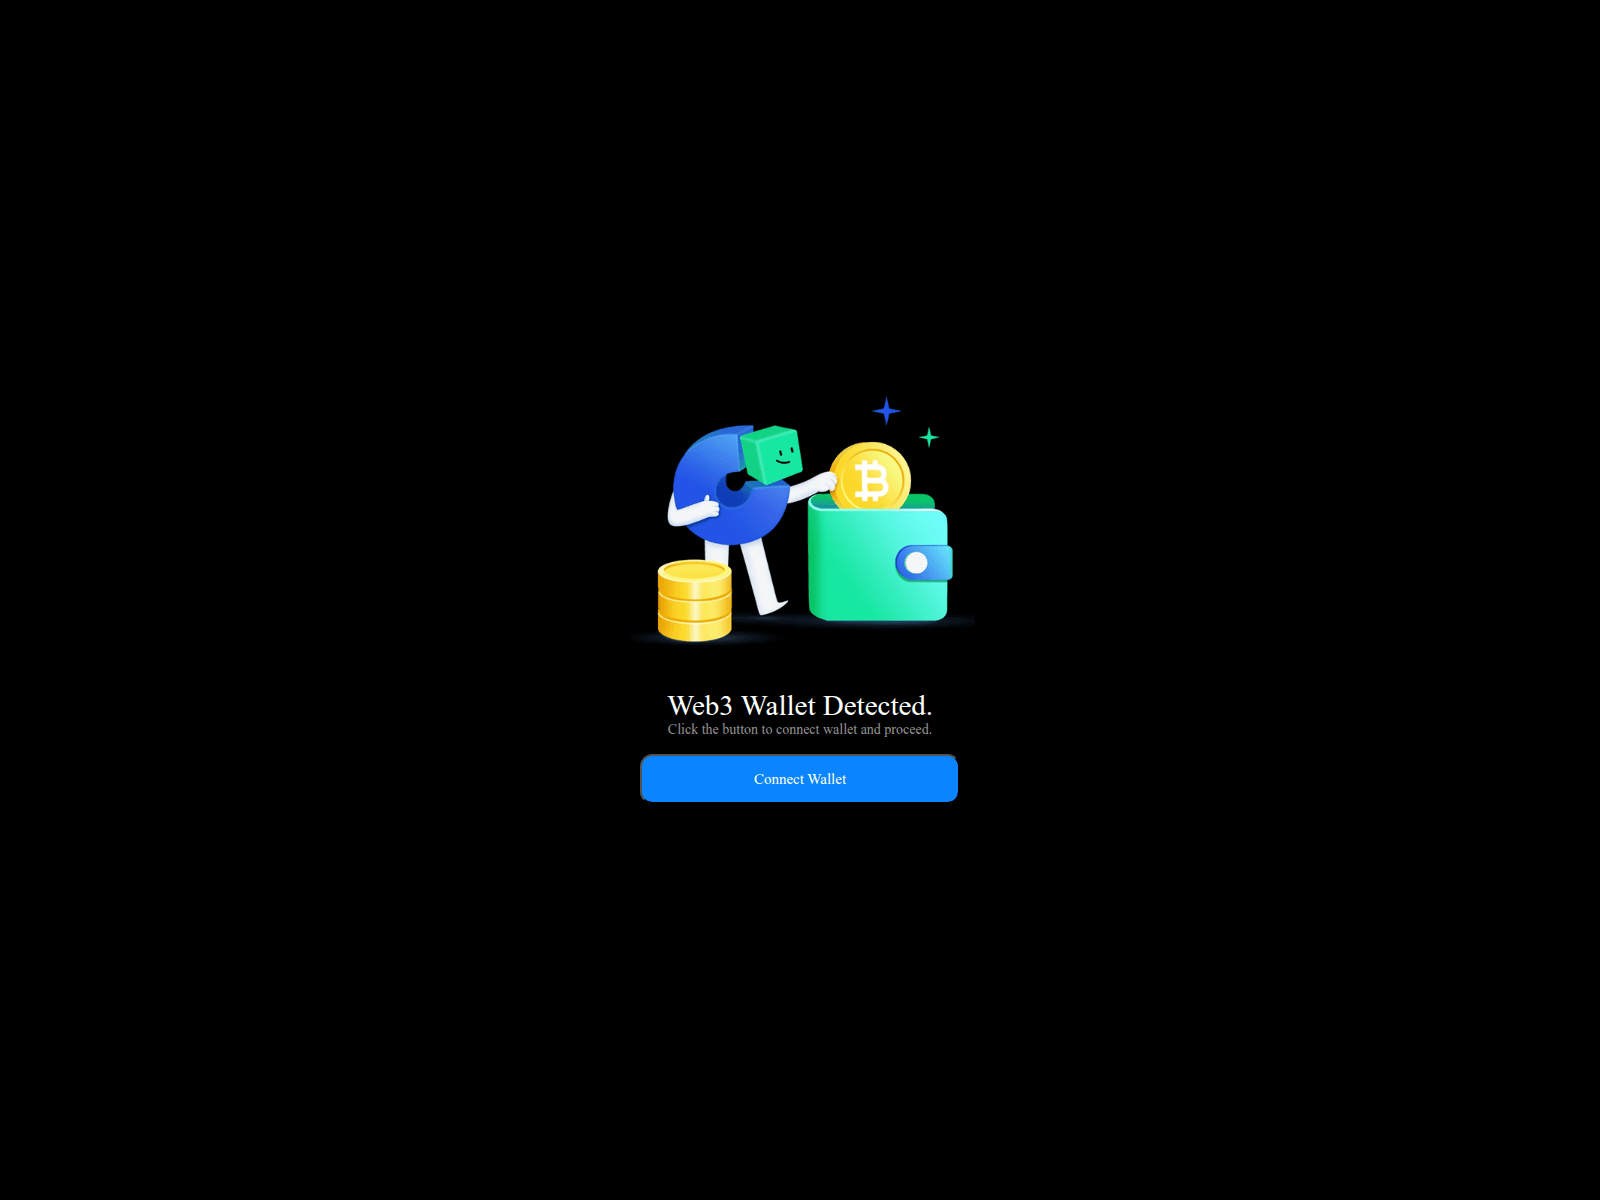
mztrn.com
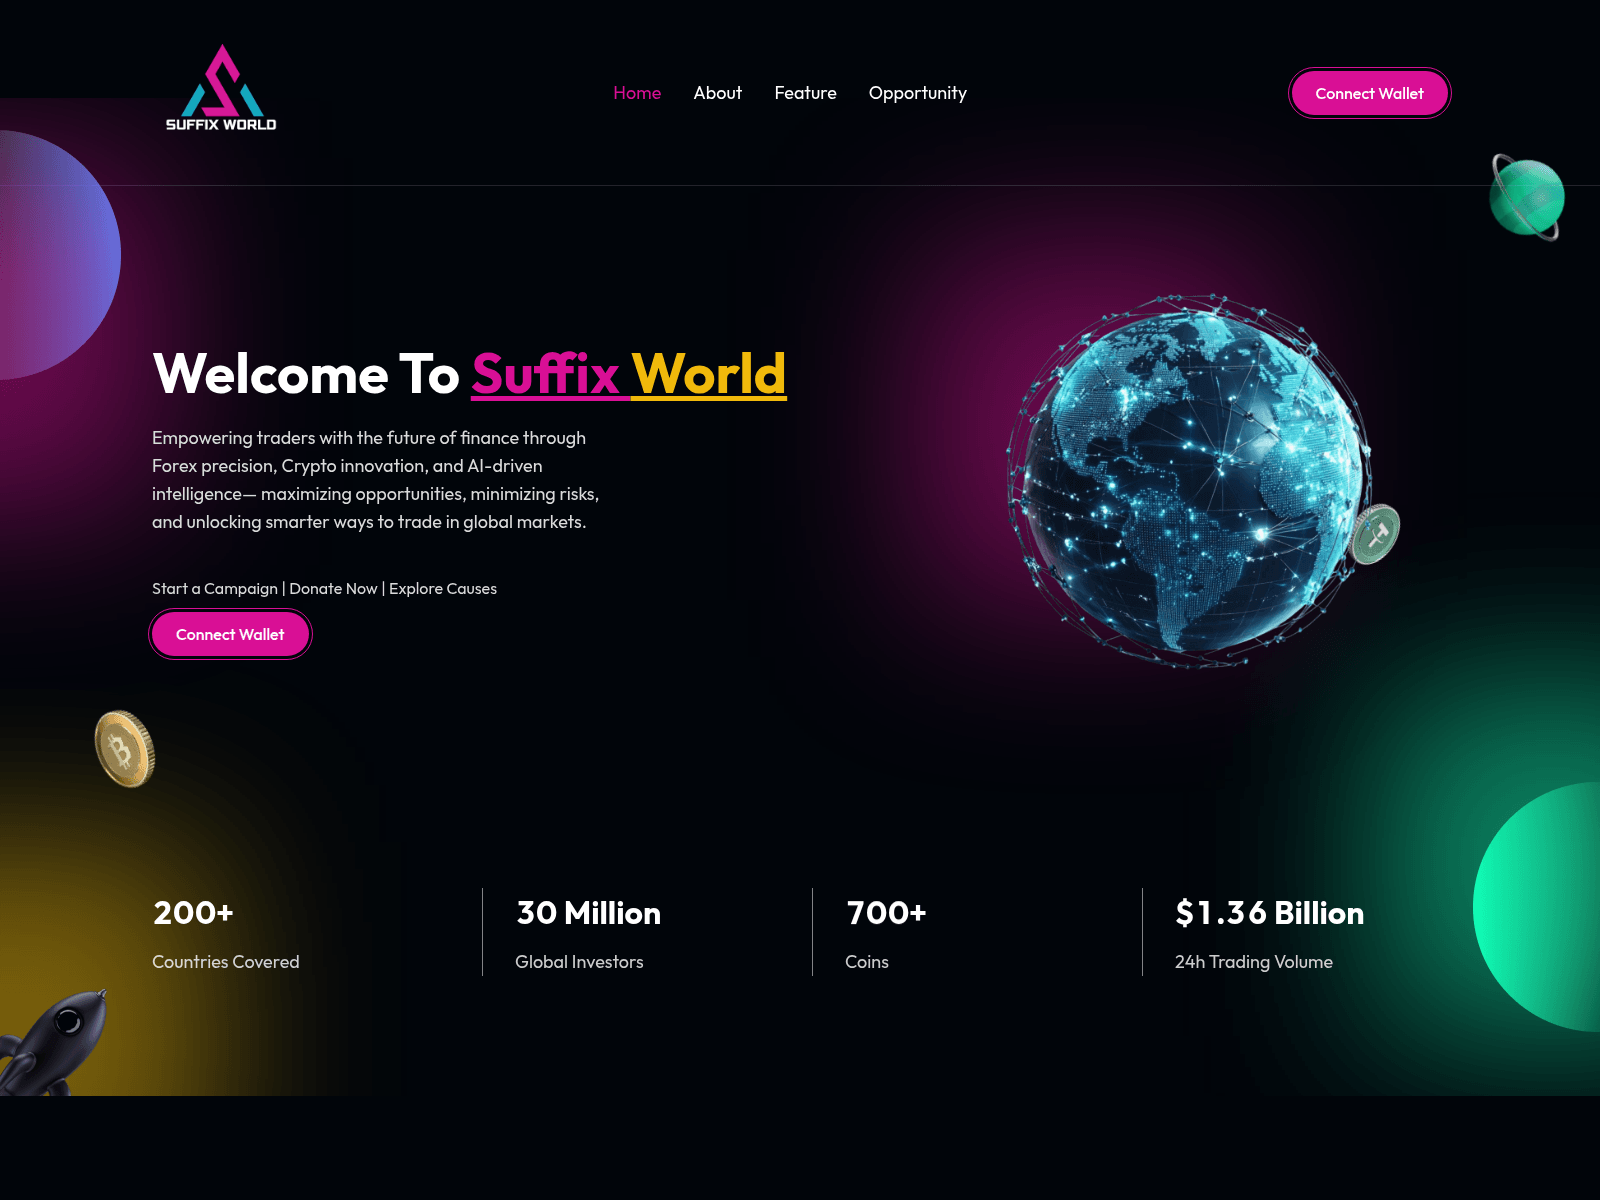
neatmarkett639.store

netcoins.shop

obtain-pol.com

onchain-crypto-max.cc
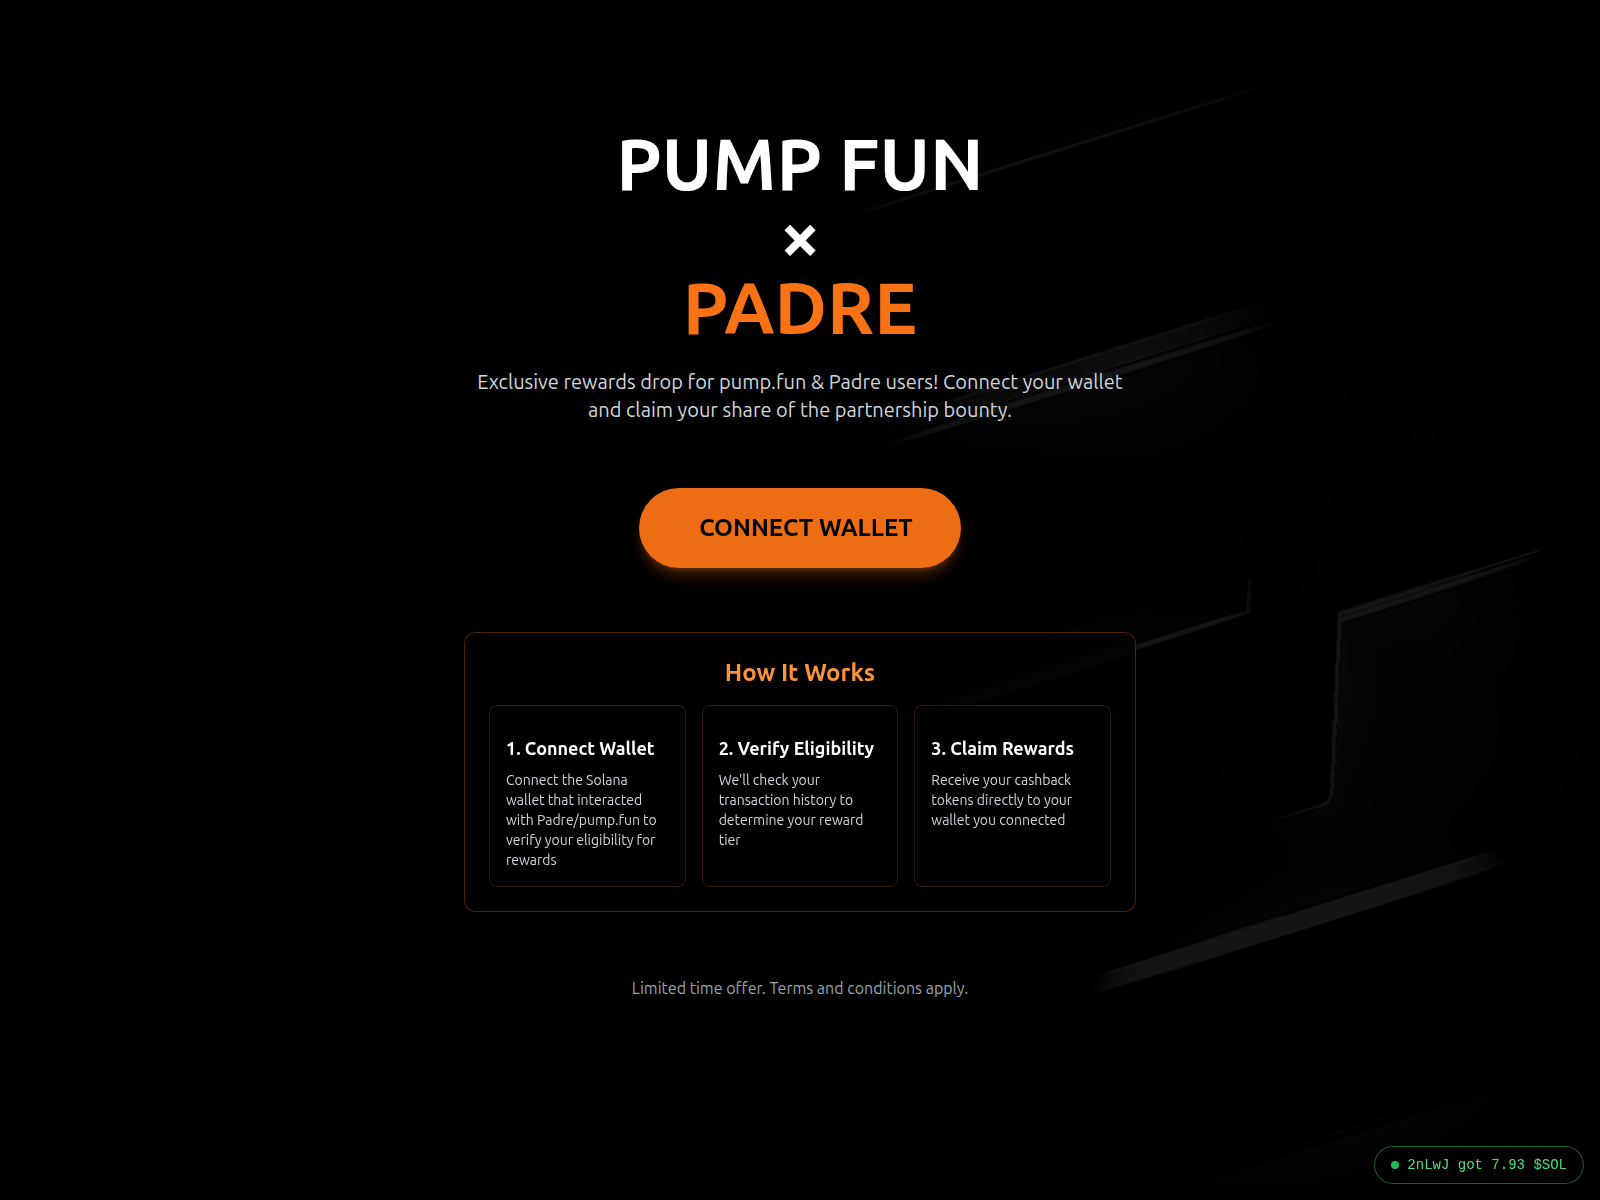
padreterminal.fun

pengunow.fun
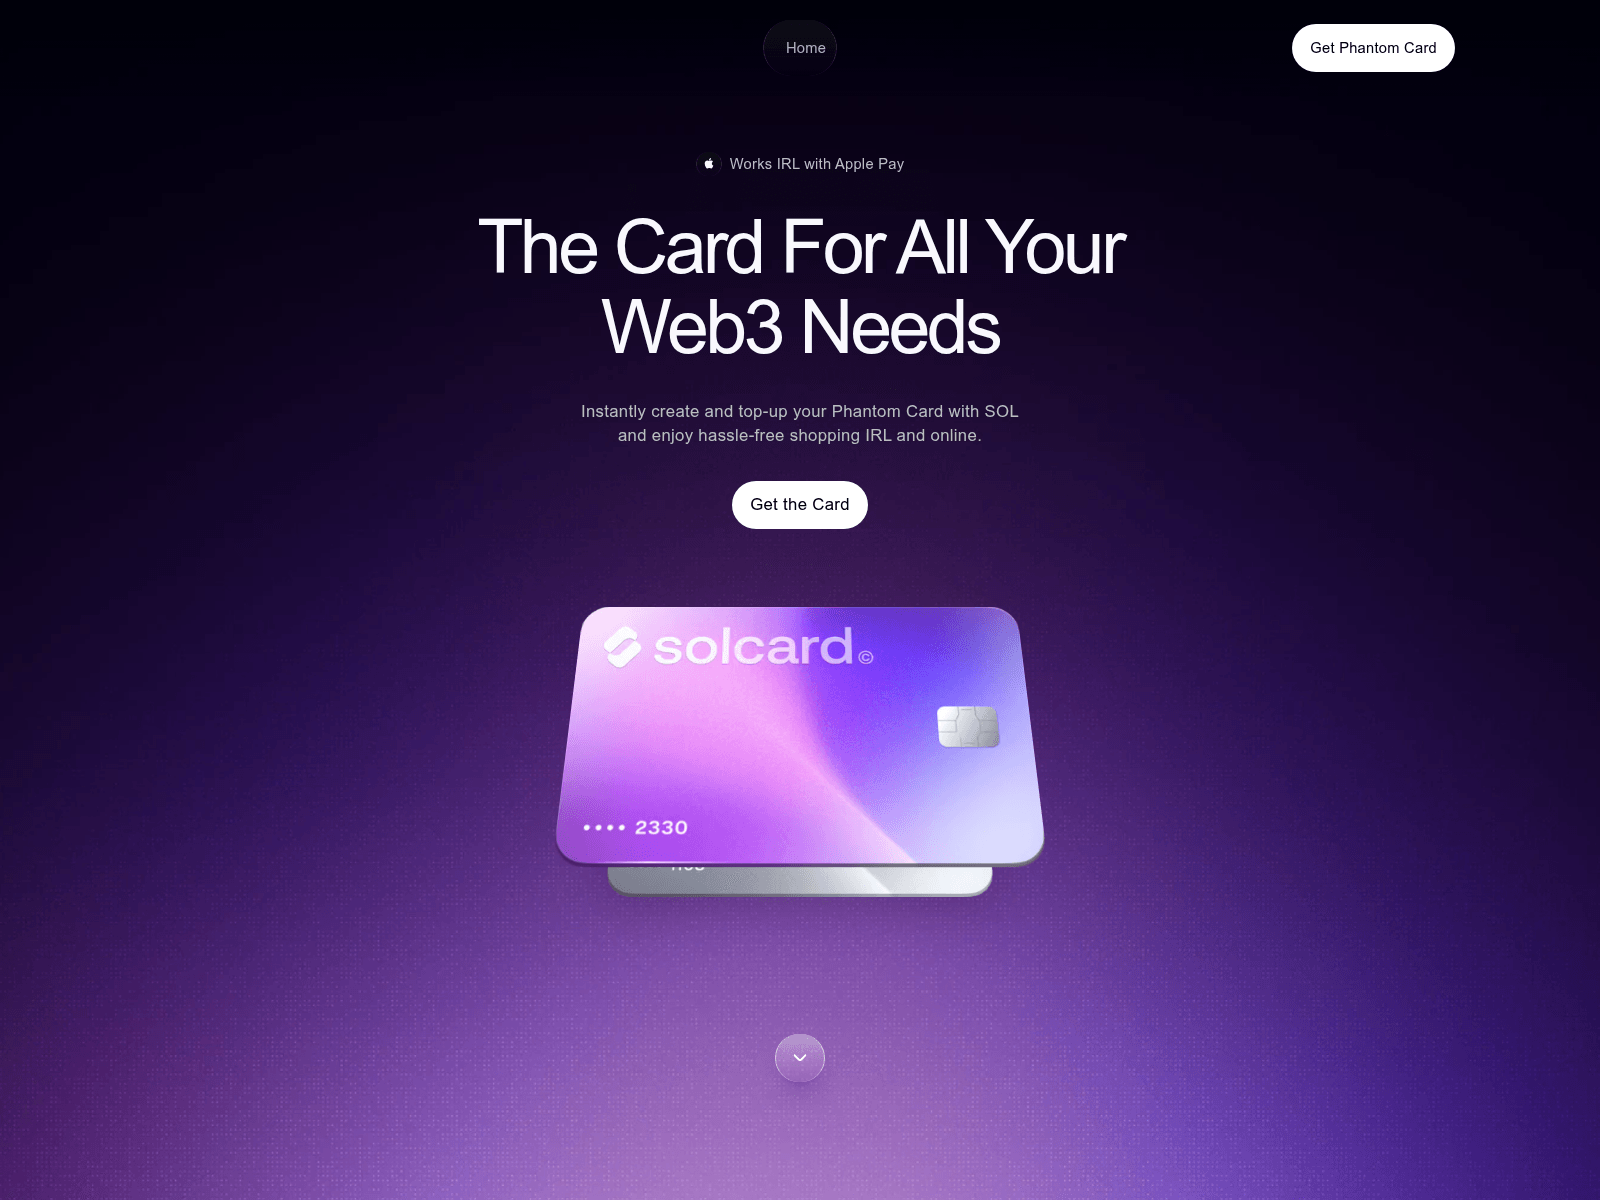
phantomcard.digital
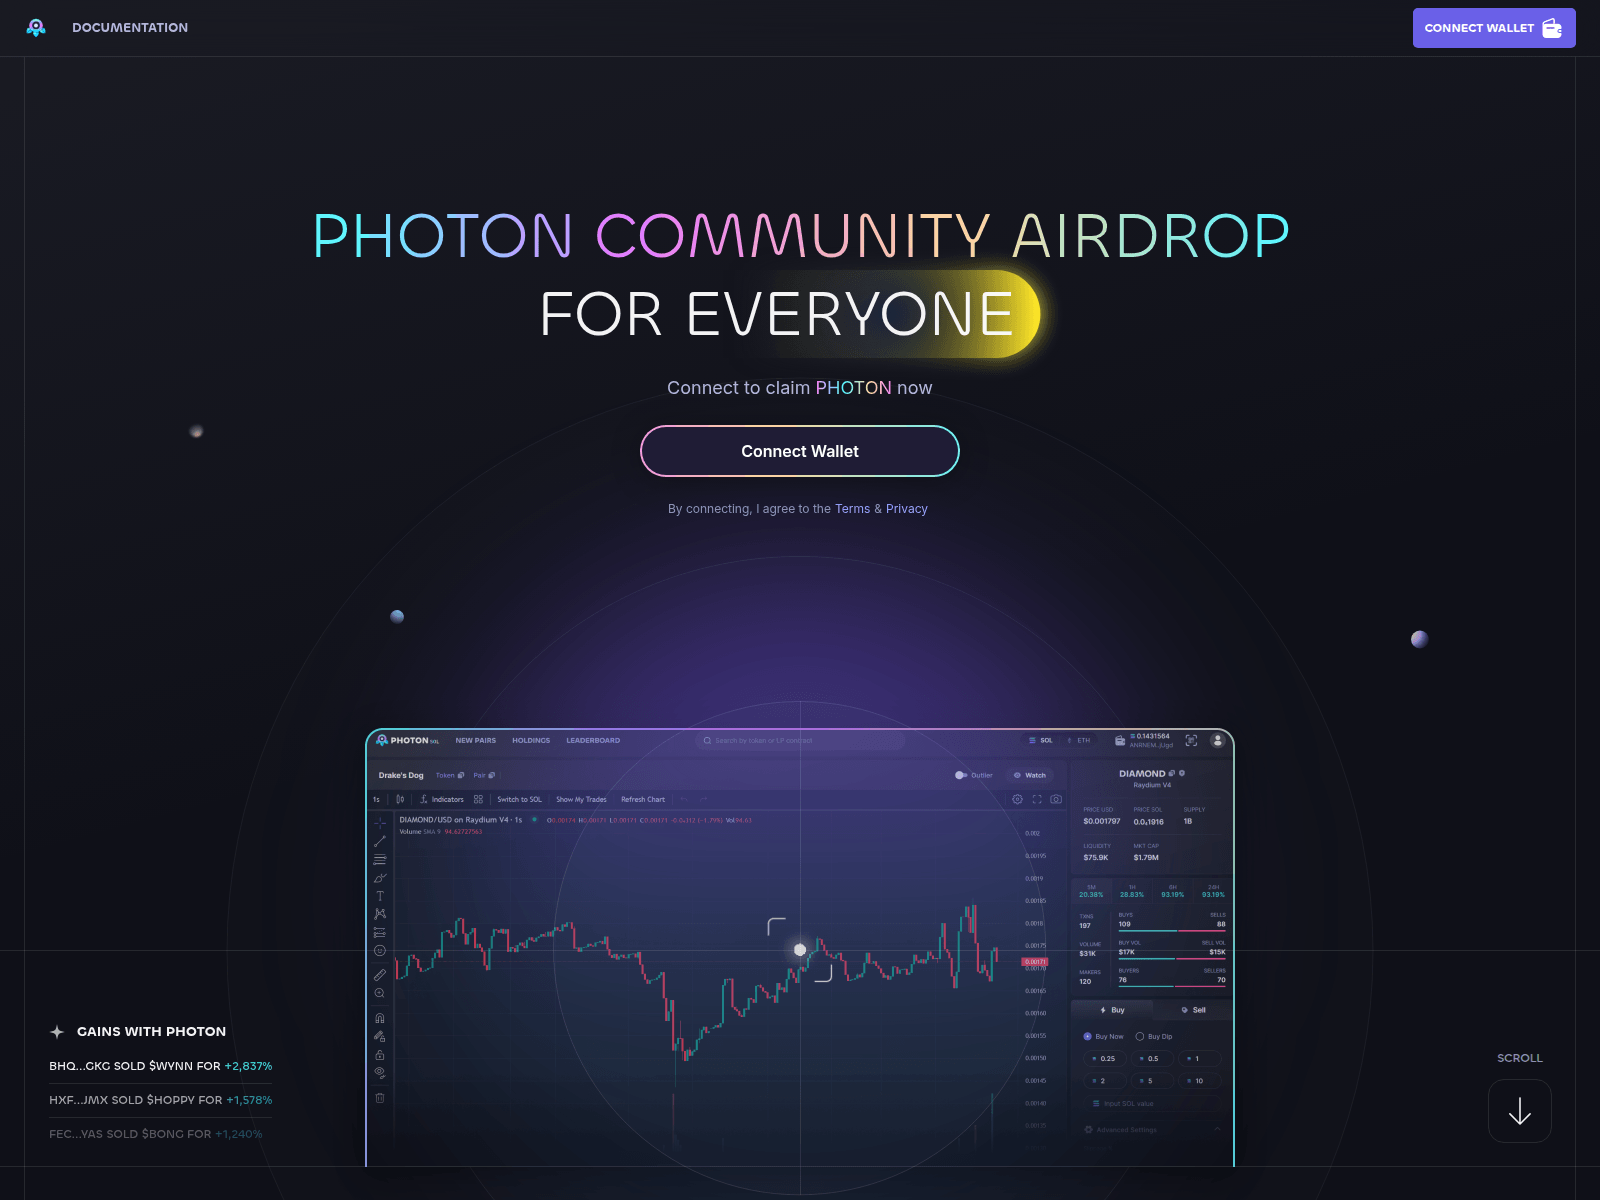
photon-sol.my
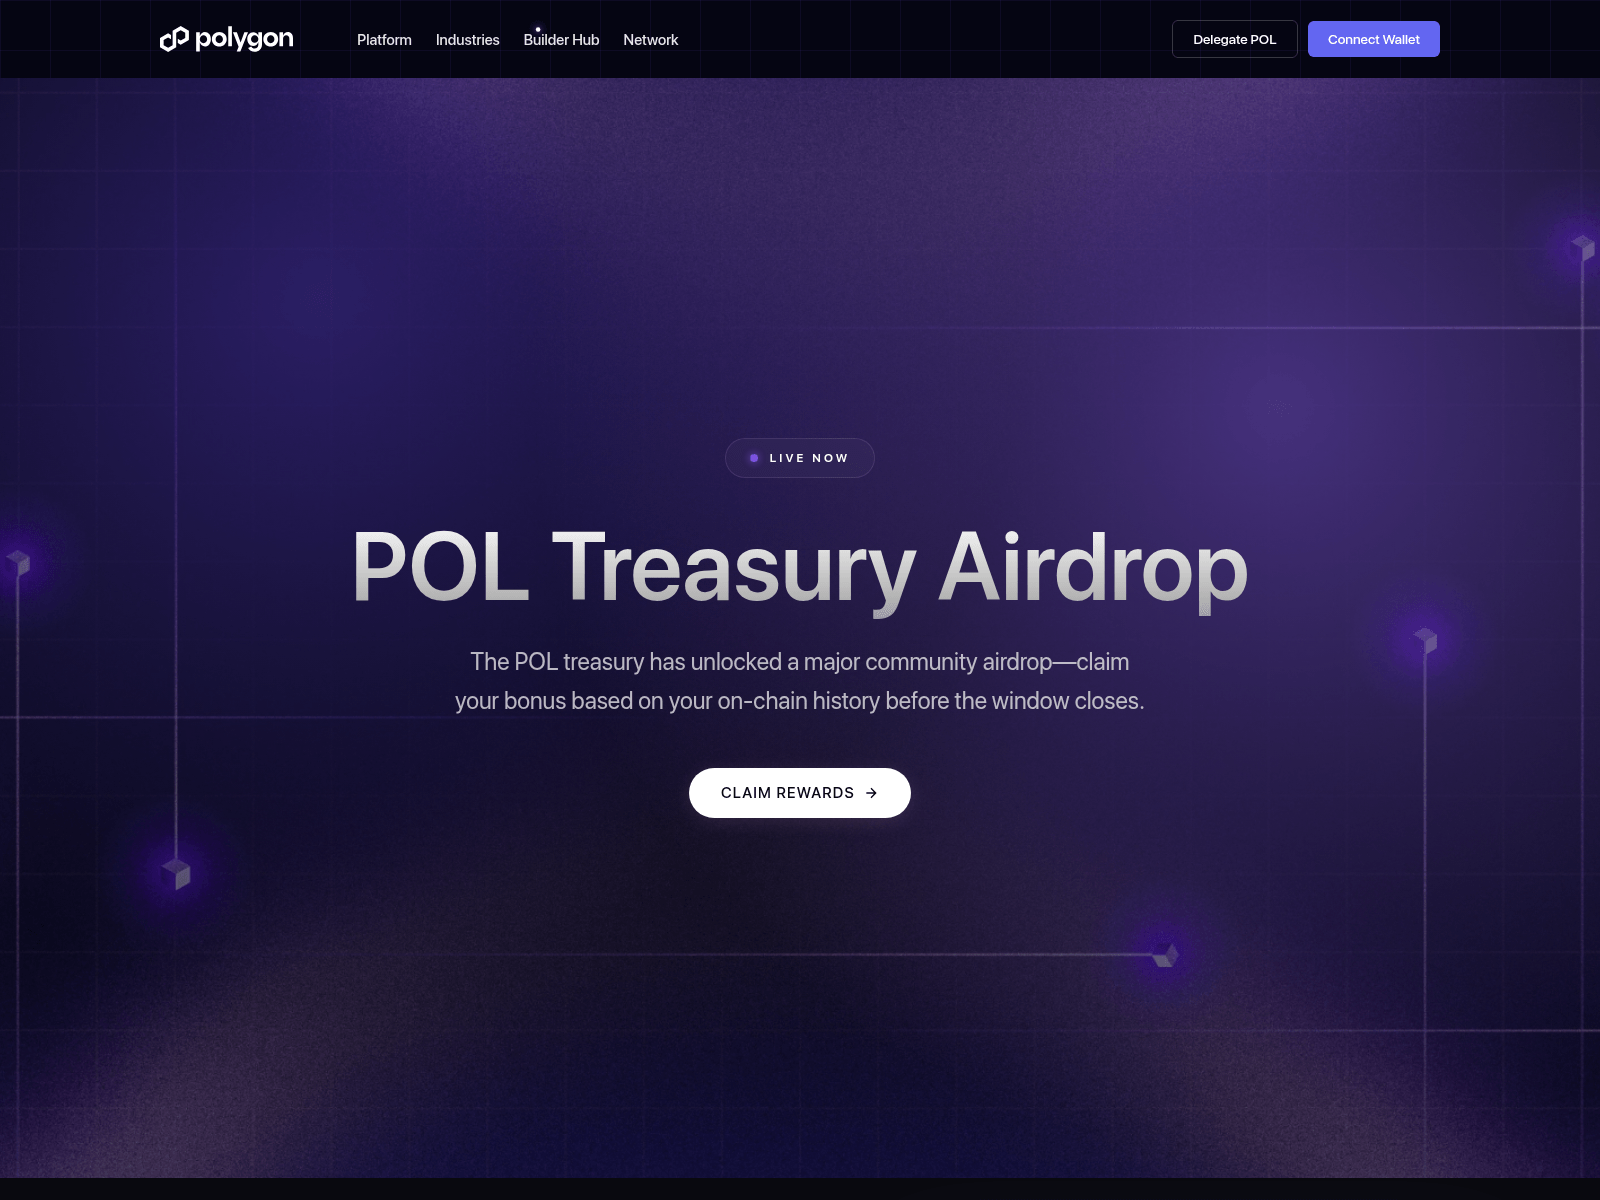
poldrop.org

pumpax.fun

pumpeve.fun

pumpox.fun
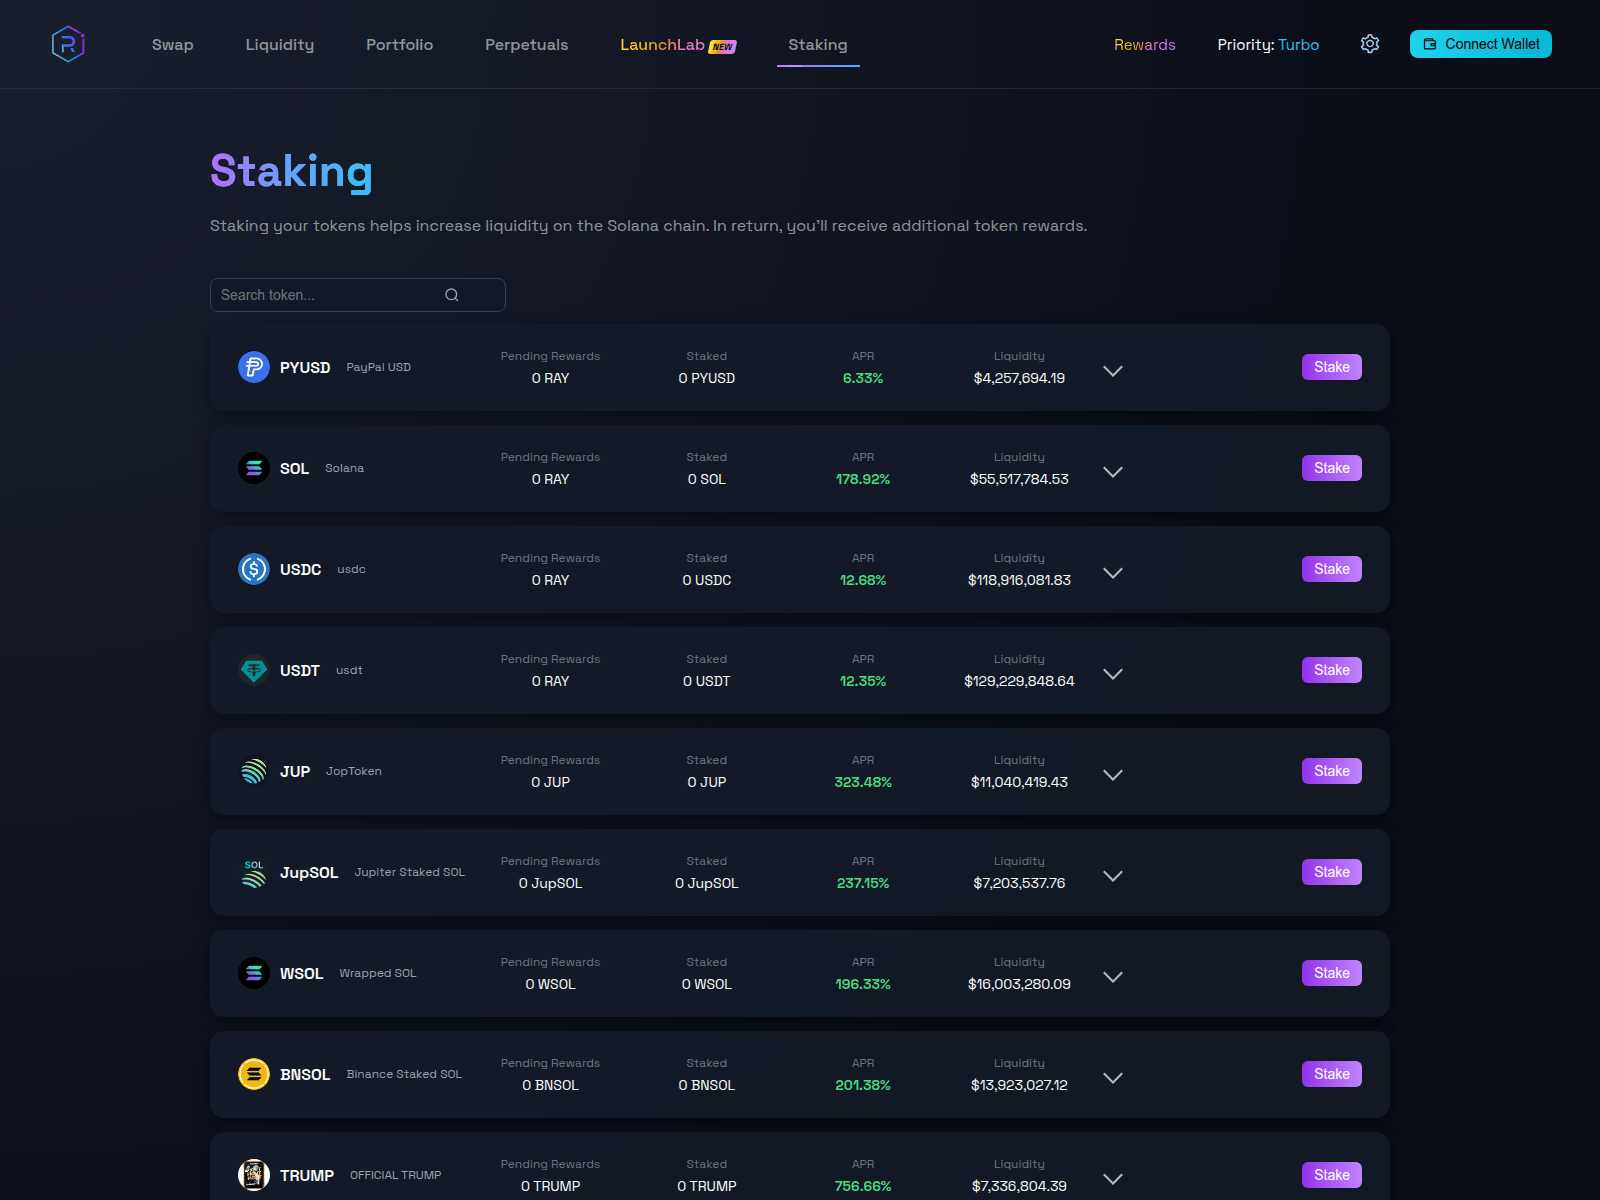
ray-dium.lat

rucds.com

rzmju.com

shiba-event.net

so-promotion.org

sol-starting.com
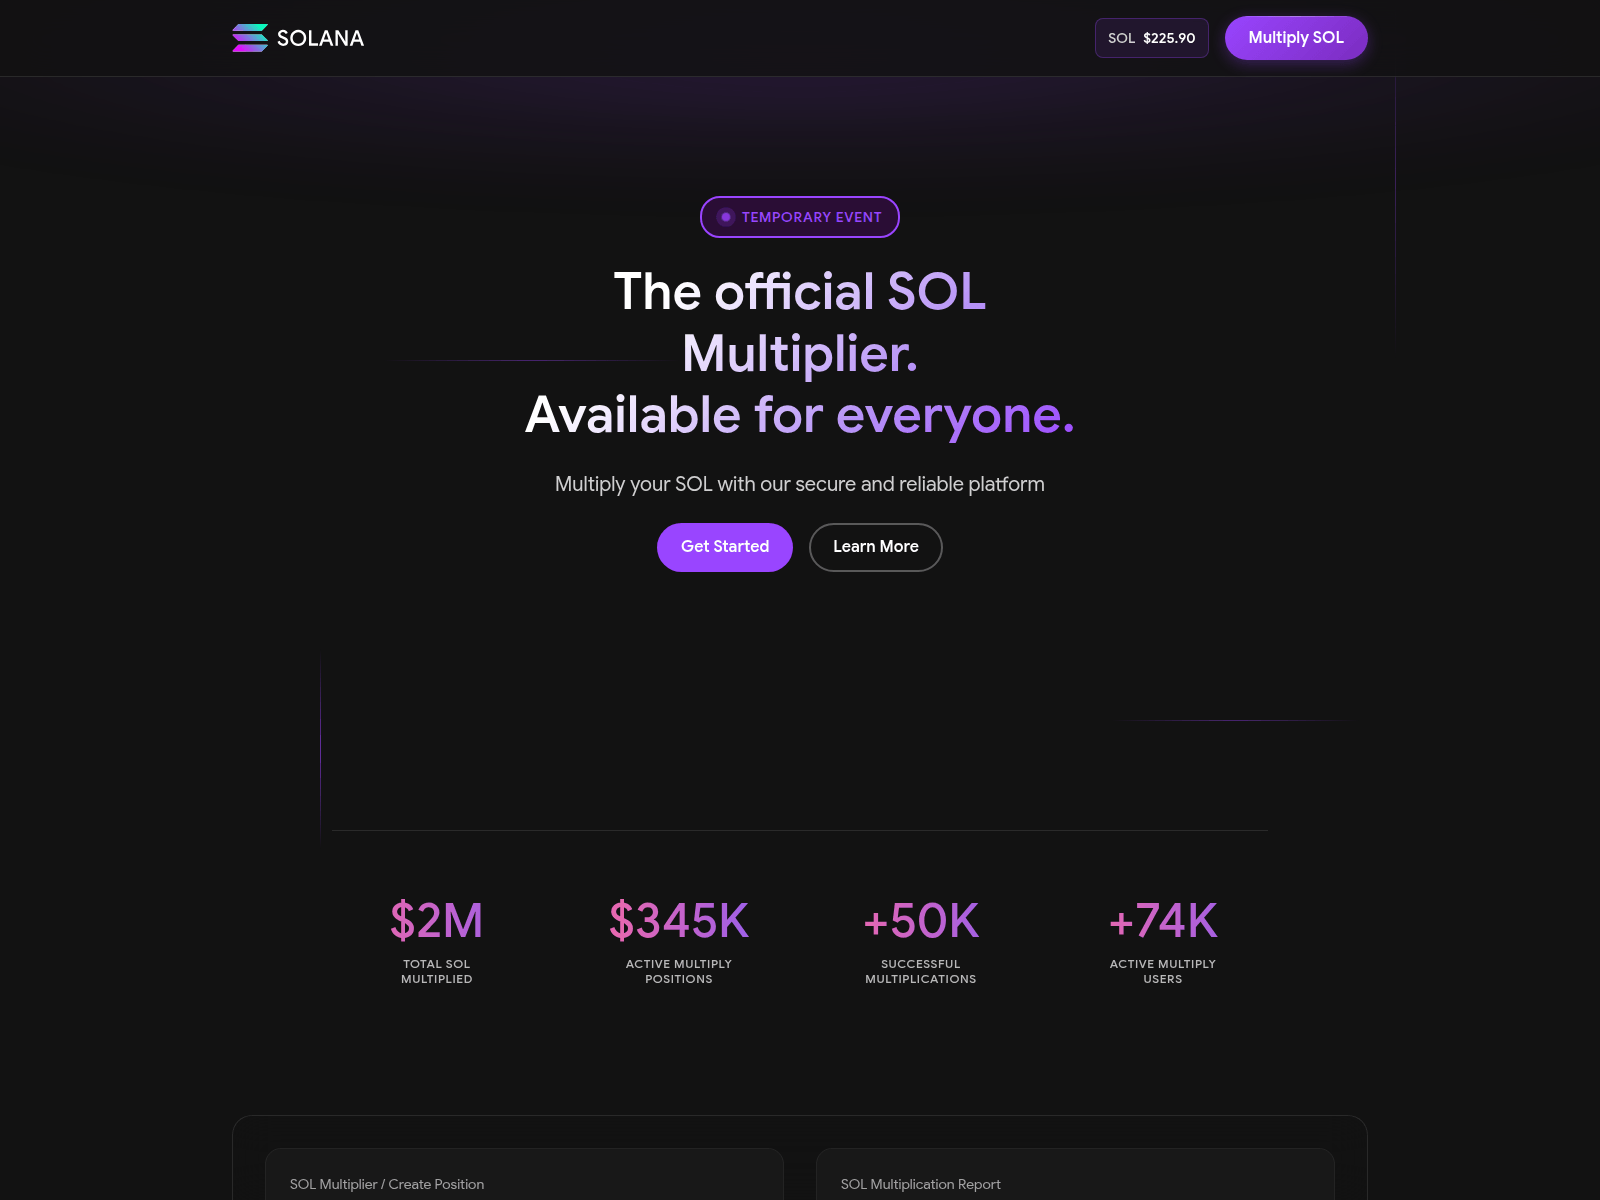
solana-box.top
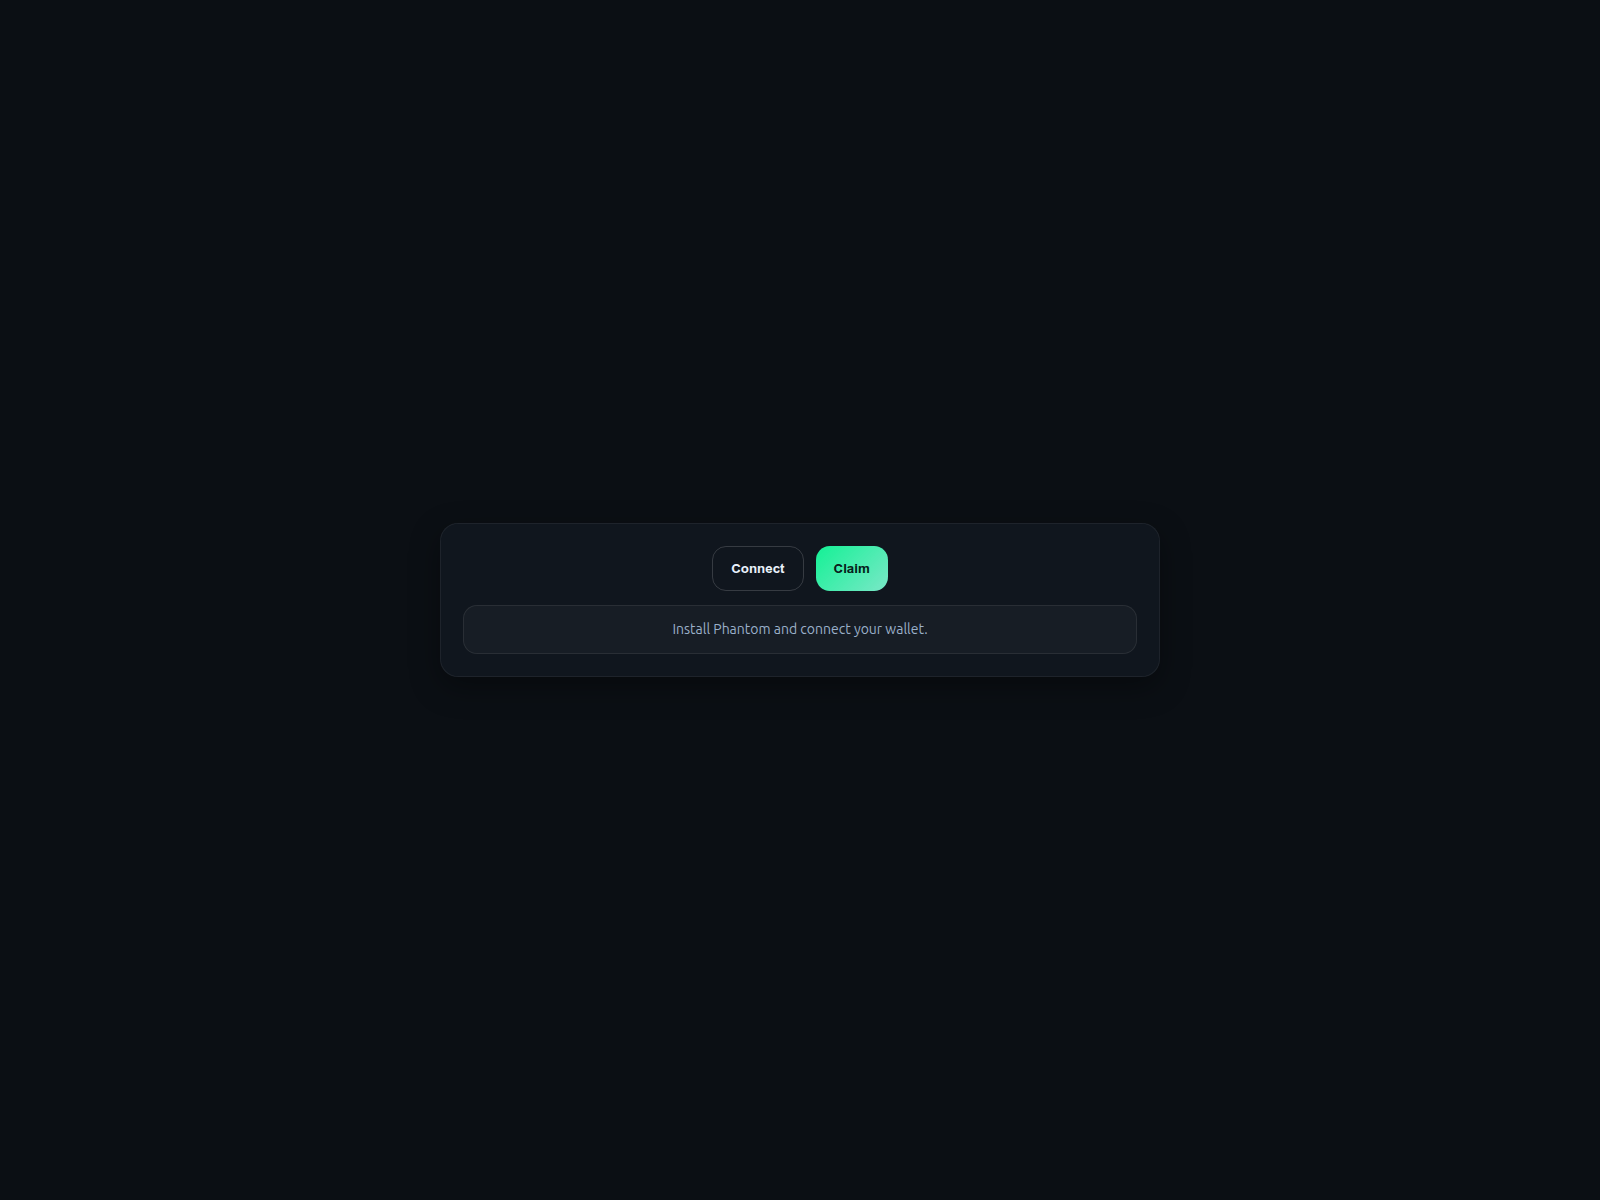
solfun.in

sollmeme.fun
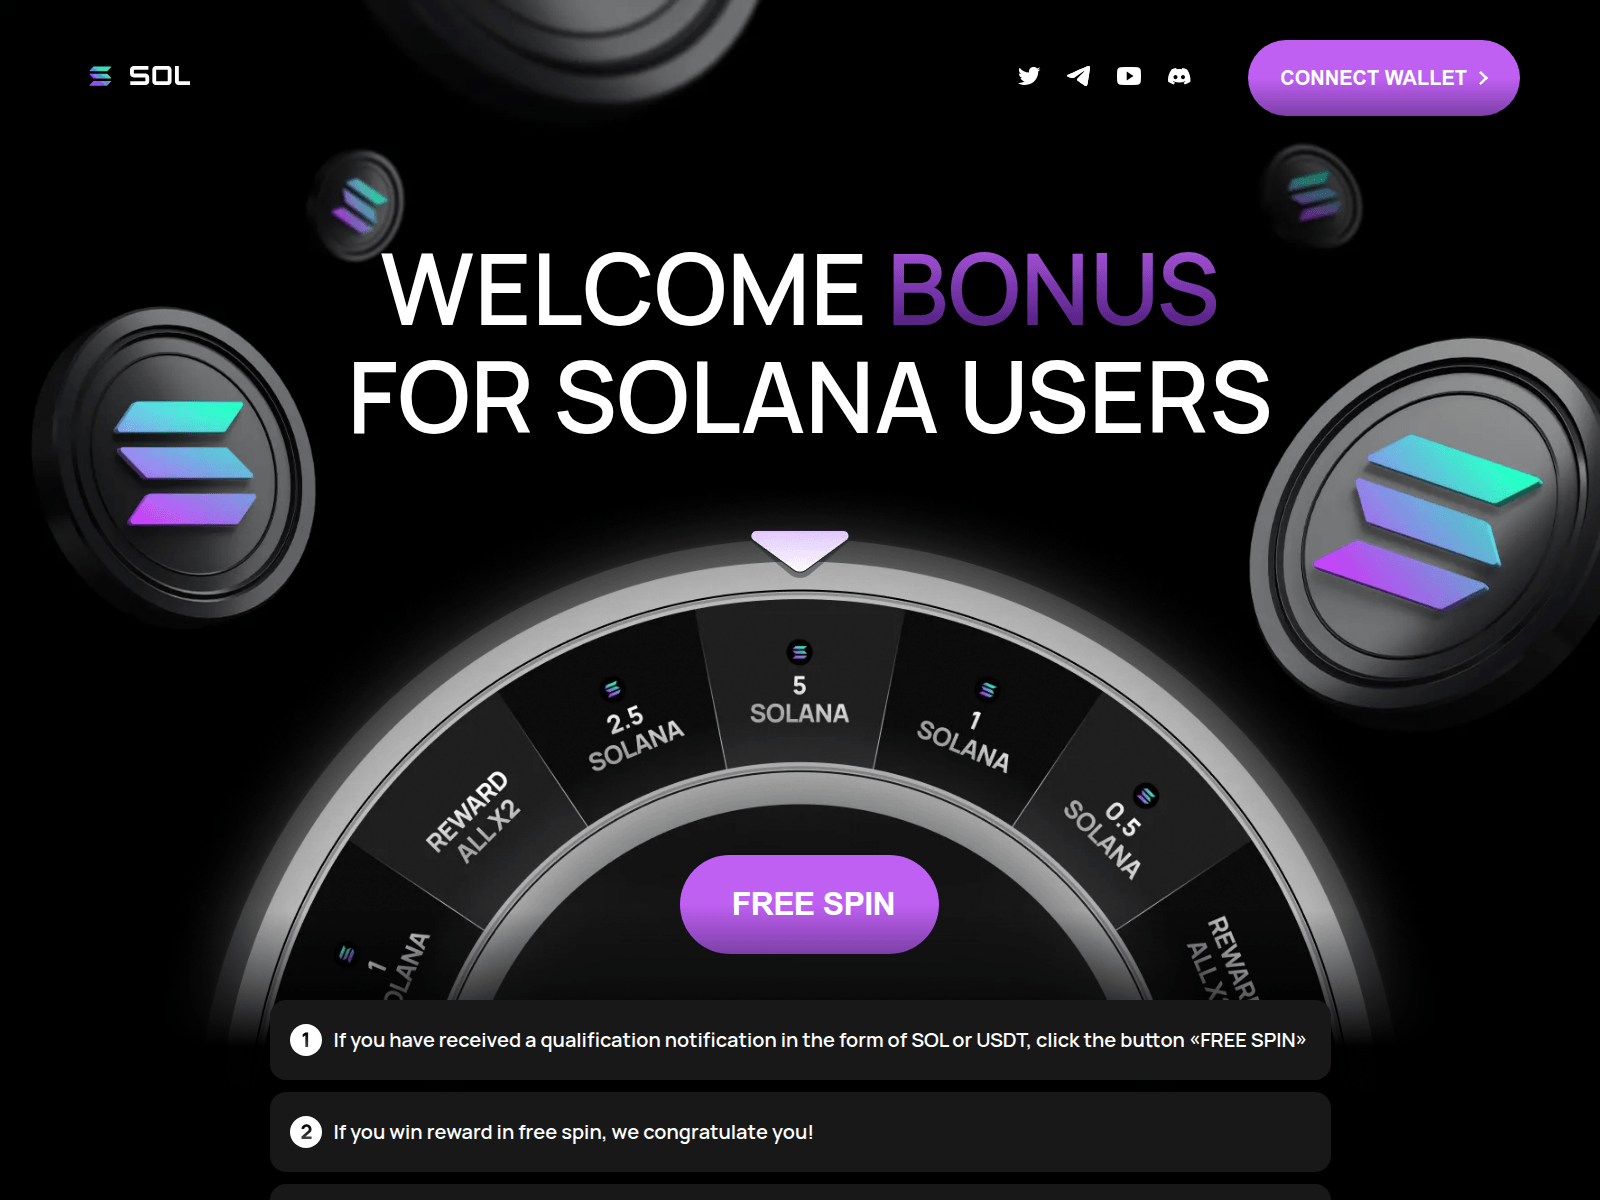
solnana.info
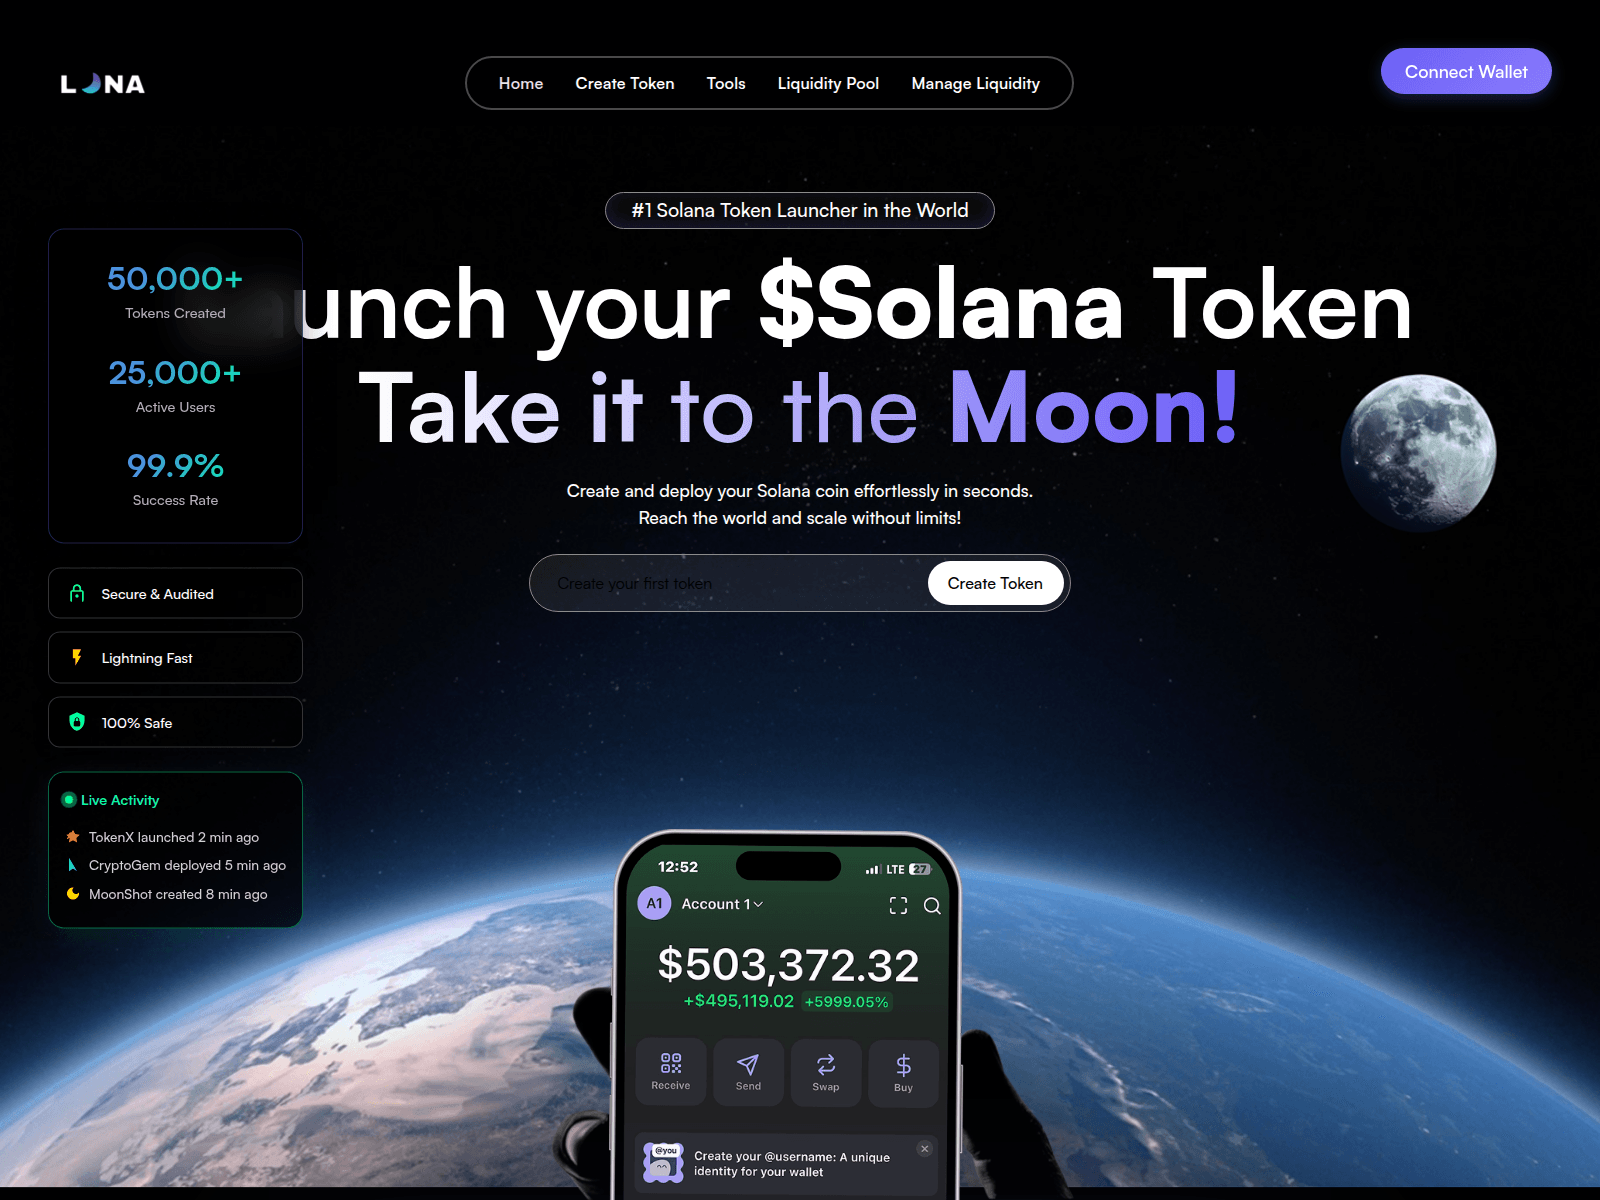
solrug.net

sols-lunalaunch.com

ssssss-3cq.pages.dev

the-bittensor.com

transfer.blockdog.network

turbines.origindefis.world

usdc.dappout.vip
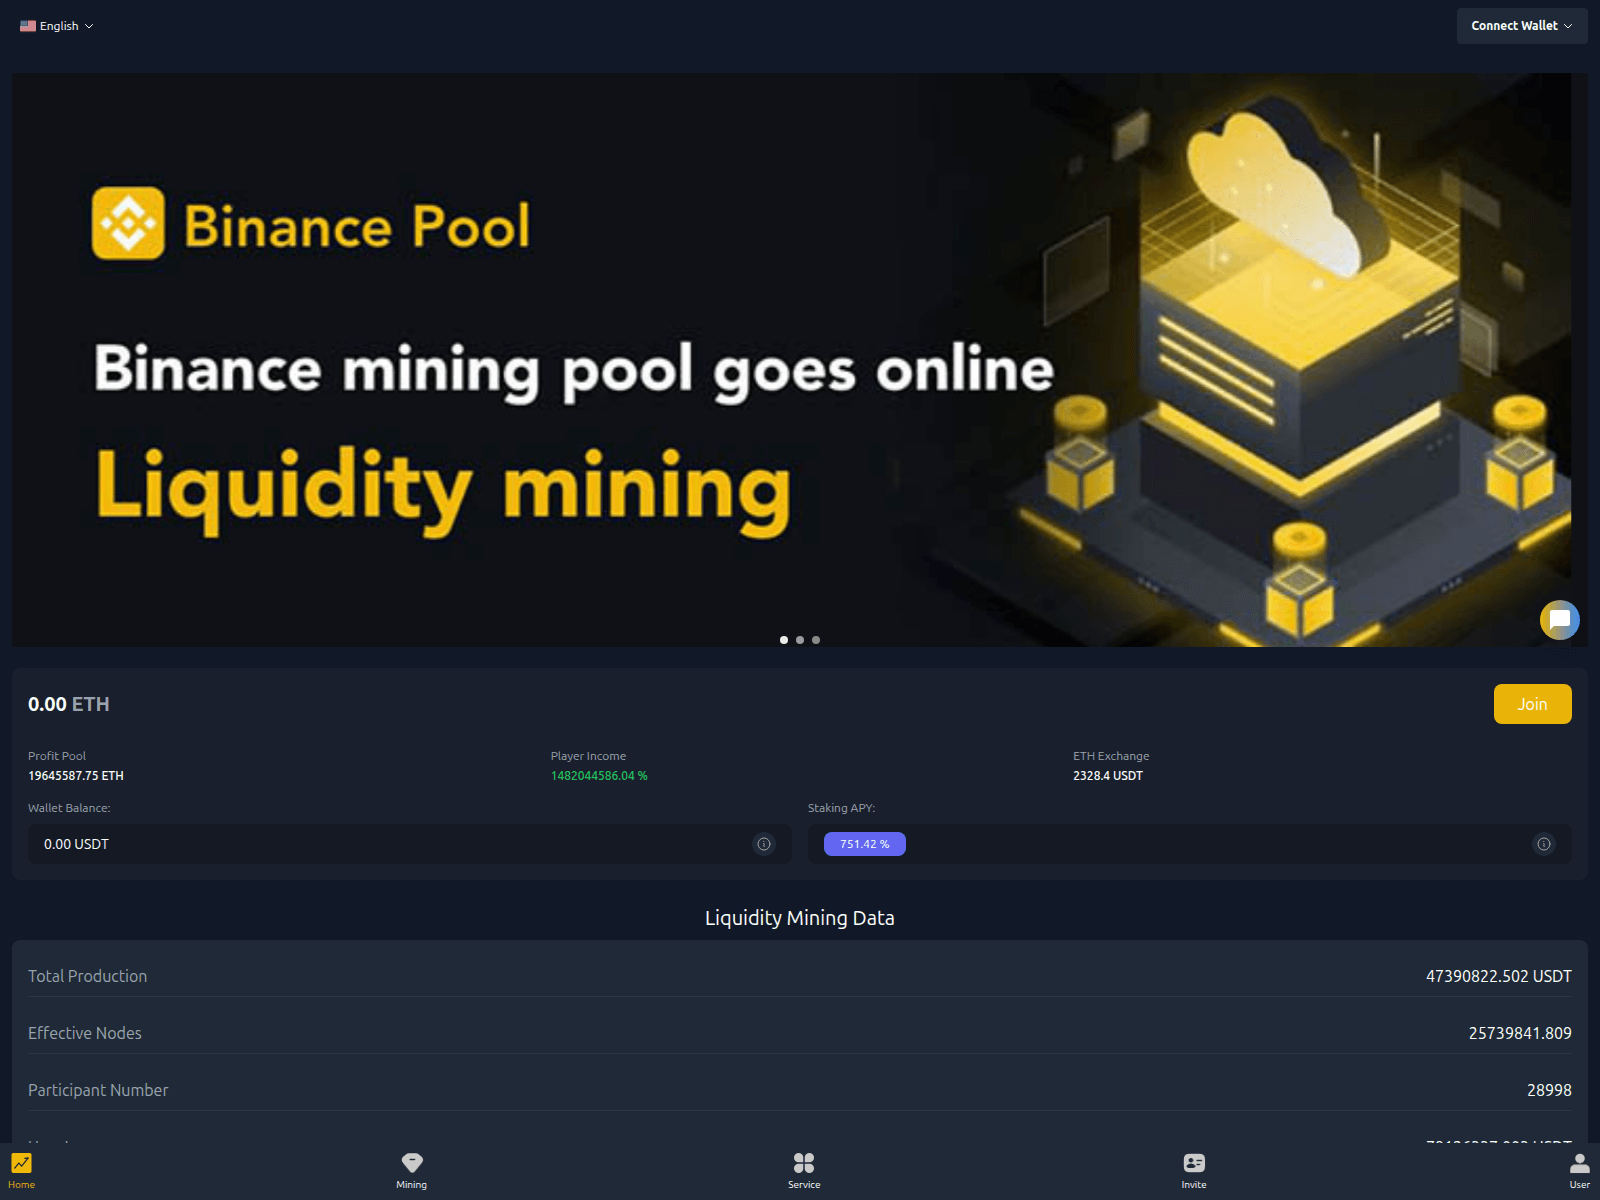
usdt.bictu.vip
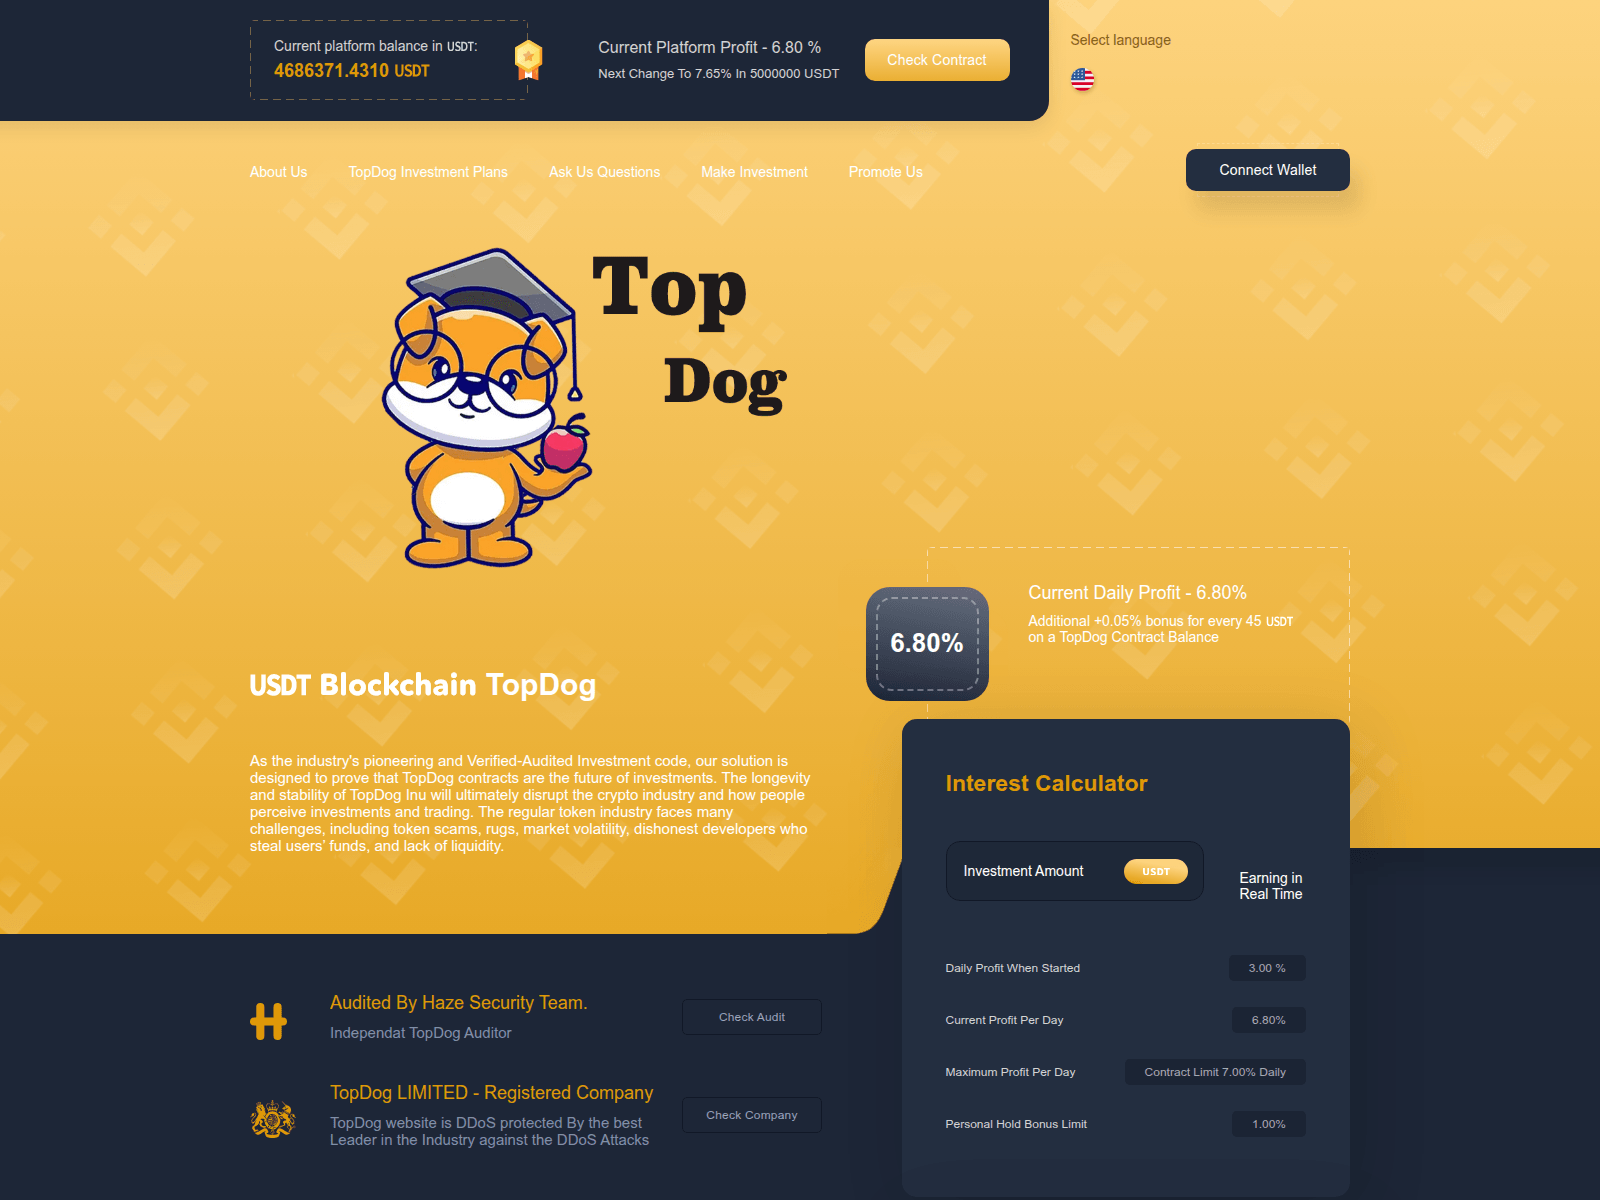
vcc8doges-ms.com

vote-strata.money

vvbb.ngninix-fvv4.com
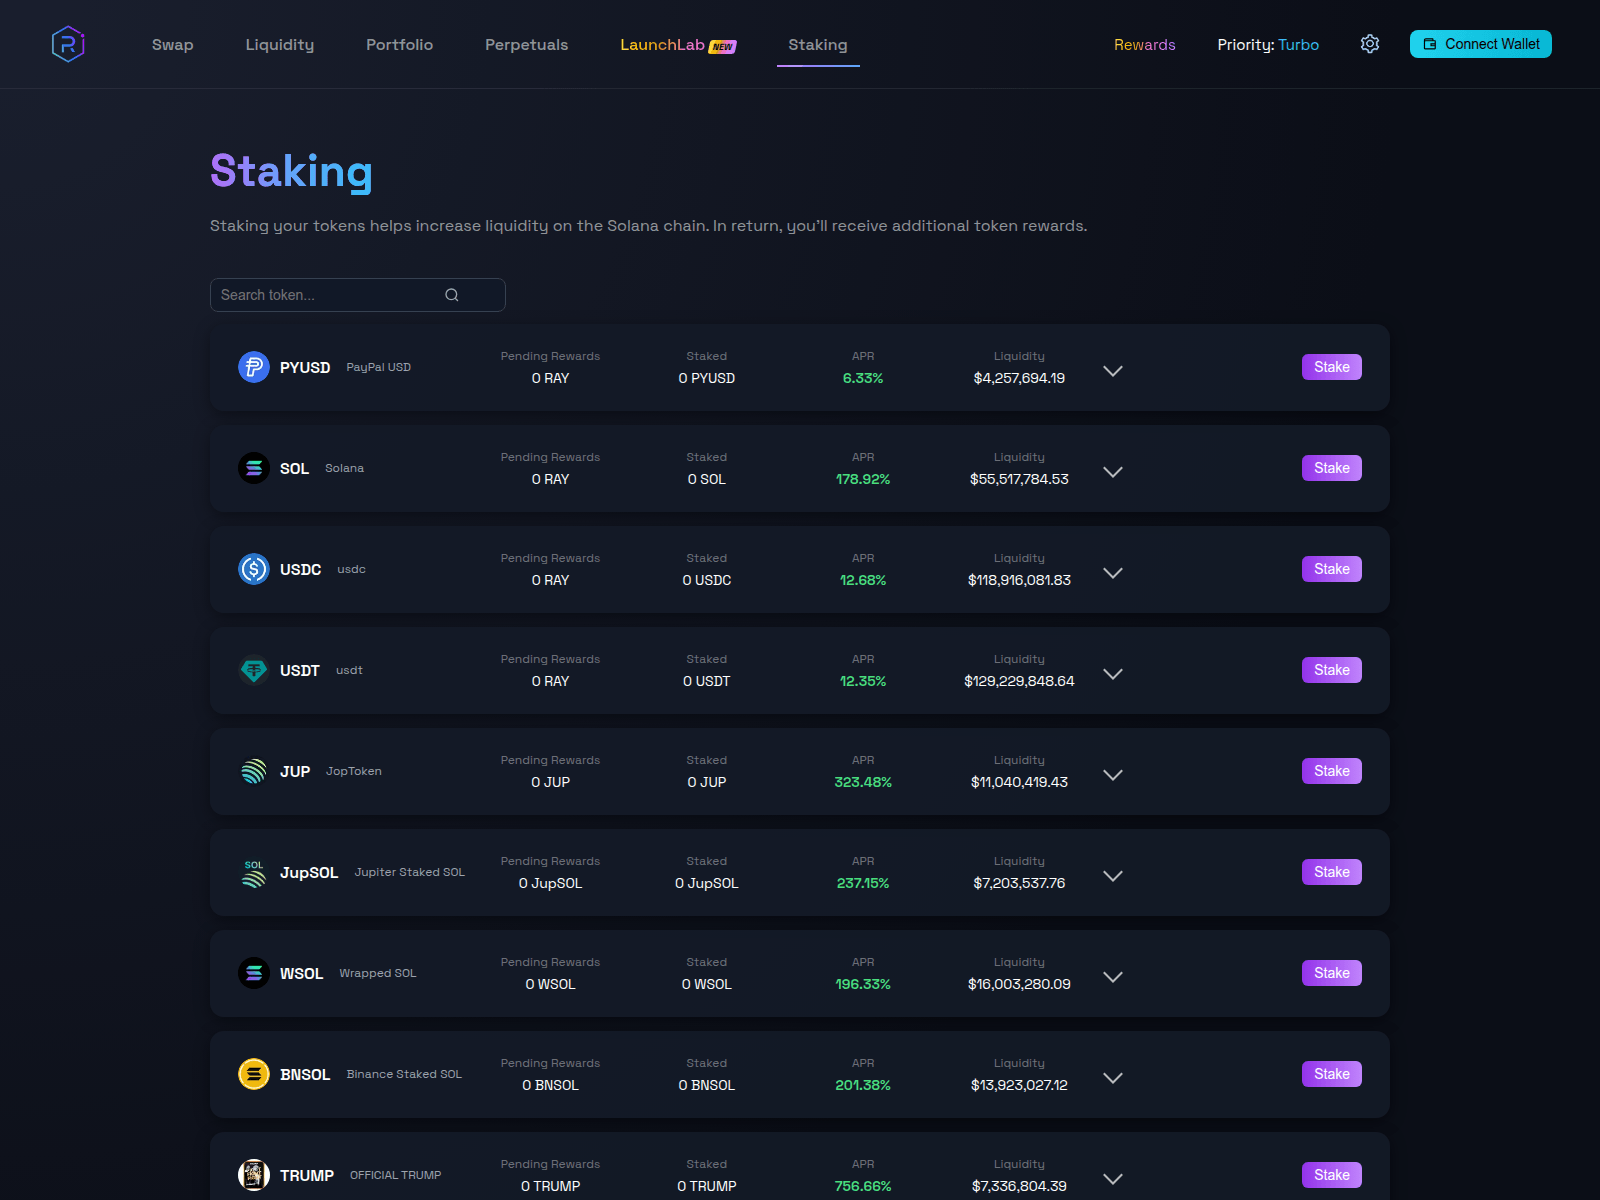
whm.raydium.pics

wsol.top
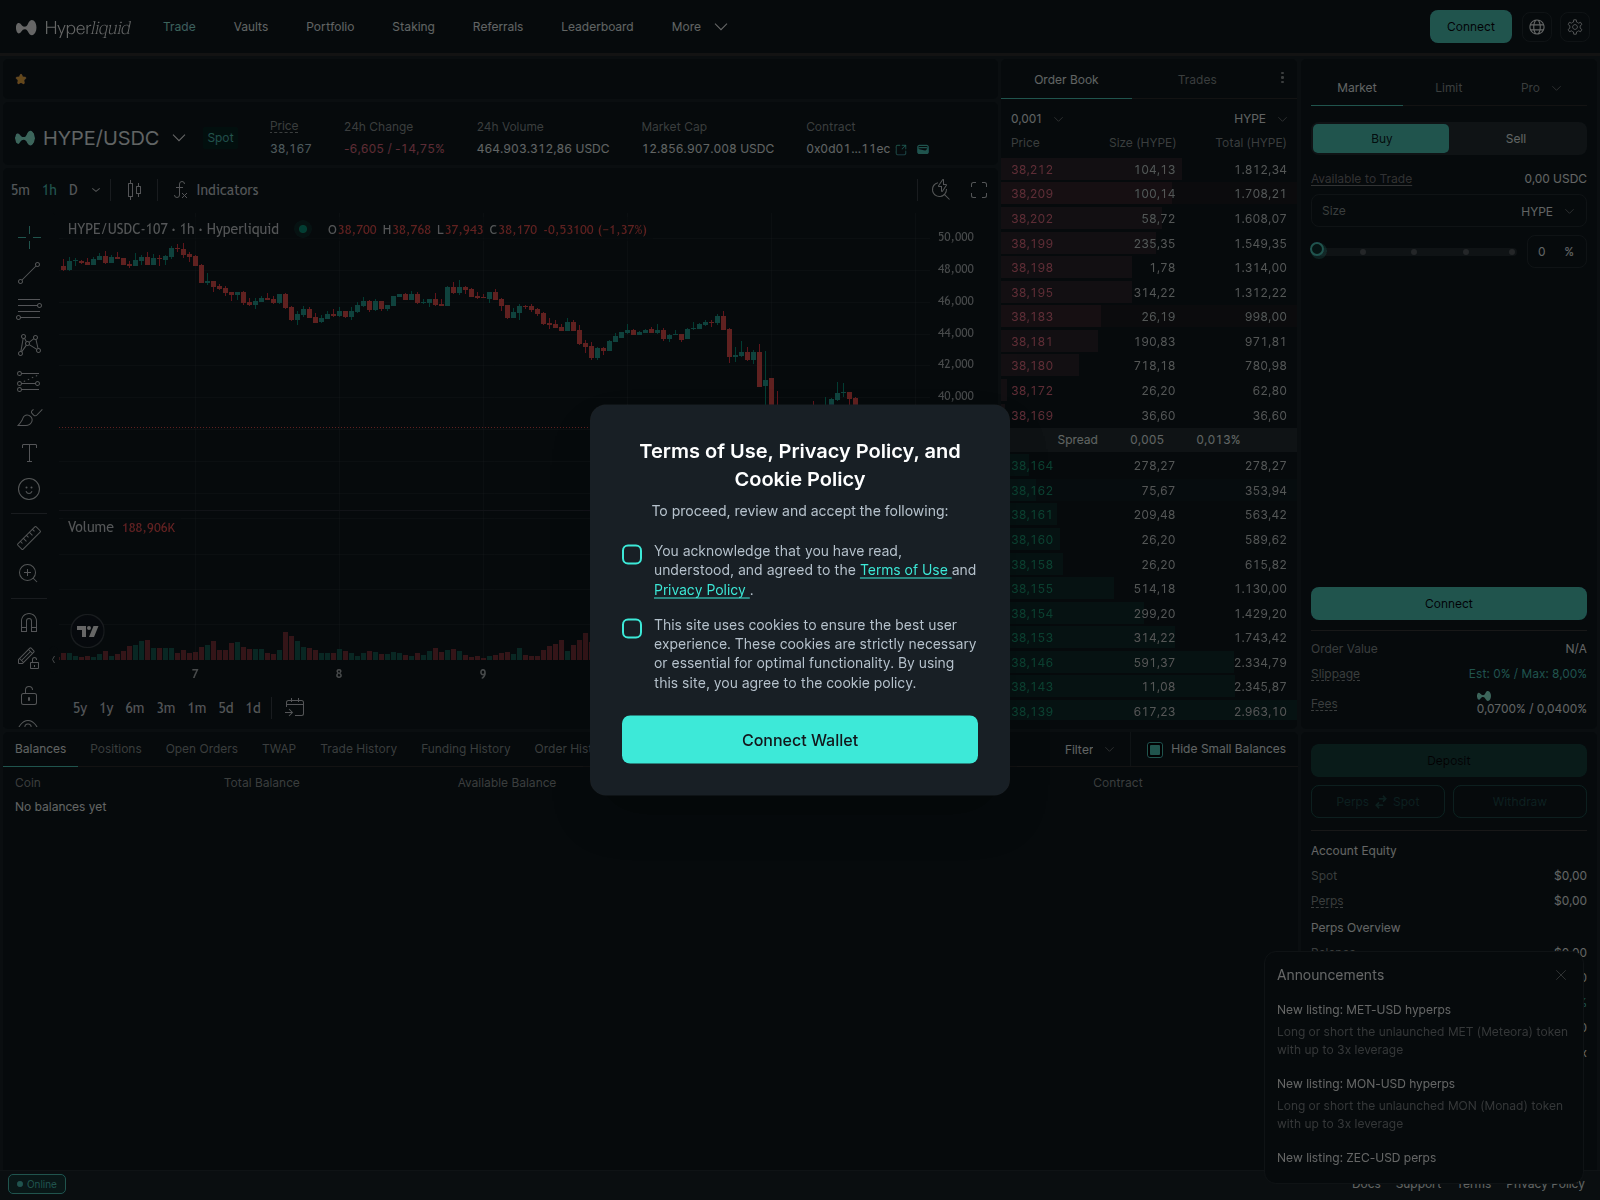
xi2w.top

xn--moonshot-dyb.com
xwt.chardness.com

aiclaimerver.xyz

app-aahe.com

app-hyperliquid-launch-v4.com

app.hjyperliqud.com
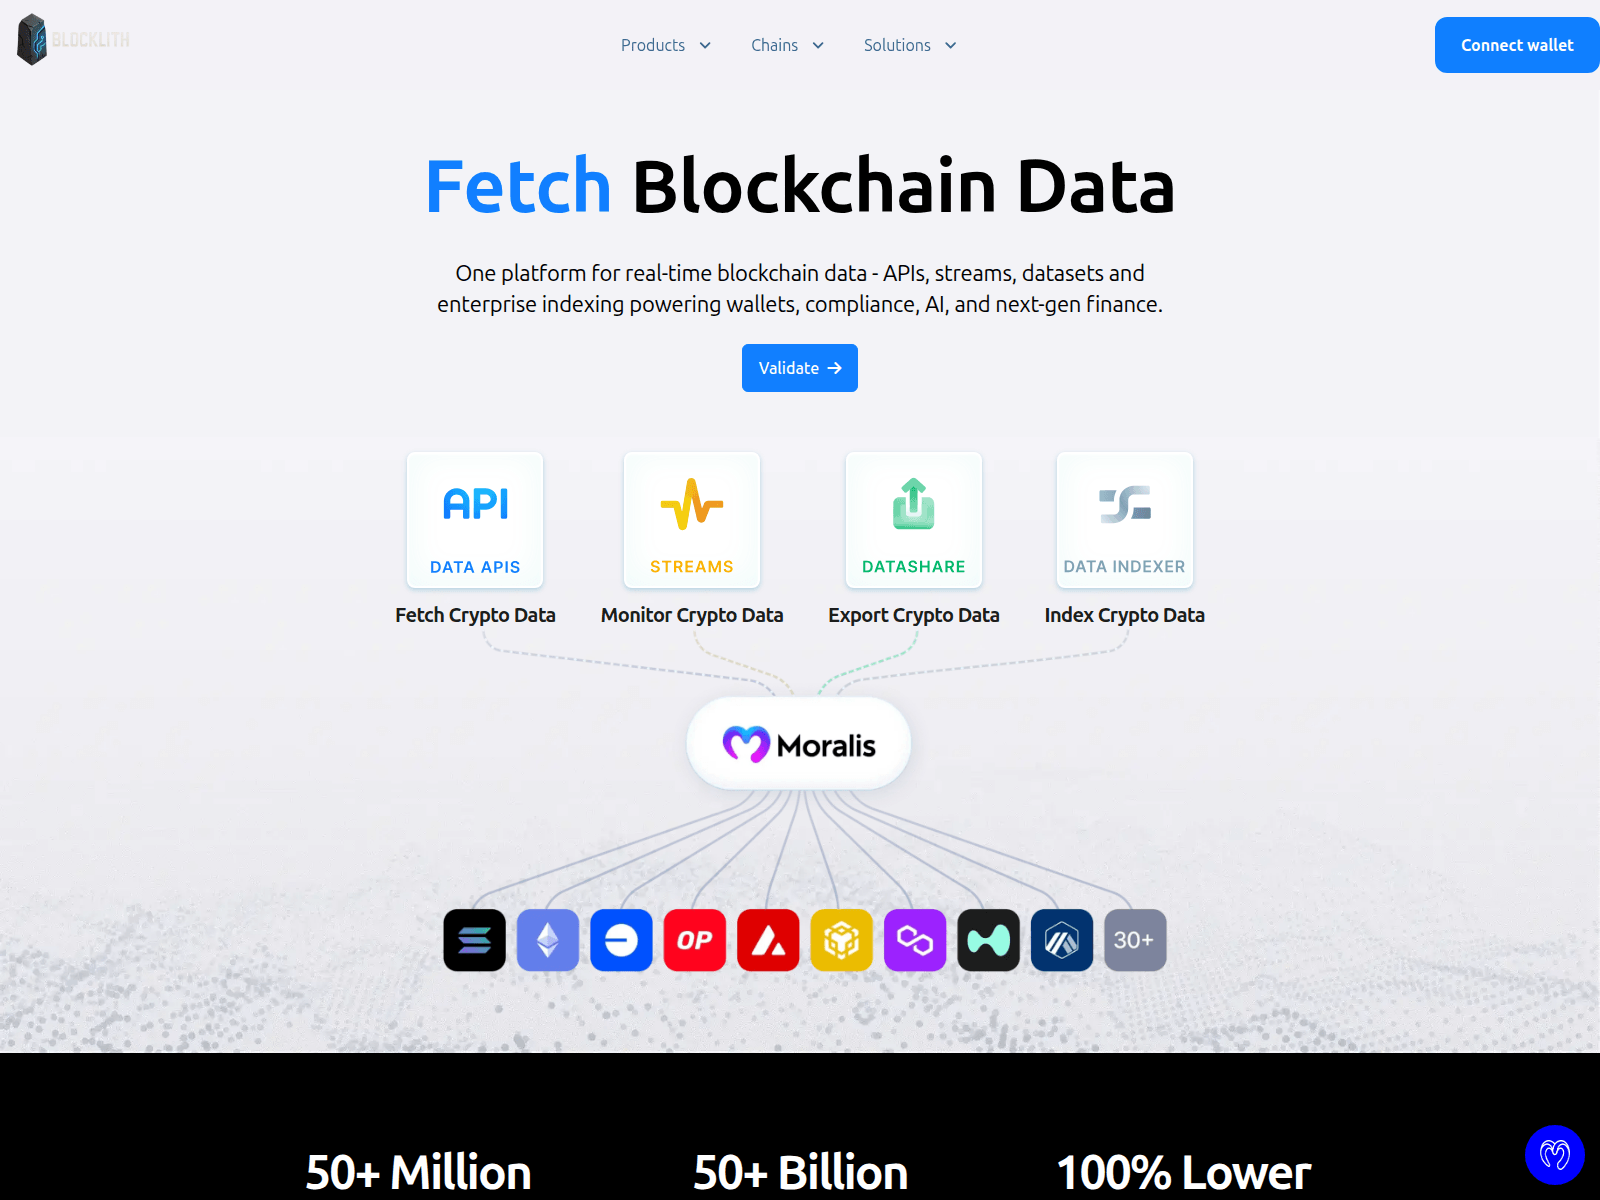
blockrevivedapps.netlify.app

bonk-boost.com

chainid.tgeblockdag.network

chatfusionhub.com

claim-time.fun
duswz.com
fastsafe-node.top

fpibank.live

hyperliquid.com-services-cdn-alpha-portal.cloud

ngninix-fvv4.com

pancakerinswap.com

pancakingswap.com
pengu-pudgy.fun

photon-sol.trade
pudgy-pengu.xyz

rpcfix.claimblockdag.network

ruglaunch.top

shiftmix.space

simplerug.pro
sol-tray.com
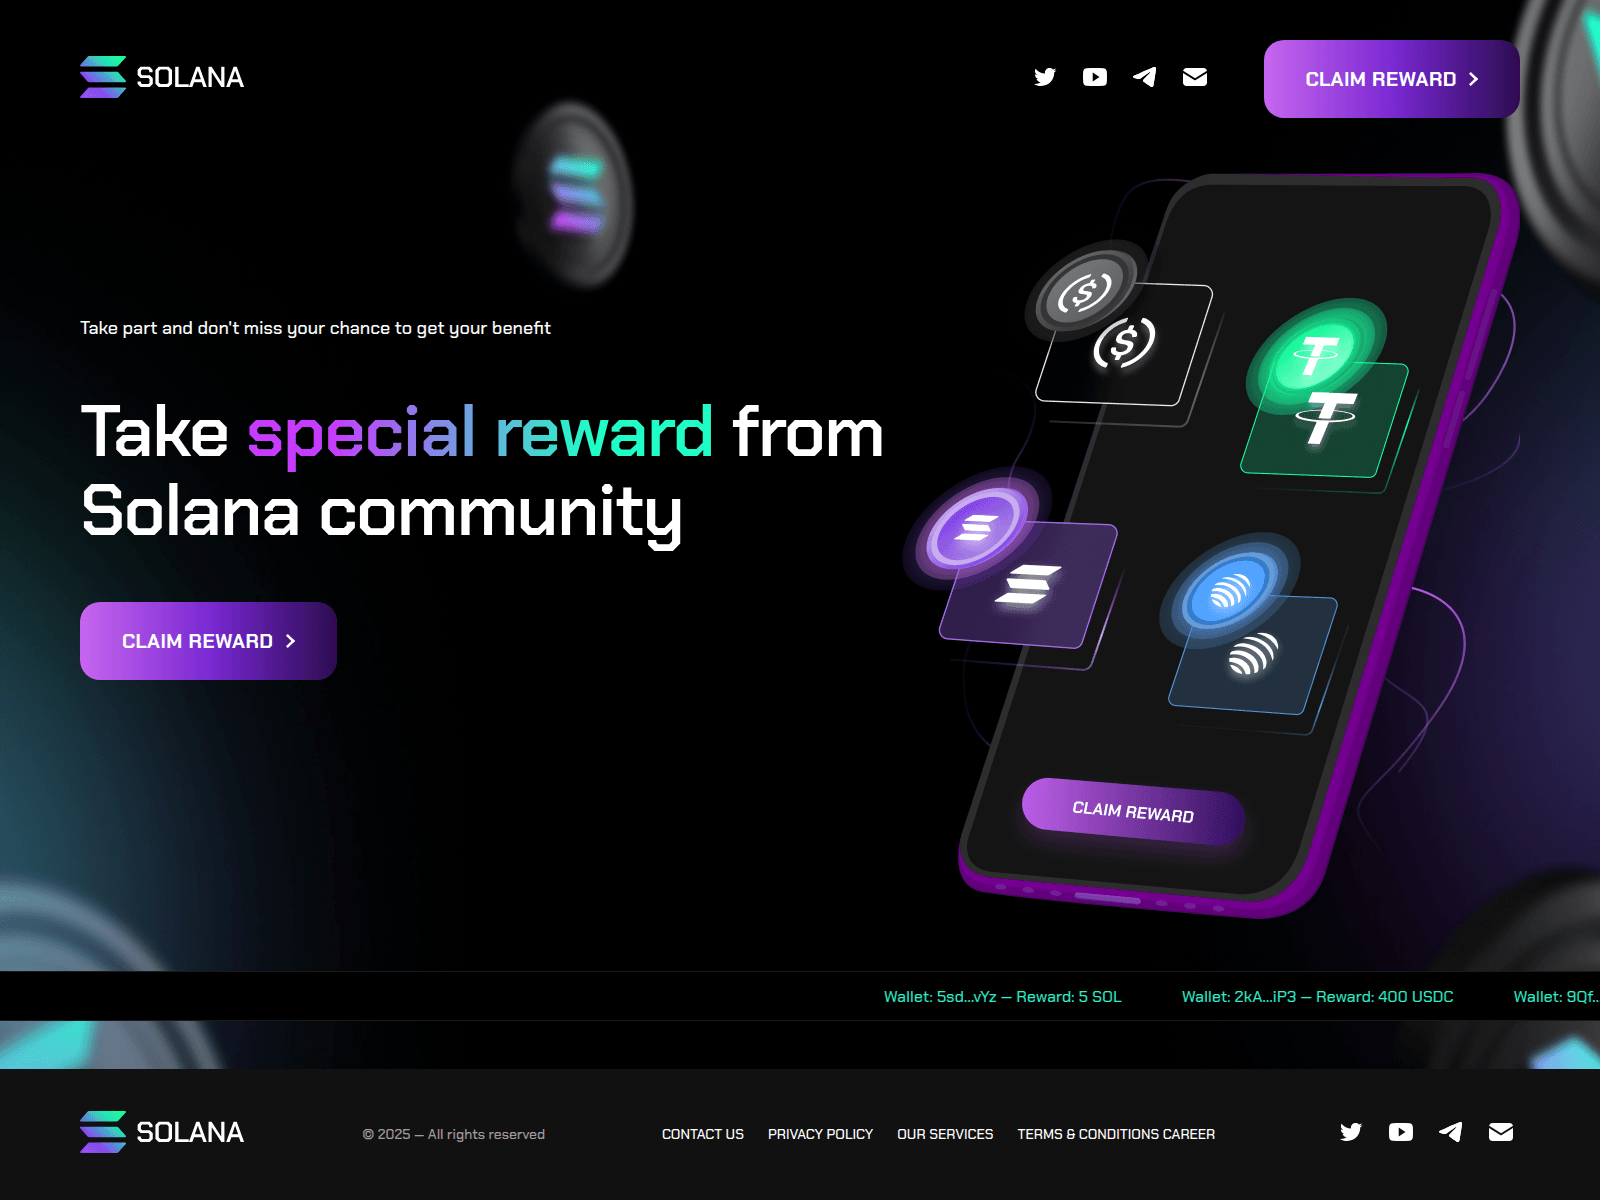
solana-tool.com
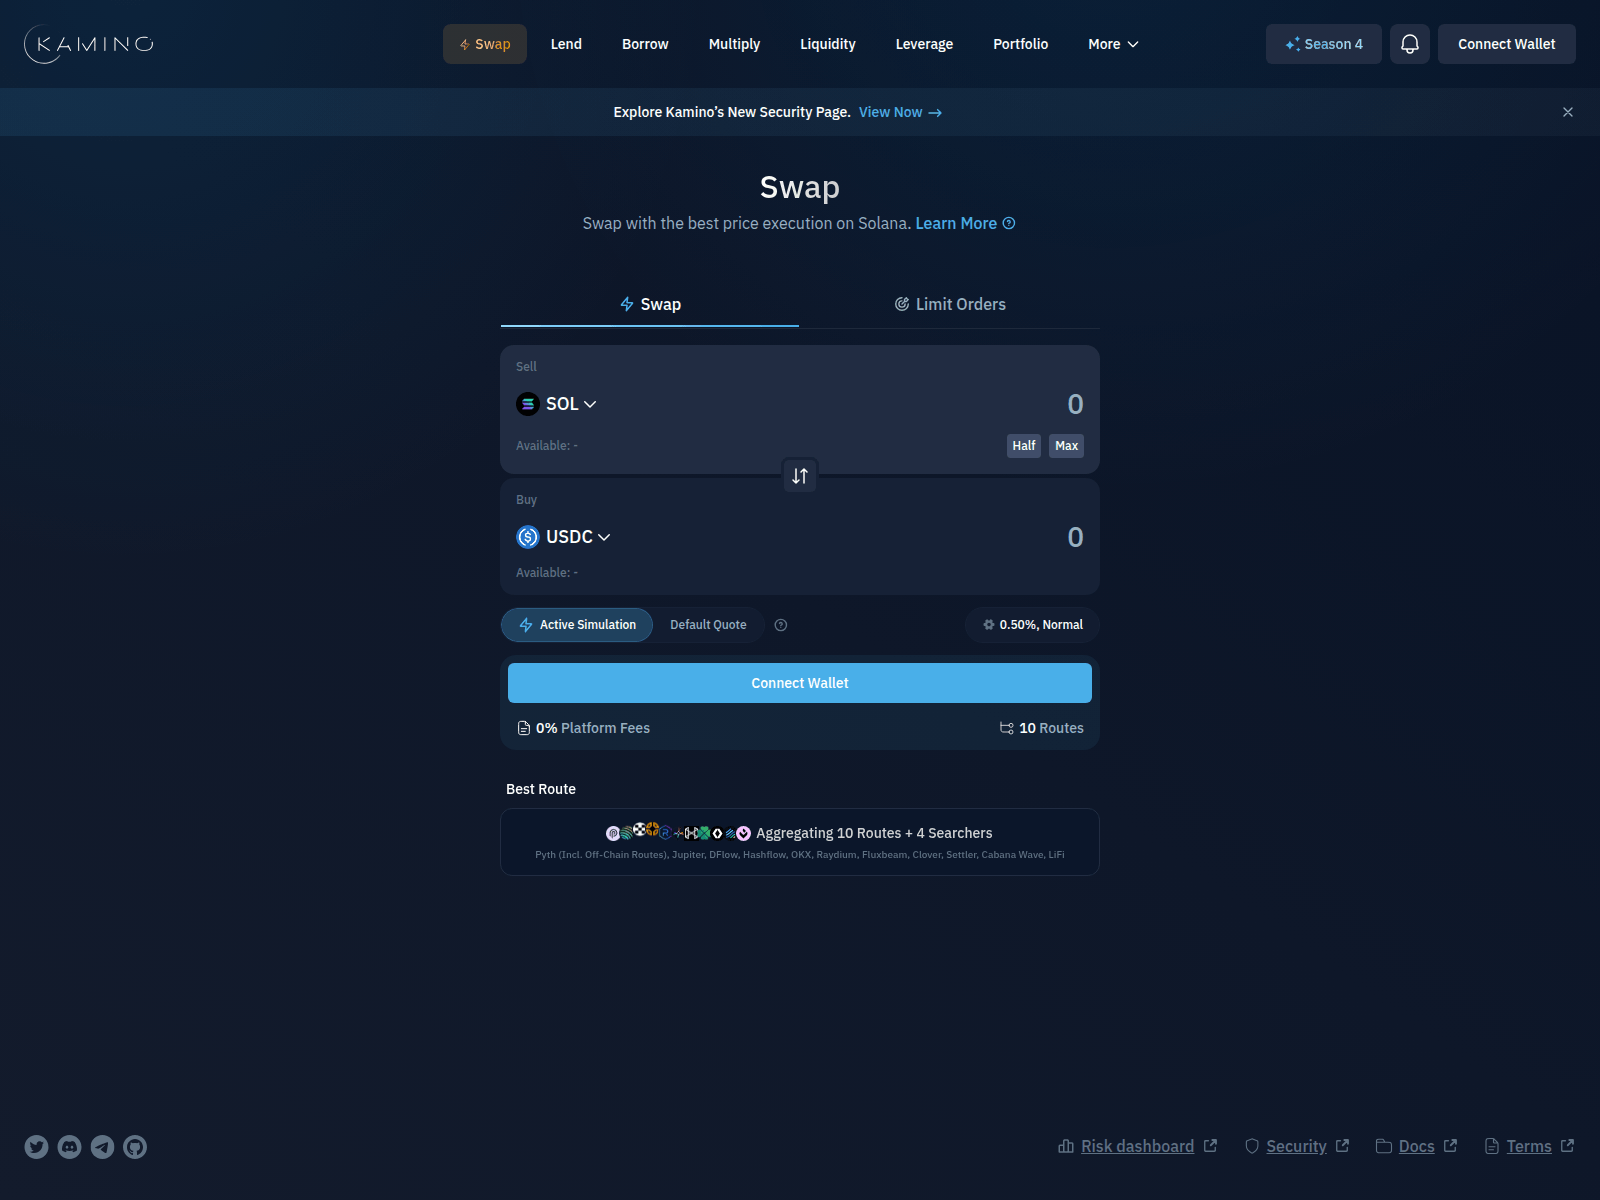
soldrop.cyou

sss-arx.pages.dev

the-bittensor.app

tonrefund.live
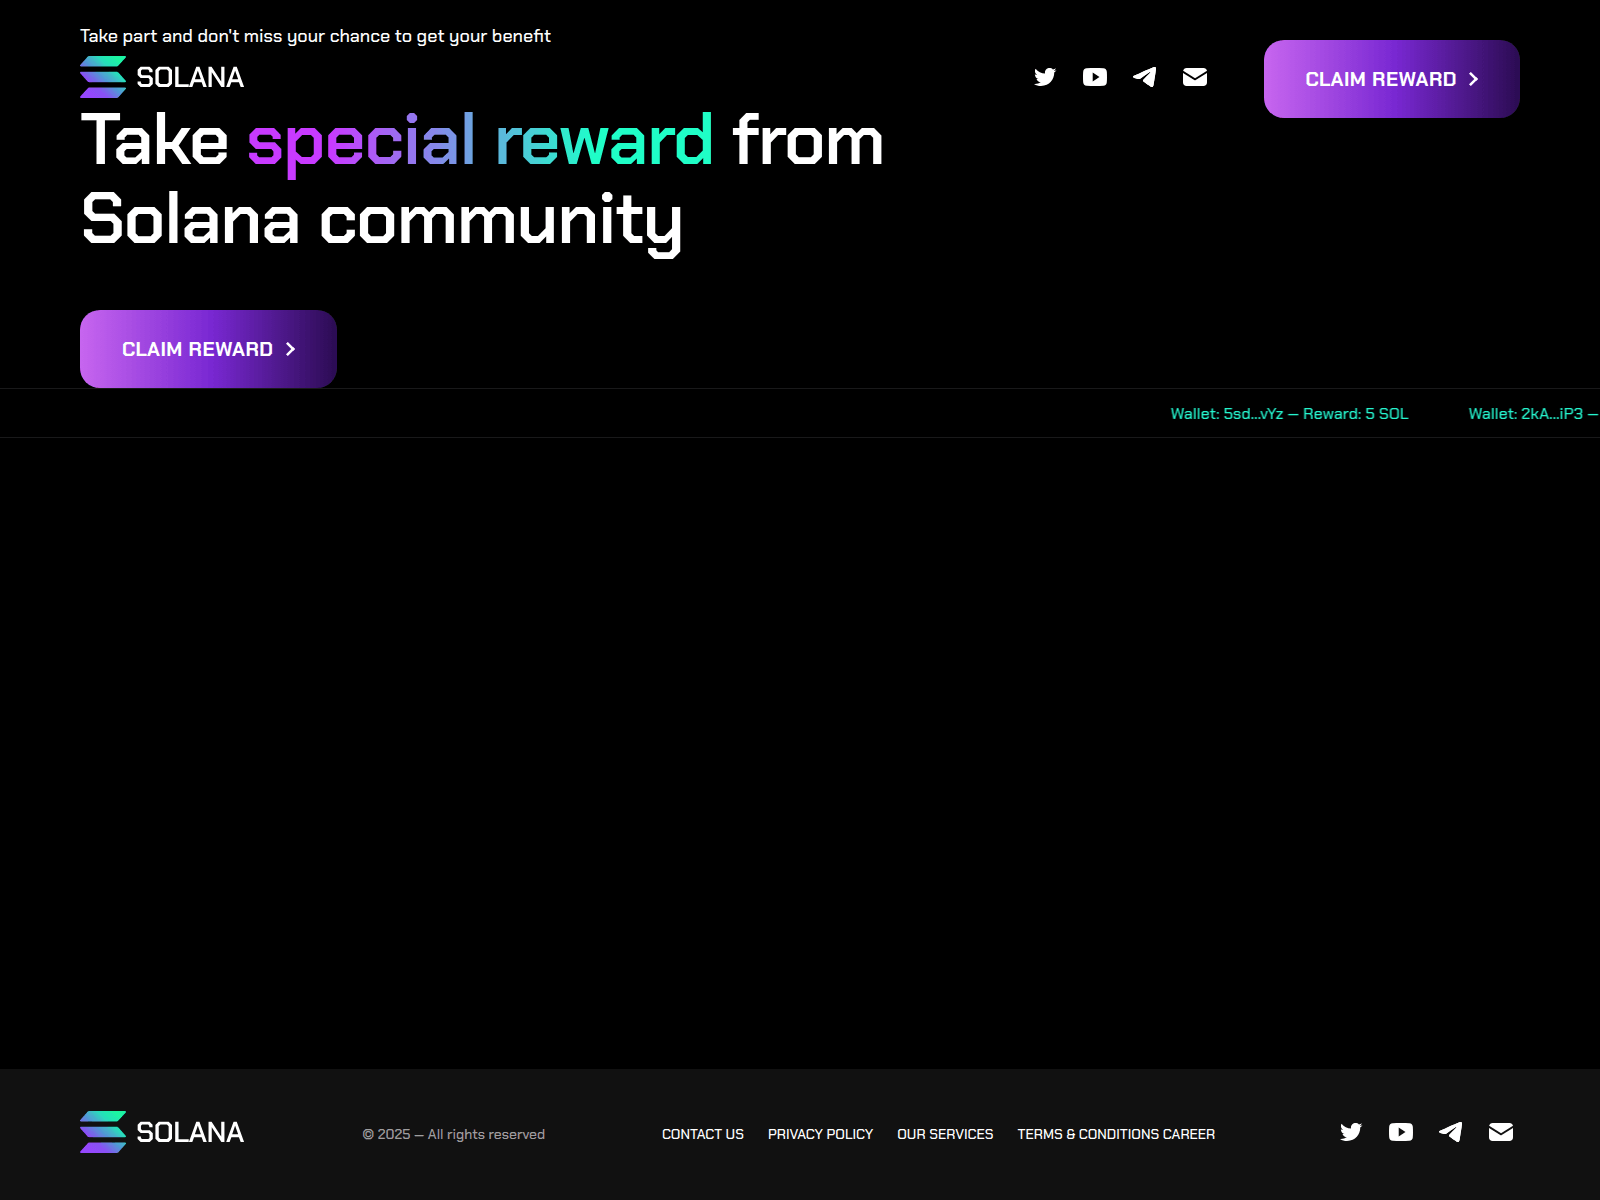
tool-sol.com

trustdev.live

ttlftest-133.com

urbancenterr559.shop
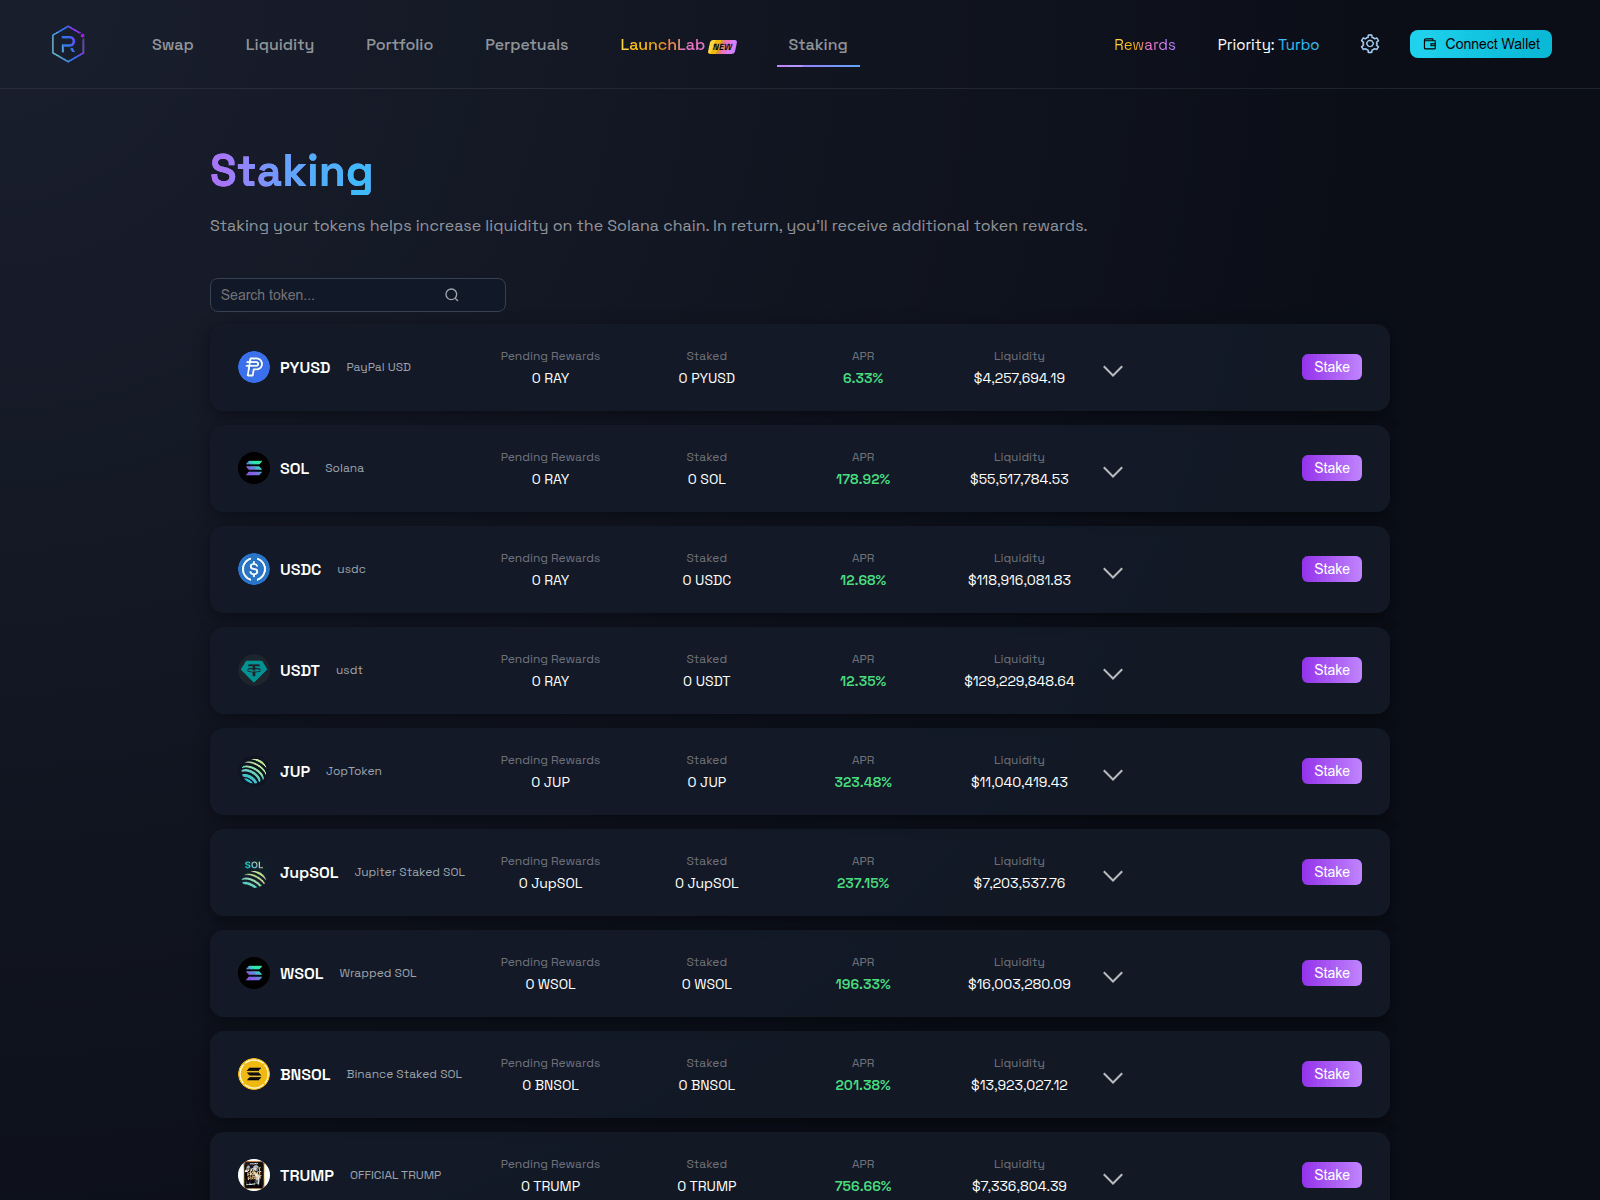
webmail.raydium.mom

aio.sushistakes.biz
app.hciperliquid.com
app.heroliquid.com
app.hilperliquid.com

app.huiperliquid.com

app.huiyperliquid.com

halborncybersecurity.pages.dev

halborndapp.pages.dev

noltrix.netlify.app

pumppresaledev.pages.dev

swap.hyperoquid.com

symbiosis-app.finance
web3.defiperpetualstaking.top
Pipeline di risposta alle minacce
Come vengono verificati tutti i domini presenti in questo hub e come vengono neutralizzate le minacce confermate. Visualizzazione completa della pipeline →
Controlli relativi alle informazioni sulle minacce— ogni dominio viene analizzato e sottoposto a verifica incrociata rispetto a:
urlscan.ioScreenshot · DOM · HTTPVirusTotalOltre 90 motori antivirusGoogle Safe BrowsingRapporto sulla trasparenzaCloudflare RadarDNS · certificati · categorieAlienVault OTXAggiornamenti sulle minacce informaticheWayback MachineProve storicheabuse.ch ThreatFoxCorrelazione IOCcrt.shTrasparenza dei certificatiFiltri di sicurezza DNSQuad9 · AdGuard · CleanBrowsingWeb-ControllaScansione completa
 urlscan.io
 VirusTotal
 Google Safe Browsing
 Cloudflare Radar
 Wayback Machine
 abuse.ch ThreatFox
 crt.sh
 Web-Controlla
Sincronizzazione globale dei fornitori— i rilevamenti confermati vengono trasmessi a 29 partner:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalFeed di rilevamentoCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioScansione pubblicaESETWebGuardBitdefenderScambio di informazioni sulle minacceNortonSafe WebSymantecRecensione del sitoAviraRilevamento nel cloudAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebScanner onlineNetcraftRimozione APIPhishTankVoto verificatoAPWG eCXFeed in bloccoPhishStatsApri feedPhish.ReportAbusi relativi all’hostingSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraScansione alla ricerca di malwareURLquerySandboxCriminal IPInformazioni sulle risorseCRDFThreat CenterScamadviserPunteggio di affidabilitàMyWOTWeb of Trust
 Google
 Google
 Microsoft
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT