
Cerca i domini monitorati ed esamina le prove archiviate, i rilevamenti e gli ultimi dati relativi alla disponibilità osservata.
219,828
Totale monitorato
213,490
VT rilevato
91,931
Ultima visualizzazione: attivo
127,897
Non disponibile all'ultimo controllo
576
VT In attesa di conferma
How This Attack Works
Angel Drainer operates by luring victims into interacting with malicious websites that appear legitimate. The attack unfolds in a series of deceptive steps designed to steal cryptocurrency assets.
STEP 1
Baiting with Fake Offers
Attackers create phishing sites mimicking trusted platforms like NFT marketplaces or DeFi protocols, often using domains like opensea.com.offer-proposal.com to appear authentic. Victims are enticed with fake airdrops, giveaways, or urgent account verification prompts.
STEP 2
Wallet Connection Request
Once on the site, users are prompted to connect their crypto wallets (e.g., MetaMask) to 'claim' rewards or 'verify' their accounts. This step often bypasses user suspicion by mimicking standard Web3 interactions.
STEP 3
Malicious Smart Contract Execution
Upon connection, the site triggers a malicious smart contract that requests sweeping permissions, allowing attackers to drain funds or NFTs from the wallet. Victims often don’t realize they’ve approved a transaction that compromises their assets.
STEP 4
Asset Drainage and Laundering
Stolen funds are quickly transferred to attacker-controlled wallets and laundered through mixers like Tornado Cash or cross-chain bridges, making recovery nearly impossible.
Technical Analysis
Angel Drainer is a sophisticated phishing-as-a-service (PhaaS) toolkit that emerged in late 2022, primarily targeting cryptocurrency users. It leverages malicious JavaScript embedded in phishing websites to interact with victims’ wallets. The core mechanism involves tricking users into signing transactions that call functions like 'approve()' or 'transferFrom()' on ERC-20 tokens or NFTs, granting attackers full control over assets. These scripts are often obfuscated to evade detection by antivirus software or browser security extensions. Infrastructure-wise, attackers rely on cheap or compromised domain registrars—PhishDestroy data shows NICENIC INTERNATIONAL GROUP CO., LIMITED (1,173 domains) and Cloudflare, Inc. (434 domains) as top choices for hosting these threats. Common TLDs include .com (1,212 domains), .xyz (712), and .app (290), often paired with free hosting on platforms like Vercel, as seen in examples like mysteryclaims6345-live.vercel.app.
The toolkit also employs advanced evasion techniques, such as IP-based redirects to show benign content to bots or security researchers while serving malicious payloads to real users. Angel Drainer campaigns frequently clone legitimate Web3 interfaces, using typosquatting or subdomain tricks (e.g., opensea.com.offer-proposal.com) to deceive users. On the blockchain side, stolen assets are often routed through intermediary wallets before being mixed, with on-chain analysis revealing connections to known money laundering services. This combination of social engineering and technical exploitation makes Angel Drainer a persistent and evolving threat in the Web3 ecosystem.
Additionally, attackers customize their campaigns based on trending topics in the crypto space, such as new token launches or NFT drops, to maximize victim engagement. The use of decentralized hosting and domain privacy services further complicates takedown efforts, as seen with the 431 active domains still operational in PhishDestroy’s database. This infrastructure resilience, paired with the toolkit’s low barrier to entry for cybercriminals, underscores why Angel Drainer remains a critical risk.
Real Cases
ParaSpace NFT Exploit (2023)
$5 million stolen
In March 2023, attackers used Angel Drainer to target users of the ParaSpace NFT lending platform, tricking them into signing malicious transactions via a fake update prompt, resulting in $5 million in stolen assets.
Fake OpenSea Campaign (2023)
$1.7 million stolen
A widespread phishing campaign in late 2023 mimicked OpenSea’s interface, using domains similar to opensea.com.offer-proposal.com, draining $1.7 million in NFTs and tokens from unsuspecting users.
Blur Marketplace Scam (2024)
$2.3 million stolen
Early 2024 saw Angel Drainer used in a fake Blur marketplace airdrop scam, where users connected wallets to claim 'free tokens,' losing $2.3 million in assets to malicious smart contracts.
How to Detect
Unsolicited offers or urgent prompts for wallet connection on websites mimicking platforms like OpenSea or Vercel, often using domains tracked by PhishDestroy such as mysteryclaims6345-live.vercel.app.
Suspicious domain structures, especially subdomains or unusual TLDs like .xyz or .app, which account for a significant portion of the 4,385 domains in our database.
Transaction requests that ask for broad permissions or unlimited token approvals when connecting a wallet to a site.
Lack of HTTPS or mixed content warnings on supposed Web3 platforms, often a sign of hastily deployed phishing pages.
Unexpected wallet activity or pop-ups prompting signature approvals without clear explanations of the transaction purpose.
How to Protect Yourself
1
Always verify the URL of Web3 platforms before connecting your wallet—avoid clicking links from unsolicited emails or social media, as PhishDestroy has identified 4,385 Angel Drainer-related domains.
2
Use hardware wallets or wallet extensions with transaction simulation features to preview smart contract interactions before signing.
3
Enable two-factor authentication (2FA) and set spending limits on your crypto wallets to minimize potential losses.
4
Regularly monitor your wallet for unauthorized transactions using blockchain explorers and revoke permissions for unused dApps.
5
Leverage PhishDestroy’s threat database to check suspicious domains or report potential Angel Drainer phishing sites for community protection.
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 4,455 domains tracked for this threat type
Angel Drainer 4,455 domains


moonsshot.xyz

mooonshot.net

mooonshots.com
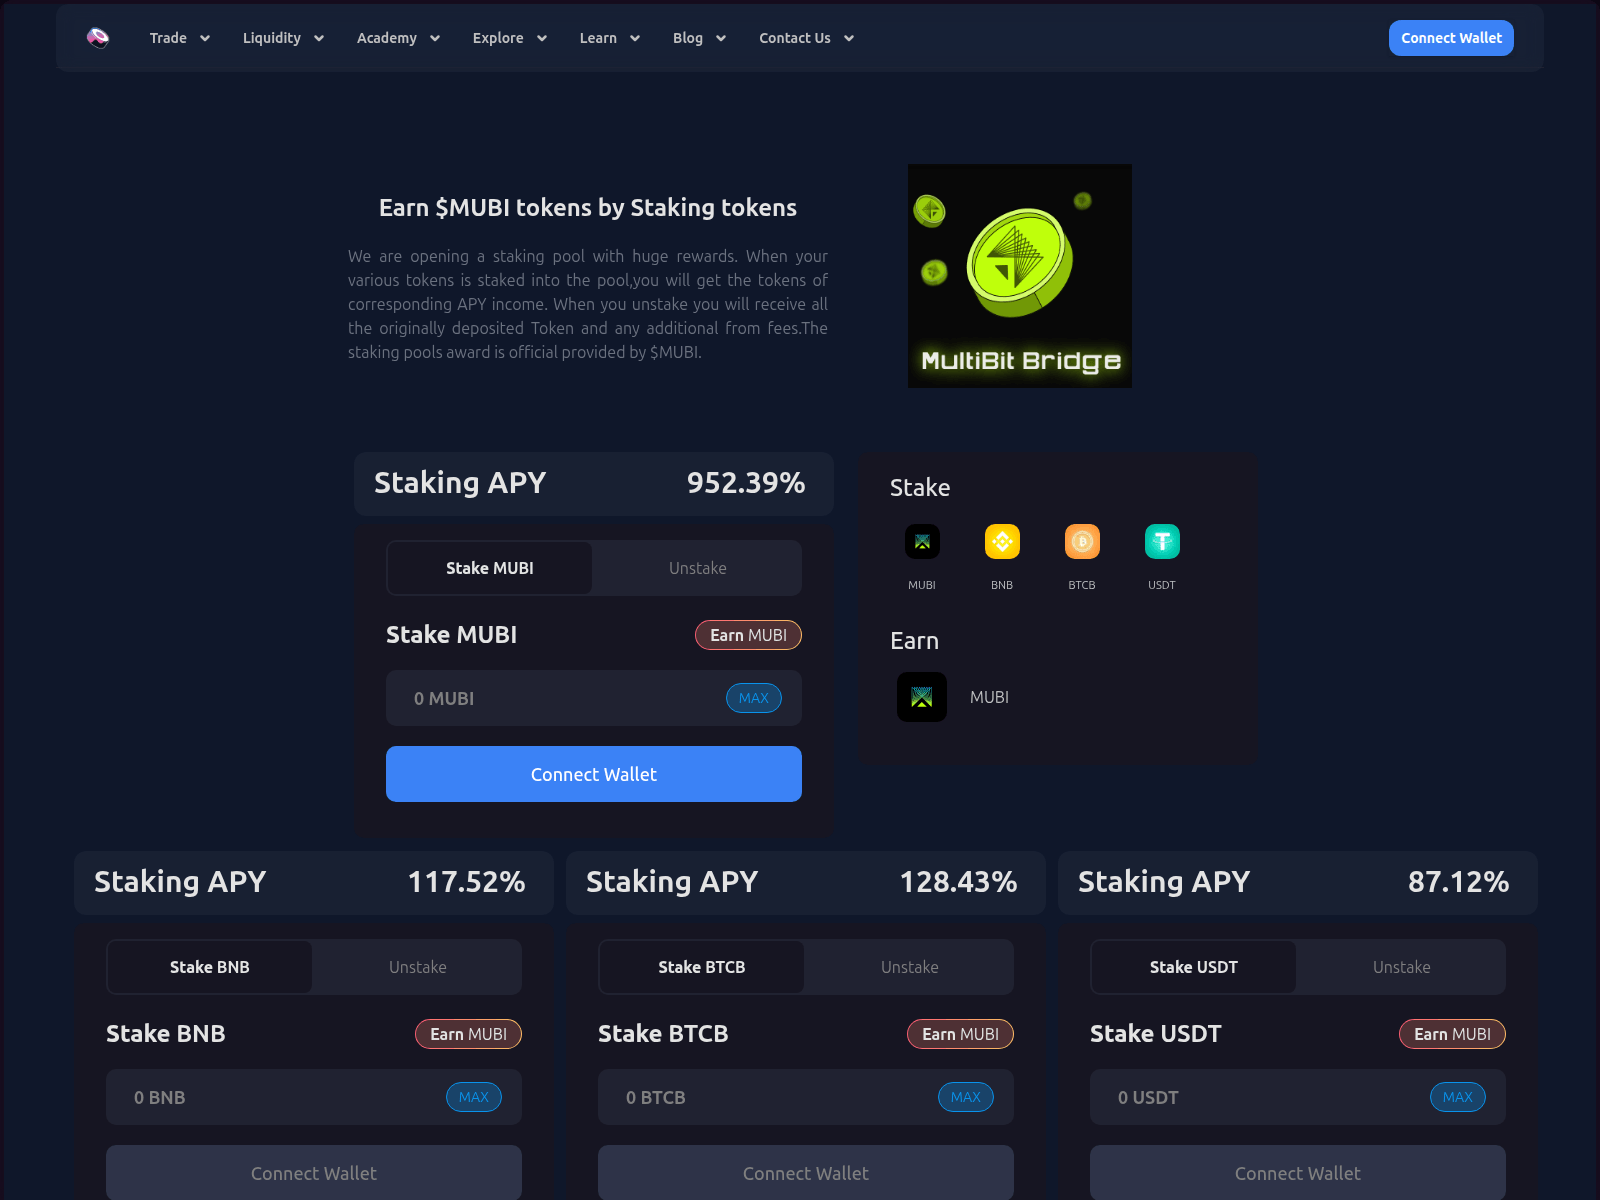
mubi.sushi.us.com

naiholder.uno

near-sushi.fit

nexchain.exchange
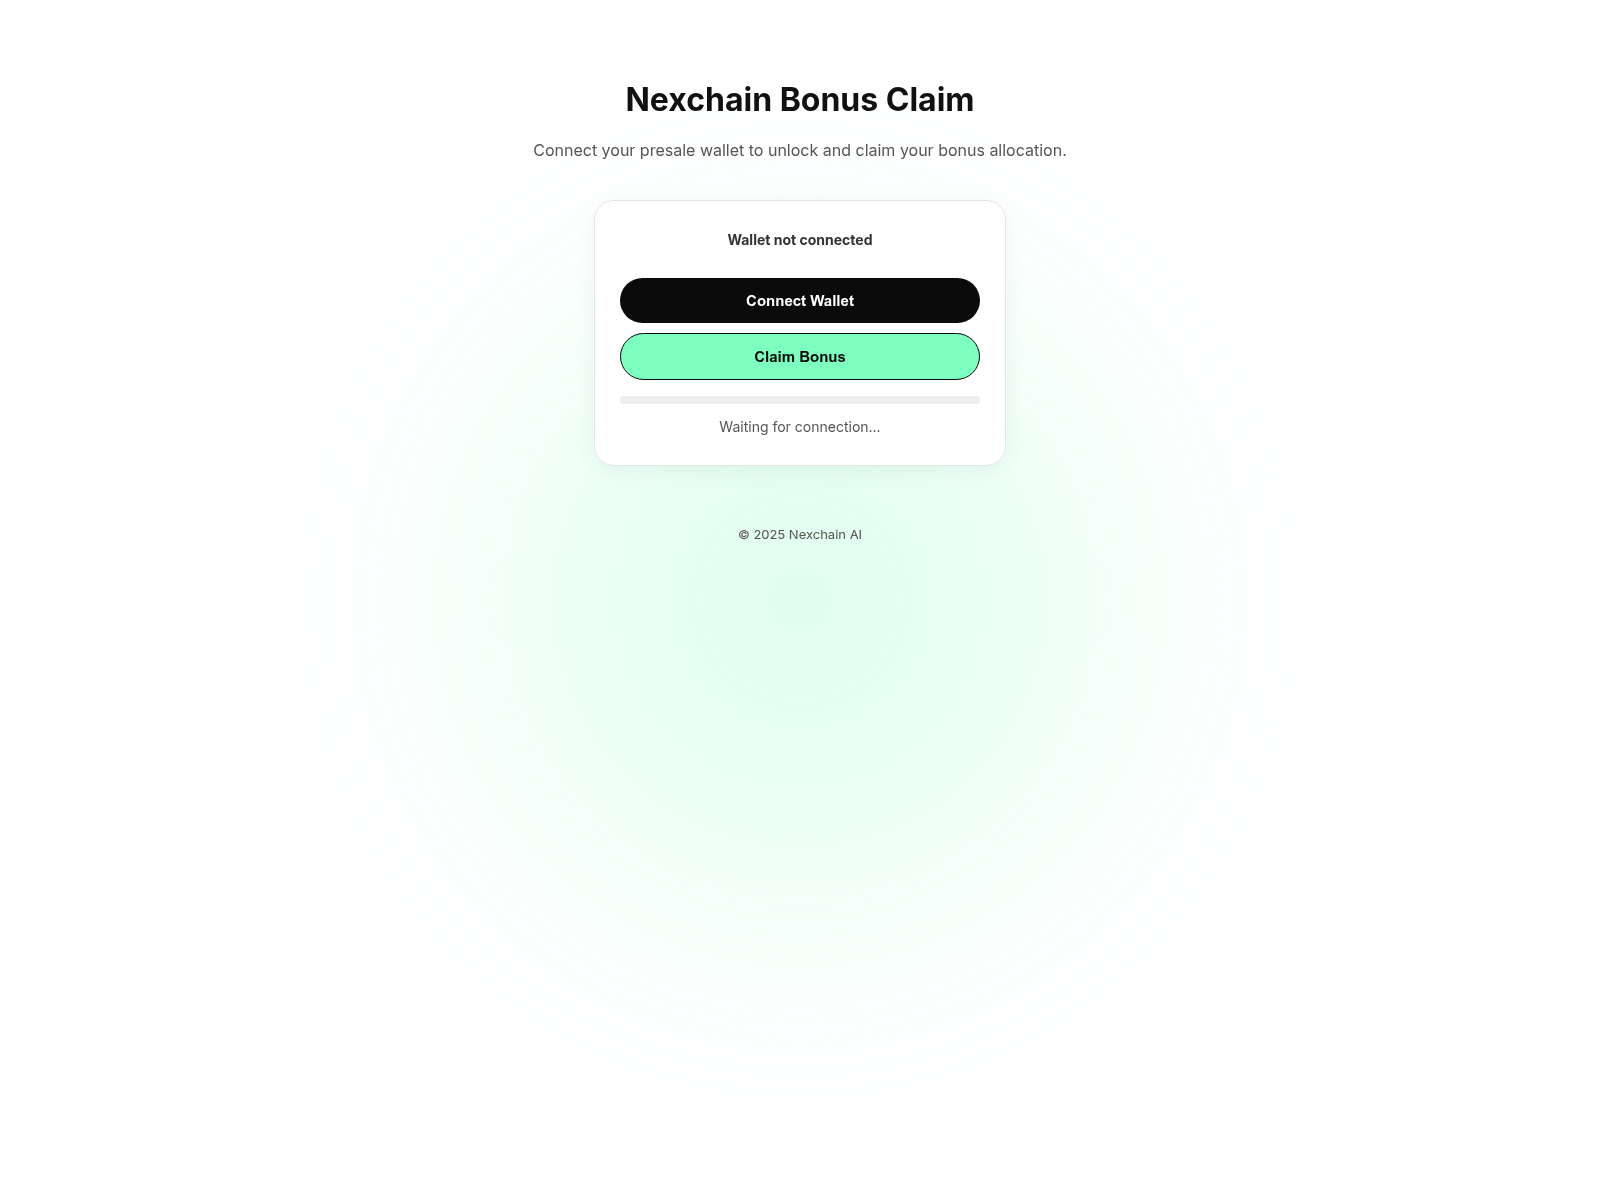
nexchains-ai.info
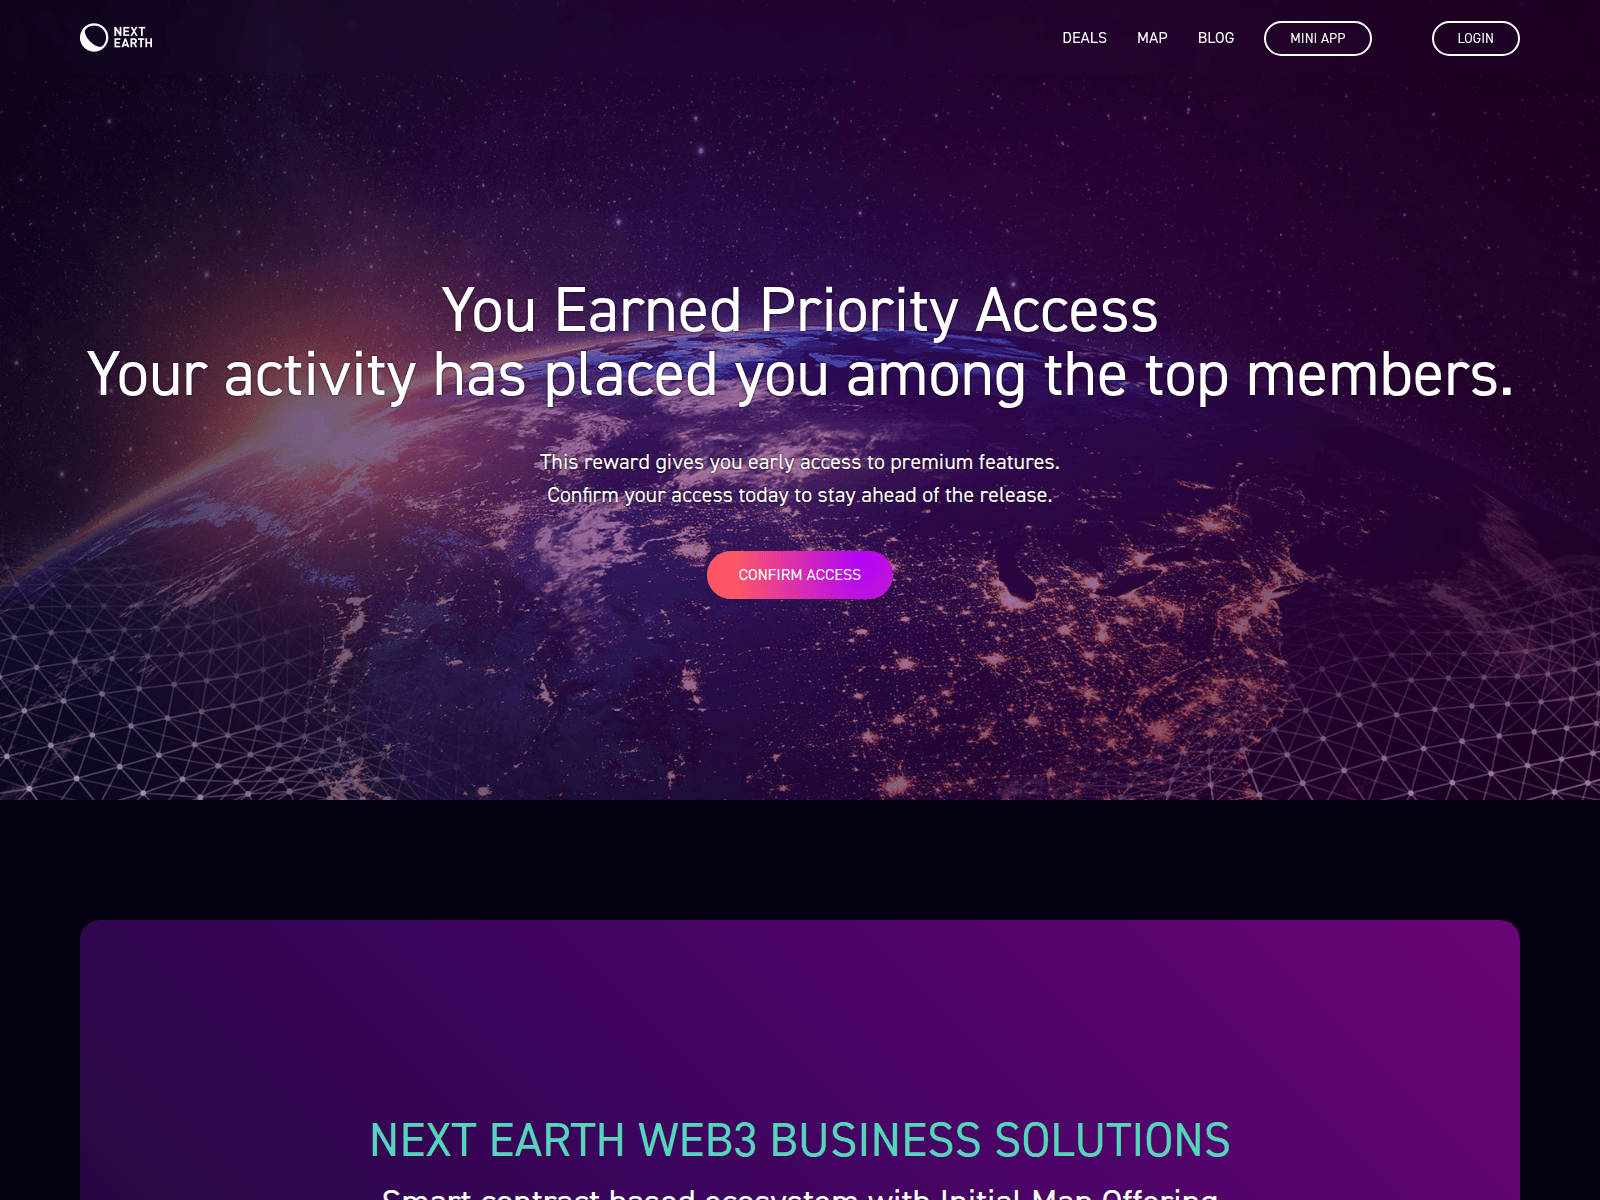
nextearth-v2.app
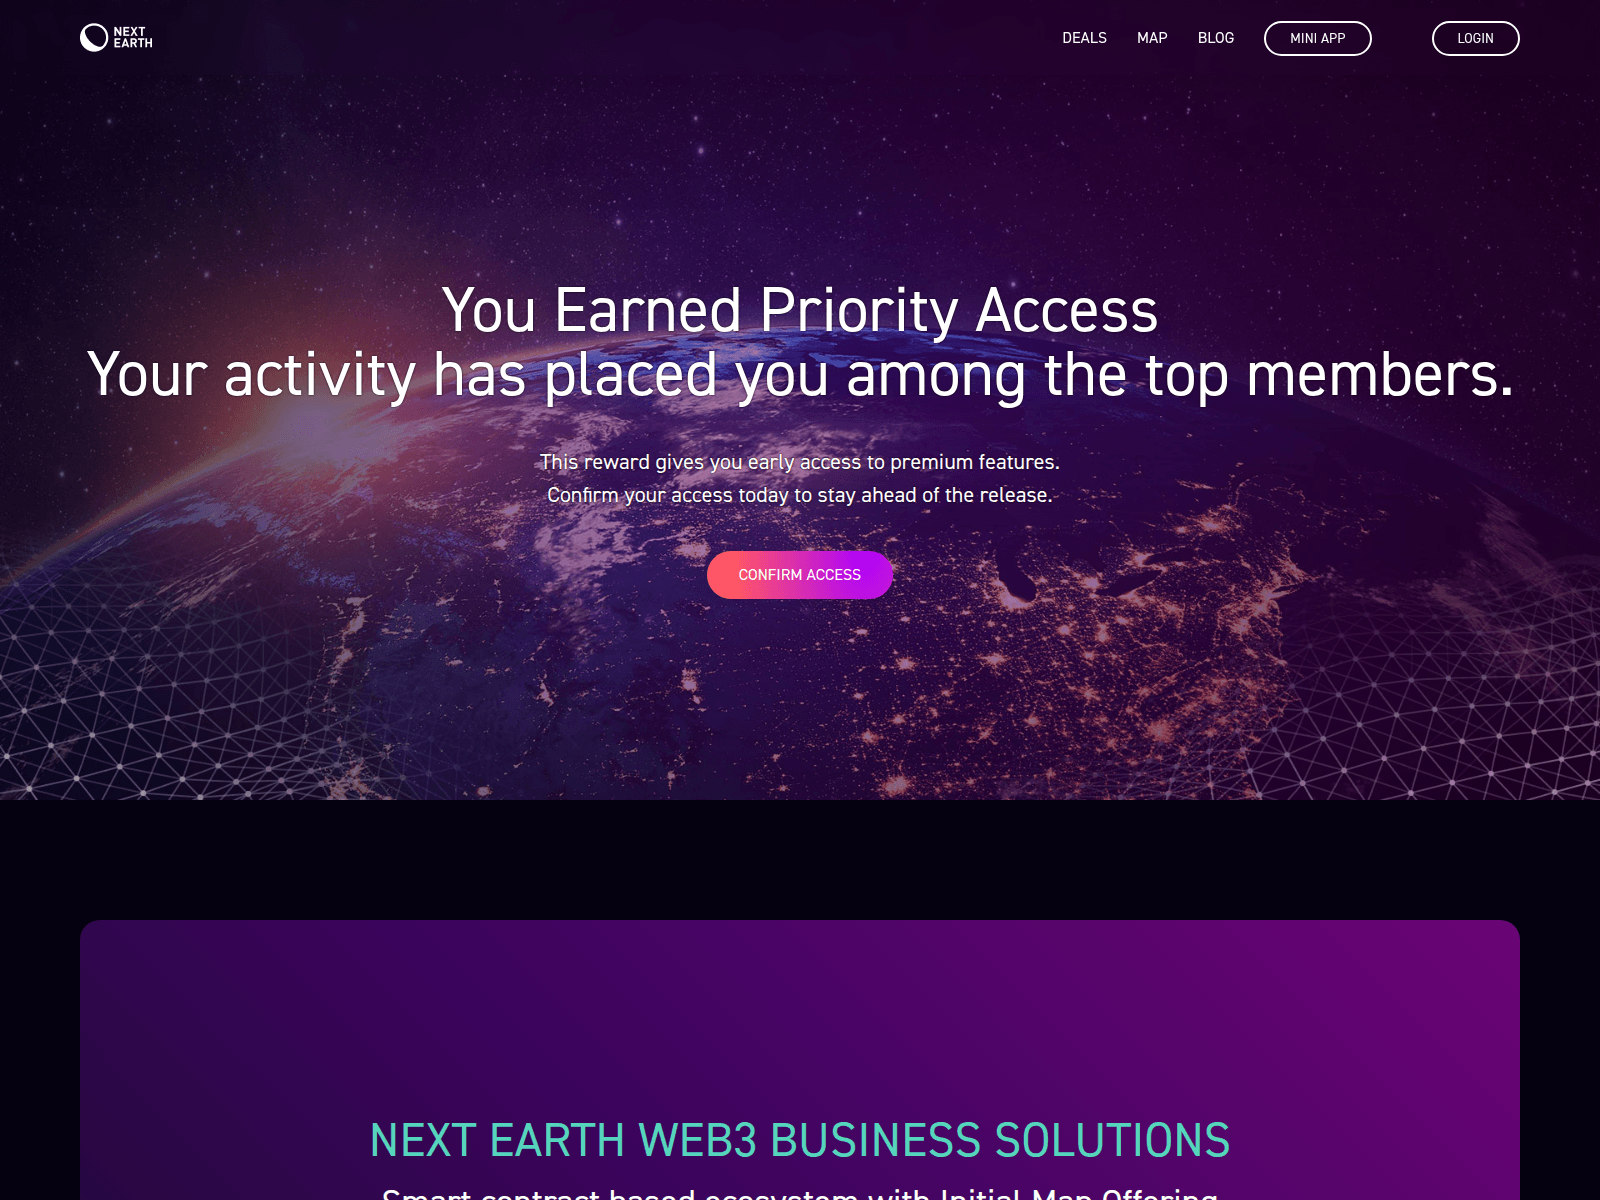
nextearth-v2.forum

nftstrategys.xyz

ninjasoldiers.xyz

nliquid.net
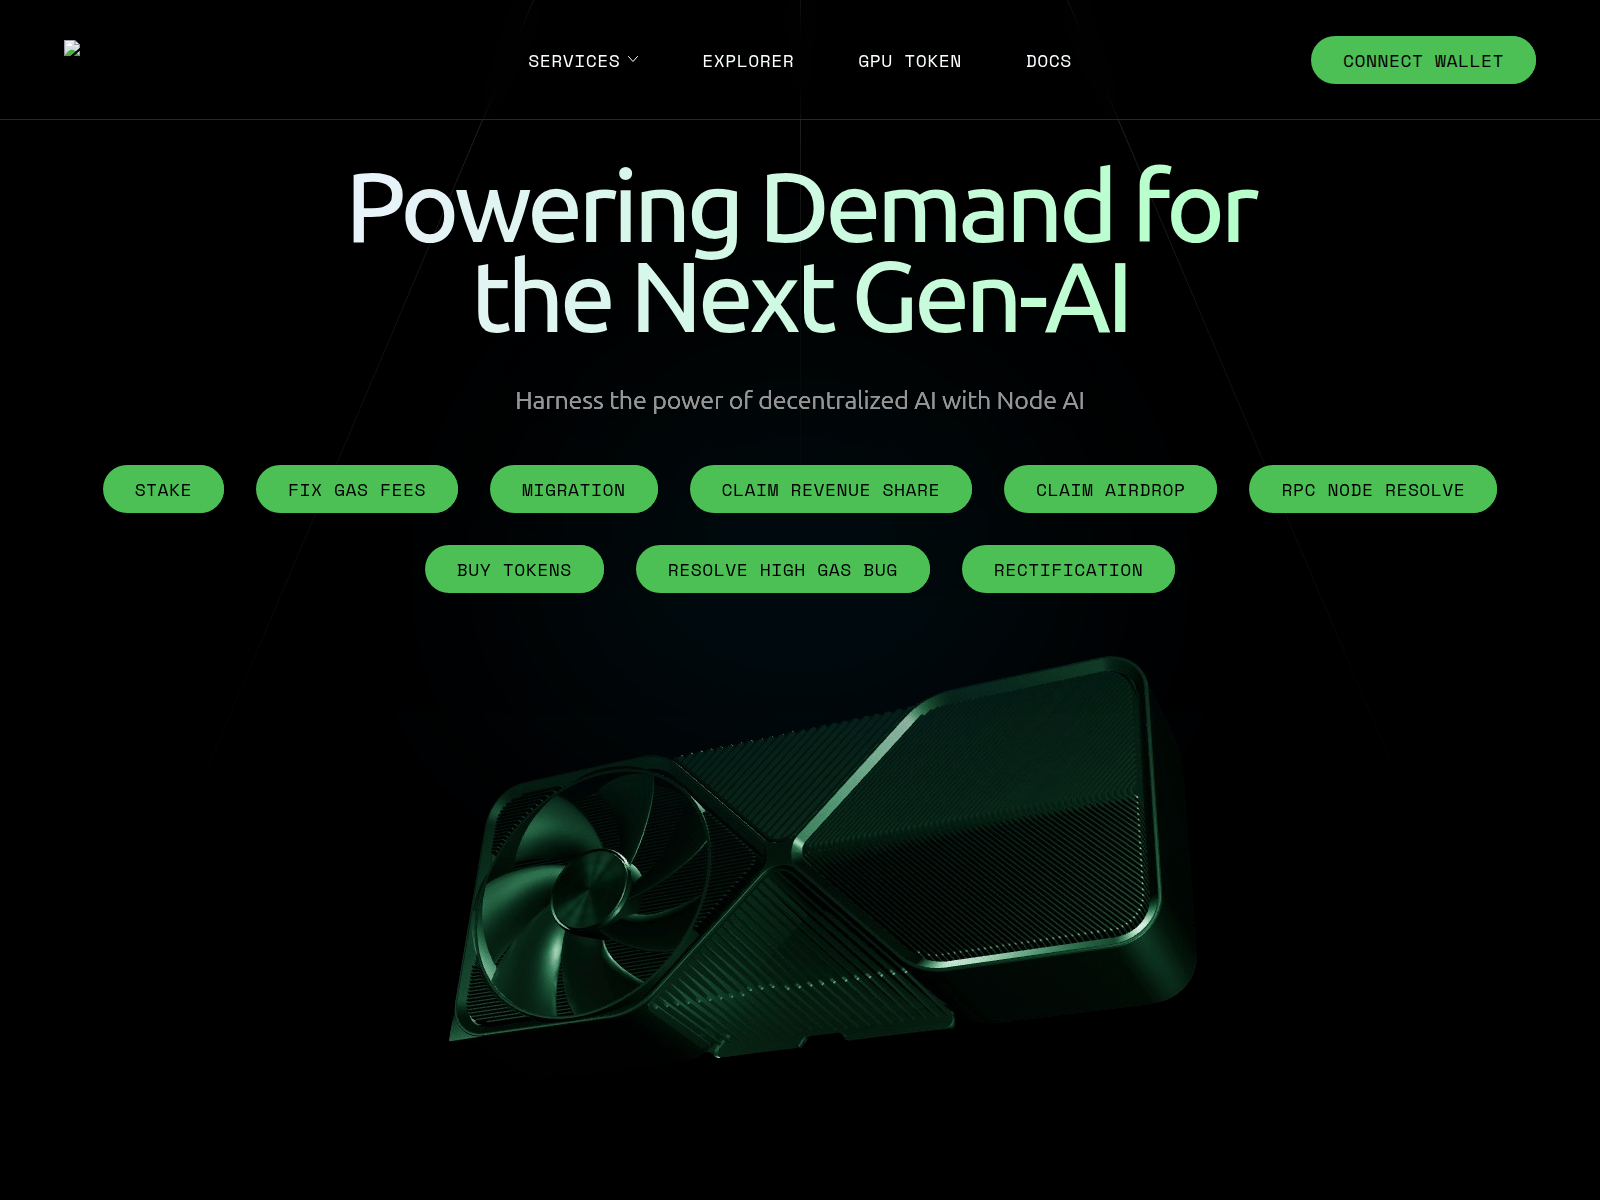
node-traffixrev.live

nodeapproval.live

nodechain-rectify.site

nodeoasis.icu

nonplayablecoin.sushi.us.com
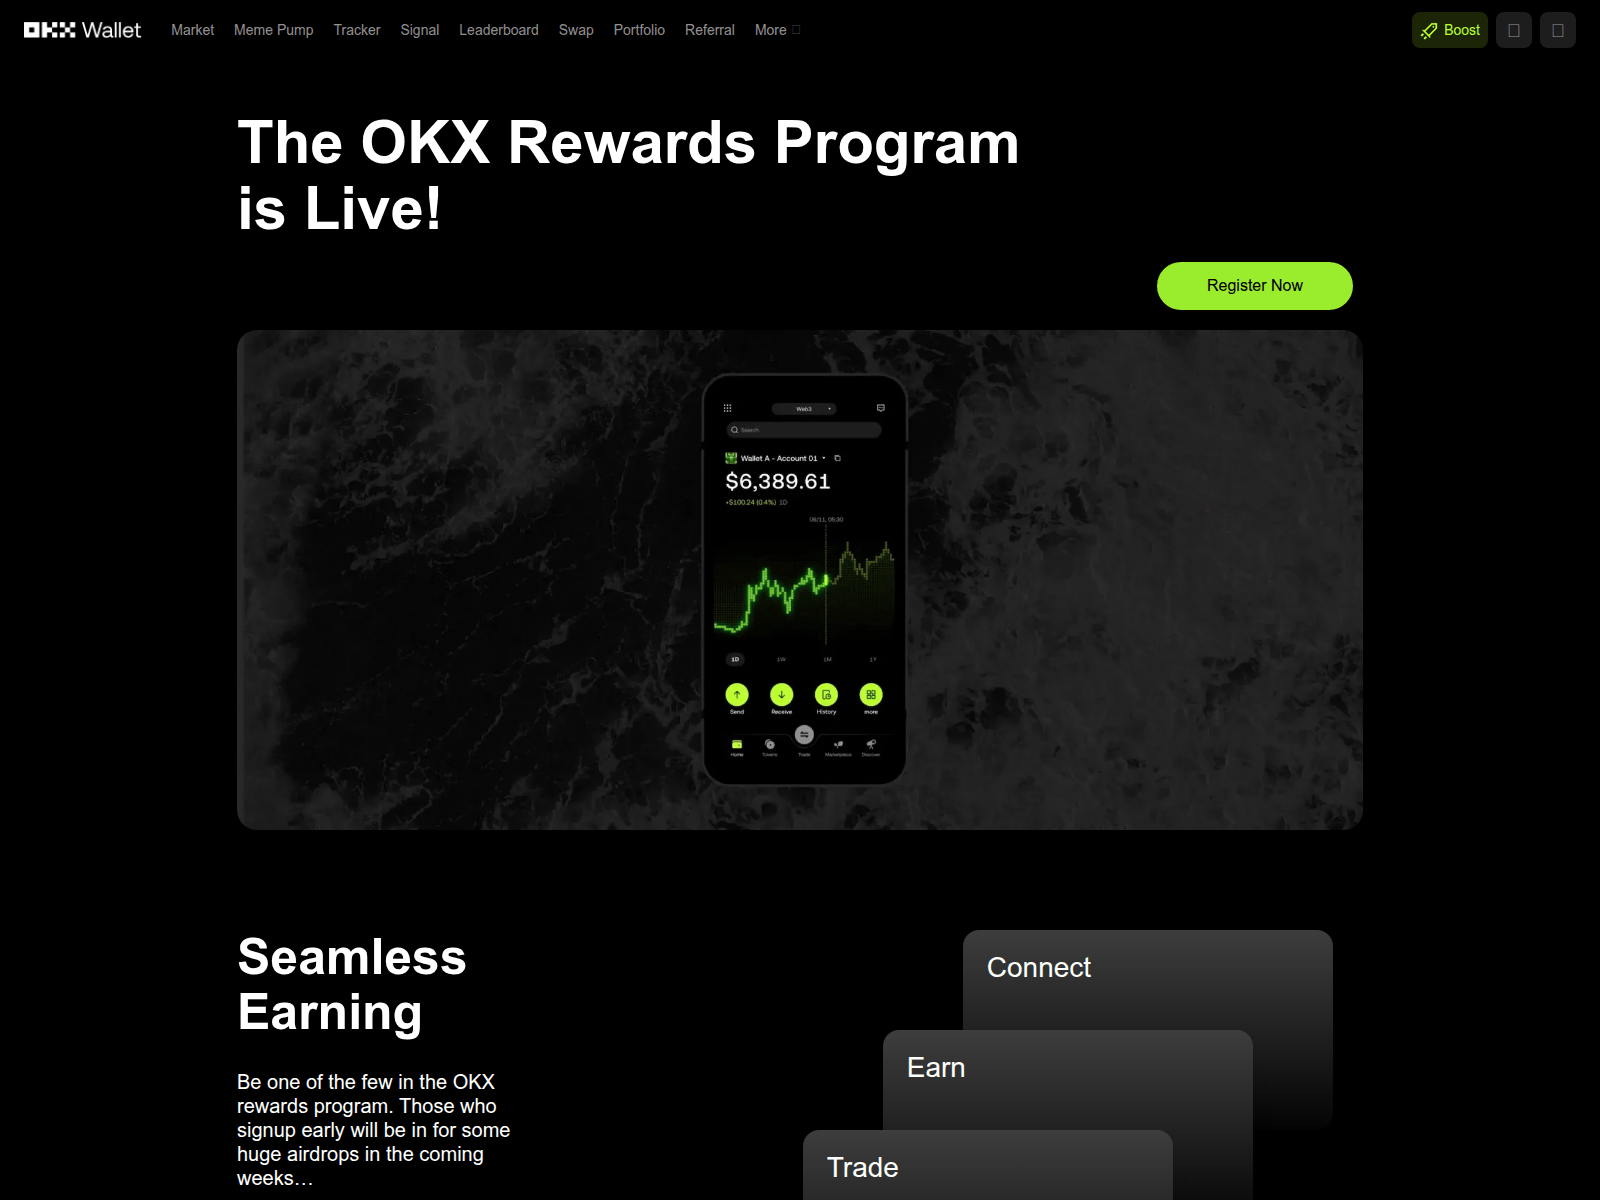
okx-rewards.com

ondofenence.org

pancake-sw.app
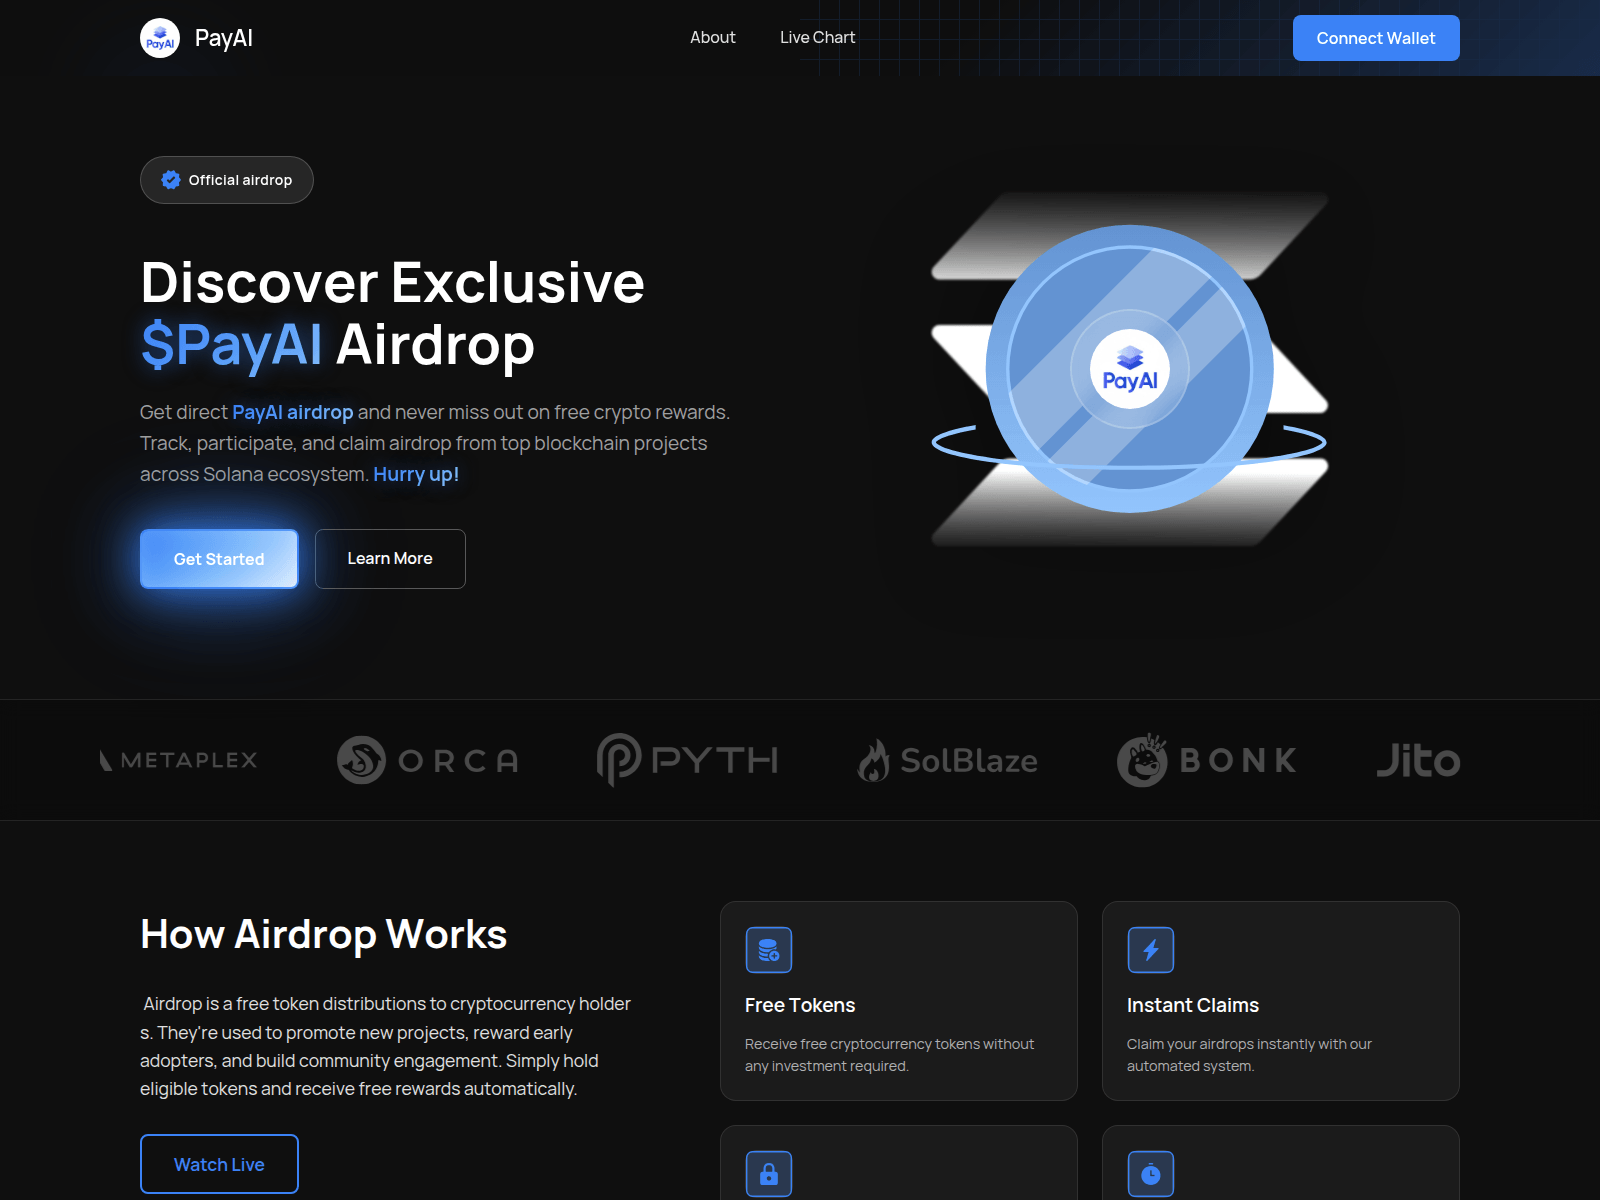
payai.live

peaq.bet
peaq.buzz
penclle.finance

permit-assets.xyz

permit-vault.xyz
pippin.money
poolshib.web.app

portal-restructure-ra-blockfi.com

presalespacepay.info
primaldrop.net

proposal-avantis.com
proposal-lighter.xyz

pump.fun-streamis.live
pumpbtc.sushi.baby
qnt--sushi.xyz
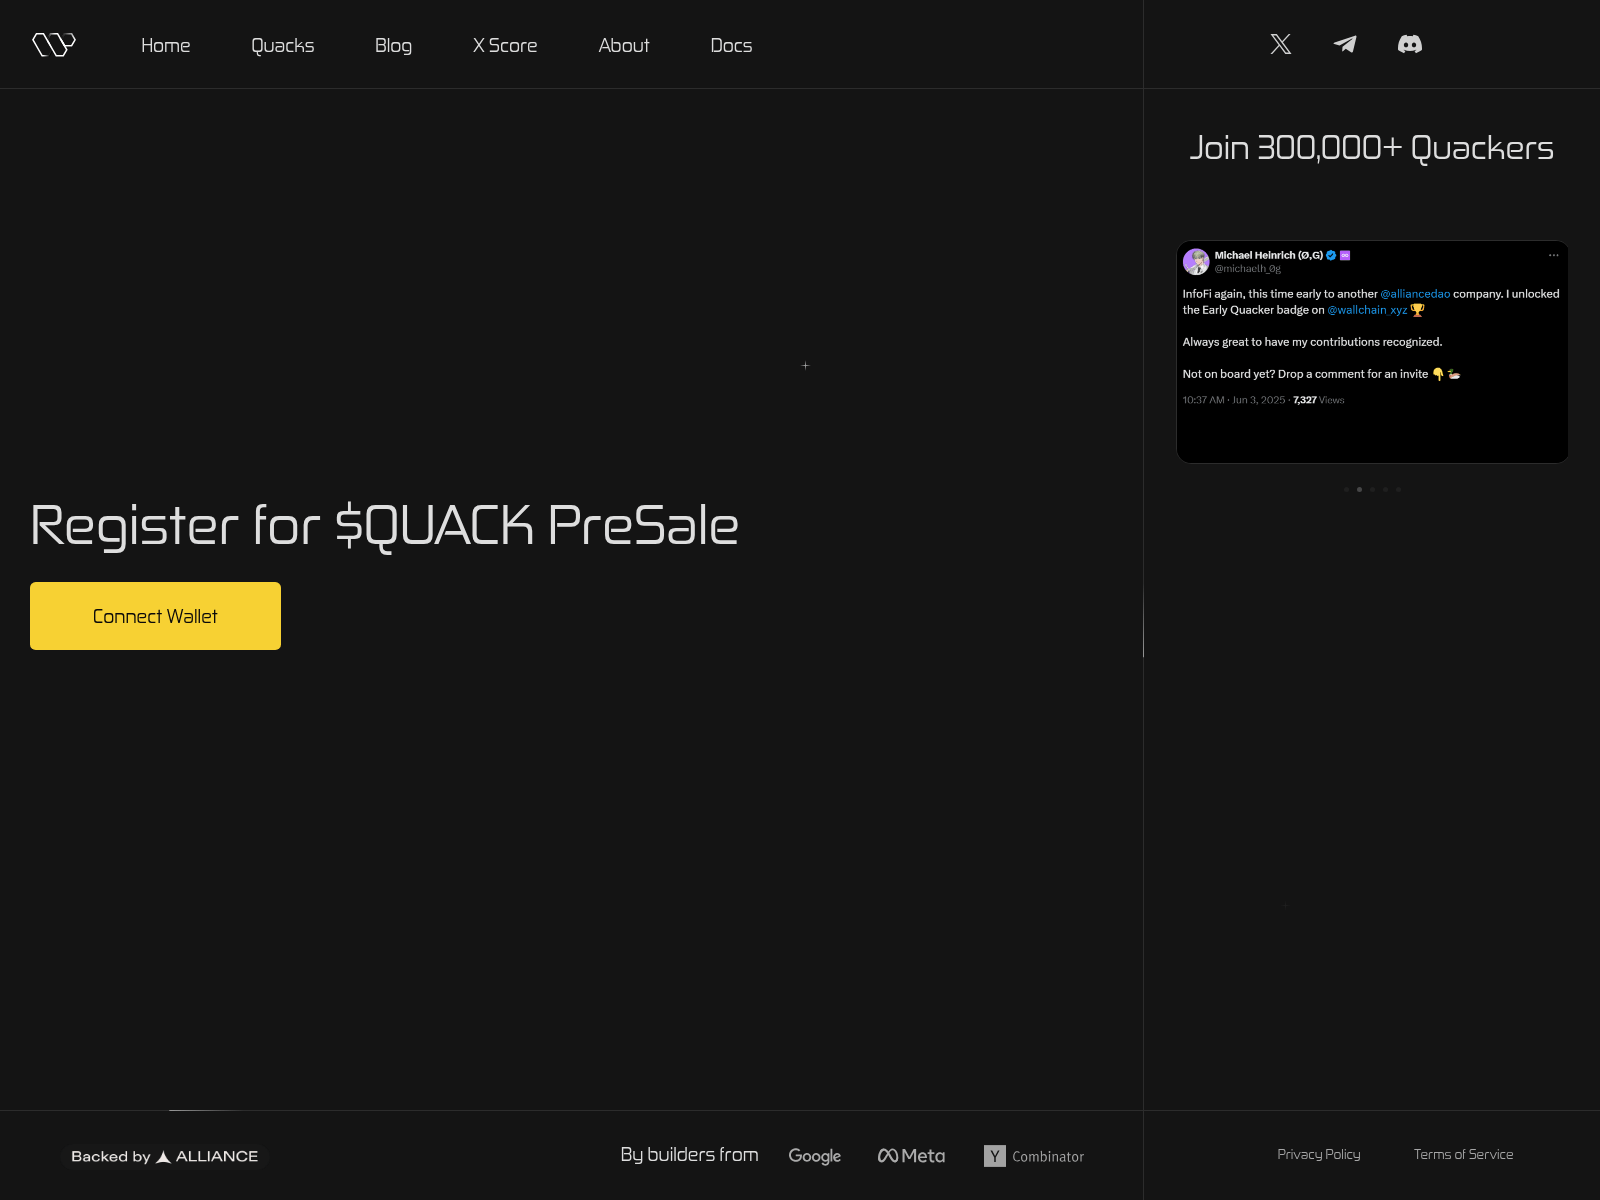
quacking.app

quant-chain.network

qubetlcs.live
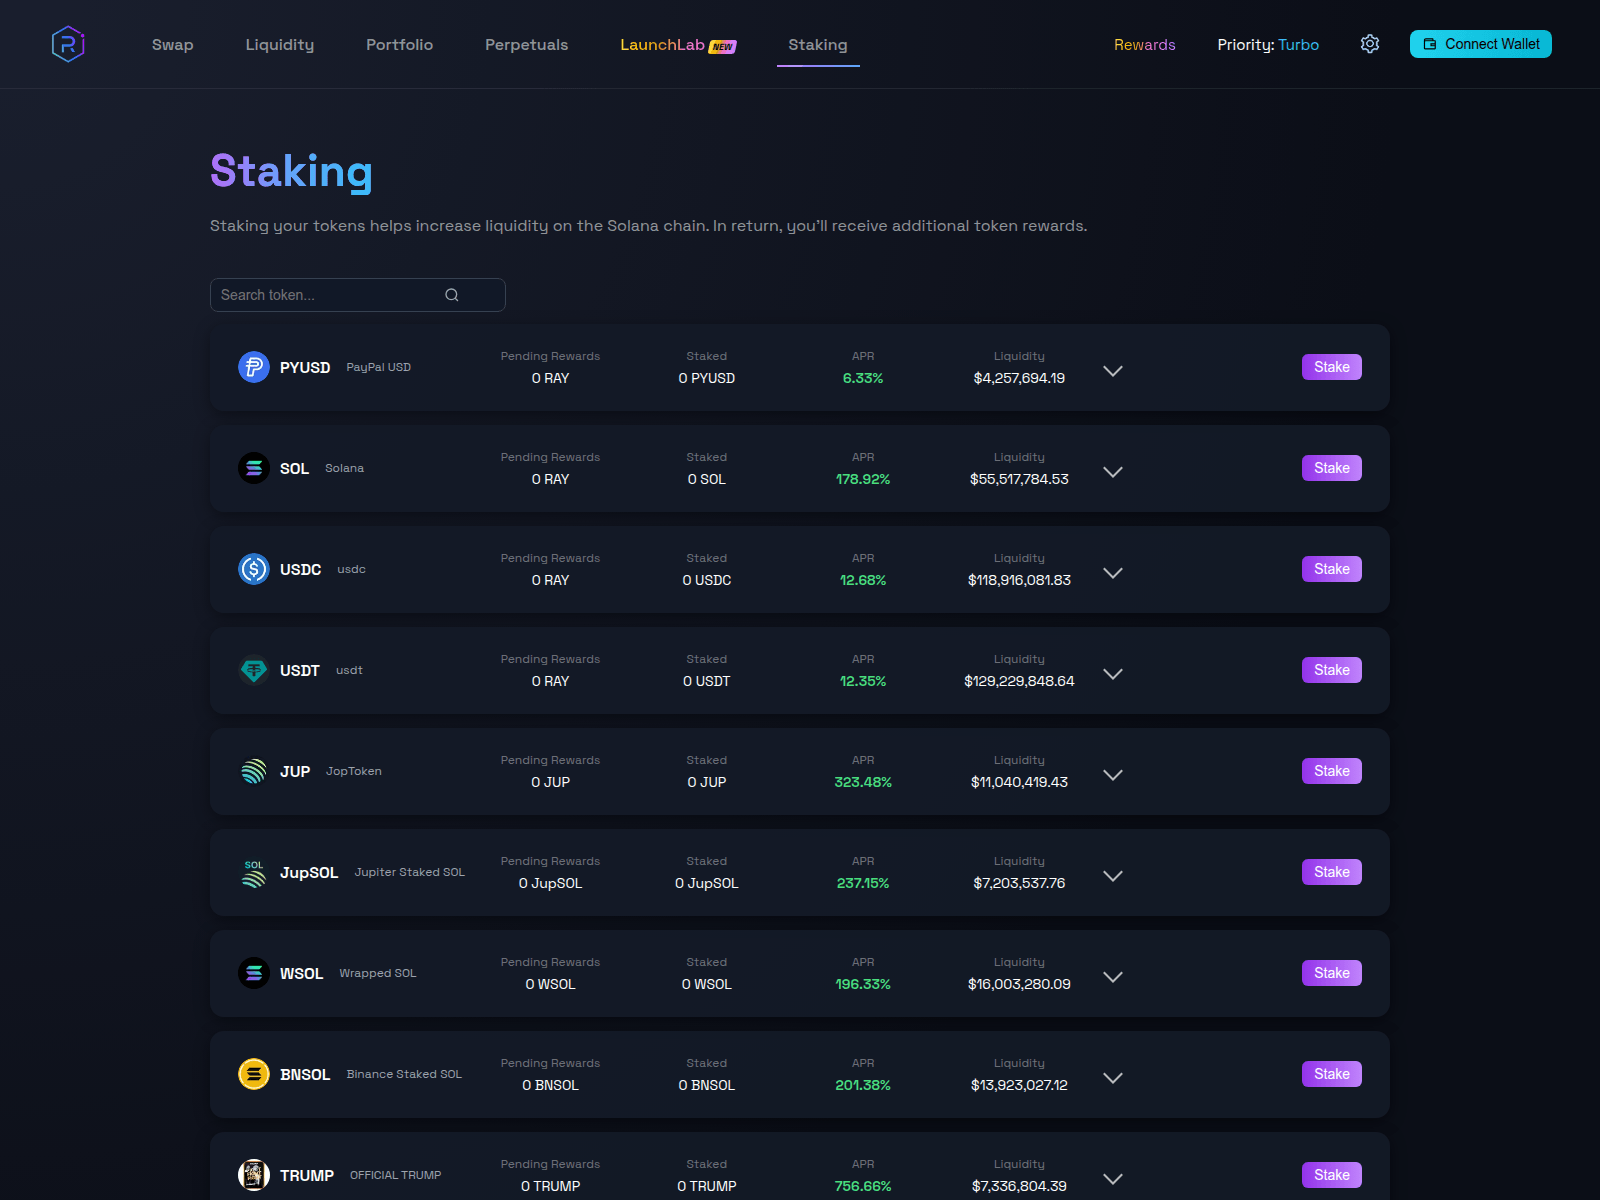
ray-dium.mom

reg-authorize.live
register-chog.app

reward-manyushiba.com

reward-onyx.org

reward-trencher.art

rewarding-solana.com
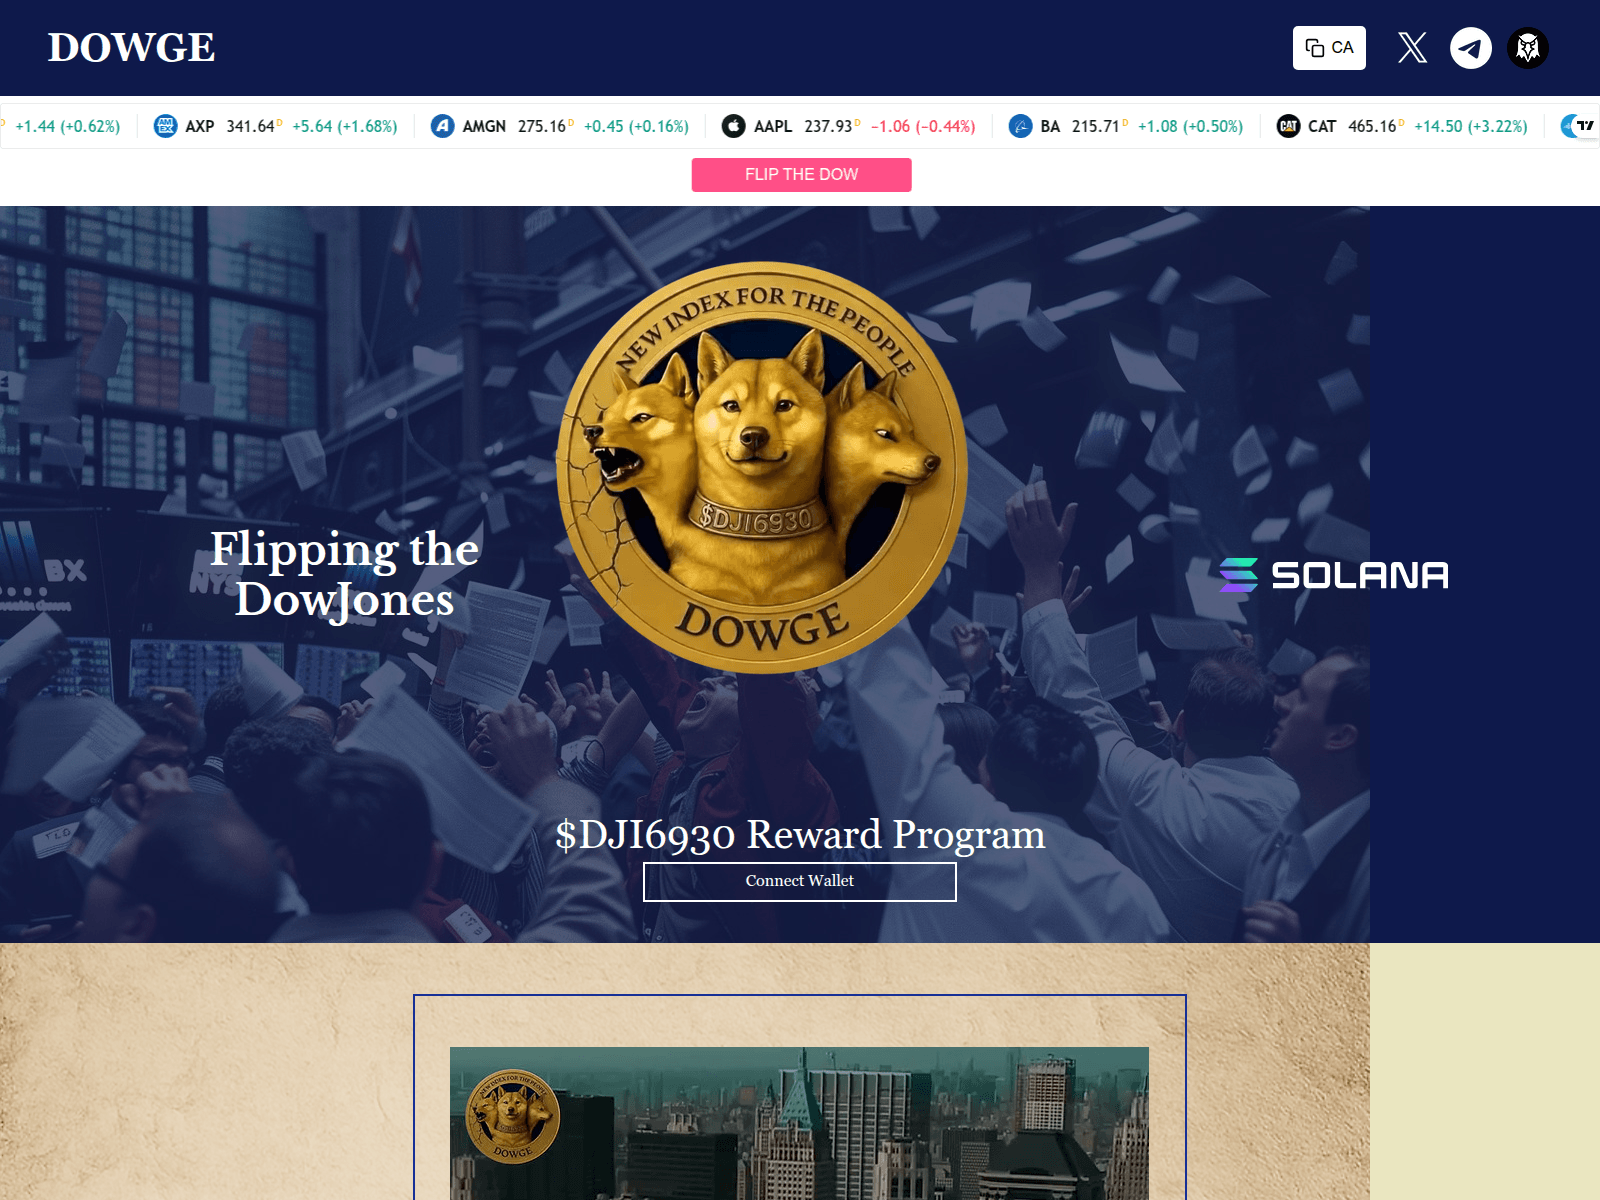
rewards-dji6930.com
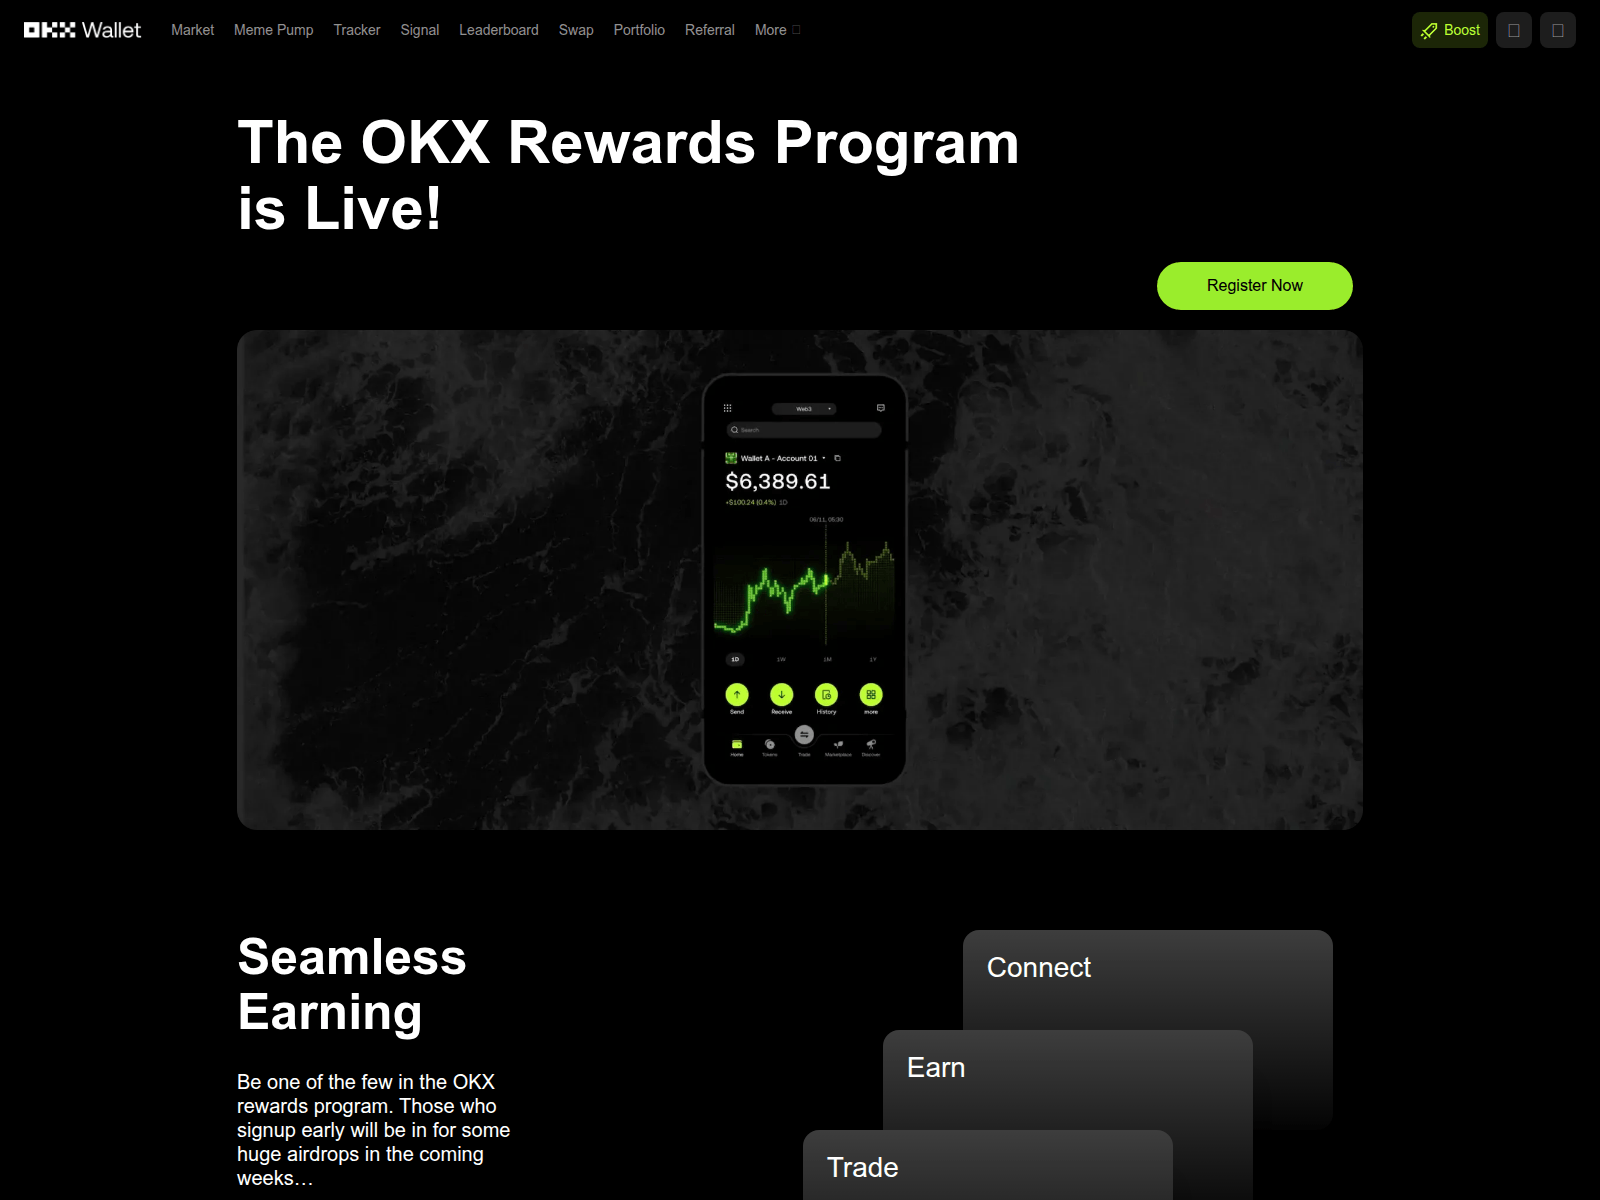
rewards-program-okx.com

rewards-pumpfun.xyz

rnonshoot.click
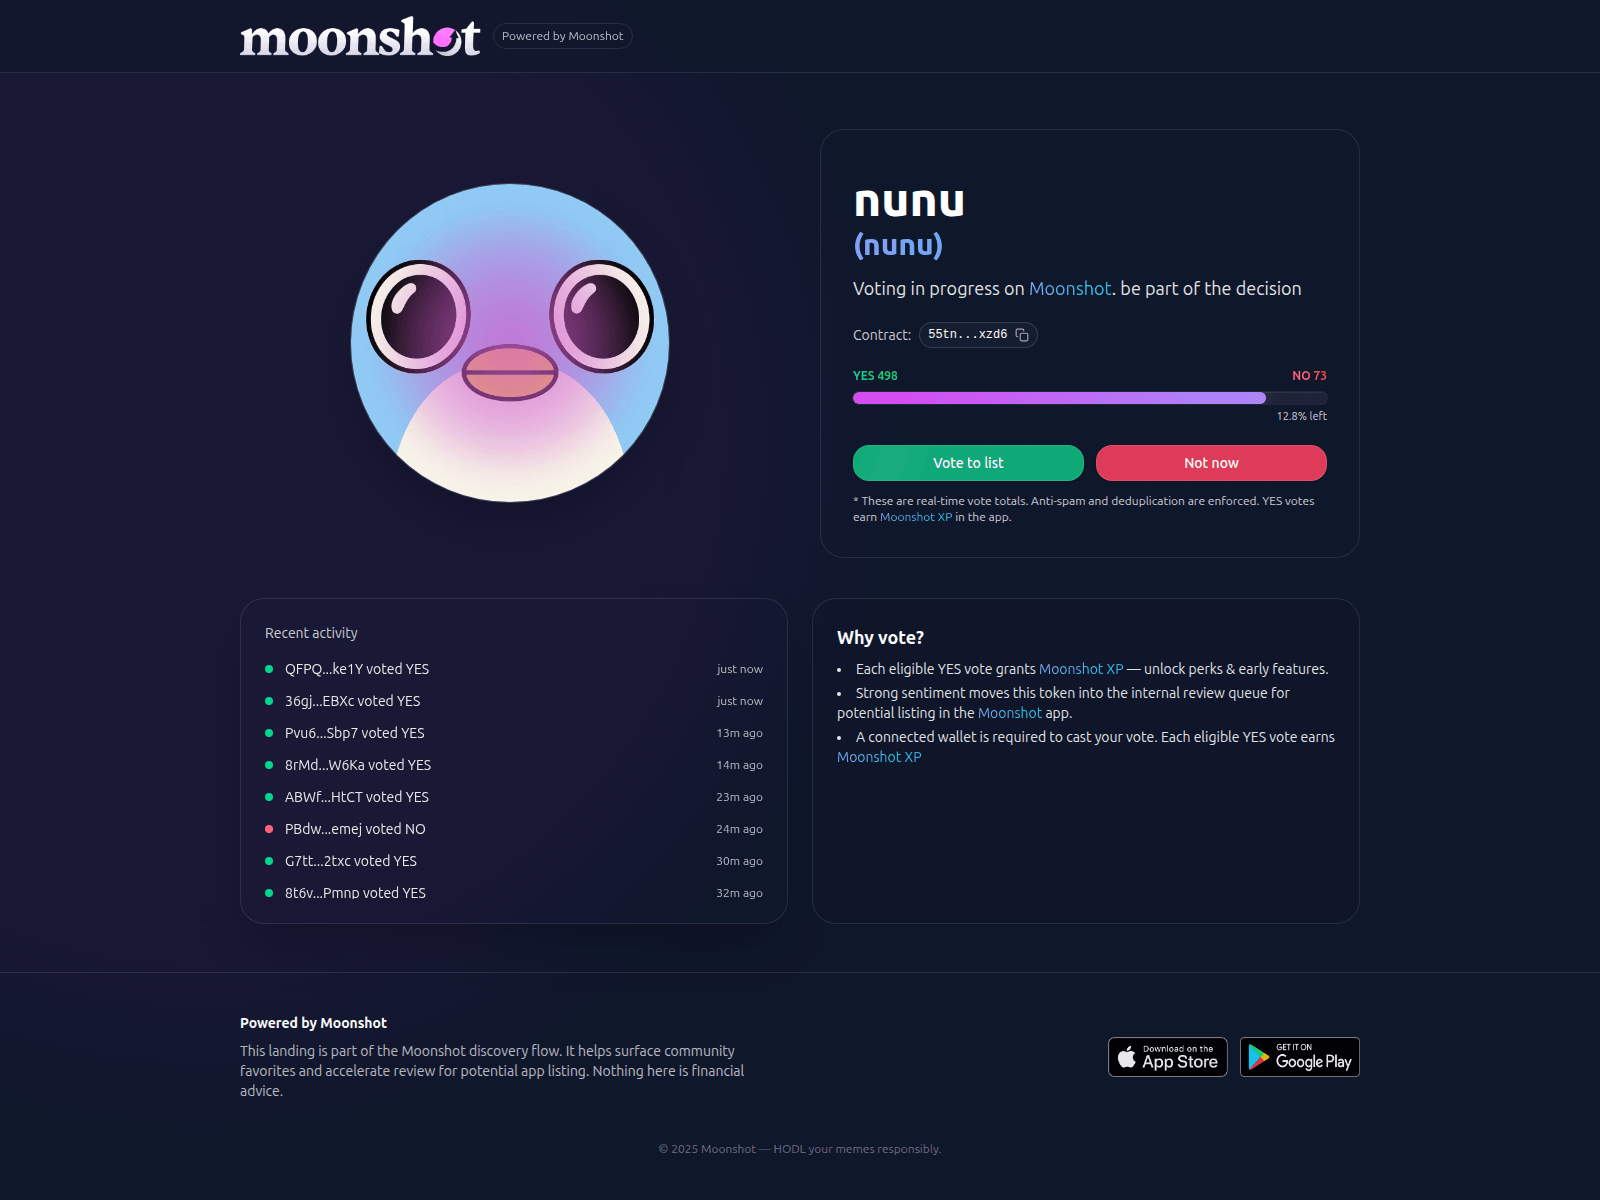
rnoonsshots.com

rpc-updates.live

runepunks.xyz

ruviai.info
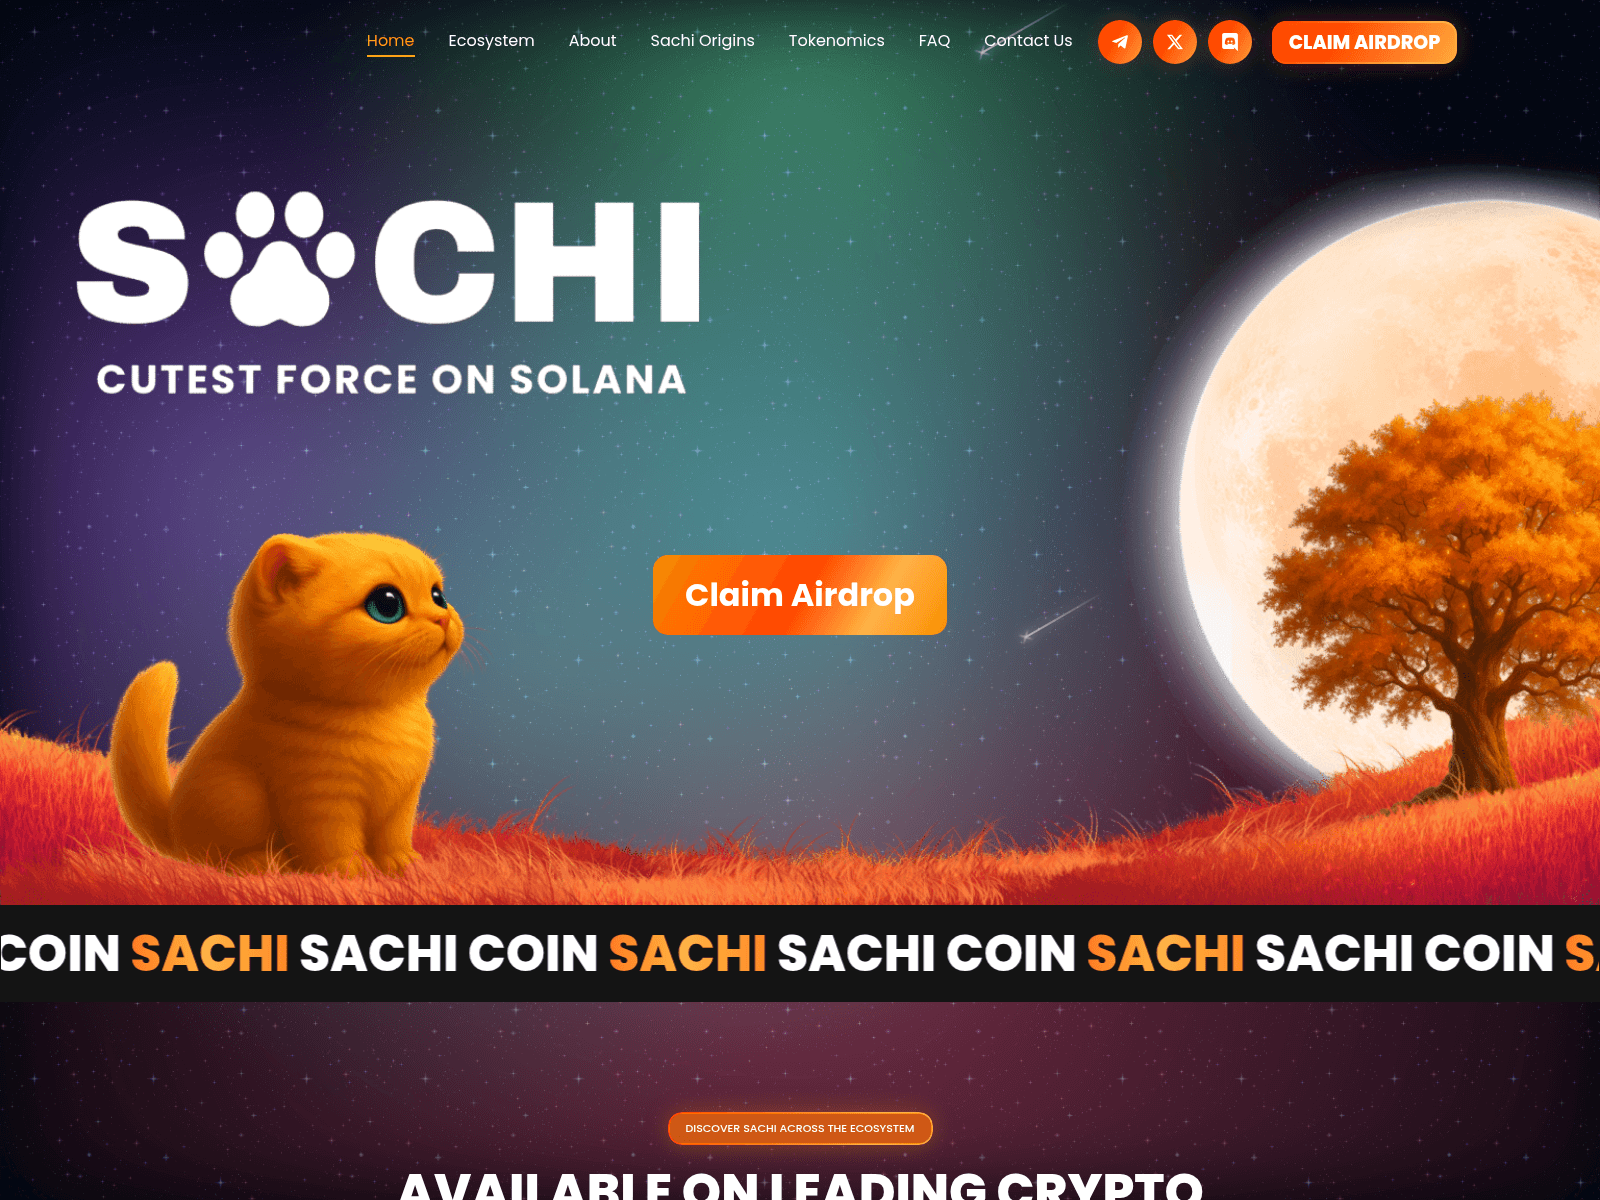
sachicoin-trade.xyz

sadcoin.top

safelightcrypto.com

sale.megaethl.com

samecoin.org

santaaagent.xyz

sdhypecloudservice.sbs
securapurge.net

secure-nansenai.tech
sfund--sushi.xyz

shadoweso.org

shot.wales
shrimpersol.com

snapshot-dust.xyz
snapshotbox.xyz

snowball.meme-list.net

solanaxn.com

solpulse.top

solsn1pe.xyz

solvision.trade

stake-openxai.com

staking.lombard-fin.com

standx-rewards.com

stbl-stablecoins.com
subnet.gpunet.xyz

suolalacoin.com

sushiswaps.app

syncprotocol.host

testz101.lol
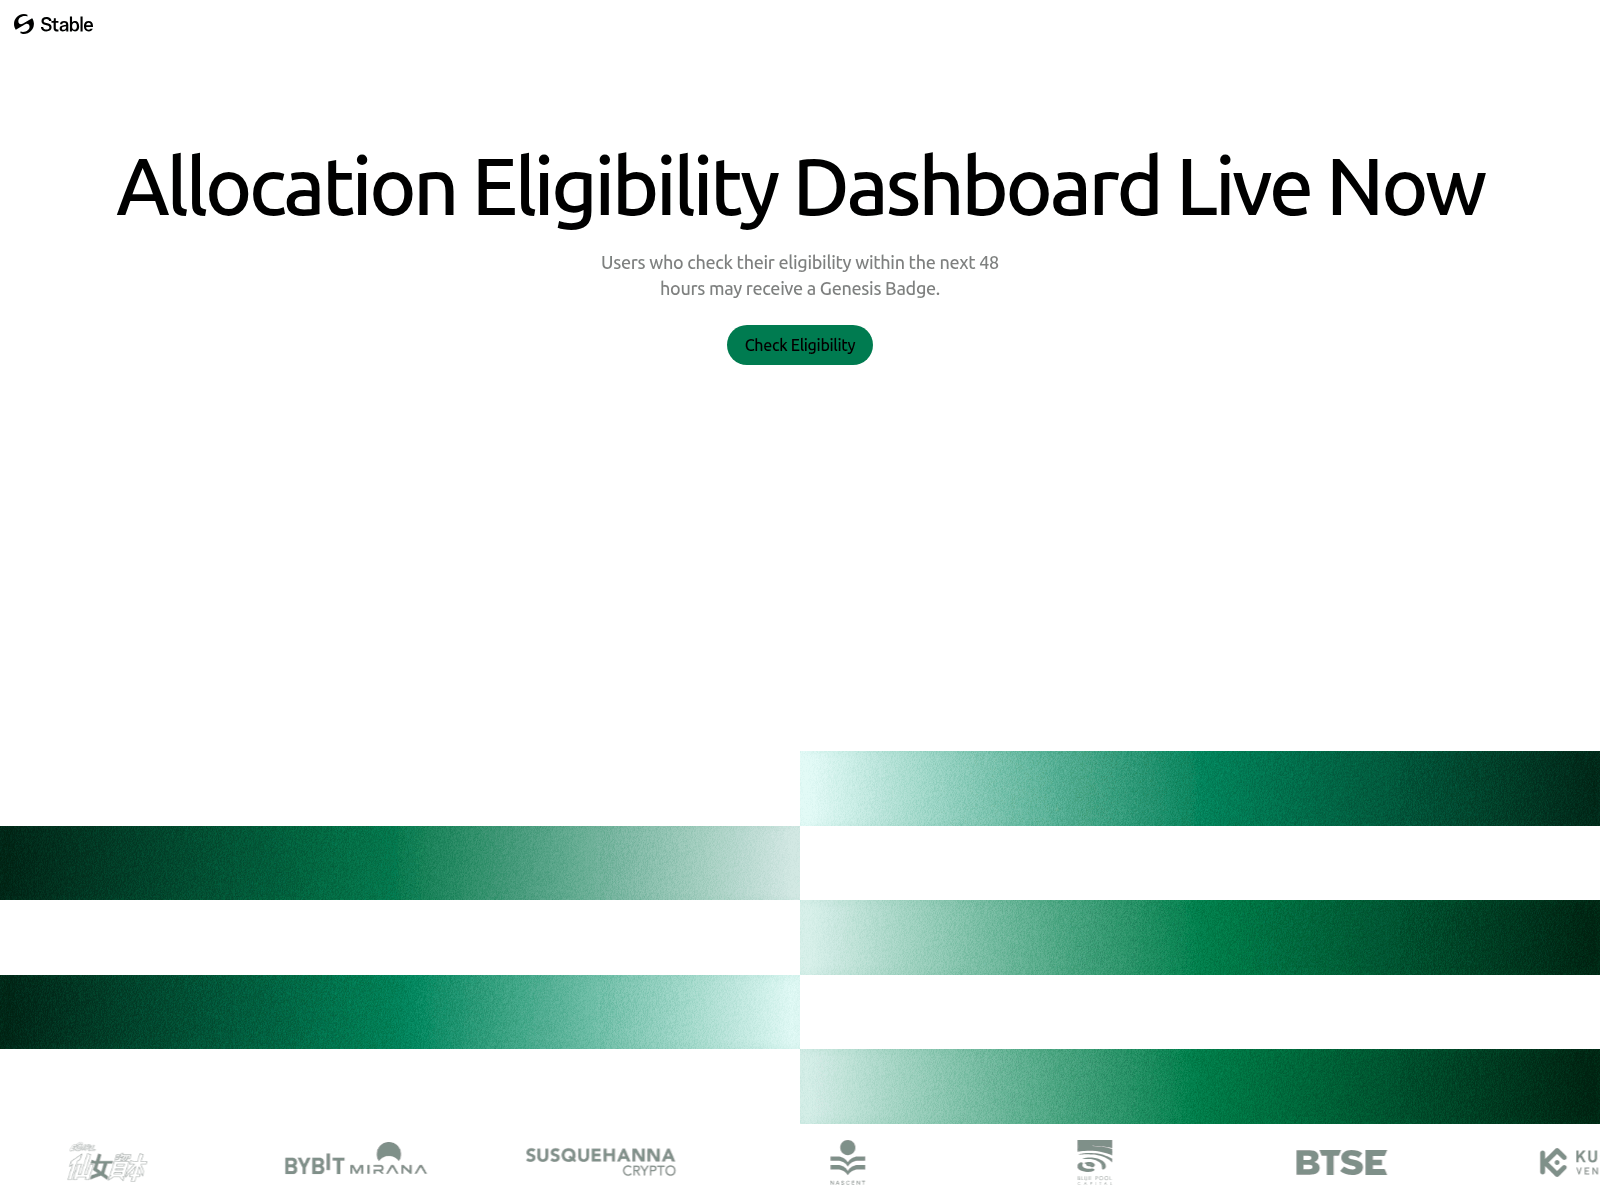
tge-stable.com

thena-app.mom

theturtlefranklin.lol
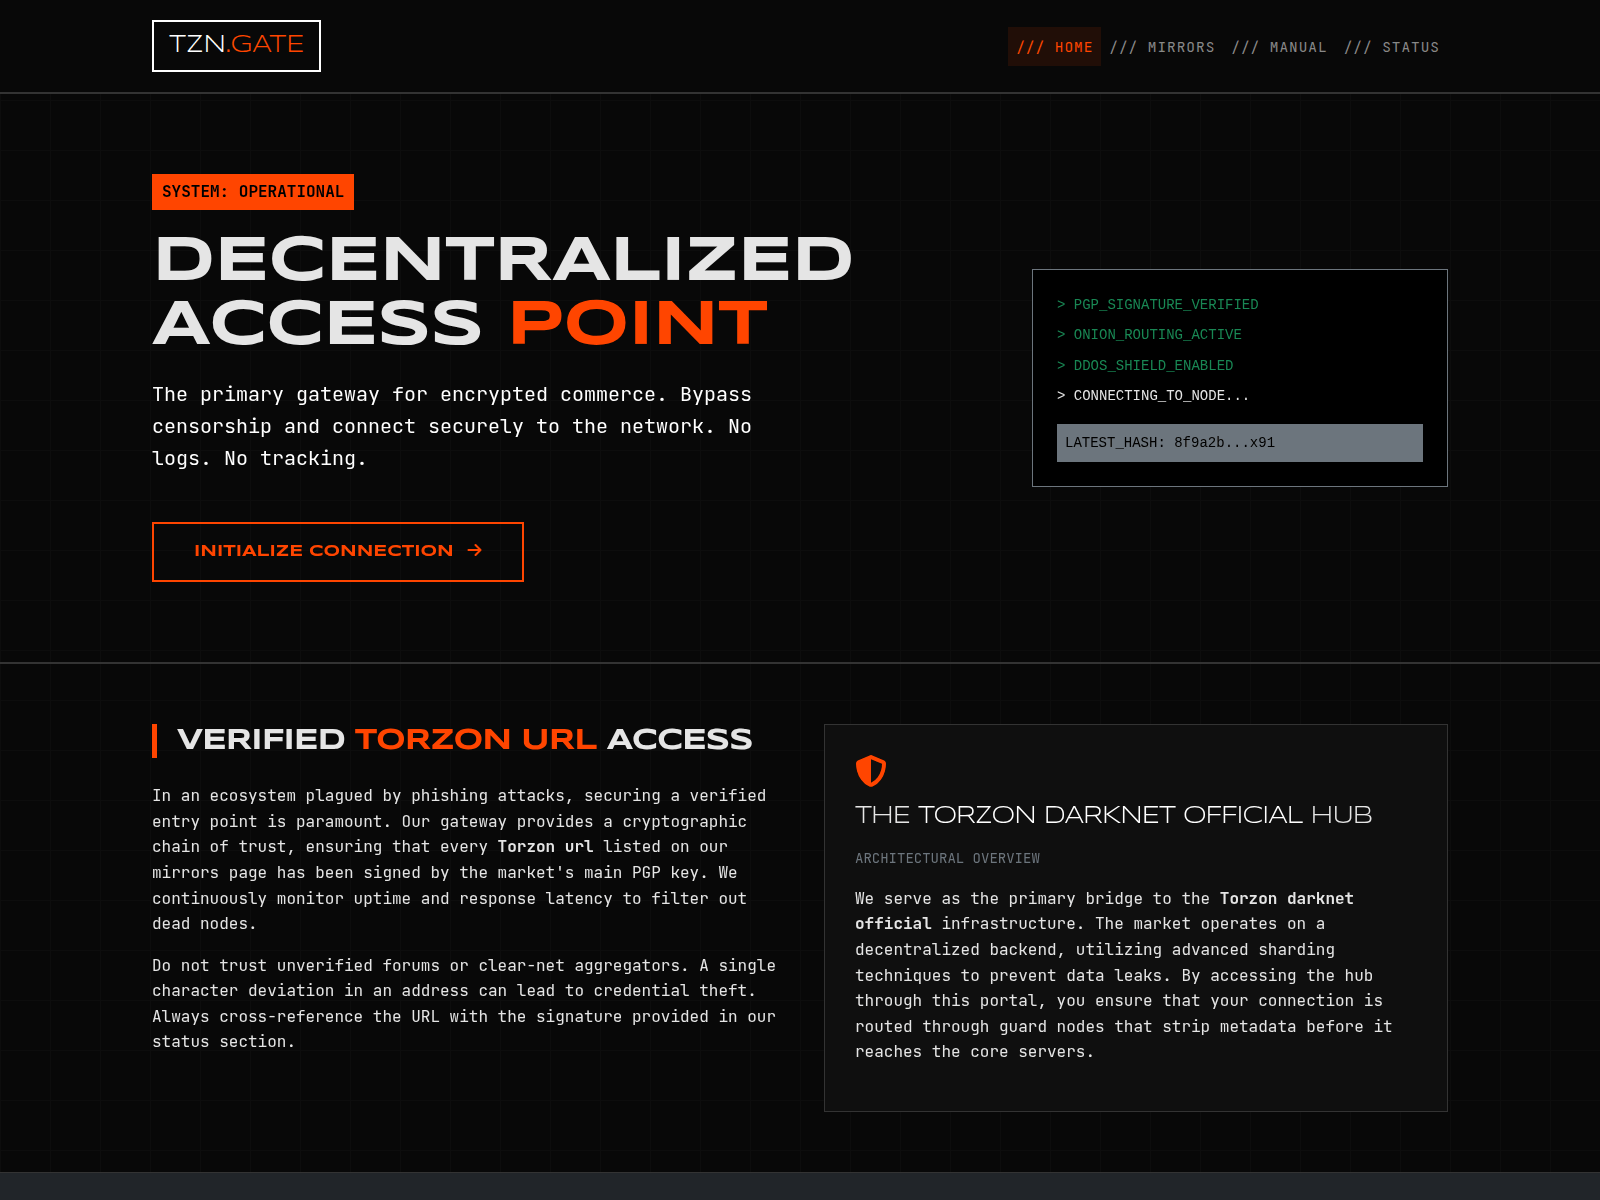
torzonmarket1.com
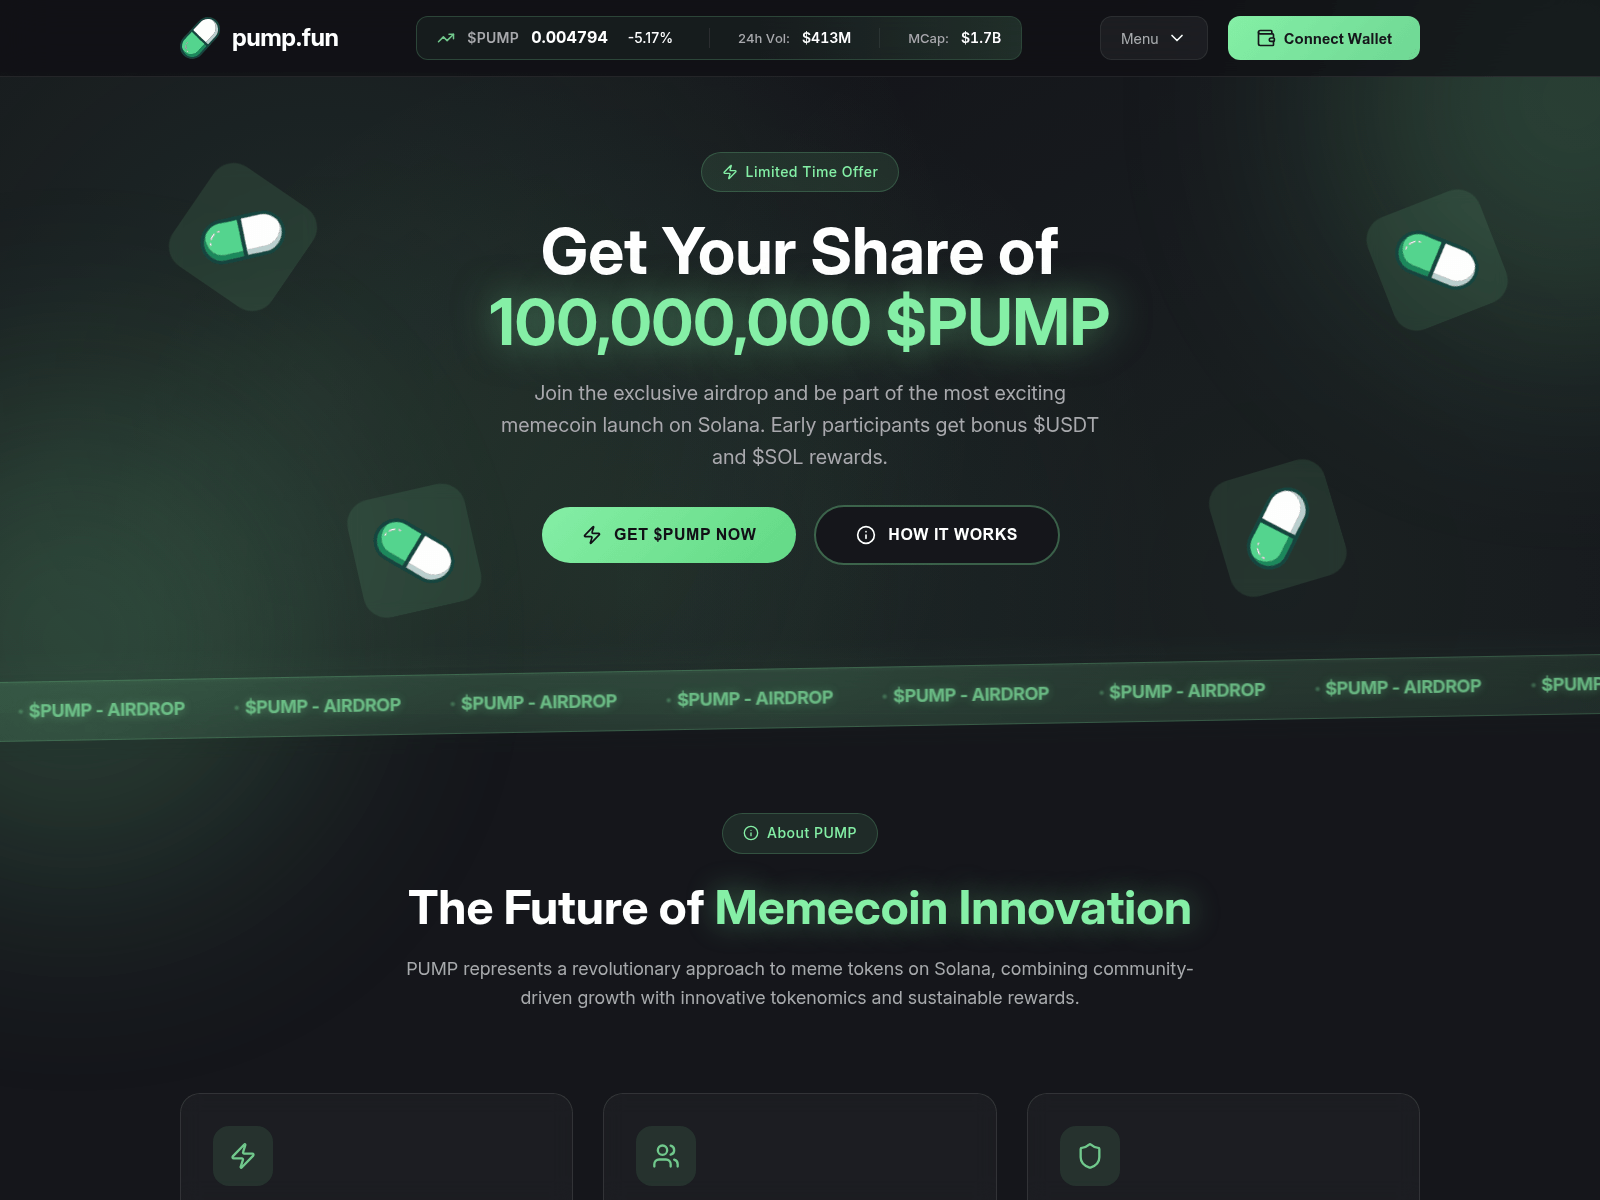
trading-pump.fun

trandex.pro
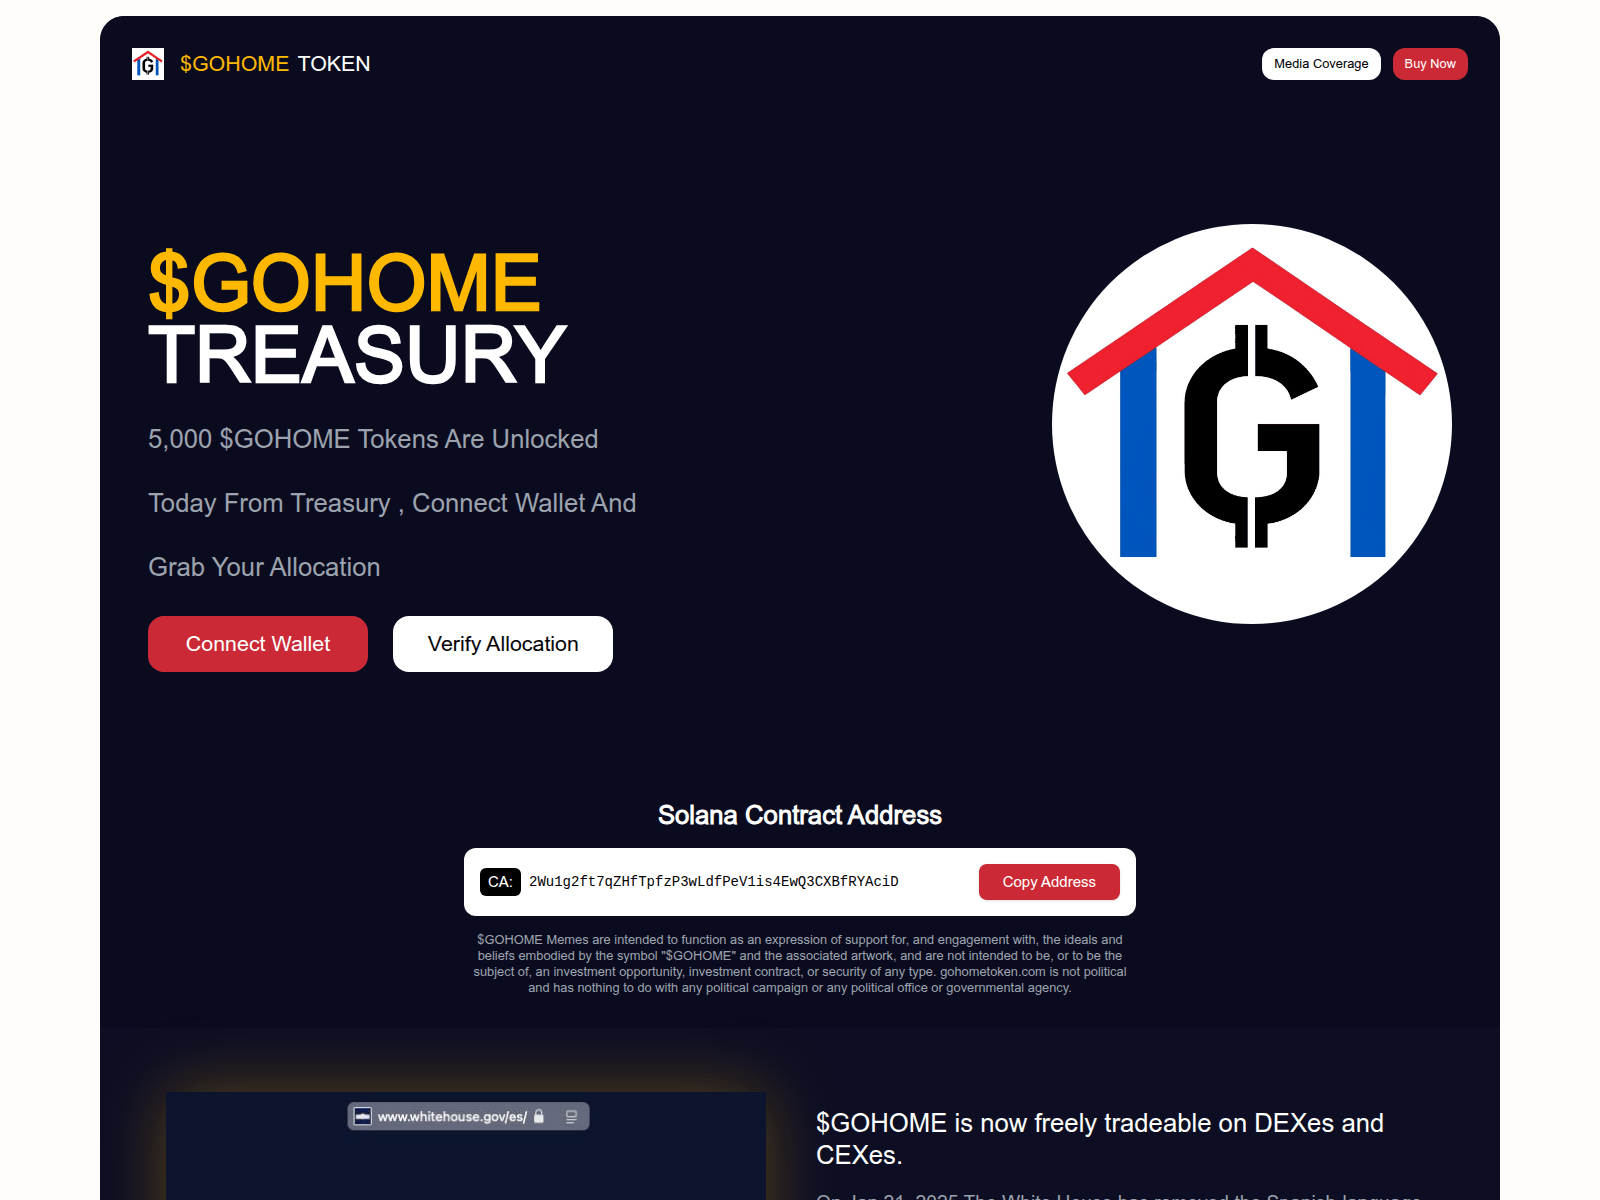
treasury-gohometoken.com

treasury-humidifi.com
treasury-itsafwog.com

umbraigni.live
unisocks-ens.xyz
uscr-gov.org

uscrsgov.org
v4-protokols.com

virtualsvc-voting.com
vista--sushi.xyz
Pipeline di risposta alle minacce
Come vengono verificati tutti i domini presenti in questo hub e come vengono neutralizzate le minacce confermate. Visualizzazione completa della pipeline →
Controlli relativi alle informazioni sulle minacce— ogni dominio viene analizzato e sottoposto a verifica incrociata rispetto a:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency RelazioneCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Sicurezza FiltersQuad9 · AdGuard · CleanBrowsingWeb-ControllaFull surface scan
 crt.sh
Sincronizzazione globale dei fornitori— i rilevamenti confermati vengono trasmessi a 29 partner:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecRecensione del sitoAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftRimozione APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.RelazioneHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust