Lompat ke laporan keamanan
Keamanan domain dan intelijen ancaman
worldlibertyfs.com favicon

worldlibertyfs.com

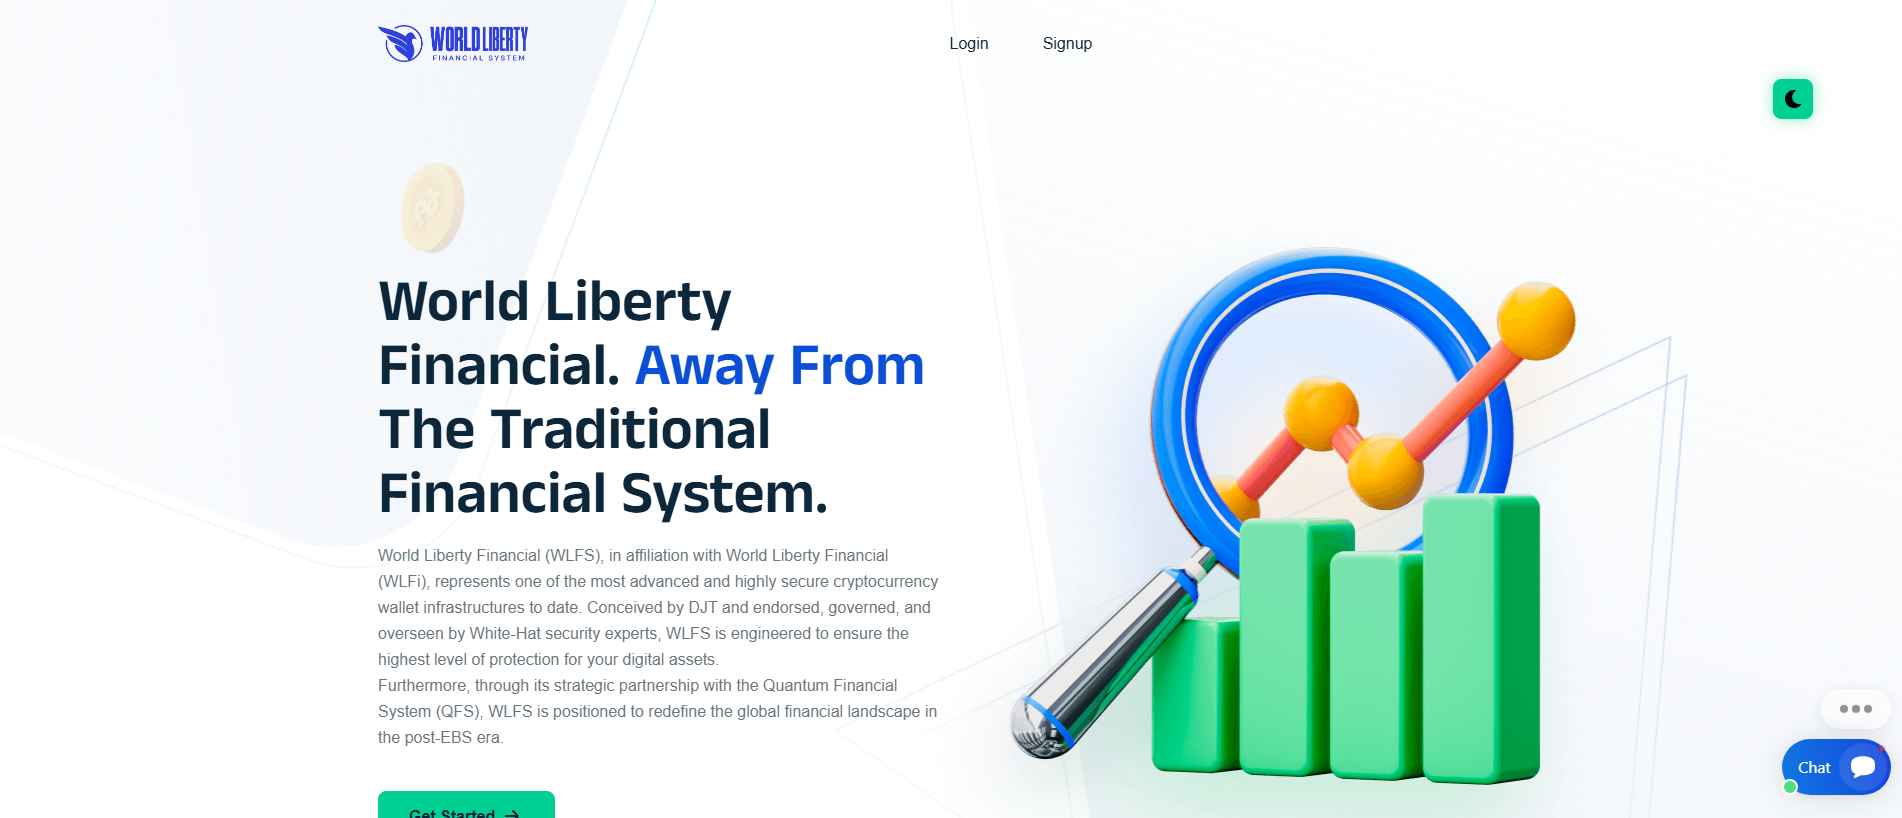
“World Liberty Financial System - We’re embracing the future with crypto and leaving the slow and ou…”

Putusan ancaman Kritis 85/100 skor bukti
Ketersediaan Konten tidak tersedia Konten tidak tersedia dalam observasi terbaru
Deteksi Total Virus: 5/89 Daftar blokir yang disimpan cocok: 2 URLQuery threat systems: 2 alerts Peniruan identitas merek: MetaMask Domain muda: 28 berumur hari
OTX: 3 refs 14/09/2026 MetaMask 1 Report Sent
Actions API
⚠️
Domain ini telah ditandai sebagai berbahaya
Mesin keamanan melaporkan deteksi: 5. Daftar blokir publik yang melaporkan kecocokan: 2. Berhati-hatilah — jangan memasukkan kredensial atau informasi pribadi.
Ringkasan laporan

worldlibertyfs.com — Konten tidak tersedia. Peniruan identitas merek: MetaMask; Jenis penipuan: Impersonation. Ringkasan bukti: VirusTotal 5/89 (ChainPatrol, alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, Netcraft); URLQuery 2 alerts; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 85/100. Registrar: Gransy, s.r.o.

Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.

Ringkasan bukti

KRITIS
Skor
85/100

Assessment
Stored evidence for worldlibertyfs.com: VirusTotal recorded 5 detections among 89 scanners on 2026-09-14. That ratio reproduces the stored check in its original units and is not converted into another measure. MetaMask and SEAL appear as named external blocklist observations for worldlibertyfs.com. Each item in this report remains at the scope supplied by its dated source record.

Detection Evidence
VirusTotal records 5 detections among 89 scanners in the stored snapshot dated 2026-09-14. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-09-14 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.

Source Context
MetaMask and SEAL are recorded as named external blocklist observations for worldlibertyfs.com in the snapshot dated 2026-09-14. The stored MetaMask and SEAL blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains worldlibertyfs.com as a publisher record. That PhishDestroy record is counted separately from the MetaMask and SEAL external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.

Reachability and Timeline
The record first observed worldlibertyfs.com on 2026-09-14. The MetaMask and SEAL blocklist snapshot is dated 2026-09-14 and remains a separate event in the stored timeline. The registration date is separately recorded as 2026-08-23. A URLScan reference was stored on 2026-09-14 as a dated artifact for review. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.

Registration and Infrastructure
For worldlibertyfs.com, the registrar field records Gransy, s.r.o.; this is kept as an exact source value. The source stores 198.251.84.200 as the observed address in this record. The registration date for worldlibertyfs.com is recorded as 2026-08-23. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.

Conclusion
The worldlibertyfs.com record states that VirusTotal recorded 5 detections among 89 scanners on 2026-09-14. MetaMask and SEAL remain named blocklist observations from the snapshot dated 2026-09-14. PhishDestroy remains a separate publisher catalogue entry in the stored record. For worldlibertyfs.com, the registrar field records Gransy, s.r.o.; this remains separate from the other source fields. The observed address field in this record contains 198.251.84.200. The supported conclusion is bounded to the exact stored observations for worldlibertyfs.com. Any statement beyond those source values would require additional dated material.

Recommended Actions
Avoid submitting sensitive information to worldlibertyfs.com during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain worldlibertyfs.com as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and MetaMask and SEAL blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to worldlibertyfs.com. The stored record does not justify extending that rule to 198.251.84.200 or to other infrastructure records.

VirusTotal
VirusTotal
5 det.
URLQuery
URLQuery
2 threat alerts
OTX references
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
Sertifikat TLS
Kedaluwarsa atau belum diverifikasi
Usia
28d Very New!
Status terpantau
Konten tidak tersedia
PhishDestroy
Daftar Hapus
Terdaftar
Reports Sent
1
Cakupan data VirusTotal 5 / 89 URLQuery 2 threat-system alerts OTX 3 community references CF Radar scan completed URLScan capture laporan yang disimpan URLScan verdict Analisis selesai TLS Kedaluwarsa atau belum diverifikasi WHOIS 28d old Tangkapan layar 4 captures · 3 sources Scamadviser 80/100
Intelijen Keamanan Jaringan
Threat Detection Systems 2 alerts
Detection System Indicator Verdict Alert
DNS4EU worldlibertyfs.com malicious Sinkholed
Quad9 DNS worldlibertyfs.com malicious Sinkholed

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition Sep 15, 2026 · 01:04 UTC
    Domain state transitioned from alive to dead.
  2. Threat First Observed Sep 14, 2026 · 10:26 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 198.251.84.200.

Alur Tanggapan Ancaman Pipeline

Penemuan
Checks
Reports
Ketersediaan
16/16
Sent Report Recorded
Stored sent-report record for registrar Gransy, s.r.o., hosting provider, 1 abuse contact
abuse@regtons.com
14/09/2026

Status Daftar Blokir Publik

Evasion analysis

Cloaking & traffic-distribution check

Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.

Stored cloaking flag
Not yet scanned
Last cloaking scan

Scanner note: dns_error: raw=dns_error; via=local_dns_prefilter

Live TDS fingerprint check
Seven Keitaro fingerprints plus a crawler-versus-browser comparison, run from the PhishDestroy scanner when this section scrolls into view.
Waiting

Tangkapan tersimpan · 4 sources

Intelijen Domain

Domain
URLScan Verdict Analisis selesai score 0 report ↗
Server / ASN LiteSpeed · AS53667 FranTech Solutions
Reputasi IP abuse score 11/100 4 reports Email SpamPort ScanBrute-ForceWeb App Attack checked 14/09/2026
OTX Tags 2026-09all-domainsblocklistcryptodomaindrainerfraudlivemonthlyphishdestroyphishingscam
Registrar Gransy, s.r.o
Alamat IP 198.251.84.200 LU
LokasiLU Luxembourg, LU
JaringanAS53667 · FranTech Solutions
PendaftaranDibuat 23/08/2026 (28d · Very New!) Expires 23/08/2027
Waktu hingga pertama kali tidak tersedia 14h
Yang kami hitung Waktu yang berlalu sejak laporan penyalahgunaan pertama kali disimpan hingga pengamatan pertama bahwa konten tersebut tidak tersedia. Hal ini tidak dapat menentukan penyebabnya.
Isi setiap laporan Catatan laporan keluar yang disimpan dapat merujuk pada bukti yang tersedia pada saat itu, seperti keputusan vendor, data pendaftaran, detail hosting, klasifikasi, atau tangkapan layar. Halaman ini tidak menyimpulkan secara pasti muatan yang dikirimkan, penerimaan, pengakuan, atau tindakan oleh penerima.
Detail teknisDNS, SAN SSL, cap waktu
Pertama Kali Terdeteksi14/09/2026
DOM Analysisanalyzed 14/09/2026score 85/100
IoC Extractionscanned 15/09/20260 wallet · 0 Telegram IoCs
Submitted URLhttps://worldlibertyfs.com/
Server namans5.asurahosting.comns5.my-control-panel.comns6.asurahosting.comns6.my-control-panel.com
TLS Observationscanned 14/09/2026
Favicon Hash
ID kasus
Judul Halaman
World Liberty Financial System - We’re embracing the future with crypto and leaving the slow and outdated big banks behind.
Sertifikat TLS
Kedaluwarsa atau belum diverifikasi · Diterbitkan oleh YR2
Referensi Silang Intelijen Ancaman · source references
ScamAdviser Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
Teknologi · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
Laporkan Domain Ini Kirimkan bukti & bantu lindungi orang lain

Analisis VirusTotal

5 / Vendor keamanan 89 menandai domain ini
View on VT
Last analyzed Previous stored snapshot: 5 detections
ChainPatrol
alphaMountain.ai
Forcepoint ThreatSeeker
Gridinsoft
Netcraft
Analisis Performa Situs

Google PageSpeed Insights — mobile performance audit of worldlibertyfs.com · checked Sep 14, 2026

100
Good
Performance
FCP
0.76s
First Contentful Paint
LCP
0.76s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
1.04s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Domain serupa

79 domain serupa tersimpan

Tampilkan semua (67)
metasmask.io insertion Laporan internal metramask.io insertion Laporan internal mewtamask.io insertion Laporan internal mmetamask.io homoglyph Laporan internal mtamask.io omission Laporan internal mwetamask.io insertion Laporan internal nmetamask.io homoglyph Laporan internal metamark.io bitsquatting Laporan internal metamaskj.io addition Laporan internal metammask.io homoglyph Laporan internal metamnask.io homoglyph Laporan internal emtamask.io transposition m-etamask.io hyphenation meamask.io omission meatmask.io transposition meramask.io replacement mertamask.io insertion metaamask.io repetition metaamsk.io transposition metaask.io omission metalmask.io insertion metamaask.io insertion metamadsk.io insertion metamaek.io replacement metamak.io omission metamas.io omission metamasak.io insertion metamasdk.io insertion metamask-io.com various metamasl.io replacement metamasm.io replacement metamsak.io transposition metamsk.io omission metamusk.io vowel-swap metamzsk.io replacement metarnask.io homoglyph metmaask.io transposition metmask.io omission metsamask.io insertion metsmask.io replacement mettamask.io repetition metwmask.io replacement metyamask.io insertion metzmask.io replacement meyamask.io replacement meytamask.io insertion mitamask.io vowel-swap mnetamask.io homoglyph mretamask.io insertion mrtamask.io replacement mstamask.io replacement mteamask.io transposition mwtamask.io replacement rnetamask.io homoglyph matamask.io bitsquatting mdtamask.io bitsquatting metamasi.io bitsquatting metamasj.io bitsquatting metamaska.io addition metamaskk.io addition metamaskl.io addition metamaso.io bitsquatting metamesk.io bitsquatting metamqsk.io bitsquatting metemask.io bitsquatting netamask.io homoglyph xn--metamas-bhb.io homoglyph

Bukti & Laporan Eksternal

Snapshot bukti yang dikirim
Sent: Ledger records: 1 Case ID: PD-20260914-26CD29 Recipient: abuse@regtons.com
Page title stored with report: New Private Tab
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 679.3 KB
PDF notice generated Notice text archived (650 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (Unknown):
International Anti-Cybercrime Regulations
Budapest Convention on Cybercrime
Universal Fraud Prevention Laws
Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.

Apakah Anda Terpengaruh oleh Situs Ini?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Europol
Temukan saluran pelaporan resmi untuk negara UE Anda
National police directory
Waspadalah terhadap penipu yang mengatasnamakan pemulihan! Penjahat dapat menghubungi korban lagi sambil berpura-pura menjadi penyelidik, pengacara, atau agen pemulihan. Jangan membayar biaya di muka atau membagikan kredensial. Pelajari lebih lanjut tentang penipuan dalam proses pemulihan →

Laporkan kepada Pihak Berwenang di Daerah Anda

Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.

Direktori 97 negara
Draf yang dibantu AI — detail insiden diproses oleh penyedia AI Tinjau dan kirimkan sendiri

Periksa Domain Apa Pun

Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik

Pindai Sekarang

Laporkan Phishing

Laporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas

Laporan

Pemberitahuan Ancaman Real-Time

Laporan phishing terbaru dan perubahan ketersediaan yang diamati

Pantau

Tetap Terinformasi, Tetap Aman

Pantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive

Pemberitahuan Ancaman Real-Time Ajukan Banding Terhadap Iklan Ini
HTML · IFRAME

Sematkan Laporan Ini

Bagikan informasi ancaman ini di situs web atau blog Anda

embed.html
<iframe
  src="https://phishdestroy.io/id/embed/domain/worldlibertyfs.com"
  title="PhishDestroy threat report for worldlibertyfs.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>