VirusTotal
15 / 91
Laporan


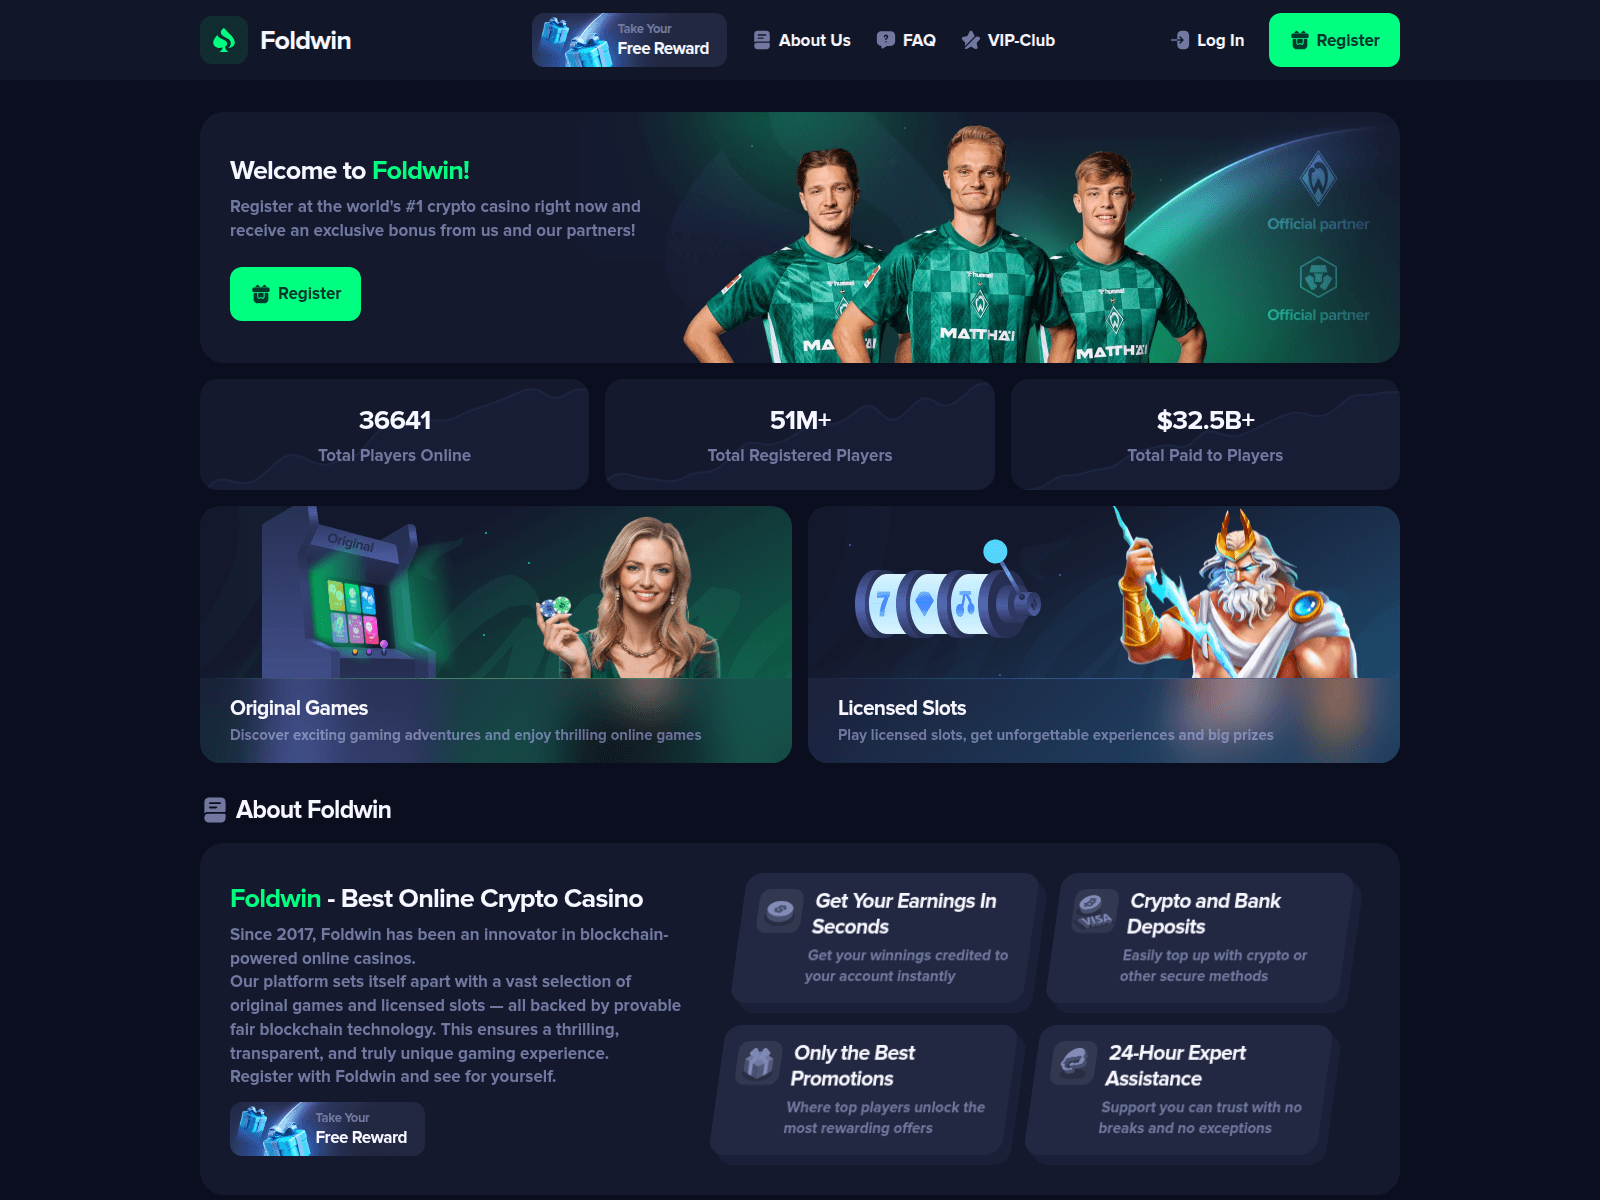
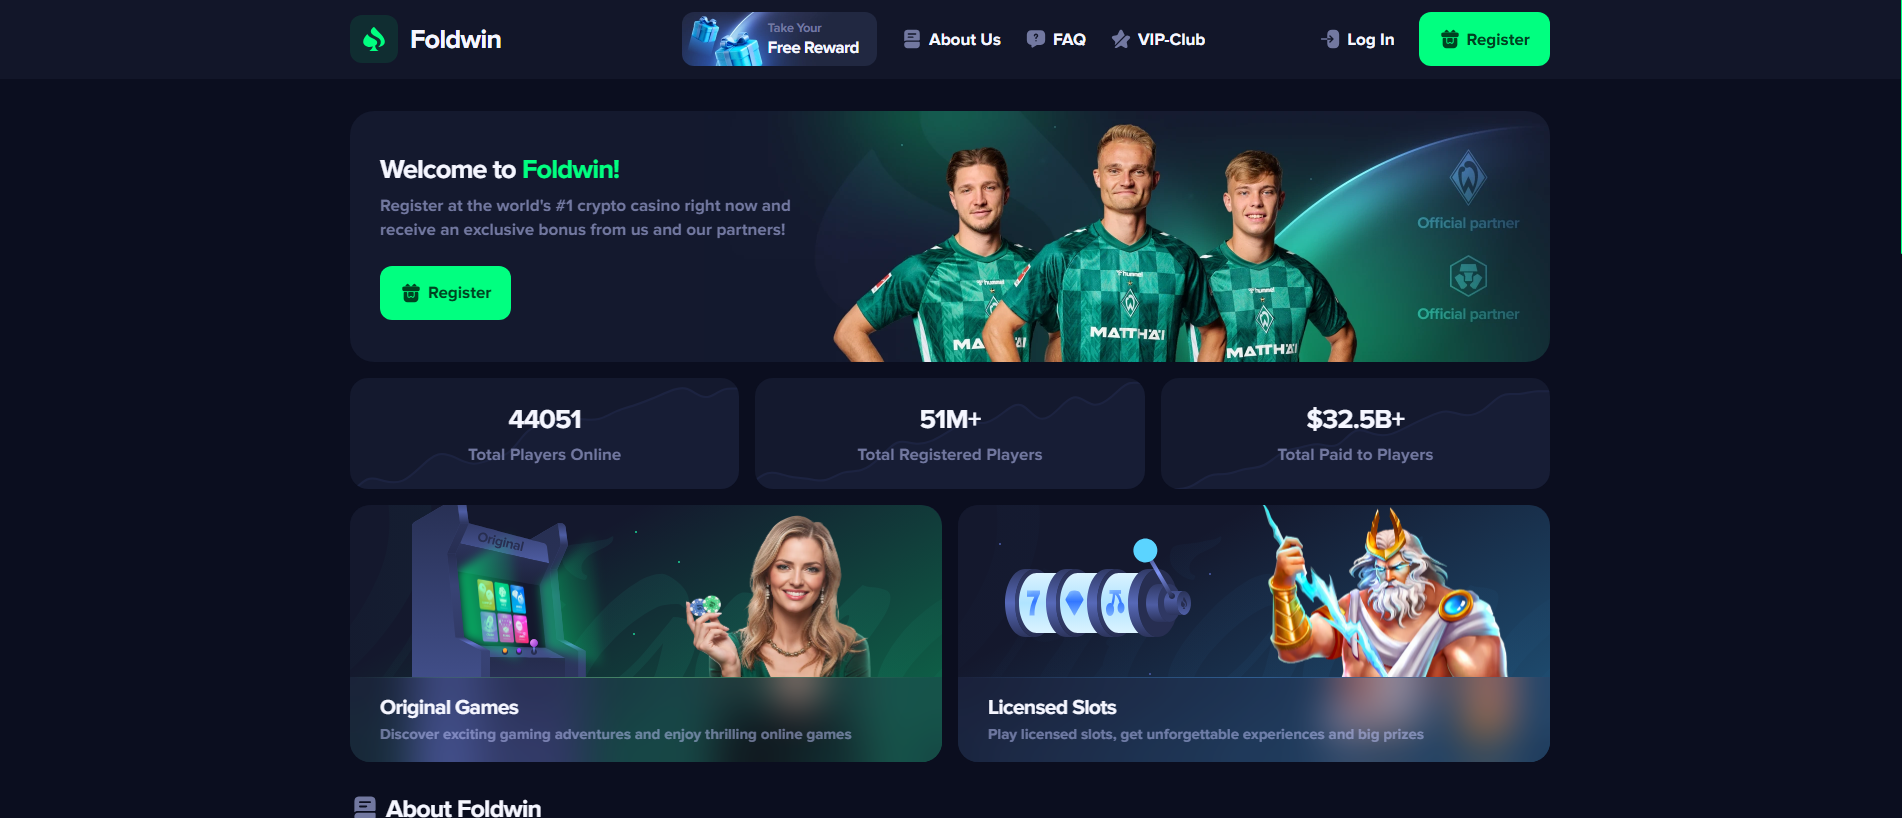
play.foldwin.com — Terakhir diketahui aktif (HTTP 200). Peniruan identitas merek: Cryptoscam; Jenis penipuan: Impersonation. Ringkasan bukti: VirusTotal 15/91 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); URLScan malicious verdict; Spamhaus DBL_PHISH; 1 external blocklist match (ScamSniffer); PhishDestroy score 100/100. Registrar: Fewmoretaps OU d/b/a T….
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.

On 2026-10-01, play.foldwin.com returned an HTTP status code of 200 in a recorded observation. The same domain was first observed on 2026-09-29, and a PhishDestroy internal listing is recorded as true.
The HTTP check on 2026-10-01 recorded status 200, while the first observation of play.foldwin.com dates to 2026-09-29. VirusTotal on 2026-09-28 recorded 15 detections across 91 scanners, and ScamSniffer appears as the sole external blocklist entry on 2026-10-01. A PageSpeed check on 2026-09-29 recorded a performance score of 37, and the SSL scan on 2026-09-29 named the issuer as Let's Encrypt / YE1.
The VirusTotal scan on 2026-09-28, the PageSpeed and SSL scans on 2026-09-29, and the HTTP and blocklist checks on 2026-10-01 come from different dates, so the records describe separate moments rather than one snapshot. Because the ScamSniffer listing and the PhishDestroy internal listing were recorded on different dates, a reader can compare when each source flagged the domain without treating either as a final judgment.
Anyone reviewing play.foldwin.com should retain the dated records from VirusTotal, ScamSniffer, PageSpeed, and the HTTP check so later observations can be compared against them. During that review, avoid submitting passwords, payment details, or other sensitive information to the domain until the recorded signals have been independently verified. Subsequent checks of play.foldwin.com should be logged with their own dates so changes in the ScamSniffer listing, the PhishDestroy internal listing, and the VirusTotal detections can be tracked over time.
Data pengamatan perbandingan crawler versus browser yang telah disimpan untuk host ini, ditambah pemeriksaan sidik jari secara real-time untuk sistem distribusi lalu lintas bergaya Keitaro.
Catatan pemindai: alive_content: raw=ok; http=200; via=https_proxy
 (BY)
PhishDestroy Investigation
Reputasi Edge-IP tidak dikaitkan dengan domain ini.
violet.ns.cloudflare.comwesley.ns.cloudflare.comLocation describes the IP network.
facbd59a7bba491c60e7ea6806bdd82e1eea79d9e0988b55b284b8b407d27067Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of play.foldwin.com · checked Sep 29, 2026
62.60.226.245. 13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Template-based draft · optional AI wording assistance requires separate consent
Setiap jalur merupakan salah satu alasan mengapa sebuah domain terhubung ke host ini. Ukuran node menandai deteksi VirusTotal, sedangkan node bergaris putus-putus menunjukkan bahwa node tersebut sudah offline. Daftar lengkapnya tercantum di bawah ini.
Catatan bukti terpisah untuk domain yang dapat didaftarkan di atas: play.foldwin.com.
foldwin.com 17 VTHash favicon yang sama atau judul halaman yang sama dengan host ini.
Laporan-laporan ini diselesaikan dengan IP edge bersama yang sama. Mereka membantu penemuan laporan tetapi tidak menyiratkan kepemilikan bersama atau server asal bersama.
Domain-domain ini juga menargetkan pengguna Cryptoscam. Lihat semua ancaman dari Cryptoscam →
Didaftarkan melalui penyedia layanan pendaftaran yang sama. Sebuah penyedia layanan pendaftaran melayani jutaan pelanggan yang tidak saling terkait, sehingga hal ini sekadar mengelompokkan laporan-laporan tersebut, bukan membuktikan adanya hubungan.
Laporan baru-baru ini ditambahkan dari database PhishDestroy. Tautan penemuan ini tidak berarti infrastruktur atau kepemilikan bersama.
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive