OTX
4 community references
Laporan

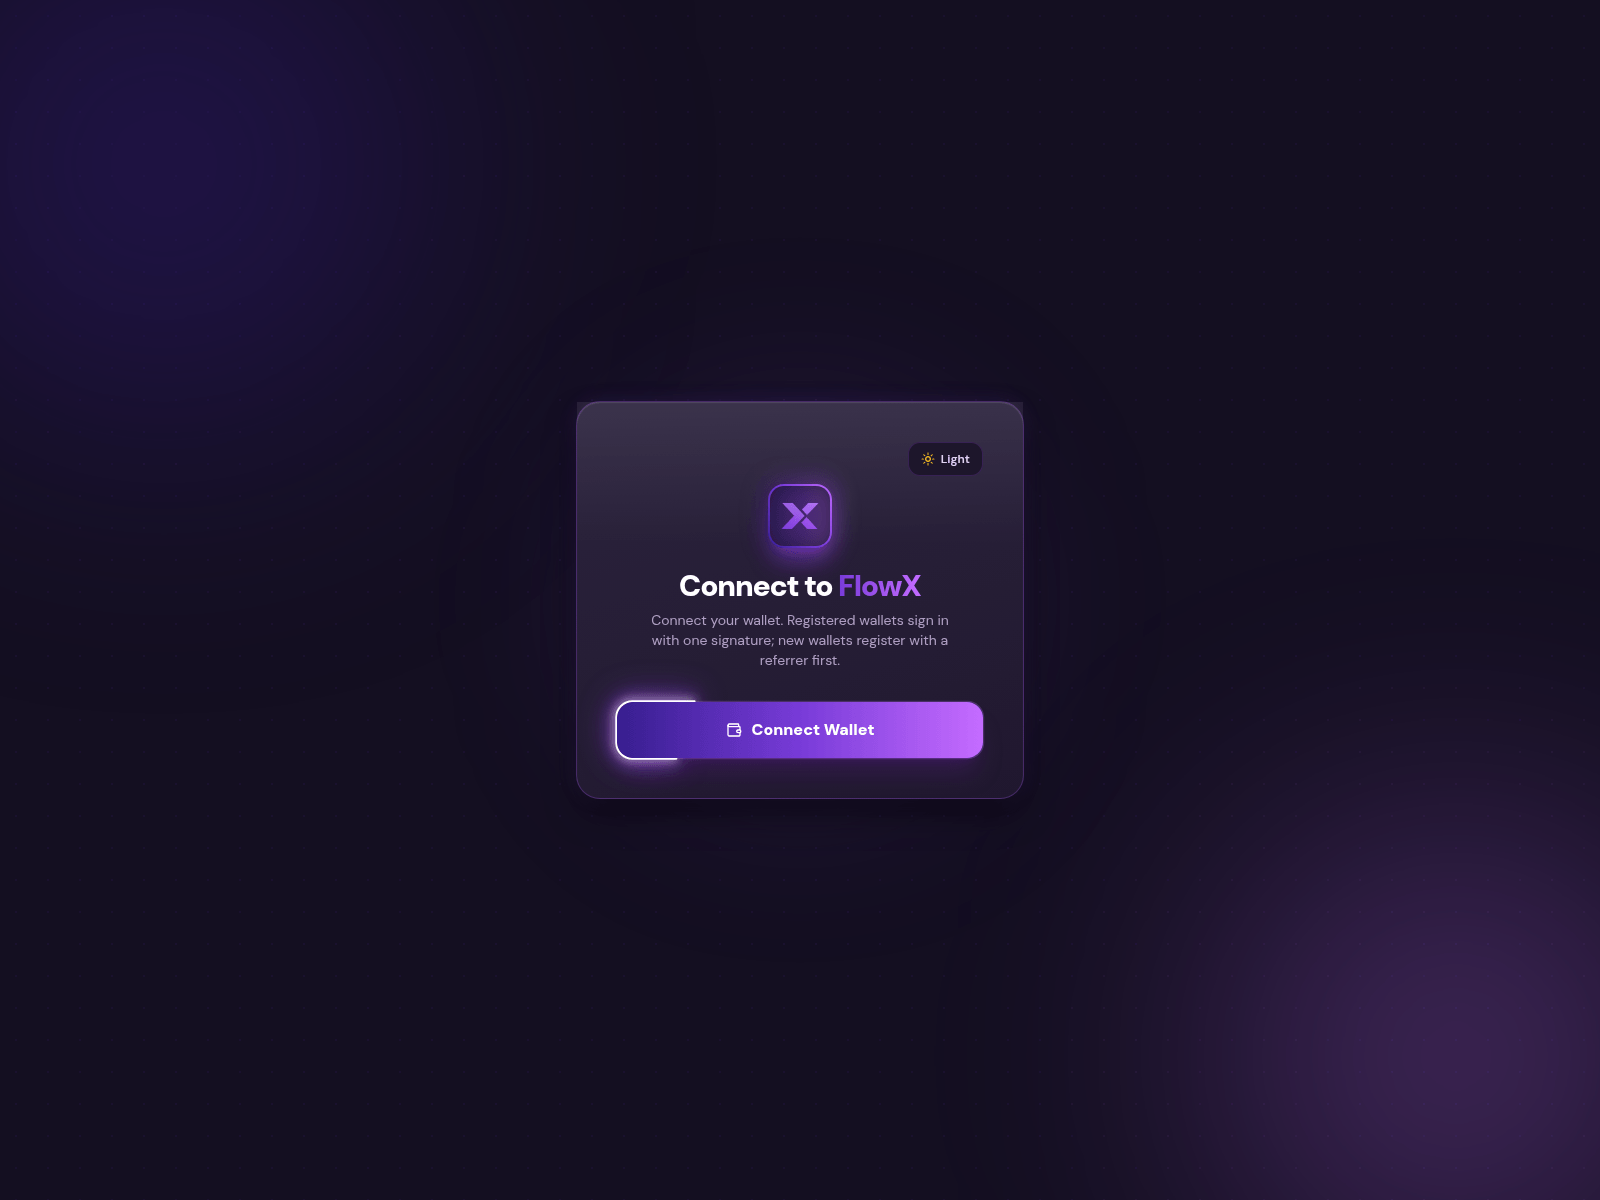
“FlowX Dashboard | Staking & Decentralized Yield Platform”
fxrprotocol.io — Terakhir diketahui aktif (HTTP 200). Jenis penipuan: Crypto Drainer. Ringkasan bukti: URLScan capture; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 66/100. Registrar: Dynadot.
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.

fxrprotocol.io was first observed on 2026-10-11, with external blocklist entries recorded by MetaMask and SEAL on that date. The domain is also referenced in multiple intelligence sources, adding context to its current assessment.
MetaMask and SEAL included fxrprotocol.io in their external blocklists on 2026-10-11. PhishDestroy documented an internal listing for the domain on the same date. OTX recorded four separate pulses referencing fxrprotocol.io, also dated 2026-10-11. The domain was registered with Dynadot Inc on 2026-09-25, and its SSL certificate was issued by Let's Encrypt / YE1, scanned on 2026-10-11.
PhishDestroy contains an internal listing that records fxrprotocol.io in its monitored database, providing a point of reference for internal security checks. OTX documents four distinct pulses, which measure community-contributed intelligence and allow for comparison with external blocklist entries. The scope of these observations covers both internal and external security perspectives, with all records dated closely together for consistent review.
For fxrprotocol.io, preserve the external blocklist records from MetaMask and SEAL for ongoing reference. Retain the OTX pulse data and PhishDestroy internal listing to compare against future findings. Review all recorded evidence periodically to monitor for new or updated source entries related to the domain.
Data pengamatan perbandingan crawler versus browser yang telah disimpan untuk host ini, ditambah pemeriksaan sidik jari secara real-time untuk sistem distribusi lalu lintas bergaya Keitaro.
cloudflareCatatan pemindai: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare
 (US)
Reputasi Edge-IP tidak dikaitkan dengan domain ini.
jose.ns.cloudflare.comliz.ns.cloudflare.comLocation describes the IP network.
a683d3dcb99fa118e5acab15ff9fa1f3f41d56ac2a420708a928212750503981Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
172.67.162.16. 7 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Template-based draft · optional AI wording assistance requires separate consent
Setiap jalur merupakan salah satu alasan mengapa sebuah domain terhubung ke host ini. Ukuran node menandai deteksi VirusTotal, sedangkan node bergaris putus-putus menunjukkan bahwa node tersebut sudah offline. Daftar lengkapnya tercantum di bawah ini.
Laporan-laporan ini diselesaikan dengan IP edge bersama yang sama. Mereka membantu penemuan laporan tetapi tidak menyiratkan kepemilikan bersama atau server asal bersama.
Didaftarkan melalui penyedia layanan pendaftaran yang sama. Sebuah penyedia layanan pendaftaran melayani jutaan pelanggan yang tidak saling terkait, sehingga hal ini sekadar mengelompokkan laporan-laporan tersebut, bukan membuktikan adanya hubungan.
Laporan baru-baru ini ditambahkan dari database PhishDestroy. Tautan penemuan ini tidak berarti infrastruktur atau kepemilikan bersama.
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive