FBI IC3
Laporkan kejahatan yang dimungkinkan oleh internet di Amerika Serikat
Federal tips line1-800-CALL-FBI

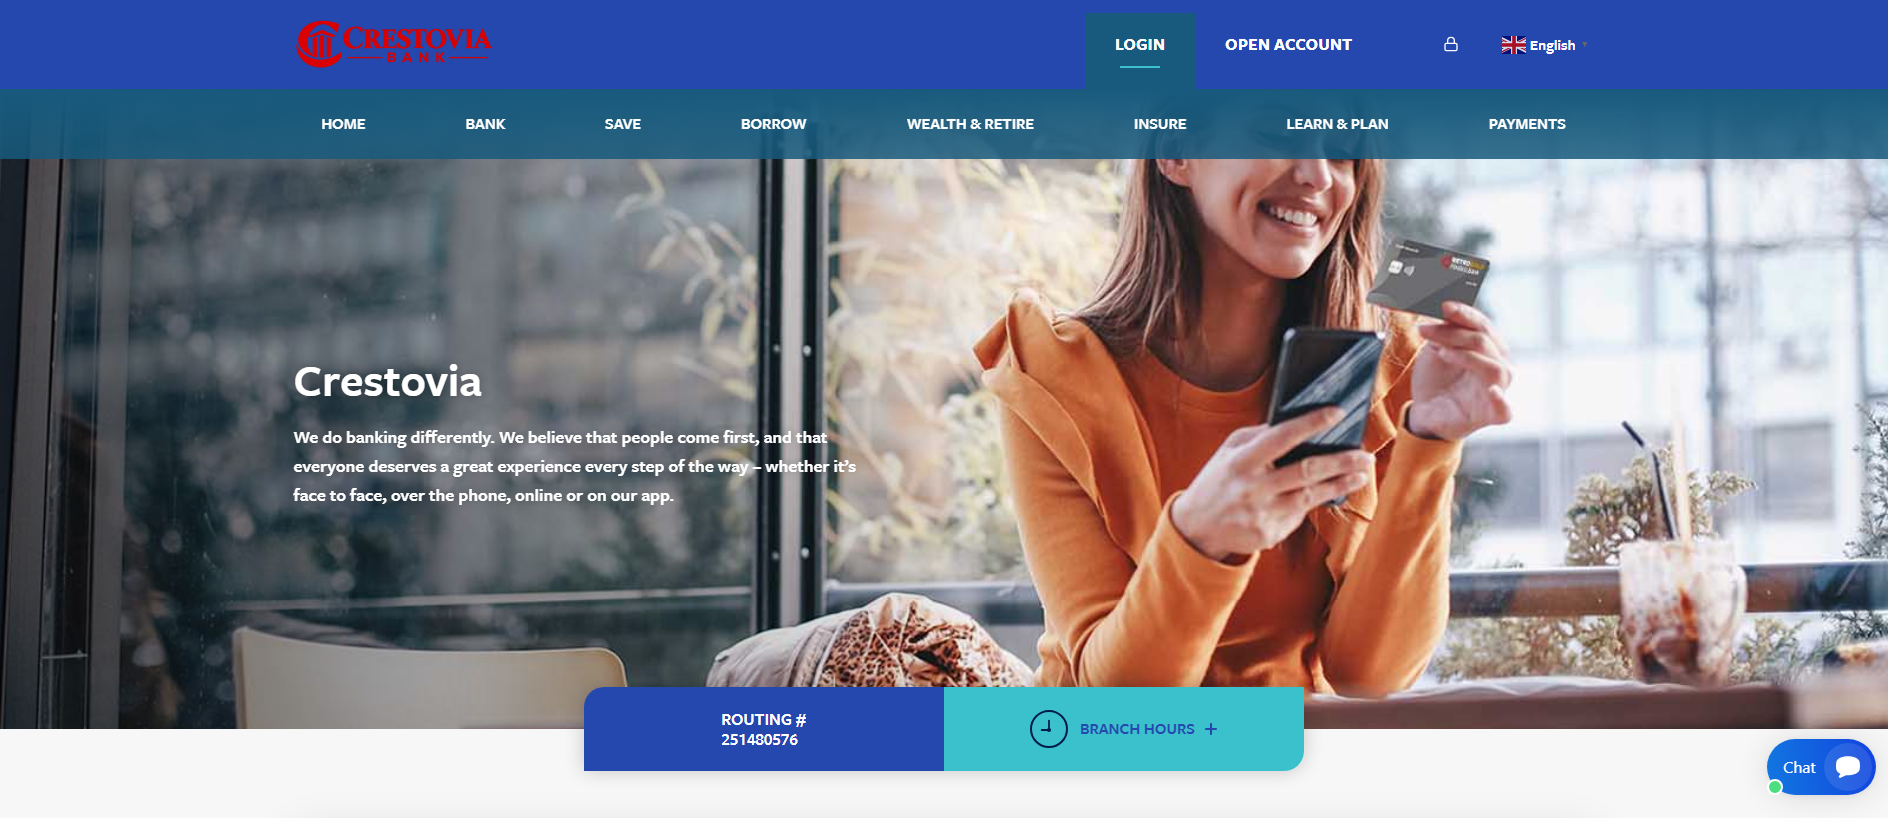
“Home | Mobile Banking, Credit Cards, Mortgages, Auto Loan”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@inwx.com.
The latest stored availability evidence still shows the domain reachable; 39 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
crestoviabnk.com — Terakhir diketahui aktif (HTTP 200). Peniruan identitas merek: Unknown; Jenis penipuan: Impersonation. Ringkasan bukti: VirusTotal 7/89 (alphaMountain.ai, Fortinet, Google Safe Browsing, Gridinsoft, Netcraft); URLScan malicious verdict; Google Safe Browsing flagged; PhishDestroy score 100/100. Registrar: INWX.
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.
PhishDestroy first observed crestoviabnk.com on Sep 19, 2026. Stored content metadata identifies Unknown as the apparent target. The captured page title is “Home | Mobile Banking, Credit Cards, Mortgages, Auto Loan”. Page analysis recorded additional brand references to Mastercard. Stored page analysis classifies the content as impersonation. Current evidence score: 100/100 (critical).
Positive findings are stored from 3 sources: VirusTotal, Google Safe Browsing, and URLScan. On Sep 21, 2026 at 05:26 UTC, VirusTotal recorded 7 detections among 89 engines: alphaMountain.ai, Fortinet, Google Safe Browsing, Gridinsoft, Netcraft, SOCRadar, desenmascara.me; Google Safe Browsing flagged the domain: Social Engineering. URLScan returned a malicious verdict with score 100; scan metadata assigned phishing as its category on Sep 20, 2026 at 03:30 UTC. Non-positive and contextual checks: AlienVault OTX listed 4 community pulse references (not vendor detections) on Sep 21, 2026 at 05:28 UTC. The separate external-blocklist snapshot contained no matches on Sep 21, 2026 at 10:20 UTC. URLQuery recorded no positive detection on Sep 19, 2026 at 18:32 UTC.
HTTP 200 was recorded on Sep 21, 2026 at 02:23 UTC. Registration records for the domain list INWX GmbH as the registrar and Sep 9, 2026 as the creation date. Registration preceded first observation by 10 days. At collection time, the hostname resolved to 198.251.84.200 on AS53667 (PONYNET - FranTech Solutions, US). The recorded endpoint location is Luxembourg, US. The stored server header is LiteSpeed. DOM analysis on Sep 20, 2026 at 02:20 UTC returned 100/100. The evidence archive retains 4 visual captures from PhishDestroy, URLScan, and URLQuery. TLS metadata lists YR1 as the certificate issuer; checked Sep 19, 2026 at 19:02 UTC.
The content indicators and 3 positive source findings support the current Unknown-themed impersonation classification.

198.251.84.200. Evasion analysis
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
LiteSpeedScanner note: captcha: raw=captcha; http=200; via=https_proxy; server=LiteSpeed
 (NL)

Google PageSpeed Insights — mobile performance audit of crestoviabnk.com · checked Sep 19, 2026
PD-20260919-BAF7CD Recipient: abuse@inwx.com Registrar: INWX GmbH & Co. KG (Germany) Policy Violations: “Acceptable Use Policy prohibits phishing, identity fraud, malware and other illegal activities; registrar reserves the right to disable DNS or revoke domains used for abuse.” Applicable Laws: German StGB §§202a–c; §263; EU Directive 2013/40/EU; ICANN DNS Abuse Framework
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Infrastructure map · crestoviabnk.com
Each spoke is one reason two domains are linked. Ring size marks VirusTotal detections; dashed nodes are already offline. Full lists below.
IP asal ini menghosting beberapa domain phishing — infrastruktur dapat digunakan bersama di seluruh kampanye.
These domains also target Tidak diketahui users. View all Unknown threats →
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive


 elitedigitmax.com
 globalelitescapital.com
 mail.bitfinexcreditunion.co
 automatedtradingpoint.com
 allworldcards.net
 aurexsdigital.com
 globalelitemeridian.com
 moviracfb.com